Linux and open source trends in 2024

0
[ad_1]

In 2024, the Linux and open-source landscape is poised for significant change. Known for its strong security and adaptability, Linux continues to be a key player in the tech world. This article explores the evolving trends in Linux and open source, highlighting groundbreaking developments from enhanced security to innovative educational roles. Join us as we explore how these technologies are shaping our digital future.

The Crucial Role of Privacy Tools in Linux

Linux, renowned for its robust security, provides a solid foundation for users to prioritize safety and privacy. However, it’s crucial to recognize that while Linux secures your device, it doesn’t inherently protect the data you send over the internet. Data transmitted from your Linux device can be just as vulnerable as on any other platform once it leaves your system.

This is where VPNs play a pivotal role as they hide your original IP address, effectively masking your online footprint. This means that the websites and services you access only see the IP address provided by the VPN, not your actual one. This level of privacy is further bolstered by AES encryption with PIA, making your data indecipherable to potential cybercriminals. As we delve into the future of Linux and open source, the importance of such privacy tools becomes increasingly crucial in our connected world.

Revolutionizing Open Source Interaction

The open-source community, the bedrock of collaborative innovation, is on the brink of a transformative shift. The next few years are expected to usher in an era of advanced collaboration platforms, leveraging the power of cloud computing and real-time collaboration tools. These platforms won’t just streamline project management and code development; they’ll actively foster a more inclusive and global participation. Expect a surge in virtual hackathons, open-source contribution sprints, and cross-project collaborations that break down geographical barriers. This evolution will not only democratize access to open-source projects but also enrich them with diverse perspectives and expertise.

Sustainable Computing: Linux’s Green Revolution

The urgency of environmental sustainability is reshaping the ethos of Linux and open-source projects. Upcoming initiatives are likely to emphasize eco-friendly software development, which includes optimizing code for lower energy consumption and supporting hardware longevity. Projects may increasingly adopt ‘green coding’ practices that prioritize efficiency and minimal resource usage. We might also see a rise in open-source software tailored for renewable energy management, smart grid technologies, and environmental data analysis. These efforts reflect a growing consciousness within the Linux community to align tech innovation with ecological responsibility.

Emerging Hardware Compatibility

Linux’s reputation for adaptability will be significantly bolstered as it expands its compatibility with emerging technologies. We are likely to witness Linux systems seamlessly integrating with a variety of new hardware, from advanced wearables to IoT devices. This includes better support for cutting-edge processors and GPUs, facilitating Linux’s use in high-performance computing and AI research. Additionally, as AR and VR technologies mature, expect Linux to play a significant role in driving these innovations forward, providing a stable and versatile platform for development and deployment.

The Educational Role of Linux and Open Source

In education, Linux and open source are transitioning from optional tools to integral components of the curriculum. Their role in teaching not only programming and system administration but also in fostering critical thinking and collaborative skills is becoming more pronounced. Educational institutions might increasingly adopt Linux-based environments for their cost-effectiveness and customizability, offering students a more hands-on learning experience. Furthermore, open-source contributions and projects could become a key part of tech education, preparing students for the collaborative and ever-changing nature of the tech industry.

AI and Open Source: A Partnership Poised for Innovation

The synergy between AI and open source is set to unlock new horizons in technological advancement. Open-source AI projects are facilitating more transparent, ethical, and community-driven development of AI technologies. These projects offer a platform for experimentation and innovation in fields like machine learning, natural language processing, and predictive analytics. Additionally, the integration of AI into open-source tools is simplifying complex tasks like code review, bug tracking, and software optimization, enhancing the efficiency and quality of open-source software development.

A Vision of Progressive and Secure Technology

As we look to the future, Linux and open source stand at the forefront of a digital revolution that is not just technological but also cultural and ecological. The developments in these realms are set to create a more inclusive, sustainable, and innovative technological landscape.


[ad_2]
Source link
Ransomware-as-a-Service Attacks targeting Middle East & Africa

0
[ad_1]

The Middle East and Africa (MEA) region has witnessed a surge in ransomware-as-a-service (RaaS) attacks, posing a grave threat to digital security.

This comprehensive report delves into the key findings, attack trends, the impact on businesses, and the crucial preventive measures that must be adopted to combat this escalating cyber threat.

The digital transformation journey of the MEA region, while opening new avenues for growth, has also exposed it to sophisticated cyber threats.

Among these, ransomware attacks have emerged as a formidable challenge, with a notable increase in incidents orchestrated through the RaaS model.

Data Leaks in the middle east & Africa
Data Leaks in the Middle East & Africa

This phenomenon not only jeopardizes the security of critical data but also undermines the economic stability of the affected regions.

Technical Analysis

The Gulf Cooperation Council (GCC) countries, South Africa, and Turkey have been identified as the hotspots for these cyber assaults.

The report also highlights the proliferation of information stealers, with over 1.2 million infected devices across MEA, underscoring the extensive reach of cybercriminal networks.

LockBit, BlackCat (ALPHV), and Arvin Club have been pinpointed as the most active ransomware gangs in the region, with LockBit accounting for 38% of the attacks.

Ransom attacks
Ransom attacks

Recent research by Group-IB highlights a staggering 68% increase in ransomware attacks across the MEA region, with the financial services and real estate sectors being the primary targets.

This surge in ransomware incidents is attributed to the RaaS model, which has democratized access to sophisticated cyberattack tools, enabling even low-skilled criminals to launch devastating attacks.

The RaaS model has significantly lowered the barrier to entry for cybercriminals, leading to a diversification of targets and an increase in attack frequency.

Financial services, real estate, and manufacturing sectors have borne the brunt of these attacks, with a notable rise in data leaks and compromised corporate networks.

The involvement of Initial Access Brokers (IABs) in selling access to these networks on the dark web further complicates the threat landscape, making it imperative for businesses to bolster their cybersecurity defenses.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are incredibly harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter


[ad_2]
Source link

Nepali Hacker Tops Hall of Fame by Reporting Facebook’s Zero-Click Flaw

0
[ad_1]

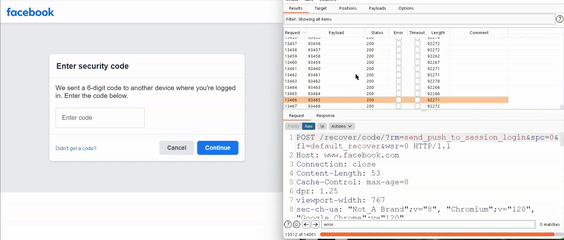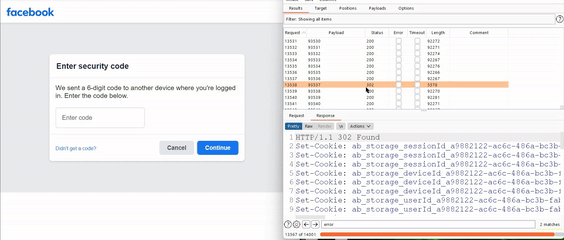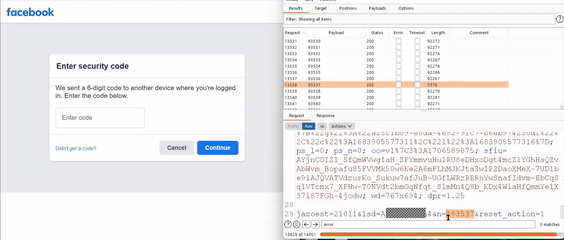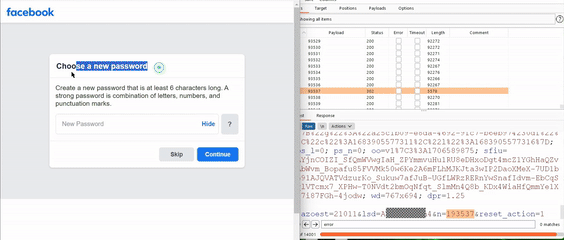
Samip Aryal, a cybersecurity researcher and an ethical hacker from Nepal, bypassed the system’s rate-limiting feature and subsequently checked possible combinations of 6-digit numbers (from 000000 to 999999) for two hours.

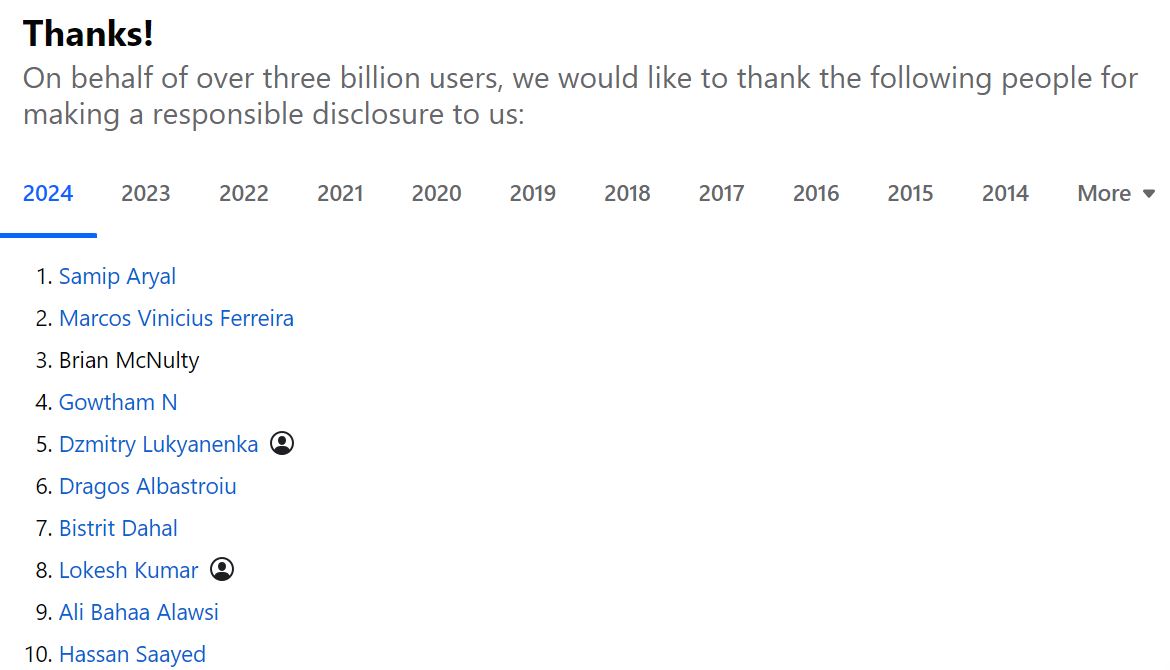
Samip Aryal, a Nepali bug bounty hunter, discovered a zero-click flaw in Facebook’s password reset system, potentially allowing hackers to compromise any targeted account. This exploit earned Aryal his highest bug bounty, making him top the Facebook Hall of Fame for White-Hat Hackers 2024 ranking, though the exact bounty amount remains unknown.]

Nepali Hacker Tops Facebook Hall of Fame by Exposing Account Takeover Flaw
Samip Aryal tops Facebook Hall of Fame list

Aryal discovered a way to abuse Facebook’s password reset functionality without rate-limiting. The bug allowed attackers to hijack user accounts through “zero-click” attacks (without user interaction) by requesting a password reset and brute force the 6-digit security codes. 

The vulnerability was discovered in Facebook’s password reset functionality. It allowed hackers to bypass the system’s rate-limiting feature and subsequently check possible combinations of 6-digit numbers (from 000000 to 999999) for two hours.

In his blog, Aryal revealed finding a vulnerable endpoint on Android Studio while testing Facebook versions. He received a pop-up in the password reset flow offering users to send a security code through Facebook notification. The code remained active for two hours despite incorrect inputs.

“I didn’t see any sort of code invalidation after entering the correct code but with multiple previous invalid tries (unlike in the SMS reset functionality),” Aryal explained.

He used a brute-force attack methodology to cover the entire search space in an hour, revealing that some users had the nonce code displayed on the notification, a zero-click exploit. The code was displayed on another screen with a single click.

For your information, a cryptographic nonce is an arbitrary number that can only be used once in a cryptographic communication. He further noted that hackers could hijack Facebook user accounts by choosing any account, going to its password reset flow, selecting “Send code via Facebook notification,” trying any code to receive a server response, and brute forcing it in two hours. Facebook application users would receive notifications with a six-digit code or prompting them to tap to see the login code.

Nepali Hacker Tops Facebook Hall of Fame by Exposing Account Takeover Flaw
PoC GIF

Aryal responsibly disclosed the flaw to Facebook on January 30, 2024, and the issue was fixed on February 2. 

The vulnerability could lead to personal information theft, disinformation spread, and network attacks. Being aware of emerging security threats on Meta and other social networking platforms is also crucial to keep your accounts protected.

It is worth mentioning that Meta accounts have particularly been the target of scams lately. In March 2023, researchers at Guardio discovered an info-stealing campaign involving fake ChatGPT extensions claiming to integrate with Google search results but in reality attempting to steal Facebook accounts. 

WithSecure cybersecurity firm identified a connection between recent DarkGate malware attacks and Vietnam-based threat actors attempting to hijack Meta business accounts and steal sensitive data in October 2023.

To stay safe, users should enable two-factor authentication, use strong, unique passwords, be cautious with password reset requests, and stay updated on security threats. 

  1. 6 of the Best Crypto Bug Bounty Programs
  2. 10 Famous Bug Bounty Hunters of All Time
  3. Bug bounty: Hack Tesla Model 3 to win your own Model 3
  4. OpenAI’s ChatGPT Bug Bounty Program – Earn $200 to $20k
  5. Bug Bounty: Earn $40K for hacking Facebook, Instagram, WhatsApp

[ad_2]
Source link

Leaked Galaxy Tab S6 Lite (2024) pricing suggests price decrease

0
[ad_1]

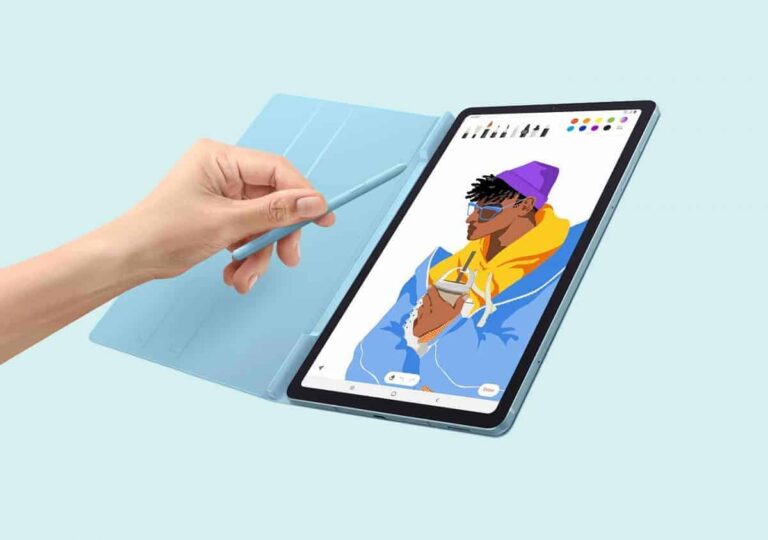
The pricing and configuration details of the Samsung Galaxy Tab S6 Lite (2024) for the European markets have leaked out. It will arrive as the successor to the S6 Lite 2022 edition. The upcoming offering has already bagged multiple certifications hinting at its imminent launch.

Samsung Galaxy Tab S6 Lite (2024) details surface for the European market

Citing a European source, Appuals reports that the Samsung Galaxy Tab S6 Lite (2024) will launch in 4GB + 64GB and 4GB + 128GB RAM and storage configurations. The WiFi-only version of the base option will cost €429 whereas the higher model will be available for €489. On the other hand, the LTE network version of the same variants will cost €459 and €519.

Compared to the 2022 edition, the upcoming S6 Lite (2024) edition price seems to be cheaper for all variants except the 64GB WiFi-only model. The publication adds that the pricing could vary depending on the market region. The Tab S6 Lite (2024) will come in Chiffon Pink, Oxford Grey, and Light Green color options.

Only a few upgrades expected on the upcoming offering

Appuals says that the Galaxy Tab S6 Lite (2024) is confirmed to feature a 10.4-inch display as per the source. This is the same as its predecessor. Based on leaks and rumors, an Exynos 1280 processor will reportedly power the tablet. It is expected to be backed by a 6,840mAh battery unit (advertised as 7,000mAh) with support for 15W charging. The upcoming offering will run on Android 14 with OneUI 6 layered on the top.

Samsung first launched the Galaxy Tab S6 Lite in 2020. The brand followed it up with a 2022 edition with incremental upgrades. We assume the upcoming 2024 edition will also continue the same tradition.


[ad_2]
Source link
X reinstates policy against misgendering & deadnaming

0
[ad_1]

X is again making it illegal for users to misgender and deadname other users on the platform. The policy was dropped last year, but X is reinstating it again following numerous criticisms.

As Ars Technica reports, in April last year, X (called Twitter back then) updated its abuse and harassment policy to allow for misgendering and deadnaming. The policy was adopted in the pre-Musk era in 2018. But the billionaire later suggested that his tweets might violate the policy.

Meanwhile, the latest update to X’s policy in January indicates that the company is again banning users from misgendering and deadnaming transgender people and other members of the LGBTQ+ community under the newly-added “Use of Prior Names and Pronouns” section.

Misgendering and deadnaming is illegal again on X

As the new policy reads, X will “reduce the visibility of posts that purposefully use different pronouns to address someone other than what that person uses for themselves, or that use a previous name that someone no longer goes by as part of their transition.”

Posts that contain misgendering and deadnaming will be removed from search results, timelines, trends, and notifications. Additionally, no ads will be shown adjacent to them.

The non-profit LGBTQ advocacy organization GLAAD blamed X back then for not banning misgendering and deadnaming. It said Twitter’s move was “the latest example of just how unsafe the company is for users and advertisers alike.” Meanwhile, the organization said policies that explicitly ban misgendering and deadnaming are better than vague policies that confuse content moderators.

LGBTQ+ advocacy groups are not happy with X’s recent policy update

The platform only acts against misgendering and deadnaming if it receives a complaint from the target. That is according to a new policy. “Given the complexity of determining whether such a violation has occurred, we must always hear from the target to determine if a violation has occurred.”

Meanwhile, GLAAD suggests that self-reporting is not the best possible way to tackle desecration against the LGBTQ+ community. Presumably, because it puts all the burden on the victim’s shoulders. The GLAAD’s Jenni Olson told Ars that X’s recent move is a step back from stronger protections that the platform had in place for many years.


[ad_2]
Source link
A week in security (February 26 – March 3)

0
[ad_1]

March 1, 2024 – Scammers are attacking Mac users interested in cryptocurrencies using a fake fix for a meeting link that won’t work.

March 1, 2024 – Pig butchering scams are usually tied to cryptocurrency investments that make for big business with victims on both sides of the line.

February 29, 2024 – One of our researchers was targeted by a scammer advertising on Airbnb and hosting a fake Tripadvisor website.

February 29, 2024 – A vulnerability, now fixed, in Facebook could have allowed an attacker to take over a Facebook account without the victim needing to click on anything at all.

February 28, 2024 – Detecting and disrupting a months-long malware campaign on an MSP.


[ad_2]
Source link

Vivo X Fold 3 Pro specifications & design appear ahead of launch

0
[ad_1]

The Vivo X Fold 3 Pro specifications and design have just surfaced ahead of its expected launch. This smartphone is tipped to arrive at some point this month. Vivo still didn’t reveal the launch date, though.

The Vivo X Fold 3 Pro specifications and design have been revealed

The phone’s specifications and design have been shared by Digital Chat Station, a well-known Chinese tipster. The design was shared recently, while the phone’s specifications surfaced today from the same source.

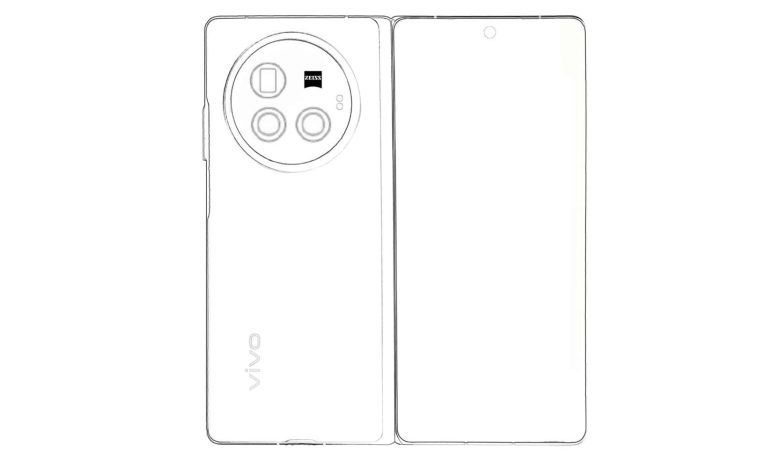
Let’s first check out the schematic that the tipster offered, you can check it out below. It seems like the Vivo X Fold 3 will have a similar form factor to most book-style foldables. It will have a display camera hole on the cover display and three cameras on the back. ZEISS optics will be a part of the package, and so will a periscope telephoto camera.

Vivo X Fold 3 Pro sketch 1

Two 120Hz displays will be on offer, along with the Snapdragon 8 Gen 3 SoC

What about the specs? Well, an 8.03-inch main display is tipped. It’s said to offer a 2480 x 2200 resolution, and it will be an LTPO panel (1-120Hz refresh rate). Dolby Vision and HDR10+ content support are expected. A 6.53-inch 2748 x 1172 AMOLED display is also expected with a 120Hz refresh rate.

The Snapdragon 8 Gen 3 processor will fuel this smartphone, while it will also include 16GB of LPDDR5X RAM. The phone is tipped to offer 1TB of UFS 4.0 flash storage as well. Android 14 will come pre-installed on the device, with Vivo’s OriginOS 4. Do note that this is a Chinese variant we’ll talking about. We’re not sure if the global one will be coming, but Vivo has not launched one of its foldable phones globally just yet.

Vivo plans to utilize a 5,800mAh battery, and offer blazing fast charging

A 5,800mAh battery is also tipped, as is 120W wired, and 50W wireless charging. The device is also said to offer reverse wireless charging. An in-display ultrasonic fingerprint scanner will be located on both the main and cover displays, it has been said, and an IR blaster will also be a part of the package.

A 50-megapixel main camera (OmniVision OV50H sensor, OIS, V3 chip) will be backed by a 50-megapixel ultrawide unit. The third camera on the back will be a 64-megapixel periscope telephoto camera (OmniVision OV64B sensor, 3x optical zoom). The tipster says we can expect a 32-megapixel selfie camera on both of the phone’s displays.

The regular Vivo X Fold 3 could also arrive

Stereo speakers will be a part of the package, as will two SIM card slots. The device will support 5G, Bluetooth 5.4, and Wi-Fi 7 as well, in case you were wondering. This smartphone is tipped to arrive alongside the Vivo Pad 3 tablets, and the vanilla Vivo X Fold 3 could also launch. The Vivo X Fold 3 actually got its 3C certification. That model will offer 80W wired charging.


[ad_2]
Source link

Microsoft released a new update to fix Edge’s previous buggy update

0
[ad_1]

Microsoft has corrected a prior glitchy update to its Edge browser, which was causing numerous problems for users. The tech giant admitted that many users’ browsing experiences had been negatively impacted by several vulnerabilities that had been unintentionally introduced by the original update.

The buggy update led to complaints from users about slow loading times, frequent crashes, and other performance issues. A user on Neowin was the first to spot the issues and report them to the blog. Other Edge users later raised their voices on Reddit and Microsoft’s support website against the buggy update that turned the browser unfunctional.

You can now get Microsoft Edge’s new update from the company’s download servers.

Following the update, Edge was unable to open webpages. It notified users that “this page is having a problem” or there is “not enough memory to open this page.” The glitchy update even led to the browser’s settings panel and bookmarks stopping working.

The memory error was supposedly due to an Enhanced Web Protection update that Microsoft intended to bring to Edge. Some users reported that they could solve the issue by turning off “Enhance your security on the web” in Edge’s settings.

These issues were created by the stable version of Edge, 122.0.2365.63. Disabling the add-ons and closing tabs couldn’t solve the problem either.

If you’re an impacted user, the fix has arrived. Microsoft first removed version 122.0.2365.63 from its download servers and then released version 122.0.2365.66 as a fix. You can now update your browser to the latest version to ensure everything works fine.

In February, Microsoft also fixed the automatic import glitch on Edge that imported data and tabs from Google Chrome without user consent. Microsoft claims the issue was due to a software bug. However, some rivals like Mozilla demand an investigation into Microsoft’s tactics for keeping users on its Edge browser.


[ad_2]
Source link

U.S. Charged Iranian Hacker, Rewards up to $10 Million

0
[ad_1]

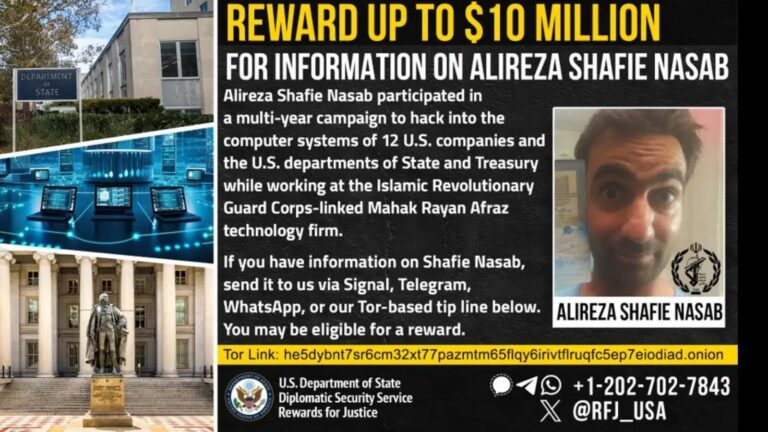
The United States Department of Justice (DoJ) has charged an Iranian national, Alireza Shafie Nasab, for his alleged involvement in a sophisticated cyber-espionage campaign targeting American entities.

The indictment, unsealed recently, reveals a multi-year operation that compromised governmental and private sector systems, including the U.S. Departments of the Treasury and State, defense contractors, and companies based in New York.

A Persistent Cyber Campaign

Nasab, 39, is accused of working under the guise of a cybersecurity specialist for Mahak Rayan Afraz (MRA), an Iranian company with links to the Islamic Revolutionary Guard Corps (IRGC).

From 2016 through April 2021, the campaign involved spear-phishing and other hacking techniques to infect over 200,000 victim devices, many containing sensitive or classified defense information.

The Rewards for Justice Twitter account recently announced that the U.S. government has pressed charges against a group of Iranian hackers for their involvement in cyber attacks.

The spear-phishing campaigns were meticulously organized using a custom application, allowing Nasab and his co-conspirators to deploy their attacks effectively.

In one instance, they breached an administrator email account at a defense contractor. It was then used to create rogue accounts and send further spear-phishing emails to other defense contractors and a consulting firm.

Social Engineering and Identity Theft

Apart from spear-phishing, the conspirators also engaged in social engineering, often masquerading as women to gain the trust of their victims and deploy malware.

Nasab is believed to have played a crucial role in procuring infrastructure for the campaign, using stolen identities to register servers and email accounts.

Nasab faces multiple charges, including conspiracy to commit computer fraud, wire fraud, and aggravated identity theft.

He could face up to 47 years in prison if convicted on all counts. Despite being at large, the U.S. State Department has announced a reward of up to $10 million for information leading to his identification or location.

Broader Context of U.S.-Iran Relations

The indictment comes amid a backdrop of tense U.S.-Iran relations, with ongoing concerns about Iran’s nuclear program and its support for proxy forces in the Middle East.

The U.S. has been involved in efforts to curb Iran’s nuclear ambitions and has faced various provocations, including the seizure of tankers and military escalations.

The charges against Nasab underscore the global threat posed by state-linked cybercriminals.

The U.S. has taken a firm stance against such activities, offering substantial rewards for information and demonstrating a commitment to pursuing justice, even when the suspects are beyond their immediate reach.

The case against Nasab is a stark reminder of the cybersecurity risks facing nations and the importance of international cooperation in combating cyber threats.

It also highlights the U.S. government’s determination to hold individuals accountable for cyber espionage, regardless of location or affiliations.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are incredibly harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter


[ad_2]
Source link