New ‘thinnest and lightest’ book-style foldable is coming

0

[ad_1]

A new “thinnest and lightest” book-style foldable is coming, based on a new report. This information comes from Digital Chat Station, a well-known tipster from China. He’s referring to the Vivo X Fold 3, by the way.

New ‘thinnest and lightest’ book-style foldable smartphone is on its way

He actually referred to it as the “thinnest and lightest large foldable” in general. In other words, it’s expected to outdo the HONOR V Purse as well. At the moment, HONOR has both the thinnest and lightest book-style foldable and large foldable in general.

The HONOR Magic V2 is 9.9mm thick and weighs 231 grams (its lightest variant). That is a book-style foldable. On the other hand, the HONOR V Purse is an outward-folding foldable, and it is 8.6mm thick, while it weighs 214 grams.

It’s possible that the tipster did not consider outwards-folding devices

It’s possible Digital Chat Station forgot about the HONOR V Purse when he shared his post. Expecting the Vivo X Fold 3 to be thinner and lighter than the HONOR V Purse, while retaining an inwards-folding design could be a stretch. We’ll see, though.

One thing is for sure, he does expect it to be both thinner and lighter than the HONOR Magic V2. That will be a feat on its own. Why? Well, the HONOR Magic V2 is already a stunningly thin and light phone, for a large foldable.

This is the very first book-style foldable that actually felt like a regular smartphone when folded. It had quite an impact on us when we tried it out at IFA 2023 for the first time. If Vivo manages to outdo that, that will be quite a feat.

The phone will include two 120Hz panels, and the Snapdragon 8 Gen 2 SoC… most likely

In terms of specs, the phone is expected to include an 8.03-inch main display and a 6.53-inch cover panel. Both of those will be LTPO AMOLED displays, and they’ll be very bright too. They will also offer up to 120Hz refresh rate.

Vivo is expected to include an in-display fingerprint scanner on both displays, while the device is said to include the Snapdragon 8 Gen 2. Its ‘Pro’ model will ship with the Snapdragon 8 Gen 3, it’s rumored.

80W wired charging is also tipped

A 5,600mAh or 5,700mAh battery is expected inside of the device, while the phone will likely support 80W wired charging. A 50-megapixel main camera is expected to be included, along with a 50-megapixel ultrawide unit, and a 50-megapixel telephoto camera (up to 40x digital zoom).

The Vivo X Fold 3 series is expected to arrive later this month. Let’s hope these devices will be the first foldable phones from Vivo to launch in markets outside of China.

[ad_2]

Source link

As expected, AI image generators can be used to make misleading political photos

0

[ad_1]

AI image generation has gotten extremely realistic… just in time for the US presidential election. This is one of the biggest concerns going into the voting season. A group of researchers has been testing some of the top image generators. They found that some of the top AI image generators can make misleading political images.

The Center for Countering Digital Hate conducted a study using image generators such as OpenAI’s ChatGPT Plus, Microsoft’s Image Creator, and MidJourney to test their capacity to generate false political content. The center fed the generators prompts that could possibly produce misleading content.

One of the most popular image generators could be used to make misleading political images

Companies like OpenAI, Microsoft, MidJourney, and Stability AI signed an agreement to work together to block misleading political content. Thus, we expect the companies to do a ton of work to block political prompts. This seems to be working out as far as OpenAI is concerned. The researchers found that ChatGPT and Microsoft Image Creator (both powered by OpenAI’s DALL-E) were successful at blocking political prompts. This looks good on the company. However,

While this is the case, the researchers found that 41% of the time, the image generators were more susceptible to generating images depicting voter fraud than generating images of Donald Trump or Joe Biden. This points to a major issue that needs to be addressed.

MidJourney might have an issue

During the testing, the researchers found that MidJourney was the most likely candidate to produce misleading images. The researchers found that MidJourney produced misleading political images 65% of the time. According to the report, some of the images produced are already available to the public. This means that there are already false images making it around the internet.

While this is the case, MidJourney responded to the report. It said in a statement “updates related specifically to the upcoming U.S. election are coming soon.” So, hopefully, we’ll see an improvement in this.

[ad_2]

Source link

Project DDoSia – Russian Hackers Planning Massive DDoS Attack

0

[ad_1]

Hackers launch large-scale DDoS attacks to disrupt and make online services inaccessible, driven by motives like revenge or protest, flooding targets with massive amounts of traffic to disable websites.

Recently, the cybersecurity researchers at Sekoia identified that the Russian hacker group “NoName057(16)” has been actively planning to conduct massive DDoS attacks.

Since the Ukraine conflict began, the nationalist hacktivist groups, notably the “NoName057(16),” have risen and are found to be launching Project DDoSia. 

They target pro-Ukraine entities, mostly NATO members.

Sekoia actively tracks its C2 infrastructure, which is automated for target collection and real-time monitoring.

Document

Integrate ANY.RUN in your company for Effective Malware Analysis

Malware analysis can be fast and simple. Just let us show you the way to:

  • Interact with malware safely
  • Set up virtual machine in Linux and all Windows OS versions
  • Work in a team
  • Get detailed reports with maximum data
  • If you want to test all these features now with completely free access to the sandbox: ..

Project DDoSia: Massive DDoS Attack

The Project DDoSia’s Telegram channel recently, on 11 November 2023, dropped a surprise update by expanding processor support to 32-bit and adding FreeBSD compatibility. 

While the prior versions had AMD64, ARM, and ARM64 covered. Main ZIP has two folders (d_eu, d_ru) for location-based execution.

Executing shows a warning, suggesting VPN for users in Russia.

Warning message (Source – Sekoia)

No VPN mandate in Russia hints at the NoName057(16) group’s possible ties with the state despite no public acknowledgment. 

The latest version alters encryption for user-C2 server data exchange. The operating diagram for DDoSia project initiation is provided as a reminder.

Attack Chain (Source – Sekoia)

The latest update adds encryption for data in HTTP POST requests which is a new feature absent in previous versions.

C value, a GUID identifying the user’s machine, is encrypted and extracted from \HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Cryptography\MachineGuid on Windows. 

The U value is from the client_id.txt file via DDoSia’s Telegram Bot. Besides this, the JSON table “inf” tracks seven elements under Windows, likely for statistical analysis, enhancing transmission sophistication.

The latest software version improved data transmission, but DDoSia admins changed the C2 servers frequently in 2024, facing stability challenges, read the Sekoia report.

NoName057(16) updated the Telegram channel with each server config change which requires users to download and install for continued attacks. 

Besides this, DDoSia lacks automated IP address change despite frequent C2 changes. Infrastructure interruptions didn’t hamper NoName057(16) group’s daily attacks.

DDoSia likely uses its servers to actively participate in attacks.

Top Countries Targeted

Here below we have mentioned all the top targeted countries:-

  • Ukraine
  • Finland
  • Italy
  • Spain
  • Germany
  • Lithuania
  • France
  • Poland
  • Switzerland
  • Romania
  • Netherlands
  • Estonia
  • Sweden
  • Latvia
  • Greece
  • United Kingdom
  • Czech Republic
  • Belgium

Top Sectors Targeted

Here below, we have mentioned all the sectors that are targeted most:-

  • Government
  • Banking
  • Transportation
  • Technology
  • Energy
  • Defence

The DDoSia’s Telegram project nears 20,000 users, while NoName057(16) channels surpass 60,000, doubling since 2023. 

The growth represents a politically and economically motivated community.

NoName057(16) collaborates with hacktivist groups, forming alliances against Italian infrastructures. 

Despite DDoSia’s ever-changing infrastructure, it consistently claims attacks.

Not only that even, it also provides daily software updates and a 2024 version with enhanced encryption.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are incredibly harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter


[ad_2]

Source link

Fake Skype, Zoom, Google Meet Sites Infecting Devices with Multiple RATs

0

[ad_1]

Android and Windows users, beware of fake online meeting sites such as Google Meet, Zoom, and Skype, infecting devices with malicious malware like SpyNote RAT for Android, NjRAT, and DCRat.

Fake Skype, Zoom, Google Meet Sites Infecting Devices with Multiple RATs

Zscaler’s ThreatLabz cybersecurity researchers have discovered a new scam where Remote Access Trojans (RATs) are distributed through online meeting platforms, targeting Android and Windows users with malware. The purpose is to distribute malware that can steal sensitive data and control infected devices.

Researchers discovered a threat actor creating fraudulent websites for spreading malware, including SpyNote RAT for Android and NjRAT and DCRat for Windows, in December 2023. These RATs can steal confidential information and log keystrokes. Users are lured through fake online meeting sites impersonating brands like Skype, Google Meet, and Zoom. 

The actor used shared web hosting, hosting all fake sites on a single IP address in Russian, and URLs that closely resembled the actual websites. The attackers distributed multiple malware families using these fake websites, posing a significant threat to innocent users.

To download the software, users must either click the Android or Windows buttons. When they click on Android, a malicious APK file gets downloaded, whereas clicking on the Windows button triggers the download of a BAT file, which automates tasks and performs additional actions, such as downloading a RAT payload.

A campaign imitating legitimate online meeting platforms is a significant threat, with fake sites mimicking their appearance and functionality. In December, as noted by Zscaler in a blog post, a fake Skype site, join-skypeinfo, was created to trick users into downloading the application, leading to a BAT file and a WinRAR archive file. 

The fake Google Meet site, online-cloudmeetingpro, was hosted on a subpath resembling a joining link. The fake Zoom sites have URLs with genuine Zoom meeting IDs that increase the risk of falling victim to the scam. 

These fake websites also contained an open directory with NjRAT executable files, suggesting the attacker may use them in other campaigns. 

Fake Skype, Zoom, Google Meet Sites Infecting Devices with Multiple RATs
Fake Skype, Zoom and Google Meets websites identified by researchers (Screenshot via Zscaler)

Such campaigns can have devastating consequences. RATs can compromise devices, allowing attackers to steal sensitive information, monitor user activity, and potentially control the infected device.

To protect yourself, double-check URLs, verify meeting invitations, download software from official sources, and use antivirus and anti-malware software. Beware of fake websites, verify meeting invitations, and download applications from official sources.

  1. Konni RAT Exploiting Word Docs to Steal Data from Windows
  2. Fake Chrome Browser Update Installs NetSupport Manager RAT
  3. Bifrost RAT Variant Targets Linux Devices, Mimics VMware Domain
  4. AsyncRAT Infiltrates Key US Infrastructure Through GIFs and SVGs
  5. Popular Android Screen Recorder iRecorder App Revealed as Trojan


[ad_2]

Source link

Samsung patent shows rollable smartphone with air quality sensor

0

[ad_1]

Samsung may be considering adding an innovative feature to its future rollable smartphones. A newly-published patent application from the company details a rollable smartphone with a built-in air quality sensor. It features a unique pipeline system for airflow and a sensor to measure air quality.

Samsung patents a rollable smartphone that can measure air quality

The concept of rollable smartphones has tantalized tech enthusiasts for years but the realization of this futuristic form factor remains elusive. Despite years of development, rollables are confined to prototypes and concept devices. A commercial product is nowhere in sight. There are rumors that Vivo and Transsion will collaborate to launch the world’s first commercial rollable smartphone later this year but these are just rumors.

Samsung has also long shown interest in rollable devices, even as it religiously pushes the foldable market forward. We have already seen a few concept designs and patents related to rollable smartphones from the Korean firm. The USPTO (United States Patent and Trademark Office) published the latest patent application on February 29, 2024. It is for an “electronic device including openable and closable pipeline”.

The patent documents and accompanying sketches describe a smartphone with a rollable display and a built-in air quality sensor. First reported by Pigtou, the futuristic Samsung device features two housings. One of them can slide over the other. The rollable panel also doubles up as controls for the opening and closing of the pipeline. This helps regulate the airflow to the sensor, giving you accurate air quality readings quickly.

Samsung has also implemented measures to prevent internal device components from contaminating the sensor. This ensures the reliability of the readings. The device can actively monitor the air quality of your surroundings and alert you to changes in air quality. The whole product has a space-efficient design, so the device doesn’t look bulky despite featuring a built-in air quality sensor.

This device may not see the light of day anytime soon

As said earlier, rollable smartphones aren’t commercially available yet. They only exist in prototypes and concepts. Samsung has patented many rollable designs but there is no such product in its pipeline, at least not just yet. This unique rollable device with a built-in air quality sensor may also be just an idea that the company wants to protect. It may or may not turn the concept into a real product. Even if it does, certainly not anytime soon. It may be one for the future.

Samsung rollable smartphone patent air quality sensor

[ad_2]

Source link

Trust in AI companies is on the decline

0

[ad_1]

When all AI companies talk about their products, they typically talk about how their the most secure AI products on the face of the planet. However, this isn’t doing much to sway concerned users. According to a new report, it appears that trust in AI is on the decline across most of the world.

AI models need to be trained on data from across the internet and our conversations. So, trust is one of the most important topics in AI technology. People have to trust that AI companies are going to follow through on their word and create AI technology that’s actually safe.

Trust in AI companies is on the decline according to a new report

Globally, trust in AI companies has changed over the past five years. Many markets around the world trust them much less than back in 2019. According to a report about 53% of surveyed users actually trust AI companies globally. However, that number is substantially lower than five years ago. Back then, about 61% of users trusted AI companies. In the US, the number dropped from 50% five years ago to just 35%. That’s a pretty significant drop.

Five years ago, generative AI wasn’t really a thing for the public. So, we can bet that the advent of this technology caused a sharp downturn. Aside from the fact that it lets users generate content, the fact that regulation is sparse is another factor. People are calling for more governmental regulation of AI. “When it comes to AI regulation, the public’s response is pretty clear: ‘What regulation?’,” said Edelman global technology chair Justin Westcott.

Right now, there aren’t any real laws or regulations surrounding AI technology, so it’s understandable that people are losing faith in the technology. The research data reveals that most developed companies are less likely to embrace AI technology. This list includes countries like France, Australia, the US, the UK, The Netherlands, Sweden, Ireland, and Canada.

However, it appears that it’s the opposite for countries like Saudi Arabia, India, China, Kenya, Nigeria and Thailand. These countries are more likely to embrace AI technology.

Be that as it may, the trends show that fewer people are willing to embrace and trust AI technology. We’ll have to see if this changes as more industries embrace the technology.

[ad_2]

Source link

Hackers Install macOS Malware Via Weaponised Calendar Invites

0

[ad_1]

Hackers use weaponized calendar invites to exploit vulnerabilities in email systems, tricking users into clicking on malicious links or downloading malware disguised as event attachments. 

By leveraging trust in calendar invitations, threat actors increase the likelihood of successful phishing attacks and unauthorized access to sensitive information.

Cybersecurity researchers at Malwarebytes recently discovered that hackers are actively exploiting the weaponized calendar invites to install macOS malware.

macOS Malware Calendar Invites

Mac users seeking cryptocurrency opportunities are targeted by cybercriminals using fake calendar invites.

Document

Integrate ANY.RUN in your company for Effective Malware Analysis

Malware analysis can be fast and simple. Just let us show you the way to:

  • Interact with malware safely
  • Set up virtual machine in Linux and all Windows OS versions
  • Work in a team
  • Get detailed reports with maximum data
  • If you want to test all these features now with completely free access to the sandbox: ..

Links sent during attacks install malware on the target’s machine. 

Brian Krebs flagged the issue, and asserted that scammers pose as cryptocurrency investors, and lure people into fake partnership meetings on Telegram.

Luring message (Source – MalwareBytes)

Signum Capital issued a warning about impersonation attempts on Twitter in January.

Threat actors contact the targets via Telegram DMs in which they lure their targets by offering opportunities for calls or meetings.

Interested targets receive fake meeting invitations. 

When victims attempt to join, the link fails. Scammers blame regional access restrictions and advise running a script to fix it. 

Malwarebytes’ Thomas Reed confirmed threat actors’ use of scripts to compromise users isn’t new.

AppleScripts come in .scpt files, but victims need to open in Script Editor and may spot the code.

AppleScript applets act like normal apps, enhancing trustworthiness with code signing and icons. 

Script Editor (Source – MalwareBytes)

Due to this obfuscating the code is possible which makes it less likely for Apple’s notarization process to detect potential threats.

When a user enters their password, the script doesn’t see it but gains root access. Actions run with administrator privileges without additional authentication. 

The script can easily trick users into granting root permissions through a standard authentication request dialog.

AppleScript excels at malware crafting. Certain malicious programs like OSX.DubRobber, OSX.OSAMiner utilized AppleScript solely or near-solely.

A basic Apple Script, in this case, downloaded and ran a macOS Trojan whose purpose is unknown.

If it’s revealed as a cryptocurrency-stealing banking Trojan, then it wouldn’t be surprising.

How To Recognize The Scam?

Here below we have mentioned all the key tactics used by the threat actors, and these tactics will help in recognizing the scam:-

  • DM approach on Telegram
  • Crypto investment lure
  • Calendly platform preferred
  • Fake “regional restriction” urgency
  • Script with .scpt extension
  • Hosted on a fake meeting support site

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are incredibly harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter


[ad_2]

Source link

ALPHV ransomware gang fakes own death, fools no one

0

[ad_1]

For the second time in only four months, all is not well on the ALPHV (aka BlackCat) ransomware gang’s dark web site. Gone are the lists of compromised victims. In their place, a veritable garden of law enforcement badges has sprouted beneath the ominous message “THIS WEBSITE HAS BEEN SEIZED.”

The ALPHV ransomware dark web site has a new look

So far, so FBI, but all is not what it seems.

ALPHV is arguably the second most dangerous ransomware group in the world. It sells Ransomware-as-a-Service (RaaS) to criminal affiliates who pay for its ransomware with a share of the ransoms they extract.

When a task force of international law enforcement agencies score a hit on a target this big, they tend to make a bit of a song and dance about it. At a minimum, there are announcements. Last time the FBI disrupted ALPHV with an unscheduled home page redecoration in December, the law enforcement agency was very happy to tell everyone.

When the UK’s National Crime Agency (NCA) took a slice out of the LockBit gang last month it didn’t just tell everyone in a press release, it celebrated with a week-long fiesta of premium-grade trolling on LockBit’s own website.

They have every reason to celebrate their success, but this takedown—if that’s what it really is—has been greeted with nothing but silence from law enforcement.

In fact, ransomware experts have weighed in with an alternative explanation: ALPHV has recycled the takedown banner provided by law enforcement in December, and staged a fake takedown to cover its tracks while it runs off with its affiliates’ money.

The story starts on February 21, 2024, when an ALPHV affiliate attacked Change Healthcare, one of the largest healthcare technology companies in the USA. The attack has caused enormous disruption and been described by the American Hospital Association (AHA) President and CEO Rick Pollack as “the most significant and consequential incident of its kind against the US health care system in history.”

On March 3, a user on the RAMP dark web forum claimed they were the affiliate behind the Change Healthcare attack. They alleged that two days earlier Change Healthcare had paid ALPHV $22 million—backing up their claim with a link to a Bitcoin wallet that shows a 350 bitcoin transfer on March 1—and that ALPHV then suspended their account.

VX Underground reported that a day later, other ALPHV affiliates were also locked out of their accounts, while ALPHV issued an “ambiguous” message seemingly pointing the finger at the FBI for…something, before putting the source code to its ransomware up for sale for $5 million.

The final act in this entirely unconvincing drama was the appearance of a “THIS WEBSITE HAS BEEN SEIZED” banner on the ALPHV dark web site. Not only was the banner identical to the one used by law enforcement in December, it appeared to have been lazily copied from the compromised site.

The giveaway, spotted by ransomware researcher Fabian Wosar, was the URL of the takedown image, which was being kept in a directory called THIS WEBSITE HAS BEEN SEIZED_files.

“An image URL like this is what Firefox and the Tor Browser create when you use the ‘Save page as’ function to save a copy of a website to disk,” he pointed out.

Of course, it’s not impossible that law enforcement would do this, but it’s a far cry from the no-stone-left-unturned effort of the recent LockBit takedown. Unconvinced, Wosar took to X (formerly Twitter) to say he’d reached out to contacts at Europol and the NCA, and they declined “any sort of involvement”.

It’s the second reminder in under a month, following revelations that the LockBit gang didn’t delete its victims’ stolen data when they were paid a ransom, that you just can’t trust criminals.

How to avoid ransomware

  • Block common forms of entry. Create a plan for patching vulnerabilities in internet-facing systems quickly; and disable or harden remote access like RDP and VPNs.
  • Prevent intrusions. Stop threats early before they can even infiltrate or infect your endpoints. Use endpoint security software that can prevent exploits and malware used to deliver ransomware.
  • Detect intrusions. Make it harder for intruders to operate inside your organization by segmenting networks and assigning access rights prudently. Use EDR or MDR to detect unusual activity before an attack occurs.
  • Stop malicious encryption. Deploy Endpoint Detection and Response software like ThreatDown EDR that uses multiple different detection techniques to identify ransomware, and ransomware rollback to restore damaged system files.
  • Create offsite, offline backups. Keep backups offsite and offline, beyond the reach of attackers. Test them regularly to make sure you can restore essential business functions swiftly.
  • Don’t get attacked twice. Once you’ve isolated the outbreak and stopped the first attack, you must remove every trace of the attackers, their malware, their tools, and their methods of entry, to avoid being attacked again.

Our business solutions remove all remnants of ransomware and prevent you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.


[ad_2]

Source link

New leak reveals more renders and specs of Galaxy A55, A35

0

[ad_1]

Yesterday, Samsung officially announced the launch date for the Galaxy A55 and Galaxy A35. The duo will debut on Monday, March 11. Leaks have already revealed plenty about the phones, including their specs, design, and alleged European pricing. Someone even posted a detailed review video of the former, going in-depth into its performance. The upcoming phones have just surfaced in another leak.

Samsung’s Galaxy A55 and A35 leaked again

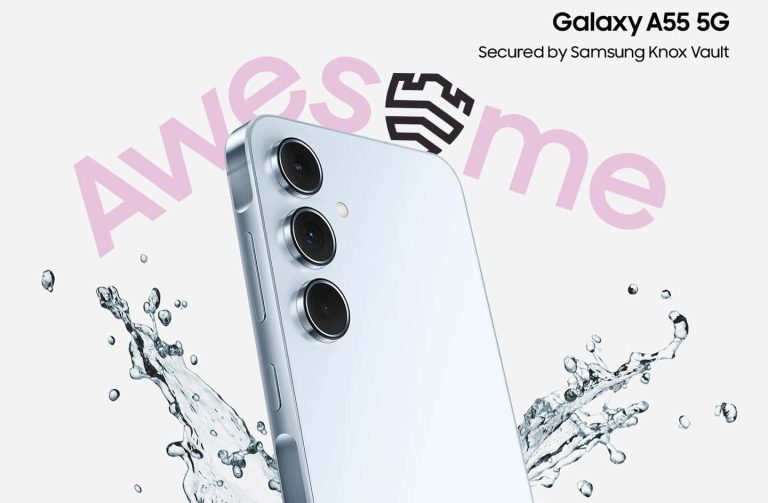
The latest leak of the Galaxy A55 and Galaxy A35 comes courtesy of the ever-reliable tipster Evan Blass, aka evleaks. He shared a bunch of official-looking renders and images from marketing materials or online product listings on X. The images reveal Samsung Knox Vault support for both models. The company has already confirmed that the devices will boast Knox Security, so that was expected.

As leaked before, both devices will be available in four colors: Awesome Ice Blue, Awesome Lemon, Awesome Lilac, and Awesome Navy. The Galaxy A55 and Galaxy A35 also sport an identical design, including a flat back with a vertical camera array, a punch-hole display, and a flat frame with the Key Island design. However, the former has a metallic frame while the latter’s frame is made of plastic.

The images shared by Blass also confirm a 5,000mAh battery. Both devices are expected to boast 25W fast wired charging. Additionally, we can see a 50MP primary rear camera and a 5MP macro camera for the duo. The Galaxy A55 pairs those with a 12MP ultrawide lens and a 32MP selfie shooter. The latter two cameras have an 8MP and 13MP resolution, respectively, on the Galaxy A35.

The upcoming mid-range duo will boast an official IP rating for dust and water resistance (likely IP67). Samsung has also confirmed that the Galaxy A55 and Galaxy A35 will get four years of Android OS updates with five years of security updates. The devices will run Android 14-based One UI 6.1 out of the box, so they will get updates up to Android 18. Security patches will come at least until March 2029.

Samsung mid-rangers are getting more powerful

The prematurely posted review of the Galaxy A55 revealed that the new phone will be substantially more powerful than its predecessor, the Galaxy A54. It is said to bring over 20% boost in CPU performance, over 30% boost in GPU performance, and a whopping 167% boost in NPU performance. The device also handles thermals better and is available in a 12GB RAM variant. Stay tuned for the official launch next week.


[ad_2]

Source link

How to Watch President Biden’s Address

0

[ad_1]

President Joe Biden is set to give his annual State of the Union address on Thursday, March 7, 2024

As it seems to happen every year, this State of the Union address is being delivered at a pretty critical time for President Biden. This year, it’s due to it being an election year. Following the Super Tuesday victories by former president Trump, it’s likely going to be Trump versus Biden in November. And this is going to be a prime opportunity for Biden to talk about his plans for the rest of 2024, and moving forward.

How do I watch Biden’s Joint Address to Congress?

President Biden’s first State of the Union will be broadcast virtually everywhere.

All of the major news networks will be airing it. That includes CNN, FOX, NBC, ABC, PBS and C-SPAN. The White House is also going to be streaming the event on its YouTube, Facebook, and Twitter/X pages. As usual, the Twitter stream will show on-screen commentary from Administration officials and cabinet members. So, Twitter/X users are able to stay in the conversation about what’s happening.

YouTube will also air the speech from all of the major news networks, in addition to The White House. So if you have a news network that you prefer to watch, you can still do that on YouTube. Or you can stay neutral with The White House or C-SPAN, which won’t provide any analysis of the address and just show the address itself. While Fox News is typically republican leaning, and CNN or MSNBC is Democrat leaning.

When does it start?

The State of the Union will begin at 9 PM ET. Of course, many news networks will start their coverage earlier, talking about what they expect to hear from Biden in tonight’s speech and such.

As usual, the speech is expected to last about 60 to 90 minutes. So expect it to end around 10:30 PM ET. Following the speech, all of the talking heads from the news channels will be giving their analysis. That includes ABC, CBS, CNN, NBC and many others.

Biden’s previous State of the Union and Joint Address to Congress were over an hour long. With a time of one hour and five minutes in 2021 (this was a Joint Address due to him having just taken office in January 2021). Around an hour and one minute in 2022 and one hour and 13 minutes in 2023. So we’d expect this to be over an hour but less than 90 minutes.

What will Biden talk about?

This is Biden’s third State of the Union, and depending on the outcome of the November election, it could be his last. It’s not often that a President gets the undivided attention of the Cabinet, Senate, US House of Representatives and the Supreme Court, all in the same room. So there’s lots of topics that will be covered.

Of course, a big one is going to be Biden’s age, as he goes into this Election year. Obviously, no president gets a free pass, but with Biden being 81 years old, he’s getting a lot more attention about his age than before. A big part of this is because he’s the oldest person to ever be president. However, his opponent – Donald Trump – is not much younger, currently at 77 years of age.

On the policy side of things, Biden will undoubtedly talk about new policy proposals. The State of the Union is typically where presidents get a chance to lay out their goals and rally Americans to support these plans. So far, The White House has not disclosed what Biden will specifically talk about, but we can expect him to reference unfinished business from his first term. Biden will also likely press for military assistance for Ukraine to reinforce American leadership overseas.

One of the big topics this year, going into the Election, is about the right to have an abortion. Under President Trump, the Supreme Court was able to roll back Roe v Wade, basically making it up to the States. This has caused a lot of issues for women who need to get an abortion due to health issues. Of course, the most high-profile case recently was Kate Cox who lives in Texas but was not able to get an abortion in her home state even though her health was in danger, and her fetus had a fatal condition. Obviously, Democrats are eager to demonstrate how the US Supreme Court’s decision to overturn Roe v Wade has limited reproduction rights. It’s also a topic that Democrats ran on in the mid-terms, and we’d expect the same for 2024.

Who’s delivering the republican response?

This year, it’ll be Senator Katie Britt of Alabama who will deliver the Republican Response to Biden’s speech. Senator Britt is 41 years of age, and has become the youngest female senator and many in the part believes she could be a rising star.

It’s likely that Britt will mention Trump in her speech and put him over as the party’s contender for the presidency this year. It’s also likely that Trump will provide a response to Biden’s speech over on Truth Social after the State of the Union is over.

Who will be attending?

The US Senate, the US House of Representatives, the Supreme Court Justices, and the President’s Cabinet are all in attendance. The First Lady typically has a box in the upper area of the room with many guests that the President will mention throughout his speech. This year, guests for the State of the Union include Kate Cox, a Texas woman who was unable to get an abortion in her home state even though her health was in danger and her fetus had a fatal condition.

Every year, there is also a designated survivor who will not be at the Capitol but instead in a bunker watching the speech with the Secret Service. We don’t yet know who the designated survivor is this year, which is usually disclosed right before the speech begins. However, last year it was Labor Secretary Marty Walsh.

The naming of a Designated Survivor began in the 1960s, to coincide with the Cold War era, because of the threat of nuclear attacks. However, the identity of the designated survivor was not regularly made public until the 1980s.

The purpose of the Designated Survivor is in case there is a mass casualty or an attack on the Capitol during the speech. We’ve seen how this plays out in the ABC show Designated Survivor. Typically, a member of the cabinet is chosen every year, while the other party will choose someone from Congress to be their designated survivor. So that the government can continue in the aftermath.
[ad_2]

Source link