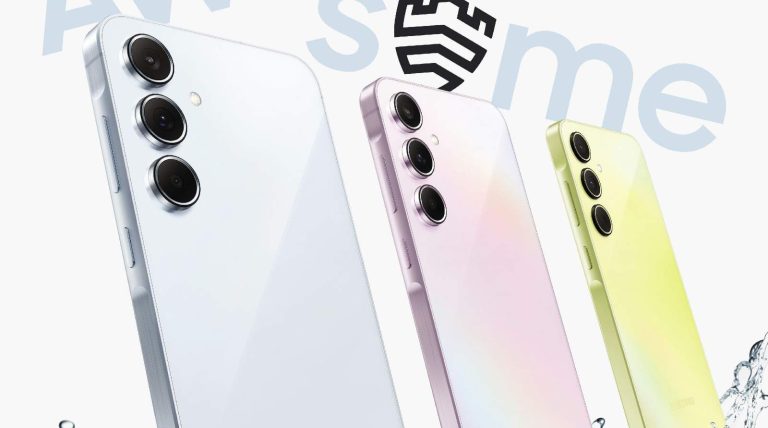
Earlier today, Samsung announced that the Gaalxy A55 and Galaxy A35 will debut on March 11. While the official launch is still a few days away, two European retailers have jumped the gun. French telecom company Orange and Polish electronics retailer RTV Euro AGD listed the upcoming devices on their websites with detailed specs.
European retailers have prematurely listed the Galaxy A55 & A35
After a series of leaks, Samsung today confirmed that the Gaalxy A55 and Galaxy A35 will go official on Monday, March 11. The launch event will take place in India. The company didn’t reveal the release date for the phones. It usually opens sales in most global markets about a week after the launch. The US release comes a week or two after that.
While we wait for the official unveiling next Monday, some European retailers can’t seem to wait. Orange and RTV Euro AGD have already published product pages for the Galaxy A55 and Galaxy A35 on their official websites. The listings don’t have a release date or price details but contain detailed specs of the duo. Orange has even named the unannounced Exynos 1480 processor powering the A55.
If these listings are accurate, the Galaxy A55 won’t bring a camera upgrade over the Galaxy A54 but will feature a larger display. It is said to come with a 6.6-inch Super AMOLED panel with a 1080×2340 pixels resolution. Earlier leaks said the screen will boast a 120Hz refresh rate and 1,000 nits of peak brightness. The device measures 161.1 x 77.4 x 8.2mm in dimension and is expected to feature a metallic frame.
The Exynos 1480 chipset will be paired with at least 6GB of RAM, with leaks hinting at 8GB and 12GB RAM variants as well. Storage options may include 128GB and 256GB, though we wouldn’t rule out the possibility of a 512GB model. The Galaxy A55 will pack a 5,000mAh battery, likely with 25W fast wired charging. You also get IP67 dust and water resistance and an under-display fingerprint scanner.
Galaxy A35 gets a camera upgrade
These leaks from European retailers confirm a camera upgrade for the Galaxy A35. It features a 50MP primary shooter (Galaxy A34 has a 48MP main camera). Samsung has equipped the device with the Galaxy A54’s Exynos 1380 processor. The rest of the setup is largely unchanged, including the build quality. Unlike the Galaxy A55, it doesn’t have a metallic frame. Stay tuned for the official launch next Monday.
Huawei has previously sued Amazon in Germany over WiFi patent infringement. But Alan Fan, Head of Huawei’s Intellectual Property Rights Department, confirmed that the recent partnership resolved the pending lawsuit.
Amazon & Huawei sign patent licensing deal
“Patent licensing expands the number of companies that can use what otherwise would be proprietary technologies, which, in turn, provides consumers with more innovative products and services.” Fan added.
Huawei’s official also stated the patent deal with Amazon shows American and Chinese companies are collaborating “without limitations in standards and patent licensing.”
Scott Hayden, Vice President of IP for Amazon, also noted the retailer “respects Huawei’s efforts to license its patents to companies like Amazon, which frequently use industry technical standards when inventing new products and services for customers.”
Huawei is yet to disclose the details of its agreement with Amazon. The US government is also expected to react to the deal and request an explanation from Amazon. The giant retailer might have to back off the deal if the corporation violates US trade restrictions against Chinese companies.
Huawei’s patent portfolio is wildly growing
Simultaneously, Huawei announced a cross-licensing patent deal with Vivo, another Chinese OEM. The agreement provides Vivo with communication technologies to deploy 5G connectivity. Huawei has similar patent deals with Xiaomi and Oppo.
When it comes to 5G patents, Huawei holds the rights to some of the most advanced technologies. The firm’s patent portfolio became even richer in 2021 after acquiring over 90 patents from Blackberry.
A new study dubbed ComPromptMized, warns of zero-click worms exploiting generative AI, spreading through systems sans user interaction, and posing data theft risks. Experts stress urgent AI security measures.
Researchers have recently unveiled findings indicating the creation of a computer worm capable of targeting generative AI-powered applications. This revelation comes amidst growing concerns over the security of artificial intelligence systems.
In a collaborative effort led by Stav Cohen from Technion – Israel Institute of Technology, Ron Bitton from Intuit, and Ben Nassi from Cornell Tech, the team developed and tested this novel worm against popular AI models, including Gemini Pro (previously Bard AI), ChatGPT, and LLaVA.
While the study highlights the potential malicious applications of such technology, it also echoes a warning issued last year by Europol regarding prompt engineering and jailbreaking of AI chatbots.
The research suggests that attackers could exploit this worm to manipulate AI models into replicating malicious inputs and engaging in harmful activities. One alarming demonstration involved the worm attacking generative AI email assistants, effectively stealing email data and distributing spam.
The mechanism behind the worm’s operation is intriguing yet concerning. By introducing specific text into an email, attackers could “poison” the databases of certain email application clients. This manipulation could then prompt models like ChatGPT and Gemini to replicate the malicious input and extract sensitive user data from the context.
In their study dubbed ComPromptMized, the researchers explored various scenarios, including both black-box and white-box accesses, and tested the worm’s effectiveness against different types of input data, such as text and images. The findings underscore the potential threats posed by such attacks on the burgeoning GenAI ecosystems.
The implications of this research extend beyond theoretical concerns. As more companies integrate generative AI capabilities into their applications, the risk of exploitation becomes increasingly tangible. The ability of malicious actors to leverage AI technology for nefarious purposes underscores the urgent need for robust security measures in AI development and deployment.
Beth Linker, Senior Director of AI & SAST at the Synopsys Software Integrity Group, emphasized the significance of this research, stating, “This attack highlights the vulnerability of GenAI-powered proactive agents as a potential target for exploitation. With the proliferation of new AI-driven tools promising to streamline our digital interactions, it is crucial for organizations to carefully consider the permissions granted to these tools and implement robust safety measures.”
While the research provides valuable insights into the vulnerabilities of generative AI systems, it also serves as a call to action for stakeholders across various industries. As we continue to embrace the benefits of AI innovation, it is imperative to remain alert against emerging threats and prioritize the development of strong security protocols.
We’re going to let you in on a little cybersecurity secret… There’s malware on Mac computers. There pretty much always has been.
As revealed in our 2024 ThreatDown State of Malware report, a full 11% of all detections recorded by Malwarebytes on Mac computers in 2023 were for different variants of malware—the catch-all term that cybersecurity researchers use to refer to ransomware, trojans, info stealers, worms, viruses, and more.
That 11% figure may not sound imposing but remember that many people today still believe that Apple devices, including Mac computers, are invulnerable to cyberinfections because of some sort of vague “Apple magic.”
In reality, “Apple magic” is more a byproduct of old advertising (this 2006 commercial from the “I’m a Mac, and I’m a PC” series did irreparable harm) and faulty conclusions concerning cybersecurity’s biggest breaches and attacks: People mistakenly believe that because most attacks target Windows computers and servers, no attacks target Macs.
The truth is far more nuanced, as the visible, overwhelming focus of cyberattacks on Windows machines is a consequence of Microsoft’s long-standing success in business computing.
For decades, every multinational corporation, every local travel agency, every dentist, every hospital, every school, government, and city hall practically ran on Windows. This mass adoption was good for Microsoft and its revenue, but it also drew and maintained the interests of cybercriminals, who would develop malware that could impact the highest number of victims. This is why the biggest attacks, even today, predominantly target Windows-based malware and the sometimes-unpatched vulnerabilities found in Windows software and applications.
Essentially, as Windows is the biggest target, cybercriminals zero in their efforts respectively.
But new information last year revealed that could all be changing.
Mac malware tactics shifted in 2023
Apple’s desktop and laptop operating system, macOS, represents a 31% share of US desktop operating systems, and roughly 25% of all businesses reportedly utilize Mac devices somewhere in their networks.
While the LockBit variant for Mac was not operational upon discovery, the LockBit ransomware gang said at the time that it was “actively being developed.” Fortunately, LockBit suffered enormous blows this year, and the ransomware gang is probably less concerned with Mac malware development and more concerned with “avoiding prison.”
Separately, in September 2023, Malwarebytes discovered a cybercriminal campaign that tricked Mac users into accidentally installing a type of malware that can steal passwords, browser data, cookies, files, and cryptocurrency. The malware, called Atomic Stealer (or AMOS for short) was delivered through “malvertising,” a malware delivery tactic that abuses Google ads to send everyday users to malicious websites that—though they may appear legitimate—fool people into downloading malware.
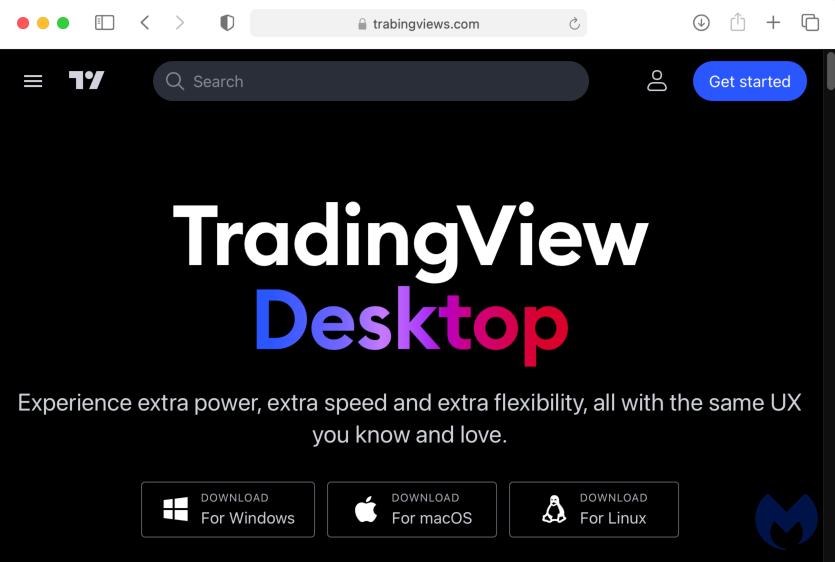
In this campaign, when users searched on Google for the financial marketing trading app “TradingView,” they were sometimes shown a malicious search result that appeared entirely authentic: a website with TradingView branding was visible, and download buttons for Windows, Mac, and Linux were clearly listed.
But users who clicked the Mac download button instead received AMOS.
This malvertising site mimics TradingView to fool users into downloading malware for different operating systems.
Just months later, AMOS again wriggled its way onto Mac computers, this time through a new delivery chain that has more typically targeted Windows users.
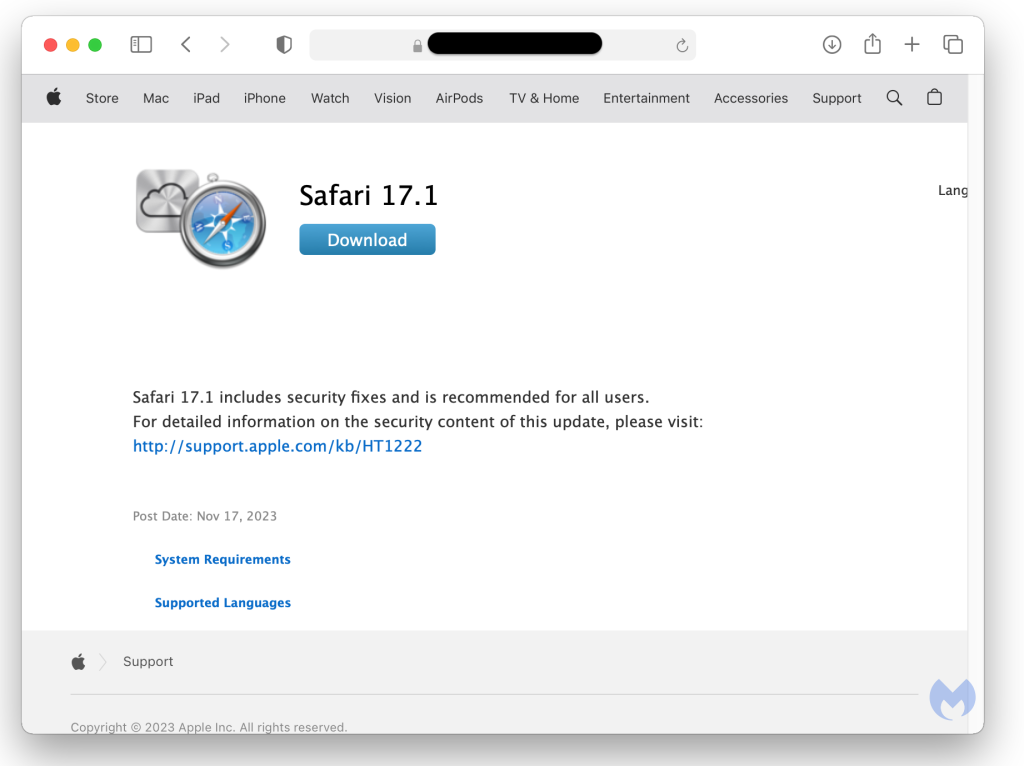
In November, Malwarebytes found AMOS being distributed through a malware delivery chain known as “ClearFake.” The ClearFake campaign tricks users into believing they’re downloading an approved web browser update. That has frequently meant a lot of malicious prompts mimicking Google Chrome’s branding and update language, but the more recent campaign imitated the default browser on Mac devices—Safari.
A template is used that mimics the official Apple websites and webpages to convince users into downloading a Safari “update” that instead contains malware.
“This may very well be the first time we see one of the main social engineering campaigns, previously reserved for Windows, branch out not only in terms of geolocation but also operating system.”
Replace “magic” with Malwarebytes
Cyberthreats on Mac aren’t non-existent, they’re just different. But different threats still need effective protection, which is where Malwarebytes Premium can help.
Malwarebytes Premium detects and blocks the most common infostealers that target Macs—including AMOS—along with annoying browser hijackers and adware threats such as Genieo, Vsearch, Crossrider, and more. Stay protected, proactively, with Malwarebytes Premium for Mac.
We don’t just report on threats—we remove them
Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.
The OnePlus 13 & Xiaomi 15 series are said to use ultrasonic in-display fingerprint scanners
Both companies have been using in-display fingerprint scanners for a while. The thing is, both have been relying on optical in-display fingerprint scanners. That will change with the next generation of flagship phones, though, it seems.
Ultrasonic in-display fingerprint scanners are more advanced and more secure at the same time. There are a number of advantages, so it’s great to see that both companies are planning to take a step forward.
They’re not only more secure but can be activated while the display is off by simply playing your finger around the area where the scanner is placed. You don’t need to previously tap the display. They’re usually also more accurate, and so on.
Do note that both companies are allegedly testing such fingerprint scanners for the aforementioned devices. Still, nothing guarantees that they’ll actually be used. So we’ll have to wait in order to be sure.
The Xiaomi 15 will keep a flat display, while the ‘Ultra’ will utilize a curved one
One of the tipsters also mentioned that the Xiaomi 15 will keep a flat display. The Xiaomi 15 Ultra will go for a curved display just like its predecessor, it is said. That’s not surprising at all, Xiaomi is sticking with its practice.
Lawsuits against Elon Musk’s X are coming from left and right. In one of the recent cases, the company’s former executives have filed a lawsuit, demanding roughly $128 million in severance payments. These executives were laid off after Musk took over the Twitter platform (later rebranded to X) in 2022.
Following Musk’s takeover, he drastically changed Twitter by firing the company’s top executives, including former CEO Parag Agrawal, CFO Ned Segal, chief legal officer Vijaya Gadde, and general counsel Sean Edgett. The lawsuit claims that Musk had a “special ire” against these executives because of their role in the billionaire’s legal battle with Twitter when he wanted to cancel the deal.
X should pay roughly $128 million in severance payments to its former executives
As the lawsuit reads, these executives have not yet received their severance payment from their former company. The total payment is around $128 million. Parag Agrawal demands $57.4 million in severance payments, while Segal’s payments are $44.5 million.
Gadde and Edgett are also entitled to $20 million and $6.8 million in severance benefits, respectively. Agrawal, Segal, and Gadde have also filed a separate lawsuit against Musk over some unpaid legal bills.
Plaintiffs also accuse Elon Musk of making up a “fake cause” to lay them off and avoid paying severance payments. Additionally, Twitter’s former executives cited a story from Musk’s biographer, Walter Isaacson. He revealed in his book that Musk was in a rush to close Twitter’s deal a day early.
This was supposedly because the billionaire aimed to fire those executives “for cause” before they could use their stock options to stay longer at the company. As Isaacson says, this tactic saved Musk around $200 million.
X’s unpaid severance benefits could exceed $628 million
“Musk doesn’t pay his bills, believes the rules don’t apply to him, and uses his wealth and power to run roughshod over anyone who disagrees with him,” the lawsuit notes. “Because Musk decided he didn’t want to pay Plaintiffs’ severance benefits, he simply fired them without reason, then made up fake cause and appointed employees of his various companies to uphold his decision.”
X is also facing another lawsuit from its former employees over unpaid severance. This lawsuit is said to be up to $500 million.
Have you ever wished you could take a message back or noticed a typo right after hitting send? Fortunately, many popular messaging apps like WhatsApp and Telegram already offer the option to edit your messages after sending them. Now, Instagram is finally jumping on board with this feature.
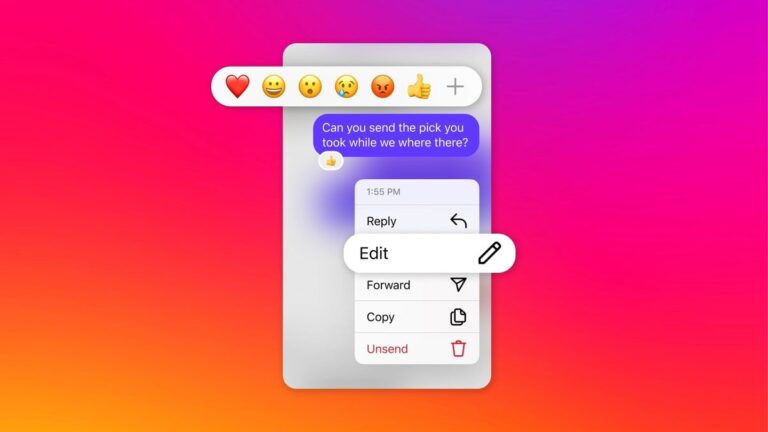
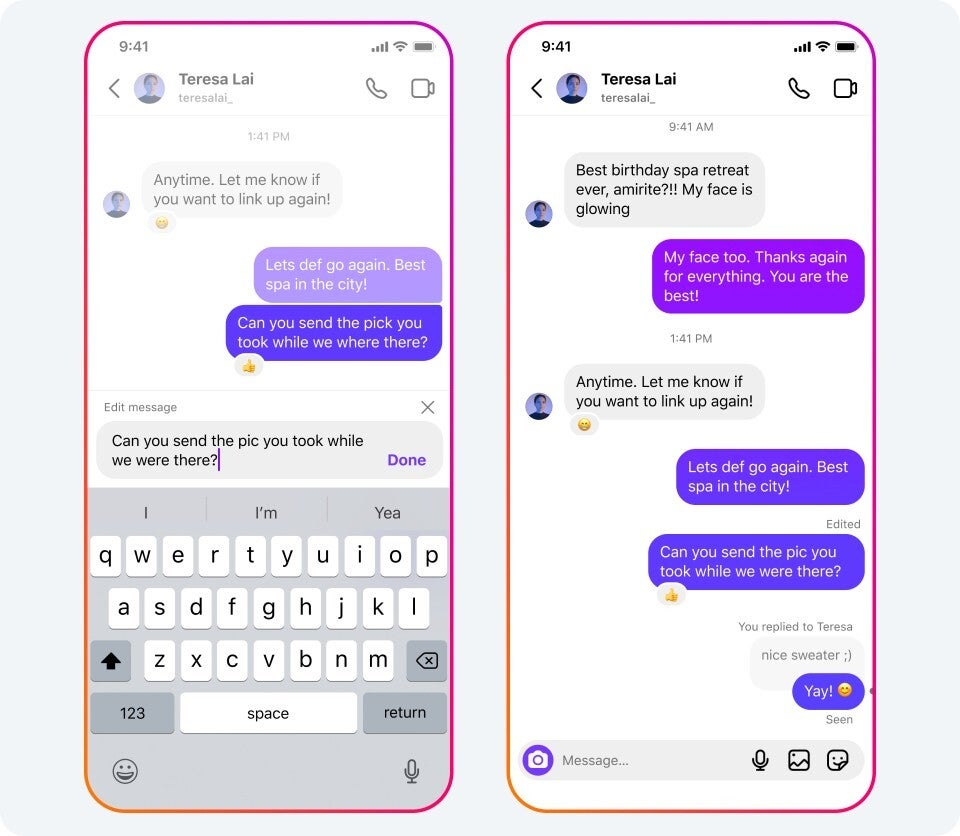
Meta has recently released a software update for the Instagram app, bringing the long-awaited feature of editing direct messages (DMs). However, there’s a catch: you only have a 15-minute window to make any changes. To edit a message, simply press and hold on the sent message, then select “edit” from the dropdown menu.
The new Edit feature in action (Image Credit–Meta)
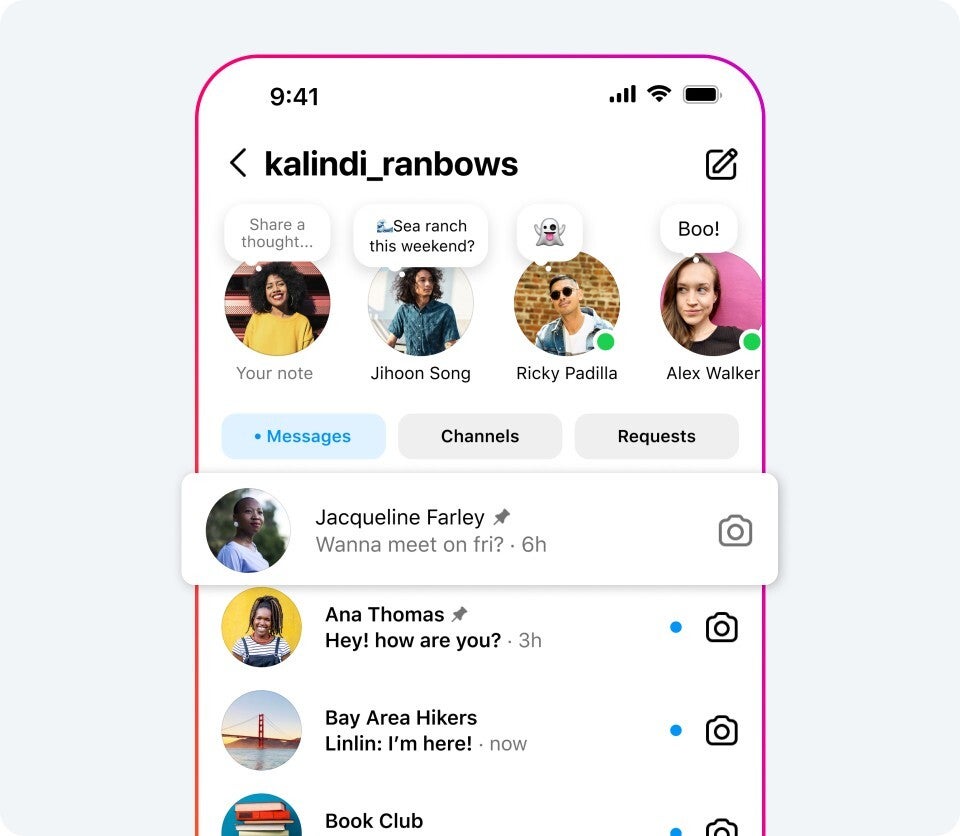
Alongside the editing feature, the recent update also introduces the option to pin up to three of your favorite direct messages at the top of your feed. This is particularly handy for ongoing conversations. To pin a conversation, hold down the conversation tab, locate the dropdown menu, and tap “pin” to prioritize it.
Pin chats at the top of your feed (Image Credit–Meta)
In addition to these changes, the update brings an easier way to manage read receipts. You can now toggle read receipts on or off for all your chats or choose specific ones according to your preference. This gives you greater control over whether others are notified when you’ve read their messages.
To turn it on or off for all chats:
Go to account settings
Tap Messages and story replies
Tap Show read receipts
Toggle read receipts on or off for all of your chats.
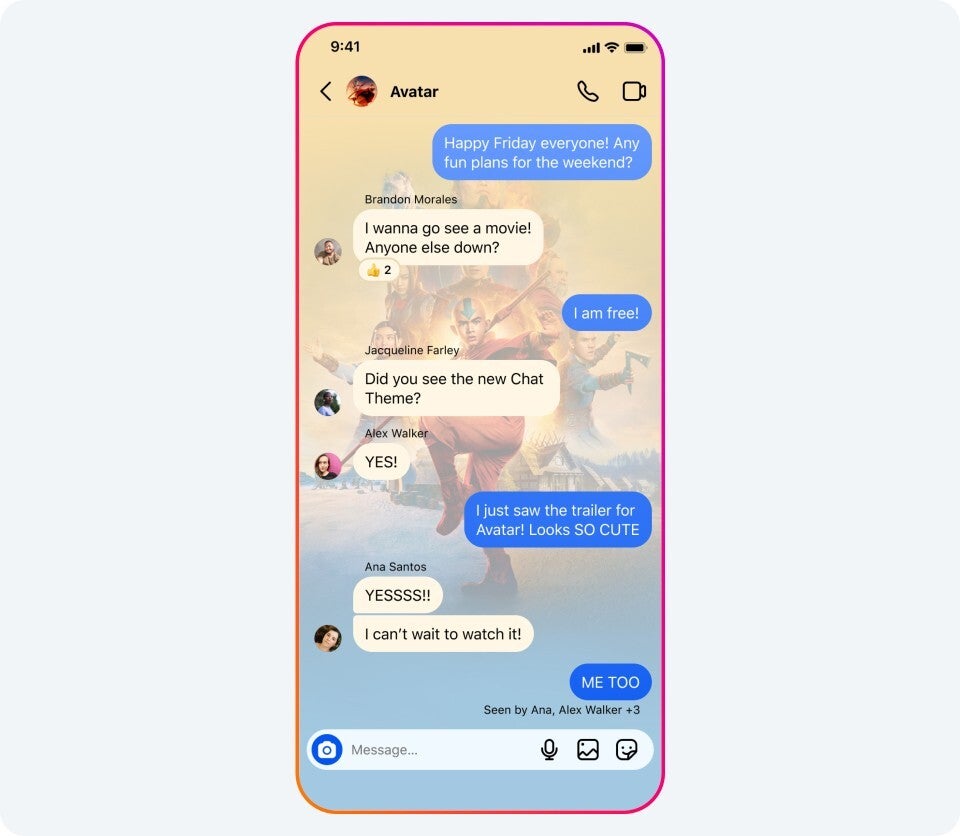
The update also adds some changes to chat themes. There are new DM themes, including trending ones tied to Dune: Part Two or Avatar: The Last Airbender. To switch the theme for a chat, tap the chat name at the top, go into themes, and choose one. Alternatively, you can just press and hold anywhere on the background of an open chat.
Avatar: The Last Airbender theme (Image Credit–Meta)
The update also lets you save your favorite stickers in your DMs for quick access. Just press and hold the sticker you want to save and you’ll find it at the top next time you go to stickers.
28 OPPO devices are getting Android 14 this month, globally, and the rollout started
Do note that the rollout is staged, so you may not get it straight away. Still, Android 14 is coming, alongside ColorOS 14. Some of the company’s higher-end phones are on this list, but there are a ton of cheaper devices too.
When it comes to the newest devices, the OPPO Find N3 and OPPO Find N3 Flip are listed first. We’ve already received an update for the OPPO Find N3 yesterday, so it’s definitely rolling out to global units.
In addition to those two phones, the OPPO Find N2 Flip is also getting it, and the Find X5 Pro and Find X5 too. Even the OPPO Find X3 Pro is listed here, and even older OPPO flagship.
Quite a few Reno devices are listed here too
When it comes to the Reno series, quite a few devices are listed. The OPPO Reno10 Pro+ 5G, Reno10 Pro 5G, and Reno10 5G are here. The same goes for the Reno8 Pro 5G, Reno8 5G, Reno8, REno8 T 5G, and Reno8 T. The Reno7 is also mentioned. That’s basically it as far as Reno devices are concerned.
The rest of the list includes the OPPO F23 5G, F21s Pro, F21 Pro, K10 5G, A98 5G, A78 5G, A77 5G, A77s, A77, A58, A57, A38, and the OPPO A18. That is it as far as global units are concerned. One India-specific update is also mentioned, the OPPO A78.
The changelog will differ from one device to the other
The changelog between the devices will not be the same, of course. All of them will get some improvements for Android 14 directly from Google. As far as ColorOS 14-specific features are concerned, they do differ from device to device.
The OPPO Find N3, in particular, received Aqua Dynamics with morphing forms, a File Dock
“Don’t drink and drive” and now, here’s another rule: “Don’t phone and drive”. Since humans are not to be trusted with either rule, Android Auto will help us. It’s not clear when built-in breathalyzers are coming to our vehicles, but Android Auto is now enforcing the “Don’t phone and drive” with its latest feature: it bans certain apps.Tom’s Guide shares a finding from the German SmartDroid about the recently updated version 11.4 of Android Auto. Now, certain apps that are “restricted”, will display a small “P” (as “Parked”) bubble in the bottom right corner of the app icon. Before this, users who tried to access stationary-only apps would receive an error message if their car was in motion, the story goes.
This “P” icon has appeared more and more frequently on gaming or video streaming apps on Android Auto, like GameSnacks, a collection of touchscreen games for AA users.
Alongside the launch of its version 11.4, Android Auto can now summarize long text messages that can be listened to while driving. The only caveat is that messages containing more than 40 words will be paraphrased, while anything under that will be read in its entirety.
The AI-boosted Android Auto can also suggest relevant replies and actions, so you can simply tap once to send a message, share your ETA or start a call.
Let’s say that someone sends you a “Where the hell are you?” while you’re driving. As you don’t want to distract yourself, you’ll be able to just push a button and your Expected Time of Arrival (ETA) will be sent to the one who’s so obsessed with you.
Threat actors known as CACTUS orchestrated a sophisticated attack on two companies simultaneously, exploiting a software vulnerability within 24 hours of its disclosure.
This coordinated ransomware attack highlighted organizations’ growing risks in the digital landscape.
The attack involved intricate steps, including infiltrating networks, implanting remote access tools, encrypting workstations, and targeting virtualization infrastructure across different servers.
virtualization infrastructure
Rapid Exploitation of Vulnerabilities
The attack began less than 24 hours after disclosing a critical vulnerability in the Ivanti MobileIron Sentry, identified as CVE-2023-38035, with a CVSS score of 9.8.
This flaw allowed attackers to bypass authentication controls and execute code remotely.
The rapid weaponization of this vulnerability underscores a growing trend among cybercriminals to exploit software bugs swiftly, often before organizations can patch them.
ransomware group had targeted only Windows workloads
CACTUS’s operation was not only swift but also meticulously coordinated.
The hackers initially infiltrated one organization’s network before moving on to another company within the same group.
Despite the companies operating independently with separate networks, the attackers managed to exploit the interconnectedness of some machines to launch simultaneous attacks on both entities.
The assault was multifaceted, involving data exfiltration and the encryption of workstations and virtual machines, including domain controllers.
Recently, Bitdefender Labs collaborated in an investigation that unfortunately confirms two significant predictions made for 2024: the swift proliferation of opportunistic ransomware and the growing sophistication of cyber attacks.
Key Points:
Rapid Response: CACTUS swiftly capitalized on a Remote Code Execution (RCE) vulnerability, emphasizing the need for organizations to address such threats promptly.
Meticulous Coordination: The attack was meticulously planned, with synchronized actions on both companies within a five-minute window
Expanded Target Scope: CACTUS expanded its targets beyond Windows workloads to include ESXi and Hyper-V hosts, showcasing a broader focus
Forensic Expertise: The affected companies sought forensic expertise from Bitdefender Labs instead of paying the ransom, demonstrating a proactive approach to handling cyber threats
Expanding Targets and Sophisticated Tactics
Traditionally focusing on Windows workloads, CACTUS has expanded its scope to include ESXi and Hyper-V hosts, indicating a broader targeting strategy.
The group employed various remote access tools and tunnels, demonstrating high sophistication in maintaining persistence within compromised networks.
This operation’s success was partly due to using legitimate tools for remote access, such as AnyDesk, and the exploitation of security servers as gateways for further attacks.
The CACTUS ransomware attack is a stark reminder of the evolving threat landscape and the need for organizations to remain vigilant.
It emphasizes the criticality of promptly addressing known vulnerabilities and the benefits of employing robust cybersecurity defenses.
As cybercriminals continue to refine their tactics, the collaborative efforts of security professionals and the adoption of advanced protection technologies will be paramount in safeguarding against such sophisticated threats.
You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are incredibly harmful, can wreak havoc, and damage your network.
Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter