AMOS macOS Stealer Steals Special Files and Browser Data

0
[ad_1]

A new variant of the AMOS (Atomic) Stealer malware has emerged, targeting macOS users with sophisticated techniques to steal sensitive information.

Bitdefender’s recent analysis sheds light on this alarming development, revealing the malware’s methods and implications for individual users and organizations.
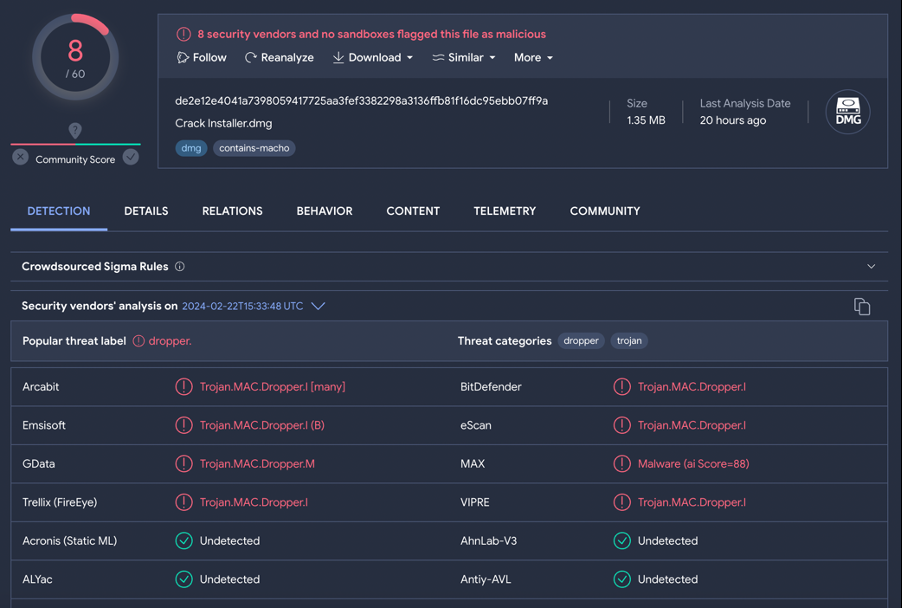
A short look into the code revealed that these files are significantly similar to other samples analysed in the last months
A short look into the code revealed that these files are significantly similar to other samples analyzed in the last months

You can analyze a malware file, network, module, and registry activity with the ANY.RUN malware sandbox, and the Threat Intelligence Lookup that will let you interact with the OS directly from the browser.

Stealthy Infiltration and Data Theft

The AMOS Stealer, first documented in early 2023, has quickly become one of the most prevalent threats to macOS users.

This new variant employs a combination of Python and Apple Script code to execute its malicious activities discreetly.

By dropping a Python script on the victim’s disk, the malware is capable of gathering a wide range of sensitive data, including files associated with crypto-wallet extensions, browser data (passwords, cookies, login data, etc.), files from Desktop and Documents directories, hardware-related and system information, and even the password of the local user account.

One of the most cunning tactics this malware uses is displaying a fake dialog impersonating the operating system.

Under the guise of a system update, it prompts users for their local account password, which, if entered, is captured and utilized for further malicious activities.

Bitdefender’s further analysis of the AMOS Stealer’s code revealed significant similarities with the RustDoor backdoor, suggesting a convergence of tactics among different malware families.

Both malware types focus on collecting sensitive files from the victim’s computer, with the AMOS Stealer being a more developed version capable of additional data theft, including the extraction of Safari browser cookies.

Distribution Tactics

The AMOS Stealer spreads through disk image files that are surprisingly small, making them less likely to raise suspicion.

These files contain a FAT binary with Mach-O files for both Intel and ARM architectures, acting as a dropper for the Python script.

A common tactic to bypass Apple’s security mechanisms involves tricking users into right-clicking and opening a seemingly innocuous “Crack Installer” application in the disk image.
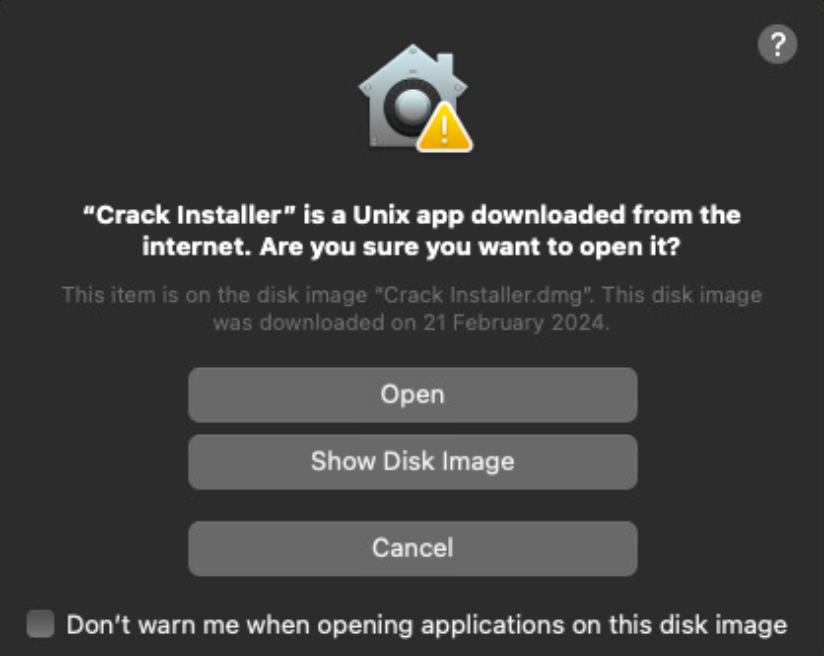
Crack Installer
Crack Installer

Protecting Against AMOS Stealer

Given the stealthy nature and potential damage caused by the AMOS Stealer, macOS users must stay vigilant.

Apple’s built-in protections, such as XProtect and the Malware Removal Tool (MRT), offer some defense against known malware by automatically updating and blocking malicious software. 

However, the evolving tactics of malware creators mean that users must also adopt safe browsing habits, be cautious of unsolicited software updates, and consider additional cybersecurity measures.

The discovery of the new AMOS Stealer variant highlights the ongoing malware threat to macOS users.
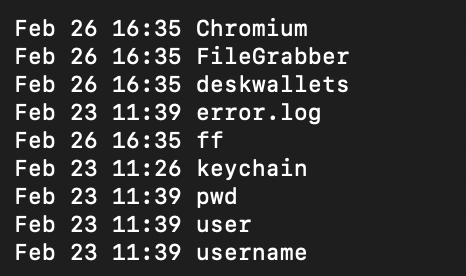
AMOS (Atomic) Stealer was previously associated  with a Russian threat actor, which is again confirmed by the address of the C2 server
AMOS (Atomic) Stealer was previously associated  with a Russian threat actor, which is again confirmed by the address of the C2 server

By employing sophisticated techniques to steal a wide range of sensitive information, this malware poses a significant risk to personal and organizational security. Awareness and proactive cybersecurity practices are essential in combating this and similar threats.

IOCs

IOCs Hashes for the DMG files:

  • 0caf5b5cc825e724c912ea2a32eceb59
  • f0dc72530fa06b278b7da797e5fcb3a1
  • 6c402df53630f7a41f9ceaafdca63173
  • e5c059cc26cc430d3294694635e06aef
  • b1e0274963801a8c27ef5d6b17fe4255
  • 8672d682b0a8963704761c2cc54f7acc
  • 11183a3f8a624dbf66393f449db8212e
  • e6412f07e6f2db27c79ad501fbdb6a99
  • b1b64298a01b55720eb71145978dd96b
  • 15e64a1f7c5ca5d64f4b2a8bf60d76a0
  • 4dce69d4d030bd60ee24503b8bdda39d
  • 740e5f807102b524188ffd198fe9bb3b
  • 8c71b553c29ff57cf135863f6de7125e

IOCs for the Mach-O droppers:

  • 6aab14b38bbb6b07bd9e5b29a6514b62
  • af23cd92ab15ebcc02b91664a0adc6fb
  • d9c40f35b9eaf16a2a7b4204a4e369a8
  • 6e777e9d95945386ced5c1cbb3173854
  • bc113574cfe6b8d0fb6fb13f43be261b
  • e125d2e359995c4f4b4d262244767385
  • 98fdef18dfca95dfd75630d8f1d54322
  • a66027146c009b3fdbc29400c7c74346
  • df74b93df64240e86d8d721c03d7a8a3
  • 08fc1d03db95a69cddcd173c1311e681
  • 013f3ba3a61ba52ba00b53da40da8a2b
  • 259809091a9d4144a307c6363e32d2ea

IoCs for the Python scripts

  • 6e375185480ee26c2f31c04c36a8a0e8
  • c8ac97b9df5a2dc51be6a65e6d7bce6b
  • 70b0f6ff8facca122591249f9770d7c9
  • fba8e41640a249f638de197ad615bd72

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are incredibly harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link
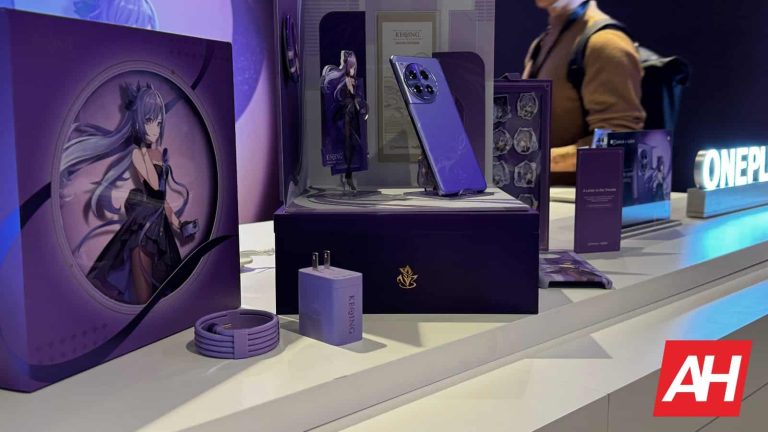
The OnePlus 12R now comes in a Genshin Impact Edition

0
[ad_1]

OnePlus has unveiled a new crossover with HoYoverse as part of MWC 2024, and will be releasing a new OnePlus 12R Genshin Impact Edition. Like last year’s Genshin Impact Edition of the OnePlus 11, the new OnePlus 12R crossover phone will have a themed design. This will come alongside a themed box and a whole bunch of goodies that come inside of it. While the OnePlus 11 was themed after Xiangling, this time around the phone will be themed after Keqing, one of the game’s Electro-wielding heroes. As such, the phone and the special edition collector’s box come in a brand-new violet colorway with various design elements revolving around the character.

This includes an etching of Keqing’s name across the bottom of the phone’s back panel. Additionally, there are etchings of Keqing’s signature lightning stiletto and Electro element. But the crossover doesn’t stop there. The box itself is a collectible and was designed to be kept and put on display. The phone also comes with a handful of collectible merchandise, as well as a themed Keqing case, SIM ejector tool, charging brick, and USB-C charging cable. On top of all that, the phone has a fully customized UI. Including personalized power-on and fingerprint unlock animations.

What’s really neat though are the customized system app icons, in addition to the charging animation themed after the Electro element. There’s also one last little trick this phone offers. And it’s the coolest part about the device.

The OnePlus 12R Genshin Impact Edition will project Keqing’s name onto surfaces

You’re probably wondering how the phone does this. And that’s a valid thing to wonder about. The process is actually rather fitting given the name. Using a process called “Electro Etching,” the “Keqing” that comes etched across the bottom of the phone’s back panel will project onto nearby surfaces. This happens because Electro Etching reflects light. So if you illuminate the back of the device, specifically the name Keqing, it’ll reflect the light back and project the name.

It’s a very cool little trick that would fit perfectly in a collector setup with everything else on display alongside the device.

The phone is available in limited quantities, starting at $649.99

If you’re a huge Genshin Impact fan and want to get your hands on this phone, there’s good and bad news. Pre-orders opened on February 28 but it didn’t take long for stock to be depleted. The good news is that OnePlus will have more stock of the device once it launches on March 21. The phone goes live at 6 A.M. PST/9 A.M. EST.

That being said, the phone will still be available in limited quantities. So you’ll want to be fast if you plan to pick this phone up. The OnePlus 12R Genshin Impact Edition will be sold exclusively through the OnePlus website. It’ll retail for $649.99 in the US and $869.99 CAD in Canada. OnePlus is also extending its “ANY phone in ANY condition” promotion to the OnePlus 12R Genshin Impact Edition. This means you can trade in your old device for $100 off the Genshin phone if you’re a US consumer. Those buying the phone in Canada will be able to save $150 CAD.


[ad_2]
Source link

Sundar Pichai reacted to Gemini’s inaccurate images, says it’s ‘completely unacceptable’

0
[ad_1]

Over the past week, Google has been getting some backlash over its AI tool Gemini. It has the ability to generate images of people, but it has been generating racially inaccurate depictions of historical figures. Now, Sundar Pichai, Google’s CEO, has finally spoken out about Gemini’s inaccurate images.

It’s good to see Google’s CEO publicly addressing these issues. He was notably quiet during the company’s previous round of layoffs. A massive number of people were let go from their jobs, and people were wondering what the company had to say about it.

Sundar Pichai addresses Gemini’s inaccurate images

So, to catch you up, people using Gemini’s image generation feature have found that the tool created inaccurate depictions of historical figures. When generating images of people who would be historically white, Gemini would “miss the mark” and depict them as a non-white race. Also, the tool would depict people who’d be male as female.

We would see images of German people being depicted as dark-skinned. There was another example where a person asked it to generate an image of the founding fathers, and it showed images of people of Asian descent. There are many more examples of this, and it led some people to call the tool “woke”. It seems to be that Google was looking to make Gemini a very inclusive platform, but it overshot it just a bit Anyway, we have to give it points for effort.

In any case, this is an issue that the company is currently working on. For certain regions in the world, Gemini does not generate images of people. The company halted the image generation of human beings until it could fix the issue.

Google’s CEO, Sundar Pichai, finally addressed the issue and issued a statement. He said, “I know that some of its responses have offended our users and shown bias – to be clear, that’s completely unacceptable and we got it wrong,”. Along with that statement, he also gave some good news for people wanting the functionality to return. “Our teams have been working around the clock to address these issues. We’re already seeing a substantial improvement on a wide range of prompts.”

So, the company is making improvements to its tool. As for the timeline, we are still in the dark. The issue with Gemini seems to be a deeply rooted flaw in the system. So, there’s no telling how long it will take Google to fix this issue. We’re all just going to have to stay tuned.


[ad_2]
Source link

YouTube picture-in-picture may be globally expanding beyond the premium membership

0
[ad_1]

Picture-in-Picture (PiP), the feature that lets you watch videos in a floating window while using other apps, is a staple for many mobile users. While Android has made PiP as part of the operating system for some time, the YouTube app itself has been more selective about its availability.

Until recently, only YouTube Premium subscribers outside the US could take advantage of PiP, unlike in the US where free users have had that benefit. That seems to be changing, though, as reports  are circulating of non-Premium users in Europe suddenly discovering access to YouTube’s PiP functionality.

Conflicting information and speculation among users

Confusingly, as Android Police notes, YouTube’s official support page still maintain that PiP requires a Premium subscription outside the US. Further, the feature wasn’t replicable in tests outside of Europe. This leads to a few possible scenarios:
  1. Experimentation: YouTube may be testing PiP with a select group of non-Premium European users.
  2. Accidental Rollout: The feature’s appearance could be an unintended error.
  3. Delayed Official Announcement: An expansion of PiP for non-Premium users outside the US could be in the works, but YouTube hasn’t made a formal statement yet.

Possible limitations and US precedent

Even if expanded PiP access becomes official, some restrictions may still apply. YouTube’s support pages note that even in the US, where non-Premium PiP debuted, music videos remain unavailable without Premium. Some copyrighted content could be similarly restricted for free users.This aligns with 2022’s rollout of PiP to non-Premium users on iPhone and iPad in the US. At the time, YouTube specified “non-music content” as the scope of the PiP expansion.

While the evidence right now seems promising, it’s too early to say for sure whether YouTube’s PiP will become widely available to non-Premium users outside the US. It will be interesting to see how YouTube continues to navigate the balance between providing access to PiP for non-Premium users while respecting copyright restrictions. As the platform evolves, it is likely that more updates and changes will follow.


[ad_2]
Source link

Researchers Exposed Predator Spyware Infrastructure Associated

0
[ad_1]

The Predator Files project, coordinated by the European Investigative Collaborations (EIC), has highlighted the extensive use of Predator spyware by customers of Intellexa surveillance solutions.

The intrusion set, known as Lycantrox, was exposed by Sekoia.io in collaboration with Amnesty International, CitizenLab, and MediaPart.

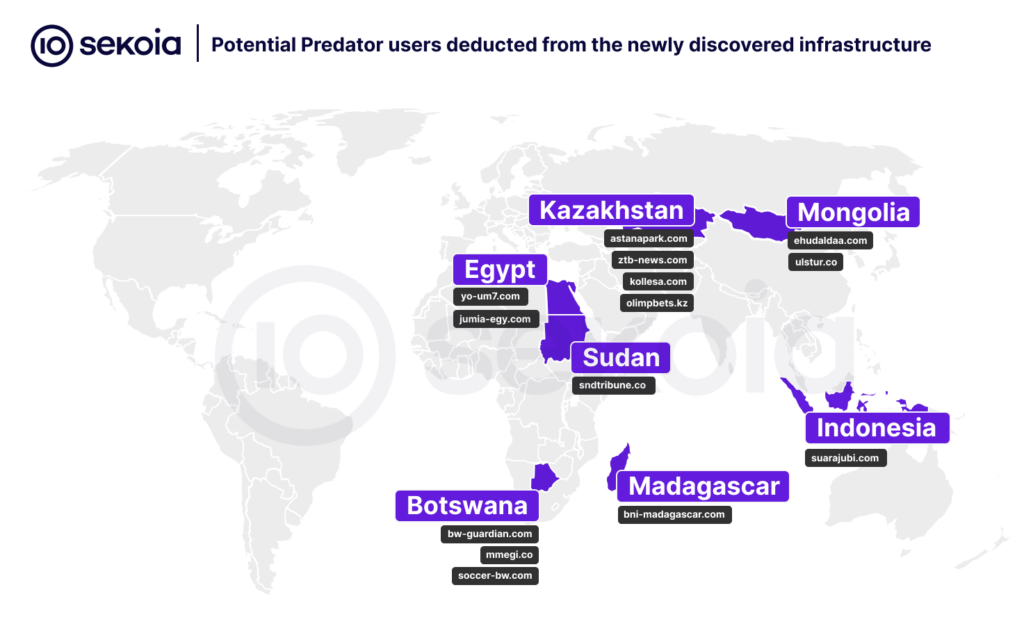
Alleged customers analysis

The exposure led to the shutdown of the spyware’s infrastructure, which was used against civil society, journalists, politicians, and academics.

However, despite the initial disruption, Sekoia.io discovered new infrastructure indicating that Predator spyware is still actively used.

You can analyze a malware file, network, module, and registry activity with the ANY.RUN malware sandbox and the Threat Intelligence Lookup that will let you interact with the OS directly from the browser.

Evolving Tactics for Stealth Operations

The new infrastructure revealed a shift towards more generic malicious domains, suggesting that government services using Intellexa’s solutions adapt their operations for greater plausible deniability.

Angola’s Concealed Continuation

Previously identified domains linked to Angola suggested government use of Predator.

The latest findings show Portuguese-speaking malicious domains not directly tied to Angola, hinting at continued use with improved operational security.

Madagascar’s Subtle Shift

Madagascar, which had acknowledged the use of Predator, now shows fewer noticeable malicious domains.

A domain resembling the French newspaper Le Monde was linked to Madagascar with medium confidence.

Indonesia and Kazakhstan: Business as Usual

Indonesia’s new domains confirm ongoing political surveillance, while Kazakhstan continues its use of Predator without significant operational changes.

Egypt’s Unchanged Stance

Egypt-related domains continue to mimic various sectors, with no notable change in operational security.

Sekoia.io has identified domains related to Botswana, Mongolia, and Sudan, expanding the list of potential Predator users.

Ongoing Vigilance and Collaboration

Sekoia TDR analysts remain committed to monitoring cyber mercenary groups and supporting initiatives like the Pall Mall Process to combat the irresponsible use of commercial cyber intrusion capabilities.

In conclusion, despite setbacks, the Predator spyware ecosystem remains a persistent threat.

The efforts of Sekoia.io and its partners underscore the importance of continued vigilance and international cooperation to address the challenges posed by commercial surveillance technologies.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are incredibly harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link
ALPHV is singling out healthcare sector, say FBI and CISA

0
[ad_1]

In an updated #StopRansomware security advisory, the Cybersecurity and Infrastructure Security Agency (CISA), the Federal Bureau of Investigation (FBI), and the Department of Health and Human Services (HHS) has warned the healthcare industry about the danger of the ALPHV ransomware group, also known as Blackcat. According to the advisory:

Since mid-December 2023, of the nearly 70 leaked victims, the healthcare sector has been the most commonly victimized.

We have reported in the past that ransomware groups show absolutely no respect to previous promises to leave the healthcare sector alone. This is not a new phenomenon, but ALPHV focusing on healthcare specifically is a relatively new one.

On the grapevine you can hear that ALPHV asked their affiliates to focus on this industry as a kind of payback for the disruptions to their infrastructure in December last year by law enforcement.

The recent attack on Change Healthcare has been reportedly caused by ALPHV, but we don’t feel it’s right to say that they didn’t attack healthcare way before the said disruption.

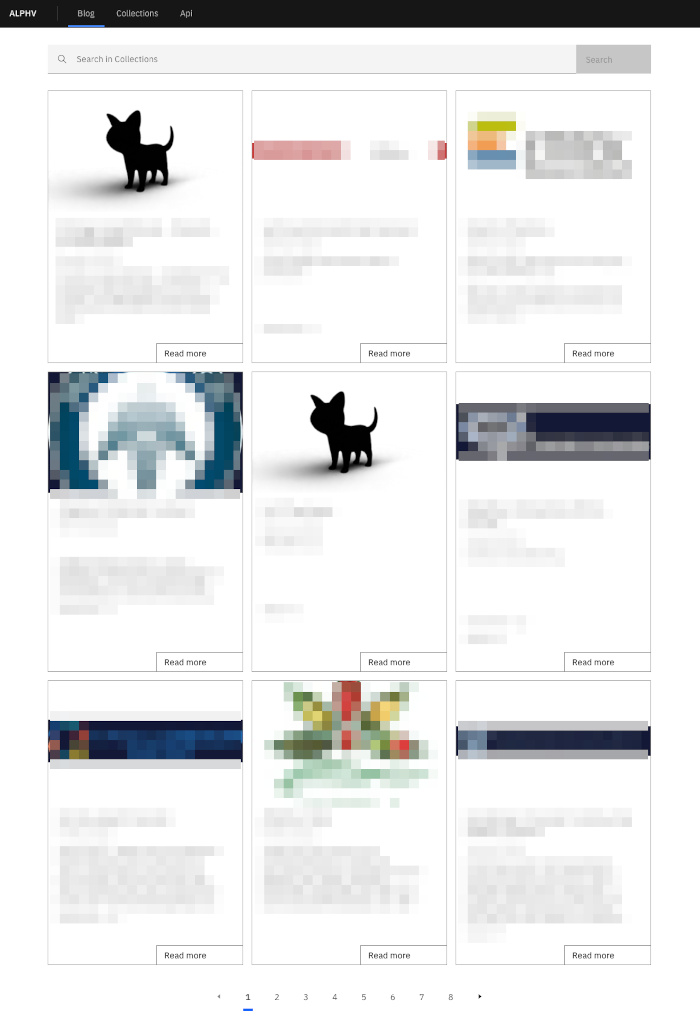
The ALPHV leak site home page. Four of the last nine victims were in healthcare

And unfortunately ALPHV is not the only one. In a new low, the attack on Lurie Children’s Hospital has been claimed by the Rhysida ransomware group.

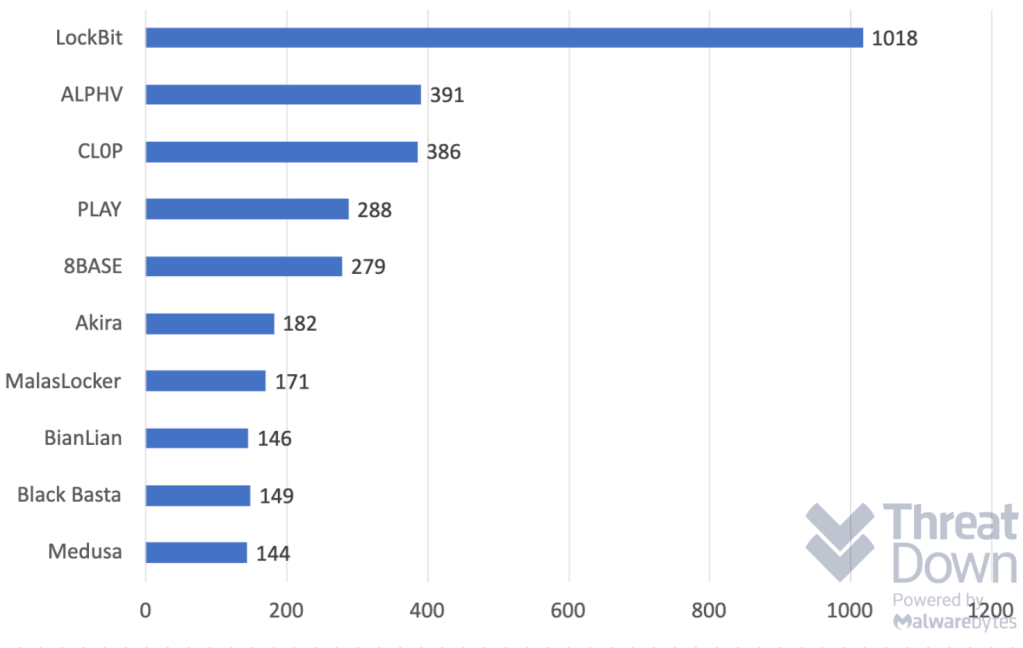
ALPHV is a Ransomware-as-a-Service (RaaS) group, meaning that its ransomware is made available to criminal affiliates using a software-as-a-service (SaaS) business model. ALPHV was ranked second in the list of most active big game ransomware groups of 2023.

According to the advisory, ALPHV’s affiliates use advanced social engineering techniques and open source research on a company to gain initial access. They pose as company IT and/or helpdesk staff and use phone calls or SMS messages to obtain credentials from employees to access the target network. After the initial breach they deploy remote access software such as AnyDesk, Mega sync, and Splashtop to prepare the theft of data from the network.

From the initial access they use various other legitimate, living off the land (LOTL), tools to further their access. Once the data has been safely moved to their Dropbox or Mega accounts, the ransomware is deployed to encrypt machines in the network. The latest ALPHV Blackcat update has the capability to encrypt both Windows and Linux devices, as well as VMWare instances.

It is unclear how ALPHV would stimulate attacks on healthcare institutions among its affiliates. We do understand that some of the data found during these attacks is very valuable on the underground market.

Having seen how devastating attacks on healthcare can be, we would encourage every cybercriminal involved to waive their right to be treated in any healthcare facility. Or, at least, try and realize the damage they are doing and the potential impact on people’s health.

How to avoid ransomware

  • Block common forms of entry. Create a plan for patching vulnerabilities in internet-facing systems quickly; and disable or harden remote access like RDP and VPNs.
  • Prevent intrusions. Stop threats early before they can even infiltrate or infect your endpoints. Use endpoint security software that can prevent exploits and malware used to deliver ransomware.
  • Detect intrusions. Make it harder for intruders to operate inside your organization by segmenting networks and assigning access rights prudently. Use EDR or MDR to detect unusual activity before an attack occurs.
  • Stop malicious encryption. Deploy Endpoint Detection and Response software like ThreatDown EDR that uses multiple different detection techniques to identify ransomware, and ransomware rollback to restore damaged system files.
  • Create offsite, offline backups. Keep backups offsite and offline, beyond the reach of attackers. Test them regularly to make sure you can restore essential business functions swiftly.
  • Don’t get attacked twice. Once you’ve isolated the outbreak and stopped the first attack, you must remove every trace of the attackers, their malware, their tools, and their methods of entry, to avoid being attacked again.

Our business solutions remove all remnants of ransomware and prevent you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.


[ad_2]
Source link

Samsung phones receive a Google Play System update after half a year

0
[ad_1]

After a months-long unexplained delay, a new Google Play System Update (GPSU) is finally rolling out to Samsung Galaxy smartphones. The devices, including the Galaxy S24 series, are picking up the January 2024 GPSU. They have been stuck on the July 2023 release for so long.

The Galaxy S24 and other Samsung devices get a new Play System Update

Google pushes monthly Play System Updates to Android smartphones and tablets. These are updates for underlying system services that make the core of Android. New releases are installed automatically behind the scenes, though users can manually check for them. Unlike major Android updates and security patches, Google has complete control over Play System Updates.

However, for the past several months, most Samsung phones haven’t received a new GPSU. They last picked up one in July 2023. The issue affected flagships, foldables, and mid-range devices alike. It was unclear whether there was a problem with Galaxy products that blocked their access to new releases or Google held back the updates for some undisclosed reason.

Even the Galaxy S24 series, which debuted last month, arrived with the July 2023 GPSU. Neither Google nor Samsung came forward to tell what was going on. Thankfully, whoever was at fault has addressed the problem. A new Google Play System Update is now rolling out to the likes of the Galaxy S24 and other models. It isn’t the latest release—the February GPSU is already available for Pixels—but a fairly recent one.

As reported by Android expert Mishaal Rahman, the January and February 2024 GPSUs don’t bring any “interesting changes.” However, he says the March 2024 release will have “a pretty significant” changelog. The source didn’t go into details but it shouldn’t be long before we get to know more. There is only one day remaining in February, so a new GPSU is on the horizon.

Check for updates on your Samsung devices

If your Samsung Galaxy is also stuck on the July 2023 Play System Update, the January 2024 release should reach you soon. You can check for it manually from the Settings app. Scroll down to the About phone section, tap on Software information, and then on Google Play system update. Your phone will now check for a new GPSU.

If available, you will be prompted to download it. But if you still don’t see an update, fret not. It should be available in a few days. You can repeat these steps to check for Google Play System Updates anytime. These updates usually aren’t big, though you might still need to restart the phone to complete the installation.


[ad_2]
Source link

Google wants publications to use AI to write articles, and it’s willing to pay

0
[ad_1]

Right now, many people fear the march of generative AI technology becoming more powerful. It proves to be a major threat to the journalism industry, and Google’s new tool only strengthens our fear of it. Google was testing a tool called Genesis via a new program, and this tool allows people to generate news articles using AI.

Speaking of AI technology, Google’s CEO has finally spoken out about the recent drama with Gemini’s image generator. Gemini has been generating pictures inaccurately depicting people’s race and gender. He said that this is “completely unacceptable.” He also stated that the company is making progress to fix it.

Google is testing Genesis via a new program

According to reports, Google is in the process of training Genesis for a public release. As such, the company is contacting news outlets to potentially use the tool. At this point, we’re not certain which outlets the company contacted. However, we know that it’s focusing on smaller publications.

In order to use the tool, publications have to agree to a minimum number of articles being posted. Google wants the publications to post at least three news articles a day using the AI tool. Also, they need to post at least one newsletter and one marketing campaign every month using the AI tool. That’s definitely a doable task.

Google isn’t just asking favors here, as the company is offering money to these companies to use the tool. We don’t know the specific amounts. However, reports say that Google is offering five-figure sums. So, the company is paying publications between $10,000 and $99,999. We’re pretty sure that the publications will receive this money over the course of the agreed-upon 12-month period.

At this point, there’s still a lot of information that we don’t know. Since this is a platform dedicated to making news articles, we can expect it to be optimized for news. It will do a better job than if a person simply went to ChatGPT or Gemini and asked it to write an article. Also, Google says that the articles will still need human intervention. So, it will still need to be a human Editor to make sure that everything is in check.

Regardless, there are still some issues with this

Firstly, Google says that the Genesis program does not want to replace human journalists. However, it’s blatantly obvious that this tool gives publications more reason to forgo human workers. Articles can be produced quickly with very little effort. So, why hire human writers when articles can be produced at lightning speed?

Also, the company is targeting smaller news publications, which will present a major barrier to entry for potential journalists. Smaller news publications are where many journalists get their start. Well, if you are a smaller news company, and you’re not quite pulling in the big bucks like The Verge or CNET, the last thing you’re focusing on is hiring full-time journalists.

Providing smaller news organizations with AI tools that eliminate the need for human writers could make it less likely that potential journalists will be able to get their start there. However, that’s only speculation at this point.

Right now, we don’t know the potential risks of this tool. So, we are just going to have to wait and see what happens.


[ad_2]
Source link

FBI, CISA warns Of ALPHV Blackcat Ransomware Attacking Hospitals

0
[ad_1]

To raise awareness of the ALPHV Blackcat ransomware as a service (RaaS) that targets the US healthcare industry, the FBI, CISA, and the Department of Health and Human Services (HHS) have collaborated to release a joint Cybersecurity Advisory (CSA).

To get initial access to the victim’s device, the BlackCat/ALPHV ransomware uses previously compromised credentials.

The malware compromises Active Directory administrator and user accounts as soon as it has access.

“Since mid-December 2023, of the nearly 70 leaked victims, the healthcare sector has been the most commonly victimized”, reads the joint advisory.

You can analyze a malware file, network, module, and registry activity with the ANY.RUN malware sandbox, and the Threat Intelligence Lookup that will let you interact with the OS directly from the browser.

“This is likely in response to the ALPHV Blackcat administrator’s post encouraging its affiliates to target hospitals after operational action against the group and its infrastructure in early December 2023”.

ALPHV Blackcat Attack Techniques

ALPHV Blackcat affiliates obtain initial access to a company through sophisticated social engineering methods and open-source investigation.

Actors utilize phone calls or SMS messages to gain credentials from staff members to enter the target network, posing as business IT and helpdesk employees.

ALPHV Blackcat affiliates use uniform resource locators (URLs) to communicate with victims via live chat, making demands and restoring the encrypted files.

ALPHV Blackcat affiliates use remote access tools like AnyDesk, Mega sync, and Splashtop to prepare for data exfiltration after they get access to a victim network.

Affiliates of ALPHV Blackcat establish a user account called “aadmin” and utilize Kerberos token generation to get access to domains.

Once inside networks, they employ tools like Plink and Ngrok, authorized remote access and tunneling tools.

ALPHV Blackcat affiliates get multi-factor authentication (MFA) credentials, login credentials, and session cookies using the open-source Evilginx2 adversary-in-the-middle attack framework.

The ransomware is then deployed, with the ransom note embedded as a file.txt.

Ransom Note

The finding comes after CISA warned last week that there had been active exploitation in the wild of a critical-severity authentication bypass vulnerability in ConnectWise ScreenConnect (CVE-2024-1709). 

The co-founder of RedSense, Yelisey Bohuslavskiy, has connected the compromised state of Change Healthcare to the ScreenConnect vulnerability.

This advisory contains updates to the FBI’s FLASH BlackCat/ALPHV ransomware indicators of compromise for April 2022 and December 2023.

A ScreenConnect remote access domain is one of the additional indications of the compromise included.

ScreenConnect remote access domain

The FBI, CISA, and HHS advise software manufacturers to increase their clients’ security postures by limiting the impact of ransomware techniques by using secure-by-design concepts and strategies in software development practices.

It is imperative that “critical infrastructure organizations” implement the guidelines into practice to lessen the probability and consequences of data extortion incidents and the ALPHV Blackcat ransomware.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are extremely harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link
One year later, Rhadamanthys is still dropped via malvertising

0
[ad_1]

It was just a little over a year ago that the Rhadamanthys stealer was first publicly seen distributed via malicious ads. Throughout 2023, we observed a continuation in malvertising chains related to software downloads.

Fast forward to 2024 and the same malvertising campaigns are still going on. After a lull last summer, we noticed an increase since the fall which so far has been sustained. The most recent targeted searches are for Parsec and FreeCad, followed by WinSCP, Advanced IP Scanner, Slack and Notion.

Threat actors are targeting business users with payloads such as FakeBat, Nitrogen or Hijackloader. One other malware family we have seen here and there is Rhadamanthys. In this blog post, we detail the latest distribution chain related to this malware.

Key points

  • Rhadamanthys is an infostealer distributed via malspam and malvertising.
  • Google searches for popular software such as Notion return malicious ads.
  • Threat actors are using decoy websites to trick users into downloading malware.
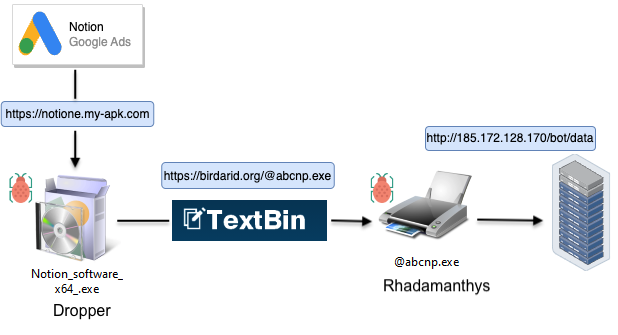
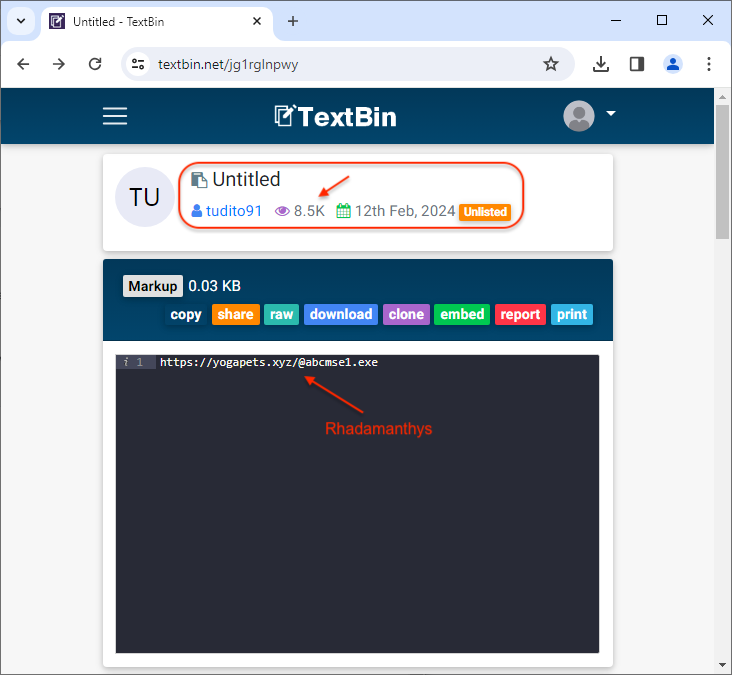
  • The initial payload is a dropper that retrieves Rhadamanthys via a URL pasted online.
  • The TexBin paste site shows the URL was seen/accessed 8.5K times.

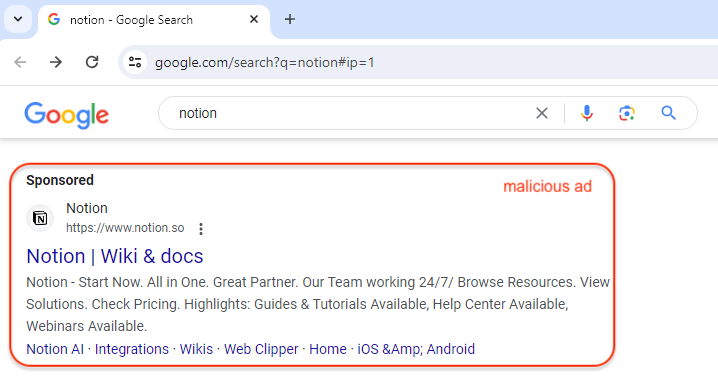
Malicious ad

Threat actors continue to impersonate well-known brands via sponsored search results. As can be seen below in a search for Notion (productivity software), an extremely deceiving ad is shown. Because it includes the official logo and website for Notion, most users will not think twice and click on the link.

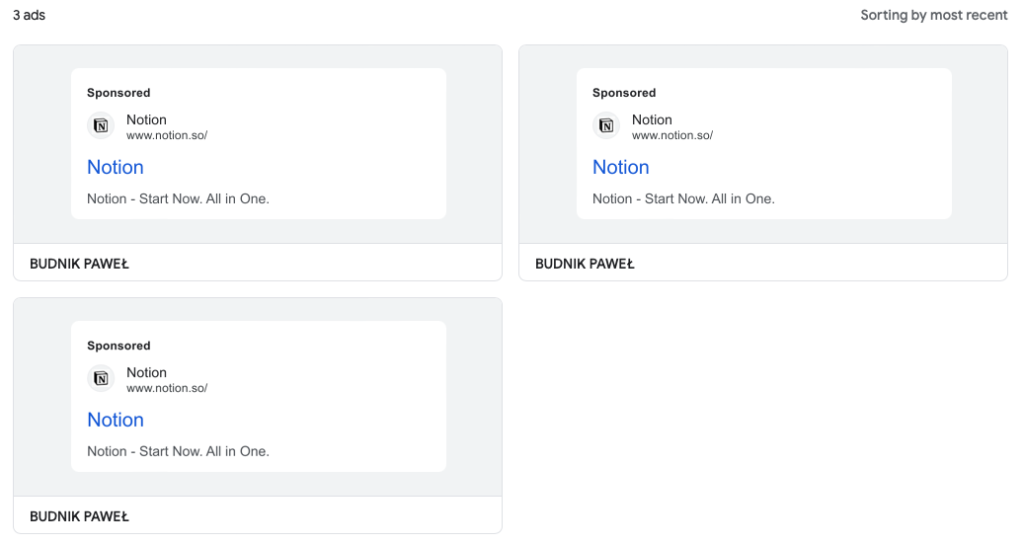
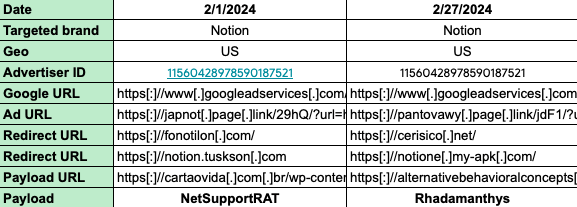
While the ad looks real on the surface, the Google Ads Transparency Center page (which can be accessed by clicking on the menu right next to the ad’s URL) shows this ad was created by a certain ‘BUDNIK PAWEŁ’ from Poland. According to the same report, the first ad first appeared on January 23, 2024.

As a matter of fact, we have been tracking this fraudulent advertiser for a few weeks and had reported it to Google in early February, when we first ran into it. At the time, victims who clicked the ad and visited the site were tricked with a download for NetSupport RAT.

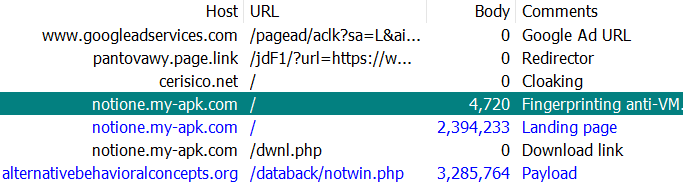
In this more recent campaign, the threat actor is pushing Rhadamanthys as the final payload, after an initial dropper. In the web traffic seen below, we can see that the threat actor uses a number of redirects to evade detection. URL shorteners and redirectors are quite common for the initial ad click, often followed by an attacker-controlled domain responsible for cloaking traffic.

There is one more check within the browser via JavaScript to detect virtual machines before the actual landing page is displayed to the victim.

Landing page and payload

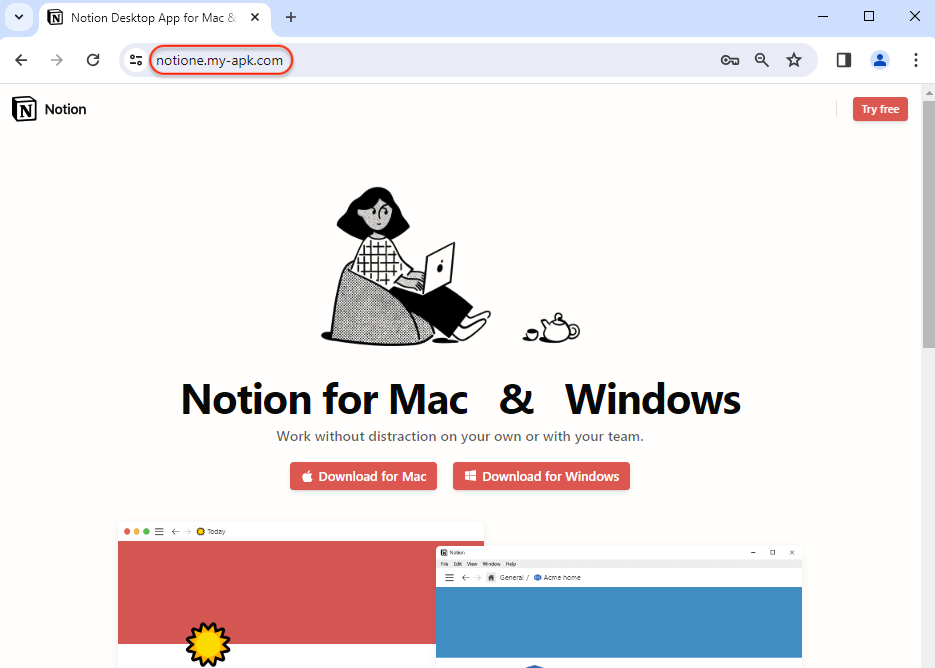
The landing page is the decoy site that victims will see after they click on the ad. Apart from the URL in the address bar, it looks very similar to the official web site for Notion, although somewhat simplified. There are two download buttons, one for Mac and the other for Windows.

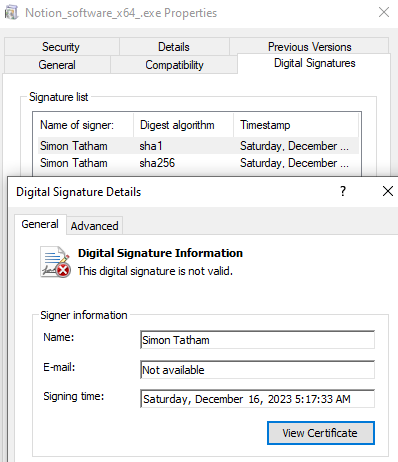
The Windows binary is a signed file but its digital signature is not valid. The name of the signer that shows here is from the inventor of PuTTY, a popular admin tool. This digital certificate is likely fake or was revoked, but it may evade detection in some cases.

This dropper contacts the paste site TextBin where it retrieves a URL for the followup payload, Rhadamanthys. If the numbers are correct this unlisted paste was viewed 8.5k times already.

Rhadamanthys attempts to steal credentials stored in applications such as PuTTY, WinSCP and mail programs (screenshot from Joe Sandbox):

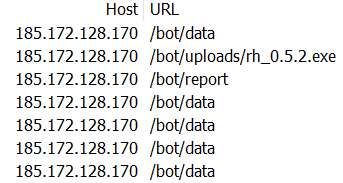
Upon execution, Rhadamanthys reports to its command and control server, sends and receives data.

Conclusion

Not a lot has changed with malvertising campaigns focused on software downloads as we enter the second year of actively tracking them. Sponsored search results continue to be highly misleading due to the fact that any verified individual is able to impersonate popular brands by using their logo and official site within the ad itself.

We are aware of reports shared within private circles, that businesses were compromised after an employee clicked on a malicious ad. Follow-up activities post infection include the usual ‘pentesting tools’ that precede a company-wide breach or ransomware deployment.

The infrastructure used in this particular attack was reported to the relevant parties. Malwarebytes and ThreatDown customers are protected against the payloads and distribution sites.

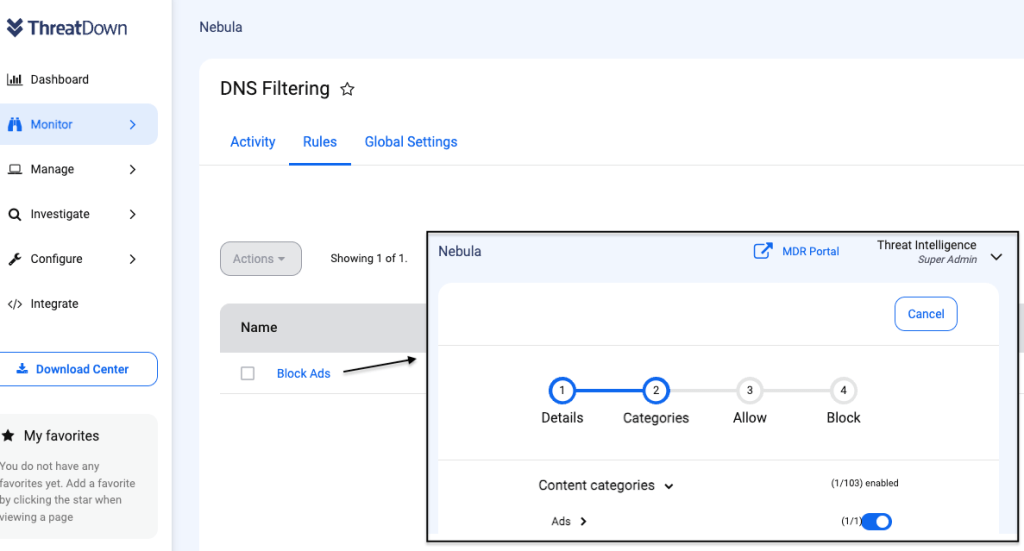
Additionally, EDR customers who have DNS Filtering can proactively block online ads by enabling the rule for advertisements. This is a simple, and yet powerful way to prevent malvertising across an entire organization or in specific areas.

Endpoint users will see a customizable message when they click on an ad such as those that appear on a search engine results page:

Indicators of Compromise

Malvertising chain

pantovawy.page[.]link
cerisico[.]net
notione.my-apk[.]com
alternativebehavioralconcepts[.]org

Dropper

6f4a0cc0fa22b66f75f5798d3b259d470beb776d79de2264c2affc0b5fa924a2

Dropper IP

185[.]172[.]128[.]169

Rhadamanthys download URL

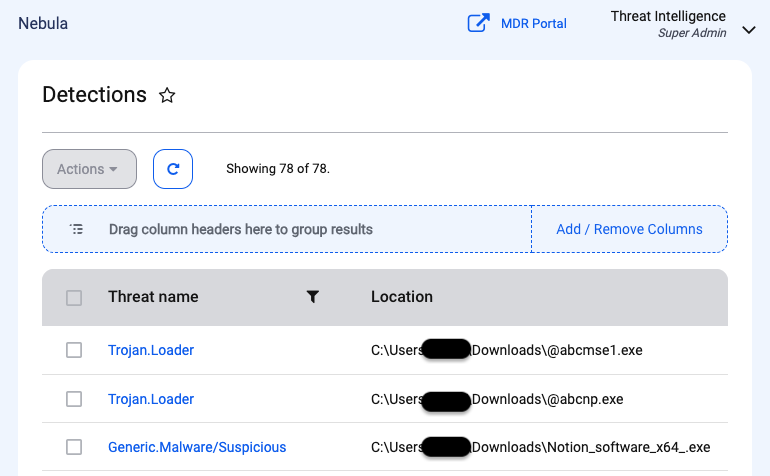
yogapets[.]xyz/@abcmse1.exe
birdarid[.]org/@abcnp.exe

Rhadamanthys

e179a9e5d75d56140d11cbd29d92d8137b0a73f964dd3cfd46564ada572a3109
679fad2fd86d2fd9e1ec38fa15280c1186f35343583c7e83ab382b8c255f9e18

Rhadamanthys C2

185[.]172[.]128[.]170

[ad_2]
Source link