Apple investors demand transparency on AI usage

0
[ad_1]

Apple plans to showcase multiple new artificial intelligence features at this year’s Worldwide Developers Conference (WWDC). Apple’s major shareholders look set to prod the firm into opening up about how it uses artificial intelligence (AI). It occurred at the company’s annual general meeting when investors with substantial stakes in the company argued for greater transparency, which does not seem to be Apple’s biggest forte.

Investors forcing Apple to unravel ethical guidelines for AI

The AFL-CIO proposal demands that Apple should reveal its use of AI and any ethical guidelines dictating its implementation. According to Financial Times, notable backers of this move include Norges Bank Investment Management and Legal & General, both of whom are Apple’s eighth and tenth largest shareholders respectively.

In voting disclosures, Norges Bank, which runs the world’s biggest sovereign wealth fund, stressed that Apple’s board should consider the “social consequences of its operations and products”. Legal & General also criticized Apple for not disclosing its approach to managing risks associated with AI, which will ultimately lead to negative publicity.

Another source reporting on the subject revealed details about another meeting between Legal & General and Apple to discuss AI. But to no avail, the tech firm refused to become more transparent. Legal & General argues that Apple needs to be more forthright about its AI applications and risk management processes.

Apple’s pushback on the resolution

The company’s own investor advisory firm, Institutional Shareholder Services, prompts Apple to support the resolution. They are objecting to Apple’s existing guidelines for not being specific about risks that could result from AI use, thus raising questions about shareholders’ capacity to correctly assess them.

Apple however is trying hard to convince its investors not to vote for the resolution arguing that it is too broad and would reveal sensitive plans and initiatives thus causing harm to the company’s competitive position. However, with over 30% of investors supporting these non-binding petitions in the U.S., they can exert enough pressure on the firm.


[ad_2]
Source link
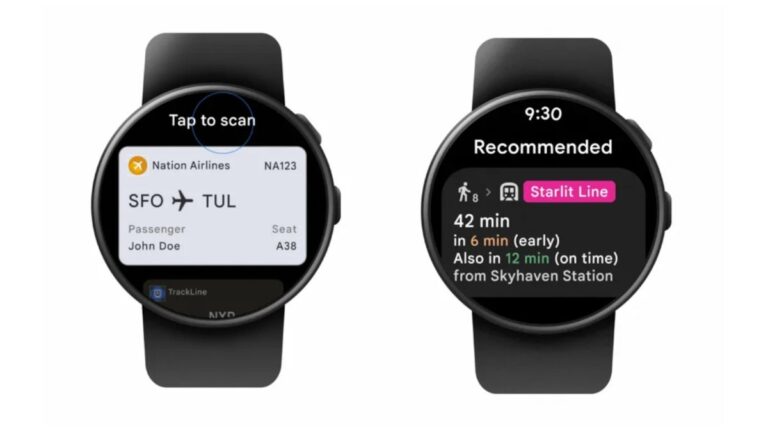
Google brings Wallet passes to Wear OS watches along with transit directions

0
[ad_1]

Google announced several new features coming to Android devices in February, such as AI-powered tools, navigation app improvements, as well as new health, wellness and fitness data options.

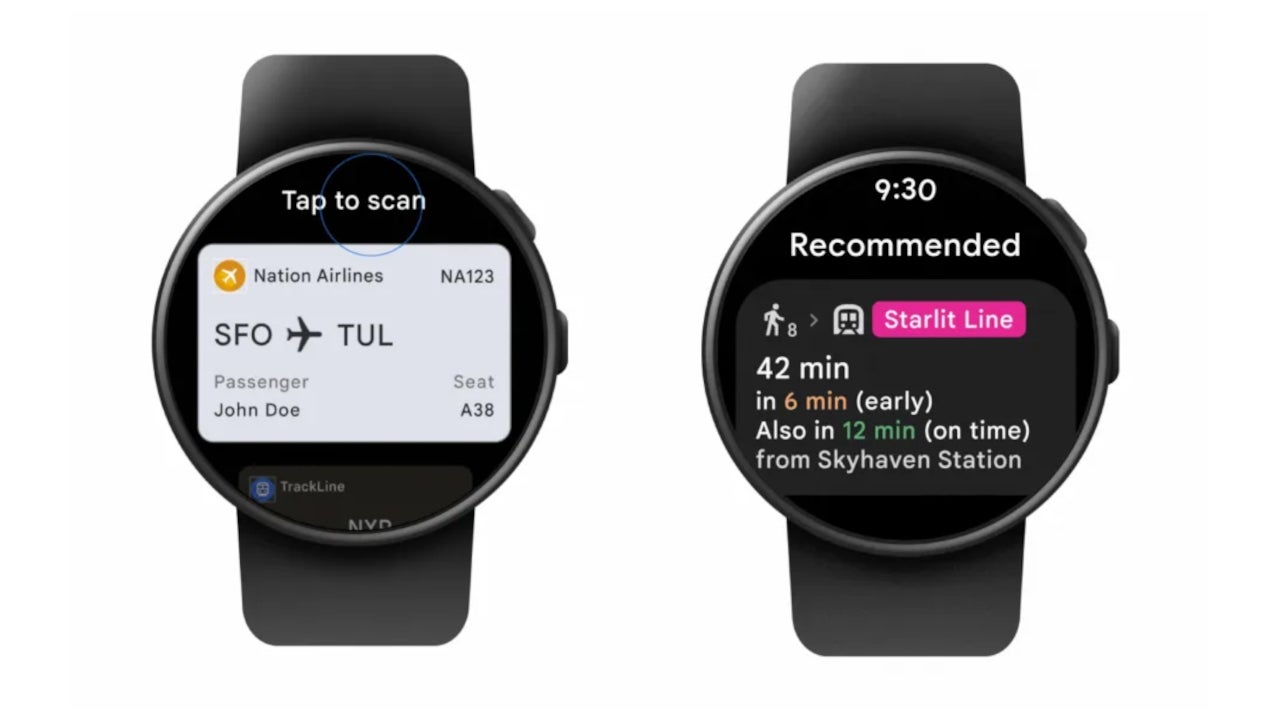
For those using Wear OS smartwatches, the list of new features arriving this month is a bit shorter, but they’re worth mentioning. As the title says, Google Wallet passes are finally coming to Wear OS watches, the search giant announced early this week.

This means that Wear OS watches can now access boarding passes, event tickets, gym memberships, loyalty cards and more directly from their wrists. Google is even allowing users to choose which passes to hide or display for even easier access.

In addition to Wallet passes, Google confirmed that public transit directions are now available on Maps for Wear OS, thus removing the need to pull out the phone from their pockets and instead find all the info they need on their wrists.

Information such as departure times and compass-guided navigation directions are available directly from Wear OS watches going forward. Of course, those who prefer their phones can also mirror directions to their watch and navigate hands-free.

These features, along with several others, will be rolling out in the next couple of days, so be on the lookout for a new update on your Android-powered device.


[ad_2]
Source link

Hackers Advertising New Version of WarZone Malware

0
[ad_1]

Cybersecurity experts have raised alarms as a new version of the notorious WarZone Remote Access Trojan (RAT) has been spotted being advertised on various hacking forums.

The latest iteration, known as WarZone RAT v3, boasts enhanced features and capabilities, making it a more potent threat to individuals and organizations alike.

The WarZone RAT is an advanced type of Remote Administration Tool that allows cybercriminals to manage and monitor targeted devices remotely.

This tool is particularly designed for Windows operating systems and is known for its speed and stealthiness.

The RAT enables attackers to gain unauthorized access to victims’ computers, allowing them to steal sensitive information, deploy additional malware, and maintain persistent access to compromised systems.

You can analyze a malware file, network, module, and registry activity with the ANY.RUN malware sandbox, and the Threat Intelligence Lookup that will let you interact with the OS directly from the browser.

The Federal Bureau of Investigation (FBI) recently seized several Internet domains that were being used to sell Warzone RAT malware.

The agency also arrested individuals who were involved in selling the malware. Warzone RAT is a Remote Access Trojan that allows attackers to gain unauthorized access to a victim’s computer and steal sensitive information.

WarZone RAT v3 On Hacking Forums

The advertisement for WarZone RAT v3, as seen by ThreatMon in a recently leaked screenshot, highlights several new features that enhance its effectiveness.

One such feature is the “Smart Updater,” which allows the RAT to update its tools file on all clients, including new ones, without detection. 

This feature can also be disabled at the user’s discretion, providing flexibility to the attacker.

Moreover, the advertisement mentions the ability to uninstall old files if the new file can be executed successfully, suggesting that the RAT can clean up its tracks to avoid detection.

It also claims that users can connect to their WarZone Server and even expose the HTTP server to the internet, potentially increasing the reach of their malicious activities.

The list of features includes client control, file manager, startup manager, remote system control, and more.

These tools give attackers a wide range of capabilities, from basic surveillance to full control over the infected device.

The RAT also includes a “WarZone rat poison” feature, which could refer to a mechanism for corrupting or disabling security software on the victim’s computer.

Security experts warn that the availability of such sophisticated tools on hacking forums increases the risk of cyber attacks, especially for those who lack robust cybersecurity measures.

The ease of access to these tools allows even low-skilled attackers to launch advanced attacks, making it crucial for individuals and organizations to stay vigilant and keep their security systems up to date.

The advertisement of WarZone RAT v3 also emphasizes its ability to make payloads harder to detect, which is a significant concern for cybersecurity professionals.

As the cyber threat landscape continues to evolve, staying informed and prepared is the best defense against these insidious attacks.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are extremely harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

Galaxy Z Fold 6 design revealed, shown from all sides

0
[ad_1]

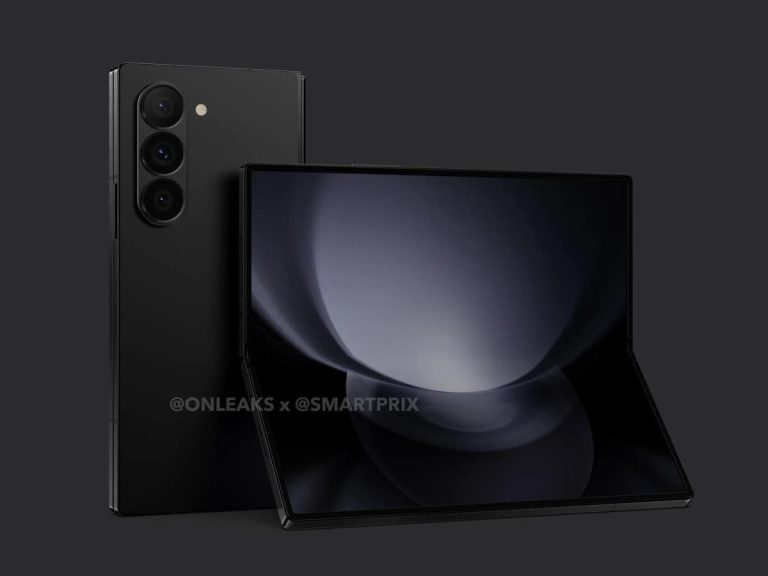
The Samsung Galaxy Z Fold 6 design has just been revealed thanks to CAD-based renders. @OnLeaks partnered up with SmartPrix in order to bring us these images and a video.

The Galaxy Z Fold 6 design revealed via images and a video

Yes, you read that right. Both images and video are available below. You’ll find them below the article, and they really don’t leave much to the imagination. The video itself spins the unfolded render of the Galaxy Z Fold 6 and thus shows us the device from all sides.

The overall design language doesn’t seem to be much different than what the Galaxy Z Fold 5 offered. The phone has flat sides all around, which are slightly rounded towards the edges.

Its back side is flat, as is its front side. There are three cameras included on the back, in the top-left corner. They’re a part of a camera island, as they were last year. They’re once again vertically aligned, though the camera island seems to be larger than last year.

Samsung will once again use an under-display camera on the main panel

The phone’s speakers sit both at the top and at the bottom of this smartphone. A display camera hole seems to be included on the cover display, while Samsung will once again use an under-display camera on the main panel.

Based on the CAD renders, the Galaxy Z Fold 6 will include a 7.6-inch main panel. That’s the same size of the display as the Galaxy Z Fold 5 features. The thing is, the Galaxy Z Fold 6 will be a bit shorter and a bit wider than its predecessor.

It will be wider than its predecessor, which is actually a good thing

It will allegedly be 1.4mm shorter and 2.6mm wider than the Galaxy Z Fold 6, when unfolded. The device will measure 154.9 x 129.9 x 6.1mm. That also suggests that Samsung is changing the aspect ratio of the cover display, as tipped. It also looks to be wider, it’s nowhere near as narrow as the one on the Galaxy Z Fold 5. Many people will appreciate that.

The Galaxy Z Fold 6 will likely launch in July, or possibly August. The Samsung Galaxy Z Fold 5 did arrive in July last year, so… we’re expecting a late July launch. The Galaxy Z Flip 6 will launch alongside it, and possibly the Galaxy Ring too.


[ad_2]
Source link

Zoom will no longer support certain iOS devices starting next month

0
[ad_1]

Zoom recently updated its support page with new release notes for iOS devices and revealed plans to drop support for certain iOS versions. The newest Zoom update brings a bunch of new features and improvements, but also a warning for users who own old iOS devices that they may no longer be able to use Zoom starting next month.The changelog of the Zoom update released this week mentions that this is the last planned release to support iOS versions 11 and 12. This means that the next update planned to arrive in March will only support iOS devices running on iOS 13 or higher. If you’ve already upgraded to an iOS 13 device, then you don’t have to worry about the upcoming change.

In related news, the latest Zoom update introduces some interesting new features like all screens mode and auto-move to/from Waiting Room. Also, Zoom has gained the ability to view Webinar Q&A submissions from before joining, as well as an enhanced UI for Thread Summary with AI Companion in Team Chat.

There are also a couple Mail and Calendar features included in the update, such as the ability to disable Zoom Mail sound effects and some enhancements to Zoom Calendar notifications.

Last but not least, the latest version of Zoom can hide sensitive data during a call. For example, when this feature is enabled, it will mute a user’s sounds and tones when pressing a dial pad key on their phone’s screen or keyboard during a call. Instead of actual numbers, the app will now display asterisks.

Besides that, users affected by speaker issues during a call will now be notified via a pop-up message alert.


[ad_2]
Source link

Saving frames of a YouTube video is about to get easier than ever

0
[ad_1]

Saving a video frame hasn’t always been the easiest task whether you are on a desktop or mobile. While you could always use the usual screen-capturing tools on either platform, it wasn’t always possible to get a clean output without menus and player controls being visible, unless you cropped a significant portion out of the picture. Fortunately, this has now been somewhat remedied on the desktop, and an Android solution appears to be on the way as well.

Saving a YouTube video frame is only available on desktops as of now

Grabbing a clean screenshot of a particular frame on a YouTube video, for example, used to be a challenge without resorting to third-party extensions that could take care of this task for you.

Google fixed this on the desktop via an update to the YouTube media player. It now requires only a double right-click to save a frame from the video. After the double right-click you will see the option “Save video frame as…” marked as “NEW”. This option would output a clean .jpg or PNG of the entire frame.

@Leopeva64 on X has spotted this feature in the Canary builds of the Chrome browser since early last year. He regularly scours the Chromium Gerrit repository for new commits of upcoming features. This went live for Chrome desktop, but there was still no way to do this on Android, other than waiting for the player controls to fade and then screenshot using the usual button combinations on your respective mobile device.

You will soon be able to use the feature on Android devices

However, recent code updates indicate that Google will soon allow you to save video frames directly from YouTube on Android devices. This was also spotted by the user via yet another commit on the Chromium Gerrit repo called “Mark copy/save video frame features as disabled on Android,” with a description that clearly states “These features are not implemented on Android yet”.

This indicates that plans are in motion to bring this handy tool to Android, although there is no clear indication of how Google will implement it.


[ad_2]
Source link

Samsung Knox coming to 2024 smart TVs

0
[ad_1]

Samsung announced today that the security and management framework that we find these days on just about every Galaxy device, Knox, is going to be installed on its newest smart TVs too.

Meant to provide complex security and privacy for both businesses and end users, Samsung Knox recently achieved “Common Criteria” (CC) certification ahead of its launch on smart TVs.

The South Korean company notes that it has now received CC certification for Samsung Knox for 10 consecutive years, which feels like an incredible achievement for Samsung’s IT and security solution.

Of course, Knox has been available on Samsung’s smart TVs for quite a while, so this is just a heads-up for those who plan to purchase a 2024 model. For your peace of mind, the CC certification highlights three key aspects where Samsung Knox scored highly:

  1. Tizen OS Monitoring: Samsung Knox actively detects potential hacking threats in real time, flagging any unauthorized changes in critical sectors of Tizen OS, the core of Samsung TVs.
  2. Phishing Website Blocking: Samsung Knox verifies web pages accessed by users, preemptively blocking any phishing sites to safeguard user data and privacy.
  3. Enhanced Personal Information Protection: Samsung Knox ensures seamless protection of users’ sensitive personal data through a secure connection with Samsung Knox Vault, a dedicated processor for security functions.

Samsung’s 2024 TVs are not yet available to consumers, but the company has already introduced its lineup for the year at the beginning of January, so the first models are expected to arrive very soon.

[ad_2]
Source link

Beware of Typos that May lead malicious PyPI Package Installation

0
[ad_1]

Cybersecurity experts have raised alarms over a new threat vector targeting Python developers: typo-squatting on the Python Package Index (PyPI).

The notorious Lazarus group, known for its cyber espionage and sabotage activities, has been implicated in the release of malicious packages designed to exploit typographical errors made by developers when installing packages.

You can analyze a malware file, network, module, and registry activity with the ANY.RUN malware sandbox, and the Threat Intelligence Lookup that will let you interact with the OS directly from the browser.

Typosquatting: A Gateway for Malware

The JPCERT/CC has confirmed the release of several malicious packages on PyPI, including pycryptoenv, pycryptoconf, quasarlib, and swapmempool.

These packages were crafted to resemble the legitimate pycrypto package, a widely used encryption library in Python.

Python packages released by Lazarus attack group

The subtle misspellings are intended to dupe unsuspecting developers into downloading and installing malware on their systems.

Inside the Malicious Packages

Upon closer examination, the structure of these packages reveals a concerning setup. For instance, pycryptoenv it contains a file named test.py, which is not a Python script but an XOR-encoded DLL file.

The file within the package handles the decoding and execution of this file.

Flow up to Comebacker execution

This malware, called Comebacker, is not new to the cybersecurity community. Lazarus previously used it in a campaign targeting security researchers, as reported by Google in January 2021.

The malware is executed through a series of steps, starting with the decoding of test.py, saving it as output.py, and then running it as a DLL file.

The Comebacker Malware

The Comebacker malware uses HTTP POST requests to communicate with its command and control (C2) servers.

Comparison of characteristic NOP commands between Comebacker and BLINDINGCAN

The data sent and received is encoded, and upon successful communication, the server sends back a Windows executable file.

This file is then executed in memory, avoiding detection by traditional antivirus software.

Lazarus has employed comparable techniques in disseminating malware through different package repositories, including npm, suggesting a more extensive approach to infiltrating software supply chains. This particular occurrence is not an isolated event.

npm package released by Lazarus attack group

A previous report by BleepingComputer highlighted the deployment of fake VMware PyPI packages by Lazarus hackers, further underscoring the group’s focus on infiltrating developer ecosystems.

Protecting Against Typosquatting Attacks

The malicious packages in question have been downloaded hundreds of times, suggesting that many developers have fallen victim to this scheme. 

Number of pycryptoenv downloads

Developers must be vigilant when installing packages, double-check the spelling, and verify the source’s authenticity.

Additionally, organizations should consider implementing automated tools to detect and block the installation of potentially malicious packages.

The discovery of these malicious PyPI packages is a stark reminder of the evolving threat landscape and the need for heightened awareness among developers.

As the Lazarus group continues to refine its strategies, the cybersecurity community must remain proactive in identifying and mitigating such threats.

For more detailed information on the malware and its behavior and the indicators of compromise, readers are directed to the appendices provided by JPCERT/CC.

This article is based on the findings and reports from JPCERT/CC and other cybersecurity sources.

The information provided aims to educate and inform the public about typo-squatting risks and the importance of cautious package installation practices.

You can block malware, including Trojans, ransomware, spyware, rootkits, worms, and zero-day exploits, with Perimeter81 malware protection. All are extremely harmful, can wreak havoc, and damage your network.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

Best of MWC 2024: HONOR Magic6 Pro

0
[ad_1]

Outstanding camera performance meets well-executed hybrid software.

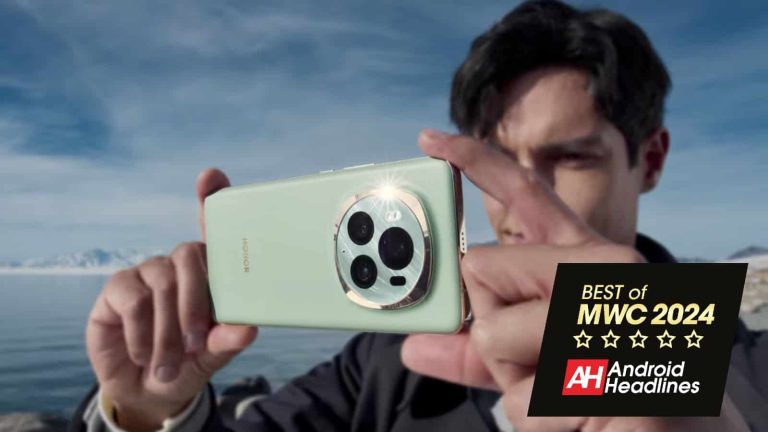
The HONOR Magic6 Pro was one of the most attention-grabbing smartphones at MWC 2024… for a good reason. HONOR announced the global variant of the device at MWC 2024, and this is one of those phones that you should pay attention to. We’ve been using it for a couple of weeks now, and our review is already out. The HONOR Magic6 Pro is a step up compared to its predecessor, and not only does it offer great cameras, but it shines in various other aspects, which is why we’ve decided to give it one of our MWC 2024 awards.

Sleek, comfortable, and easy to recognize

The HONOR Magic6 Pro is a large phone, there’s no denying it. It’s a very comfortable phone to use, though. HONOR has been doing a great job when it comes to ergonomics for quite some time now. The company’s phones are usually really well-designed, and they are a pleasure to handle. The same is the case here. The glass model is more slippery, but we spent the most time with the vegan leather model. The backplate on the phone is very soft, and it does add the much-needed grip. The phone does seem a bit smaller than it actually is thanks to the design, which is a good thing.

It does have a pill-shaped hole on the front, but that cutout has a purpose. The 3D facial scanning on this phone is great, and the ToF 3D camera sits up there, along with a regular front-facing camera. Even the phone’s rear-facing camera island is easy to set apart from the competition. The entire package looks very nice, and even the bezels around the display seem to be uniform, or at least very close to that. They’re also very thin, which only adds to the premium feel of the device.

Android & iOS under the same roof

I talked about MagicOS 8.0 at length in the full review for a very good reason. HONOR has been dancing on both Android and iOS sides of things for quite some time now, in regards to software. Until now, however, the software did feel a bit unfinished. The MagicOS 8.0 improved things quite a bit. Everything got an extra level of polish, and it actually feels like you’re getting both Android and iOS as part of MagicOS 8.0. You are getting all the Android features you’d expect, but you’re also getting some iOS-like functionality that many of you will appreciate. This combo works really well under the MagicOS 8.0 roof, to be quite honest.

When it comes to iOS, the 3D facial scanning and the pill-shaped hole are reminiscent of iOS, and the facial scanning works just as well, if not better. HONOR even added some software functionality that includes that pill-shaped hole, just like Apple did. Your lock screen notifications are pulled to the bottom, to be easier to reach, and the notification toggles are separated from your notification shade. All of that reminds us of iOS. However, you can swipe across the home screen to access your notification shade, which is a touch of Android, for ease of use. Speaking of which, swiping on the left 2/3 of the screen will have that effect, while doing the same on the right 1/3 will access the quick toggles screen. This solution is very effective and smart, as you’ll be accessing your notifications more frequently.

The animations in MagicOS 8.0 are outstanding, and the overall software experience is very fluid. You do get a ton of Always-On Display options, and the same goes for lock screen options. MagicOS 8.0 is a very nice mix of both Android and iOS-like functions, and it felt really nice to use.

Outstanding cameras & fast charging

The HONOR Magic6 Pro is a camera-centric phone. HONOR customized the main camera, which also offers variable aperture, and it does a great job in terms of performance. The same goes for the 180-megapixel periscope telephoto camera. We’ve enjoyed using this phone for our picture-taking needs, and for the most part, it does a great job. You do get three very capable cameras on the back, and the selfie camera is also very good, which is something that most companies don’t really care about. That’s not the case here.

The battery life also proved to be great, but if you end up needing a charge in the middle of the day, you do get access to 80W wired and 66W wireless charging. Both of those charging methods are very fast. Presuming you have the right charger, you can top-up the phone in no time. We’re only scratching the surface here. The bottom line is, the HONOR Magic6 Pro is an outstanding smartphone, and it won one of our awards for a reason.


[ad_2]
Source link

TikTok starts to rub out Universal Music Group content, no new deal has been reached

0
[ad_1]

TikTok starts to remove Universal Music Publishing Group content from the pest-like short video app, as no new licensing agreement with the music label has been reached, the social media firm said.

TikTok has also started to mute videos on its platform that feature songs written by any songwriter signed on to UMPG (Universal Music Publishing Group), after removing the songs from Universal Music Group (UMG), as the licensing deal expired on January 31 (via Reuters).

The report cites a person familiar with the matter, who says TikTok is likely to remove “all the UMPG content before the end of February”, considering the legality of the matter. TikTok, however, has reached out to UMG and is still open to negotiate a new deal, the source added.

Back in the end of January 2024, Universal Music Group stated that it couldn’t reach new deal terms with TikTok. The disagreements were mainly about how artists are paid and how TikTok uses AI. Universal Music accused TikTok of trying to push for a deal that was less favorable than before.

UMG is the parent company of UMPG that represents an expansive roster of artists such as Taylor Swift, Bad Bunny, Sting, The Weeknd, Alicia Keys, Steve Lacy, Drake, Billie Eilish, Kendrick Lamar, Rosalía, Harry Styles, Ariana Grande, Justin Bieber, Adele, U2, Elton John, Brandi Carlile, Coldplay, Pearl Jam, and Bob Dylan. Although I can’t recall any TikTok videos with Bob Dylan…

The music label had reached a deal with TikTok in February 2021, which allowed users on the video app to add clips from UMG’s catalog to their videos.

UMG, the world’s largest music company, had said TikTok accounts for only about 1% of its total revenue.
TikTok said UMG and UMPG catalog represents around 20% to 30% of popular songs, that vary depending on the region.


[ad_2]
Source link