TikTok fight against fake news heats up ahead of EU elections

0
[ad_1]

As the European Parliament elections approach, misinformation and fake news campaigns continue to rise. To combat this issue, social media platform TikTok has announced a new initiative aimed at curbing misinformation, according to Reuters.

The platform announced on Wednesday that it will release a local language app for all EU members, consisting of 27 countries. The initiative, dubbed “election centers,” is a sequel to the app’s 2021 approach to battle misinformation amid elections in Greece, the Netherlands, Poland, Slovakia, and Spain.

“Next month, we will launch a local language Election Centre in-app for each of the 27 individual EU member states to ensure people can easily separate fact from fiction,” TikTok’s head of trust & safety EMEA Kevin Morgan said.

TikTok gears up to battle misinformation during the EU elections in June

TikTok’s local app aims to inform and educate EU voters about the electoral process. The ByteDance-owned platform has reportedly produced educational videos regarding voting. The content will be accessible via the election centers.

“Working with local electoral commissions and civil society organizations, these Election Centres will be a place where our community can find trusted and authoritative information,” Morgan said.

TikTok’s head of trust & safety also noted the app plans to expand its partnership with fact-checkers and launch nine additional media literacy campaigns this year to curb misinformation better. The platform now works with nine fact-checking organizations in Europe.

TikTok also plans to open a mission control space in its Dublin office. The division oversees the election-related content on the app from June 6 to June 9.

TikTok’s popularity is on the rise in every corner of the world. The app is now the fastest-growing social platform in the US. TikTok also currently hosts 134 million users from EU members monthly, and roughly 30% of European Parliament lawmakers use the app. The EU’s Digital Services Act (DSA) obligates every social platform with over 45 million monthly users to tackle misinformation, especially during elections.

Around 400 million EU voters should cast their ballots in June. Meanwhile, EU officials are deeply concerned about the impact of misinformation campaigns and election manipulation. EU Industry Commissioner Thierry Breton warned of “geopolitical instability” and “manipulation of citizens” amid the June elections in the bloc. He also warned about “foreign interference of all kinds,” that aims to target the elections.


[ad_2]
Source link
Nothing Phone (2a) price gets revealed ahead of launch

0
[ad_1]

The Nothing Phone (2a) price just got revealed, ahead of the phone’s launch. Various sources were guessing that the phone will cost around €400, but it may be even more affordable than that.

The Nothing Phone (2a) price gets revealed early

According to folks over at Dealabs, the Nothing Phone (2a) will cost €349 in Europe. That means that it will be €50 more affordable than the original Nothing Phone (1). The Nothing Phone (2) is priced at €679, by the way.

Do note that this is likely the price tag of an 8GB RAM model with 128GB of storage. A 12GB RAM model with 256GB of storage is also rumored, and that one is said to cost €399 in Europe. These price tags are based on info pulled from France, but it should be the same elsewhere too.

Nothing has already confirmed that the device will launch on March 5, Its name has also been confirmed, while we also know that it won’t launch in the US. Well, it won’t launch the normal way. It will, however, be a part of a limited ‘Developer Program’ that we don’t know much about just yet. That’s a shame, as the Nothing Phone (2) did arrive to the States.

This will be a rather capable mid-ranger, based on the leaked specifications

Now, the phone’s specifications did surface as well. The Nothing Phone (2a) is expected to ship with the MediaTek Dimensity 7200 Ultra processor. Both 8GB and 12GB RAM models will seemingly be available.

A 6.7-inch fullHD+ display is rumored, and it will have a 120Hz refresh rate. Android 14 will come pre-installed on the device, along with the company’s Nothing OS 2.5 Android skin.

45W wired charging is also tipped, and the same goes for a dual 50-megapixel camera setup on the back. Those will be wide and ultrawide shooters, it seems. A single 32-megapixel camera is said to be included on the front.

The phone is coming in about half a month, but chances are we’ll get more information at MWC 2024, as Nothing will be there.


[ad_2]
Source link

OpenAI seeks ways to pull the plug on Google and occupy its search engine throne

0
[ad_1]

Sergey Brin and Larry Page’s lovechild – that’s just another way of saying “Google!” – might be in danger. OpenAI is coming for its search engine throne, a new hot rumor has it.

That means in the future, one might be “OpenAI-ng it” instead of “Googling it”, as MSPowerUser states. The source is The Information, citing an anonymous insider which claims OpenAI is currently developing a web search product. The details remain unclear: will the search tool be integrated within the popular ChatGPT platform… or this could be some separate, standalone product.

Regardless, it’s clear that such a move is aimed directly at Google’s search engine hegemony. OpenAI has taken the “Shoot for the stars!” mantra quite literally and it will be very interesting to see what comes out of it.

If it’s real. So far, no confirmation comes from Sam Altman’s project.

Leaks and rumors about OpenAI could turn out to be true, as the company has resorted to hiring investigators to crack down leakers and to “mitigate potential insider threats”.

The undisclosed source declares that the OpenAI search engine tool might utilize Bing, Microsoft’s search platform, “for some of its functionality”. This aligns with Microsoft’s significant investments in OpenAI and its ongoing integration of GPT-based AI into products like Bing Chat and Copilot.

[ad_2]
Source link

Critical DNSSEC Flaw Attacker Bring DNS With Single DNS Packet

0
[ad_1]

A new flaw has been discovered in DNSSEC, which, when exploited by threat actors, could result in the unavailability of technologies such as web browsing, email, and instant messaging. This new class of attacks has been termed “KeyTrap” by researchers. 

Moreover, a threat actor could completely disable large parts of the worldwide internet. KeyTrap attacks affect not only DNS but also the applications using it. The “KeyTrap” class of attacks has been assigned with CVE-2023-50387, and the severity is yet to be categorized.  As of December 2023, 31.47% of the web clients used DNSSEC-validating DNS resolvers worldwide. 

Document
Live Account Takeover Attack Simulation

Live attack simulation Webinar demonstrates various ways in which account takeover can happen and practices to protect your websites and APIs against ATO attacks.

Technical Analysis

This particular vulnerability exists due to the processing of responses from specially crafted DNSSEC-signed zones, which causes CPU exhaustion on a DNSSEC-validating resolver.

Successful exploitation of this vulnerability could significantly affect the resolver’s performance, disrupting the DNS resolution service.

As a workaround, DNSSEC validation can be disabled entirely, preventing this vulnerability. However, this was not a recommended resolution. Additionally, there is no evidence of active exploitation of this vulnerability by threat actors.

To fix this vulnerability, it is advised to upgrade to the following versions of BIND 9 and BIND Supported Preview Edition:

Nevertheless, researchers also stated that “The flaws are not recent,” describing an obsolete internet standard, RFC 2535, from 1999. Fast forwarding to 2012, there was another implementation flaw for DNSSEC validation in standards RFC 6781 and RFC 6840. 

Although this vulnerability has existed for the past 25 years, it went unnoticed by the community due to the complexity of the DNSSEC validation requirements. 

If this vulnerability had been exploited, it would not only result in the unavailability of DNS but also could have potential risks of disabling security mechanisms such as anti-spam defenses, Public Key Infrastructure (PKI), or even inter-domain routing security like RPKI (Resource Public Key Infrastructure).

Furthermore, a complete report about this vulnerability has been published by ATHENE researchers, which provides detailed information about the impact, attack types, vectors, and other information.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

New Xiaomi 14 Ultra images share even more details about the phone

0
[ad_1]

The Xiaomi 14 Ultra renders surfaced yesterday for the very first time. Those images basically revealed the phone’s design to the world. Well, new Xiaomi 14 Ultra images are now here, and they reveal even more details about the device.

New Xiaomi 14 Ultra images give us even more details about the upcoming flagship

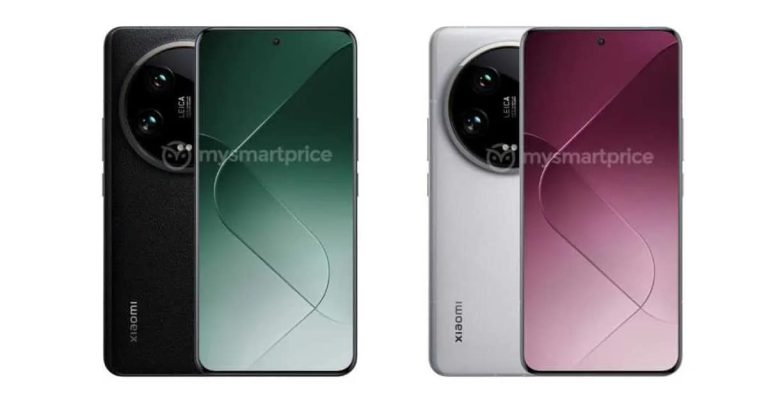
Yesterday’s shots did show us the phone from all sides except for one… its front. Well, these images from MySmartPrice do change that. Two images have appeared, as you can see below this paragraph.

Xiaomi 14 Ultra front and back leak

They’re showing both the black and white colors of the Xiaomi 14 Ultra. Those are seemingly the only colors that are coming. They will both have a vegan leather backplate, based on what we’ve seen thus far. There are some rumors about glass models too, but we’re not sure about that.

The display will be flat, it seems

In any case, these images of the device do show us both the front and the back sides. Based on these images, the display won’t be curved as we thought it would. The panel itself seems to be flat, but the curve towards the sides is there. So basically the sides will be curved, but the display won’t, at least that’s what it looks like here

The Xiaomi 14 Ultra will follow in the Samsung Galaxy S24 Ultra‘s footsteps, kind of. Samsung’s flagship also switched to a flat display this year. Xiaomi seems to be going the same route.

The bezels around the display are very minimal, and they actually seem to be uniform, but we cannot confirm that just yet. All the physical buttons sit on the right-hand side, and the camera is centered at the top of the display.

The camera island does seem very similar to the one included in the Xiaomi 13 Ultra

The camera island on the back will look very similar to last year, in terms of the sensor arrangement on the inside. Four cameras will be present on the back, but the back side of the phone will be flat. On the Xiaomi 13 Ultra, the back side gradually rises in height towards the camera island. That’s not the case here, it seems.

The Xiaomi 14 Ultra will launch on February 25 for global markets. It will launch at MWC 2024 in Barcelona. There is some talk about a February 22 launch in China, but that event is not official yet.


[ad_2]
Source link

Privacy-first DuckDuckGo browser adds password sync feature

0
[ad_1]

DuckDuckGo, the company behind the privacy-oriented search engine and web browser of the same name, has introduced a new Sync & Backup feature for its browser. It lets you sync your saved passwords, bookmarks, and Email Protection settings across multiple devices. In line with the firm’s privacy-first approach, the feature doesn’t require an account to sync the information.

DuckDuckGo browser can now sync saved passwords across your devices

DuckDuckGo isn’t a household name in the browser world but is fairly popular among privacy-conscious users. It takes pride in being extremely privacy-oriented while still offering most of the features you expect from a web browser if not all. One of its biggest drawbacks was the lack of a password sync feature. People using DuckDuckGo for privacy couldn’t access their saved passwords across their devices.

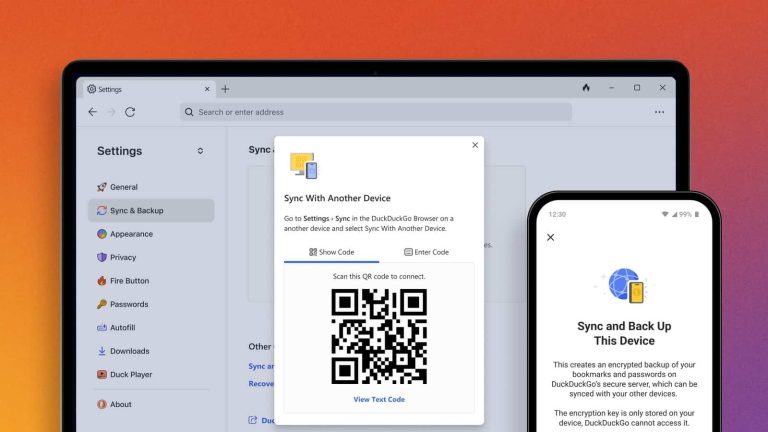
The company has now addressed this limitation. With the new Sync & Backup features, you can find your saved passwords, bookmarks, and more on the DuckDuckGo browser on all of your Android or iOS phones, tablets, and computers. However, since it doesn’t require an account, you will have to manually link all your devices to sync the information. Follow the steps below to do that.

Once you have updated DuckDuckGo to the latest version, click on the three vertical dots in the top-right corner and select Settings. Tap on Sync & Backup and select Sync With Another Device. If asked, unlock your device to verify your identity. Now, repeat these steps on all of your devices. On phones or tablets, you will see a QR code. On laptops and desktop computers, you will find an alphanumeric code.

Scan the QR code on one device from the other or manually enter the alphanumeric code to sync the devices. If only one of your devices synced, go back to the unsynced device and select Sync and Back Up This Device under the Single-Device Setup menu in Sync & Backup. This should sync the device with others. You will find a list of all your synced devices here. You can edit device names and adjust your settings.

DuckDuckGo Sync feature 2

Your data is end-to-end encrypted

DuckDuckGo makes you sync your devices manually to protect your privacy. This ensures that your data remains end-to-end encrypted throughout the process. “Your passwords are completely inaccessible to anyone but you,” the company assures. “That includes us: DuckDuckGo cannot access your data at any time,” because the unique key needed to decrypt it is stored locally on your devices.

This means DuckDuckGo can’t help you recover the saved data in case you lose or damage your devices. Thankfully, there is a workaround that works locally. When you first set up Sync, you will be asked to download a Recovery PDF. The document contains your recovery code. You have to scan this code to recover your passwords and other saved data on DuckDuckGo. Make sure to store this document securely on some other device.

DuckDuckGo Sync feature 3


[ad_2]
Source link

Xbox February update adds touch controls for remote play on Android and iOS

0
[ad_1]

Whether you’re rocking an iPhone or an Android phone as your daily driver, you are no longer limited to playing games specifically designed for smaller screens. Microsoft promised last month that it will make it possible to play games on iOS and Android devices without having to use a controller.

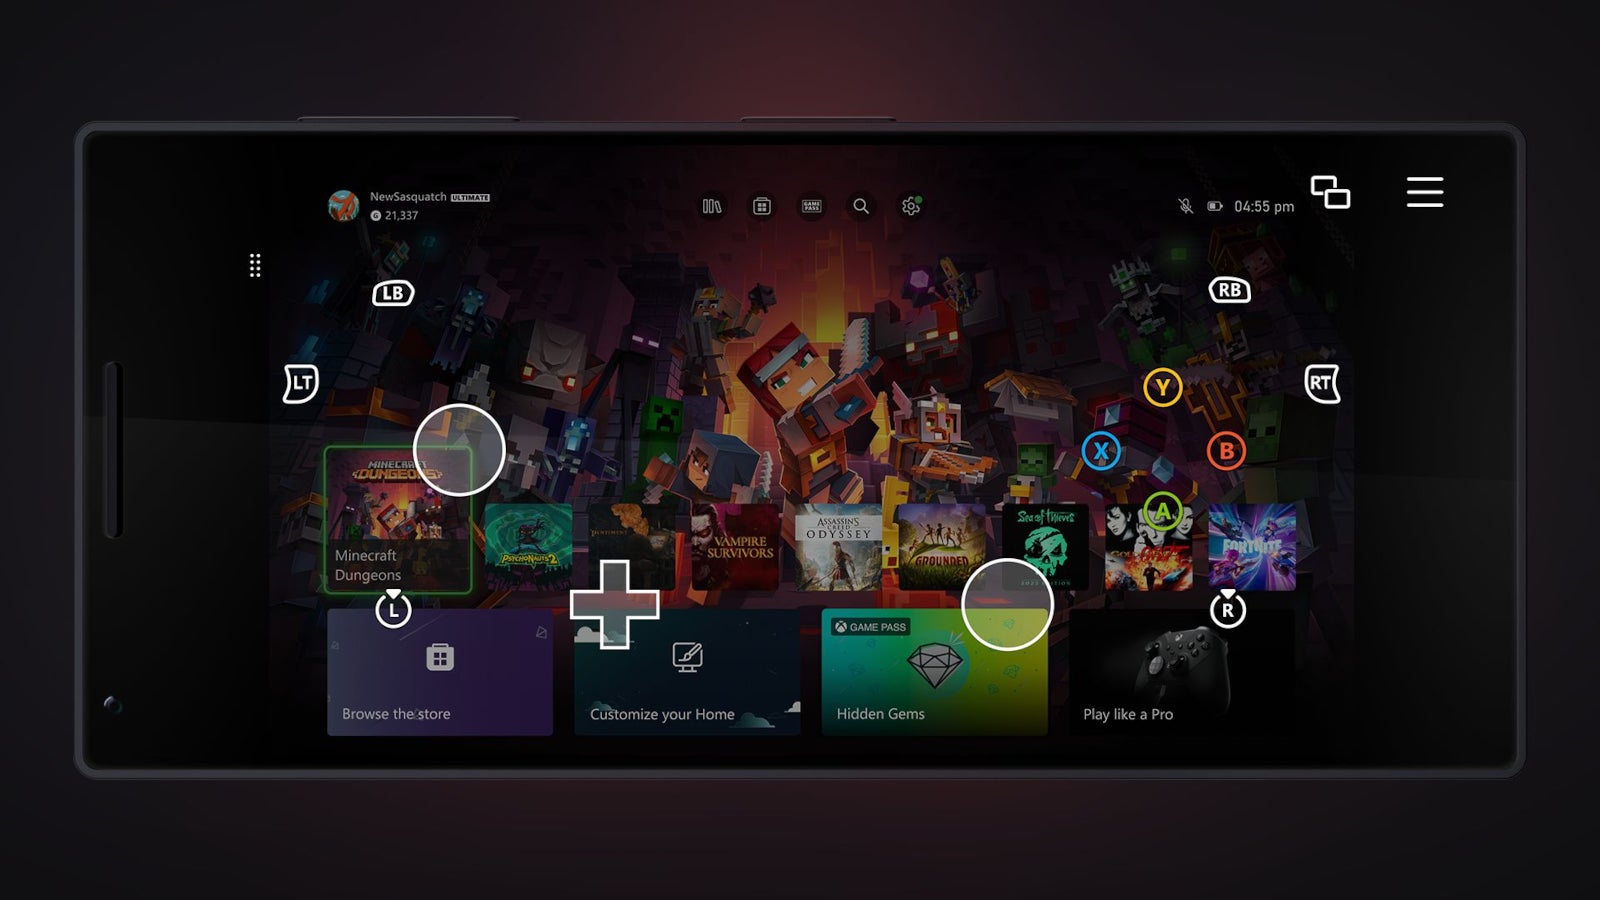
Today, the Xbox February update is bringing the much-needed touch controls for remote play with the iOS and Android Xbox apps. This means that even if you don’t have an Xbox Wireless Controller, you can now play games when away from your console.

The same custom touch layouts available through Xbox Cloud Gaming (Beta) are now available when remotely playing games from your Xbox console. The vast majority of games support touch controls, including Minecraft Dungeons, Psychonauts 2, and Sea of Thieves.

In fact, Xbox remote play supports custom touch control layouts on more than a hundred games when using the Xbox app on iOS, Android, and Windows devices.

Besides adding touch controls in Xbox remote play, the latest Xbox update brings a new thumbstick calibration tool for Xbox Wireless Controllers, as well as improved filtering and sorting in My games & apps.

[ad_2]
Source link

Microsoft Patch Tuesday 2024 : 73 Security Flaws

0
[ad_1]

As part of its February 2024 Patch Tuesday updates, Microsoft has published patches to address 73 security flaws, including two zero-day vulnerabilities that have been actively exploited.

Five of the 73 vulnerabilities are classified as ‘Critical’, 65 as ‘Important’, and three as ‘Moderate’ in severity.

Document
Live Account Takeover Attack Simulation

Live attack simulation Webinar demonstrates various ways in which account takeover can happen and practices to protect your websites and APIs against ATO attacks.

Two Zero-Days Patched

The two vulnerabilities identified as being actively targeted are:

CVE-2024-21351 – Windows SmartScreen Security Bypass

The vulnerability, which has a CVSS score of 7.6, enables an attacker to insert code into SmartScreen and perhaps acquire code execution. This could result in some data disclosure, a lack of system availability, or both. 

“An authorized attacker must send the user a malicious file and convince the user to open it,” Microsoft said.

Thus, if this vulnerability was successfully exploited, an attacker could bypass the SmartScreen user experience. 

Microsoft does not disclose the widespread of these attacks, although it is anticipated that the number of exploits will rise.

CVE-2024-21412 – Internet Shortcut Files Security Feature Bypass Vulnerability

“An unauthenticated attacker could send the targeted user a specially crafted file that is designed to bypass displayed security checks,” Microsoft.

In this case, it would be impossible for the attacker to convince a user to see content that they controlled. In addition, by clicking on the file link, the attacker would have convinced them to take action.

As a result, the attacker must convince the victim to open a malicious file that they sent them.

According to a Trend Micro report, the Water Hydra APT is using the vulnerability to infect victims with the malware DarkMe. 

After developing a proof-of-concept (PoC) for additional testing, the researchers found that the original shortcut bypassed the CVE-2023-36025 patch while evading SmartScreen security measures.

Critical Security Flaws Addressed

Five critical vulnerabilities, including those involving privilege elevation (CVE-2024-21410), denial of service (CVE-2024-20684), remote code execution (CVE-2024-21357, CVE-2024-21413), and information disclosure (CVE-2024-21380) are fixed in this Patch Tuesday.

Other vendors, in addition to Microsoft, have also provided security upgrades in recent weeks to address multiple vulnerabilities. These firms include Google, Adobe, Cisco, ExpressVPN, Ivanti, Fortinet, Linux, SAP and JetBrains.

The complete list of the 73 Microsoft CVEs may be found here.

Stay updated on Cybersecurity news, Whitepapers, and Infographics. Follow us on LinkedIn & Twitter.


[ad_2]
Source link

Do you hate voice messages? Skype announces Audio Transcription feature and makes them into text

0
[ad_1]

If you find yourself often in noisy environments, or you’ve got hearing problems, or you haven’t got the time to listen to lengthy voice messages – or you simply hate it when your friends bombard you with 60-second “uhhhh”/“uhmmmm”-plagued voice messages that actually contain 2 lines of meaningful information – well, Skype has you covered.The once-almighty chat platform announces the new Audio Transcription feature that converts voice messages into text for improved clarity and accessibility (via MSPowerUser). Users can activate transcription with a tap, seeing both audio waveform and text simultaneously.

Thanks to Skype’s latest Insider build (8.113) the new feature for improved accessibility and clarity in audio messaging (Audio Transcription) is accessible: it allows users to convert voice messages into text format, enhancing message comprehension and facilitating communication for users with hearing impairments.

“Moreover, Skype also introduced a top menu selector for easier navigation between reaction categories, eliminating the need for extensive scrolling. The user-friendly design features readily accessible favorite reactions and expands the emoticon library with more options for expressive communication”, the report reads.

These features are currently available in the Insider build and are expected to be released to the broader user base in the near future!


[ad_2]
Source link

New York Mayor sues Instagram, YouTube, TikTok parent companies over youth mental health crisis

0
[ad_1]

Eric Adams, Mayor of New York City, said that his administration has filed a lawsuit against social media companies for fueling mental health crisis among the youth (via Reuters).

The lawsuit includes Facebook and Instagram’s parent company Meta, as well as YouTube’s Google (legally known as Alphabet), Snapchat’s Snap Inc. and TikTok’s ByteDance. The lawsuit is filed in the California Superior Court and alleges that the companies intentionally designed their platforms to “purposefully manipulate and addict children and teens to social media applications”.

“Over the past decade, we have seen just how addictive and overwhelming the online world can be, exposing our children to a non-stop stream of harmful content and fueling our national youth mental health crisis”, Adams said in a statement.

This is far from the first time that social media giants are hit with similar lawsuits – they’ve come under intense scrutiny as regulators push them to protect children from harmful content. Meta, TikTok and YouTube already face hundreds of lawsuits filed on behalf of children and school districts over the addictiveness of social media, the report reads.

Just last month Meta CEO Mark Zuckerberg apologized to families at a US Senate hearing about the impact that social media has on children.

Per their own spokesperson, Meta says they wanted teens to have “safe, age-appropriate experiences online”, while TikTok said it will continue to work to keep the community safe by tackling industry-wide challenges.

Alphabet (read Google, YouTube) denied the allegations: “We’ve built services and policies to give young people age-appropriate experiences, and parents robust controls. The allegations in this complaint are simply not true”, Google’s spokesperson Jose Castaneda said in a statement.


[ad_2]
Source link