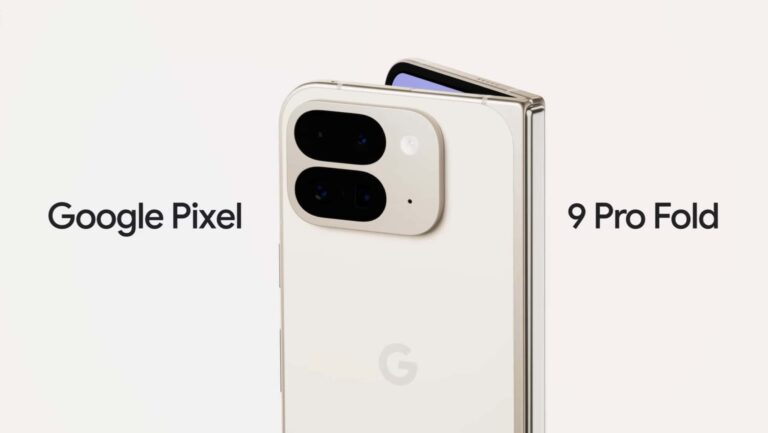
Google’s Pixel 9 Pro Fold is getting a larger 6.24-inch Outer Display

0
[ad_1]

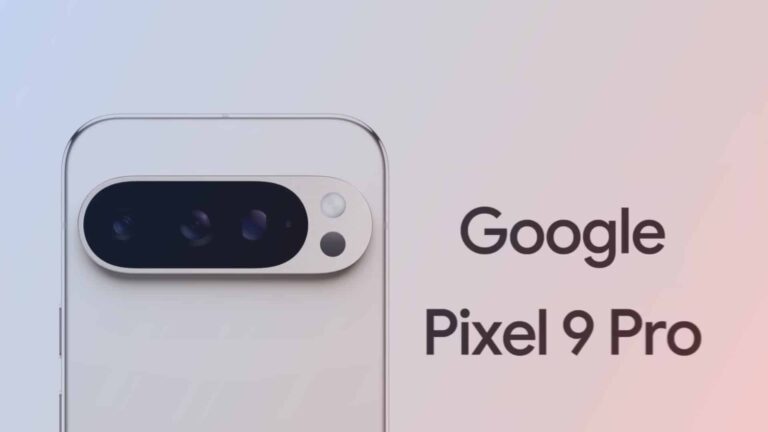
Next month, we’re expecting Google to finally take the wraps off of the Pixel 9 Pro Fold. Even though they’ve already teased it in a video a few weeks ago. This time around, Google is looking to go with a taller cover display, which is going to change the aspect ratios of both displays.

According to Android Authority, the Pixel 9 Pro Fold is going to sport a 6.24-inch display, at a resolution of 2,424 x 1080. Versus the 5.8-inch 2,092 x 1080 resolution of the original Pixel Fold. It is also getting a much needed brightness boost, now at 1,800 nits of brightness for HDR content – which means peak brightness is likely even higher.

The main display is also changing, and will now be an 8-inch display with a resolution of 2,152 x 2,076 and a brightness boost of up to 1,600 nits for HDR. This is a tiny bit larger, and closer to being a square, much like many other foldables.

aaa2 840w 472h png

Google’s making the OnePlus Open

Based on what we have seen so far, it really sounds and looks like Google is making the Pixel 9 Pro Fold much more like the OnePlus Open (or OPPO Find N3). And I’m perfectly fine with that. The OnePlus Open is an insanely good foldable, even a year later. The screen sizes are a tad different between the OnePlus Open and Pixel 9 Pro Fold, so it’s not quite a carbon copy, but close enough.

Now with these changes, Google is also changing how many of us use your foldable – if we’ve only used a Pixel Fold. Because of the short and wide cover display, when you opened the Pixel Fold, it was more of a landscape tablet, which means you were already in tablet mode for apps that supported it. Versus other foldables that require you to rotate the phone to get into tablet mode.

We should know more about the Google Pixel 9 Pro Fold come August 13, when Google is expected to announce the entire Pixel 9 lineup. Which includes the Pixel 9, Pixel 9 Pro, Pixel 9 Pro XL and Pixel 9 Pro Fold.


[ad_2]
Source link

How AI is Changing the Game

0
[ad_1]

In today’s world, as it globalizes, video content creators are under increasing pressure to make their creations available to an ever more diverse international audience. It is now much easier to translate videos with the advent of technology mayflies and Artificial Intelligence (AI) rising. We no longer speak of it as being a difficult or hard task. Innovative tools powered by AI, like the Rask AI Platform, are leading the way in this changed scene.

Video creators can, therefore, extend social media by giving their material actual global reach. Through such platforms, a lot of different features are supported: real-time translation, many video platforms, and localizing videos into multiple languages. This happens most strikingly through these functions, which enable creators to overcome language barriers and reach out to a variety of linguistic and cultural communities around the world.

Best Video Translation Apps

Here is the original list of top AI-driven video translation tools, which are aimed at helping content creators bring their video content to the world. These online video software options are based on the latest new techniques in neural networks and designed right from the metal up to do a full translation that is authentic and fast.

Accurate video translation software like these translation apps can make sure that your audio and video content are both identifiable and understandable for listeners anywhere in the world all in any lingual context it’s being received. On this list, all video translator apps offer some unique form of special service (or at least a unique peeking feature) that enables creators to handle their video content soundly with ease.

The Rask AI Platform: A Pioneer in AI Video Translation

AI

As for the Rask AI Platform, it is the pioneer in video translation technology. Relying on the most skilled AI, this tool will help preserve video translation that looks perfectly fine. Its annealing innovation bridge makes a new connection for the video-translating content creator and his global clientele. This is the best video translator platform. The program does not only automatically translate subtitles expertly into a variety of languages. It also composes in those same languages and presents what are possibly accurate renditions.

By installing Rask AI, the best video translator software, for those who test to see where their videos are instantly translated into another language and given back quickly. It has a friendly interface and works very fast. You can upload videos from any source, let the app know what language you want them translated into and in just a few clicks will have translated subtitles ready for you. It is easy to use and is available now. For further information, please click here!

Auto AI Translator

The market-leading Auto AI video translator is focusing on bringing real-time translation to live content. In an environment like this, where the noise level is so high that you cannot hear what people are actually saying at all, along with the world’s most advanced text-to-speech recognition technology, the machine is able to accurately identify voices or map sound into characters.

Naturally, when it comes to live events it need hardly be said that this is indispensable. It’s machine translation technology, based on the most advanced neural networks that are able to comprehend different dialects and intonations. The new level of technology changes the game entirely for broadcasters and content providers worldwide who need fresh, translated solutions immediately at any time.

In addition, Auto AI Translator includes functions of automatic speaker recognition and contextual understanding to try to ensure the flow and clarity of subtitles in a fast-paced live interaction.

VideoTranslate

As well as doing transcriptions and translations, VideoTranslate provides a full range of service packs, which are all matters needed by global content creators. It is also an added convenience for businesses that produce a lot of content, in particular, because this function allows for single-button batch translating, effectively saving labor and waiting time.

When VideoTranslate works with speech recognition and machine translation to match the dubbing tracks with the original voiced source record video, viewers listening to translated video and audio can enjoy a seamless experience. The interface is user-friendly, making all those people who’ve never done video translation feel they get to grips at once.

Translate Your World

Translate Your World is an online video editor that is specifically tailored for real-time interpretation of live speech and webinars. It translates into more than 100 different languages altogether. With real-time speech translation that can be streamed to audiences all over the globe, as a speaker and audience member, the whole world translates with you! The real-time interpretation device employing advanced AI technology and a minimal delay works great for international conferences or educational lectures.
As Internet speeds continue to increase all around the world, everyone now has good broadband. Whether you have a slow or high-speed modem, as long as you can directly access the internet, TYW will offer a perfect translation globally. Furthermore, Translate Your World has interactive features that help the live users feel more “live”: real-time speaking, switching to another language, and feedback instruments for people who are not sitting in the audience but rather at home or in a classroom. This video translator also lets you adjust subtitles. Namely, organizers can set font size and color groups.

The Impact of AI on Video Translation

Labor-intensive manual input for video translation is now a thing of the past because artificial intelligence makes such work much more efficient than any human ever could. AI, which translates video by using the soundtrack itself as audio content can, working at utmost efficiency if not accuracy only, extract words spoken (but in text form). Through this function, broadcasts around the world can be instantaneously translated and make updates widely available to a global audience.

Using artificial intelligence technology leads not only to faster but better quality translations. Through continual learning and incremental improvement by AI models, they now possess a deep understanding of nuance in language and idiomatic expressions, as well as cultural background. The result is translations much closer to what the author originally meant than you would otherwise expect.

Further, AI provides a means of maintaining consistency in terminology and style across a large database of materials, such as native language resources and glossaries for media use or teaching and learning purposes. With AI-based video translation tools gaining popularity, even smaller creators and companies are now able to afford multilingual content creation.

Challenges and Future Prospects for AI Video Translation

The incorporation of AI in audio and video translation also carries with it more drawbacks. A prime example of this is that in each language, folks tend to imply a wealth of detail: differences in dialect, in accent, in a large context such as the culture where an expression was made.
In order for translation to be both accurate and sensitive to culture, the desire for such detail must depend on efforts. Furthermore, the strengths of AI translation are inevitably diminished by technical limitations such as background noise and whether there are two speakers speaking at the same time.

How do we meet the challenge in such situations? The future looks promising for video translation with AI. These advances are aimed at reducing as far as possible the need for human participation and giving more autonomy to machine translation systems.

Best Video Translation Tools: Conclusion

As digital connections between cultures grow, the demand for video translation services can only increase. Video translator apps like Rask AI Platform have been at the front of this sea change. They can help social media video creators and even consumers knock down language barriers to make communication more effective. As AI technology continues to advance, the future of video translation online tools is boundless. We might expect a day when video content is available to everyone worldwide on equal terms and speaks the same language as its audience.

[ad_2]
Source link

BlueStacks Emulator For Windows Vulnerability Exposes Millions Of Gamers

0
[ad_1]

A significant vulnerability was discovered in BlueStacks, the world’s fastest Android emulator and cloud gaming platform. When used against a victim, this gives attackers complete access to the machine.

The American technology business BlueStacks, also known as BlueStacks by now.gg, Inc., is well-known for developing the BlueStacks App Player and other cloud-based cross-platform applications.

The BlueStacks App Player allows Android applications to run on devices running Microsoft Windows or macOS. 

BlueStacks exchanges virtual machine configuration files amongst several OS users and keeps them in a world-writable directory, which makes it feasible for an unauthorized user to backdoor an image and obtain privileged user code execution capabilities.

Join our free webinar to learn about combating slow DDoS attacks, a major threat today.

Understanding The Vulnerability

The critical flaw is identified as BlueStacks privilege escalation via virtual machine backdooring tracked as CVE-2024-33352.

An attacker can automatically add executable code to the virtual machine by changing the BlueStacks configuration.

This allows the attacker to create a backdoor that will launch whenever an authorized user launches the emulator. 

Later, the code may be made to escape Virtual Box and enter the host operating system by reconfiguring the shared directory settings to include the entire C drive.

The attacker would edit the file on the C drive and alter it to enable a virtual machine escape, giving them complete access to the Windows filesystem.

Hence, the attacker installs malicious software on the Android virtual machine (VM), which has the ability to deliver a payload into the host system’s startup directory. 

This payload is run with the victim’s privileges when the victim restarts their computer, granting the attacker complete control.

The vulnerability was brought to light by researcher Maciej Miszczyk. BlueStacks for Windows (versions prior to 10.40.1000.502) are affected.

Protect Your Business Emails From Spoofing, Phishing & BEC with AI-Powered Security | Free Demo


[ad_2]
Source link

Check out all 3 Google Pixel 9 smartphones in this Latest Leak

0
[ad_1]

We are now less than three weeks away from Google’s upcoming Pixel launch, which is currently set for August 13 in Mountain View, California. This means the leaking faucet that is Google is in overtime now. This morning, Evleaks posted a render showing off the Pixel 9, Pixel 9 Pro, and Pixel 9 Pro XL side-by-side, which can really show us how thin the bezels are on these new phones. And the answer is, very thin.

It’s a low-resolution render, so we can’t see a whole lot on this one, but it does match up the very many other leaks we’ve seen. As well as real life video and pictures that we’ve seen lately. From here we can see that the Pixel 9 is the same size as the Pixel 8, with the Pixel 9 Pro also being that same size. And then there’s the Pixel 9 Pro XL which is the same size as the 6.7-inch Pixel 8 Pro.

This is a new strategy for Google this year, offering two “Pro” slab phones this year in different sizes, which is similar to what Apple does. They offer two different iPhones and then two different sizes of each. This is also likely going to be a way for Google to up the price once again, at least on the Pixel 9 Pro XL. Although, the Pixel 9 Pro could also sit nicely in between the two models, price-wise.

GTQ2m9xXgAAdEAK

Google is finally giving everyone a flagship, small phone

While not as small as some would like, the Pixel 9 Pro is going to be a hot seller for being a flagship small phone. The only other competition there is, is the Galaxy S24. With this phone, we’re going to see a triple camera setup on the rear, and with Google’s computational photography, that should be incredible. It will also sport the Tensor G4 chipset, which we are hoping for some big performance and efficiency gains this year.

We’re likely to see many more leaks of the Pixel 9 series in the coming days and weeks, as Google’s event is still a little less than three weeks away. And we all know how good Google is at keeping a lid on leaks.


[ad_2]
Source link

iPhone 18 series may use a new Samsung’s camera sensor

0
[ad_1]

Apple could change its strategy regarding the camera supplier for its iPhone devices. The Cupertino giant has been working exclusively with Sony in this section for years. However, a new report suggests that Samsung will become a new iPhone camera sensor supplier for Apple in the coming years.

Ming-Chi Kuo, a renowned industry analyst, posted on X/Twitter that Apple and Samsung already have an agreement for an advanced camera sensor. Samsung would even have already established a team exclusively dedicated to development.

Samsung to ship the new iPhone camera sensor in 2026

According to the report, it will be a “1/2.6-inch 48MP ultra-wide CMOS” sensor. The post specifically mentions that it will be an “ultra-wide” sensor, something that also reflects its size. For reference, the iPhone 15 Pro Max ultra-wide sensor has a size of 1/2.55″, slightly larger than the leaked one.

So, it’s possible that Apple will turn to Samsung for a new advanced ultra-wide lens, but continue to collaborate with Sony for the main sensor of its iPhone devices. Be that as it may, the news would be a hard blow for Sony, which would lose some presence in tens of millions of iPhone devices annually. Currently, the Japanese company monopolizes the entire camera system of iPhone devices. However, now Samsung could join the equation by bringing the ultra-wide sensor.

Samsung would start shipping the new camera sensor in 2026, so Apple could implement it in the iPhone 18 series. Kuo’s report does not offer additional details about Apple’s reasons for the change in strategy. However, Sony has been losing some ground in some flagship mobile devices in recent years. For example, brands like Xiaomi or Huawei have used Omnivision sensors in their high-end devices. In any case, the Xiaomi “Ultra” lineup still trusts Sony for its main camera.

Perhaps the change in strategy is due to the fact that Apple plans to incorporate new image technologies and only Samsung was capable of doing so. It is also possible that the company is optimizing costs. Be that as it may, more details may emerge in the future.


[ad_2]
Source link

Chinese Hackers Using Shared Framework To Create Multi-Platform Malware

0
[ad_1]

Shared frameworks are often prone to hackers’ abuses as they have been built into various applications, which offer a range of systems that can be exploited at the same time.

By attacking shared framework vulnerabilities, hackers can get into many apps and information stores, which escalates their malicious acts in terms of efficiency and scale.

Cybersecurity researchers at Symantec recently discovered that Chinese hackers have been actively abusing the Shared Framework to create Windows, Linux, macOS, and Android malware.

Chinese Hackers Using Multi-Platform Malware

The malware toolkit of the Daggerfly espionage group has been refreshed by adding new versions of already known threats and a previously unattributed macOS backdoor.

Join our free webinar to learn about combating slow DDoS attacks, a major threat today.

The latest attacks against the targets in Taiwan and a US NGO in China are examples of how the group’s tactics have evolved, including the exploitation of an Apache HTTP Server vulnerability.

This development shows that Daggerfly continues to evolve and remains involved in international and domestic spying operations, extending its decade-long history in the cyber field.

Macma is a macOS backdoor that was first documented in 2021. It has been active since 2019 and is continuously developing.

Watering hole attacks in Hong Kong were the initial distribution channels through which it exploited loopholes to install itself into macOS devices.

According to a recent Symantec analysis of different Macma variations, its functions change meaningfully with time, consequently comprising newly updated modules, improved file paths, heightened logging, and other features such as better screen-capture capabilities.

These ongoing developments depict a relentless threat by the Macma backdoor, which has a proven ability of targeting macOS systems.

New evidence links the Macma macOS backdoor to the Daggerfly threat group. Symantec discovered shared command-and-control infrastructure between Macma variants and a MgBot dropper. 

While Macma and other known Daggerfly malware share code from a common library, which provides functionality across multiple platforms. 

This shared codebase and infrastructure strongly suggest that Macma is part of the Daggerfly toolkit, marking a significant development in attributing this previously unaffiliated backdoor to a specific advanced persistent threat group.

Daggerfly’s toolkit now includes a sophisticated Windows backdoor called Suzafk (aka Nightdoor or NetMM). 

This multi-staged malware uses TCP or OneDrive for command and control, employs anti-analysis techniques, and shares code with other Daggerfly tools. 

Suzafk’s capabilities include remote command execution, persistence via scheduled tasks, and encrypted configuration storage. 

This addition, along with evidence of malware targeting various operating systems, including Android and Solaris, demonstrates Daggerfly’s advanced capabilities and adaptability in conducting espionage activities across multiple platforms.

IoCs

IoCs (Source – Symantec)

Protect Your Business Emails From Spoofing, Phishing & BEC with AI-Powered Security | Free Demo


[ad_2]
Source link

TracFone will pay $16 million to settle FCC data breach investigation

0
[ad_1]

Following three separate data breaches between 2021 and 2023 which exposed the proprietary information (PI) of TracFone Wireless customers, the Federal Communications Commission (FCC) announced that the Verizon-owned company has agreed to pay a $16 million civil penalty to settle the government investigation, and it has made an agreement to improve its application programming interface  (API) security.

TracFone Wireless Inc. is an American prepay wireless service provider wholly owned by Verizon. TracFone services are used by the brands Straight Talk, Total by Verizon Wireless, and Walmart Family Mobile.

The settlement ends an investigation into TracFone’s security practices to uncover whether the breaches were the result of ineffective cybersecurity protocols. The Enforcement Bureau (EB) of the FCC found that cybercriminals gained access to certain TracFone customer information, including PI and customer proprietary network information (CPNI), by exploiting vulnerabilities related to customer-facing APIs.

APIs allow different computer programs or components to communicate with one another. When the security behind the APIs is not secure enough, cybercriminals can abuse them to gather information without authorization.

The FCC media release explains in detail that it is possible to leverage numerous APIs to access customer information from websites. And according to the FCC’s own Enforcement Bureau, that is exactly what happened at TracFone.

In addition to the civil penalty, the FCC secured extra assignments for TracFone in the Consent Decree:

  • TracFone has to deploy a mandated information security program, with novel provisions to reduce API vulnerabilities in ways consistent with widely accepted standards, like those identified by the National Institute of Standards and Technology (NIST) and the Open Worldwide Application Security Project (OWASP).
  • TracFone must improve protection measures against SIM-swapping. SIM swapping (and the very similar port-out fraud) is the unlawful use of someone’s personal information to steal their phone number and swap or transfer it to another device. With this, criminals can intercept calls, messages, and certain multi-factor authentication (MFA) codes.
  • TracFone has to undergo annual assessments—including by independent third parties—of its information security program.
  • Employees and certain third parties are to receive privacy and security awareness training.

The Enforcement Bureau reported to the FCC that:

“After gaining access to customer information during one of the three breaches, the threat actors completed an undisclosed number of unauthorized port-outs.”

 All this occurs as the FCC has continued a mission against SIM-swapping.

Protecting yourself after a data breach

There are some actions you can take if you are, or suspect you may have been, the victim of a data breach.

  • Check the vendor’s advice. Every breach is different, so check with the vendor to find out what’s happened and follow any specific advice they offer.
  • Change your password. You can make a stolen password useless to thieves by changing it. Choose a strong password that you don’t use for anything else. Better yet, let a password manager choose one for you.
  • Enable two-factor authentication (2FA). If you can, use a FIDO2-compliant hardware key, laptop or phone as your second factor. Some forms of two-factor authentication (2FA) can be phished just as easily as a password. 2FA that relies on a FIDO2 device can’t be phished.
  • Watch out for fake vendors. The thieves may contact you posing as the vendor. Check the vendor website to see if they are contacting victims and verify the identity of anyone who contacts you using a different communication channel.
  • Take your time. Phishing attacks often impersonate people or brands you know, and use themes that require urgent attention, such as missed deliveries, account suspensions, and security alerts.
  • Consider not storing your card details. It’s definitely more convenient to get sites to remember your card details for you, but we highly recommend not storing that information on websites.
  • Set up identity monitoring. Identity monitoring alerts you if your personal information is found being traded illegally online, and helps you recover after.

Check your exposure

You can verify whether your information is available online due to data breaches by using the Malwarebytes Digital Footprint portal. Just enter your email address (it’s best to submit the one you most frequently use) to our free Digital Footprint scan, and we’ll give you a report. For those whose information was not included, you’ll still likely find other exposures in previous data breaches.


We don’t just report on threats – we help safeguard your entire digital identity

Cybersecurity risks should never spread beyond a headline. Protect your—and your family’s—personal information by using identity protection.


[ad_2]
Source link

How to use AI Portrait Studio on Samsung Galaxy Z Fold 6

0
[ad_1]

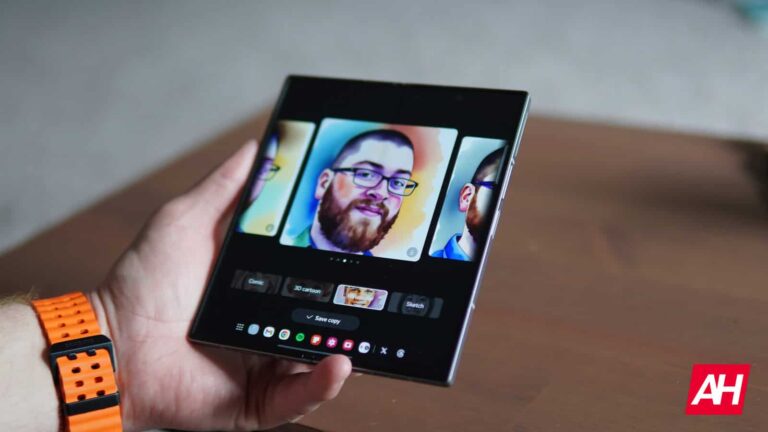
Samsung’s Galaxy AI was announced earlier this year with the Galaxy S24 series. Now, with the new Galaxy Z Flip 6 and Fold 6, Samsung is bringing even more AI features to its phones, including an AI Portrait Studio. This is actually a pretty fun tool to have in your photo editor, as it can transform your selfies into cartoons, comics, watercolors, or sketches. And it’s actually super easy to do.

What is AI Portrait Studio?

AI Portrait Studio is a new feature within the Generative Edit suite in Galaxy AI. It’s only available in Samsung’s Gallery app. For now, it can transform your selfies into a comic, 3D cartoon, watercolor, or sketch. We fully expect Samsung to add more in the future.

Currently, you can’t do regular edits in the AI Portrait Studio, like brightening the foreground or background or changing the beauty filter. That will likely come in the future. Though some of that you can do already without AI.

How to use AI Portrait Studio?

To get started, first take a selfie or a picture of someone else.

Next, open that photo in the Gallery app.

Screenshot 20240724 124051 Gallery

From here, you’ll want to tap on the Generative Edit icon at the bottom of the screen.

Screenshot 20240724 124101 Photo Editor

Once that loads up, you’ll see a button called “Portrait Studio” on your picture itself. Tap on that.

Screenshot 20240724 124106 Photo Editor

Here, you’ll see four options at the bottom: Comic, 3D Cartoon, Watercolor, and Sketch. Tap on the one you want to generate. Then tap on the blue and green generate button at the bottom.

Screenshot 20240724 124131 Photo Editor

After a few seconds, it’ll provide you with four options that you can select and download. If you don’t like any of them, you can tap on “Generate” again at the end of the pictures that it provided.

You can repeat that for each option in the AI Portrait Studio, there’s really no limit on how many times you can do this, as you might have expected.

And that’s it. That’s the AI Portrait Studio in Galaxy AI.


[ad_2]
Source link

Beware Of Malicious Python Packages That Steal Users Sensitive Data

0
[ad_1]

Malicious Python packages uploaded by “dsfsdfds” to PyPI infiltrated user systems by exfiltrating sensitive data to a Telegram bot likely linked to Iraqi cybercriminals. 

Active since 2022 and containing more than 90,000 Arabic messages, it has functioned as both a command-and-control center and an underground marketplace for social media manipulation tools. 

It highlights a broader cybercriminal network, emphasizing the need for in-depth investigation and collaboration within cybersecurity communities.

A malicious script scans the victim’s file system, particularly the root directory and DCIM folder, targeting files with extensions like .py, .php, .zip, .png, .jpg, and .jpeg.  

Once found, the script transmits both file paths and the actual data (files and photos) to the attacker’s Telegram bot without the user’s awareness. This is achieved through a hardcoded Telegram bot token and chat ID within the script, revealing the attacker’s infrastructure details.

Join our free webinar to learn about combating slow DDoS attacks, a major threat today.

Python Packages Data Exfiltration

Analysis of the exfiltrated data revealed hardcoded credentials for a Telegram bot used by the attackers.

Exploiting these credentials, researchers gained direct access to the bot and observed a significant activity history stretching back to at least 2022. 

The messages, primarily in Arabic, provided clues about the bot operator’s location and operations. By analyzing message language and content with tools like GitHub’s TeleTracker, researchers identified the operator as likely being based in Iraq. 

The bot’s activity suggested it was part of a network of bots controlled by the same actor.

Initially, the bot functioned as an underground marketplace, offering various illicit services, which included purchasing social media engagement metrics like views and followers, spam services, and discounted subscriptions to streaming platforms like Netflix.

An investigation into a malicious Python package revealed a hidden Telegram bot, while further analysis of the bot’s message history uncovered evidence of a broader cybercriminal operation.  

The messages hinted at financial theft and appeared to originate from compromised systems, suggesting the packages were a successful initial attack vector and highlighting the need for a deep investigation into cybersecurity. 

In reality, the malicious packages that appeared to be isolated did in fact serve as the entry point to a more complex criminal network that was based on Telegram. 

Researchers at Checkmarx uncovered malicious Python packages on PyPI that exfiltrated user data to a Telegram bot. This exposed a larger Iraqi cybercriminal network and highlighted the dangers of a compromised developer machine. 

In an enterprise setting, such a breach could provide attackers with an initial foothold to launch further attacks within the organization’s network. 

Avoid these four Python packages: testbrojct2, proxyfullscraper, proxyalhttp, and proxyfullscrapers, as they are identified as malicious by exploiting the PyPI repository to install them on unsuspecting systems. 

Once installed, they scrape the files, including potentially sensitive ones like Python scripts, images, and compressed archives, and the stolen data is then sent to a Telegram bot controlled by cybercriminals, which exposes the system to a variety of threats, depending on the criminals’ goals, which could include financial fraud or further system compromise.

Protect Your Business Emails From Spoofing, Phishing & BEC with AI-Powered Security | Free Demo


[ad_2]
Source link

Discover versatility of Ulefone Armor Pad 3 Pro’s built-in HDMI port

0
[ad_1]

Ulefone’s Armor Pad 3 Pro isn’t your average Android tablet. Built to conquer extreme conditions, it’s a testament to rugged innovation. Its adjustable dual 1100-lumen LED lights, massive 33,280mAh battery with 66W charging, reverse charging, and IP68/IP69K and MIL-STD-810H-grade durability are unparalleled. It even offers an HDMI port, adding a new dimension to its usability. The company recently released a video showcasing its applications across various scenarios.

Built-in HDMI port expands the Ulephone Armor Pad 3 Pro’s usability

Whether you’re a construction worker on a dusty job site, a hiker scaling a mountain peak, or simply someone who’s clumsy with electronics, the Ulephone Armor Pad 3 Pro is suitable for everyone. It’s certified to withstand drops, dust infiltration, and complete submersion in water. No more worrying about accidental spills or unexpected downpours. But toughness isn’t everything, and Ulephone knows that. The Armor Pad 3 Pro is a powerhouse of a tablet.

Ulefone Armor Pad 3 Pro (2)

It has MediaTek’s MT8788 processor paired with 16GB of RAM and 256GB of storage. This ensures smooth operation for even the most demanding tasks. Shuffling between apps, streaming HD content, or playing graphic-intensive games—this Ulephone tablet handles it all with ease. Its built-in LED lights and gigantic battery with reverse charging support add to its versatility. You have emergency lights and power backup for other mobile devices. How cool is that?

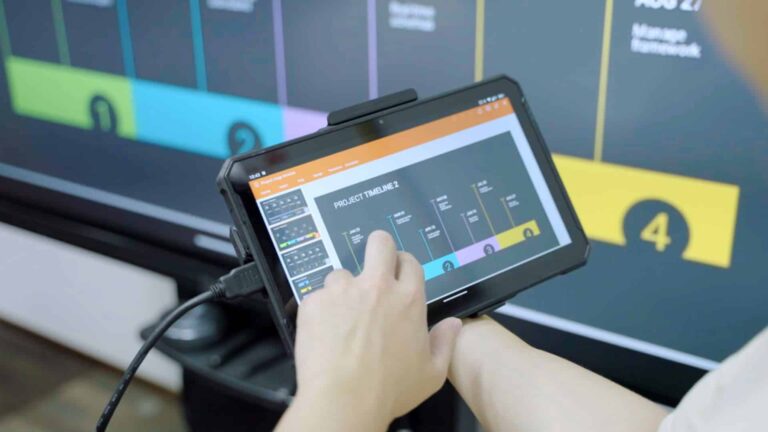
Then comes the real game-changer, the Armor Pad 3 Pro’s built-in HDMI port. It elevates your tablet experience to a whole new level. You can connect the device to a larger screen for a detailed view of files and information, perfect for presentations or complex spreadsheets, editing high-resolution photos and videos with superior precision, real-time collaboration with colleagues and clients, and content consumption, all while maintaining controls from the tablet.

All of this at an affordable price

Ulephone’s Armor Pad 3 Pro also packs a 50MP rear camera, a 32MP selfie camera (both cameras support 1080p video recording), Corning Gorilla Glass 5 display protection, microSD card support of up to 2GB, dual stereo speakers, a side-mounted fingerprint scanner, 3.5mm headphone jack, dual-SIM slot, in-box charger, GPS, and NFC. If anything, Android 13 out-of-the-box and the lack of 5G cellular connectivity could be a dealbreaker.

However, Ulephone is known for making tech affordable, and the Armor Pad 3 Pro maintains the philosophy. Usually priced at $560, this impressive tablet is available for as low as $252 (excluding taxes) with free shipping. Head to the official Ulephone website for more information. The tablet is shipped globally via AliExpress. You get additional discounts if you order multiple units.


[ad_2]
Source link