OpenAI quietly launched one of its coolest ChatGPT features

0

[ad_1]

When using AI chatbots, you’re usually stuck with the chatbot that companies build for you. That’s not bad, as they’re extremely powerful, but OpenAI recently gave its users the ability to create their own custom GPTs. Well, OpenAI just launched the ability to tag custom chatbots in conversations. We’re just wondering why the company was being so secretive about it.

Before jumping in, OpenAI recently launched the GPT store. The GPT store is basically an app store for custom chatbots. On an app store, people are able to create and present their own apps to be downloaded by other people. Well, people are able to create their own custom GPTs and post them to the store for others to install.

Also, people will be able to monetize their GPTs so that they can earn a revenue stream from them. If you are interested in installing custom GPTs or creating your own, you will need to be signed up for a ChatGPT Plus account. This service costs $20/month.

Now allows you to tag custom GPTs.

Right now, when you install a custom GPT, you will interact with that GPT in its own conversation. This is useful and convenient. However, what if a certain conversation calls for more than one GPT to be used? Well, this is something that OpenAI addressed with this new addition. As spotted by X User Dan Shipper, OpenAI just released a feature that will let you actually tag custom GPTs in your conversations.

Say, you are using regular ChatGPT, but you need to access a GPT that specializes in accounting. Well, instead of going to a separate conversation with an accounting GPT, you can simply type the “@” symbol and tag that GPT in your existing conversation. Then, you will get results from that accounting GPT inside of your conversation.

You’ll be able to continue your conversation with the pre-existing context without having to leave it. This is an extremely convenient way of accessing multiple GPTs. For some reason, OpenAI launched this feature without any fanfare or announcements. The company recently went through some drama with leaked conversations, so we’re sure that it’s dealing with that mess.


[ad_2]

Source link
Hackers Hijacking MS-SQL Servers to Install Mimic Ransomware

0

[ad_1]

The Trigona ransomware threat actor has been observed engaging in new activities, such as installing Mimic malware that targets MS-SQL servers. 

MS-SQL servers’ Bulk Copy Program (BCP) feature is abused during the malware installation process. The BCP utility bcp.exe is a command-line tool used for importing or exporting large amounts of external data in MS-SQL servers. 

The Trigona ransomware is still alive, targeting MS-SQL servers, and has been active since at least June 2022. First discovered in June 2022, mimic ransomware was designed to target people who spoke English and Russian.

Recently, the Trigona ransomware threat actor has been infecting poorly maintained MS-SQL servers with the Mimic and Trigona ransomware strains. 

Document

Run Free ThreatScan on Your Mailbox

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Try Trustifi Free Threat Scan with Sophisticated AI-Powered Email Protection .

Attackers Hijacking MS-SQL Servers

In searching for files to encrypt, mimic ransomware is known to misuse a file search tool named Everything. It is believed that the threat actor is using the Everything tool to speed up the target system’s file encryption. 

Additionally, the attacker imitated a few aspects of the Conti ransomware, whose source code was leaked during the program’s development.

According to the AhnLab Security Intelligence Center (ASEC) report, almost the same external structure was employed in this attack, and the Mimic ransomware samples were found in the Trend Micro report from January 2023 and the Securonix report from January 2024.

 “The folder that is ultimately installed not only contains Mimic ransomware and the Everything tool but also the Defender Control tool (DC.exe) for deactivating Windows Defender and the SDelete tool (xdel.exe) of Sysinternals”, ASEC shared with Cyber Security News.

Installed Files
Installed Files

The email address of the threat actor in the ransom note differs from that in earlier instances of the Mimic ransomware and is also missing from other attack scenarios.

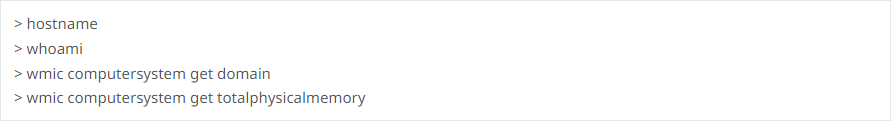
The threat actor would use the information obtained from the following commands to install malware strains that were appropriate for the environment.

Look up the infected system’s information

To take control of the compromised system, the threat actor installed AnyDesk. It has also been discovered that the attacker also attempted to connect via RDP to the compromised system and take control of it remotely using a malware strain designed for port forwarding.

“Although no malware or command log that sets the system boot option to safe mode was found, logs of the MS-SQL server process executing a system restart command was identified”, researchers said.

Recommendation

Brute force and dictionary attacks are common ways to target MS-SQL servers on systems where account credentials are not properly managed. Administrators need to utilize complex passwords and update them regularly.

Updating V3 to the most recent version is also necessary to prevent malware infection beforehand. Administrators should also deploy security tools like firewalls to prevent external threat actors from accessing database servers.

[ad_2]

Source link

Galaxy A35 and A55 gain more certifications ahead of launch

0

[ad_1]

Samsung is rapidly completing all the formalities before bringing the Galaxy A35 and Galaxy A55 to the market. Over the past few weeks, the devices have picked up several regulatory certifications around the world. They have now been spotted on the Bluetooth SIG and GCF (Global Certification Forum) websites too, hinting at a nearing launch.

Bluetooth SIG and GCF certify Samsung’s Galaxy A35 and A55

The GCF certified the Galaxy A35 with the model numbers SM-A356E and SM-A356E/DS. The Galaxy A55 picked up the same certification with the model numbers A556B/DS, SM-A556E/DS, and SM-A556E. All of these are global versions of the phones, with “DS” at the end indicating dual-SIM variants. Samsung will also release the duo in the US. It has already received the FCC certification for the former. The latter should follow soon.

Apart from the model numbers, the listings on the GCF website don’t reveal anything else about the Galaxy A35 and Galaxy A55. The Bluetooth SIG certification, meanwhile, confirms support for Bluetooth V5.3 on both models. Note that the latter picked up the Bluetooth certification last week. The former has also now gained it, including the global, US, Canadian, and Chinese versions.

All of these developments hint at a nearing launch of the two mid-range smartphones. When we say nearing, we don’t mean it is happening within a week or two. Samsung likely still has a lot of things to do before it unveils the Galaxy A35 and Galaxy A55. Rumors suggest the devices will go official in April or the earliest in March. You can expect more leaks, rumors, and certifications for the phones in the coming months.

Both devices will bring a few notable upgrades

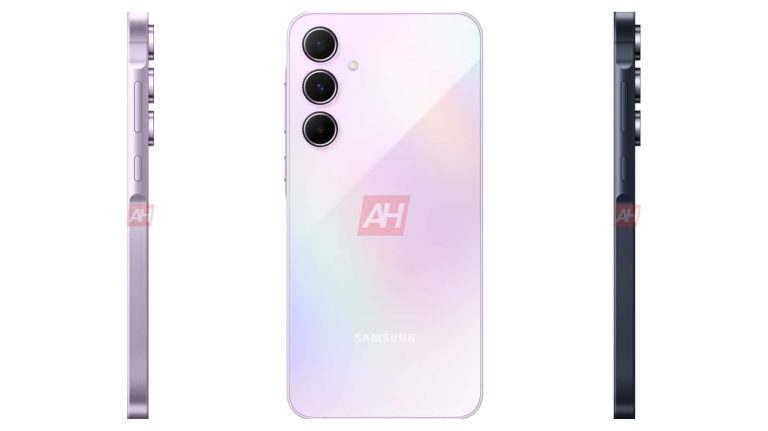
A few weeks ago, we exclusively leaked the official renders of the Galaxy A35 and Galaxy A55, revealing their design. The two phones look identical but have a key differentiating factor on their frame. The latter has antenna lines, while the former doesn’t. This means Samsung will upgrade the Galaxy A55 to a metallic frame while the other model will get a plastic frame.

This doesn’t mean the Galaxy A35 won’t improve upon the Galaxy A34. Most notably, it is rumored to feature a 50MP primary rear camera, which should be a much newer sensor than the 2023 model’s 48MP unit. Both new devices should also bring a few more iterative upgrades, including a newer processor and the latest version of One UI based on Android 14. Stay tuned for the official launch of the phones.

[ad_2]

Source link

Apple A18 Pro surpasses M3 family in single-core benchmark test

0

[ad_1]

A couple of days back, a tipster shared the alleged first benchmark scores of the Snapdragon 8 Gen 4 and Dimensity 9400. The two upcoming chipsets achieved staggering numbers on Geekbench 6 and AnTuTu, though we have doubts over the legitimacy of the leaked scores. Meanwhile, the same source is now back with early Geekbench 6 scores of the Apple A18 Pro. Once again, we are looking at stunning numbers, at least for single-core CPU tests.

Apple A18 Pro returns excellent score in single-core Geekbench 6 tests

According to the tipster, who goes by the username @negativeonehero on X, the Apple A18 Pro scored around 3,500 in an early single-core CPU test on Geekbench 6. That makes it faster than the company’s M3, M3 Pro, and M3 Max processors for Macbooks. As pointed out by Wccftech, the new A-series chipset is about 14% faster than the entire M3 family, which is remarkable for a smartphone processor.

Unsurprisingly, the A18 Pro leaves the Snapdragon 8 Gen 4 and Dimensity 9400 in the dust when it comes to single-core CPU performance. In the same test, the next-gen Qualcomm and MediaTek processors scored 2,845 and 2,776, respectively. So, the Apple chip is over 23% faster than its rivals. However, the A18 Pro finds itself lagging big time when it comes to multi-core CPU performance, scoring only around 8,200.

The Snapdragon 8 Gen 4 and Dimensity 9400 scored 10,628 and 11,739, respectively. We know these two have eight CPU cores with no efficiency core, while the A18 Pro likely has six CPU cores. But such a gap in multi-core performance still comes as a surprise. The good thing is that it is in the early stages of development. Apple has ample time to improve its multi-core performance.

All this said, there’s no way to verify if these benchmark scores are legitimate. No doubt, all three chipsets will bring notable improvements to CPU and GPU performance over their respective predecessors. But whether the end product delivers the same level of performance we see in these early benchmark runs, only time will tell. We should get clearer pictures in the coming months as the companies progress with their development works.

Only the Pro iPhones will get the Pro chip

In recent years, Apple has been shipping the new iPhones with two different chips. The Pro and Pro Max models get the latest A-series chip, while the other two models arrive with last year’s processor. The company is seemingly changing that practice this year. It is said to be readying two new processors—A18 and A18 Pro—for the iPhone 16 series, though only the two Pro models will get the Pro chip. Stay tuned for more about the next-gen iPhones.


[ad_2]

Source link

U.S. Officials Detained a 19-year-old SIM-Swap Hacker

0

[ad_1]

In the murky depths of the digital underworld, a tale unfolds: the rise and fall of “King Bob,” a moniker masking 19-year-old Noah Michael Urban, a Florida man entangled in a web of cybercrime. 

An investigation revealed the accused’s role in a hacking group linked to cyberattacks on major U.S. tech companies in summer 2022 (KrebsOnSecurity).

Document

Run Free ThreatScan on Your Mailbox

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Try Trustifi Free Threat Scan with Sophisticated AI-Powered Email Protection .

Accused of wire fraud, identity theft, and orchestrating SIM-swapping attacks, Urban’s story transcends individual transgression, painting a chilling portrait of interconnected criminal networks and the escalating dangers they pose.

Prosecutors allege Urban, operating under aliases like “Sosa,” amassed a staggering $800,000 through unauthorized SIM swaps between 2022 and 2023. 

This seemingly individual act unravels further, revealing Urban’s suspected involvement in notorious hacker groups like Oktapus and Scattered Spider. 

These groups, responsible for a string of breaches at major tech companies like Twilio, LastPass, and DoorDash, employed sophisticated phishing tactics, leaving a trail of compromised data and financial losses.

Phishing with Finesse: 0ktapus’s Web of Deceit:

Group-IB’s investigation dubbed the group “0ktapus” due to its use of seemingly legitimate domain names to lure unsuspecting employees into divulging credentials. 

This intricate “phishing” strategy enabled them to access and exploit vulnerabilities in over 130 organizations, showcasing a level of sophistication rarely seen in such attacks. 

Notably, this modus operandi involved a domino effect, where access gained in one breach became a springboard for subsequent attacks, highlighting the interconnectedness of the cybercrime landscape.

Beyond financial gain, Urban’s online persona, “King Bob,” reveals a peculiar obsession: trading and acquiring unreleased music, particularly from renowned rappers. 

His active participation in Leaked[.]cx, a platform notorious for such “grails,” adds another layer of intrigue. 

However, speculation surrounds his sudden disappearance from the platform, prompting questions about a possible connection between the enigmatic “King Bob” and the ongoing legal proceedings against Urban.

The investigation delves deeper, exposing the brutal underbelly of the SIM-swapping underworld.

In February 2023, a bombshell report by KrebsOnSecurity exposed a disturbing trend: organized SIM-swapping gangs specifically targeting T-Mobile customers. 

Ties between Urban and individuals like “Foreshadow,” a victim-turned-accomplice forced into servitude, illuminate the prevalent violence within these groups. 

Foreshadow’s harrowing experience, documented in a ransom video, serves as a stark reminder of the dangers individuals face in this sphere. 

Urban’s involvement extends beyond individual groups. His affiliation with “The Com,” a notorious cybercriminal community known for boasting about exploits, and “Star Fraud,” linked to high-profile extortion attacks against companies like Caesars Entertainment and MGM Resorts, paints a picture of a sprawling and interconnected network of cybercriminals. 

Experts warn against the consequences of delayed action from law enforcement, highlighting the potential for online violence to spill over into the real world and impact everyday people.

[ad_2]

Source link

Energy Giant Schneider Electric Hit by Cactus Ransomware Attack

0

[ad_1]

Schneider Electric’s Sustainability Business division hit by Cactus ransomware attack. The incident highlights the growing threat to industrial organizations. Get the latest updates on impact and response.

Schneider Electric, a global leader in energy management and automation, has suffered a ransomware attack that impacted its Sustainability Business division. The attack, which occurred on January 17, 2024, involved the deployment of the Cactus ransomware, a strain known for targeting industrial organizations.

The Impact:

The attack primarily affected Schneider Electric’s EcoStruxure Resource Advisor platform, used by over 2,000 companies worldwide to monitor energy and resource data. While the full extent of the breach is still under investigation, it is confirmed that some data was accessed by the attackers. Fortunately, no other Schneider Electric divisions or business units were affected.

Schneider Electric’s Response:

According to a press release, the company immediately launched a global incident response, mobilizing its internal team and bringing in external cybersecurity experts to contain the attack and restore affected systems. Additionally, Schneider Electric is notifying customers who may have been impacted by the breach.

On January 17th, 2024, a ransomware incident affected Schneider Electric’s Sustainability Business division. The attack has impacted Resource Advisor and other division-specific systems. Schneider Electric Global Incident Response team has been immediately mobilized to respond to the attack, contain the incident, and reinforce existing security measures. The Sustainability Business division has informed impacted customers.

Schneider Electric

Current Status and Potential Impact:

As of January 31, 2024, Schneider Electric is still working to restore full functionality to its systems. Most systems are expected to be back online within the next few days. However, the attack could potentially disrupt operations for some of Schneider Electric’s customers, and there is a risk that customer data may have been compromised.

Expert Opinions:

Cybersecurity experts have expressed concern about the growing trend of ransomware attacks targeting industrial organizations. They warn that such attacks can have significant consequences, disrupting critical infrastructure and potentially endangering public safety.

John Gallagher, Vice President of Viakoo Labs at Viakoo said “Whether for IoT, OT, or ICS systems it has been a long-standing best practice to ensure these systems are on dedicated and isolated networks to prevent lateral movement if vulnerable IoT devices are breached. But this is not that situation; this is a business division and more like a fully separate company.”

John advised that “In addition to isolated or segmented networks, effective use of zero trust principles can also be effective in preventing lateral movement within an organization.”

“Using application-based discovery to identify all application, device, and port relationships can also be effective in setting up and maintaining an isolated network. Too often a network is properly configured and isolated, but over time both users and configuration drift can impact that segmentation and allow punch-throughs,” he added.

Schneider Electric Energy Giant Confirms Cactus Ransomware Attack
Homepage of Cactus ransomware’s dark web domain – For now, there is no mention of Schneider Electric (Screenshot: Hackread.com)

Key Takeaways:

  • Schneider Electric’s Sustainability Business division was hit by a ransomware attack on January 17, 2024.
  • The attack involved the Cactus ransomware strain and impacted the EcoStruxure Resource Advisor platform.
  • Some data was accessed by the attackers, but the full extent of the breach is still under investigation.
  • Schneider Electric is working to restore systems and notify impacted customers.
  • The attack is a reminder of the growing threat of ransomware targeting industrial organizations.
  1. LockBit Ransomware Gang Claims Subway as New Victim
  2. Schneider Electric Shipped USB Drives Loaded with Malware
  3. New CISA Advisories Highlight Vulnerabilities in Top ICS Products
  4. TeamViewer Exploited to Obtain Remote Access, Deploy Ransomware
  5. Controller-level flaws can let hackers physically damage moving bridges


[ad_2]

Source link

Pixel sales were strong in Q4 2023, suggests Google’s latest report

0

[ad_1]

Google has released its financial report for Q4 last year. That financial report suggests that the Pixel phone sales were quite strong in Q4 2023. Now, Google doesn’t exactly share those numbers, but hear us out.

Pixel device sales have seemingly been quite strong for Google in Q4 2023

The ‘Subscriptions’ category, which includes Android, Pixel phones, tablets, smartwatches, and truly wireless earbuds, has earned $10.79 billion, which is an increase of 22.7% compared to Q4 2022.

This does give us a strong suggestion that Pixel phones have been selling really well for the company. The Pixel 8 and Pixel 8 Pro in specific have likely seen very good sales numbers, compared to previous generations.

It would be great if Google actually shared some sales numbers with everyone, but that doesn’t usually happen, and chances are it won’t happen anytime soon either. This is the best indication we’ll get unless something ends up changing.

Google’s revenue rose by 13% in Q4 2023 (YoY)

Now, in regards to some other numbers… Google’s Q4 2023 revenue rose 13% year-over-year (YoY) to $86.31 billion. It was $76.05 billion a year before, in Q4 2022. In the entire year of 2023, Google took in $307.39 billion, which is a 9% increase compared to 2022.

Google Search revenue increased by 12.7% to $48.02 billion. YouTube revenue, on the other hand, also did great with a 15.5% increase to $9.20 billion. Google advertising has seen an 11% increase on an annual basis, to $65.52 billion.

Google’s Cloud Services also did great in Q4 2023 with a 25.7% revenue increase, to $9.19 billion. What decreased is the number of employees, it shrunk by 4.1% to 182,502. Google had 190,234 employees a year before.

Sundar Pichai said: “We are pleased with the ongoing strength in Search and the growing contribution from YouTube and Cloud”. He also had to mention AI, of course, by adding: “Each of these [Search, Youtube & Cloud] is already benefiting from our AI investments and innovation. As we enter the Gemini era, the best is yet to come.”

[ad_2]

Source link

Hit by poor chip demand, Samsung’s 2023 profit dropped 85%

0

[ad_1]

Samsung has published its earnings report for 2023. As expected, the company suffered a steep decline in operating profit despite a relatively health consolidated sales revenue. Poor semiconductor demand hurt it big time, with the business unit posting a loss for the first time in 14 years.

Samsung suffered an 85% profit decline in 2023

According to Samsung’s official press release, the company made KRW 67.78 trillion (approx. $50.8 billion) in sales revenue and KRW 2.82 trillion (approx. $2.1 billion) in operating profit in the fourth quarter of 2023. The figures respectively mark a 3.8% and 34.5% year-on-year (YoY) decline from the same period in 2022.

While this already looks bad for a global conglomerate, it had even worse financial performance in the previous three quarters of last year. The year-end quarter was a more positive one. Its profit margin for October-December 2023 was 4.2%, up from 3.6% in the third quarter and 1% in the first two quarters.

With such a poor show throughout the year, Samsung’s operating profit for the whole of 2023 was just KRW 6.57 trillion (approx. $4.9 billion). That is despite a consolidated sales revenue of KRW 258.94 trillion (approx. $194 billion). The company generated a profit of KRW 43.38 trillion in 2022 when its revenue was KRW 302 trillion. Last year, its profit declined 85% YoY, while revenue dropped only 14%.

In 2023, Samsung was hit hard by a global decline in semiconductor demand and prices. The DS Division, which encompasses the semiconductor business, posted a loss throughout the year. It was the company’s first loss from the chip business in 14 years, since the global financial crisis of 2008. All other major business divisions fared relatively well for Samsung last year.

Samsung expects a better financial performance in 2024

Samsung expects its earnings to improve in 2024. The company plans to focus on improving profitability by increasing sales of “high value-added products,” while the component businesses aim to meet the demand for advanced products, such as generative AI. The Device eXperience (DX) Division, which includes the smartphone business, will bring more AI features to smartphones and other products.

As far as the semiconductor business is concerned, Samsung projects a recovery in demand this year as the smartphone market rebounds after a slowdown in 2023. There are still various potential obstacles, including interest rate policies and geopolitical issues, but the Korean firm likely expects the chip division to return to profitability in 2024. It remains to be seen whether Samsung manages to turn the tide this year. The company will publish its Q1 2024 earnings report in April.

[ad_2]

Source link

First OnePlus 12 update brings Hasselblad Master Mode

0

[ad_1]

The very first (global) OnePlus 12 update has arrived, and it delivers Hasselblad Master Mode to the device. This is something that OnePlus promised would arrive to the device, and it just has, prior to release.

Hasselblad Master Mode is a part of the very first OnePlus 12 update

You’ve probably seen some OnePlus 12 reviews by now, including ours, however, the phone is still up for pre-order. So there’s still time for OnePlus 12 to push updates to the device before they arrive into the hands of customers.

This is one such update, and possibly even the last one prior to release. The Hasselblad Master Mode is definitely the most notable addition to this update. It allows you to set levels for saturation, contrast, sharpness, and vignette before you take the photo.

It is a part of the OxygenOS v14.0.0.404 (EX01), which weighs 6.48GB. Yes, this is a huge update so make sure you’re either connected to Wi-Fi or that you have plenty of data before you download it.

ProXDR is now also available in the Google Photos app

What else is included here? Well, ProXDR is now available in the Google Photos app, and this update also improves the fingerprint scanner. OnePlus has also listed improved stability and compatibility of Wi-Fi network connections.

Every function related to NFC has also been improved, as the NFC functionality has been boosted. On top of that, Bluetooth should work better than before now, as OnePlus says that the stability has been improved, as well as compatibility.

The last change noted here is the improved system stability. OnePlus probably optimized things further and also squashed some bugs in order to get there. That’s always nice to see, of course.

This update is coming to you in the form of an OTA (over-the-air) update. Your phone will let you know when it’s available, and depending on your settings it may even download and install it. You can also manually check whether it’s available if you’re impatient.

[ad_2]

Source link

MediaTek’s flagship Dimensity 9400 SoC coming in Q4 2024

0

[ad_1]

MediaTek’s flagship Dimensity 9400 SoC will launch in Q4 this year. This information is actually official, as it comes from the company’s CEO. Rick Tsai, MediaTek’s CEO confirmed as much, while sharing some additional details. He didn’t specifically mention the chip by name, but everyone knows what he was talking about.

MediaTek’s flagship Dimensity 9400 SoC is coming in the last quarter of the year

He said that the chip will come with boosted AI capabilities too. That’s basically it. Rick Tsai didn’t really go into details, he simply wanted to tease the arrival of the chip.

With that said, we do have some additional info about this chip, thanks to rumors. MediaTek is expected to continue using ARM’s CPU designs, unlike Qualcomm. The company will move to the Cortex-X5 cores.

Much like the Dimensity 9300, the Dimensity 9400 is not expected to feature efficiency cores. That should bring forth rather high multi-core performance. Who knows, maybe the Snapdragon 8 Gen 4 has similar plans, some rumors did hint that’s the case.

LPDDR5T support is also expected

LPDDR5T support could be included as part of the package, and the company will use TSMC’s new 3nm process in order to bring this chip forth. Qualcomm will also use TSMC’s second-gen 3nm process for the Snapdragon 8 Gen 4.

We haven’t really seen the MediaTek Dimensity 9300 in all that many phones. It did prove to be quite a capable processor inside the Vivo X100 Pro and some other devices, though. So the hopes are high for the Dimensity 9400.

One area that was hope MediaTek will improve in is power efficiency. The company’s flagship processors are still not on par with flagship chips from Qualcomm in that area. As far as sheer power goes, they’re definitely up there.

It will also be interesting to compare the MediaTek Dimensity 9400 vs Qualcomm’s Snapdragon 8 Gen 4, as the Snapdragon 8 Gen 4 will feature Oryon cores for the first time.

[ad_2]

Source link