Critical Flaws Found in GNU C Library, Major Linux Distros at Risk

0

[ad_1]

Millions of Linux systems are at risk due to four critical vulnerabilities found in the GNU C Library (glibc), a fundamental component of most Linux distributions.

The Qualys Threat Research Unit (TRU) has discovered four significant vulnerabilities in the GNU C Library, a crucial component of Linux-based systems. Researchers have discovered multiple vulnerabilities in the library’s syslog and qsort functions, raising significant security concerns.

The first vulnerability, tracked as CVE-2023-6246, is a heap-based buffer overflow law. It is discovered in the GNU C Library’s __vsyslog_internal() function and affects syslog() and vsyslog().

The vulnerability, originating in glibc 2.37 introduced in August 2022, was subsequently backported to glibc 2.36, leading to its tracing. Most major Linux distributions, including Debian, Ubuntu, and Fedora, are vulnerable to this flaw, which allows local privilege escalation and lets unprivileged users gain full root access.

The same function affected by CVE-2023-6246 has two more, but minor impact vulnerabilities: CVE-2023-6779 (glibc) and CVE-2023-6780 (glibc). These vulnerabilities involve off-by-one heap-based buffer overflows and integer overflow issues.

Once triggered, these flaws appeared far more challenging than the first vulnerability (CVE-2023-6246). Further probing revealed that their effective exploitation is even more complex.  

The last one is a memory corruption issue discovered in the GNU C Library’s qsort function, occurring due to missing bounds check. This vulnerability can be exploited when qsort() is used with a nontransitive comparison function and when an attacker manages to control a large number of elements, leading to malloc() failure.

The flaws affect glibc’s handling of input formats within syslog() and could trigger buffer overflows and memory corruption, allowing attackers to inject malicious code into vulnerable systems. Exploitation of these vulnerabilities may allow attackers to gain remote code execution (RCE) on affected systems, potentially leading to data theft and system compromise.

The syslog vulnerability allows root access, affecting major Linux distributions, while the qsort vulnerability leads to memory corruption. What is more concerning is that the vulnerabilities affect all glibc versions from September 1992 (glibc 1.04) to the current release (glibc 2.38).

TRU contacted the glibc security team regarding the flaws on 12 December 2023, but the team decided not to treat memory corruption in qsort() as a vulnerability. On 16 January 2024, TRU backported commit b9390ba to all stable versions of glibc, and the coordinated release date was set for 30 January 2023.

The discovery highlights the painful fact that even the most trusted components can have flaws. These issues usually have far-reaching implications, potentially impacting millions of users globally and making a large number of applications vulnerable and exploitable, as noted by TRU’s Product Manager, Saeed Abbasi in the company’s blog post:

“The recent discovery of these vulnerabilities is not just a technical concern but a matter of widespread security implications.”

Users are advised to update their glibc versions immediately to mitigate risks, while system administrators and developers should review their applications/libraries to ensure their systems are safe.

  1. Mélofée: The Latest Malware Targeting Linux Servers
  2. WiFi Flaws Allow Network Traffic Interception on Linux
  3. Bluetooth Vulnerability Enables Keystroke Injection Linux
  4. Linux Vulnerability Exposes Millions of Systems to Attack
  5. Free Download Manager Site Pushed Linux Password Stealer


[ad_2]

Source link

OnePlus returns to key European market after a long hiatus

0

[ad_1]

OnePlus has made a return to a key European market after a rather lengthy hiatus. This news follows the agreement between OPPO and Nokia over 5G patents, which caused OPPO and OnePlus quite a bit of problems.

OnePlus has returned to a key European market after a long hiatus

OnePlus has returned to Germany, as its smartphones were not available there for over a year. OPPO is still missing as of writing this article, but OPPO’s smartphones are also expected to return.

Nokia sued the two companies over 5G patents in 2022, and their devices have been missing from Germany since August 2022. An agreement was reached quite recently between companies, so both OnePlus and OPPO can resume their business in Germany.

OnePlus and OPPO are sister companies, for those of you who are unaware. Both companies are a part of the BBK Electronics family, and the same goes for Vivo, in case you didn’t know that.

Both the OnePlus 12 and OnePlus 12R are now available in the country

OnePlus has returned to Germany with its latest smartphones, the OnePlus 12 and OnePlus 12R. Both devices are now available to pre-order in Germany, in case you’re interested.

OnePlus actually has a deal for both smartphones. You can bundle them with a free pair of OnePlus Buds Pro 2 earphones. Those earphones cost €179 on their own, so that’s a nice perk.

It’s also worth noting that the top-end OnePlus 12 device, the one with 16GB of RAM and 512GB of storage, is also 9% off. That brings its price down to €999, while the 12GB RAM + 512GB storage option costs €949 in the country. Yes, the prices in the EU are considerably higher than the ones in the US.

Do note that some extra discounts are available with each purchase. You can get a 50% discount on the company’s 50W wireless charging, which brings the price down to €35. The OnePlus Pad can be bought for €450, which is a 10% discount.

The OnePlus 12R, on the flip side, comes in one variant, with 16GB of RAM and 256GB of storage. That device can be yours for €699.

[ad_2]

Source link

Microsoft Edge could be importing your data without permission

0

[ad_1]

After the most recent Windows update, it appears Microsoft Edge might be importing your data from other browsers without asking. It’s no secret Microsoft wants you to switch permanently to Edge, they try every other day after all. But, be it a glitch or more, it seems the browser has gone a step further. Users who have recently updated Windows might want to double-check their settings in Edge.

Microsoft Edge importing data from other browsers

This is apparently an issue that has been happening for months. Users on various social media platforms have reported Edge “stealing” their data from other browsers on their devices. It is true that Microsoft has been working on a feature to import your data from other browsers. However, according to these reports, not only is this feature on without consent, but users are having trouble getting it to stay off.

The entire ordeal got more attention recently when Tom Warren of The Verge reported falling victim to it. After a Windows update, he saw Microsoft Edge open itself with the tabs he had been working on in Chrome. Some research later, and it turns out this isn’t anything new. Microsoft Edge now has its import feature turned on by default. This allows it to import not just your browsing history, but also your bookmarks, cookies, extensions, settings, and even your auto-fill data.

Is this a concern, and how to turn it off?

Though extremely handy for people making the switch to Edge, this does result in a massive breach of trust. The biggest red flag is how Edge does not ask for your consent before turning this feature on. Auto-fill data can have some very sensitive information stored in it. Information users don’t want being shared around without being informed. Furthermore, if additional reports and tests are to be believed, it appears Edge imports this data even with the option turned off.

Turning this feature off is quite simple, though it cannot be guaranteed at the moment that it will actually remain off. Simply go into Settings, then Profiles, and you will find the option there under Import Browsing Data. You will also see options to manually import data from other browsers on your system should you wish.

Microsoft has recently put a lot of effort into making Edge a much better browser than Internet Explorer ever was. But, despite Edge being a solid browser, most people are unwilling to switch over from what they’re familiar with. Microsoft might continue to become even more aggressive going forward in attempts to make users switch over. If it does, we could be looking at an Apple-like Microsoft ecosystem where everything is tightly controlled and under Microsoft’s supervision.


[ad_2]

Source link

TikTok’s silent dance: Universal Music Group pulls the plug on tunes

0

[ad_1]

Imagine watching a video of a dancing group of people without any music. It could be quite amusing, right? Well, TikTok users might soon experience just that, as songs are about to vanish from the platform.

According to Variety (via 9to5Mac), Universal Music Group, one of the biggest players in the music industry, has stated that it couldn’t reach new deal terms with TikTok. The disagreements were mainly about how artists are paid and how TikTok uses AI. Universal Music accused TikTok of trying to push for a deal that was less favorable than before.

UMG mentioned that its existing agreement with TikTok is due to expire on January 31. It stated:

If the deal actually ends, UMG is gonna yank its music from TikTok. That’s a big chunk of tunes gone, and for TikTok, that could be trouble. The app thrives on those catchy beats for its viral videos. Without a library full of popular music, creating those viral clips might get a bit tricky.And UMG has the A-listers when it comes to popular music. Think of Taylor Swift, Bad Bunny, Sting, The Weeknd, Alicia Keys, Steve Lacy, Drake, Billie Eilish, Kendrick Lamar, Rosalía, Harry Styles, Ariana Grande, Justin Bieber, Adele, U2, Elton John, Brandi Carlile, Coldplay, Pearl Jam, and Bob Dylan. If they pull the plug, TikTok loses a star-studded cast, making those lip-syncs and dance-offs a bit less star-powered.

TikTok clapped back at UMG, saying,

The social media thinks UMG has chosen to walk away from the powerful support of a platform with over a billion users that serves as a free promotional and discovery vehicle for their talent.

In a letter, the music company also referred to TikTok as “an increasingly influential platform with powerful technology and a massive worldwide user base.” However, UMG highlighted three key concerns: fair compensation for their artists and songwriters, safeguarding human artists from the negative impacts of AI, and ensuring online safety for TikTok users.

Talking about online safety, TikTok has been dealing with some issues lately. The state of Iowa threw a lawsuit at the company, claiming the app isn’t suitable for users under 17. Also, TikTok pulled a tool researchers used to study hashtag trends after facing criticism. This has added to the ongoing tension between social media platforms and researchers looking into topics like misinformation.

[ad_2]

Source link

GitLab Patched A Workspace Creation Vulnerability

0

[ad_1]

Days after releasing a major update, GitLab rolled out another emergency update addressing a serious vulnerability affecting workspace creation. The service urged all users to update to the latest releases at the earliest, assuring that the web and GitLab Dedicated environments already run the patched versions.

GitLab Workspace Creation Vulnerability

According to a recent post, GitLab patched five vulnerabilities affecting the service, including a critical severity flaw. As described, exploiting the vulnerability could allow arbitrary file write during workspace creation.

While the advisory doesn’t elaborate on this vulnerability, CVE-2024-0402, it did highlight its severity, mentioning its CVSS score (9.9). This critical severity flaw caught the attention of GitLab’s team member, compelling the service to release the patch for all available versions. In fact, GitLab also backported this fix to versions 16.5.8, 16.6.6, 16.7.4, and 16.8.1.

Other GitLab Security Fixes

Besides, the other vulnerabilities addressed with the latest update include the following medium severity issues.

  • CVE-2023-6159 (CVSS 6.5): Exploiting the vulnerability could allow an adversary to trigger Regular Expression Denial of Service (ReDoS) via a maliciously crafted input containing Cargo.toml. GitLab came to know of this vulnerability through a HackerOne bug report.
  • CVE-2023-5933 (CVSS 6.4): Improper input sanitization of user name could allow arbitrary API PUT requests.
  • CVE-2023-5612 (CVSS 5.3): The vulnerability existed due to unwarranted exposure of user email address via tags even with disabled profile visibility settings.
  • CVE-2024-0456 (CVSS 4.3): This vulnerability could let an unauthorized attacker assign arbitrary users to MRs within the project.

The recent update marks the second major security release from GitLab. Earlier this month, GitLab released versions 16.7.2, 16.6.4, and 16.5.6 for both Community Edition and Enterprise Edition (CC/EE), patching a severe zero-click vulnerability. Now that another security release has been out, users must update their systems with the latest versions to receive all patches in time.

Let us know your thoughts in the comments.

[ad_2]

Source link

Google is working on Ultra HDR support for third-party apps

0

[ad_1]

The Google Pixel 8 series, launched in October, introduced support for the Ultra HDR images for devices on Android 14. It provided users the ability to capture brighter and more dynamic images and experience them on supported devices with HDR screens. Samsung followed suit with the Galaxy S24 series, announcing that popular social media platforms like Snapchat and Instagram would now support Ultra HDR on their new phones.

Now, Android expert Mishaal Rahman has uncovered evidence suggesting that Google is set to expand Ultra HDR support to third-party camera apps using the CameraX API, allowing users on Android 14 to capture stunning HDR images beyond the confines of their OEM camera apps.

The integration of Ultra HDR image capture support into the CameraX API holds promising implications for users who prefer third-party camera apps. Rahman’s findings indicate that apps utilizing the CameraX API will soon be able to output images in the new JPEG_R format designed for Ultra HDR.

Users will probably be able to use their preferred third-party camera app without sacrificing the JPEG_R format

This development will not only benefit social media and messaging apps but also open up exciting possibilities for third-party camera applications. Users on Android 14 can look forward to a more diverse range of apps that can leverage the enhanced capabilities of Ultra HDR, making it easier to capture stunning and lifelike images across various scenarios.

While the details on which phones will support this functionality remain unclear, the move to integrate Ultra HDR support into the CameraX API is a positive step toward widespread availability. As HDR technology becomes more prevalent in smartphones, Google’s initiative to extend the support beyond its proprietary apps showcases a commitment to enhancing the overall user experience and fostering innovation within the Android ecosystem.

In summary, Google‘s efforts to bring Ultra HDR support to third-party camera apps through the CameraX API is a promising development for photography enthusiasts.


[ad_2]

Source link

The AI-powered Gboard Smart Reply now cooperates with two more messaging apps

0

[ad_1]

Back in 2018, Google was testing the Smart Reply feature for the omnipresent Gboard, providing suggestions in chats. Fast forward to 2024, now the Gboard Smart Reply is on the AI juice (in the case of the Pixel 8 Pro) and it’s expanding.

The Pixel 8 Pro was announced months before the Galaxy S24, and out of the two, the Koreans were far louder when presenting the AI – they even came up with the whole “Galaxy AI” thing. However, the Pixel 8 Pro is as AI as it gets, taking advantage of Google’s AI model Gemini Nano (via Android Headlines).

For example, there’s the Recorder Summarize, which transcribes audio recordings and spits out an AI-generated summary – tailor-made for lengthy podcasts. If you scoff at people not thinking with their own heads in 2024, just wait until such features become mass-available.

Gboard Smart Reply is also AI-boosted on the Pixel 8 Pro and is now compatible with two more messaging apps.

This is a feature that uses generative AI to suggest the next message you should send in a conversation. It uses conversational awareness to ascertain what the conversation is about and gives you a suggestion of what you should type next.

Only compatible with WhatsApp at the beginning, the Gboard Smart Reply is also available for Line (a telemedicine service that lets you book appointments and talk with doctors online) and KakaoTalk (a popular Korean messaging service with a 53 million monthly active user base).

[ad_2]

Source link

iPhone becomes a motivational speaker in Google’s latest ad

0

[ad_1]

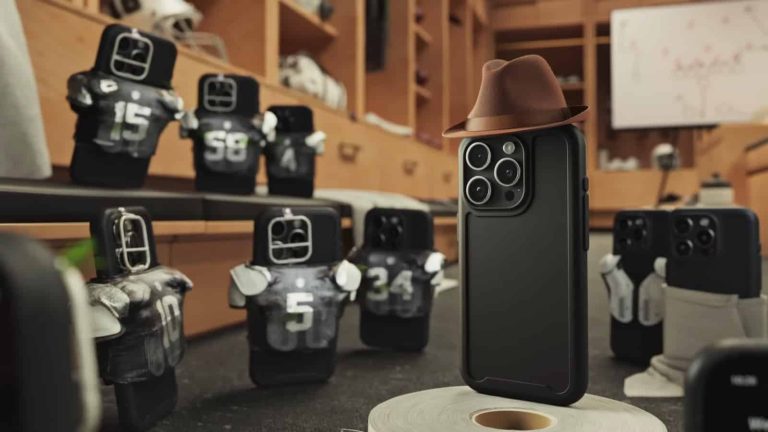
Google has released a new #BestPhonesForever ad, it’s called ‘The Big Game’, and it’s a hoot, as were the previous ones. In this new ad, Apple’s iPhone becomes a motivational speaker, of sorts. It plays the role of a coach who is trying to motivate his team.

An iPhone becomes a motivational speaker during halftime of a match against Google’s Pixels

Why is he trying to motivate his team, though? Well, because of the Pixel’s new AI features. As per usual, this is Google’s way of taking a dig at Apple in an entertaining way.

Now, in this ad, iPhones find themselves in a locker room at halftime of a ‘Big Game’, a game against the Pixels. Coach iPhone decides to hold a speech in order to motivate his players, as they’re worried about Pixel’s new AI features.

He says “This game isn’t over yet”. To what one of the players says “But Coach, the other team keeps getting new AI features”. At that point, others start listing Google’s new features, as does the Coach as part of his speech.

Various Google AI features are mentioned here

Features such as Circle to Search and Video Boost features are mentioned. One of the players says “We’re doomed”. Coach iPhone doesn’t give up, however, not at all. He proceeds by saying “Sure, Team Pixel got advanced AI to fix group photos and summarize recordings and reduce noise in videos. But it doesn’t matter what you got on the inside. It’s what’s on the outside that counts”.

He then mentions some changes that the new iPhones have seen, such as a “different shaped charging port”, hinting at a Type-C charging port, and an Action Button too, amongst other outside changes.

To make things even funnier, at one point, one of the players/iPhones starts to ring, as a spam caller is on the other side. Towards the end of the ad, a Pixel appears, and iPhones says “I, um, lost my playbook. Can I borrow yours?”

This add has a duration of less than a minute. The video is embedded below in case you want to check it out. It sure is entertaining, as were all the previous ones.

[ad_2]

Source link

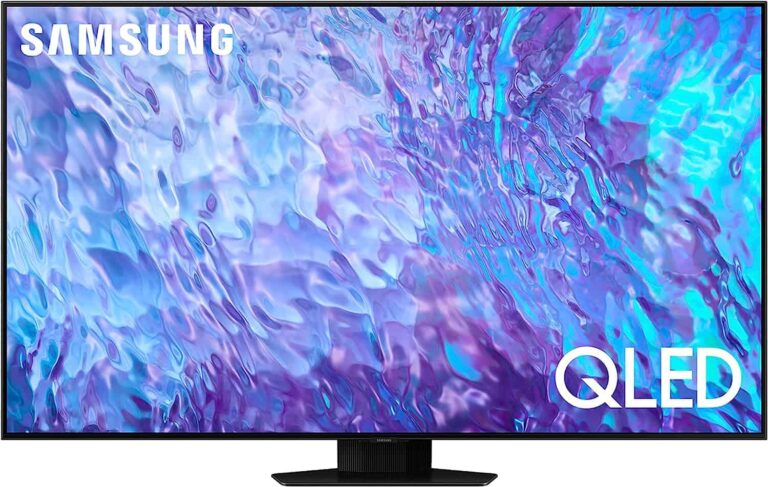
The Samsung Q80C is the perfect TV to watch Super Bowl LVIII

0

[ad_1]

The Super Bowl is coming up pretty quickly here, on February 11, and the Samsung Q80C is going to be the perfect TV to watch the big game on. And today, you can grab the Q80C at some of its lowest prices ever. Here’s the breakdown per size:

  • 50-inch: $897 (reg. $997)
  • 55-inch: $997 (reg. $1,197)
  • 65-inch: $1,097 (reg. $1,397)
  • 75-inch: $1,497 (reg. $1,897)
  • 85-inch: $1,897 (reg. $3,297)
  • 98-inch: $4,997 (reg. $7,997)

The Samsung Q80C QLED TV is a great choice for anyone looking for a high-quality, feature-rich TV. With its stunning picture quality, immersive sound, and smart features, the Q80C is sure to impress.

One of the biggest selling points of the Q80C is its picture quality. The TV uses Quantum Dot technology to deliver over a billion colors, resulting in incredibly vibrant and lifelike images. The Q80C also supports HDR10+, which provides a wider range of colors and contrast for an even more immersive viewing experience.

In addition to its excellent picture quality, the Q80C also offers great sound. The TV is equipped with a 2.2.2-channel speaker system that delivers clear, powerful sound. The Q80C also supports Dolby Atmos, which creates an immersive soundscape that surrounds you with audio.

The Q80C is also packed with smart features. The TV runs on Samsung’s Tizen operating system, which gives you access to a wide range of streaming apps, including Netflix, Hulu, and Amazon Prime Video. The Q80C also supports voice control, so you can control the TV with your voice.

Overall, the Samsung Q80C QLED TV is a great choice for anyone looking for a high-quality, feature-rich TV. With its stunning picture quality, immersive sound, and smart features, the Q80C is sure to impress.

You can pick up the Samsung Q80C QLED TV from Best Buy at the link below.

Buy at Amazon

[ad_2]

Source link

45K+ Publicly Exposed Jenkins Instances Vulnerable to RCE Attacks

0

[ad_1]

It was previously reported that Jenkins was discovered with a new critical vulnerability, which was associated with unauthenticated arbitrary file reads that can be utilized by threat actors to read sensitive files on the server. The CVE was mentioned as CVE-2024-23897, and the severity is yet to be categorized.

There were also reports mentioning a massive scan of Jenkins servers over the internet, according to a security researcher. However, currently, it has been reported that there are more than 45,000 publicly available Jenkins instances online.

Document

Run Free ThreatScan on Your Mailbox

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Try Trustifi Free Threat Scan with Sophisticated AI-Powered Email Protection .

Publicly Exposed Jenkins Servers

According to the reports shared with Cyber Security News, Jenkins has a total market share of 43%, which is a massively higher quadrant number than other CI/CD software. This makes Jenkins one of the most used open-source CI/CD servers across organizations.

Moreover, the vulnerability CVE-2023-23897 does not require any authentication on vulnerable instances. Though there is a specific criterion for exploiting the vulnerable instances, it is still deemed as a critical vulnerability due to the ease of exploitation.

For a security researcher or threat actor to find if a specific Jenkins instance is vulnerable, they do not require any kind of special skills. A simple cURL command with only the IP address and port number of the server is more than enough to confirm if an instance is vulnerable.

45000 Servers exposed

Shadowserver reported that there were more than 45,000 servers that could be exploited if they had been misconfigured. Adding to the threat, another vulnerability was also reported that was in combination with CVE-2023-23897. 

This vulnerability was an unauthenticated, remote code execution vulnerability that could allow a threat actor to execute arbitrary commands on the vulnerable instance. However, as per Shadowserver reports, China has the highest number of Jenkins instances, accounting for nearly 12,000 servers.

Followed by the United States of America with 11,830 servers. Germany and India have approximately 3000 and 2500 servers, respectively. Other countries had multiple Jenkins servers exposed over the internet.

Nevertheless, it is recommended that all organizations upgrade the Jenkins servers to the latest versions to prevent these servers from getting exploited by threat actors.

[ad_2]

Source link