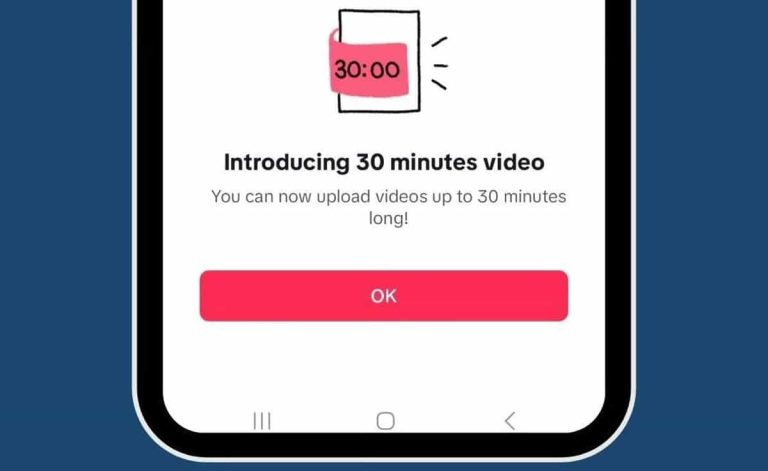
TikTok planning 30-minute video uploads to compete with YouTube

0
[ad_1]

TikTok will soon offer 30-minute video uploads, it seems, as it’s aiming at YouTube. This information comes from Matt Navarra, a social media consultant. He spotted this option in the iOS beta version of the app.

TikTok seems to be planning to offer 30-minute video uploads

Now, Navarra did mention that some users spotted this option in the Android beta version of TikTok as well. So the change is not exclusive to iOS, not even in the testing phase. Considering that it’s already in beta, we could end up seeing it on offer soon.

TechCrunch reached out to TikTok but did not get a response from the company. It seems to be pretty obvious what TikTok is doing, though. The company completely rules short-form video content and is looking to get more into YouTube’s territory.

TikTok has been slowly, but surely, increasing the duration cap of videos. The original videos were capped out at 15 seconds, then it was bumped up to a minute. Later it was expanded to three minutes, and then 10 minutes.

TikTok actually started testing 15-minute video uploads not that long ago, only a couple of months ago. Well, it seems like the company is aiming even higher than that.

TikTok is aiming at YouTube with this change

While TikTok is trying to up the video limit cap in order to compete with YouTube, YouTube did the opposite. YouTube Shorts are basically competing directly with TikTok’s short-form content and they’ve been around for years.

Needless to say, 30-minute videos are a completely different beast. That move would open TikTok to various new creators who like to go in-depth with their content. That would enable various reviews and all kinds of other content.

At that point, we could even watch full sitcom episodes on TikTok, theoretically. Some studios may even end up using TikTok for that purpose. It would be nice to be able to filter the length of videos you’re getting, though.

If TikTok does make this move, a lot of users could end up with videos that are too long for their liking. The vast majority of TikTok users still expect really short and yet entertaining videos, not long-form content. Who knows, perhaps TikTok is planning some sort of a filter, we’ll see.

TikTok 30 minute video testing


[ad_2]
Source link

Snapdragon 8 Gen 4 could launch sooner than expected

0
[ad_1]

Qualcomm’s Snapdragon 8 Gen 4 processor could launch sooner than expected. That info is based on something a well-known tipster said. The information is coming from Digital Chat Station and was shared via Weibo.

The Snapdragon 8 Gen 4 could launch sooner than expected

The tipster said that internal testing of the chip is progressing well. He did not specifically mention anything related to the launch date of the Snapdragon 8 Gen 4, but he did mention phones that will be fueled by that processor.

He mentioned that those phones will enter mass production in September, which is a bit earlier than usual. GizmoChina seems to think the tipster is talking about the Xiaomi 15 series, amongst others, which is a possibility.

In any case, based on the timing of mass production of these phones, the Snapdragon 8 Gen 4 could indeed launch a bit sooner than expected. The Snapdragon 8 Gen 3 launched on October 24, while the Snapdragon 8 Gen 2 arrived in November.

The Snapdragon 8 Gen 3 arrived on October 24 last year

Qualcomm seems to be moving these launch dates up constantly. Well, that will be the case if the Snapdragon 8 Gen 4 does indeed launch early. Based on what we’ve seen thus far, it will arrive earlier than October 24, perhaps even in September.

Do take all of this with a grain of salt, though, as it’s based on mass production timelines for smartphones expected to be fueled by the Snapdragon 8 Gen 4. Even though those timelines do come from a reliable source.

The Snapdragon 8 Gen 4 will be a 3nm processor, as Qualcomm will stick with TSMC for the production of that chip. That chip is codenamed ‘Sun’, and it allegedly adopts a 2+6 structure. The design and performance of Qualcomm’s Oryon architecture has been “significantly improved”, allegedly. That chip is expected to bring a performance leap to the table.

There’s still a lot of time before the Snapdragon 8 Gen 4 is expected, so let’s wait for more information before making any conclusions.


[ad_2]
Source link

Kasseika Ransomware Exploits Driver Functionality to Kill Antivirus

0
[ad_1]

Ransomware is a tool that hackers use to extort money from their targets like individuals, businesses, and governments. The malware encrypts the target’s data and demands payment to unlock it.

This malicious strategy increases the possibility of payment by giving threat actors financial profits in the form of bitcoin in exchange for vital information.

Cybersecurity researchers at Trend Micro recently discovered that threat actors are actively exploiting the driver functionality to kill Antivirus programs.

Document
Run Free ThreatScan on Your Mailbox

Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Try Trustifi Free Threat Scan with Sophisticated AI-Powered Email Protection .

Kasseika Ransomware Kill’s Antivirus

In 2023, Kasseika ransomware joined the BYOVD trend, following Akira, BlackByte, and AvosLocker. They used Martini driver to disable antivirus programs that resemble the BlackMatter with pseudo-ransom extensions. 

This suggests a mature actor with access to BlackMatter’s source code previously linked to DarkSide and ALPHV. Since its 2021 shutdown, exclusive ransomware groups have adapted BlackMatter’s old code for new strains.

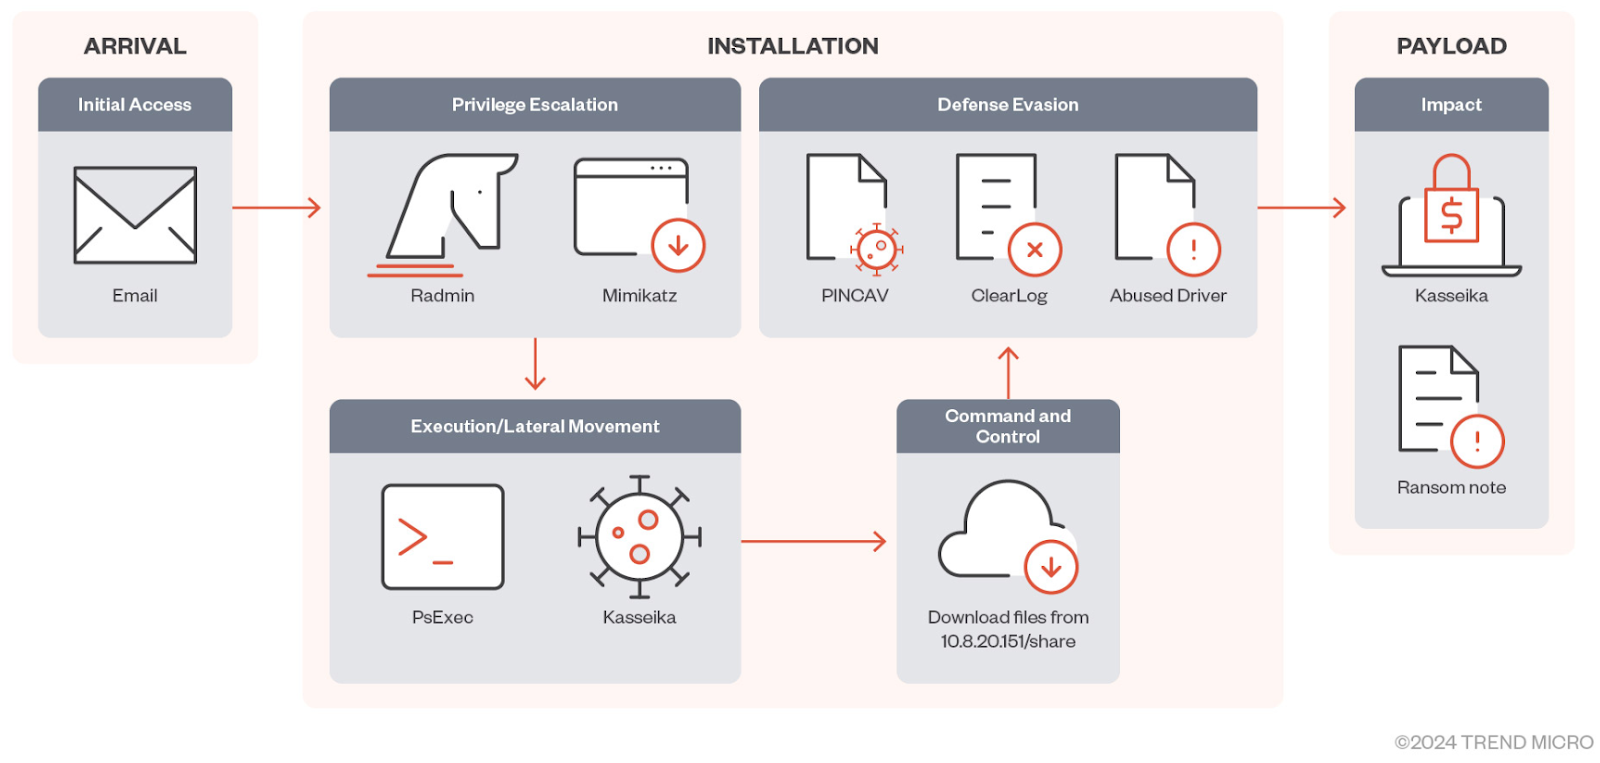
Infection chain (Source - Trend Micro)
Infection chain (Source – Trend Micro)

Kasseika ransomware employs targeted phishing for initial access by gathering credentials and using PsExec to move within the network. 

It exploits Martini.sys to disable security tools, which helps terminate processes and leverages FindWindowA API to detect security-related processes. 

The script ensures a clean state by setting up flexible variables for future use. Kasseika transfers files, terminates antivirus processes with Martini.exe, and also executes smartscreen_protected.exe as its ransomware binary. The Clear.bat is then executed to erase traces of the operation.

Kasseika ransomware is a Themida-packed 32-bit Windows PE file that employs robust obfuscation and anti-debugging. 

It terminates processes accessing Windows Restart Manager by modifying the registry keys and enumerating session hashes before encryption. 

It erases shadow copies using WMIC queries and decrypts its extension with Base64 encoding. Kasseika uses ChaCha20 and RSA from CryptoPP by generating a modified matrix for encryption. 

After renaming and dropping CBhwKBgQD.README.txt as a ransom note, Kasseika changes the system wallpaper post-encryption.

Kasseika ransomware employs wevutil.exe to discreetly wipe Application, Security, and System event logs that help in evading easy detection and response by security tools.

Recommendations 

Here below we have mentioned all the recommendations:-

  • Grant admin rights only when necessary.
  • Regularly update security products and perform scans.
  • Secure backups for critical data.
  • Practice safe email and website habits.
  • Encourage reporting of suspicious emails and files.
  • Educate users on social engineering risks regularly.

Organizations can enhance security with a multilayered strategy by covering the endpoints, email, web, and network entry points. 

The detection of malicious components and suspicious behavior by security solutions is crucial for enterprise protection.


[ad_2]
Source link

Tesla, Sony, Alpine Players Breached on Day One

0
[ad_1]

Pwn2Own Automotive 2024 takes place in Tokyo, Japan, from January 24 to 26.

The Pwn2Own Automotive 2024 hacking contest, taking place in Tokyo, Japan from January 24 to January 26, focuses on loopholes in automotive technologies. Tesla is the contest’s sponsor with VicOne and Trend Micro’s Zero Day Initiative as co-hosts.

During the context, they will demonstrate zero-day exploits targeting Model 3/Y or Model S/X systems, including the infotainment, modem, tuner, wireless, and autopilot systems. The top prize for zero-day exploits will be $200,000 and a Tesla car.

On its first day, many vulnerabilities were highlighted, including weaknesses in Tesla’s modem, Sony’s infotainment systems, and Alpine’s car audio players, raising concerns about the security of connected vehicles.

Security researchers hacked multiple fully patched EV charging stations and infotainment systems. The NCC Group EDG team won $70,000 for hacking the Pioneer DMH-WT7600NEX infotainment system and the Phoenix Contact CHARX SEC-3100 EV charger exploiting zero days.  

Sina Kheirkhah successfully attacked ChargePoint Home Flex, earning $60,000 and six Master of Pwn Points. Tobias Scharnowski and Felix Buchmann attacked Sony XAV-AX5500 for $40,000 and four Master of Pwn Points. Gary Li Wang exploited the Sony XAV-AX5500 using a stack-based buffer overflow.

Security researchers successfully hacked a Tesla Modem and earned $722,500 in total in awards for identifying three bug collisions and 24 unique zero-day exploits. Synacktiv Team completed a 3-bug chain against Tesla Modem and JuiceBox 40 Smart EV Charging Station, earning $100,000 and $60,000 along with 10 and 6 Master of Pwn Points, respectively.

This means, the team chained three zero-day bugs to gain root permissions on a Tesla Modem. The Synacktiv Team also successfully attacked the Ubiquiti Connect EV Station, earning six Master of Pwn Points and $60,000.

A third exploit chain targeted the ChargePoint Home Flex EV charger, which earned security researchers $16,000 in cash and $295,000 in prizes.

The PCAutomotive Team successfully targeted the Alpine Halo9 iLX-F509 using a UAF exploit, earning $40,000 and 4 Master of Pwn Points. They discovered a vulnerability in Alpine’s car audio player, allowing arbitrary code execution. This could potentially give attackers control over the audio system, allowing them to play loud noises or inject malicious code into other connected systems.

RET2 Systems also achieved 6 Master of Pwn Points and $60,000 for exploiting a 2-bug chain against the Phoenix Contact CHARX SEC-3100. The PHP Hooligans / Midnight Blue team successfully targeted a Sony XAV-AX5500, earning $20,000.

For additional insights on Pwn2Own Automotive’s day 1 results, check out Zero Day Initiative’s blog.

The Pwn2Own exploits highlight the growing vulnerability of cars to cyberattacks due to the increasing integration of technology in vehicles. While researchers disclose their findings to help manufacturers fix vulnerabilities, car owners must remain vigilant.

  1. 6 of the Best Crypto Bug Bounty Programs
  2. Bug bounty: Hack Tesla Model 3 to win your own Model 3
  3. Pwn2Own 2023: Tesla Model 3, Windows 11, Ubuntu Pwned

[ad_2]
Source link

Android 14 QPR2 Beta 3.1 is now out with bug fixes

0
[ad_1]

Google is now rolling out Android 14 QPR2 Beta 3.1, focusing on resolving numerous bugs and improving system stability. This release comes following the Android 14 QPR2 Beta 3 update released earlier this month, which introduced significant UI changes. Notably, both the Android 14 QPR2 Beta 3 and Android 14 QPR2 Beta 2 released in December have already addressed several bugs.

The latest update, identified as AP11.231215.009, includes the January 2024 security patch. It is available for all Pixel phones starting from the Pixel 6 series to the Google Pixel 8 series. It also includes the Google Pixel 5a, Pixel tablet, and the Google Pixel Fold.

Issues fixed in the Android 14 QPR2 Beta 3.1 update

Among the notable issues addressed in this release are improvements to the Game Dashboard overlay, unlocking failures with always-on display mode and fingerprint, Quick Settings dialog height irregularities, incorrect default search engine settings after a cloud backup restore, display area update issues in accessibility settings, and audio quality degradation during calls or recording using the microphone.

The update also tackles problems related to device keyboard settings, missing translations for various languages, work profile icons not displaying for paused work apps, rendering issues with shaders, incorrect scaling of icons in picture-in-picture mode, launcher glitches for foldable devices, and unresponsiveness of the app divider for foldable devices in split-screen mode. Additionally, various issues impacting system stability, performance, connectivity, camera, and accessibility have been addressed.

Although some known problems still exist

However, Android 14 QPR2 Beta 3.1 is not without its known problems. Some users may experience unexpected reboots due to a native crash issue, and a system connectivity issue may cause call failures. Additionally, foldable or tablet devices may encounter UI navigation handle visibility problems. That is per course when it comes to beta builds, though. This is definitely not ready to be used instead of stable software, but it’s getting there.


[ad_2]
Source link

Apple could introduce fees and restrictions for downloads outside its App Store

0
[ad_1]

As the new European tech rules, known as the Digital Markets Act (DMA), get ready to kick in soon, Apple is getting set for a future where it has to allow its users to download apps from places other than its App Store.

The Cupertino tech giant hasn’t spilled the beans on how exactly sideloading will go down. However, according to The Wall Street Journal, it looks like developers might not get a free pass to bypass the company’s fees and app review guidelines after all.

Thanks to the new European law aimed at loosening Apple’s tight hold on apps, folks in the EU would finally be able to download software onto their iPhones or iPads without relying solely on the App Store.

Yet, insiders familiar with Apple’s moves indicate that the company intends to collect fees from developers who provide downloads outside the App Store. Additionally, the company aims to retain the authority to review every app downloaded outside its App Store. It’s worth noting that these plans from Apple haven’t been officially revealed and are subject to change.

The proposed restrictions and fees might reignite tensions with app developers, as some had anticipated the new law would enable them to distribute their apps to users without being subject to Apple’s restrictions or what they perceive as hefty commissions.

Just a while back, Spotify, which is already gearing up with new download choices in anticipation of the upcoming changes, and Epic Games, the creator of Fortnite, slammed Apple’s recently revealed policies that permit third-party payment systems, aligning with a US federal court decision.

Following a prolonged legal tussle with Epic Games, the new regulations decree that developers must still fork out a substantial 27 percent commission on transactions conducted outside of the App Store (though smaller developers will face a lower 12 percent charge).

Apple’s reaction to the fresh EU regulations sets the stage for another potential battleground in the company’s global struggle to uphold control over third-party software and the substantial profits that accompany it.

Back in 2022, the European Union greenlit the DMA, intending to curb the purportedly anticompetitive tactics of tech firms. The DMA puts the brakes on gatekeepers, including Apple, Google, Microsoft, Amazon, Meta, and TikTok, preventing practices such as self-preferencing, data exclusivity, and unfair trading.

[ad_2]
Source link

Users Falling Victim to Social Engineering Scams

0
[ad_1]

Check Point’s Live Cyber Threat Map identified 20,000 instances of QR code phishing and malware attacks within two weeks, highlighting the vulnerability of QR codes to cybercriminals. 

Check Point Software Technologies, a cybersecurity solutions provider, has published new research illustrating a typical QR code attack. In this attack, scammers utilize QR codes to redirect users to a credential harvesting page, adjusting the redirection chain based on the user’s device.

The goal is to install malware and steal credentials. Check Point’s Live Cyber Threat Map identified 20,000 instances of QR code attacks within two weeks, highlighting the vulnerability of QR codes to cyber criminals. 

Hackread.com previously reported that Check Point Research noticed a whopping 587% increase in QR-code-based phishing attacks between August and September 2023. This could be attributed to the lack of QR code protection in email security solutions and the widespread use of scanning QR codes. 

Security vendors worked to develop new protections, but threat actors responded with a new variation of QR code attacks. Recently Bitdefender observed a rise in YouTube stream-jacking campaigns using deepfake videos for cryptocurrency theft. YouTube stream-jacking is a cybercrime where criminals steal accounts using livestream pop-ups, QR codes, and malicious links. 

In October 2023, SlashNext reported a rise in QR-code-based phishing attacks using Quishing and QRLJacking. Quishing involves circulating a QR code with malware download links on various platforms, redirecting users to phishing websites or downloading malware.

It happens because QR codes have several layers of obfuscation, including the QR code itself, a blind redirect to another domain, and an anti-reverse engineering payload. These layers can be used to redirect users to suspicious activities or fake login pages. Hackers can increase their success rate by navigating conditional redirection.

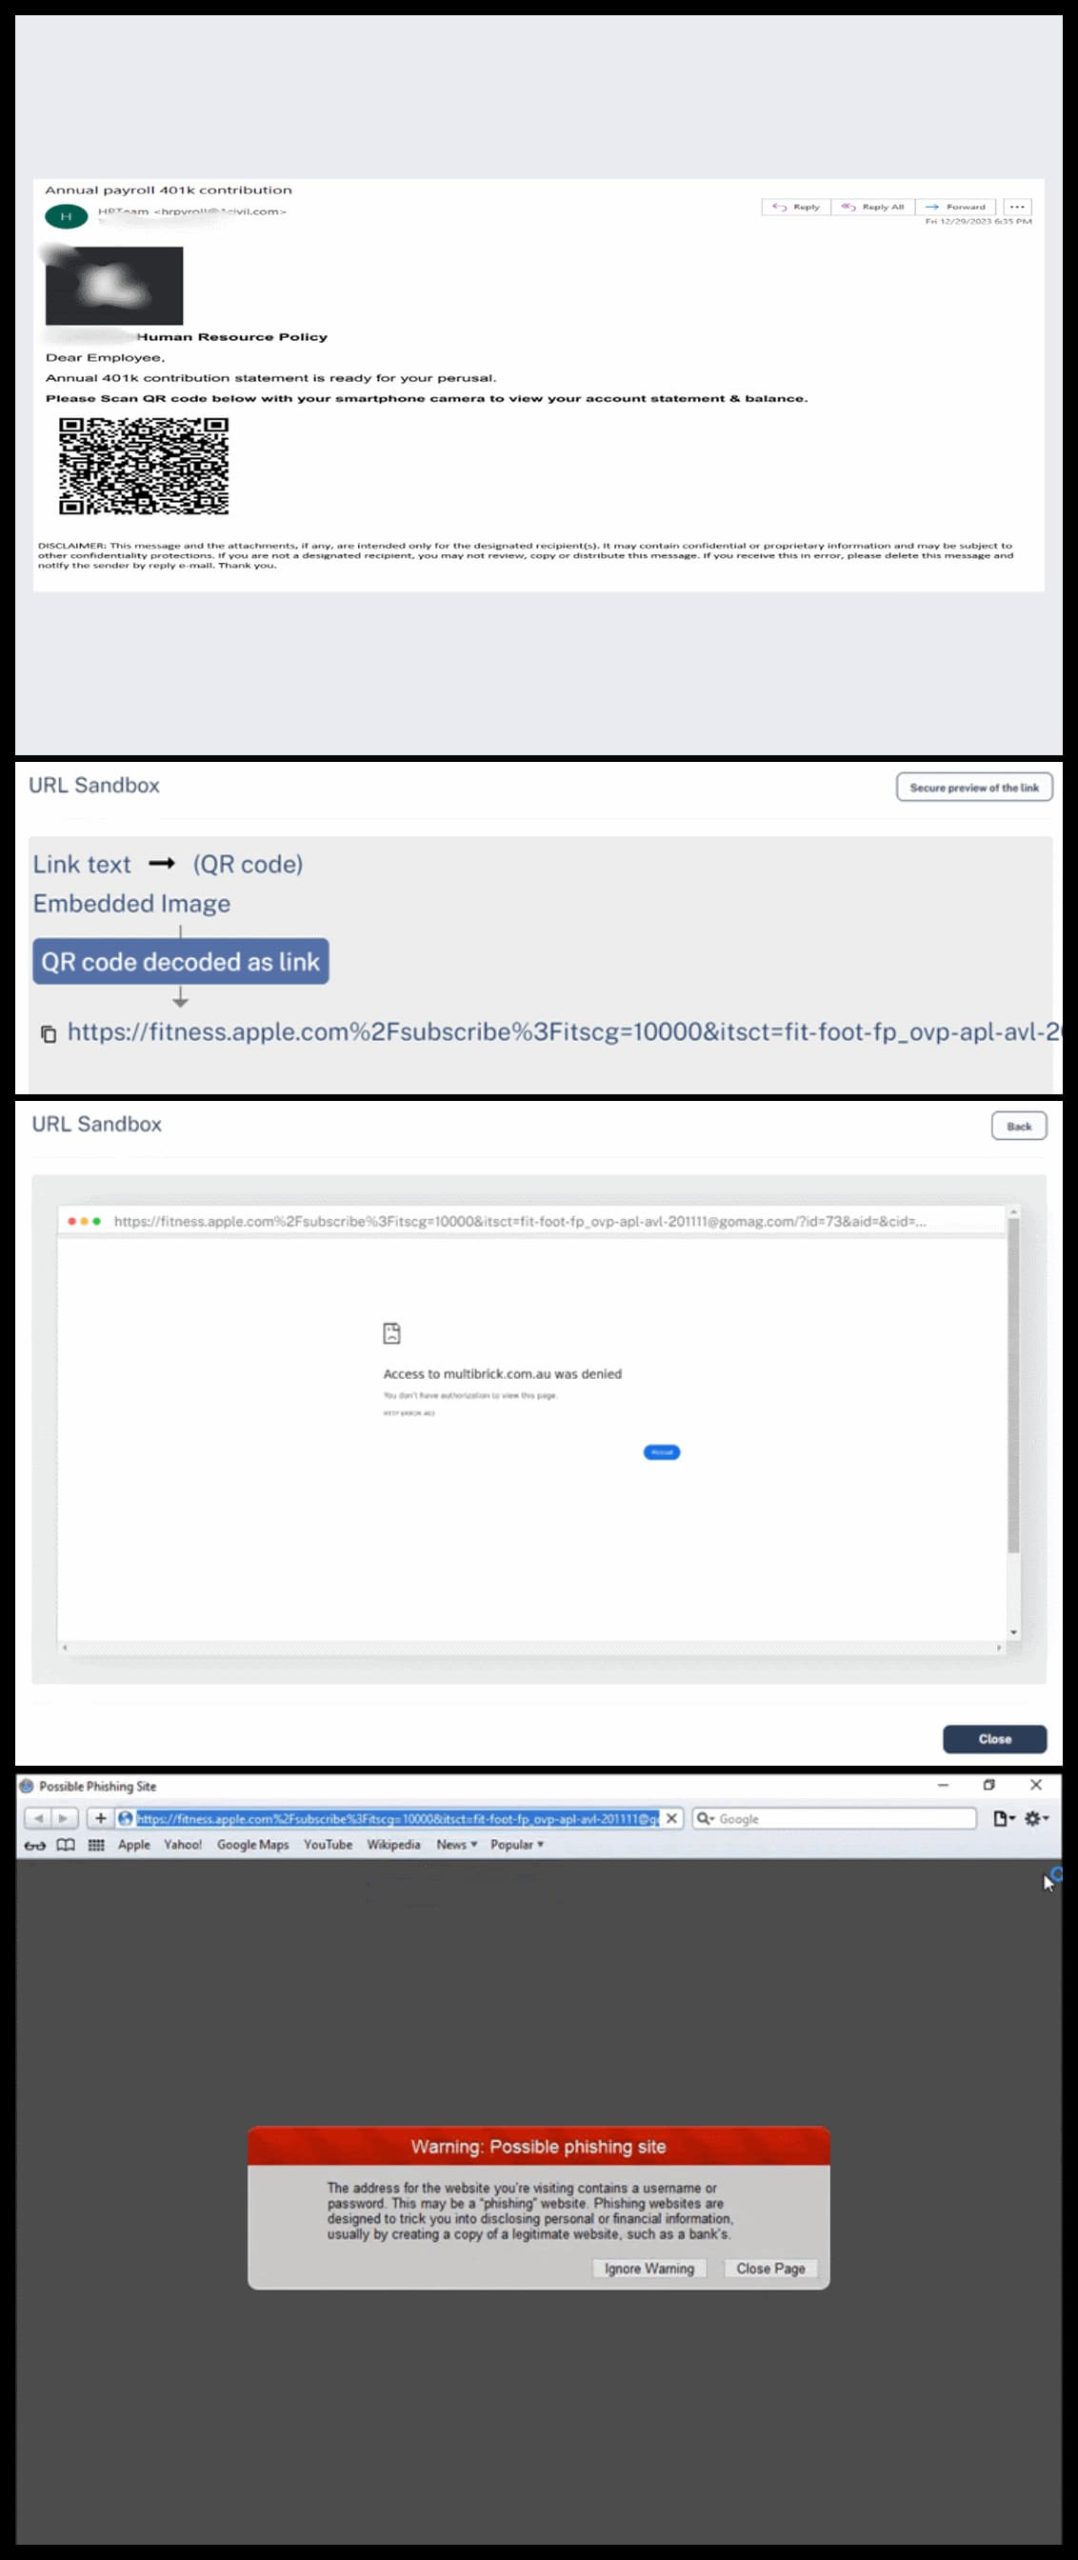
Attacks sending QR codes with conditional redirection, using social engineering techniques and BEC 3.0. Check Point researchers provide multiple examples of how these phishing attempts will look like. In one such instance, users are requested for an annual 401K contribution statement by scanning the QR code. 

“The QR code has a conditional destination point based on browser, device, screen size, and more,” directed to different pages depending on these parameters, Check Point Research noted in their report shared with Hackread.com.

Users’ device type affects the display of links though, as Mac users see one link, while Android users see another. However, the result will be the same. Nevertheless, these attacks highlight the convincing nature of phishing attempts and the importance of multi-layered cybersecurity in preventing the consequences of such attacks.

Typically, default security layers will let go if the first redirect is clean. However, a complete security solution can prevent these attacks by blocking multiple layers. This includes email security, browser security, mobile security, anti-malware, and post-delivery security. These layers work together to block suspicious behaviour, inspect websites, and decode QR code attacks.

QR Code Phishing Soars 587%: Users Falling Victim to Social Engineering Scams
Phishing email and tactics employed by scammers in some of the attacks – Click and zoom for better quality (Credit: Check Point)

However, since such attacks are difficult to detect or thwart due to multiple obfuscation layers, security professionals need AI-based security, the ability to decode QR code attacks, and multiple layers of protection. By implementing these best practices, security professionals can substantially prevent phishing attacks and protect their systems.

  1. Trezor Data Breach Exposes Email and Names of 66,000 Users
  2. Phishing 3.0: Crooks Leverage AWS in Deceptive Email Campaigns
  3. Inferno Drainer Phishing Nets Scammers $80M from Crypto Wallets
  4. Global malspam targets hotels, spreading Redline and Vidar stealers
  5. New Phishing Scam Hooks META Businesses with Trademark Threats

[ad_2]
Source link

Samsung patent shows a smartphone with extendable display

0
[ad_1]

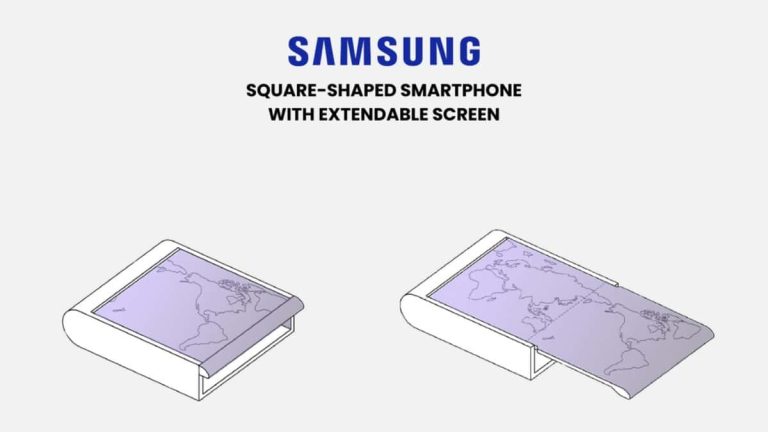
A newly disclosed patent of a ‘square-shaped Samsung smartphone’ with an extendable display is capturing attention as it addresses some challenges associated with flexible displays in foldable phones. David Kowalski on X and Websiterating collaboratively discovered and shared this patent.

The problem that this rollable display patent solves:

Most smartphone manufacturers have significantly improved the hinge mechanism on foldable devices such as the Galaxy Z Fold 5 or the OnePlus Open, to prevent the expensive display panel from cracking over time. However, the crease on the display panel is something that takes some time to get used to.

In the foldable design, the display folds with a very small radius of curvature, which results in an unwanted crease over the hinge area. This new extendable form factor will reportedly increase the radius of the curved shape and possibly eliminate the crease. Notably, this ‘square-shaped Samsung smartphone with an extendable screen‘ also solves the problem of the spring-back effect in metal layers of extendable displays.

Samsung extendable display patent 2

The patent talks about a display panel with three distinct portions

One of the key features introduced by the patent is a display panel with three distinct portions. It highlights parallel alignment and unique connections. The design incorporates a support member with three support parts, including a curved portion. It contributes to the flexibility and resilience of the display.

Various portions of the display panel extend in different directions, adding versatility to the device’s form factor. The patent also outlines a manufacturing method involving the use of a sliding core for bending, filling the support member, and bonding components with adhesive.

This patent from Samsung represents a significant stride in the development of flexible display technology. Users can expect more robust, durable, and versatile foldable devices in the future. The innovations introduced in the patent may usher in a new generation of displays that seamlessly blend flexibility with reliability. This opens doors to a range of creative and practical applications such as a phone with rollable display.


[ad_2]
Source link

Apple will be first to use TSMC’s 2nm chips

0
[ad_1]

It seems like Apple will be the very first company to use TSMC’s 2nm chips. This information comes from DigiTimes. The source says that Apple is “widely believed to be the initial client to utilize the process”, and that info is acquired from sources that the site spoke to.

Apple could become the first company to get its hands on TSMC’s 2nm chips

TSMC is expected to begin production of 2nm chips in the second half of next year. We’re not sure if the iPhone 17 models will get it, but it sure looks like a possibility. We’ll have to wait and see. If not the iPhone 17 series, then the iPhone 18 devices for sure.

With that being said, some of you may not know what that means. Well, the 2nm term refers to the architecture and design used to build that chip. The decreases in node size correspond to a smaller transistor size. The more transistors that can be placed on a processor, the more of a speed boost the chip gets. Also, power efficiency gets improved too.

The Apple A17 Pro is a 3nm processor

Apple’s current-gen flagship processor, the Apple A17 Pro, is a 3nm processor. Apple’s M3 series chips are also built on the 3-nanometer node. The jump from 5 to 3nm nodes brought various advantages to the table.

2nm nodes are set to move things forward even more. TSMC is even rumored to be working on 1nm nodes. The company is actually already preparing for manufacturing of such chips, based on a recent report.

2nm chip manufacturing will be more complex

It’s also worth saying that TSMC’s shift to 2nm tech will also see the company adopt GAAFET (gate-all-around field-effect transistors) with nanosheets, instead of FinFET. That will make manufacturing more complicated, that’s for sure.

Do note that TSMC still hasn’t confirmed anything regarding its 2nm chips, so it remains to be seen how accurate this report is.


[ad_2]
Source link

Xiaomi 14 Ultra camera module appears with some juicy details

0
[ad_1]

The Xiaomi 14 Ultra camera module has just appeared online. Along with it, a tipster has also revealed some camera details. This information comes from Anvin, who shared it via X (formerly known as Twitter).

The Xiaomi 14 Ultra camera module appeared, along with some specs

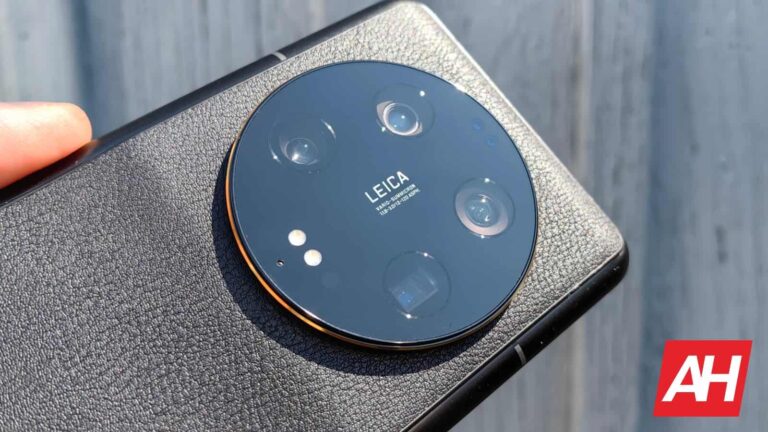
You can see what the camera module will look like below. Truth be said this is just the top part of the entire camera module, but it does reveal where the cameras will sit. Yes, there will be four of them, along with some additional sensors.

Xiaomi 14 Ultra alleged camera module

Now, Xiaomi is said to utilize Sony’s LYT-900 (LYTIA) camera sensor for the main camera on the phone. That is the same camera that OPPO used in the OPPO Find X7 Ultra. It will feature a VARIO-SUMMILUX 1:1.63-2.5/12-120 aspherical lens from Leica on top of that sensor. You’ll also get f/1.63-f/2.5 variable aperture as part of the package.

The tipster also mentioned that the main camera will be backed by a 120mm periscope telephoto lens. That is basically everything Anvin shared thus far.

Previously shared information is a bit different

Now, it’s worth noting that this info kind of goes against what Digital Chat Station shared back in October. Digital Chat Station is way more prominent when it comes to tips and is rarely wrong, so take the information Anvin shared with a grain of salt.

Digital Chat Station said that an f/1.6-f/4.0 variable aperture will be included, which is quite different from what Anvin reported. Just to be clear, we’re talking about multi-stop aperture, not dual-stop like the company included in the Xiaomi 13 Ultra.

Digital Chat Station also said that four 50-megapixel cameras will sit on the back of the phone. If we had to guess, we’d say that the device will include a wide main camera, an ultrawide unit, a telephoto camera, and a periscope telephoto unit.

It’s also worth noting that a new camera kit with a battery will be available for the phone. The Xiaomi 14 Ultra is expected to launch in April, but it could arrive sooner.


[ad_2]
Source link