Aembit Announces New Workload IAM Integration with CrowdStrike to Help Enterprises Secure Workload-to-Workload Access

0

[ad_1]

Silver Spring, Maryland, January 30th, 2024, Cyberwire

Aembit Becomes the First Workload IAM Platform to Integrate with the Industry-Leading CrowdStrike Falcon Platform to Drive Workload Conditional Access

Aembit, the Workload Identity and Access Management (IAM) platform that enables DevOps and security teams to discover, manage, enforce and audit access between workloads, today announced the availability of a new integration with the industry-leading CrowdStrike Falcon® platform to give enterprises the ability to dynamically manage and enforce conditional access policies based on the real-time security posture of their applications and services. This integration signifies a significant leap in Aembit’s mission to empower organizations to apply Zero Trust principles to make workload-to-workload access more secure and manageable. 

Workload IAM transforms enterprise security by securing workload-to-workload access through policy-driven, identity-based, and secretless access controls, moving away from the legacy unmanaged, secrets-based approach. 

Through this partnership, the Aembit Workload IAM solution checks to see if a CrowdStrike Falcon agent is running on the workload and evaluates its real-time security posture to drive workload access decisions to applications and data. With this approach, now enterprises can protect their workloads from unauthorized access, even against the backdrop of changing conditions and dynamic access requirements. Additional customer benefits from this partnership include:

  • Managed Workload-to-Workload Access: Enforce and manage workload access to other applications, SaaS services, and third-party APIs based on identity and policy set by the security team, driving down risk.
  • Seamless Deployment: Drive consolidation by effortlessly integrating the Aembit Workload IAM Platform with the Falcon platform in a few clicks, providing a unified experience for managing workload identities while understanding workload security posture.
  • Zero Trust Security Model: Embrace a Zero Trust approach, ensuring that every access request, regardless of the source, is verified before granting access rights. Aembit’s solution enforces the principle of least privilege based on identity, policy, and workload security posture, minimizing potential security vulnerabilities.
  • Visibility and Monitoring: Gain extensive visibility into workload identities and access permissions, enabling swift detection and response to potential security threats. Monitor and audit access logs based on identity for comprehensive security oversight.

This industry-first collaboration builds on the recent CrowdStrike Falcon Fund strategic investment in Aembit, underscoring the global cybersecurity leader’s commitment to fostering innovation within the space. The investment reflects the recognition of the growing demands for securing workload access.

Aembit Workload IAM is available in the CrowdStrike Marketplace, a one-stop destination and world-class ecosystem of third party products. See more here. 

Supporting Quotes:

“Today’s attacks are increasingly identity-based, which is why enforcing identity-protection across the enterprise at every layer is critical for modern security. The CrowdStrike Falcon platform is rapidly becoming the center of cybersecurity’s ecosystem. This integration with Aembit enables organizations to secure machine identities as part of a holistic approach to security.” said Daniel Bernard, chief business officer at CrowdStrike.

“The launch of the Aembit Workload IAM Platform on the CrowdStrike Marketplace represents a significant advancement in our joint mission to securely manage workload-to-workload access,” said David Goldschlag, CEO and co-founder at Aembit.

“We are excited to bring the power of Aembit’s Workload IAM to the CrowdStrike Marketplace. This collaboration enables us to deliver Zero Trust for workload access in a way that simplifies and automates the evolving security challenges faced by DevOps and DevSecOps teams,” said Apurva Dave, CMO at Aembit.

Press Contact

Apurva Dave

Chief Marketing Officer

[email protected]

About Aembit

Aembit is the Workload Identity and Access Management (IAM) Platform that lets every business safely build its next generation of applications by inherently trusting how it connects to partners, customers, and cloud services. Aembit provides seamless and secure access from your workloads to the services they depend on, like APIs, databases, and cloud resources, while simplifying application development, delivery, compliance, and audit. Follow Aembit on LinkedIn.

Learn: Website or CrowdStrike Marketplace

Follow: LinkedIn | Twitter

Use: Free-Forever Tier

Contact

Chief Marketing Officer
Apurva Dave
Aembit
[email protected]
(202) 525-6661


[ad_2]

Source link
TikTok wants you to shop for anything in your videos

0

[ad_1]

Very few of the companies you see nowadays stick to one thing. A lot of the time, companies dip their toes into different industries in order to expand their appeal. For example, we all know TikTok as the video streaming company. Well, The ByteDance-owned app is also looking to be an e-commerce company. According to a new report, TikTok is working on a feature to add shoppable links to any video.

The company is actually putting a lot of work and effort into becoming an e-commerce company. It’s been working on building its e-commerce business in the States for some time. In fact, TikTok hopes to make $17.5 billion this year by selling products in the U.S. Its plans are to be an alternative to Amazon, giving people a friendly and video-first interface to navigate when looking for new products to buy.

TikTok wants shoppable links in every video

This sounds like the kind of overbearing AI-driven feature that Google would unveil. According to a new report, TikTok wants to let people shop for items from every video on the platform. Right now, creators can promote an item on their video and post a link to where people can buy that item. However, this approach only allows people to buy a limited number of devices.

What the company wants to do is develop a feature that can analyze objects inside of videos and identify them. When it does that, it will be able to find a link to where you can buy that item. So, if a person is using a certain type of iPhone in the video or a certain dress, the technology will be able to analyze that and provide a link to where a person can buy one of those items.

Obviously, this picture will not be 100% accurate, and not every item in a video will be available to buy. However, TikTok will still analyze the video and give you links to similar objects. So, if a user is wearing a certain shirt that cannot be bought anywhere, then TikTok will give you a link to buy a similar-looking shirt.

Right now, this feature is in early testing, so there’s no telling when exactly it’s going to launch to the public. We will just have to wait for it to surface.

[ad_2]

Source link

A Neuralink chip has finally been implanted into a human

0

[ad_1]

After receiving the green light from the FDA last year, a Neuralink chip has been implanted into a human in a revolutionary first. The announcement came from Elon Musk himself on his social media platform, X. Musk is the founder of Neuralink, though he does not actively hold an executive position at the company. The tweet was short and didn’t divulge much, but it seems the operation has been a success.

What is Neuralink?

Neuralink is one of the most ambitious projects eccentric billionaire Elon Musk has ever fathered. His record includes super quick electric cars, autonomous driving, and rockets that can land back on Earth, amongst other notable achievements. Neuralink, like the projects mentioned above, is a science fiction concept trying to be made a reality.

The company envisions an implantable brain-computer interface. This interface will allow users to control devices using just their thoughts. Musk hopes this technology will one day let people experience completely alien realities. The company lauds its product as “cosmetically invisible”, which would translate to many more potential customers.

The First Neuralink human test run is a go

The FDA gave Neuralink permission last year to begin recruiting human testers. Candidates with quadriplegia and ALS were preferred for the trial runs. Neuralink had mentioned then that their initial goal would be allowing users to “control” a keyboard and computer cursor. Understandably, it’s no surprise the company saw many willing candidates hoping for a solution to their disabilities. On January 30th, 2024, Elon Musk tweeted the following:

That’s not much to go on, but it seems the operation was a success. “promising neuron spike detection” possibly alludes to the chip functioning within acceptable and expected parameters.

Reception to the news

Neuralink has always had its fair share of critics, and there was no shortage of people citing their skepticism. These critics only gained more fuel when the company’s initial tests on monkeys led to some serious complications. For example, the test subjects had suffered from seizures, brain swelling, and paralysis. Elon Musk later confirmed that no monkey had actually died from a Neuralink implant.

As expected, memes also flooded the replies to Musk’s tweet above. This isn’t surprising, especially considering Musk himself often tweets out memes. Lastly, as is unavoidable nowadays, lots of users also brought politics into the conversation.

If the first human tester recovers well and Neuralink does its job, it could signal a completely new age of transhumanism. It would also mean that, as Neuralink and similar technologies improve, many more uses will start opening up. And lastly, this technology has the potential to revolutionize the entertainment industry completely. VR headsets will be looked at as a crude tool from a bygone era if Neuralink becomes what Musk wants it to become.


[ad_2]

Source link

Apple warns of “privacy and security threats” after EU requires it to allow sideloading

0

[ad_1]

Despite several warnings about the risks, Apple will allow European iPhone owners to install apps obtained from outside the official App store (sideloading).

These drastic changes are brought about to comply with the European Union’s (EU) Digital Markets Act (DMA). The Digital Markets Act (DMA) establishes a set of clearly defined objective criteria to identify “gatekeepers”. Gatekeepers are large digital platforms providing so called core platform services, such as for example online search engines, app stores, and messenger services.

The Digital Markets Act aims to regulate the gatekeeper power of the largest digital companies. The EU designated iOS, Safari, and the App Store as “core platform services” under the Digital Markets Act. According to the DMA, Apple as it is now has a monopoly in the App Store, and will no longer be allowed to use that to enforce a monopoly in payments in apps.

For reference, something similar happened when the US accused Microsoft of illegally monopolizing the web browser market for Windows. A few law cases later they reached a settlement in which Microsoft agreed to modify some of its business practices, opening up the opportunity for Windows users to switch to other browsers.

The Apple Newsroom says:

“The changes include more than 600 new APIs, expanded app analytics, functionality for alternative browser engines, and options for processing app payments and distributing iOS apps.”

But Apple also warns very firmly about the consequences.

“The new options for processing payments and downloading apps on iOS open new avenues for malware, fraud and scams, illicit and harmful content, and other privacy and security threats.”

Another big change is that web browsers won’t be forced to use Safari’s WebKit engine, opening the space for Chromium based browsers and a more desktop-alike feel for Firefox.

The fact that Apple only allows other browsers to drop WebKit in Europe means that browser developers are forced to make hard choices. Mozilla spokesperson Damiano DeMonte tells The Verge it’s extremely disappointed with the way things turned out.

“We are still reviewing the technical details but are extremely disappointed with Apple’s proposed plan to restrict the newly-announced BrowserEngineKit to EU-specific apps. The effect of this would be to force an independent browser like Firefox to build and maintain two separate browser implementations — a burden Apple themselves will not have to bear.”

We asked Malwarebytes Director of Core Technology and resident Apple expert Thomas Reed how he felt about the announced changes and the associated risks.

Thomas is waiting for more details as well, but he expects that Apple will use the experience it gathered with macOS by nature of its openness and only open it up only as much as it is forced to, and no more. Thomas expects Apple to impose notarization on iOS apps from outside the App Store, just as they did for macOS.

“If they completely open up iOS to the same degree as macOS, I think there will be some inevitable malware, adware, and PUP issues. The biggest problem with iOS currently is PUPs and scam apps that manage to get past the review process. I think those will also be a problem with apps from outside the App Store, and I think Apple will combat those similarly. Which is to say, far from perfectly.”

Developers can get acquainted with these changes on the Apple Developer Support page and start testing new capabilities in the iOS 17.4 beta. The new capabilities will become available to users in the 27 EU countries around the beginning of March 2024.

Don’t rely on the fact that this will be limited to the EU. Although the most significant app policy changes apply only to EU countries, other shifts concerning cloud gaming and in-app purchases will take effect worldwide.


We don’t just report on iOS security—we provide it

Cybersecurity risks should never spread beyond a headline. Keep threats off your iOS devices by downloading Malwarebytes for iOS today.


[ad_2]

Source link

Chrome for Android readies unified “add to home screen” button

0

[ad_1]

Google Chrome is unifying its options for adding a website to the home screen on your Android device. While the overall experience remains mostly unchanged, you will not encounter two different options on different websites. The company is housing both options under a single button.

Google unifies the “add to home screen” button on Chrome for Android

Google Chrome for Android lets you add website shortcuts to the home screen. Not only the browser’s home page but the home screen of the device. You get an app icon with the website’s logo. Tapping it takes you directly to that website in Chrome. It’s a convenient way to access websites that you visit frequently.

Currently, there are two different options to get these website shortcuts via Chrome for Android. On most sites, the overflow menu (three vertical dots in the top right corner) shows an “Add to Home screen” button. Tapping it lets you customize the name of the app icon before placing it on the home screen of your device.

However, on some websites, you will see an “Install app” button instead of the “Add to Home screen” button. This might be confusing if you just wanted to add a shortcut to the website without installing a separate app unless you are aware that this button serves the same purpose differently.

The “Install app” only appears on websites that have a Progressive Web App (PWA). Tapping it installs the PWA, which feels like a native Android app but is handled by your browser rather than the Google Play Store. Along with a home screen shortcut, PWAs also get an icon on the app drawer with the website’s logo.

Google seemingly knows that only showing users one or the other option could be confusing. It is now testing a unified interface. As spotted by WindowsReport, the latest Canary builds of Chrome for Android have a new flag to enable the “PWA Universal Install” feature.

Once enabled, you will find an expandable “Add to Home screen” button on the overflow menu on all websites in Chrome. Tapping it will let you pick between a home screen shortcut and a PWA, likely depending on availability. This is a welcome change that gives users more flexibility and clears confusion.

Google is still testing this change

As of this writing, the unified “add to home screen” button on Google Chrome for Android is non-functional. The company might still be working on this change while testing the new layout among a small group of users. We will let you know when this update rolls out publicly.

[ad_2]

Source link

X to hire 100 content moderators for new Trust and Safety center

0

[ad_1]

Social media company X, formerly known as Twitter, plans to open a new office dedicated to its center of excellence for Trust and Safety. Located in Austin, Texas, it will be home to a team focused on enforcing the app‘s content and safety rules. The Elon Musk-led firm aims to hire 100 full-time employees for this content moderation job.

X to open a new Trust and Safety center, hire 100 content moderators

Twitter has undergone a lot of changes since Elon Musk took over the company in 2022. Not only did Musk rebrand the social network to X, but also laid off thousands of employees to cut operational costs. He downsized the trust and safety team with plans to rely on automated detection of hateful and abusive content. Musk said machines will be integral to content moderation on the platform.

In a recent blog post, X said it sent its first ever fully-automated report to the National Center for Missing and Exploited Children (NCMEC) in 2023. Overall, the firm sent 850,000 reports to NCMEC last year, over eight times more than it did in 2022. X also suspended 12.4 million accounts for violating our CSE policies in 2023, up from 2.3 million accounts in 2022.

Additionally, it has “reduced the number of successful searches for known Child Sexual Abuse Material (CSAM) patterns by over 99% since December 2022.” Based on these numbers, Musk’s reliance on machines for content moderation, particularly child sexual exploitation (CSE) materials, seems effective. However, it appears X is looking to expand its human team of content moderators too.

The new team will focus on fighting child abuse content

In the same blog post, the company announced its plans to build a Trust and Safety Center of Excellence in Austin, Texas, and hire more in-house agents to stop the spread of CSE materials and other types of harmful content. Joe Benarroch, head of business operations at X, has now shared more details. He didn’t specify when the office will be operational but confirmed that the new team will focus on fighting child abuse content.

“X does not have a line of business focused on children, but it’s important that we make these investments to keep stopping offenders from using our platform for any distribution or engagement with CSE content,” Benarroch said. “The team is currently being built,” he added. The goal is to fill the positions by the end of 2024, though the pace of hiring will depend on finding the right talent.

Interestingly, this announcement comes just a few days before the Senate Judiciary Committee’s hearing on January 31 about online child safety. X CEO Linda Yaccarino will testify before the Committee, along with the CEOs of Meta, Snap, TikTok, Discord, and other companies. X says only 1% of its daily users are aged below 17, with a lower age limit of 13. It doesn’t show targeted ads to its teen users.


[ad_2]

Source link

Simple Yet Vital Tips to Send Documents Securely via Email

0

[ad_1]

In the information age where knowledge equals money, securing business communications, especially through e-mails, is critical and very important. Email is still a fundamental medium for communication in the business world. Regardless, its susceptibility to cybersecurity threats has worked as an impetus behind major risks involved especially when transmitting secure documents.

This article solves the above dilemma by revealing scopes of threats posed to a business through sending materials via unencrypted attachment and recommends secure methods such as Tresorit’s solution on encrypted email that it believes will practically diminish these crimes or rather pointing out in detail dangers associated with using non-secured communication tools, followed by actions required for preventing respectively.

Appreciation of Risks Associated With Unencrypted Email

Email communications that are non-encrypted from one recipient to another can be compared with postcards passed through the mail – they become available for reading by anybody who somehow has access to them. This lack of security can lead to several risks, including:

  • Data Breaches: Cyber criminals can hack unencrypted emails, which results in data breaches that jeopardize confidential business information.
  • Phishing Attacks: They typically carry out phishing attacks when one sends an open email which is not encrypted to disguise as the recipient alternative at a request for information.
  • Legal Repercussions: If we are speaking about some areas of industry, sending liable information through channels which do not guarantee any levels of security can provoke legal issues that might arise from breaking data protection laws such as the General Data Protection Regulation.

Tresorit’s Encrypted Email Solution

In this regard, Tresorit’s encrypted e-mail solution provides a strong way of emailing documents securely due to its un-plain text nature. The use of their platform involves a cypher, which means that nobody but the sender and presumed recipient of this email would be able to perceive its content. Key features include:

  • End-to-End Encryption: It also encrypts data before leaving the device, so it is protected in transit and at rest.
  • Access Control: This increases the levels of security in that senders have control over who can access their email messages and for how long.
  • Easy to Use: It is also easy to use since the service can be incorporated efficiently into most of the email platforms already being used.

Secured Email Communication 5 Best Practices

  • Use Encrypted Email Services: Choose a service such as Tresorit that offers mail encryption capabilities
  • Verify Recipient Identity: Before sending any sensitive information always verify the recipient’s identity.
  • Avoid Public Wi-Fi for Sending Confidential Emails: Public networks are more vulnerable to attacks.
  • Regularly Update Security Software: Do not forget to update your anti-virus and firewall software as well to stay protected from newly arisen threats.
  • Educate Employees: Continual training focusing on the best practices in cyber security can help deal with human error.

Importance of Secure Email in Various Industries

In industries such as health care, finance and law which often exchange sensitive information the use of encrypted mail service proves not only a best practice but also most times mandatory to meet regulatory requirements. Encrypted email services are in keeping with data protection laws and avoid expensive breaches of confidential information.

Conclusion

Email sending itself is easy while ensuring security requires deep consideration, especially in business terms. As cyber threats become more complicated, sending unencrypted emails is no longer an option for modern business.

Therefore, implementing secure approaches such as Tresorit’s encrypted email solution is critical for protecting confidential data and keeping client confidence while abiding by the law. Thanks to its comprehensive solution, you can send documents securely via email.

  1. Secure Email Gateway Vs. Integrated Cloud Email Security
  2. Reverse Email Lookup: A Tool to Strengthen Cybersecurity
  3. Email Hacking Reigns as Top Cybersecurity Threat, Indusface


[ad_2]

Source link

The eSIM Transfer Tool is Expanding to All Android Devices

0

[ad_1]

Until now, physical SIMs have dominated the industry, and using them has only been possible with an allocated slot inside the phone. It adds significant challenges for manufacturers trying to improve smartphone durability. Moreover, transferring Mobile plans from one device to another has been less than ideal. To address these issues, eSIMs are on the rise, being adopted by many flagship devices, and they will only get better with Android’s new built-in eSIM transfer tool.

eSIM transfer tool has started reaching more Android devices

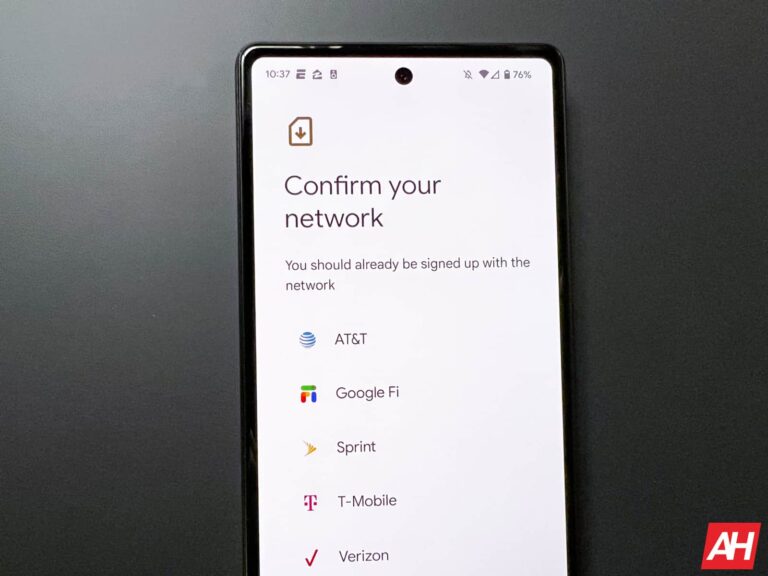
Unlike physical SIMs, eSIMs eliminate the need for removal and can be migrated to other devices without needing the ejector tool/pin. Moving plans with physical SIMs also involves complex processes. With a solution at hand, Google stepped up at last year’s Mobile World Congress, revealing its eSIM transfer tool. Recently, users setting up the Pixel 8 Pro for the first time in the US, discovered this feature within a popup. Until now, the feature’s availability has been exclusive to Pixel 8 Pro and Samsung Galaxy S24 Ultra. But now, it’s transcending to other brands, as one user noticed it on the LG V60 too.

The Google eSIM transfer tool aims to streamline network migration amid devices. While the launch details are scarce, some users are testifying about the feature’s implementation in the Pixel 8 Pro. Live shots from a reliable source prove that the feature is not exclusive to Galaxy devices. While Samsung adopted the feature last year with OneUI 5.1, the eSIM transfer tool is now expanding to devices other than Galaxies.

Migrating from Pixel 8 Pro to Galaxy S24 Ultra, and vice versa

Within the images of Galaxy S24 Ultra’s initial setup, the eSIM transfer tool detected a nearby Pixel 8 Pro. Right away, it prompted the user to scan the QR code and migrate eSIM from the previous device. Tested and confirmed, the tool works bidirectionally, switching the eSIM from newer to older devices. The tool’s interface seems inclusive and operational on phones using Android 14.

The new eSIM transfer tool improves how Android devices handle non-physical SIMs. While the feature is lacking widespread adoption by carriers, it does offer flexibility to users managing Network Plans on more than one device.

Quitely but surely, the new eSIM transfer tool is garnering attention. And it’s likely to become the industry standard for carriers, as more smartphone manufacturers adopt this feature. As Google and Samsung’s collaboration for the tool unfolds, the Galaxy S24 Ultra and Pixel 8 Pro have started offering cross-platform eSIM migration and it will only improve in the future.

[ad_2]

Source link

TikTok wants to compete with YouTube via horizontal videos

0

[ad_1]

It seems like TikTok not only wants to increase the cap for video duration even more, but it also wants creators to post horizontal content. TikTok seemingly wants to compete with YouTube with these horizontal videos.

TikTok seemingly wants creators to upload horizontal videos in order to compete with YouTube

What’s going on here? Well, The Verge shared the information, and even though it still didn’t hear back from TikTok on the matter, things seem rather obvious at this point.

TikTok is well-known for short-form, vertical videos. The company has been constantly increasing the duration cap that people can upload, and that cap will increase even more soon. More on that later on.

The company is incentivizing creators to upload horizontal content

Let’s talk about what’s new here. TikTok seems to be incentivizing creators to start posting horizontal videos that are over a minute long. Creators such as @candicedchap and @kenlyealtumbiz have received such a prompt.

In that prompt, TikTok says that it will “boost” such videos within 72 hours of posting. Creators who are on TikTok for over 3 months are eligible for such a viewership boost. That doesn’t apply to ads or videos from political parties, though, of course.

You could soon be able to upload TikToks that are up to 30 minutes long

Now, let’s get back to the video duration. TikTok expanded the video duration cap to 10 minutes in early 2022, then to 15 minutes a couple of months ago. It is now planning to push that even further by offering users a chance to upload videos that are up to 30 minutes long.

That detail alone pushes the platform into the YouTube territory, kind of. Most videos on YouTube are over 10 minutes long, and many of them are far longer than that. If you add horizontal content to the table too… well, it’s obvious what TikTok is doing here

Things are changing, but the vast majority of people still see TikTok as a short-form video platform only

It’s a bit odd, as TikTok started off as a true short-form video platform. It offered bite-sized videos for quick consumption, and it has been on the path to completely change that for a while now. Truth be said short videos are still the main appeal for many, and they’re still available, but things seem to be changing.

As already mentioned, TikTok has not released an official statement regarding this just yet, so we’ll see what the company has to say.

[ad_2]

Source link

Samsung’s Galaxy A35 & Galaxy A55 inch closer to launch

0

[ad_1]

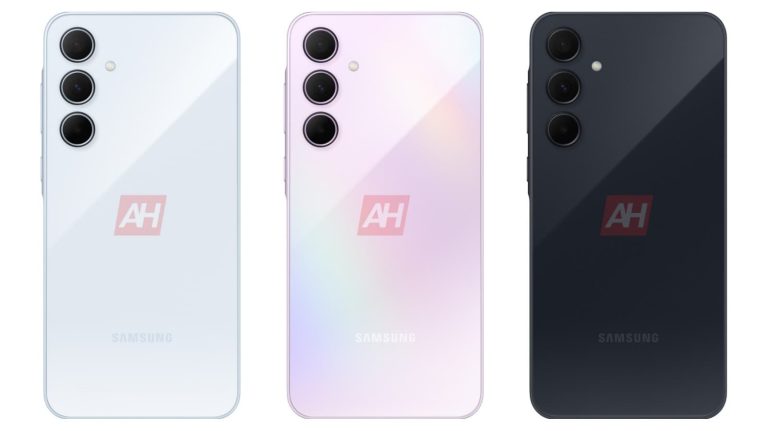
Earlier this month, we exclusively leaked the official renders of the Samsung Galaxy A35 and Galaxy A55. The devices are nearing their market debut. While a launch date is still missing, the upcoming mid-range smartphones have just cleared another hurdle on the way. They have picked up regulatory approval from India’s BIS (Bureau of Indian Standards). The former also received an official support page on the company’s website.

BIS certifies Samsung’s Galaxy A35 and Galaxy A55 ahead of launch

The Galaxy A35 and Galaxy A55 will lead Samsung‘s next generation of A-series smartphones. The latter will top the lineup with premium specs and a strong build, including a metallic frame. Our exclusive leaks have already confirmed the design of both models—like all other recent Samsung phones, these two also look identical. Benchmark listings and regulatory certifications have also revealed bits of information about the devices.

As we wait for an official announcement from the Korean firm, MySmartPrice spotted the duo on the BIS website. As expected, the Indian regulatory body certified the Galaxy A35 with the model number SM-A356E/DS and the Galaxy A55 with SM-A556E/DS. These are global versions of the phones with dual-SIM support. The US versions have the suffix “U” in place of “E” in the model numbers, while the Korean versions have “N”.

The Galaxy A35 has also got an official support page on the Samsung UAE website with the same model number. While none of these listings give us more information, these are an indication of a nearing launch. The FCC recently certified the Galaxy A35 with the model numbers SM-A356U, SM-A356U1, SM-A356V, and SM-A356E. The units with “U1” and “V” suffixes in model numbers are unlocked and Verizon versions of the same phone for the US.

The FCC revealed that the phone will boast 5G cellular connectivity, Bluetooth, NFC, and Wi-Fi 6. It will also support a wide range of navigation systems and feature a microSD card slot. Samsung might offer it in 128GB and 256GB storage variants. We are expecting a 5,000mAh battery with 25W charging, an Exynos 1380 processor with up to 8GB RAM, a 50MP primary rear camera, and Android 14. The Galaxy A55 should get a more powerful processor.

These phones might debut in a few months

Samsung launched the Galaxy A34 and Galaxy A54 in March 2023. The two succeeding models should also arrive around the same time this year. There are rumors about a slight delay, but not much. We could see the Galaxy A35 and Galaxy A55 go official in April if not in March. Over the next couple of months, you can expect tons of new leaks and rumors about the two upcoming Samsung mid-range phones

[ad_2]

Source link