Cybersecurity spend to soar in 2024: How companies can maximize their investment

0
[ad_1]

“Spend smarter, not harder” is the mantra for 2024, as Gartner forecasts a 14.3% jump in global security and risk management spending—an uptick which brings a renewed focus on the need for cost-effective cybersecurity investments.

Inefficient cybersecurity spending, a known problem, becomes even more pressing with increased budgets—especially since inefficient spending often results in buying disparate security tools, which can create more security gaps and increase breach risks.

In a nutshell, with cybersecurity spending on the rise in 2024, businesses must make investments that aren’t just cost-effective, but which actually strengthen defenses too.

Let’s dive into three essential strategies for smart cybersecurity spending in 2024.

Conduct a thorough needs analysis

We’ve all experienced buyer’s remorse at some point, purchasing items that we later realize weren’t necessary. If only we had thoroughly questioned our need for that cool $430 HyperCube beforehand (alright, guilty as charged).

A similar concept applies in the realm of cybersecurity spending. Without carefully analyzing what goods or services they really need, organizations can fall into the trap of “tool sprawl”—the accumulation of too many cybersecurity tools.

The goal should be to tailor cybersecurity investments to actual needs, avoiding the latest, unnecessary technologies. For example, small businesses probably won’t benefit from complex, enterprise-level intrusion detection systems, and large businesses probably don’t need basic, consumer-grade security solutions.

Hastily choosing multiple cybersecurity vendors can also be a recipe for disaster. Juggling multiple vendors often complicates support processes, increases the training burden due to various systems, and challenges seamless tool integration.

Opt for integrated security solutions

To avoid wasteful spending, invest in security platforms which merge several protective measures in one. Not only is this more cost-effective, but it also actually improves your security posture.

Every additional security tool a company buys requires its own set of configurations, updates, and management protocols, ultimately translating to longer response times, inefficient workflows, and an inability to have a unified view of the threat landscape.

Opting for integrated security solutions like the popular ThreatDown Bundles can be a game-changer in terms of a targeted, lean approach to cybersecurity spending. By consolidating multiple security functions into a single platform, these integrations reduce overhead costs related to hardware, maintenance, and administration.

Emphasize added value

Imagine you’re hungry, and you can grab a basic $2 burger. That’s good, but for $5, you can upgrade to a complete meal—burger, fries, drink, maybe even a vintage Furby. That’s value-added fine dining right there—more bang for your buck.

Emphasizing added value in cybersecurity is a lot like upgrading from a basic burger to a complete meal—you get more features that go beyond the foundational security measures (and best of all, without any trans fats).

For example, consider solutions featuring complimentary Vulnerability Assessment (VA) and Application Block (AB). Amid rising cybersecurity costs, VA uncovers application vulnerabilities at no extra expense, while AB actively keeps your defenses strong by preventing unwanted applications from launching, adding substantial value without breaking the bank.

Managing cybersecurity expenses in 2024

As we venture into 2024, organizations can more efficiently spend cybersecurity budgets through meticulous needs assessments, integrated solutions, and a focus on added value.

For organizations seeking to put these strategies into action, ThreatDown Bundles offer a practical solution.

ThreatDown bundles are like the Swiss Army knives of cybersecurity, consolidating essential security technologies, including Endpoint Detection and Response and Managed Detection and Response, into one unified platform. Each bundle comes with free threat prevention capabilities, Vulnerability Assessment and Application Block—to further reduce your threat surface at no additional cost.

Want to learn more?


[ad_2]
Source link
Using Instagram and Snapchat on the Galaxy S24 will be next-level

0
[ad_1]

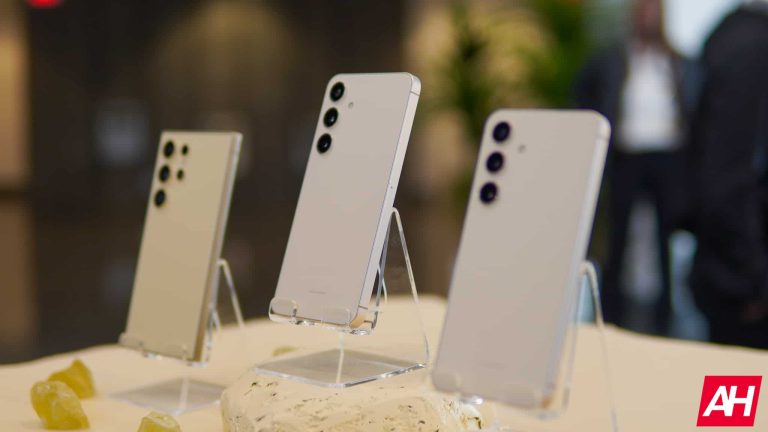
The photos you take using social media apps have never really stacked up to what you can take with your native camera app. This is because social media apps don’t typically have access to all of your camera sensors and features. Well, thanks to a new partnership, using Instagram and Snapchat on the Galaxy S24 is going to be pretty next-level.

In case you didn’t know, Samsung just announced the new Galaxy S24 phones, and they come with some nice AI features. Here’s a rundown of all the AI features the company announced for this phone. If you’re curious about these phones, check out our Galaxy S24/S24+ preview and our Galaxy S24 Ultra preview.

Sick of reading about them and ready to get your hands on one? Check out the links below. If you use one of these links, then you’ll get $50 off of your order.

Pre-order the Galaxy S24 Ultra

Pre-order the Galaxy S24/S24+

Using Instagram and Snapchat on the Galaxy S24 will be amazing

Instagram and Snapchat are known for their amazing social media experiences, not for their photo quality. No matter how great your phone’s camera is, you’re still limited by the software and image processing of these apps. The quality is good enough to get the job done, but you won’t be impressing anyone with the quality.

However, Samsung partnered with Instagram and Snap so that these apps can use more of the S24’s camera features. These apps will have access to the Nightography mode. This will allow them to take much better photos in low-light environments. So, “graming” your food in a dimly lit bar won’t be an issue.

Next up, all of your photos will look much better and well-balanced with access to Super HDR mode. This will make all of your posts look much higher quality. Lastly, these apps will gain access to video stabilization. So, no more shaky videos on your video feed. If you want this feature to work, you’ll need to enable video stabilization in the native camera app.

Aside from the camera features, you’ll be able to create Instagram Stories directly from motion photos. This shows that Samsung is looking to tightly integrate the Galaxy S24 phones with the social media experience.


[ad_2]
Source link

Anonymous Sudan’s DDoS Attacks Disrupt Network at Israeli BAZAN Group

0
[ad_1]

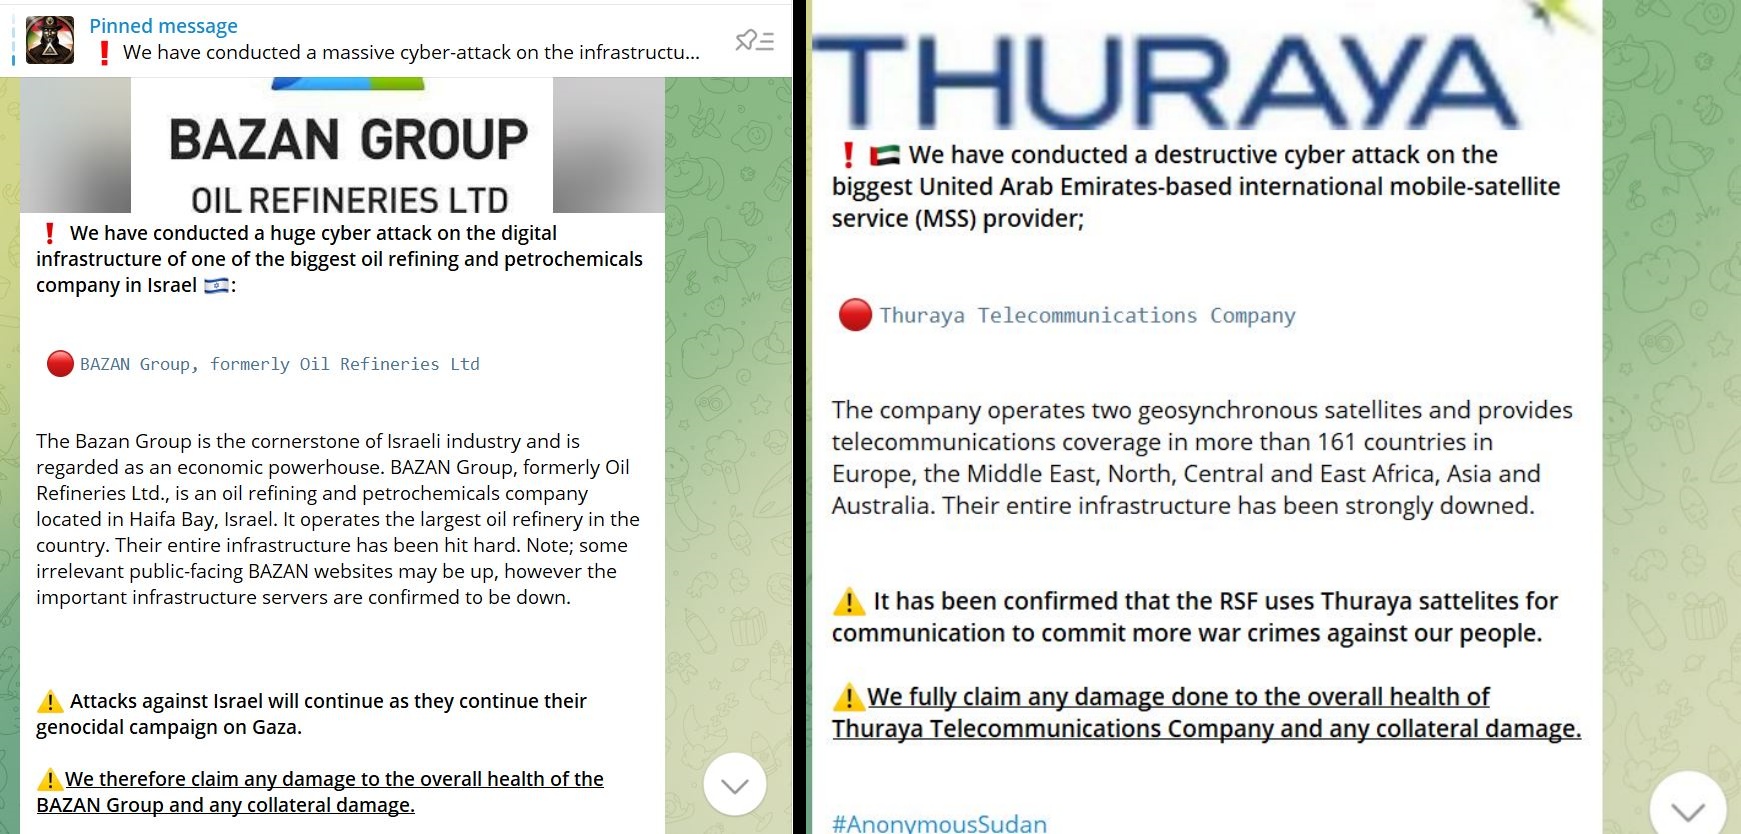
Anonymous Sudan has also claimed responsibility for DDoS attacks on Thuraya Mobile Satellite Communications Company, an international mobile-satellite service (MSS) provider based in Dubai, United Arab Emirates (UAE).

Anonymous Sudan, the pro-Palestinian hacktivist group, has taken credit for a series of Distributed Denial of Service Attacks (DDoS attacks) on BAZAN Group, Israel’s top oil refinery operator. This recent claim closely follows their announcement of targeting the London Internet Exchange (LINX) in protest against the Yemen strikes.

On Wednesday evening, January 17, the DDoS attacks began with notable intensity, causing extensive disruptions in the network of BAZAN Group’s critical infrastructure. The scale of the impact was confirmed by NetBlocks, a global internet monitoring platform specializing in tracking outages, disruptions, and censorship events worldwide.

On Wednesday, NetBlocks officially reported a significant network disruption affecting Bazan Group through its official X account on Twitter. Simultaneously, Anonymous Sudan took to its Telegram channel to announce and claim responsibility for the orchestrated attack.

“We have conducted a huge cyber attack on the digital infrastructure of one of the biggest oil refining and petrochemicals companies in Israel,” the group said. The statement was followed by additional details of what was hit and what remained untouched.

“Their entire infrastructure has been hit hard. Note; some irrelevant public-facing BAZAN websites may be up; however, the important infrastructure servers are confirmed to be down,” the group claimed.

The hacktivist group stated that the motive behind targeting the BAZAN Group was in direct response to Israeli aggression against Palestinians. The group mentioned that the DDoS attacks were a form of protest, stating that “Attacks against Israel will continue as they continue their genocidal campaign on Gaza.” The group claimed responsibility for any damage to the overall health of BAZAN Group and any collateral damage resulting from the DDoS attacks.

This incident is not the first time Bazan Group has faced DDoS attacks. In July 2023, another pro-Palestinian group named Cyber Avengers claimed responsibility for an attack on the company. Consequently, the group’s websites were taken offline and restricted to users outside Israel.

It is worth noting that on January 16, 2023, Anonymous Sudan also claimed responsibility for targeting Thuraya Mobile Satellite Communications Company, an international mobile-satellite service (MSS) provider based in Dubai, United Arab Emirates (UAE).

Anonymous Sudan revealed that their targeting of Thuraya was motivated by the belief that the company’s satellites are utilized by the Rapid Support Forces (RSF) for communication. Notably, RSF is a paramilitary force formerly operated by the Government of Sudan, accused by the hacktivists of committing war crimes against the Sudanese people.

Anonymous Sudan Hits Israeli Oil Refinery Giant BAZAN Hit with Crippling DDoS Attacks
Anonymous Sudan on Telegram

The recent series of DDoS attacks orchestrated by hacktivist groups such as Anonymous Sudan against prominent entities like BAZAN Group and Thuraya Mobile Satellite Communications Company highlight the growing cybersecurity threats targeting critical infrastructure.

Beyond the immediate disruption caused to the targeted organizations, these incidents expose the vulnerable state of IoT devices. DDoS attacks not only compromise the functionality of essential services but also serve as potent tools for expressing political or ideological grievances.

The danger lies not just in the immediate impact on the targeted entities but in the potential ripple effects, affecting users, businesses, and, in the case of BAZAN Group, the broader energy sector.

As cybersecurity threats evolve in sophistication and scale, the need for strong security measures becomes increasingly crucial to safeguard against potential economic, social, and geopolitical consequences arising from such malicious activities.

  1. Hamas hacked smartphones of over 100 IDF soldiers
  2. 10 Top DDoS Attack Protection and Mitigation Companies
  3. Hacktivists Trageting Critical ICS Infrastructure in Israel and Palestine
  4. Hamas hacked of IDF soldiers’ phones using seductive female images
  5. Protestware Uses npm Packages to Call for Peace in Gaza and Ukraine
  6. Crypto Scammers Exploit Gaza Crisis, Deceiving Users in Donation Scam

[ad_2]
Source link

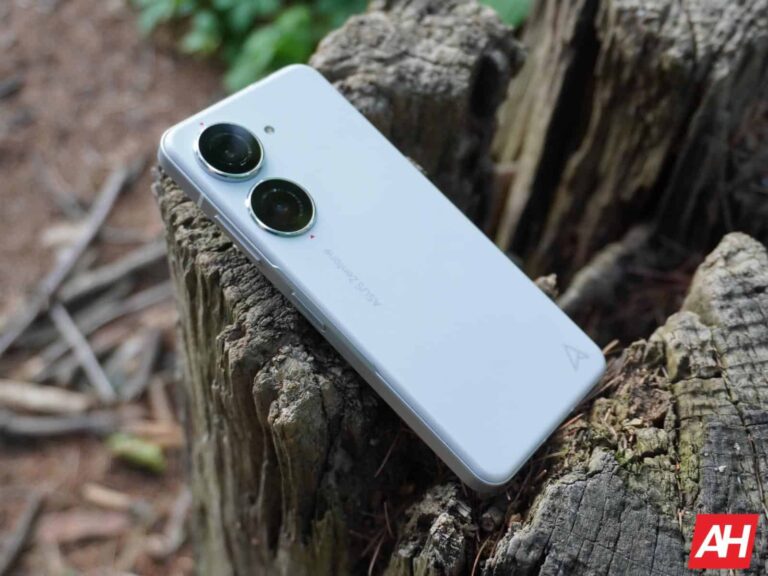
ASUS ZenFone 11 Ultra could launch sooner than expected

0
[ad_1]

The ASUS ZenFone 11 Ultra moniker has been confirmed last month. The phone appeared over at Bluetooth SIG, with that name. Well, it seems like the ASUS ZenFone 11 Ultra could launch sooner than expected, as it just crossed yet another certification hurdle.

The ASUS ZenFone 11 Ultra could launch sooner than we thought

The phone paid a visit to Indonesia’s SDPPI authority. It appeared with the model number ASUS_AI2401_H. It was once again mentioned by name, which is the second confirmation of that particular moniker.

ASUS ZenFone 11 Ultra certification 11

We don’t know much about this device at this point. We do know it will offer Bluetooth 5.4, as that was mentioned by Bluetooth SIG. Other than that, everything is based on rumors thus far.

Some rumors are suggesting this could be the same device as the ASUS ROG Phone 8 or 8 Pro. Perhaps with some tweaks. Others are saying it’s a proper new phone with a larger display.

As a reminder, the ASUS ZenFone 10 is the only flagship smartphone that ASUS launched in 2023. That device has a rather compact display at 5.9 inches. It’s the same display size the ASUS ZenFone 9 offered a year earlier.

This phone will have a large display and a flagship-grade SoC

Is ASUS getting ready to announce a new flagship smartphone with a larger display? Well, it seems like it. The thing is, the ASUS ZenFone 10 arrived back in June last year. That means we’re about 5 months away from the time ASUS is expected to announce its next-gen devices.

Considering how many certifications the ASUS ZenFone 11 Ultra popped up on thus far, its launch could arrive sooner. It remains to be seen if it will launch alongside the ASUS ZenFone 11, or will this be a completely separate launch. More information will hopefully arrive soon. We do expect it to have a considerably larger display than the ZenFone 10, and possibly include the Snapdragon 8 Gen 3 SoC.


[ad_2]
Source link

Samsung reveals Exynos 2400 specs: deca-core CPU, 3.2GHz speed

0
[ad_1]

For better or worse, Samsung is back using Exynos chips in its flagship phones. The newly launched Galaxy S24 and Galaxy S24+ ship with the Exynos 2400 in most markets, including Europe (Snapdragon 8 Gen 3 in the US and Canada). The company has now shared detailed specs of the new Exynos processor.

Samsung finally shares detailed Exynos 2400 specs

Samsung announced the Exynos 2400 during its System LSI Tech Day event in the first week of October last year. However, it didn’t reveal full specs. The company said the new chip brings a massive 14.7x boost in AI performance over the previous-gen solution (Exynos 2200), while the CPU and GPU performance have been improved too. We finally have the official numbers.

The Exynos 2400 features a deca-core CPU (ten CPU cores) featuring one Cortex-X4 prime core clocked at 3.2GHz. There are five Cortex-A720 mid-cores in the chip, split into a group of two and three with a clock speed of 2.9GHz and 2.6GHz, respectively. The four Cortex-A520 efficiency cores operate at a maximum frequency of 2GHz. Overall, it brings a 1.7x boost in CPU performance.

The Xclipse 940 custom GPU, based on AMD’s RDNA 3 architecture, also brings improvements to ray tracing, rendering, and reflections while gaming, making for a more immersive and enjoyable experience. The Exynos 2400 is also the first Exynos processor to use a Fan-out Wafer Level Package (FOWLP). It helps boost thermal management,  so you can game longer worry-free.

Samsung Exynos 2400 2

Fabricated on Samsung’s third-gen 4nm LPP+ low-power process node, the chip is more power efficient than its predecessors. Coming to the AI engine, the Exynos 2400 has a new 17K MAC (2-GNPU + 2-SNPU) Neural Processing Unit (NPU). It supports LPDDR5X RAM and UFS 4.0 storage. The chip can handle 4K displays at 120Hz and QHD+ displays at 144Hz.

The Exynos 2400 supports up to 320MP cameras with 8K video decoding at 60fps with 10-bit HEVC. The integrated 5G modem can deliver downlink speeds of up to 9.64Gbps and uplink speeds of 2.55Gbps over sub-6GHz 5G networks. The theoretical peak speeds on mmWave 5G are 12.1Gbps (downlink) and 3.67Gbps (uplink). The new Samsung processor boasts GPS, GLONASS, BeiDou, and Galileo navigation systems.

The Exynos 2400 has to set a lot of things right

Samsung’s Exynos chips don’t have the best reputation in the smartphone industry. Competing Qualcomm solutions have consistently outperformed them. The Korean firm skipped Exynos 2300 and went back to the drawing board to improve things. It has now come up with the Exynos 2400 to compete against Qualcomm’s Snapdragon 8 Gen 3. It remains to be seen whether the new Exynos gives a tough fight to its competitor. The Galaxy S24 Ultra ships with the Snapdragon chip globally.


[ad_2]
Source link

Samsung hypes up Galaxy S24 with new promotional videos

0
[ad_1]

Samsung has published a series of promotional videos for its newly launched Galaxy S24 series on YouTube. The videos take us through Galaxy AI and other features introduced with the new flagships. The company is currently taking pre-orders for the devices, with general sales beginning at the end of this month.

Samsung releases new promotional videos for the Galaxy S24 series

Galaxy AI is a comprehensive suite of on-device and cloud-based AI features on the Galaxy S24, Galaxy S24+, and Galaxy S24 Ultra. It is the biggest selling point of the phones. The company spent much time explaining the new features at the launch event yesterday. It has now followed up with step-by-step guides for two of them.

Firstly, Samsung takes us through Live Translate, a groundbreaking feature that removes language barriers and fosters communication. If you are on a phone call with someone who doesn’t speak a common language, you can use this tool to translate the call in real-time. Whatever the person says will be translated into your language. The device will also translate your response to the language the person speaks.

The whole system is built right into the stock calling app on the Galaxy S24 phones. You don’t need a separate app to use this two-way live call translation tool. To enable it, open the Phone app, tap on the three vertical dots in the top right corner, select Settings, click on Live Translate, and turn the toggle on. You can then configure the language settings and voice. The video below gives you a demo of the tool.

Circle to search is another major AI feature introduced with the Galaxy S24 series. As you might have guessed, it allows you to search for anything on the screen by drawing a circle around it. You can also scribble or drag over the object or text to select it. The device will then quickly run a Google search for whatever is displayed on the selected portion of the screen. Here’s how it works.

AI also helps improve low-light camera zoom performance

Samsung is leveraging the built-in AI capabilities of the Galaxy S24 series to improve the camera zoom performance in low-light conditions. In a short video, the company shows how you can get clear and sharp images of anything from far away even when there isn’t adequate light. And if the scene has unwanted disturbances, you can quickly erase those and fill in details with the help of AI. How cool is that?

These are just a few of the new AI features Samsung unveiled yesterday. There are AI tools for generative photo editing, note formatting, and summarizing, live translating text messages, and many more. You can expect Samsung to release more promotional videos highlighting these Galaxy S24 features in the coming days. The devices are currently available for pre-order in most countries worldwide.


[ad_2]
Source link

OpenAI signed a contract with the US Department of Defense (but don’t worry)

0
[ad_1]

Generative AI is still relatively new compared to much of the tech running our world. So, its potential wide-reaching effects are still an enigma. This is why we don’t want it around any major governmental bodies… Anyway, OpenAI just signed a contract with a major governmental body. According to sources, OpenAI signed a contract with the US Department of Defense (DOD).

The OpenAI DOD contract isn’t as scary as it sounds

However, you can stop looking up “How to build a nuclear bunker” on Google. The government isn’t putting ChatGPT in charge of the nation’s military or any big missiles. It’s going to be used for cybersecurity reasons. We don’t know what software the DOD is going to be using, exactly. We’re not sure if it’s going to be using GPT-4 or if OpenAI is going to develop a specialized model for these uses.

In any case, the contract is to help boost the country’s cybersecurity. OpenAI will lend its software to help develop open-source cybersecurity tools. So, no missiles, fortunately. Also, this technology is going to be used to participate in the DARPA AI Cyber Challenge. This is an ongoing competition for computer scientists, AI researchers, developers, ETC. to help develop powerful cybersecurity tools and patch critical vulnerabilities. With OpenAI’s powerful AI tools, we’re sure that it’s going to be a formidable contender.

Should you be worried?

Well, we’re still at the very beginning of AI’s involvement in government affairs, so this remains to be seen. The government is only using these tools to help develop cybersecurity tools, so it won’t be in charge of anything. All of the major decisions will be made by human beings.

However, the issue is that AI technology isn’t 100% reliable just yet. There’s still the chance of AI hallucinations. As much as companies try to reduce this phenomenon, it still happens. That’s not as bad if it hallucinates while generating a recipe or a book report, but it’s terrible if the nation’s cybersecurity is at stake. This is something that we’ll have to wait to see.


[ad_2]
Source link

Multichain Inferno Drainer Abuse Web3 Protocols

0
[ad_1]

A cryptocurrency-related phishing scam that uses malware called a drainer is one of the most widely used tactics these days. From November 2022 to November 2023, ‘Inferno Drainer’, a well-known multichain cryptocurrency drainer, was operational under the scam-as-a-service paradigm.

On sophisticated phishing websites, victims were deceived into linking their cryptocurrency wallets to the attackers’ infrastructure.

Group-IB found that at least 100 distinct cryptocurrency brands were impersonated on more than 16,000 distinct domains connected to Inferno Drainer’s phishing activities.

Document
Free Webinar

Compounding the problem are zero-day vulnerabilities like the MOVEit SQLi, Zimbra XSS, and 300+ such vulnerabilities that get discovered each month. Delays in fixing these vulnerabilities lead to compliance issues, these delay can be minimized with a unique feature on AppTrana that helps you to get “Zero vulnerability report” within 72 hours.

Malicious scripts observed in Inferno Drainer impersonated well-known Web3 protocols to link cryptocurrency wallets and obtain permission from the user to approve a transaction.

The hackers used prominent Web3 protocols, including Coinbase, WalletConnect, and Seaport, as a way to launch fraudulent transactions.

According to its website, Seaport is a Web3 marketplace protocol developed by OpenSea for effective and secure NFT trading.

Coinbase and WalletConnect are protocols that enable self-custody cryptocurrency wallets to connect with Web3 decentralized apps (DApp).

A user must manually approve transaction requests in their wallet after approving a DApp’s connection request (via WalletConnect).

“Once the connection with the wallet is secured, Inferno Drainer spoofed these protocols under the guise of various DApps to initialize malicious transactions,” reads the report.

To win a prize or other money reward, users are asked to link their accounts and authorize a transaction, but by doing so, they expose themselves to getting fraudulent transaction requests from the operators of the drainer.

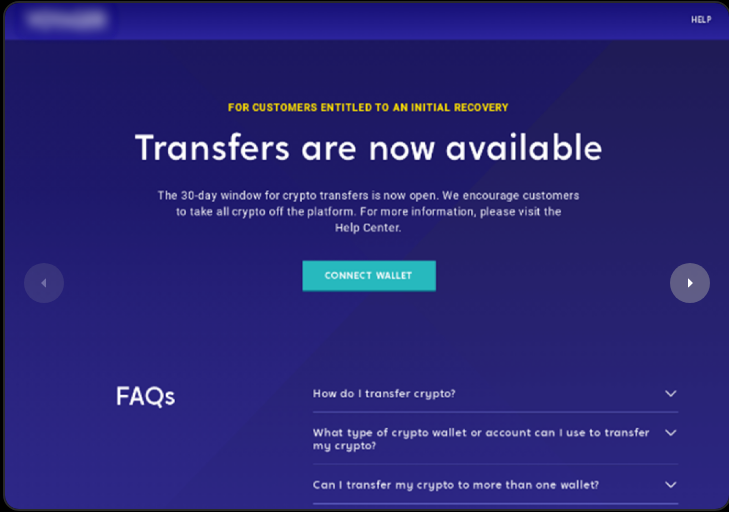
Phishing page that contained Inferno Drainer offering users to claim recovery funds

The malware was uploaded to websites posing as official cryptocurrency token projects and propagated over Discord and X (previously Twitter).

Techniques on Phishing Websites to Deceive Victims

  • Claims of airdropping free tokens.
  • Motivating the possible victim to mint NFTs and take advantage of the benefits.
  • Get compensated for any problems or disruptions the business experienced, e.g., if a company was hacked.
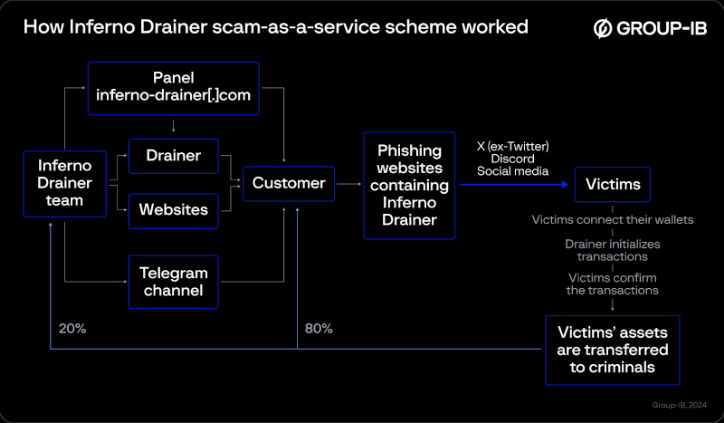
Overview of Inferno Drainer’s workflow

Amount of phishing websites in the crypto world is countless

Although the developer has now closed down Inferno Drainer, its popularity over the last 12 months has created many opportunities for criminals to accumulate wealth.

Its clients are still using it, and there’s no indication that their desire to steal NFTs and tokens has diminished.

When connecting your wallets, use caution and avoid pursuing free tokens and NFT giveaways known as airdrops.

The only way to stop similar attacks in the future is to conduct thorough investigations and bring offenders accountable. Victims must report their attacks to the appropriate law enforcement authorities.

Try Kelltron’s cost-effective penetration testing services to evaluate digital systems security. Free demo available.


[ad_2]
Source link

A true tale of virtual kidnapping: Lock and Code S05E02

0
[ad_1]

This week on the Lock and Code podcast…

On Thursday, December 28, at 8:30 pm in the Utah town of Riverdale, the city police began investigating what they believed was a kidnapping.

17-year-old foreign exchange student Kai Zhuang was missing, and according to Riverdale Police Chief Casey Warren, Zhuang was believed to be “forcefully taken” from his home, and “being held against his will.”

The evidence leaned in police’s favor. That night, Zhuang’s parents in China reportedly received a photo of Zhuang in distress. They’d also received a ransom demand.

But as police in Riverdale and across the state of Utah would soon learn, the alleged kidnapping had a few wrinkles.

For starters, there was no sign that Zhuang had been forcefully removed from his home in Riverdale, where he’d been living with his host family. In fact, Zhuang’s disappearance was so quiet that his host family was entirely unaware that he’d been missing until police came and questioned them. Additionally, investigators learned that Zhuang had experienced a recent run-in with police officers nearly 75 miles away in the city of Provo. Just eight days before his disappearance in Riverdale, Zhuang caught the attention of Provo residents because of what they deemed strange behavior for a teenager: Buying camping gear in the middle of a freezing winter season. Police officers who intervened at the residents’ requests asked Zhuang if he was okay, he assured them he was, and a ride was arranged for the teenager back home.

But what Zhuang didn’t tell Provo police at the time was that, already, he was being targeted in an extortion scam. But when Zhuang started to push back against his scammers, it was his parents who became the next target.

Zhuang—and his family—had become victims of what is known as “virtual kidnapping.”

For years, virtual kidnapping scams happened most frequently in Mexico and the Southwestern United States, in cities like Los Angeles and Houston. But in 2015, the scams began reaching farther into the US.

The scams themselves are simple yet cruel attempts at extortion. Virtual kidnappers will call phone numbers belonging to affluent neighborhoods in the US and make bogus threats about a holding a family member hostage.

As explained by the FBI in 2017, virtual kidnappers do not often know the person they are calling, their name, their occupation, or even the name of the family member they have pretended to abduct:

“When an unsuspecting person answered the phone, they would hear a female screaming, ‘Help me!’ The screamer’s voice was likely a recording. Instinctively, the victim might blurt out his or her child’s name: ‘Mary, are you okay?’ And then a man’s voice would say something like, ‘We have Mary. She’s in a truck. We are holding her hostage. You need to pay a ransom and you need to do it now or we are going to cut off her fingers.’”

Today, on the Lock and Code podcast with host David Ruiz, we are presenting a short, true story from December about virtual kidnapping. Today’s episode cites reporting and public statements from the Associated Press, the FBI, ABC4.com, Fox 6 Milwaukee, and the Riverdale Police Department.

Tune in today to listen to the full story.

Show notes and credits:

Intro Music: “Spellbound” by Kevin MacLeod (incompetech.com)
Licensed under Creative Commons: By Attribution 4.0 License
http://creativecommons.org/licenses/by/4.0/
Outro Music: “Good God” by Wowa (unminus.com)


We don’t just report on threats—we remove them

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.


[ad_2]
Source link

Google users in EU will soon have more control over their privacy

0
[ad_1]

Google users in the European Union will soon be able to choose how much data they share between Google services. The search engine giant is testing changes to some of its services to comply with new tech rules in the EU. As part of the European Union’s new Digital Markets Act, Google will be making changes to its core services from March. This will allow Google users in the EU to choose to keep certain Google services interlinked.

Google Search, Chrome, Maps, and more services are changing under the new DMA rules

As part of the new Digital Markets Act rules, most of the Google services are changing in the European Union.These include Google Search, YouTube, Chrome, Maps, Google Play, Ad services, and Google Shopping. Soon, the search titan will start showing an additional consent banner in its core services. It will ask the users whether some services can continue to share data.

Google Services

The users will have a choice to keep all or none of the aforementioned services linked. Furthermore, they will be able to choose some of the individual Google services to keep linked.

The new changes will provide Google users more control over their privacy online

In a blog post, Google has mentioned that depending on what a user decides, some of its products will work differently. If services aren’t linked, features of some services will be limited or not available at all. For example, when Search, YouTube, and Chrome are not linked, the users will not get recommendations in Search.

The Discover as well as “What to watch” feeds will be less personalized. If the Search and Maps services are not linked, then the Reservations made on Search will not show up in Google Maps. Aspects or functionality of none of the interlinked services will be affected in any way.

Essentially, the new changes will provide Google users more control over their privacy online. The users will be able to exactly decide the amount of data they want to share with Google. These changes will take effect on March 6, 2024.


[ad_2]
Source link