HONOR Magic6 announced with Snapdragon 8 Gen 3 & Android 14

0
[ad_1]

The HONOR Magic6 arrived alongside its ‘Pro’ sibling today. The two phones are quite similar in terms of the design, but rather different when specs are concerned. They launched in China, while the global launch is expected later on. More on that later. That being said, let’s focus on the design of the Magic6 first, shall we?

The HONOR Magic6 is very similar to its sibling, but there are differences

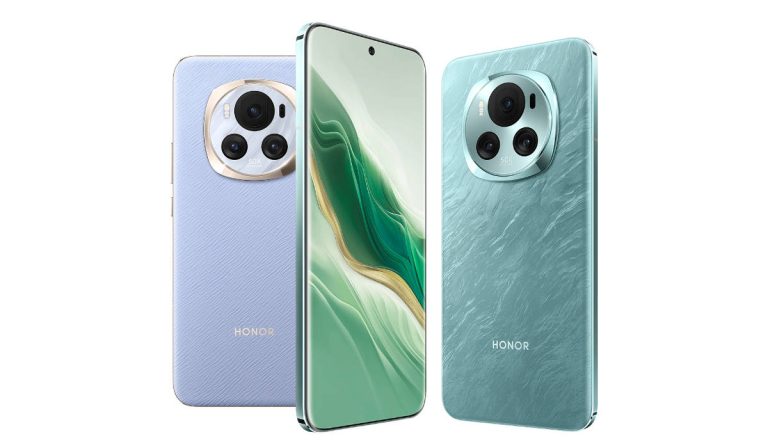
The HONOR Magic6 is made out of metal and glass just like its sibling. It has a similar-looking camera island on the back, which is easy to differentiate from other phones. The thing is, the HONOR Magic 6’s camera island is a bit smaller than the Magic6 Pro’s.

This handset has a curved display on the front, with minimal bezels. It also has a hole punch which is centered at the top of the display. In that sense, it’s a bit sleeker-looking than the ‘Pro’ model, but it loses the 3D facial scanning functionality.

There is a 6.78-inch display included on the phone. This panel is curved and has a resolution of 2800 x 1264 pixels. It’s an LTPO AMOLED display, and its refresh rate can go from 1 to 120Hz. A 4,320Hz PWM dimming is included here too, to protect your eyes.

The Snapdragon 8 Gen 3 fuels this phone, while fast wired & wireless charging is also included

The Snapdragon 8 Gen 3 SoC fuels the phone, the same chip as on the HONOR Magic6 Pro. Both 12GB and 16GB RAM variants of the phone are available. The 12GB RAM model comes with 256GB of storage, while the 16GB RAM variant is available in both 256GB and 512GB storage flavors.


HONOR included a 5,450mAh battery inside of this phone. The device supports 66W wired charging and 50W wireless charging. A charger is included inside the retail packaging, by the way.

A 50-megapixel main camera (f/1.9 aperture, OIS) is backed by a 50-megapixel ultrawide camera (f/2.0 aperture). The third camera on the back is a 32-megapixel telephoto unit (f/2.4 aperture, OIS, 50x digital zoom). On the front, you’ll find a 50-megapixel wide-angle camera (f/2.0 aperture).

Android 14 comes pre-installed on the phone with HONOR’s brand new MagicOS version

Android 14 comes pre-installed on the device, along with HONOR’s MagicOS 8.0. Two SIM card slots are included, and the phone does support facial scanning, but only via the front-facing camera. A fingerprint scanner sits under the display. 5G is also supported, as is Bluetooth 5.3.

This handset launched in China, but it’s almost certainly coming to global markets. It could launch globally next month, during the MWC 2024. That hasn’t been confirmed yet, though, so take it with a grain of salt.

The HONOR Magic6 comes in Black, Glacier White, Lake Blue, Cloud Purple, and Epi Green colors. Its pricing starts at CNY4,399 ($619) in China.


[ad_2]
Source link
Hackers Actively Exploited Ivanti 0-Day to Execute Arbitrary Commands

0
[ad_1]

Invati Connect Secure (ICS) and Ivanti Policy Secure Gateways have been discovered with two new vulnerabilities associated with authentication bypass and command injection.

The CVEs for these vulnerabilities have been assigned as CVE-2023-46805 and CVE-2024-21887. The severity of these vulnerabilities has been given as 8.2 (High) and 9.1 (Critical), respectively.

However, Ivanti has released a security advisory to address these vulnerabilities along with the patched version of the products.

It was also mentioned that Ivanti neurons for ZTA gateways cannot be exploited in production. UTA0178 actively exploited these vulnerabilities.

Exploitation in the Wild

According to the reports shared with Cyber Security News, a threat actor actively exploited these two vulnerabilities to steal configuration data, download remote files, and create a reverse tunnel from the ICS VPN appliance.

Moreover, the threat actor made several changes to the system to evade the ICS integrity checker tool. 

In addition, the threat actor backdoored a legitimate CGI file on the ICS VPN appliance to enable command execution over the compromised system.

The attacker also modified the Web SSL VPN JavaScript file to keylog and extract users’ login credentials.

Document
Free Webinar

Compounding the problem are zero-day vulnerabilities like the MOVEit SQLi, Zimbra XSS, and 300+ such vulnerabilities that get discovered each month. Delays in fixing these vulnerabilities lead to compliance issues, these delay can be minimized with a unique feature on AppTrana that helps you to get “Zero vulnerability report” within 72 hours.

Courses of the Incident

A curl command was for outbound connections to an IP Geolocation service through ip-api[.]com to Cloudflare’s 1.1.1.1 IP address. Additionally, reverse SOCKS proxy and SSH connections were established and downloaded from compromised Cyberoam appliances. 

Lateral movements were also noticed through compromised credentials to connect to internal systems through RDP, SMB, and SSH. Furthermore, there was also the transfer of multiple webshell variants, termed as “GLASSTOKEN”, to Internet-accessible web servers and systems that were only internally accessible.

The attacker created and executed several files from the system’s /tmp/ directory, which were no longer on disk at the time of analysis. A list of the following paths was excluded on the list of Integrity Checker Tool,

  • /tmp/rev
  • /tmp/s.py
  • /tmp/s.jar
  • /tmp/b
  • /tmp/kill

During the course of the incident, Volexity distributed a few malicious files and tools, the most of which comprised of webshells, proxy utilities, and file alterations that allowed credential harvesting. This was despite the fact that Volexity observed the attacker practically living off the land for the most part.

  • In numerous instances, the attacker used compromising credentials to enter onto workstations and servers and dump LSASS process memory to disk via Task Manager.
  • The attacker extracted further credentials offline by exfiltrating this output.
  • The attacker accessed a system with Virtual Hard Disk backups, including a domain controller backup. After mounting this virtual hard disk, they extracted the Active Directory database ntds.dit file and compressed it using 7-Zip.
  • The attacker found a running Veeam backup software instance and used a GitHub script to steal passwords.
  • As said, the attacker updated JavaScript on the ICS VPN Appliance’s Web SSL VPN login page to steal credentials.

A complete report about this incident has been published, providing detailed information about the threat actor’s activities, webshell information, and others.

ValueEntity_typeDescription
206.189.208.156ipaddressDigitalOcean IP address tied to UTA0178
gpoaccess[.]comhostnameSuspected UTA0178 domain discovered via domain registration patterns
webb-institute[.]comhostnameSuspected UTA0178 domain discovered via domain registration patterns
symantke[.]comhostnameUTA0178 domain used to collect credentials from compromised devices
75.145.243.85ipaddressUTA0178 IP address observed interacting with compromised device
47.207.9.89ipaddressUTA0178 IP address observed interacting with compromised device tied to Cyberoam proxy network
98.160.48.170ipaddressUTA0178 IP address observed interacting with compromised device tied to Cyberoam proxy network
173.220.106.166ipaddressUTA0178 IP address observed interacting with compromised device tied to Cyberoam proxy network
73.128.178.221ipaddressUTA0178 IP address observed interacting with compromised device tied to Cyberoam proxy network
50.243.177.161ipaddressUTA0178 IP address observed interacting with compromised device tied to Cyberoam proxy network
50.213.208.89ipaddressUTA0178 IP address observed interacting with compromised device tied to Cyberoam proxy network
64.24.179.210ipaddressUTA0178 IP address observed interacting with compromised device tied to Cyberoam proxy network
75.145.224.109ipaddressUTA0178 IP address observed interacting with compromised device tied to Cyberoam proxy network
50.215.39.49ipaddressUTA0178 IP address observed interacting with compromised device tied to Cyberoam proxy network
71.127.149.194ipaddressUTA0178 IP address observed interacting with compromised device tied to Cyberoam proxy network
173.53.43.7ipaddressUTA0178 IP address observed interacting with compromised device tied to Cyberoam proxy network

Looking for cost-effective penetration testing services? Try Kelltron’s to assess and evaluate the security posture of digital systems – Free Demo


[ad_2]
Source link

YouTube may have removed the iMessage mini-app for iOS devices

0
[ad_1]

It appears that YouTube might have removed the iMessage mini-app that allows iPhone and iPad users to send videos directly from chat without having to leave the Messages app.

The latest YouTube app update released earlier this week mentions changes like improved performance and bug fixes, but it may have also removed the iMessage mini-app.

The folks at 9to5mac confirm that the iMessage mini-app for iPhone and iPad is no longer available after the latest YouTube update, but at this time it’s impossible to tell whether or not this is something temporary.

It’s been nearly seven years since the iMessage mini-app has been added to YouTube. Unfortunately, it never became popular among iOS users, even though the app allowed them not just to send YouTube videos directly from the chat without leaving the Message app, but they could also watch videos using the native YouTube app.

Let us know in the comments if the feature disappears for you after updating the YouTube app to version 19.01.1. Although it might be hard to guess YouTube’s plans about the iMessage mini-app without an official statement.


[ad_2]
Source link

AgentTesla Malware Attack Windows Machine Steal Sensitive Data

0
[ad_1]

AgentTesla is a notorious malware that functions as a keylogger and information stealer. 

By logging keystrokes and capturing screenshots on infected systems, this notorious malware targets sensitive data like:-

  • Login credentials
  • Financial information

Recently, the cybersecurity researchers at BitSight Security discovered that AgentTesla malware had been actively attacking Windows machines to steal sensitive data.

Document
Free Webinar

Compounding the problem are zero-day vulnerabilities like the MOVEit SQLi, Zimbra XSS, and 300+ such vulnerabilities that get discovered each month. Delays in fixing these vulnerabilities lead to compliance issues, these delay can be minimized with a unique feature on AppTrana that helps you to get “Zero vulnerability report” within 72 hours.

AgentTesla Malware Attacking Windows

AgentTesla is a .NET-written Windows malware that steals sensitive data and emerged for the first time in 2014. It faced legal issues once it was sold widely, leading to its shutdown in March 2019. 

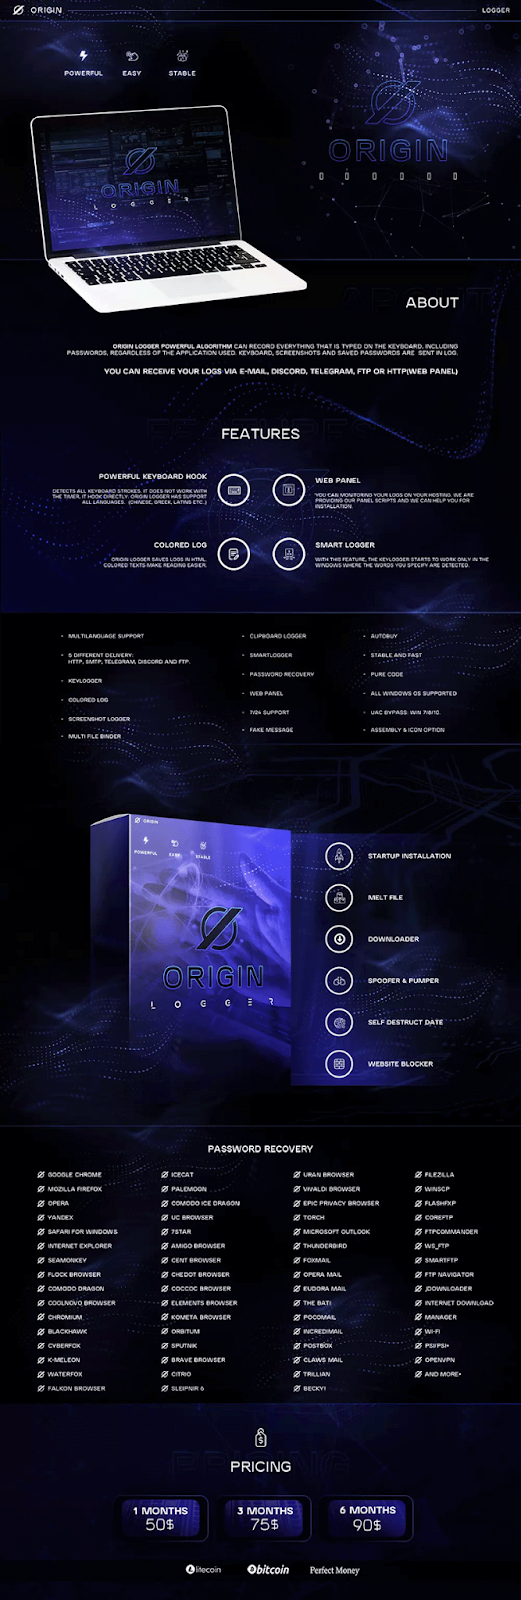
It later reemerged as OriginLogger, which shares the same code base and poses a persistent threat as a licensed-based Malware as a Service (MaaS) on the clear web with websites like-

  • agenttesla[.]com
  • originpro[.]me
OriginLogger
OriginLogger (Source – Bitsight)

Researchers found that one of the sites sells short-term licenses (up to six months) for AgentTesla’s instance “OriginLogger” with several customizations. 

AgentTesla is a prevalent malware that was rebranded and updated in November. It spreads via phishing emails with loaders like:-

After infecting it harvests the following data:-

  • Credentials
  • Keystrokes
  • Clipboard data
  • Screenshots 

Not only that even, it also uses various protocols like:-

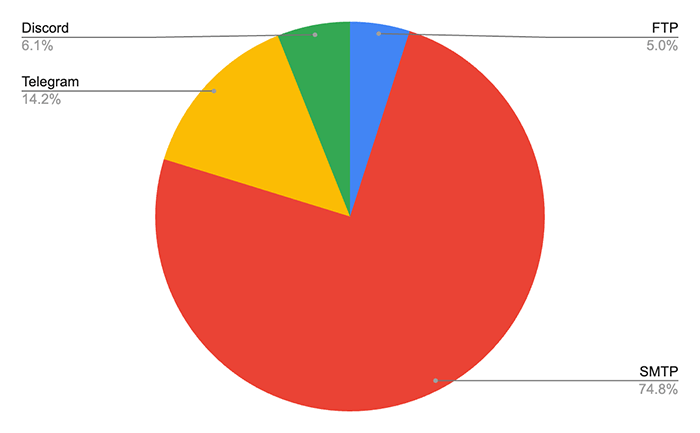
Over 1500 recent AgentTesla configurations were found, and 75% used email for exfiltration. However, since December 2022, no HTTP exfiltration has been observed.

Exfiltration methods by number of configs
Exfiltration methods by number of configs (Source – Bitsight)

The data gathered by the malware are mainly from:-

  • Browsers
  • VPN clients
  • Mail clients
  • FTP clients
  • VNC clients
  • Microsoft Applications
  • Social media apps

Pricing plans

In total, there are three plans, and here below, we have mentioned those three plans:-

  • 1-month plan will cost $50
  • 3-month plan will cost $75
  • 4-month plan will cost $90

Researchers accessed 3 months of victim data from 210 malware campaigns, compromising 5300 computers between Oct-Dec 2023. 

Around 2000 IP addresses were geographically mapped, which shows that the U.S. was the most targeted country, followed by

Common country top-level domains suggested European ties. Exploited data is used for direct exploitation and profit-driven schemes like ransomware and business email compromise attacks.

To counter the evolving threats, researchers urged to integrate the:-

  • Multi-layered defense mechanism
  • Proactive detection
  • Employee awareness
  • Robust cybersecurity strategy

Try Kelltron’s cost-effective penetration testing services for free to assess and evaluate the security posture of digital systems


[ad_2]
Source link

January security update rolling out for Pixel Watch, Pixel Watch 2

0
[ad_1]

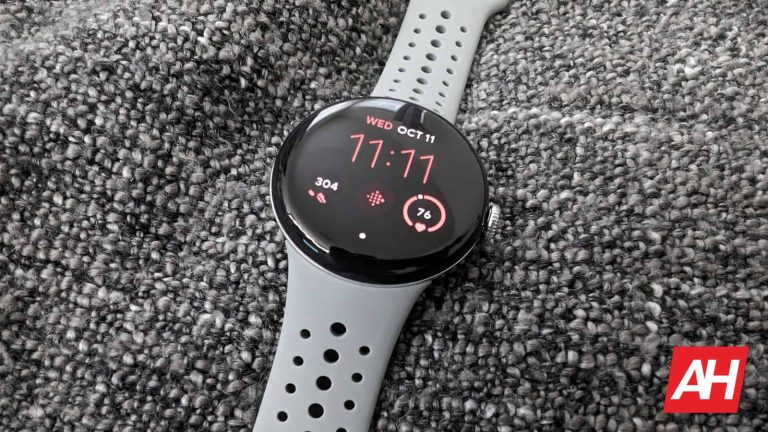
As the second week of January unfolds, Google is gearing up to release a new security patch. It will be the first security update of 2024 for the Pixel Watch and Pixel Watch 2. The tech giant has officially announced the commencement of the rollout for the January 2024 security update. It is specifically tailored for Pixel Watch devices operating on Wear OS 4.

For users eagerly awaiting the update, Google will make it available to the supported watches all over the world gradually over the next week. The phased rollout reportedly depends on the specific device and carrier.

Google recommends installing all available updates to receive the 2024 security patch

The company has primarily focused on addressing security vulnerabilities for the January 2024 security update. The build number of this update is TWD9.240105.004.A1, noted Google. You can explore the detailed changes accompanying the patch in the Android Security Bulletins. However, the emphasis is on enhancing the security posture of Pixel Watch devices. Users should expect fixes and improvements aimed at fortifying the device against potential threats.

To ensure Pixel Watch and Pixel Watch 2 users get the latest security enhancements, Google recommends users install the previously available updates. To do so, you can navigate to the Settings menu, scroll down to System, and select System Updates. Google will likely notify users on their watches when the over-the-air (OTA) update becomes accessible. Google staggers the release across carriers and devices to manage a seamless deployment.

The overarching objective of the January 2024 update is to equip Pixel Watch users with the latest security patches, aligning with Google’s commitment to providing a secure and up-to-date user experience. Users are encouraged to stay vigilant for notifications on their devices and promptly apply the update to fortify their Pixel Watches against potential security threats.


[ad_2]
Source link

Apple wants visionOS devs to avoid two terms: it’s AR and VR

0
[ad_1]

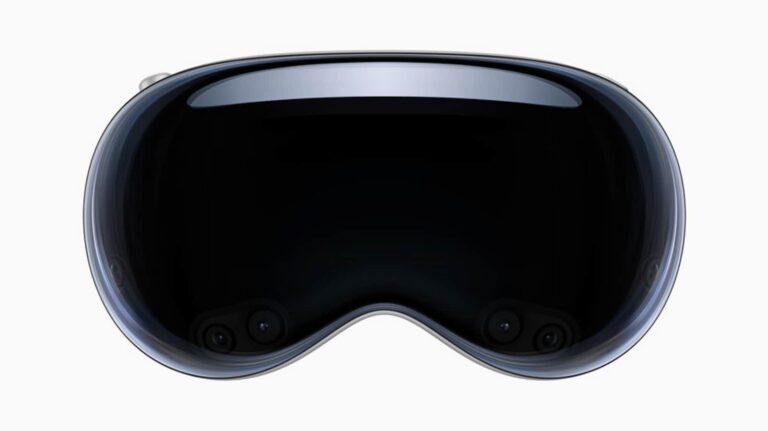
Apple Vision Pro is coming very soon; pre-orders begin on January 19, and it will hit shelves in the US on February 2. If that’s not all, it is also tipped to sell like hotcakes. It runs on Apple’s upcoming visionOS, especially for Apple Vision Pro. Now, let’s delve into Apple’s strategy on the developer front. California’s tech major has laid out stringent guidelines, urging developers not to label their applications for visionOS as “AR” or “VR.”

Apple doesn’t want visionOS apps to be called AR or VR

After Apple shared details about the Apple Vision Pro launch, they updated Xcode so that developers can now submit visionOS apps to the App Store. But there’s a rule: Apple doesn’t want developers to use terms like “AR” and “VR” for their new apps. They want to make it clear that visionOS is for spatial computing, not the traditional AR or VR stuff.

There’s more to it. The company has asked developers to avoid using terms such as AR, VR, XR, and MR, according to 9to5Mac. Notably, these terms stand for Augmented Reality, Virtual Reality, Extended Reality, and Mixed Reality, respectively. Notably, folks at TechRadar pointed out that Apple primarily markets the Vision Pro as a “spatial computing” platform. However, at the 2023 WWDC, Apple CEO Tim Cook presented it as an “entirely new AR platform.” You read it right, AR.

Apple’s new laws for developers

A new page on the Apple Developer website outlines all the recommendations and requirements for launching Apple Vision Pro apps on the App Store. The guidelines cover various aspects, including testing procedures, screenshot preparation, icon creation, and more.

Additionally, Apple provides instructions on how developers should name and describe their apps. Apple’s demand from developers to meet requirements such as using the lowercase “v” for the “visionOS” comes as expected. However, the rule against using AR or VR, nevertheless, stands out.

For users eager to experience the Apple Vision Pro, it comes at $3,499 for the 256GB storage variant. It is available exclusively in the US for now.


[ad_2]
Source link

Best of CES 2024: Hisense 110UX ULED TV

0
[ad_1]

Hisense really stole the show at CES 2024 by offering the next level of viewing experience

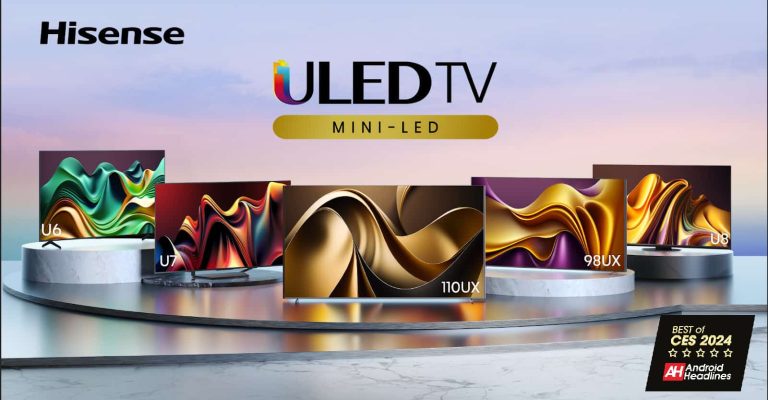
CES 2024 just happened, and a bunch of tech brands showed off their latest and greatest technology. One of the brands is Hisense, a leader in the display and television industry. Among the handful of TVs it announced, we saw the Hisense 110UX. This is truly the TV to get if you are looking to get the most out of your movie-watching experience.

There’s some serious tech going on behind the screen with the Hisense 110UX. First off, this is a massive 110-inch display made to create a cinematic movie-watching experience. It uses mini LED technology, which means that it’s capable of producing a picture with higher contrast than a traditional LCD display. Also, it pretty much eliminates all blooming. So, you will have a viewing experience on par with an OLED display.

The Hisense 110UX can be viewed in very bright environments as well. It has a jaw-dropping 10,000 nits of peak brightness. That’s incredibly bright. To put that into perspective, you can see your phone clearly in the direct sunlight with 2000 hits of brightness. So, this TV can be bright enough for any situation.

A screen this impressive wouldn’t possibly come without incredible dynamic range. In fact, the TV’s hardware and software work in sync to enhance the picture and cover a wide dynamic range. It covers 95% of the BT.2020 color palette. Other TVs from leading brands typically cover only 80%. With the inclusion of AI, the Hi-View Engine X chipset further refines the picture to make it even better.

Moving on to the audio, this TV uses 4.2.2 Channel audio and is also compatible with Dolby Atmos Flex Connect. It has an amazing picture with amazing audio to match.

The Hisense 110UX brings a truly next-level viewing experience, and that’s why it won the Android Headlines Award for Best of CES 2024.


[ad_2]
Source link

Affordable POCO X6 series is here with 120Hz displays, 67W charging

0
[ad_1]

Xiaomi has released new POCO smartphones, as expected. The POCO X6 series is here. It consists of two smartphones, the POCO X6 and POCO X6 Pro. Their design is very similar, but the ‘Pro’ model does have a slightly different-looking camera setup on the back.

Both smartphones have a two-tone finish on the back, thanks to a large camera island which is black-colored. The frame around the phone is flat, though it does have chamfered edges. All the physical buttons sit on the right-hand side of both smartphones. The two phones are different in the spec department, so we’ll talk about them separately. We’ll kick things off with the ‘Pro’ model.

The POCO X6 Pro is a bit more powerful, but it looks very similar to its sibling

The POCO X6 Pro is the more powerful of the two. It is fueled by the MediaTek Dimensity 8300-Ultra SoC. It comes with either 8GB or 12GB of RAM, and those two models are accompanied by 256GB and 512GB of storage, respectively. Xiaomi used LPDDR5X RAM here, and UFS 4.0 flash storage. When it comes to performance, LiquidCool Technology 2.0 is also on board.

A 6.67-inch CrystalRes 1.5K display sits on the front. This is an AMOLED DotDisplay, as Xiaomi calls it. The refresh rate here is 120Hz, and the phone has an instant touch sampling rate of 2,160Hz. The max brightness is 1,800 nits, and the panel is protected by the Gorilla Glass 5.

POCO X6 Pro all colors

It includes a 5,000mAh battery, and supports 67W charging

A 5,000mAh battery is also included, and 67W wired charging is supported. You’ll also find a charger in the box. A 64-megapixel main camera (OIS) sits on the front, along with an 8-megapixel ultrawide camera, and a 2-megapixel macro camera. A single 16-megapixel unit is included on the front.

There are two SIM card slots here, and 5G is supported, as is Bluetooth 5.4. The phone is IP54 certified, while HyperOS is a part of the package too, as are stereo speakers. The POCO X6 Pro also has an in-display fingerprint scanner and an IR blaster.

The POCO X6 Pro measures 160.45 x 74.34 x 8.25mm (8.35mm vegan leather model), and weighs 186 grams (plastic) / 190 grams (vegan leather model). The phone comes in Black, Gray, and Yellow colors as shown above.

The POCO X6 has a 120Hz display, and utilizes Qualcomm’s SoC

The POCO X6, on the flip side, is fueled by the Snapdragon 7s Gen 2 processor. It also comes in 8GB and 12GB RAM variants. The 8GB RAM model includes 256GB of storage. The 12GB RAM variant is available in both 256GB and 512GB storage flavors. LPDDR4X RAM is used, and UFS 2.2 flash storage, so it’s inferior to what the ‘Pro’ model offers.

A 6.67-inch CrystalRes 1.5K AMOLED DotDisplay is in use here too. It also offers a 120Hz refresh rate, and a 2,160Hz instant touch sampling rate. The peak brightness is the same as on the ‘Pro’ variant, and Gorilla Glass Victus protects this panel.

POCO X6 all colors 1

A slightly larger battery is in use here, while a charger is included

This handset includes a 5,100mAh battery, and supports 67W charging, while the charger is included in the box. The POCO X6 also has a 64-megapixel main camera with OIS, in addition to an 8-megapixel ultrawide camera, and a 2-megapixel macro unit.

The POCO X6 has two SIM card slots and supports Bluetooth 5.2, and HyperOS. It has an in-display fingerprint scanner, stereo speakers, and is IP54 certified. An IR blaster is included at the top of the phone, and facial scanning is enabled too.

This smartphone measures 161.15mm x 74.24 x 7.98mm, and weighs 181 grams. The POCO X6 comes in Black, Blue, and White colors, all of which are shown above.

The pricing starts at $249

The POCO X6 Pro with 8GB of RAM and 256GB of storage costs $299. The variant with 12GB of RAM and 512GB of storage is priced at $369 via “official e-commerce channels”. The POCO X6, ont he flip side, comes in three variants. The 8GB RAM model with 256GB of storage costs $249. The 12GB RAM models with 256GB and 512GB of storage are priceed at $269 and $319, respectively. Early bird discounts are also applicable for limited time.


[ad_2]
Source link

Best Of CES 2024: Matic robot vacuum

0
[ad_1]

Matic is the robot vacuum we’ve all been dreaming of

Robot vacuums are a very normal part of everyday life for many people these days. If you think back to about 20 years ago, it was a different story. Robot vacuums were a thing but they were much less common in households. These days, you can find robot vacuums in many people’s homes, and across every price point with a varying degree of features. Many of them offer similar functions but at the same time, can be unique in more than a few ways. All of them have one thing in common though.

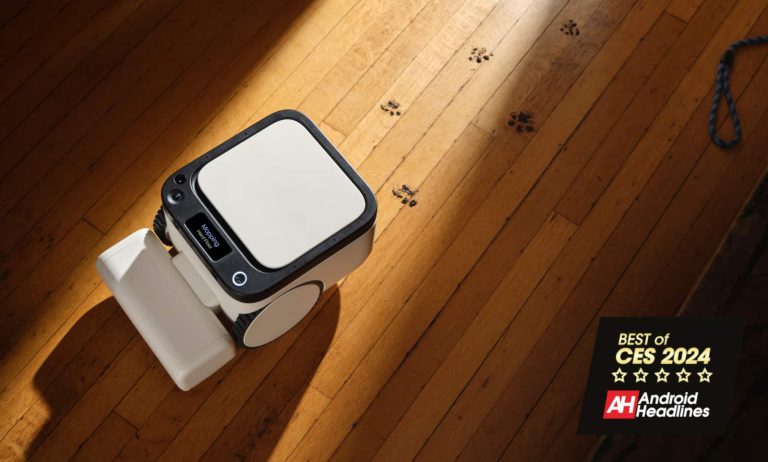
They all use a combination of sensors and lidar tech to capture a map of your home and then use that to navigate and clean up. Enter Matic, a robot vacuum that was announced at CES this week. It swaps all of that out for five cameras powered by computer vision to visually see where it’s cleaning. The reason this is a big deal is because Matic, the company of the same name that created this little cleaning bot, says it solves the two biggest problems that other robot vacuums have. They can get stuck or lost more often than you’d like. Matic apparently doesn’t have these issues.

It won’t get lost because the 5 cameras will allow it to see all of its surroundings. It knows where it’s going at all times and is less likely to bump into anything. The computer vision meanwhile, helps it learn over time to make it smarter. Learning when the best times to clean are. It also has big wheels on the front to help it roll over any floor surface. So high pile rugs shouldn’t be an issue.

Nor should other things that it might encounter as it rolls around your home sucking up dirt and debris. Cables, shoes, a coffee mug. If these things are sitting around on the floor the cameras will see it, Matic says, and the vacuum will simply move around that area.

This bot has a trick up its sleeve – it can clean up liquid spills

If there’s one thing robot vacuums need improvement on, it’s mopping. A lot of the models out today have variants with a built-in mop. But most of them won’t do as good of a job as you hope and none of them can actually clean up liquid spills. Matic can. The unique way it was designed allows it to roll forward with the vacuum head sucking up dirt and debris. If it comes across a liquid spill or a spot that needs mopping, and then the vacuum head lowers as Matic changes into mop mode, and it rolls over that area to clean it up.

It also stores all of the liquid, dirt, and debris in the same bag. You do have to empty the bag yourself, but only once every month or so. You just open up the top lid and pull the bag out and toss it, then replace the bag so it’s ready again. The idea is that Matic is a completely autonomous robot vacuum (other than emptying the bag) that doesn’t need input from you whether it’s to start a clean or set up a schedule. It’ll just clean on its own and get better at doing it the more it cleans.

Matic is a unique robot vacuum that offers features that set it apart from every other robot vacuum on the market. And that’s why Matic has earned the Best of CES 2024 award. Matic will begin shipping in March and pre-orders are already up on the Matic website. It retails for a discounted price of $1,495 if you pre-order.


[ad_2]
Source link

Galaxy S21 FE, Note 20 receive Samsung’s January 2024 update

0
[ad_1]

Samsung has released the January 2024 Android security patch for the Galaxy S21 FE. The Fan Edition (FE) device is currently picking up the latest security update in some European countries. A wider rollout should follow soon. The Galaxy Note 20 series, meanwhile, is now receiving the update in international markets following the US release a few days back.

Galaxy S21 FE gets the January 2024 security update

First spotted by SamMobile, the January SMR (Security Maintenance Release) is now available for Galaxy S21 FE users in Ireland, Spain, and the UK. The update comes with the firmware build number G990BXXS6FWL5. The build number may vary in other regions but the content of the update will remain the same. Samsung’s changelog confirms that the device is only picking up this month’s security fixes.

“The security of your device has been improved,” the official release notes state. The January 2024 security release for Galaxy devices contains fixes for 80 vulnerabilities. 75 of those are Android OS patches coming from Google, including one critical issue. The remaining five vulnerabilities don’t exist on Android OS but exclusively on Samsung products and system components.

If you are using the Galaxy S21 FE, the latest update will patch all of these vulnerabilities on your phone. Samsung has already pushed the January SMR to the Galaxy S23 FE, Galaxy S22 series, Galaxy Note 20 series, Galaxy Z Fold 5, Galaxy Z Flip 5, Galaxy Z Fold 4, Galaxy Z Flip 4, Galaxy Z Fold 3, and Galaxy Z Flip 3. The updates may not be available globally but it is just a matter of time now.

As usual, you will get a notification once a new update is available for your Samsung smartphone. You can tap on the notification to initiate the download and complete the update. To check for updates manually, go to Settings > Software update and tap on Download and install. While the latest update doesn’t bring any new features, Samsung will push Android 14-based One UI 6.1 to most of these devices shortly.

The Galaxy Note 20 series is receiving the new security patch globally

Earlier this week, Samsung pushed the January update to the Galaxy Note 20 and Galaxy Note 20 Ultra in the US. The last two Note-branded phones are now receiving the new SMR globally. The update is available in Europe and Latin America with the firmware build number N98*FXXS9HXA1. The Galaxy Note 20 series is done getting feature updates, so no One UI 6.1 for the lineup. It will get security patches at least until late 2024.


[ad_2]
Source link