DNA data deserves better, with Suzanne Bernstein: Lock and Code S05E01

0
[ad_1]

This week on the Lock and Code podcast…

Hackers want to know everything about you: Your credit card number, your ID and passport info, and now, your DNA.

On October 1 2023, on a hacking website called BreachForums, a group of cybercriminals claimed that they had stolen—and would soon sell—individual profiles for users of the genetic testing company 23andMe.

23andMe offers direct-to-consumer genetic testing kits that provide customers with different types of information, including potential indicators of health risks along with reports that detail a person’s heritage, their DNA’s geographical footprint, and, if they opt in, a service to connect with relatives who have also used 23andMe’s DNA testing service.

The data that 23andMe and similar companies collect is often seen as some of the most sensitive, personal information that exists about people today, as it can expose health risks, family connections, and medical diagnoses. This type of data has also been used to exonerate the wrongfully accused and to finally apprehend long-hidden fugitives.

In 2018, deputies from the Sacramento County Sherriff’s department arrested a serial killer known as the Golden State Killer, after investigators took DNA left at decades-old crime scenes and compared it to a then-growing database of genetic information, finding the Golden State Killer’s relatives, and then zeroing in from there.

And while the story of the Golden State Killer involves the use of genetic data to solve a crime, what happens when genetic data is part of a crime? What law enforcement agency, if any, gets involved? What rights do consumers have? And how likely is it that consumer complaints will get heard?

For customers of 23andMe, those are particularly relevant questions. After an internal investigation from the genetic testing company, it was revealed that 6.9 million customers were impacted by the October breach.

What do they do?

Today on the Lock and Code podcast with host David Ruiz, we speak with Suzanne Bernstein, a law fellow at Electronic Privacy Information Center (EPIC) to understand the value of genetic data, the risks of its exposure, and the unfortunate reality that consumers face in having to protect themselves while also trusting private corporations to secure their most sensitive data.

“We live our lives online and there’s certain risks that are unavoidable or that are manageable relative to the benefit that a consumer might get from it,” Bernstein said.

“Ultimately, while it’s not the consumer’s responsibility, an informed consumer can make the best choices about what kind of risks to take online.”

Tune in today to listen to the full conversation.

Show notes and credits:

Intro Music: “Spellbound” by Kevin MacLeod (incompetech.com)
Licensed under Creative Commons: By Attribution 4.0 License
http://creativecommons.org/licenses/by/4.0/
Outro Music: “Good God” by Wowa (unminus.com)


We don’t just report on threats—we remove them

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.


[ad_2]
Source link
Galaxy Z Fold 4, Flip 4 pick Samsung’s January 2024 update

0
[ad_1]

It’s the first business day of 2024 and Samsung has already released a new security patch. The company is pushing the January 2024 security update to the Galaxy Z Fold 4 and Galaxy Z Flip 4. More Galaxy devices will join the party over the next few weeks.

Galaxy Z Fold 4 and Flip 4 receive the January security update

As of this writing, Samsung is rolling out the January security patch to the Galaxy Z Fold 4 and Galaxy Z Flip 4 in Europe. The new firmware build numbers for the two devices are F936BXXS4EWL5 and F721BXXS4EWL5, respectively. The rollout will soon reach other markets, including the US.

The official changelog supplied by Samsung confirms that this update is all about the latest security fixes. “The device is protected with improved security,” the only entry in the changelog for both foldables reads. The Galaxy Z Fold 4 and Galaxy Z Flip 4 recently received the Android 14-based One UI 6.0 update with several new features and functional improvements. The next feature update should be One UI 6.1.

Details about the vulnerabilities patched this month are not available yet. However, as usual, the new security update should contain several dozen Android OS patches from Google. A handful of those are expected to be critical security fixes. Samsung will bundle a few Galaxy-exclusive patches with the Android fixes. The latter group of patches doesn’t apply to Android products from other brands.

The January 2024 SMR (Security Maintenance Release), as Samsung calls its security updates, will gradually reach other eligible devices. The Korean firm pushes monthly security updates to its flagships and premium mid-range models for a few years after launch. They are then demoted to quarterly updates. Budget models start at quarterly updates and drop to bi-annual releases (two updates in a year) later.

One UI 6.1 will bring new features to these Samsung foldables

Samsung will introduce One UI 6.1 with the Galaxy S24 series later this month—expected to debut on January 17. The new One UI version, which is still based on Android 14, brings several new AI features. From AI wallpapers and lockscreen effects to AI-powered camera enhancements and editing tools, there is a lot to look forward to.

Following the Galaxy S24 launch, Samsung will update its older flagships to One UI 6.1. The Galaxy Z Fold 4 and Galaxy Z Flip 4 should also receive the update. However, we don’t expect all new AI features to trickle down to older models. The company may share more details following the unveiling of the new flagships. We will keep you posted accordingly.


[ad_2]
Source link

DODOcase reveals new MagSafe iPhone 15 Cases

0
[ad_1]

DODOcase has just announced its new lineup of cases for the iPhone 15, 15 Plus, 15 Pro and 15 Pro Max. The company says that these will “seamlessly blend traditional partisanship with innovative design, DODOcase offers premium-quality cases for various Apple devices.”

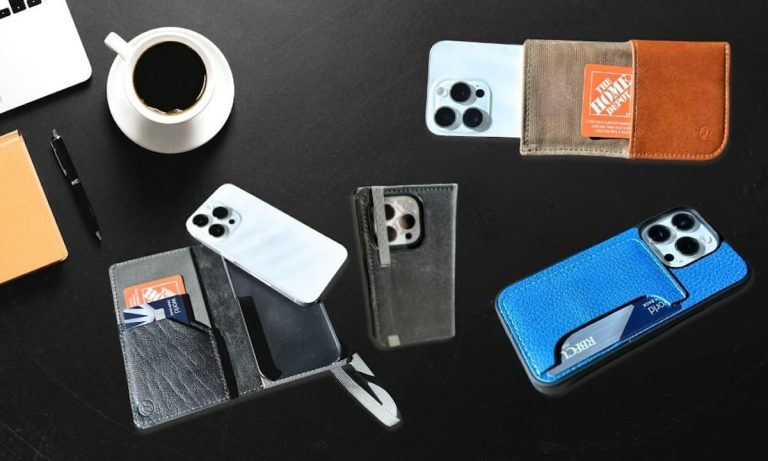
First up is a new Colorway Shockproof iPhone case with MagSafe. With this case you can really express yourself with bold colors in Italian pebble leather. It’s a shockproof case, that has a newly redesigned polymer tray to maintain a sleek minimalistic aesthetic.

Additionally, DODOcase has a new Rugged leather shockproof iPhone case with MagSafe. This is a leather case that will safeguard your iPhone 15 with a bumper that can absorb shock and protects against accidental drops.

DODOcase also has a number of new wallet cases

Aside from the MagSafe-compatible cases for the iPhone 15, DODOcase also has a number of different wallet cases available too, which includes a new Colorway shockproof iPhone Card case, which is for those that love bold colors. It uses Italian Pebble Leather to carry your cards in style.

Like its MagSafe counterpart, the Rugged Leather Shockproof iPhone case is also great for those who want a natural leather look. With a bumper around the case to protect it and absorb shock from drops.

DODOcase also offers a new Leather Phone Wallet, which is an all-in-one case for credit cards, ID, cash, business cards, and receipts for your iPhone 15. This was designed to fit comfortably in your pocket without adding any bulk.

There is also a new Durable Wallet Phone sleeve, which is a pretty simple case, it’s a sleeve that features external leather pockets for cards, cash and more. There’s also the Custom iPhone Case. You can customize your case by choosing the materials and colors, all the way down to the elastic closure. You can upgrade to add credit card slots and turn your phone into a case with a wallet.

These cases are available now on the DODOcase website. They start at $45, making them pretty competitive.


[ad_2]
Source link

T-Mobile provides early glimpse into new app for deal-loving customers

0
[ad_1]

T-Mobile started the year on a high note by taking concrete measures to safeguard customers against spam and inappropriate messages. The company is now going to improve the customer experience in another meaningful way by replacing the T-Mobile Tuesdays app with an app with expanded functionality.

Even though T-Mobilescrews up every once in a while, it more than makes up for that by rolling out new deals and perks periodically. You don’t have to wait for it to announce a deal for free stuff and rewards though. Just like for everything else, there’s an app for those feeling peckish for a deal, assuming you are a T-Mobile user. It’s called T-Mobile Tuesdays and it’s the carrier’s little way of thanking you for being a customer.

As the app’s name suggests, all you are expected to do is open the app every Tuesday and see if a deal or a prize is waiting to be claimed. Even Metro by T-Mobile and Sprint customers can download the app. T-Mobile Home Internet and Small Business Internet users are also eligible.

T-Mobile is shutting down the T-Mobile Tuesdays app and introducing in its place a new app called T Life, reports Android Authority.

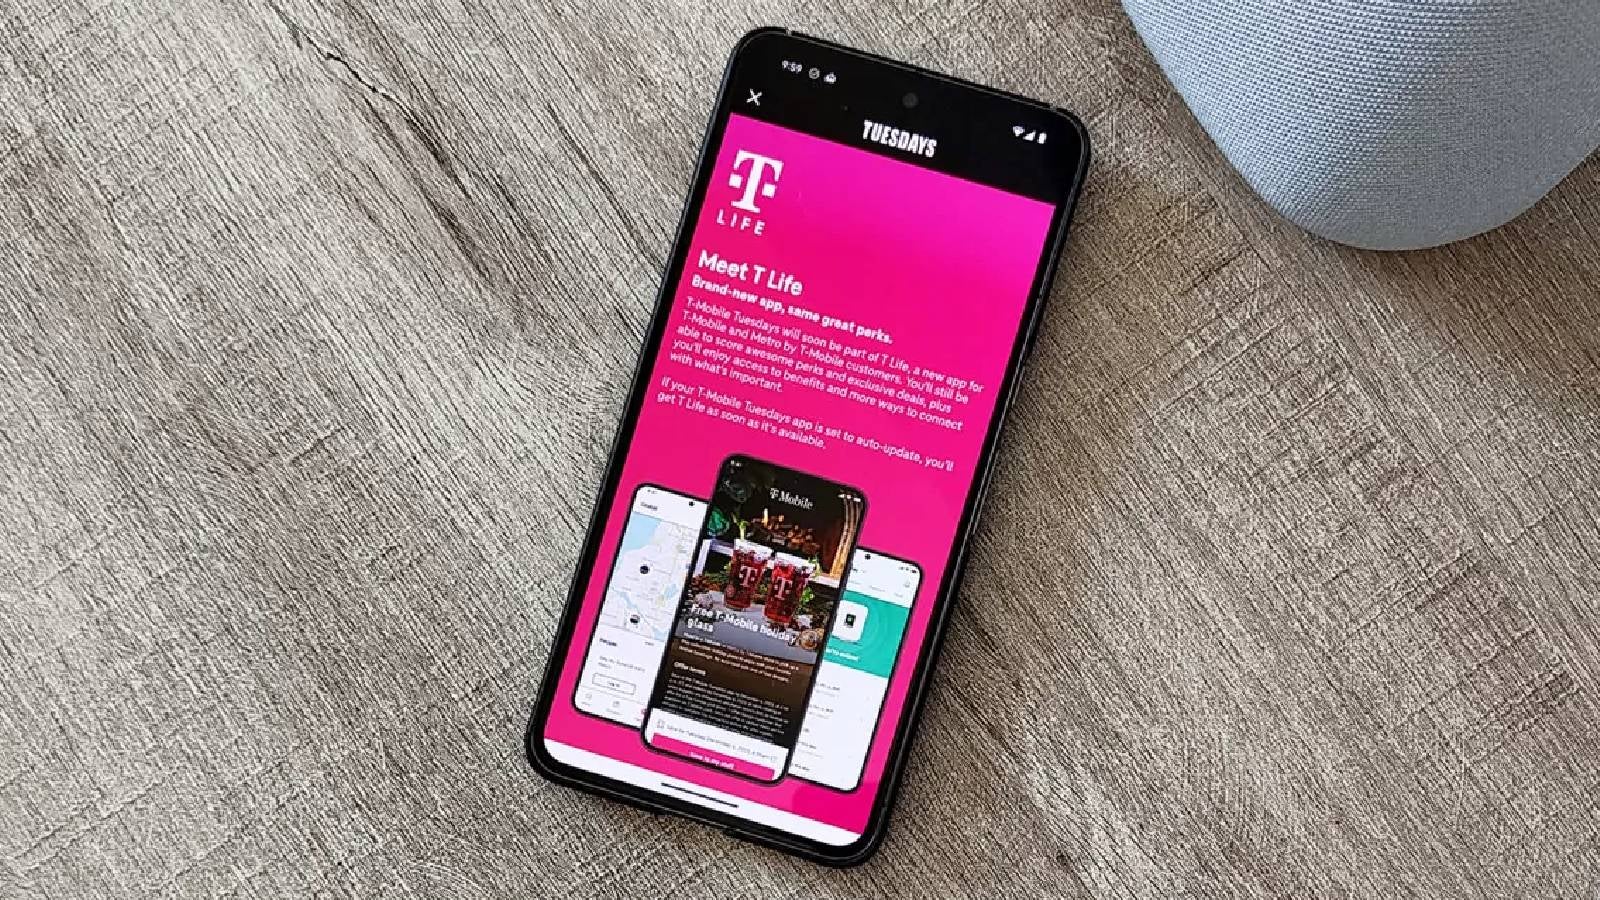
T-Mobile announced this change via the Tuesdays app. As a user, you don’t have to worry about downloading or deleting anything, as the Tuesdays app will morph into the T Life app, as long as your app is set to auto-update. The company hasn’t exactly revealed when this will happen.

Does that mean the Tuesday rewards are going away? Absolutely not. They will be a part of the new app, which will also allow you to access more benefits and provide you with “more ways to connect with what’s important.”

Released in 2016, the Tuesdays app serves more than its intended purpose at this point, which could be why it’s being replaced with a more sophisticated app. Besides, T-Mobile surely wouldn’t mind if you checked its apps on days that are not Tuesdays, and the new name will surely help with that.

The image included with the announcement gives us a little glimpse into the T Life app. It looks like a versatile app with different sections, including Global, which shows the location of a SyncUP Kids Watch, and a category which displays the status of a T-Mobile 5G Home Internet system.


[ad_2]
Source link

Galaxy A55 official renders leak in three colors

0
[ad_1]

We have stepped into the month of the Galaxy S24 launch. According to leaks, Samsung will unveil the new flagships on January 17. It will follow up with an A-series premium mid-range smartphone a couple of months later. We are talking about the Galaxy A55, which has been subject to a handful of leaks lately. Today, we bring exclusive official renders of the phone in three colors, giving you an early look at its design.

Samsung Galaxy A55 exclusive official renders

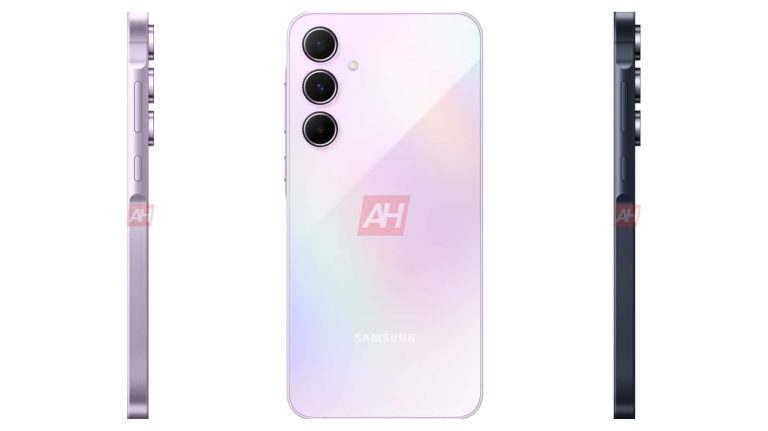
We have official renders of the Galaxy A55 in Awesome Iceblue, Awesome Lilac, and Awesome Navy colors (shown below the article). For the most part, the phone looks identical to its predecessor, the Galaxy A54. In fact, pretty much every phone Samsung launched in 2023 featured the same design language, including flagships. Not much is changing this year. However, the company appears to be differentiating mid-range models with a new design element.

The so-called Key Island button design has the frame slightly raised around the power and volume keys. Samsung introduced this design with the Galaxy A15 and Galaxy A25 launched last month. The Galaxy A55 features it too. As usual, the physical buttons sit on the right side of the device. The renders show antenna lines on the frame, confirming a metallic build. Rumors have previously hinted at an aluminum frame for the phone.

Apart from that minor bump on the right side, the frame is completely flat with rounded corners. The front and back of the handset are flat too. The rear camera array includes three lenses each protruding out of the back panel separately without a universal camera housing. A side-on view of the handset reveals that the camera lenses protrude substantially from the phone’s body. An LED flash sits next to the vertical camera setup.

On the front, the Galaxy A55 sports a flat display with sizeable bezels. The chin is slightly thicker than the other three sides, so no symmetrical bezels here. The punch hole cutout for the selfie camera sits centrally at the top. Overall, the phone doesn’t look different from the 2023 model when looking from the front or the back. The only noticeable design change is the small bump on the frame.

Samsung’s Exynos 1480 chipset will power this phone

The Galaxy A55 will be powered by Samsung’s in-house Exynos 1480 processor. The new chipset is expected to be a 4nm solution featuring four high-performance CPU cores clocked at 2.75GHz and four efficiency cores at 2.05GHz. The CPU is paired with the Xclipse 530 GPU, a custom GPU that Samsung co-developed with AMD based on its Radeon graphics technology used in PC graphics and flagship Exynos chips.

Samsung will ship the Galaxy A55 in an 8GB RAM variant, likely with 256GB of onboard storage. There may be more storage configurations, though. The device will run Android 14 out of the box, with One UI 6.1 on top. The rest of the specs, including the camera, display, and battery details, are still under wraps. We expect more leaks about the phone in the coming weeks, particularly after the Galaxy S24 launch later this month.


[ad_2]
Source link

Flutter is finally addressing its long-existing scrolling bug (or feature)

0
[ad_1]

Google has recently announced an upcoming update in its Flutter app development framework, targeted at fixing a long-existing bug related to scrolling in apps made using the platform. For those unfamiliar, Flutter is an open-source software development kit (SDK) from Google for building cross-platform mobile applications.

The peculiar scrolling bug in Flutter has earned the moniker “Flutter’s shibboleth” due to its unique nature. The bug influences the scrolling speed in Flutter-made apps depending upon the number of touches. For instance, scrolling with two fingers results in a scroll with double the speed. It deviates from the consistent scrolling experience observed in traditional Android and iOS apps.

Finally a fix for “Flutter’s shibboleth” after more than 5 years

The Flutter team has been aware of this bug since its early stages, with a GitHub issue filed in August 2017, well before Flutter’s stable release in December 2018. Despite its existence for years, a solution emerged only in October, when a Flutter contributor proposed a fix that aligns Flutter’s scrolling behavior with the standard seen on Android.

This proposal was accepted by the Flutter team as it may lead to some problems in certain scenarios. The upcoming major update, version 3.18, is currently available for beta testing. The fix addresses the bug, making scrolling in Flutter apps align with user expectations, that is the scroll speed will be independent form the number of touches. However, there will definitely be some people who used to approach it as a fun feature instead of a bug.

The Flutter team has also documented a method to revert to the fast-scrolling bug (or feature)

The Flutter team plans to further refine the scrolling behavior to accurately match how it works on iOS. With the upcoming changes, Flutter apps will automatically adapt their scrolling behavior to align with the specific platform, ensuring a more consistent and native-like experience for users.

However, recognizing the diversity of developer preferences, the Flutter team acknowledges that some may prefer to maintain the current (albeit unintentional) quick-scrolling gesture. For these developers, the team has documented a straightforward method to revert to the original scrolling style, providing flexibility for those who have grown accustomed to the existing behavior.

In conclusion, Google’s forthcoming Flutter update will address the long-standing scrolling bug (or feature for some). With the proposed changes, Flutter aims to deliver a more consistent platform-native feel for cross-platform apps. Here’s a demonstration of the fast-scrolling bug below.


[ad_2]
Source link

Motorola Razr+ heir to get “stunning” new design & AI boost

0
[ad_1]

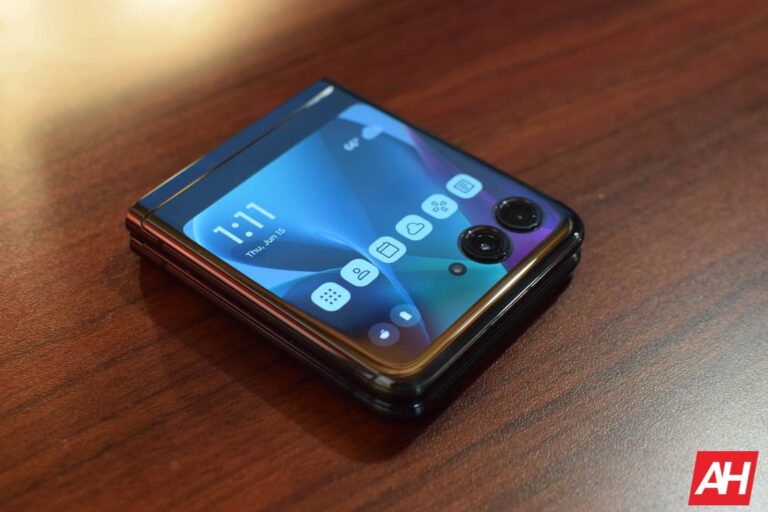
According to Lenovo China’s head of mobile devices, Chen Jin, the Motorola Razr series has a bright future. He said that the Motorola Razr+ (also known as the Motorola Razr 40 Ultra) heir will get a “stunning” new design, and also an AI boost, amongst other things.

Mr. Jin wrote on Weibo, teasing what’s to come from the company. As a side note, Motorola is owned by Lenovo, in case you don’t know that. So, this is official info we’re looking at here.

The Motorola Razr+ heir is said to get a “stunning” new design, AI boost & more

Now, Motorola’s flagship clamshell for 2024 will likely be fueled by the Snapdragon 8 Gen 3. That could explain the AI teaser provided here. A “stunning” new design is also mentioned, which indicates we may see a major change here.

The Motorola Razr+ has been mostly hailed for its design. It has a huge cover display, and it’s very eye-pleasing, well… to most people anyway. Motorola will probably look to polish things out further with the Motorola Razr+ 2024, or whatever the phone’s name ends up being.

As a side note, the Motorola Razr+ actually comes with the Snapdragon 8+ Gen 1 SoC. If its successor gets the Snapdragon 8 Gen 3, that will be quite a leap, and it would certainly be nice to see.

Its specs are still a mystery

What about the phone’s specs? Well, they’re a mystery at this point, as Chen Jin did not reveal any such details. We do presume that quite a few things will remain unchanged, such as the display size, for example.

Motorola will be looking to improve the SoC, of course, and could potentially include more RAM. We could also get better displays, but probably not larger ones, while charging is a complete mystery. We’ll have to wait and see.

Don’t expect the next-gen Motorola Razr+ to arrive soon, though. The Motorola Razr+ launched in June last year, so… we’re in for quite a wait. Well, unless Motorola drastically changes its release cycle.


[ad_2]
Source link

Samsung aims for tech dominance with excellence and flexibility

0
[ad_1]

Samsung plans to enhance its competitiveness in the global tech industry this year through technological excellence and flexibility. The company revealed its strategic priorities in a memo to employees on the occasion of the new year earlier today. The memo, signed by two top-level executives, outlined various strategies to maintain a competitive edge.

Samsung prioritizes tech supremacy and flexibility this year

According to a Korea Bizwire report, Samsung’s New Year memo to employees was jointly signed by its co-CEOs Han Jong-hee and Kyung Kye-hyun. Han is also a Vice Chairman at the company and heads its DX Division, which encompasses the visual display, digital appliances, home appliances, health and medical equipment, mobile experience, and networks businesses.

Kyung, meanwhile, is a President at Samsung and the Director of SAIT (Samsung Advanced Institute of Technology), the Korean behemoth’s research and development unit. He also leads the semiconductor business division. In their joint memo, the two co-CEOs highlighted the need to widen the technological gap with its competitors to stay ahead of the curve.

“We will prioritize strengthening our fundamental competitiveness, including the core values that have guided Samsung Electronics, such as super-gap technologies,” they said. The Samsung executives encouraged the chip division to create a technological advantage. The semiconductor business has been its cash cow for years but suffered massive losses in 2023 due to multiple factors.

Han and Kyung emphasized a customer-first strategy for mobile, home appliances, and software divisions. They urged employees to focus on performance and quality. The Samsung executives further stressed the need to be proactive to quickly adapt to changes in the industry. These include the rapid rise in the use of artificial intelligence (AI) over the past year and growing eco-friendly practices.

AI will be pivotal to all technological advancements this year

“We should revolutionize the way we work and our device experience by applying generative AI to work,” the memo read. “Moving from the passive green response of the past, we should pull off a fundamental shift in thinking and discover the green products of the future.” Samsung’s upcoming Galaxy S24 flagships bring tons of new AI features. The devices are also expected to use more recycled material.

It remains to be seen if these strategic moves bring a change to Samsung’s fortune this year. 2023 has been a forgettable year for it, at least financially. In the first nine months of last year, the company generated a sales revenue of about $147 billion, down over 17 percent from the same period in 2022. Its operating profit tumbled a whopping 90 percent to just $2.9 billion. Samsung will publish its full-year earnings report for 2023 later this month.


[ad_2]
Source link

New DLL Hijacking Technique-Attackers Bypass Windows Security

0
[ad_1]

DLL hijacking is a technique where a malicious DLL (Dynamic Link Library) is placed in a directory that a vulnerable application searches before the legitimate one. 

When the application is launched, it unknowingly loads the malicious DLL instead, allowing attackers to:-

  • Execute arbitrary code
  • Compromise the system

Recently, the cybersecurity researchers at a multi-layered incident response company, Security Joes, discovered a new DLL hijacking technique that enables threat actors to bypass Windows mechanisms.

New DLL Hijacking Technique

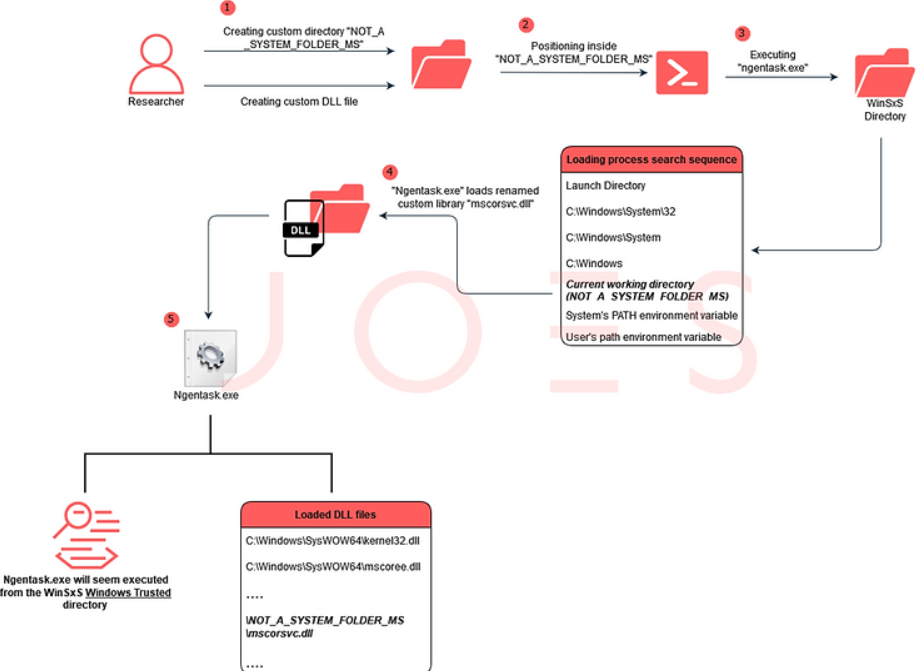
This new technique exploits trusted WinSxS executables using DLL Search Order Hijacking. 

This enables threat actors to execute malicious code within Windows folders, which eliminates the need for extra binaries. 

Besides this, it’s compatible with both Windows 10 and 11, as it bypasses high privilege requirements.

The DLL Search Order Hijacking exploits how Windows apps load DLLs, taking advantage of those without specified file paths. 

Threat actors manipulate apps depending on predefined search orders that place a malicious DLL in a prioritized directory. 

Many methods for this require apps not to specify full paths, often due to development oversights.

Knowing how Windows loads DLLs and executables is one of the key things, and the system follows a sequence during the loading process.

This ensures efficient operation by locating necessary components like DLLs. Not only that even, it also provides an alternative method for finding resources.

Besides this, the Windows OS flow for searching and loading resources includes the following things:-

  • Application’s launch directory
  • C:\Windows\System32
  • C:\Windows\System
  • C:\Windows
  • Current working directory
  • Directories in the system’s
  • User’s PATH variables

Exploiting the loading process lets threat actors inject unauthorized code into the trusted processes, which helps in deceiving the:-

  • Security tools
  • Security experts/analysts

This new malicious technique is completely sophisticated and stealthy as it enables threat actors to achieve several types of malicious goals like:-

  • Compromise systems
  • Evade detection

The WinSxS folder is a critical component in Windows OS at “C:\Windows\WinSxS.” This vital component crucially maintains multiple versions of system files. 

Not only that even, it also preserves previous versions during updates, which causes the folder to grow with each update for the Windows operating system.

Execution flow of the DLL Search Order Hijacking
Execution flow of the DLL Search Order Hijacking (Source – Security Joes)

Here below, we have mentioned all the key purposes of the WinSxS folder:-

  • Version Management
  • System Integrity
  • Dynamic Activation

Advantages New DLL hijacking technique

Here below, we have mentioned all the key advantages of this new DLL hijacking technique:-

  • Circumventing High Privilege Requirements
  • Eliminating the Need for Additional Binaries
  • Enhancing Stealth

PoC

Here below, we have mentioned the Proof-of-Concept video:-


[ad_2]
Source link

Iranian Food Delivery Giant Snappfood Cyber Attack: 3TB of Data Stolen

0
[ad_1]

A hacker or hacker group, identified as “irleaks” (presumably indicating Iran Leaks), publicly disclosed the Snappfood cyber attack on Breach Forums and Telegram over New Year’s Eve.

Snappfood, a prominent online food delivery service in Iran, has fallen victim to a major data breach, during which cybercriminals stole personal information of millions of customers, Hackread.com can confirm.

Operating similarly to other food delivery platforms, Snappfood facilitates users in Iran to conveniently order food from a diverse range of restaurants through its mobile app or website, subsequently having it delivered to their doorstep. It forms part of the larger Snapp group, which includes Snapp’s ride-hailing services.

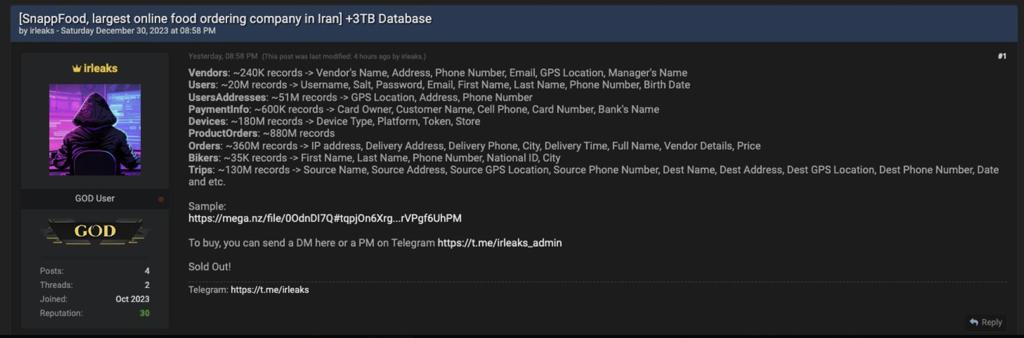
In the wake of this data breach, an individual operating under the alias “irleaks” (presumably indicating Iran Leaks) publicly disclosed a sample of the stolen data on the notorious Breach Forums, indicating the specifics of the compromised information.

As seen by Hackread.com, the hacker claimed to have acquired an extensive trove of data exceeding 3TB. Allegedly, the stolen records include:

  1. Customer Information: Details of over 20 million customers, including usernames, password hashes, email addresses, full names, dates of birth, and phone numbers.
  2. Vendor Records: Records of 240,000 vendors, featuring names, addresses, phone numbers, email addresses, GPS locations, and managers’ names.
  3. Payment Information: Payment details of over 600,000 customers, incorporating card owner names, customer full names, phone numbers, card numbers, and bank names.
  4. Device Data: Data from 180 million devices, including device types, platforms, tokens, and store names.
  5. Product Orders: The hacker alleges to have accessed more than 880 million product order records.
  6. Orders: Apparently, 360 million order details, encompassing IP addresses, delivery addresses, delivery phone numbers, city, time, customer full names, vendor details, and prices, were compromised.
  7. Biker/Rider Details: The breach also affected the details of the bikers or riders responsible for order delivery, with 35,000 records, including full names, phone numbers, national ID card details, and cities, being stolen.
  8. Trip Details: The breach allowed “irleaks” to extract trip-related information, comprising 130 million records containing source names, addresses, GPS locations, phone numbers, destinations, and addresses.
Iranian Food Delivery Giant Snappfood Cyber Attack: 3TB of Data Stolen
irleaks’ post on Breach Forums (Screenshot credit: Hackread.com)

Snappfood Acknowledges the Data Breach

While the official Snappfood Iran website was inaccessible at the time of writing this article, on December 31, 2023, the company publicly acknowledged the breach on Twitter (now X), acknowledging the issue. Snappfood’s social media representative disclosed that Iran’s Cyber Police (FATA) is actively working to identify the breach’s source.

However, the company maintains that customers’ payment data, especially card security codes (CCV), passwords, and expiration dates, remain secure and were not accessed by hackers.

Agreement between Snappfood and “irleaks”?

In a subsequent tweet on January 1, 2024, Snappfood claimed that an agreement had been reached with the hacker group, preventing the sale or leakage of the data online. While the specifics of the agreement remain undisclosed, Snappfood’s claim appears substantial, given that the hacker group had deleted their post from Breach Forums and removed the sample link previously shared on the forum and their Telegram channel at the time of writing.

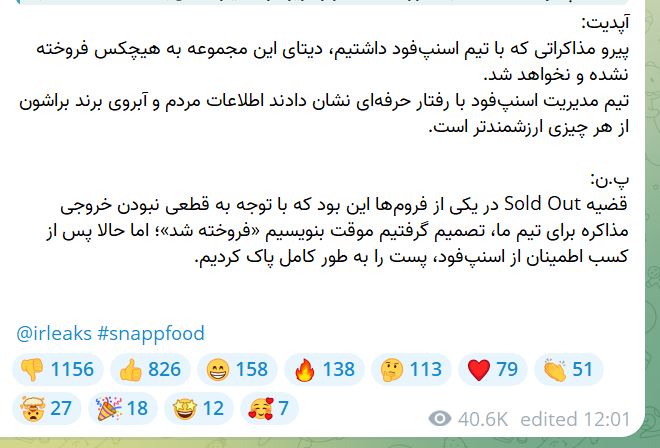
Additionally, a post from the hackers on their Telegram channel confirms the agreement and outlines the next steps for the affected company and customers. The following content has been translated using Google Translate:

The issue of Sold Out in one of the forums was that due to the uncertainty of the negotiation outcome for our team, we decided to temporarily write “sold”; But now after getting confirmation from Snapfood, we deleted the post completely.

Following the negotiations we had with the Snapfood team, the data of this collection has not and will not be sold to anyone. Snapfood’s management team showed that people’s information and brand reputation are more valuable to them than anything else.

irleaks
Iranian Food Delivery Giant Snappfood Cyber Attack: 3TB of Data Stolen
Telegram post by irleaks confirming the agreement – Screenshot credit: Hackread.com

Nevertheless, if both parties adhere to their agreement, it could be deemed a positive outcome for the company and its customers. Hackread.com has reached out to the hackers for a potential interview about the data breach, and this article will be updated accordingly if they respond.

Who is “irleaks”?

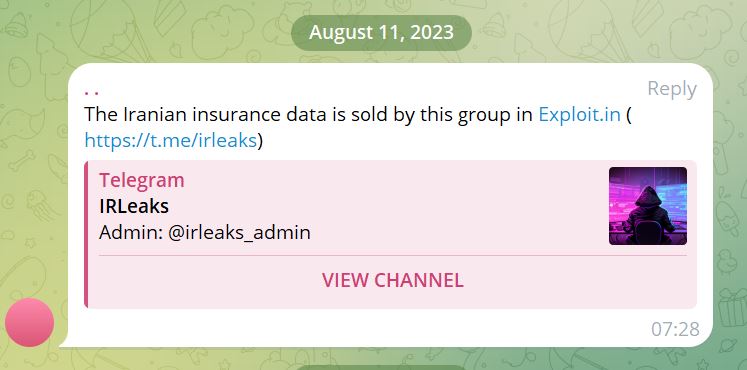
The identity of “irleaks” remains unknown, but the group is known for communicating in the Persian language. This is the same group that, in August 2023, was selling insurance data of Iranian citizens on the well-known private Russian hacker forum Exploit.in.

Iranian Food Delivery Giant Snappfood Cyber Attack: 3TB of Data Stolen
Screenshot credit: Hackread.com

Iran and Cyber Attacks

This incident is not the first instance of a high-profile company like Snappfood falling victim to a data breach. In April 2019, TAP30 (now TAPSI) exposed its database, revealing the personal details of millions of drivers and customers. Additionally, in May 2021, the Raychat app, a popular Iranian social and business messaging platform, was hacked, resulting in the leakage of data from more than 150 million users.

  1. Personal details of 42M Iranians sold on a hacking forum
  2. Disruptions at 70% of Iran’s Gas Stations Blamed on Cyberattack
  3. Anonymous Hits Iranian State Sites, Hacks Over 300 CCTV Cameras
  4. Iran State-Run TV’s Live Transmission Hacked by Edalate Ali Hackers
  5. Iranian State TV Hacked During President’s Speech on Revolution Day

[ad_2]
Source link