Google to settle lawsuit over Chrome incognito mode tracking

0
[ad_1]

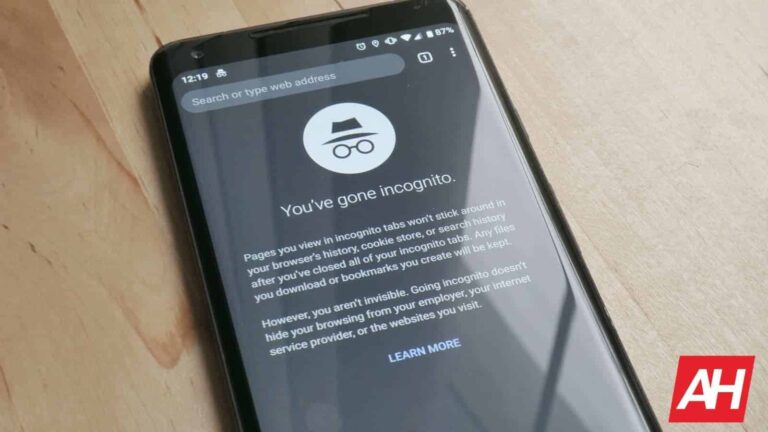
Google has reached a settlement in a lawsuit filed in 2020 over its controversial practice of tracking user activity during Chrome’s incognito mode. Google has apparently designed incognito to allow users to browse and search the internet without saving the browsing history or information entered in forms.

However, many users believe that incognito mode provides complete anonymity from both their Internet Service Provider (ISP) and the websites they visit. The lawsuit sought damages exceeding $5 billion, arguing that Google’s covert data collection from users in incognito mode violated user privacy on a massive scale.

In August 2023, Judge Yvonne Gonzalez Rogers ruled that the case would proceed, citing concerns about Google’s privacy notice and the incognito mode splash screen. The judge questioned whether these communications created a binding promise from Google not to collect user data during private browsing sessions. Additionally, she expressed reservations about Google logging data from users in incognito mode in the same logs as users without incognito mode enabled. Despite Google’s defense that the Chrome browser clearly notifies users about potential data collection when opening a new incognito tab, the case continued.

The terms of the settlement for Chrome’s tracking inside incognito remain undisclosed

Rather than proceeding to a full trial, Google has chosen to settle the lawsuit. While the terms of the settlement remains unrevealed, the agreement is expected to be presented to the court at the end of January, with approval anticipated in February. Google had previously asserted that it would vigorously defend itself against the claims, emphasizing that the Chrome browser explicitly informs users about the possibility of websites collecting information during incognito sessions.

The lawsuit has drawn attention to the perceived discrepancy between user expectations of Google Chrome‘s incognito mode and Google’s data collection practices. In response to the legal scrutiny, Google briefly tested a redesigned incognito page in 2021 but ultimately retained the original design. The settlement reflects Google’s decision to address the legal challenges rather than prolonging the dispute through a trial.


[ad_2]
Source link

OPPO Find X7 flagship series will launch on January 8

0
[ad_1]

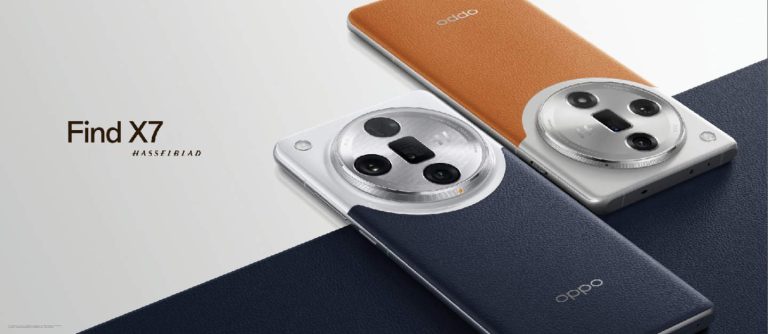
Following the OPPO Find X7 and Find X7 Ultra designs, more info just surfaced. The OPPO Find X7 series will launch on January 8, it has been confirmed by the company. The initial launch event will take place in China, though a global launch is also expected this time around.

As a reminder, the OPPO Find X6 series did not make its way to global markets. The OPPO Find X5 series did, however. We do expect to see the OPPO Find X7 series in markets outside of China, though.

The OPPO Find X7 flagship series will launch on January 8, it’s official

In any case, the OPPO Find X7 series will be announced on January 8, during an event that starts at 2:30 PM (China time). That translates to 8:30 AM CET / 7:30 AM BST / 2:30 AM EST / 11:30 PM PST (January 7).

It seems like one of the recent rumors was accurate, the ‘Pro’ model won’t launch at all. Only the OPPO Find X7 and OPPO Find X7 Ultra got listed on the OPPO Shop, and reservations are already opened for Chinese consumers.

There is always a chance that OPPO will use the ‘Pro’ moniker globally, though, we’ll see. As things stand now, however, the ‘Pro’ model is out of the question. OPPO is sticking with vanilla and ‘Ultra’ monikers.

The designs of these two phones are almost identical

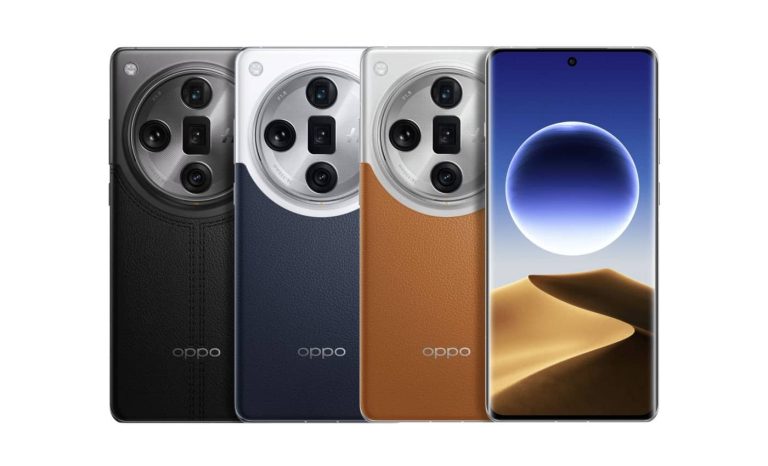
The two smartphones in question look almost the same. The one difference you’ll notice is in the camera island on the back, and only if you really pay attention. The layout in there looks the same, but the bottom cutout on the Find X7 does not include a fourth camera. It does on the OPPO Find X7 Ultra.

Also, the OPPO Find X7 Ultra has two periscope telephoto cameras on the back, unlike the OPPO Find X7. Both smartphones will be available in vegan leather + glass combos, while the vanilla model will also come in glass-only (backplate) variants.

This design is basically an evolution of what the OPPO Find X6 Pro brought to the table. It may not appeal to everyone, but it is unique, and most people seem to like it. That camera oreo is very noticeable, but it can also be useful as an anchor for your index finger, if the OPPO Find X6 Pro and OPPO Find N3 are anything to go by.


[ad_2]
Source link

The top 4 ransomware gang failures of 2023

0
[ad_1]

Ransomware gangs care about one thing: Stealing money.

Over time, their craven, cybercriminal efforts have toppled businesses, destabilized hospitals, and ruined lives. Worst of all, they show no sign of slowing down, and their extortion attempts—which no longer focus on ransomware delivery alone—are getting bolder, meaner, and uglier.

As Allan Liska, intelligence analyst at Recorded Future, recently said on the Lock and Code podcast, times have changed.

“There are no protections anymore,” Liska said. “For a while, some ransomware actors [said] ‘No, we won’t go after hospitals, or we won’t do this, or we won’t do that.’ Those protections all seem to have flown out the window, and they’ll go after anything and anyone that will make them money. It doesn’t matter how small they are or how big they are.”

Considering all this, it’s pretty damn nice to see ransomware gangs lose.

As the holidays put people closer to family and friends (and ransomware gangs closer to attacking—seriously, watch out for that), Malwarebytes Labs is sharing some of the brighter moments of 2023 in which ransomware gangs didn’t get what they wanted. And while some of these “victories” still include an unfortunate ransomware deployment, they all have the same result for the ransomware gangs involved: A lost payday.

Here are four times ransomware gangs failed in 2023.

1. The Royal Mail ransomware attack

On January 11, the Royal Mail service in the United Kingdom publicly announced that it had suffered a “severe service disruption” due to a cyber incident. Until the incident was cleared, customers were asked to not send packages or letters overseas.

Within days of Royal Mail’s announcement, news outlets began linking the alleged cyber incident to the ransomware gang LockBit, which, oddly, denied the attack.

But underneath the public reporting, a fascinating negotiation between the cybercriminal gang and its victim would play out for weeks.

On January 12, a representative for Royal Mail makes contact with a cybercriminal for LockBit on a chat hosted in the dark web. The Royal Mail rep is direct, says they work in IT, and, curiously, has a deft command of flattery, referring to LockBit’s work as “pen-testing.” More impressively, the Royal Mail rep immediately takes control of the conversation by implementing one of the most effective strategies in ransomware negotiations: Stalling for time.

Despite LockBit’s constant pushes for urgency, the Royal Mail rep grinds the conversation to a halt, at one point raising a thus-unheard-of concern with LockBit’s decryption key: Yes, it may work on a few sample files, but will it work on really big files?

“My management have heard that your decryptor might not work on large files,” the Royal Mail rep says, deploying yet another stunning negotiation tactic by trying to invoke a manager to deliver difficult news.

After days of back and forth, the LockBit rep returns to the most important issue—payment. LockBit had asked for an astounding $80 million ransom, and, after enough delay, it is time to talk money.

But again, Royal Mail’s rep turns the tables. Yes, the Royal Mail service could possibly make a payment that large, but there is only one problem, the representative says: We’re not Royal Mail.

Shock. Horror. Utter embarrassment. According to the Royal Mail rep, LockBit had attacked the wrong Royal Mail, instead deploying ransomware for a Royal Mail subsidiary, where a more reasonable starting point in ransomware demands should be about $4 million.

At this point, the LockBit rep accepts defeat.

“You are a very clever negotiator,” the LockBit agent says. “I appreciate your experience in stalling and bamboozling.”

We’ll take that as a win.

2. MGM bounces back 10 days after ransomware siege

In Sin City, the house always wins, even when it loses $100 million.

In the late hours of September 11, customers and hotel guests at the Las Vegas resort MGM Grand noticed something was off—literally. On TikTok, a user shared a video showing rows of digital gambling machines with blank, non-functional screens. On the MGM Grand website, online reservations had become inaccessible. And for some unfortunate guests, even their room keys didn’t work.

“Digital keys weren’t working,” said the same TikTok user who shared video of the hotel’s broken digital slot machines. “Had to get physical keys printed.”

MGM Grand had been hit by a ransomware gang named Scattered Spider, a group of cybercriminals that, it would turn out, had already found some luck on the Las Vegas strip.  

On September 14, Caesar’s Entertainment reported in a filing with the US Securities and Exchange Commission that it, too, had suffered a cyber breach, and according to reporting from CNBC, it received a $30 million ransom demand, which it then negotiated down by about 50 percent.

MGM Grand, however, chose a different path. Across 10 hectic days—which included equipping hotel elevators with handheld, two-way radios in case guests encountered any problems—the MGM Grand became operational once more, all without paying a ransom.  

MGM Resorts International later provided a sober estimation of the cost of the recovery effort, expecting a $100 million loss to its third-quarter results, and valid criticism about the hotelier’s security vulnerabilities remain, but in the land of vice and greed, stopping a ransomware gang is a feat that few have accomplished.

3. Qakbot shot down

Duck hunting season came early this year.

In August, an international investigation led by US law enforcement agencies nearly wiped Qakbot from the internet, shutting down a large part of the botnet’s infrastructure, retrieving $8.6 million in cryptocurrency, and removing the botnet’s associated Qakbot malware from hundreds of thousands of infected machines around the world.

When infected with the Qakbot malware, computers would join the Qakbot “botnet,” an army of devices that could be controlled by a cybercriminal gang and pilfered for login credentials. The infected machines would also be susceptible to additional malware, and in the case of Qakbot-infected computers, that additional malware was often the ransomware variant called Black Basta.

Because of this enormous reach, Black Basta consistently appeared in Malwarebytes’ monthly Ransomware Reviews that record the most active ransomware variants across publicly-recorded attacks.

In April, Black Basta was responsible for at least 40 attacks. In September, just one month after Qakbot’s announced takedown, that number dropped to six.

4. ALPHV tattles on its victim to little success

A new wrinkle about modern ransomware attacks is that some of them don’t involve any ransomware at all.

That’s because, years ago, ransomware gangs learned that their malware of choice wasn’t the sole reason that victims paid ransoms. Rather, the ransomware that was deployed was just a digital representation of a highly effective, criminal lever: Extortion.

Since at least 2020, ransomware gangs have implemented a “double-extortion” technique against victims, stealing an organization’s files and threatening to publish them online before also deploying ransomware to encrypt the original copies left behind. More recently, however, ransomware gangs have resorted to just stealing a victim’s data without detonating any ransomware afterwards. The State of Maine, for instance, likely suffered such an attack this year in a data breach that impacted 1.3 million people.

But in November, the ransomware gang ALPHV, also known as BlackCat, tried something different.

Earlier in the month, ALPHV attacked the company MeridianLink. After a few days, MeridianLink showed no sign of paying the ransom, so ALPHV upped the pressure by reporting MeridianLink to, of all places, the US Securities and Exchange Commission (SEC).

To hear ALPHV tell it, MeridianLink was required to report ALPHV’s attack to the SEC because of newly-announced rules from the federal agency that mandate the reporting of any “material cybersecurity incident” within four days.

“It has come to our attention that MeridianLink, in light of a significant breach compromising customer data and operational information, has failed to file the requisite disclosure under Item 1.05 of Form 8-K within the stipulated four business days, as mandated by the new SEC rules,” ALPHV allegedly wrote in their complaint to the SEC.

MeridianLink, however, was unimpressed. After confirming “a” cybersecurity incident, a spokesperson with the company downplayed its severity.

“Based on our investigation to date, we have identified no evidence of unauthorized access to our production platforms, and the incident has caused minimal business interruption,” the MeridianLink spokesperson said. Further, the rules cited by ALPHV were not even in effect, yet, so noncompliance would be impossible.

To date, MeridianLink has not reportedly paid the ransom. More importantly, ALPHV may have learned something the rest of the world already knows: Criminal tactics only gain sympathy within criminal enterprises. Next time, complain to your coworkers, not the federal government.  

How to avoid ransomware

  • Block common forms of entry. Create a plan for patching vulnerabilities in internet-facing systems quickly; and disable or harden remote access like RDP and VPNs.
  • Prevent intrusions. Stop threats early before they can even infiltrate or infect your endpoints. Use endpoint security software that can prevent exploits and malware used to deliver ransomware.
  • Detect intrusions. Make it harder for intruders to operate inside your organization by segmenting networks and assigning access rights prudently. Use EDR or MDR to detect unusual activity before an attack occurs.
  • Stop malicious encryption. Deploy Endpoint Detection and Response software like ThreatDown EDR that uses multiple different detection techniques to identify ransomware, and ransomware rollback to restore damaged system files.
  • Create offsite, offline backups. Keep backups offsite and offline, beyond the reach of attackers. Test them regularly to make sure you can restore essential business functions swiftly.
  • Don’t get attacked twice. Once you’ve isolated the outbreak and stopped the first attack, you must remove every trace of the attackers, their malware, their tools, and their methods of entry, to avoid being attacked again.
[ad_2]
Source link

OPPO Find X7 & Find X7 Ultra designs shown from all angles, in all colors

0
[ad_1]

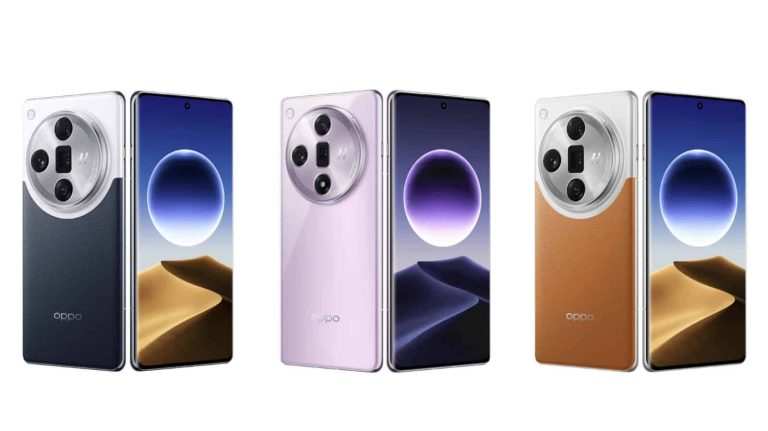
The OPPO Find X7 series is right around the corner, and the designs of the devices have just been shown, in detail. The OPPO Find X7 and Find X7 Ultra designs have been shared. These renders are showing the devices from all angles, in all colors.

The OPPO Find X7 & Find X7 Ultra designs have been shown… in all colors

The two phones seem to look the same, at first. If you take a closer look, however, you’ll notice that the OPPO Find X7 Ultra has an extra camera on the back. The bottom cutout on the OPPO Find X7 Ultra includes a fourth camera. You can see that in the renders below the article.

The OPPO Find X7, on the other hand, does not have a camera in that bottom slot. The OPPO Find X7 Ultra will include two periscope telephoto cameras on the back, actually. OPPO is once again going for a quad 50-megapixel setup on the back.

The leaked octagon camera island is nowhere to be found… which is a good thing

In terms of the overall design, it looks much better than initially reported. The octagon camera island that leaked several times won’t be a part of the picture, at all. The OPPO Find X7 series will have a huge camera oreo on the back, as did the OPPO Find X6 Pro, OPPO Find N3, and so on.

Four cutouts are included inside that camera oreo, but only the ‘Ultra’ model has four cameras. The Hasselblad logo is also visible in there. That camera oreo does protrude on the back, but it can be a nice anchor for your finger when you’re holding the phone.

Both the front and the back sides of these two phones will be curved. OPPO is mostly going for a combo of glass and vegan leather on the back here, on both units. The OPPO Find X7 will have an all-glass model too, though.

The OPPO Find X7 Pro seems to be out of the question after all

The images you can see in the galleries below are possibly all the models that we’ll get. It’s interesting that the OPPO Find X7 Pro is not here. It’s possible that OPPO simply replaced the ‘Pro’ moniker with the ‘Ultra’ moniker.

The OPPO Find X7 will come in two vegan leather + glass, and two glass-only variants. The silver + black and silver + brown color combos will be available for the vegan leather + glass models. Black and purple variants will be available for the glass-only OPPO Find X7.

The OPPO Find X7 Ultra, on the other hand, will also have silver + black and silver + brown vegan leather + glass models. The third model will be all black, but it’ll also combine glass and vegan leather on the back.

Another thing to note is that the silver color does look like white in the provided renders. OPPO will use an interesting glass backplate for that silver color, that can reflect light in different ways, it seems.

You can check out all the combos in the two galleries below.

OPPO Find X7:

OPPO Find X7 Ultra:


[ad_2]
Source link

Soon you can watch YouTube TV content on your Peloton bike

0
[ad_1]

Peloton is getting into the TV market, sort of, thanks to its new partnership with YouTube to show YouTube TV content to Peloton bike owners. On December 26, the company put out an announcement that YouTube TV will be an official content partner. This means that soon enough, you’ll be able to enjoy all of your favorite live TV content while you get your exercise on. Sure, this would be no different than if you have an actual TV in the same room as your Peloton equipment. But that won’t be necessary anymore since the content will play right on the Peloton screen.

This isn’t Peloton’s first partnership for entertainment content. As noted by Connect The Watts, Peloton reached an agreement in November to offer viewing of NBA and WNBA content via NBA League Pass. The YouTube TV partnership is by all accounts a much bigger offering for the user. Since it’s not just basketball games you’ll be able to stream. There are of course a few caveats to viewing the content.

Viewing YouTube TV content will require a Peloton All Access membership

If you want to watch content from YouTube TV, you’ll need to be a Peloton App+ member which gives you full access to everything Peloton offers. This membership is $24 a month and won’t include the cost of YouTube TV. So you’ll need to factor in the costs of both if you’re going to be a new member. If you already subscribe to both then you’ll now just be able to enjoy the two together.

Content will be viewable on all Peloton Bikes, Treadmills, and Rowers. In terms of what you can watch, you’ll be able to watch live TV from over 100 channels like ABC, CBS, FOX, NBC, and many more. Giving you more to enjoy while you work out. Peloton has always offered a plethora of exercise classes and content from workout coaches to help with motivation. But now you can watch basically whatever you want.

“We are empowering our Members to lean into what they love, like catching up on their favorite show or rooting for their home team, to help inspire them on their fitness journey,” said Peloton Senior VP of Music & Content Gwen Bethel Riley.


[ad_2]
Source link

Google Messages will let you change chat bubble colors, but only on RCS

0
[ad_1]

Google (and the rest of the world, for that matter) got tired of waiting for Apple to “get the message” and adopt RCS messaging. Android phones use RCS messaging, and it allows Google Messages to do some pretty awesome things. Well, Google Messages will let you change the color of the bubble in conversations, but this is only if you’re on RCS.

If you don’t know what RCS messaging is, it’s a new standard for messaging that succeeds SMS. With it, you’re able to send larger files, use chat reactions, enjoy end-to-end encryption, and do all sorts of cool things. These are features that you’d get with online services like WhatsApp or Telegram, but RCS is handled through your carrier just like SMS. It’s much better and more secure than the old standard. If you’re currently using an Android phone and messaging another Android user, you’re already using RCS messaging.

You can change the color of chat bubbles in Google Messages, but only with RCS

Google recently announced some new features coming to Google Messages, and they’ve been making it a better platform to use. One of the features announced was the ability to change the color of your chat bubbles on a per-conversation basis. So, you can have one theme for a conversation with your mother and one for a conversation with your spouse. It’s a fun new addition to the app, and it will make it more customizable. This feature is currently rolling out to users, so there’s a chance that you won’t see it just yet.

If you’re in a conversation, you’ll need to tap on the three-dot menu at the top right of the UI. There, you’ll see the option to change the color of the bubbles. There are nine options for colors that you can choose. Also, if you want to have it set to the system default, it can match the colors of your system theme.

If you want to use this feature, you’ll need to be texting a person who’s using RCS. This basically excludes all iPhone users for the time being. iPhone users will gain RCS sometime next year. In the meantime, you’ll only be able to change the colors for conversations you’re having with other Android users.


[ad_2]
Source link

The US may impose regulations on some Chinese DRAM makers

0
[ad_1]

The US is set to broaden its regulations to include Chinese-made general-purpose semiconductors. It is a move that could prove advantageous for South Korean memory semiconductor giants like Samsung Electronics and SK hynix. The focus of the regulations is on NAND flash and DRAM, where the technological gap with China is less significant.

The Bureau of Industry and Security (BIS) under the US Department of Commerce is planning to survey more than 100 companies across sectors. It includes automotive industries, aerospace, and defense and will start in January next year. The goal is to assess the dependence of US companies on Chinese-made general-purpose semiconductors.

Following the survey, the Department of Commerce is likely to consider imposing tariffs on these Chinese semiconductors, with potential measures to ban US defense companies from importing them. Significant in context, Apple has already canceled its deals with YMTC amid the US ban.

The US regulations are particularly aimed at companies like YMTC for NAND, CXMT for DRAM, and SMIC as a foundry

The regulations from the US Commerce Department may cast a shadow over China’s DRAM and NAND export front. US companies may reduce their reliance on Chinese semiconductors to mitigate the uncertainty of additional regulations. The regulations are aimed particularly at companies like YMTC for NAND, CXMT for DRAM, and SMIC as a foundry.

The anticipated outcome is a shift in US procurement towards South Korean products as an alternative to Chinese ones. Samsung Electronics and SK hynix, with semiconductor factories in China, may be designated as exceptions to export controls. Because it will be necessary to maintain the semiconductor supply chain.

This development is also seen as a positive turn of events for NAND businesses in the US, which have struggled amid the continuing downturn in IT demand. The NAND market, encompassing solid-state drives and other data storage devices, is fiercely competitive. There is very little technological disparity between companies leading to an oversupply.

With the potential reduction in supply from Chinese competitors due to regulatory challenges, Samsung Electronics and SK hynix are expected to increase their supply, deplete their inventory more rapidly, and witness a turnaround in their NAND business from the second half of the next year.


[ad_2]
Source link

Exploring Imgly SDK Alternatives for Ultimate Flexibility

0
[ad_1]

Imgly SDK has been a popular choice for developers seeking reliable image processing and manipulation solutions. However, in the dynamic software development environment, exploring alternatives can provide developers with greater flexibility and adaptability to varying project requirements.

In this article, we will delve into IMG.LY alternative SDKs that offer a range of features, allowing developers to choose the one that aligns best with their specific needs.

1. OpenCV (Open Source Computer Vision Library)

Overview:

OpenCV is an open-source computer vision and machine learning library widely used in the field of image processing. It provides a comprehensive set of tools and algorithms for image and video analysis, making it a versatile choice for developers.

Key Features:

  • Image processing and manipulation.
  • Object detection and recognition.
  • Facial recognition.
  • Machine learning support.

Why Choose OpenCV:

OpenCV‘s extensive community support, cross-platform compatibility, and wide range of features make it a powerful alternative for developers looking for flexibility and customization in image processing.

2. ImageMagick

Overview:

ImageMagick is a free open-source software suite for displaying, converting, and editing raster image files. It includes a command-line tool as well as a variety of libraries for different programming languages, making it adaptable to various development environments.

Key Features:

  • Image conversion and format support.
  • Image editing and manipulation.
  • Batch processing.
  • Command-line interface.

Why Choose ImageMagick:

ImageMagick’s versatility, support for a multitude of image formats, and command-line interface make it a strong contender for developers seeking a flexible image-processing solution.

3. Pillow (PIL Fork)

Overview:

Pillow, a fork of the Python Imaging Library (PIL), is a Python Imaging Library that adds image processing capabilities to Python interpreters. It is a user-friendly alternative for developers working with Python applications.

Key Features:

  • Image manipulation and processing.
  • Support for various image formats.
  • Basic image editing operations.
  • Easy integration with Python applications.

Why Choose Pillow:

Pillow is an excellent choice for Python developers due to its simplicity, ease of use, and seamless integration with Python applications.

4. Sharp (for Node.js)

Overview:

Sharp is a high-performance image processing library for Node.js applications. It is designed to be fast and efficient, making it suitable for handling image processing tasks in server-side applications.

Key Features:

  • Image resizing and manipulation.
  • Efficient memory handling.
  • Support for many image formats.
  • Advanced image processing operations.

Why Choose Sharp:

Developers working with Node.js can benefit from Sharp’s speed and efficiency, making it a go-to choice for server-side image processing tasks.

5. GD (Graphics Draw)

Overview:

GD, or Graphics Draw, is an open-source library for dynamic image creation. It supports various programming languages, including PHP, and is commonly used for tasks such as creating thumbnails, processing images, and generating dynamic charts.

Key Features:

  • Image creation and manipulation.
  • Dynamic image generation.
  • Basic drawing functions.
  • Support for multiple programming languages.

Why Choose GD:

GD is a suitable choice for web developers, especially those working with PHP, as it provides a simple and efficient solution for dynamic image generation and manipulation.

Conclusion

While Imgly SDK has been a popular choice, exploring alternative image processing libraries can offer developers ultimate flexibility based on their project requirements, programming language preferences, and specific functionalities needed.

Each of the alternatives mentioned—OpenCV, ImageMagick, Pillow, Sharp, and GD—comes with its strengths and can be tailored to meet the diverse needs of image processing tasks.

By evaluating the features, ease of integration, and community support of each alternative, developers can make an informed decision that aligns with the goals of their projects.

  1. 5 Best Video Editing SDKs for iOS
  2. Kotlin app development company – How to choose
  3. A Guide to Crafting a Dynamic App Using Weather APIs
  4. Run Android Applications on PC via Android SDK Manager
  5. The Role of DevOps in Streamlining Cloud Migration Processes
  6. Top Benefits of Using Flutter for Cross-Platform App Development

[ad_2]
Source link

OPPO Find X7 to impress gamers with 120 fps support

0
[ad_1]

The OPPO Find X7 series could impress gamers when it launches next year. According to a new report, the company’s new handsets will offer 120 fps (frames per second) support for games.

The OPPO Find X7 series could impress gamers with 120 fps support

This particular report mentions the ‘Honor of Kings’ game only. It lists devices that will offer such support, and OPPO’s new handsets are mentioned. Considering that 120 fps gaming will be enabled in that game means that the devices will support it, which also means other games can enable such support too.

This will, of course, vary from one game to the next. Devs will need to enable such support on their end, for the phone to be able to take advantage. So don’t expect every game to offer it, not at all.

Now, the OPPO Find X7 series is expected to launch next month, at least in China. The global launch is expected this time around too, unlike last year. That will occur at some point in Q1, we’re not sure.

Three devices are coming next month

OPPO is planning to announce three smartphones as part of this series, it seems. Those devices are the OPPO Find X7, OPPO Find X7 Pro, and the OPPO Find X7 Ultra. Some rumors claimed that the ‘Pro’ model may not launch at all. Others said that we’ll get two ‘Ultra’ models, and so on.

Chances are we’ll get three models, as mentioned above. Based on the rumors, the only difference between the ‘Pro’ and ‘Ultra’ models will be in satellite connectivity. The ‘Ultra’ will offer support for that. That feature may be limited to China, though.

The OPPO Find X7 series will be quite powerful, especially the ‘Pro’ and ‘Ultra’ models. The Snapdragon 8 Gen 3 will fuel those two smartphones, while the all-new Sony LYT-900 camera sensor will be used on the back.

The OPPO Find X7 will be fueled by the Dimensity 9300. All devices will feature a 120Hz display, top-of-the-line RAM and flash storage, and so on.


[ad_2]
Source link