Samsung has ramped up its preparations for the Galaxy S24 launch later this month. It has started putting up marketing banners for the new flagships in its retail stores. As expected, “Galaxy AI” is front and center of the company’s marketing efforts, a leaked banner reveals.
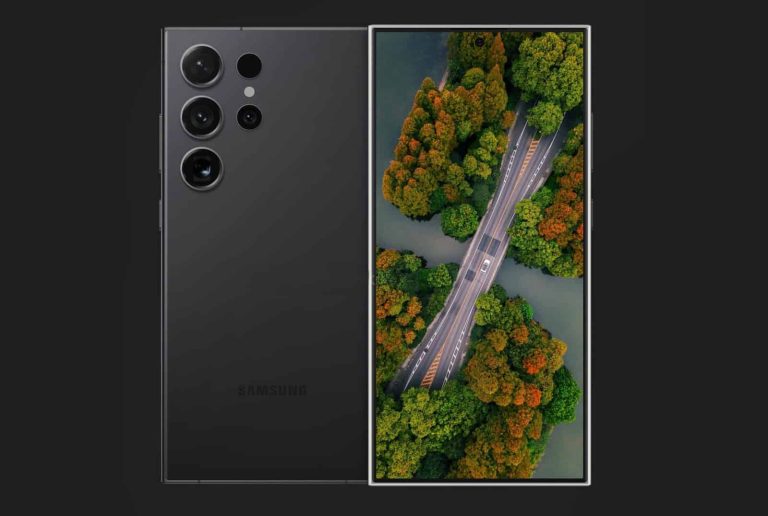
Galaxy S24 Ultra spotted on a marketing banner inside a Samsung store
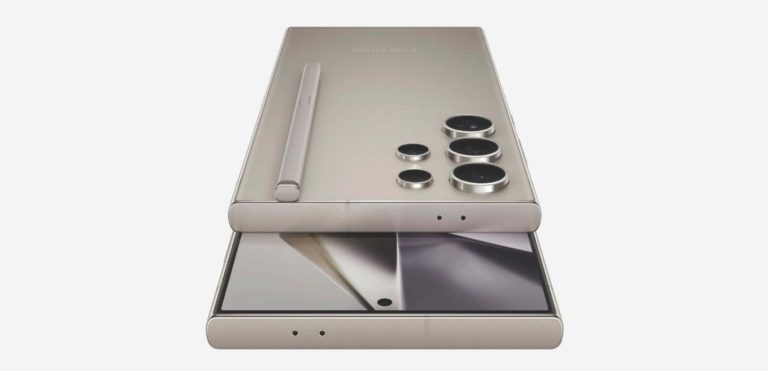
X user @DontMatterToYou recently posted a photo allegedly captured inside a Samsung store in Brazil. It shows the Galaxy S24 Ultra on a banner on the front side of a sales kiosk. The banner contains a rendering of the phone with its rear camera array and the S Pen. “Com O Poder do Galaxy IA,” the text above the image says. For those of you who are not fluent in Portuguese, it translates to “with the power of Galaxy AI.”
The image seen in the banner was also found online by X user @theonecid. It gives us a closer look at the Galaxy S24 Ultra’s top edge and the camera setup. We can see that the frame is completely flat on the top and so is the display. There are five camera rings on the back of the device, all protruding out of the rear panel separately. We are seeing a 200MP main camera, a 50MP 5x zoom camera, a 10M 3x zoom camera, and a 12MP ultrawide lens.
The fifth ring on the back of the Galaxy S24 Ultra isn’t a camera but the laser autofocus sensor. The selfie camera on this phone should be a 10MP unit. Samsung will use AI to improve the image quality with proper optimization according to shooting conditions. The new flagships will also boast AI-powered photo and video editing tools, including the ability to move or remove objects from photos and videos.
Beyond photography, AI will also enhance the Galaxy user experience in several other ways. The Galaxy S24 series will feature a new tool that can translate calls as you speak. Not only the phones can translate the incoming audio to the desired language but also translate your response to the language that the other party is speaking in, all on-device and in real-time. You can get live transcriptions too.
Samsung wants to make the best AI phones
Samsung aims to make the Galaxy S24, Galaxy S24+, and Galaxy S24 Ultra the best AI phones yet. Based on the model and region, the devices will ship with the Snapdragon 8 Gen 3 or the Exynos 2400 chipset, both of which offer unprecedented on-device AI capabilities. It remains to be seen whether Samsung’s bet on AI pays off and helps improve its flagship sales. The devices arrive on January 17.
Fortunately for Radioactive Waste Management (RWM), the first-of-its-kind hacker attack on the project was unsuccessful.
The United Kingdom’s Radioactive Waste Management (RWM) company overseeing the nation’s radioactive waste has revealed a recent cyberattack attempt through LinkedIn. While the attack was reportedly unsuccessful, it has raised eyebrows in the nuclear sector, sparking concerns about the security of critical nuclear infrastructure.
As reported by The Guardian, the hackers directed their attack at the company through LinkedIn. However, whether it was a phishing attack or an attempt to trick employees into installing malware on the system, the modus operandi remains unknown.
Typically, LinkedIn is exploited for phishing scams targeting employees of specific companies. An example from last year involves ESET researchers reporting a cyberespionage campaign by North Korean government-backed hackers from the Lazarus group. The campaign specifically targeted employees at a Spanish aerospace firm.
The RWM is spearheading the £50bn Geological Disposal Facility (GDF) project, aimed at constructing a substantial underground nuclear waste repository in Britain. As a government-owned entity, RWM facilitated the merger of three nuclear bodies—the GDF project, the Low-Level Waste Repository, and another waste management entity—to establish Nuclear Waste Services (NWS).
“NWS has seen, like many other UK businesses, that LinkedIn has been used as a source to identify the people who work within our business. These attempts were detected and denied through our multi-layered defences,” stated an NWS spokesperson.
However, the incident raises concerns, as experts warn that social media platforms such as LinkedIn are becoming preferred playgrounds for hackers. These platforms provide multiple avenues for infiltration, including the creation of fake accounts, phishing messages, and direct credential theft.
The FBI’s special agent in charge of the San Francisco and Sacramento field offices, Sean Ragan, has emphasized the ‘significant threat’ of fraudsters exploiting LinkedIn to lure users into cryptocurrency investment schemes, citing numerous potential victims and past and current cases.
In October 2023, email security firm Cofense discovered a phishing campaign abusing Smart Links, part of the LinkedIn Sales Navigator and Enterprise service, to send authentic-looking emails, steal payment data, and bypass email protection mechanisms.
In November 2023, a LinkedIn database containing over 35 million users’ personal information was leaked by a hacker named USDoD, who previously breached the FBI’s InfraGard platform. The database was obtained through web scraping, an automated process to extract data from websites.
Social engineering attacks, such as deceptive emails and malicious links, offer hackers a gateway to sensitive information. LinkedIn has taken steps to warn users about potential scams and provide resources for staying safe online. Still, concerns about digital security remain prevalent in the nuclear industry, especially after the Guardian exposé of cybersecurity vulnerabilities at the Sellafield plant.
In 2023, the Sellafield nuclear site in Cumbria experienced cybersecurity issues, indicating a need for improved safeguards and tighter regulations. The RWM incident highlights the growing interest of cybercrime syndicates to target nuclear sites.
The NWS acknowledges the need for continuous improvement to strengthen cybersecurity measures, highlighting that emergency response plans must match evolving business needs.
This information comes from a Chinese tipster ‘Smart Pikachu’, that’s a result of machine translation. Either way, the information has been shared via Weibo.
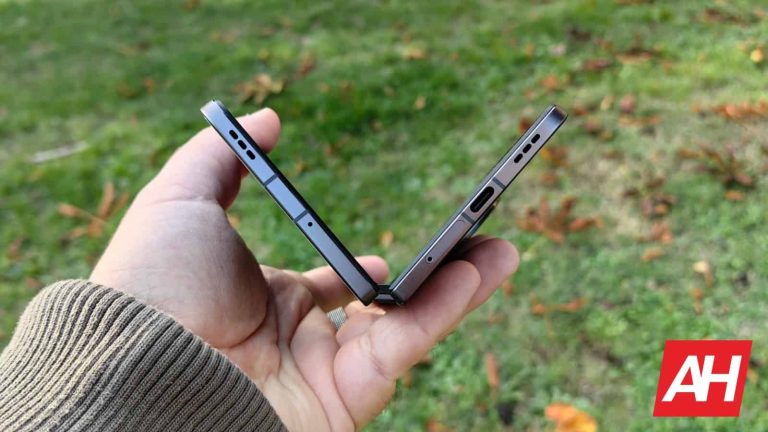
The very first foldable smartphone from Meizu could launch in H1 2024
Based on this report, Meizu is working on such a device. Nothing has been confirmed just yet, but the phone is seemingly expected to arrive in the first half of the year. The tipster did not confirm that, but that’s expected to happen.
Some of you may recall that the device was expected to arrive last year. Well, it seems like Meizu stumbled upon some issues. We don’t have all the details, but it seems like the foldable screen is the main culprit.
This smartphone is expected to be a book-style foldable, and have a main display of approximately 8 inches in diagonal. Based on that info, the phone will likely be squarish when unfolded.
The Meizu 21 Pro is also coming
The company is also working on the Meizu 21 Pro, says the tipster. That is a more powerful variant of the Meizu 21 that already launched in China. The phone is expected to be fueled by the Snapdragon 8 Gen 3 SoC.
The Meizu 21 Pro is also expected to include a QHD+ display, a larger battery, and 80W wired charging. 50W wireless charging is also rumored. That device is expected to launch by the end of January.
In regards to the company’s first foldable smartphone, we still don’t have any spec details. Chances are it will be quite powerful. We don’t believe Meizu will try to aim at a budget foldable or anything of the sort.
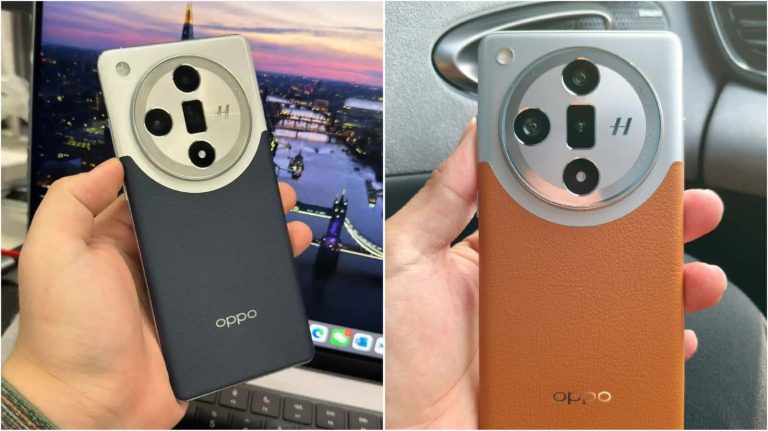
The OPPO Find X7 series phones are hardly a secret at this point. We know what the two phones will look like, as we’re waiting for the launch event on January 8. Having said that, the OPPO Find X7 and Find X7 Ultra have just surfaced in real-life images, and also several video clips.
The OPPO Find X7 series appeared in real-life images and video
That being said, if you check out the gallery below, you’ll see real-life images of both phones. The two devices are shown in basically all color options that will be available. They will look almost the same. You can spot the difference by taking a closer look at their cameras. The OPPO Find X7 Ultra will have two telephoto cameras, while the Find X7 will not. So, those are four cameras vs three cameras.
The OPPO Find X7 Ultra will be available in variants with a vegan leather backplate. Well, that material will cover most of the back, but the upper portion will be glass. The OPPO Find X7 will also utilize that design, but there will also be all-glass models available. Those are also shown above (purple and black).
Truth be said, the OPPO Find X7 series looks even better in these real-life images than it did in renders, at least to our eyes. This two-tone finish definitely stands out. Some people may still dislike the camera island, though.
The OPPO Find X7 Ultra won’t have a glass-only variant, it seems
The OPPO Find X7 Ultra will come in black, brown, and dark blue colors, all vegan leather models. On the flip side, the OPPO Find X7 will be available in black (glass), brown (leather), dark blue (leather), and purple (glass).
The OPPO Find X7 is expected to ship with the MediaTek Dimensity 9300 SoC. The OPPO Find X7 Ultra, on the other hand, will be fueled by the Snapdragon 8 Gen 3 processor. The ‘Pro’ model doesn’t seem to be coming. We’re hoping that the OPPO Find X7 series will launch globally, unlike the Find X6 series.
Samsung can’t seem to get hold of Galaxy S24 leaks. Ahead of the rumored debut on January 17, leaks have revealed almost everything we need to know about the devices. There aren’t many hardware upgrades to look forward to but the flagship trio may bring tons of new software features with artificial intelligence (AI) all over them. A fresh leak has uncovered two new features, including a generative AI photo editing tool.
The Samsung Galaxy S24 will feature an AI Photo Editor
X user @MysteryLupin recently shared a photo of what appears to be a slide from an official marketing material for the Galaxy S24 series. It details new features and other highlights of the upcoming flagship lineup. Among those is a feature called Generative Edit. The document explains that the tool uses AI to move or remove objects from an image. AI will generate relevant details based on the surrounding objects to fill the space.
This isn’t the first time we have heard about this feature. Previous leaks also revealed that you can move objects from one photo to another. You can also expand images and remove objects from videos. However, we now have confirmation that the tool doesn’t work offline. It requires an internet connection and a Samsung account. So, it is a cloud-based solution that Samsung has integrated into the Galaxy S24.
From what we know so far, Generative Edit is the company’s answer to Google’s Magic Eraser tool for Pixels. However, this is just one of the many new AI features that Samsung will introduce with the Galaxy S24. The Live Translate feature for calls is one of those. It uses AI to give you translations and transcriptions of audio calls in real-time. Your voice or text response is also translated back to the original language.
Samsung announced this feature while unveiling its generative AI model, Samsung Gauss. A recent report revealed that the feature will work even when speaking with someone using a non-Galaxy device. The Galaxy S24, Galaxy S24+, and Galaxy S24 Ultra will also bring enhancements to low-light zoom photos and videos, likely with the help of AI. Improvements for high-resolution photos (200MP and 50MP) are on the cards too.
The new flagships debut in two weeks
As of this writing, Samsung hasn’t officially announced a launch date for the Galaxy S24 series. However, as said earlier, leaks have revealed that the big unveiling will take place on January 17 in San Jose, USA. The Korean behemoth is expected to start sending out media invites for the Galaxy Unpacked event in the coming days. The phones may go on sale at the end of this month.
There’s a new Telegram update that was released on the last day of 2023, so act fast and install it, as it brings a plethora of new features.
Long story short, there are improved calls with a colorful new design that uses less of your phone’s battery, a new vaporize effect when you delete messages, the largest bot update in Telegram’s history – and more. Let’s check them out one at a time:
Upgraded calls In this update, Telegram has “totally redesigned calls”, adding new animations and shiny backgrounds that change dynamically based on the call’s status: ringing, active or ended. “The new interface requires fewer resources than before, which means it saves battery life and works better on older devices”, claims the Telegram team.
“We’ve also fixed hundreds of bugs and interface glitches – and added some improvements to call quality. More improvements to connection and audio quality are coming in 2024”. Okay, notes taken!
Thanos Snap Effect when deleting messages Remember Thanos and the way he vaporized things? Turns out, he’s now part of Telegram… “Last month we added an experimental vaporize animation on iOS for auto-deleted messages. This impressive (and energy-efficient) animation is now available on both iOS and Android and plays whenever you delete any message”.
Epic Bot update: Reactions and more “We’re closing this year with the largest update to the Bot Platform in Telegram’s history. Among dozens of new features, bots can now react to messages and manage reactions, quotes, and links, send replies to other chats or topics, and much more”, says the Telegram team and adds that bots can also get information about giveaways and boosts in channels where they are admins.
Cyber attacks are evolving rapidly with advancements in technology, as threat actors exploit new vulnerabilities in:-
The rise of the following sophisticated techniques demonstrates a growing level of complexity:-
Ransomware
AI-driven attacks
Supply chain compromises
Moreover, the expansion of Internet of Things (IoT) devices provides new attack surfaces to the threat actors.
Since threat actors are continuously adapting, that’s why the researchers recommend that organizations prioritize cybersecurity measures to mitigate evolving cyber threats.
Here below we have mentioned all the top 10 countries of origin for cyber attacks:-
China: 18.83%
United States: 17.05%
Brazil: 5.63%
India: 5.33%
Germany: 5.10%
Vietnam: 4.23%
Thailand: 2.51%
Russia: 2.46%
Indonesia: 2.41%
Netherlands: 2.20%
Most Common Types of Cyber Attacks in 2023
Here below we have mentioned all the common types of cyber attacks that occurred in 2023:-
Malware
Phishing
Denial-of-Service (DoS) Attacks
Code Injection Attacks
IoT-Based Attacks
Identity-Based Attacks
Supply Chain Attacks
Spoofing
Insider Threats
DNS Tunneling
Now let’s discuss the common types of cyber attacks in 2023:-
Malware
Malware
Malware refers to malicious software designed to harm or exploit computer systems, services, and networks, aiming for data extraction by cybercriminals for financial gain.
It targets various sensitive information like:-
Finances
Healthcare records
Emails
Passwords
Personal identification numbers
Banking details
Credit card numbers
Debit card numbers
Besides this, the malware also targets government and corporate sites as well for the following two key purposes:-
Data theft
Operational disruption
Here below, we have mentioned all the types of malware:-
Viruses
Ransomware
Scareware
Worms
Spyware
Trojans
Adware
Fileless malware
Phishing
Phishing
Phishing attacks trick victims for the attacker’s benefit, and it’s been performed mainly via emails, ranging from simple to complex and not only that even Phishing attacks are:-
Extremely low-cost
Effective
Attackers mimic trusted sources, using bait-like messages to trick victims. Besides this, Phishing attacks lead to:-
Malware
Identity theft
Data loss
Targeting personal information
Targeting business information
Threat actors exploit phishing to access accounts, compromise systems, and initiate major data breaches as well. Phishing often backs harmful actions like on-path and cross-site scripting attacks, usually via email or instant message.
Denial-of-Service (DoS) Attacks
Denial-of-Service (DoS) Attacks
Denial-of-service (DoS) attacks disrupt a device’s normal function to make it unavailable. This happens by flooding it with multiple requests, which causes the denial of service to users.
If the attack comes from various sources like a botnet, then it’s called a DDoS (Distributed denial-of-service) attack. In short, the DoS attacks overload a machine to deny additional requests.
DoS attacks typically fall into 2 categories, and here below, we have mentioned them:-
Buffer overflow attacks
Flood attacks
DoS uses one connection, and DDoS deploys multiple sources, often a botnet; however, the attacks share similarities, as the threat actors use one or many sources of malicious traffic.
Code Injection Attacks
Code Injection Attacks
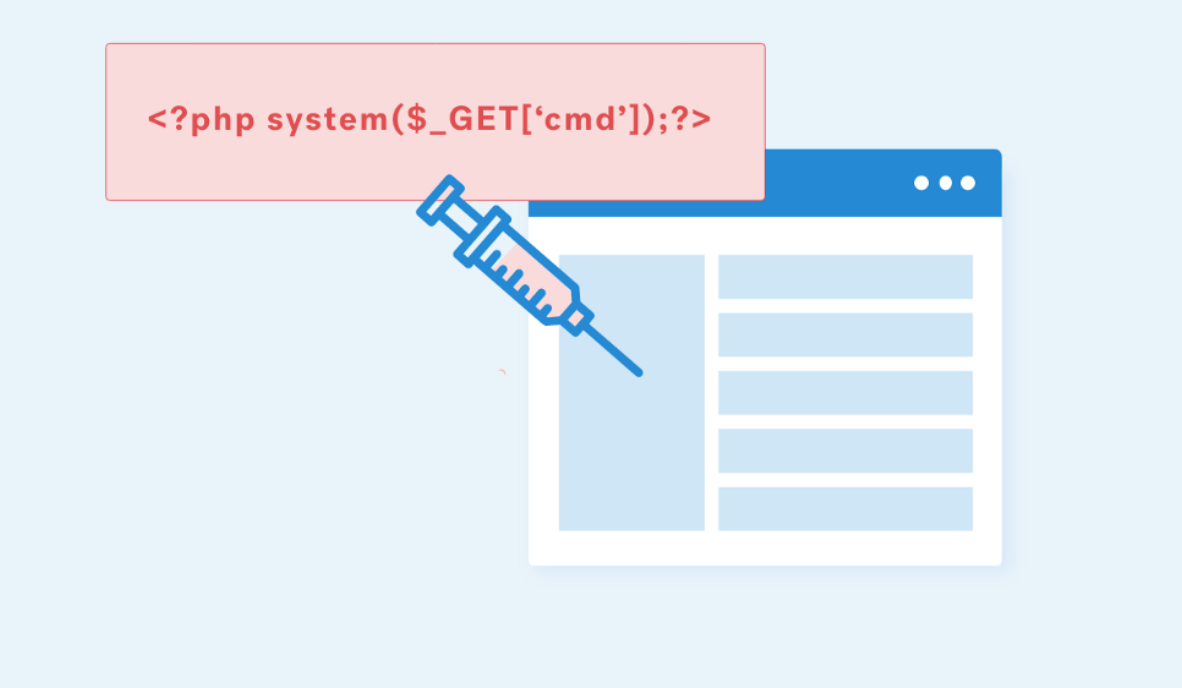
Code Injection involves injecting code into an application, and with the help of this attack, threat actors exploit the poor handling of untrusted data.
Besides this, the lack of proper input/output validation often makes these attacks possible.
Code Injection is unrestricted by injected language functionality, like PHP. In contrast, Command Injection uses existing code to execute commands, often in a shell context.
Vulnerabilities vary in discoverability and exploitation difficulty. While the successful exploits may lead to:-
Confidentiality loss
Integrity loss
Availability loss
Accountability loss
Code Injection involves injecting code into an application, and with the help of this attack, threat actors exploit the poor handling of untrusted data.
Besides this, the lack of proper input/output validation often makes these attacks possible.
Code Injection is unrestricted by injected language functionality, like PHP. In contrast, Command Injection uses existing code to execute commands, often in a shell context.
Vulnerabilities vary in discoverability and exploitation difficulty. While the successful exploits may lead to:-
Confidentiality loss
Integrity loss
Availability loss
Accountability loss
Injection flaws are often found in:-
SQL
LDAP
Xpath
NoSQL queries
OS commands
XML parsers
SMTP headers
Program arguments
IoT-Based Attacks
IoT-Based Attacks
Advancements in the technological world enabled wireless connectivity for several types of smart devices:-
While the Internet of Things (IoT) automates these devices, equipped with sensors to collect and relay data for:-
With the growing use and adaptability of IoT, cyber-attacks are actively targeted on connected devices. Though IoT devices enhance daily tasks but bring cybersecurity risks, especially for less-secured gadgets like-
Here below, we have mentioned all the common reasons why hackers target IoT devices:-
Weak passwords
Unsecured cloud storage
Unpatched software
Insecure network connections
Lack of encryption
Physical tampering
That’s for the secure operation of your IoT devices, it’s always recommended to stay vigilant and take all the necessary security measures.
Identity-Based Attacks
Identity-Based Attacks
Nowadays, organizations face frequent cyber threats like Identify-based attacks, which are evolving rapidly and becoming:-
These types of attacks are targeted by hackers who are actively looking for personal and sensitive data.
In telecom and beyond, Identity-Based Attacks are rising threats with significant consequences. Organizations must defend against various attacks like:-
Credential stuffing
Password spraying
Phishing
While regular password changes and the implementation of multi-factor authentication (MFA) will surely help to prevent these threats effectively.
In total, there are five types of Identity-Based attacks, and here below we have mentioned them:-
Credential Stuffing
Golden Ticket Attack
Kerberoasting
Man-in-the-Middle MITM Attack
Silver Ticket Attack
Supply Chain Attacks
Supply Chain Attacks
Supply chain attack targets an organization’s weak links, exploiting trust in third-party vendors. It’s an island-hopping attack relevant across industries.
While this attack rising due to new tactics, it tampers with manufacturing processes to cause disruptions by exploiting the flaws in:-
These types of attacks are hard to detect, as they spread through trusted software, affecting organizations with many customers.
A supply chain attack aims to harm by infiltrating and disrupting a weak link in an organization’s system, often by targeting a vulnerable third-party supplier. Identifying the weakest point allows hackers to concentrate on the main target.
Spoofing
Spoofing
Spoofing fakes trusted sources in emails, calls, or websites, even using technical tricks like IP or DNS spoofing. It’s a sneaky way to:-
Snatch personal info
Spread malware
Dodge controls
Launch cyber attacks
So, successful attacks mean infected systems, data breaches, and revenue loss, spoiling an organization’s reputation. Traffic rerouting can flood the networks or even direct the users to malicious sites for the following two key illicit purposes:-
Information theft
Distribution of malware
Spoofing spans communication methods with varying technical expertise. It executes phishing scams to grab sensitive info.
While here below, we have mentioned the types of Spoofing attacks:-
Email Spoofing
Caller ID Spoofing
Website Spoofing
IP Spoofing
ARP Spoofing
DNS Server Spoofing
Insider Threats
Insider Threats
Insider threats arise within an organization involving employees or partners with valid access. Whether intentional or accidental, they endanger the network security, which leads to compromised data integrity.
Besides this, most data breaches result from insider threats, as traditional cybersecurity neglects all the internal risks.
However, the familiarity insiders have with systems and vulnerabilities gives them an exclusive advantage. Tackling insider threats requires equal severity to external threats in cybersecurity strategies.
Here below, we have mentioned all the types of insider threats:-
Malicious Insider
Careless Insider
Negligent insider
Compromised insider
DNS Tunneling
DNS Tunneling
DNS Tunneling encodes program data in DNS queries that enable the control of remote servers.
Besides this, it also demands the following things to fulfill its illicit goals:-
External network access
A compromised system
Control over a domain
Authoritative server for execution
DNS is crucial for internet navigation, as it interprets the domain names to IP addresses. That’s why organizations trust it, and it’s allowed through firewalls.
DNS tunneling exploits this trust and uses DNS requests as a command and control channel for malware. Inbound traffic commands the malware, while outbound exfiltrates data.
The flexibility of DNS allows for carrying sensitive info, making this attack vector simple and effective with various toolkits available.
The HONOR Magic6 Pro design and colors just got confirmed by the company. In addition to that, the phone also surfaced in a render alongside the vanilla HONOR Magic6.
The HONOR Magic6 Pro design gets confirmed by the company
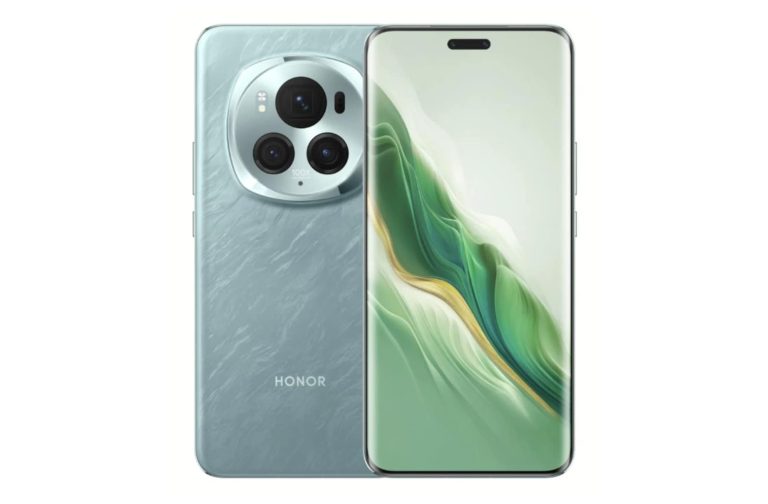
Let’s focus on the official info here first. If you check out the image provided below, you’ll see the official poster of the HONOR Magic6 Pro. There is also a pre-order listing on HONOR Mall, which shares even more details.
As you can see, the HONOR Magic6 Pro will have a triple camera setup on the back. The setup looks familiar, as the HONOR Magic5 Pro had a similar one. The shape of the camera island is different here, and the camera sensors are different in terms of size. The top one is obviously the main one, as the sensor seems to be quite large.
If we had to guess, we’d say that the phone has glass on the back, well, at least this model. That glass has a very interesting imprint, as you can see here. HONOR’s logo is also visible, and all the physical buttons sit on the right-hand side.
Both the phone’s front and back sides are shown
In addition to the official poster, the render of the phone also appeared, showing us both sides of the device. You can check out that image below. It seems like HONOR’s Magic OS 8.0 teaser from the other day really did show us the HONOR Magic6 Pro, as this front side is identical to that one.
The HONOR Magic6 Pro will have a pill-shaped camera cutout on the front, and it will be centered. It will be shorter than the one on the Magic5 Pro, but also seemingly wider. The bezels around the display are extremely thin, and the display itself is curved.
A quad-curved OLED display is also mentioned, as is the Snapdragon 8 Gen 3 SoC. MagicOS 8.0 will come pre-installed on the device, presumably on top of Android 14. The phone will be available in 256GB, 512GB, and 1TB storage options, at least in China. The device will launch in Black, White, Green, Cyan, and Purple colors.
The vanilla HONOR Magic6 will resemble its big brother
In addition to this leak, both the HONOR Magic6 and Magic6 Pro surfaced in renders, side by side. That image is shown below, and it shows white and black models. Sattelite connectivity was also mentioned for the HONOR Magic6 Pro.
The HONOR Magic6 series will launch in China on January 10, alongside Magic OS 8.0. Do note that a Porsche Design variant of the HONOR Magic6 Pro is also coming.
Hackers abuse the ChatGPT name for malicious domains to exploit the credibility associated with the ChatGPT model, deceiving users into trusting fraudulent websites.
Leveraging the model’s reputation enables them to trick individuals into:-
Revealing sensitive information
Downloading malicious content
H2 2023’s ransomware from ESET highlight isn’t typical, as it’s the “MOVEit hack” by the Russian ransomware group Cl0p, and here below, we have mentioned all the other names of Cl0p:-
Lace Tempest
FIN11
TA505
Evil Corp
This ransomware group is well-known for using ransomware in large-scale hacks; this time, their massive campaign used a zero-day vulnerability (CVE-2023-34362) in MOVEit on May 27.
The flaw, held since 2021, enabled unauthorized access, showcasing Cl0p’s evolution beyond traditional ransomware exploits. Recently, the cybersecurity researchers at ESET discovered more than 650,000 malicious domains registered resembling ChatGPT.
Massive Ransomware Attacks
The Russian ransomware group, Cl0p, hit global firms and US agencies in this attack. A notable change is that now they leak data on the open web if the ransom isn’t paid, it’s a tactic shared with the ALPHV ransomware gang.
The FBI notes ransomware evolving with multi-variant attacks like:-
Deployment of multiple ransomware variants
Use of wipers following data theft and encryption
In IoT, cybersecurity researchers find and disable the Mozi botnet with a discovered kill switch.
The Mozi botnet, which has been among the largest in three years, fell suddenly, prompting questions on kill switch use by developers or Chinese authorities.
Besides this, the new threat, Android/Pandora, hits the following types of Android devices for DDoS attacks in the same landscape:-
Smart TVs
TV boxes
Mobile devices
Cybersecurity researchers pinpoint the campaigns hitting ChatGPT users and numerous tries to access shady domains like-
Apart from this, the threats include insecure handling of OpenAI API keys, stressing the need for key privacy protection.
Cybersecurity analysts discovered a significant surge in the use of Android spyware like “SpinOk.” H2 2023 sees a surge in three-year-old JS/Agent and persistent Magecart attacks on unpatched websites.
Moreover, the prevention is possible with better security measures by developers and admins.
Cryptostealers surge with Lumma Stealer, a malware-as-a-service infostealer targeting crypto wallets. But, Bitcoin’s value rises without matching the increased cryptocurrency threats.
All these evolutions in the cybersecurity landscape highlight the diverse threat tactics.
After detecting App Installer abuse for malware distribution for several months, Microsoft disabled the protocol handler by default. The tech giant took this initiative in a bid to protect the customers from further threats.
Microsoft App Installer Disabled By Default
According to a recent blog post, Microsoft has disabled the App Installer (ms-appinstaller) protocol handler by default for its users.
The App Installer – precisely, ms-appinstaller URI (Uniform Resource Identifier) scheme (protocol) – facilitated users in direct installation of apps from the internet. It streamlined app installations, completing the process faster while using minimal disk resources.
Microsoft launched this feature with some newer versions of Windows 10. However, the tech giant had to disable it by default as it detected numerous exploitations of the protocol from different malware groups.
As elaborated, the firm observed the threat actors abusing the current implementation of the ms-appinstaller protocol handler for malware and ransomware distribution. They even detected the hacker groups distributing malware kits tailored to abuse the feature for stealth malware installations. Microsoft named some financially motivated threat actor groups, including the Storm-0569, Storm-1113, Sangria Tempest, and Storm-1674, actively abusing the feature.
Microsoft found the feature abuse and the subsequent malware campaigns to be around since mid-November 2023. The threat actors used various techniques to distribute malware, predominantly relying on social engineering and phishing.
The tech giant observed numerous malicious websites to be distributing the malware by impersonating legit software, such as Zoom, TeamViewer, Tableau and AnyDesk. Whereas, in case of Storm-1674, the threat actors distributed the malicious web page links via Teams to trick users.
After detecting these malware campaigns going around with an exponential rise, the tech giant decided to disable the feature to prevent malware abuse. Hence, Microsoft disabled the ms-appinstaller URI scheme handler by default in App Installer build 1.21.3421.0.
While this move will likely prevent the threat, Microsoft still advised the users to stay vigilant while interacting with web links.