Impacts on the crypto world

0
[ad_1]

The Binance prosecution marks a pivotal moment in the crypto world, heralding significant shifts in regulatory, operational, and investor landscapes. This article explores the profound implications of this event on the cryptocurrency market and its stakeholders. For investors seeking valuable educational materials, instantadvantageai.com stands out as an intuitive website. The reality is that investments come with substantial risks, and entering the market without thorough research can leave you in a disadvantaged position.

Immediate reactions in the crypto market

The news of Binance’s prosecution sent ripples across the crypto market, manifesting in various forms. Initially, there was a noticeable impact on Binance’s operations. The exchange faced heightened scrutiny, and this led to a cautious approach in their day-to-day operations. Users of the platform experienced changes in transaction processing times and heightened security checks, reflecting the company’s effort to align more closely with regulatory expectations.

In the broader market, cryptocurrency prices reacted with volatility. Major cryptocurrencies, including Bitcoin and Ethereum, saw fluctuations in their value, underscoring the market’s sensitivity to regulatory news. This volatility was not just confined to the leading currencies but also affected lesser-known altcoins, many of which are traded on Binance.

The crypto community’s response was a mix of concern and speculation. Investors, both individual and institutional, began reassessing their holdings and strategies. Online forums and social media platforms were abuzz with discussions about the future of Binance and the implications for similar exchanges. This environment of uncertainty led to a short-term reactive approach among investors, with some choosing to liquidate their holdings while others adopted a ‘wait and see’ strategy.

The immediate reactions in the crypto market to Binance’s prosecution highlighted the interconnected nature of legal, operational, and market aspects in the world of cryptocurrency. It was a clear demonstration of how regulatory actions against a major player can have far-reaching effects, influencing not just the entity in question but the entire crypto ecosystem.

Long-term implications for cryptocurrency exchanges

The prosecution of Binance is expected to have significant long-term implications for cryptocurrency exchanges globally. One of the most immediate effects is the increased focus on regulatory compliance. Exchanges, previously operating in relatively grey areas, are now under pressure to adhere strictly to financial regulations.

Another expected change is the consolidation of exchanges. Smaller or less compliant platforms may find it challenging to keep up with the heightened regulatory demands, potentially leading to mergers or acquisitions by larger, more established exchanges. This consolidation could reduce market fragmentation but may also limit choices for crypto traders.

The investor trust dynamic is also set to change. With the prosecution of such a prominent player like Binance, investor confidence in cryptocurrency exchanges has been shaken. This could lead to a more cautious approach from both retail and institutional investors, possibly slowing down the influx of new capital into the crypto markets.

Furthermore, this development could accelerate the push towards decentralized exchanges (DEXs). As trust in centralized exchanges wavers, the appeal of DEXs, which offer trading without the need for a central authority, could grow. This shift could fundamentally alter the way cryptocurrencies are traded, promoting a more decentralized, peer-to-peer approach.

Impact on investors and the broader crypto ecosystem

The prosecution of Binance has significant ramifications for investors and the broader cryptocurrency ecosystem. For investors, both individual and institutional, the immediate effect was a heightened sense of uncertainty. This uncertainty led to a reassessment of risk, particularly for those heavily invested in cryptocurrencies through Binance. Investors are now more cautious, scrutinizing the stability and regulatory compliance of exchanges before committing their funds. This shift in investor sentiment is prompting a more thorough due diligence process, leading to a more informed and potentially more risk-averse investment community within the crypto space.

Institutional investors, who have been increasingly entering the cryptocurrency market, are particularly sensitive to regulatory actions. The case against Binance has led to a reevaluation of the regulatory risks associated with crypto investments. This reassessment could slow down the entry of new institutional capital into the crypto market, or at least redirect it towards more regulated and established financial products like Bitcoin futures or exchange-traded funds (ETFs).

The broader cryptocurrency ecosystem is also experiencing shifts. Projects and startups that rely on cryptocurrency exchanges for liquidity and funding are facing new challenges. The heightened regulatory scrutiny may lead to more stringent listing processes, affecting the ability of new tokens and cryptocurrencies to access a wider market. Additionally, the increased focus on regulatory compliance may drive innovation in areas like blockchain analytics and security, as projects and exchanges work to align with new standards.

Conclusion

The prosecution of Binance serves as a watershed event in the cryptocurrency sector, reshaping investor behavior, regulatory approaches, and the operational dynamics of crypto exchanges. It underscores the evolving nature of this innovative yet volatile market.


[ad_2]
Source link
iPhone users just got a Journal app. Why would you use it, and do you even need it when you have the Notes app?

0
[ad_1]

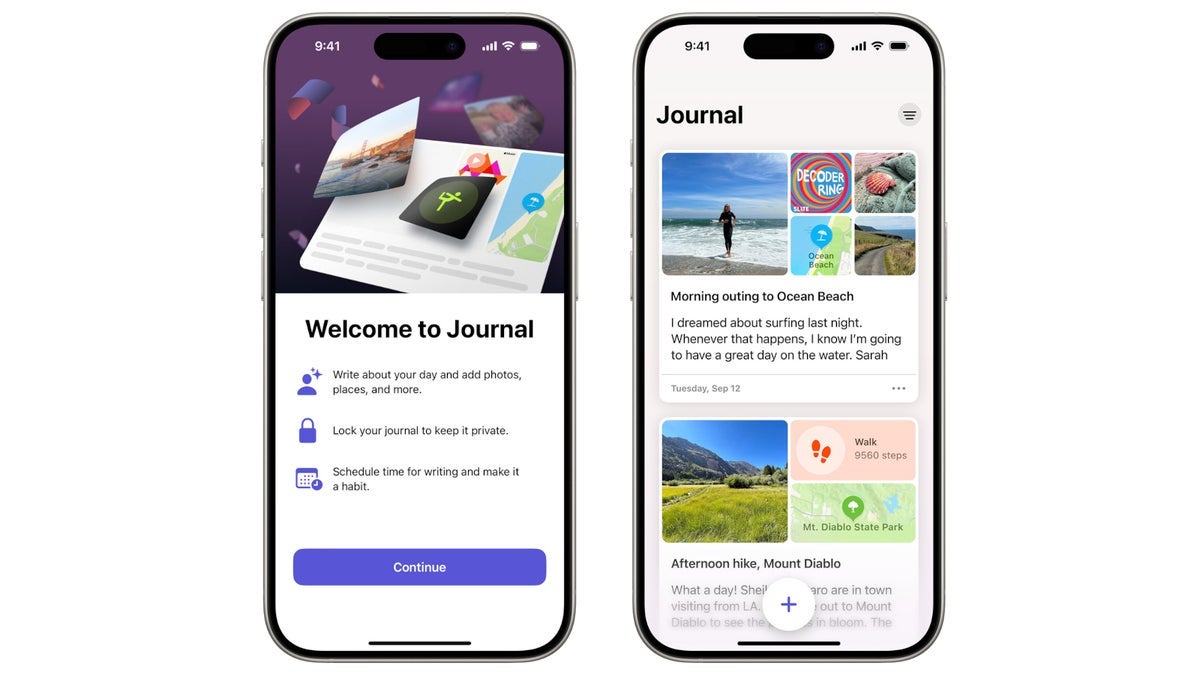
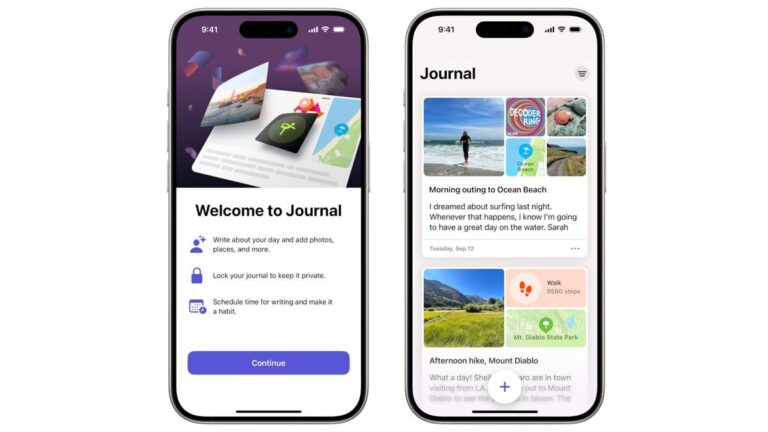
iOS 17.2 is now available, bringing a brand-new app named Journal. And now, as we’re nearing the end of 2024, it’s an ideal time to be doing some self-reflection. Now, you may be wondering why would you need a Journal app on your iPhone, especially when you have the Notes app. Well, let’s talk about it.

Is journaling different than taking notes?

People have been journaling for quite a while. Initially, it was done in diaries, physical notebooks that you hide in a locked drawer away from curious eyes, and where you shared important things about your day. Journaling is a form of self-reflection, and doing it regularly can help you figure out things about yourself and find areas for growth. 

On the other hand, note-taking is more of an administrative thing and mainly focuses on helping you remember what you need to buy or do.

Of course, nobody (or almost nobody) nowadays uses physical notebooks (I mean, I’ve almost forgotten how to write with a physical pen and end up with scribbles that aren’t really pretty every time I try!). That’s where the new Journal app comes in handy.

It’s no secret that tech is there to help us get more done and be more productive and entertained. But tech can also help us with growth!

It’s a busy world… 

We rarely have time to just sit with ourselves, as we’re constantly running around: be it work, kids, chores, projects… but self-relfecting is a vital part of becoming a better person and growing. Why? Because without you knowing yourself, what drives you or angers you, you can’t move forward and evolve as a person. 

The Journal app can be helpful if you forget to take time for yourself, as it can remind you to write, and also you get suggestions in case the empty page feels daunting.

What’s also better about the Journal app than your regular physical diary is that you can easily add photos, videos, and other media to a journal entry. How can this help with self-reflection? Let’s say you’re having an active outdoorsy day and you’ve taken loads of photos of nature. You want to be able to remember the feeling the experience brought to you, so you put it in a Journal entry.

You’re having a bad day? Maybe a quick voice note of you just saying how you’re feeling can help figure things out? Sometimes, we just feel grumpy without knowing how to fix it – well, naming the emotion you’re feeling is a way to bring clarity to your mind and help you start addressing the issue.

And, if you have all of these entries in your Journal app, you start to see the bigger picture about yourself and your emotions. Thus getting you to better know yourself, and making lasting changes to reach your fullest potential. 

Journaling challenge: let’s try this out! 

You may still be thinking that there’s no point in the Journal app. But you never really know before trying it out, do you? In fact, for you to start feeling the benefits of journaling and self-reflection, you need to do it regularly for some time.

Let’s do a challenge together! Let’s try to have at least one entry (you can do more if you want) each day for 14 days. Then, on the 14th day, let’s go through our entries and try to find these three things: 

  • What things or experiences inspire me
  • What situations make me angry
  • What can I improve about myself

See if you can find something about yourself that you didn’t know!


[ad_2]
Source link

Mighty blockchain in healthcare: Advanced use cases

0
[ad_1]

Exploring the transformative power of blockchain in healthcare, this article delves into its potential to revolutionize patient data security, clinical trials, and drug traceability. We uncover how this cutting-edge technology is reshaping healthcare paradigms for a more secure and efficient future. Immediate GPT is a user-friendly website crafted to provide investors with essential educational materials. Investing is inherently risky, and entering the market without thorough research can leave you at a significant disadvantage.

Enhancing patient data security

At the core of blockchain’s application in healthcare is its decentralized nature. Unlike conventional databases that store data in a central location, blockchain disperses data across a network of computers, making it nearly impossible for hackers to access the entire repository of sensitive patient information. This decentralized approach not only enhances security but also ensures data integrity, as each transaction on the blockchain is encrypted and linked to the previous one, creating an unalterable chain of records.

A notable real-world example of this application is the implementation of a blockchain-based patient data management system. In such a system, each patient’s data becomes a part of a secure, immutable ledger. This setup not only safeguards the information against unauthorized access but also empowers patients with control over their own data. Patients can grant or revoke access to their medical records, ensuring that their information is shared securely and only with relevant healthcare providers.

The immutability of blockchain further fortifies patient data security. Once information is entered into the blockchain, it cannot be altered or deleted, which is crucial for maintaining accurate medical records. This feature is particularly significant in scenarios where medical history plays a vital role in treatment decisions.

Moreover, blockchain’s transparency feature, while maintaining privacy, offers a unique advantage. While ensuring that patient identities are protected through advanced encryption techniques, blockchain allows for the verification of data authenticity by authorized parties. This transparency is vital in medical contexts where the authenticity of medical information is paramount.

Streamlining clinical trials

Blockchain’s most significant impact in clinical trials is on data integrity and management. In traditional clinical trials, data is collected from various sources and is susceptible to manipulation or errors, potentially leading to unreliable results. Blockchain introduces a secure, immutable ledger system where trial data is recorded in real time. This ensures that once data is entered, it cannot be altered or deleted, thus maintaining its integrity throughout the trial process.

Another critical aspect of blockchain in clinical trials is the enhancement of transparency. With blockchain, every transaction or data entry is recorded and time-stamped, creating a transparent and traceable record of all activities within the trial. This level of transparency is vital for regulatory compliance, audit trails, and maintaining public trust in the trial process. Moreover, it enables real-time monitoring of the trial progress, allowing researchers and regulators to identify and address issues promptly.

Blockchain also streamlines the participant consent process. In clinical trials, obtaining and managing participant consent can be complex and paperwork-intensive. Blockchain simplifies this process by creating a secure and transparent system where participants can give, withdraw, or manage their consent digitally. This not only reduces administrative burden but also empowers participants by giving them greater control over their involvement in the trial.

Furthermore, the decentralized nature of blockchain eliminates the need for intermediaries, facilitating direct and secure communication and data exchange between all stakeholders involved in the trial, including researchers, participants, and regulators. This direct approach reduces the possibility of miscommunication and enhances the efficiency of the trial process.

Case study 3: Drug traceability and authenticity

The pharmaceutical industry faces ongoing challenges with drug traceability and authenticity. Counterfeit drugs, which may be ineffective or harmful, are a global problem, and the complex supply chains of legitimate drugs can be difficult to monitor. Blockchain technology offers a groundbreaking solution, ensuring the traceability and authenticity of drugs from production to consumption.

Blockchain’s role in the pharmaceutical supply chain starts at the point of drug manufacture. Each batch of medication can be recorded on the blockchain with a unique identifier, capturing details like production date, batch number, and expiration date. This information becomes a part of an immutable ledger, providing a tamper-proof record. As the drugs move through the supply chain—from manufacturer to distributors, pharmacies, and finally to patients—each transaction is recorded on the blockchain. This creates a transparent and traceable journey of the drug, which can be accessed and verified by authorized stakeholders at any point.

This traceability is crucial for several reasons. First, it helps in combating counterfeit drugs. By scanning a drug’s packaging, pharmacists and consumers can verify its authenticity and origin through the blockchain records. This greatly reduces the risk of counterfeit drugs entering the supply chain and reaching patients.

Conclusion

The exploration of blockchain in healthcare reveals a future where enhanced security, efficiency, and trust redefine the industry. Its advanced applications promise to streamline healthcare processes, ensuring a safer and more transparent medical landscape for all.


[ad_2]
Source link

Pixel Launcher search might show Quick Settings

0
[ad_1]

If you need to find something on your Pixel device, you have a nifty search bar that you can use. when you search for something, you’ll see it bring up apps along with settings in the results. Now, according to a new report, the Pixel Launcher might also show quick settings as search results.

The Google search bar in the Pixel Launcher acts like a universal search bar. When you type something, you’ll see it display all types of results. Firstly, it shows you web results because it’s a Google search bar first and foremost. Along with that, you’ll also see apps that you installed on your device and settings as results. Google had been working on this feature for a while before beginning to test it.

The Pixel Launcher search bar could show you quick settings

Right now, we don’t know the rollout pace of this new feature, but one of the folks at 9To5Google spotted this on their phone. It was on a phone running the latest Android 14 QPR. When searching a term in the bar, the phone would also show quick settings as results. As you can see in the screenshots, the results will pop up, and they’ll be in the classic Material You rounded rectangular bubbles.

pixel launcher quick settings search

This is a bit bittersweet, as third-party Quick Settings don’t show up. It’s weird that the company omitted these settings. In any case, when you search for a setting, you’ll be able to interact with it from the search bar. This means that you’ll be able to toggle the settings as if you’re in the Quick Settings panel

At this point, it seems that Google is testing this out on a limited number of users. Since it’s a test, we don’t know when or if Google plans on making this a mainstay in the operating system. We’ll have to wait to see if Google retains it.


[ad_2]
Source link

NKAbuse Malware Attacking Linux Desktops & Corn Persistence

0
[ad_1]

Threat actors target Linux systems due to their prevalence in server environments, and cron jobs offer a discreet means of maintaining unauthorized access over an extended period.

Kaspersky experts discovered “NKAbuse,” a versatile malware using NKN tech for peer data exchange, written in Go with cross-architecture compatibility. 

Targeting Linux desktops primarily, it threatens:-

  • MISP
  • ARM systems
  • IoT devices

Infiltrating via implant upload, it establishes persistence through a cron job in the home folder, featuring:-

  • Flooding 
  • Backdoor access

NKAbuse Malware Attacking Linux Desktops

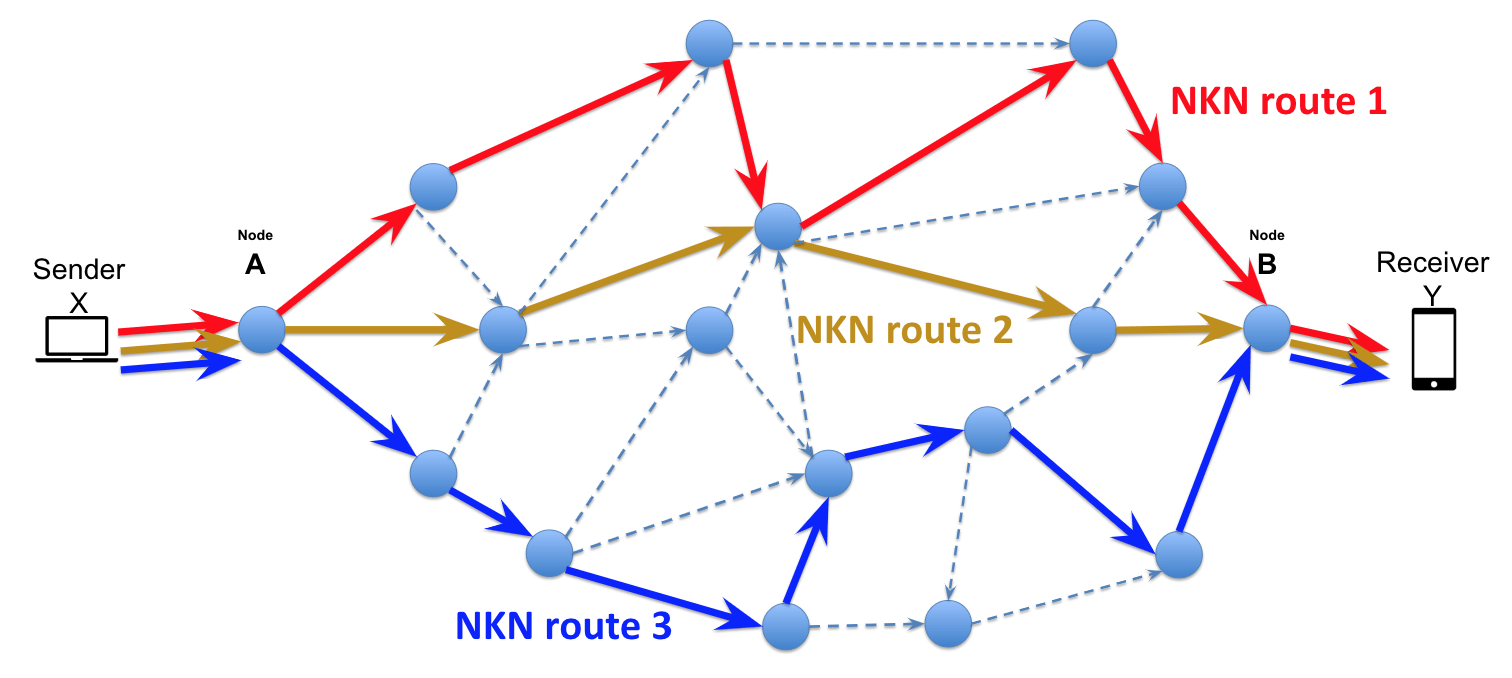
NKN (New Kind of Network) is a decentralized protocol prioritizing privacy, with more than 60,000 nodes. Featuring diverse routing algorithms, it optimizes data transmission. 

Besides this, malware exploits like the (ab)use of NKN’s blockchain protocol enable flooding attacks and Linux system backdoors.

NKN data routing diagram (Source - Securelits)
NKN data routing diagram (Source – Securelits)

GERT finds evidence indicating a Struts2 (CVE-2017-5638) exploit in an attack on a financial firm. The vulnerability allows command execution via a “shell” header, leading to script download and malware installation on the victim’s device. 

The setup process checks the OS type, downloads the second stage (malware), named “app_linux_{ARCH},” and executes it from the /tmp directory.

The malware supports eight architectures, and here below, we have mentioned them:-

  • 386
  • arm64
  • arm
  • amd64
  • mips
  • mipsel
  • mips64
  • mips64el

Malware NKAbuse, when executed, relocates to /root/.config/StoreService/, retrieves IP via ifconfig.me, and utilizes cron jobs for reboot survival. 

It employs NKN protocol for communication, creating an account, and multiclient for concurrent data exchange. 

With a handler for bot master messages, NKAbuse executes DDoS attacks, including a unique DNS overflow targeting “{JUNK}.google.com” subdomains.

According to researchers, NKAbuse is not just a DDoS tool but also a highly capable backdoor/RAT that offers various features for maintaining persistence, executing commands, and gathering sensitive information.

Its ability to operate as a backdoor and remotely control infected systems makes it a serious threat to cybersecurity.

It establishes a “Heartbeat” structure for regular communication with the bot master, storing host details, and the capabilities include:-

  • Taking screenshots
  • Creating/removing files
  • Fetching file lists
  • Listing processes
  • Running system commands
  • Sending output via NKN

NKAbuse is a unique cross-platform threat that stands out for its use of uncommon communication protocols. Crafted for botnet integration, it doubles as a host-specific backdoor.

IOCs

Host-based:-

  • MD5: 11e2d7a8d678cd72e6e5286ccfb4c833

Files created:-

  • /root/.config/StoreService
  • /root/.config/StoreService/app_linux_amd64
  • /root/.config/StoreService/files
  • /root/.config/StoreService/.cache

[ad_2]
Source link

Apple might owe you some money after settling a class-action suit

0
[ad_1]
Per USA Today, Apple might owe you some money after settling a class-action lawsuit over the Family Sharing feature. The suit, known as Walter Peters v. Apple, was settled by Apple for $25 million which means that Apple might owe you as much as (are you sitting down?) a whopping $30! Family Sharing is an App Store feature that allows purchased apps to be shared with up to six family members. The “initiating user” lists the five additional family members in the initiator’s Apple Account.

Apple forced app developers to include ads for Family Sharing on their apps’ landing pages

If the family members consent to be included in the Family Sharing program, when any family member purchases an app that supports Family Sharing from the App Store, the app is downloaded on the devices of the other family members even though only one payment is necessary to purchase the app for all six family members. The complaint noted that “Apple places and/or demands that its software developers place a small advertisement on the landing pages for its apps which states that the app supports Family Sharing.”

Up until January 30, 2019, Apple included an advertisement on each app’s landing page that said, “Supports Family Sharing. With Family Sharing set up, up to six family members can use this app.” Apple included this statement on the landing pages of apps that did not support the feature. The complaint alleges that even though Apple knew that the vast majority of the apps in the App Store did not support Family Sharing, the landing page for most subscription-based apps included the ad.

Obviously, as the complaint points out in black and white, “This advertisement is materially misleading, in that it plainly states that the App is available for Family Sharing, when
it is not.” As you might have expected, millions of App Store visitors purchased apps that they thought would be automatically shared with the five family members they previously designated. These Apple device owners were upset to find out that a particular app they paid for, which featured the Family Sharing ad on its landing page, did not actually support the feature.
The crux of the complaint against Apple reads like this: “As a result of Apple’s deceptive and misleading practices, Plaintiffs and the Class Members were induced to purchase subscription-based Apps for which Apple receives hefty fees, believing that those Apps could be shared with up to six family members—when in fact they were available only to the single user who set up the subscription.”

The complaint adds that “Apple has made millions of dollars in fraudulent sales to individuals who Apple told were receiving up to six copies of an App when they were receiving only one. Apple’s customers did not receive the benefit of their bargain. They were misled.

In the document containing the settlement, “Apple denies that it made any misleading misrepresentations with respect to the sharing of third-party subscriptions using Family Sharing or that the Named Plaintiffs or Class have suffered any injury or damages or are entitled to any restitution.” So then, why not let the whole thing play out in court? Apple explains that “taking into account the uncertainty and risks inherent in litigating this case, Apple has concluded  that continuing to defend this Action would be burdensome and expensive. Apple enters into this Agreement without in any way acknowledging any fault, liability, or wrongdoing of any kind.”

If you haven’t been notified but believe you are eligible for your share of the settlement, here is how you file a claim

If you signed up for Family Sharing between June 21st, 2015, and January 30th, 2019 with at least one other person and purchased a third-party app, you are eligible to make a claim. And those who are eligible will receive an email with details about the settlement. But if you don’t receive any notification and believe that you are eligible to make a claim, you can register by heading to the settlement website by tapping this link. The deadline to opt into the settlement is March 1st, 2024.
Depending on the number of legitimate claims received, each participant agreeing to the settlement could find themselves as much as $30 richer. The final approval hearing will take place on April 2nd, 2024. Members of the class can decide in advance whether to have their percentage of the settlement sent to them via electronic bank transfer or by check.

[ad_2]
Source link

Apple reveals discount pricing feature for subscriptions in the App Store

0
[ad_1]
A post on the Apple Developer website (via 9to5Mac) reveals that a new “contingent pricing” feature will be available in the App Store. The subscription gets its name because customers can be given a discount on a subscription contingent on them having an active subscription to another publication. That discount will continue to be offered every month as long as the customer remains subscribed to both publications.
Here is what Apple told developers on the website: “Contingent pricing for subscriptions on the App Store — a new feature that helps you attract and retain subscribers — lets you give customers a discounted subscription price as long as they’re actively subscribed to a different subscription. It can be used for subscriptions from one developer or two different developers. We’re currently piloting this feature and will be onboarding more developers in the coming months.”
Apple goes on to say that developers should start planning how they will work contingent pricing into their App Store pricing strategies. A link on the website will allow developers to sign up to receive a notification from Apple in January which is when the company will inform developers of more details related to “contingent pricing.”

In explaining exactly what “contingent pricing” is, Apple writes, “For example, you might offer Ocean Journal premium subscribers the opportunity to subscribe to Mountain Climber for a discounted price of $4.99/month instead of the regular $5.99/month. Customers pay the discounted price as long as they remain Ocean Journal subscribers.”

While Apple is writing to developers, the tech giant does explain how customers will be able to find publications in the App Store that offer “contingent pricing.” Apple says that customers will find the discounted pricing in a publication’s App Store listing, off-platform marketing channels, and planned placements in the App Store.

Apple says that it will help developers manage the implementation of “contingent pricing” by offering customers “a seamless redemption and purchasing experience” based on the contingent price proposition that the developers will be providing.

Obviously “contingent pricing” isn’t going to be available to App Store customers until sometime next year.


[ad_2]
Source link

Google Contacts app can lead you to the location of friends and family members

0
[ad_1]
How would you like to find out a friend or family member’s current location from your Google Contacts app? It sounds pretty cool, right? Android users are beginning to get this feature pushed out to them by Google in version 4.22.37.586680692 of the Google Contacts app. My Pixel 6 Pro running Android 14 QPR2 Beta 2 has yet to receive this update. 
You can check to see which version of the Contacts app your Android phone is running by going to Settings > Apps and scrolling to Contacts. Tap on Contacts to see the App info page. Scroll down to the bottom of the page and at the very bottom of the screen, the version number of the app will appear. If you don’t have the necessary version running on your phone, there is no need to panic. You’ll get it in due time.
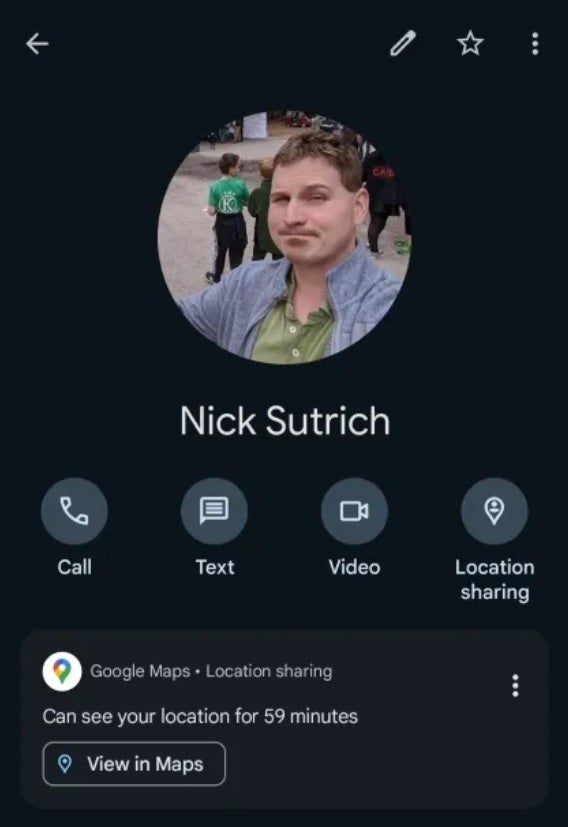
Now there are some important instructions. This feature is available to you only for those contacts who share their location with you in Google Maps and whose Gmail address you have on their Contacts card. If so, you’ll see a small part of the bottom of the screen dedicated to Google Maps-Location sharing. This will reveal whether the other party can see your location and if so, for how long they will be able to do so.

A button that says Maps will appear on this portion of the Contacts card. Tap on it and you’ll be able to see the person’s location in Google Maps. Besides making sure that your Contacts card for a specific friend or family member includes his/her Gmail address, and that the person shares his/her Google Maps location with you, you must use the Google Contacts app on your Android phone and not one offered by the manufacturer of your phone.

If your Android phone isn’t using Google Contacts, you can find the app in the Play Store by tapping on this link. And the beauty of this feature is that once you find the location of your friend or family member on Google Maps, one tap will give you directions to his/her location.

[ad_2]
Source link

Hackers Access Customer Info, Corporate Systems in MongoDB Data Breach

0
[ad_1]

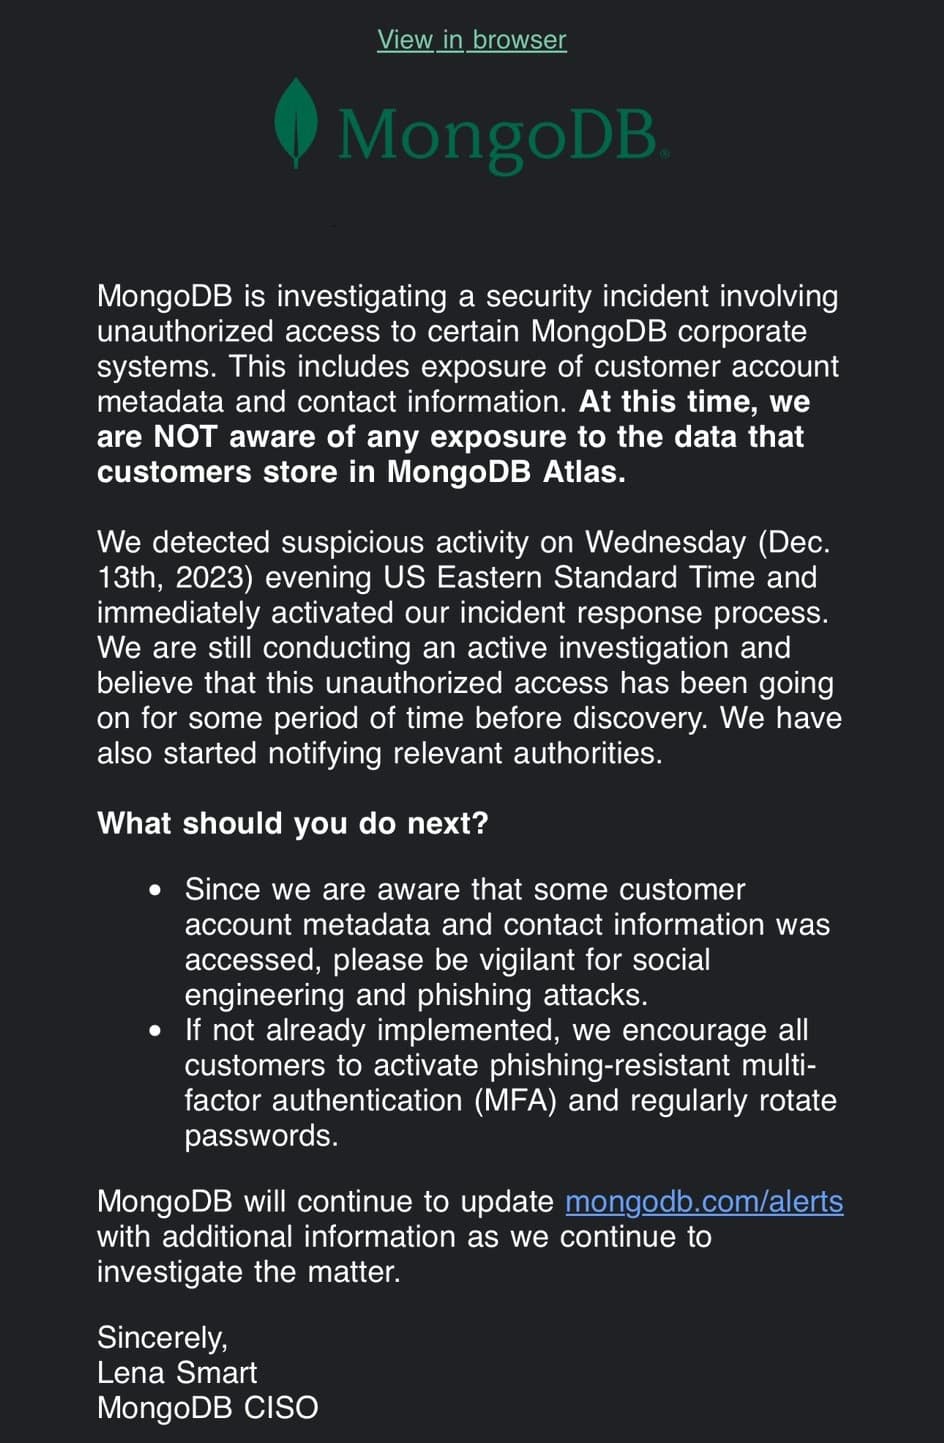
In an email, Lena Smart, MongoDB’s Chief Information Security Officer (CISO), confirmed the latest MongoDB Data Breach, revealing that while investigations are underway, it has been verified that hackers accessed customer metadata and contact information.

MongoDB, a leading database management company, has fallen victim to a security incident resulting in unauthorized access to certain corporate systems. The breach, detected on the evening of December 13th, 2023, US Eastern Standard Time, has prompted an immediate and comprehensive investigation by the company.

The breach includes the exposure of customer account metadata and contact information, heightening concerns about the potential misuse of sensitive data. MongoDB activated its incident response process upon the discovery of suspicious activities, but it is believed that the unauthorized access may have been ongoing for some time before being detected.

Lena Smart, MongoDB’s Chief Information Security Officer (CISO), sent an email communication to MongoDB customers, outlining the details of the breach and urging caution in the wake of potential social engineering and phishing threats. The company assures customers that, as of now, there is no indication of exposure to the data stored in MongoDB Atlas, a cloud-based database service.

Despite the incident, MongoDB is actively managing the situation, with ongoing updates promised on their alert page (mongodb.com/alerts) as the investigation progresses. Relevant authorities have also been notified, underlining the seriousness of the security breach.

In a subsequent update at 5:25 PM EST on December 16, 2023, MongoDB reported a spike in login attempts, causing issues for customers attempting to access the MongoDB Atlas and Support Portal. However, MongoDB clarified that this was unrelated to the security incident and advised affected users to try again in a few minutes.

Lena Smart, in her email to customers, emphasized proactive steps to mitigate potential risks. MongoDB recommends customers be vigilant for social engineering and phishing attacks and take immediate action, such as activating phishing-resistant multi-factor authentication (MFA) and regularly rotating MongoDB Atlas passwords.

Hi,

MongoDB is investigating a security incident involving
unauthorized access to certain MongoDB corporate
systems. This includes exposure of customer account
metadata and contact information. At this time, we
are NOT aware of any exposure to the data that
customers store in MongoDB Atlas.

We detected suspicious activity on Wednesday (Dec.
13th, 2023) evening US Eastern Standard Time and
immediately activated our incident response process.
We are still conducting an active investigation and
believe that this unauthorized access has been going
on for some period of time before discovery. We have
also started notifying relevant authorities.

What should you do next?

Since we are aware that some customer
account metadata and contact information was
accessed, please be vigilant for social
engineering and phishing attacks.

If not already implemented, we encourage all
customers to activate phishing-resistant multi-
factor authentication (MFA) and regularly rotate
passwords.

MongoDB will continue to update mongodb.com/alerts
with additional information as we continue to
investigate the matter.

Sincerely,
Lena Smart
MongoDB CISO
Hackers Access Customer Info in Latest MongoDB Data Breach
Email sent by the company’s CISO reveals the latest MongoDB data breach (Screenshot credit: Hackread.com)

As the investigation unfolds, MongoDB customers are anxiously awaiting further updates on the situation. The incident serves as a stark reminder of the constant and evolving threats faced by companies in the digital age, underscoring the importance of robust cybersecurity measures and the need for continuous vigilance in safeguarding sensitive customer information.

  1. 47% of online MongoDB databases hacked demanding ransom
  2. 11 million personal unprotected MongoDB records leaked online
  3. Ride-hailing app leaks data of millions of Iranians from MongoDB
  4. Unprotected MongoDB leaks resume of 202M Chinese job seekers
  5. Hackers leave ransom note after wiping out MongoDB in 13 seconds

[ad_2]
Source link

Hackers Fix Polish Train Glitch, Face Legal Pushback by the Manufacturer

0
[ad_1]

Whitehat hackers are vital for companies, large to small, but what if some businesses fail to grasp the significance of ethical hacking?

In a recent cybersecurity incident, three Polish hackers achieved success in repairing the malfunctioning software of a train, initially serviced by independent repair shops for a regional rail operator.

However, the narrative took a twist when accusations arose against the manufacturer, Newag, alleging that they remotely rendered inoperable trains serviced by the Polish train repair company, SPS. That’s not all, reportedly, Newag is threatening the hackers with a lawsuit.

The practice of remotely disabling or “bricking” products serviced by third-party entities is not unfamiliar, as major tech companies, such as Apple, adopt similar measures to safeguard revenue streams.

While we don’t want to get overly religious or emotional, it’s an undeniable fact that Whitehat hackers, also known as ethical hackers or cybersecurity researchers, are nothing short of a blessing. Numerous cases exist where ethical hackers have saved companies from devastating hacks.

Further, take, for instance, this whitehat hacker who went the extra mile to unlock a car for a family that lost their keys. And let’s not forget the notorious WannaCry ransomware attack, which was successfully thwarted by a whitehat hacker, while cybersecurity and technology giants remained clueless. However, Newag’s response to the event highlights a notable lack of understanding of cybersecurity on their part.

The issues surrounding Newag’s Impuls series of trains, which are operated by independent entities, have been ongoing since the summer, adversely affecting customer service. These trains exhibited mysterious failures, refusing to restart after routine maintenance. To unravel the mystery behind these disruptions, SPS enlisted the expertise of Dragon Sector, a group of ethical hackers.

Insights from Dragon Sector reveal a concerning aspect of Newag trains’ software programming in Poland. According to the ethical hacking group, Newag’s trains were equipped with a unique feature that triggered a software lockdown if they remained stationary for more than 10 days.

Regardless, the complexities of Newag’s software go beyond mere inactivity, extending to a sophisticated mechanism that activates when a train parks at specific GPS locations.

Remarkably, these preset GPS locations align strategically with independent repair shops spread across Poland. This means that the software lockdown could be initiated not only based on the duration of inactivity but also when a train is parked at designated locations, which happen to coincide with indie repair shops.

A noteworthy revelation is that at least one of these predetermined GPS locations included a repair shop still in the construction phase at the time when the programming details came to light. This raises questions about the intention and scope of Newag’s software lockdown strategy, as it appears to extend beyond the straightforward goal of preventing prolonged inactivity.

One of Dragon Sector’s hackers, Michał Kowalczyk, stated that this issue seems deliberate from Newag. “Today we are sure that it was a deliberate action on Newag’s part. We discovered the manufacturer’s interference in the software, which led to forced failures and to the fact that the trains did not start,” Michał claimed.

Zaufana Trzecia Strona, a Polish language IT security news website also reports that repair countermeasures would activate if parts were replaced without a hidden unlock sequence in the train’s computer. Additionally, codes would shut the train down after one million kilometres, and hardware could allow remote interaction with Newag trains.

Newag, Poland’s oldest railway company, denies accusations and blames SPS for initiating a conspiracy theory. The company now demands the repaired trains be removed from service immediately, claiming they had been “hacked” and might be unsafe. 

Newag claims the story is slander from competitors and threatens to sue Dragon Sector. The company believes it to be an attack on independent repair, which has become a controversial issue pitting consumers and companies like Apple, John Deere, and many across the car industry against each other. Right-to-repair is combated through proprietary software and encryption that the company can only read.

Lower Silesian Railways, a rail operator, has been in a dispute with Newag, which produces its Impuls 45WE hybrid multiple units. In June 2022, the railroad experienced multiple no-start failures with these trainsets, resulting in fewer trains running than scheduled and impacting passenger service.

Nevertheless, this should come as no surprise, as companies and businesses frequently don’t appreciate the efforts of whitehat hackers who are doing good. Cybersecurity researchers like Rob Dyke and Wesley Wineberg are prime examples of what can occur when companies fail to grasp the importance of responsible disclosures.

  1. Whitehat hacker bypasses SQL injection filter for Cloudflare
  2. “Good hackers” took over billboard to send security warning
  3. White hat hackers infect Canon DSLR camera with ransomware
  4. Whitehat hackers accessed primary keys of Azure’s Cosmos DB Users
  5. Whitehat hacker shows how to detect hidden cameras in Airbnb, hotels

[ad_2]
Source link