Google could be working on an AI assistant for the Pixel 9

0
[ad_1]

Right now, the Pixel 8 Pro enjoys some heightened AI capabilities thanks to Gemini. That’s great for folks using this phone, but Google is already planning on the AI chops for its next flagship phone, the Pixel 9 series. According to a new report, the Pixel 9 will have its own exclusive AI assistant called Pixie.

Billions of Android phones around the world have access to the all-powerful Google Assistant. It’s been able to establish itself as the king of voice assistants. The company announced Assistant With Bard (AWB) back in October, so it’s only going to get smarter as time goes on. As you can imagine, AWB will be the Google Assistant powered up with the Bard chatbot. We’re still waiting for information on that feature to come as Google pushes further into this AI world.

Google is working on the Pixie assistant for the Pixel 9

Obviously, you’ll want to take this news cautiously. We’re talking about something that, if true, won’t hit the market for almost a year. We’re dealing with early information, so anything could change at any moment.

Sources say that Google is working on an AI assistant that will be exclusive to Pixel devices. From how it sounds, it seems that this will be separate from AWB. This powerful AI assistant is expected to be called Pixie. Aside from having an adorable name, Pixie is expected to have some powerful AI prowess. It may be able to integrate with apps like Gmail, Google Maps, and other apps, but we don’t know how. We can expect that it will have deep integration. Don’t be surprised if you’ll be able to tell it to draft emails or other messages for you.

As for the availability, we don’t know what Pixel devices will be able to have Pixie. We’re not sure if Google is going to make it exclusive to the Pixel 9 phones or distribute it down to the current and recent Pixel devices on the market.

The report also states that Google could possibly develop a pair of AI glasses that will utilize Pixie. Now, we don’t know anything about these glasses, but it seems that the company is referring to them only as an “internal discussion”. So, there might not be any solid plans to develop these glasses.

With the information we have, it looks like the classes will have a camera to scan the world and give you real-time feedback based on what they see. This could be Google Lens on steroids (and on your face.)

Since this is all still early information, we’ll need to wait for more details to know what’s going to happen.


[ad_2]
Source link

Apple to introduce new feature that makes life harder for iPhone thieves

0
[ad_1]

Reportedly, Apple has plans to make it harder for iPhone thieves to steal your personal information even if they have your device’s passcode.

A new feature called Stolen Device Protection is included in the bet version of iOS 17.3. The feature limits access to your private information in case someone gets hold of both your iPhone and your passcode.

Thieves sometimes lurk in public places like bars on the lookout for iPhone owners typing in their passcode. Once they know the passcode, they steal the device and gain access.

With the passcode, a thief can perform a lot of actions that have financial consequences and some that make it harder to retrieve the device:

  • View and use passwords or passkeys saved in the iCloud Keychain
  • Apply for a new Apple Card
  • Turn off Lost Mode
  • Erase all content and settings
  • Take certain Apple Cash and Savings actions in Wallet
  • Use payment methods saved in Safari
  • Use your iPhone to set up a new device
  • Change your Apple ID password
  • Update select Apple ID account security settings, including adding or removing a trusted device, trusted phone number, Recovery Key, or Recovery Contact
  • Change your iPhone passcode
  • Add or remove Face ID or Touch ID
  • Turn off “Find My”

However, when users turn on Stolen Device Protection, Face ID or Touch ID authentication is required for all of the above actions and also to turn off Stolen Device Protection.

Apple said it will share additional information about Stolen Device Protection soon, to clarify how the feature works.


We don’t just report on iOS security—we provide it

Cybersecurity risks should never spread beyond a headline. Keep threats off your iOS devices by downloading Malwarebytes for iOS today.


[ad_2]
Source link

New GambleForce Hacker Gang Hacks Targets with Open Source Tools

0
[ad_1]

Cybersecurity researchers at Singapore-based Group-IB have unmasked EagleStrike, a subgroup of the GambleForce hacker group. They are opportunistic hackers exploiting simple vulnerabilities.

In September 2023, Group-IB’s Threat Intelligence unit discovered a command and control server hosting publicly available open-source pentesting tools, none being custom-made, designed for SQL injections.

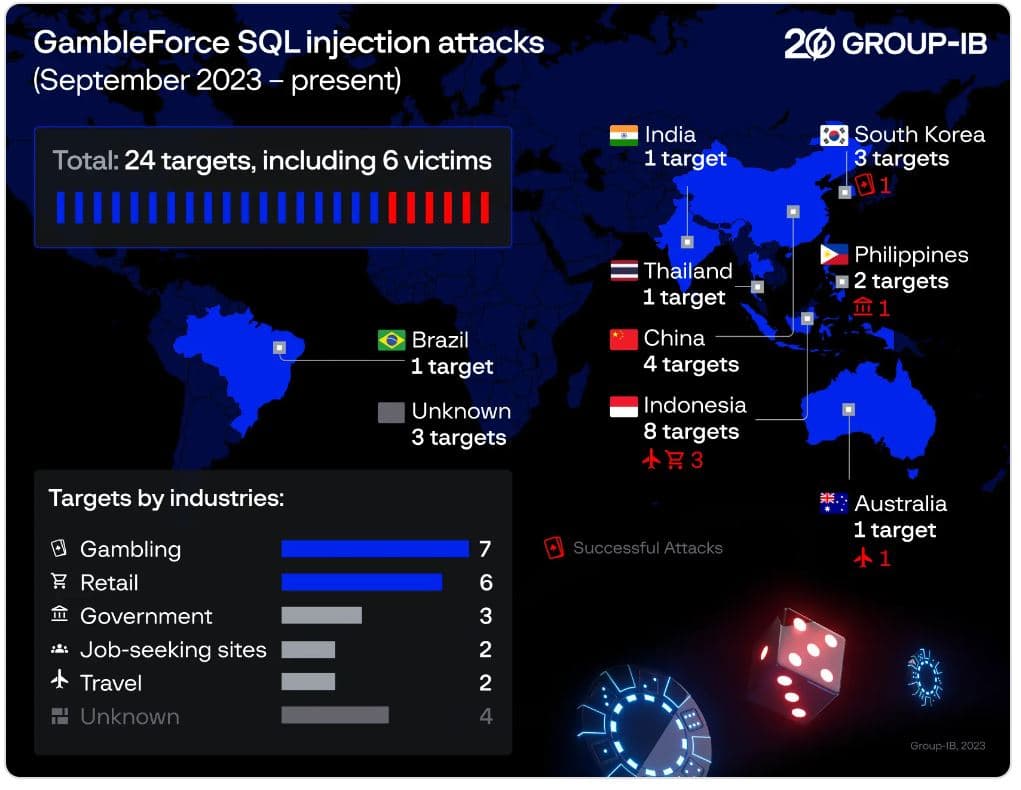
The attacker was identified as “GambleForce,” who had targeted 24 organizations in government, gambling, retail, travel, and job-seeking sectors across 8 countries between September and December 2023, successfully compromising 6 websites in Australia, Indonesia, the Philippines, and South Korea. The group has also targeted websites in China, India, and Thailand.

New Hacker Group GambleForce Hacks Targets with Open Source Tools

The group uses basic yet effective techniques like SQL injections. It exploits vulnerable website content management systems (CMS) to extract user databases containing logins, hashed passwords, and tables from accessible databases.

GambleForce is not selective in its targets but collects hashed and plain text credentials. This suggests a broader motive beyond targeted attacks, possibly amassing data for future exploits or selling on the dark web.

The threat actors aim to exfiltrate any available information within targeted databases, such as hashed and plain text user credentials. The group’s actions with the stolen data remain unknown.

In an attack targeting Brazil, GambleForce exploited CVE-2023-23752, a vulnerability in the Joomla CMS, and snatched data directly from contact form submissions, showcasing their adaptability and willingness to improvise.

Further probing revealed that GambleForce uses open-source tools like dirsearch, redis-rogue-getshell, and Tinyproxy for directory brute-forcing, web traffic intercepting, and SQL injections to exploit vulnerabilities in database servers. Their preferred tool is sqlmap, a pentesting tool that exploits SQL injection vulnerabilities. 

Researchers also found Cobalt Strike, a popular pen-testing framework, on their server, showcasing commands in Chinese. It is worth noting that recently Chinese scammers have wreaked havoc by creating cloned versions of legitimate websites and redirecting visitors to gambling sites. 

In November 2023, Hackread.com reported about the activities of Chinese hackers in which MindaNews, a Philippine newspaper, discovered a Chinese clone of its website (mmart-inn.com) that has been illegally replicating the newspaper’s content for two years, with the most recent translation being from February 2023.

In its blog post, Group-IB’s Threat Intelligence wrote that its researchers shared the recent findings with its 24/7 Computer Emergency Response Team (CERT-GIB), which took down the cybercriminals’ C2 server. GambleForce is likely to regroup/rebuild its infrastructure before launching new attacks.

Nevertheless, the case goes on to show that even the most basic security gaps can have significant consequences, underscoring the need for a layered defence strategy that prioritizes patching known vulnerabilities and implementing vital security controls.

  1. Domain Squatting and Brand Hijacking: A Silent Threat
  2. Chinese APT Posing as Cloud Services to Spy on Cambodia
  3. Chinese APT spying on Vietnam military with FoundCore RAT
  4. Hackers attack Casino’s fish tank thermometer to obtain data
  5. ChatGPT Clone Apps Collecting Personal Data on iOS, Play Store

[ad_2]
Source link

Samsung to keep Galaxy S24 prices unchanged from S23

0
[ad_1]

Samsung is gearing up to launch the Galaxy S24 series in about a month. Rumors say the new flagships will debut on January 17, 2024. Leaks have already revealed detailed specifications, features, and design of the devices. While there aren’t many hardware upgrades to look forward to, the firm has invested big in software, particularly in on-device AI features. If a new rumor is accurate, these improvements won’t add to the prices of the phones.

Galaxy S24 phones tipped to cost the same as Samsung’s 2023 flagships

According to a new report from the Korean publication hankyung.com, Samsung doesn’t plan to raise the prices of the Galaxy S24, Galaxy S24+, and Galaxy S24 Ultra over their respective predecessors. The company reportedly expects the unchanged price to help boost sales as the global smartphone market recovers from a slowdown. It is aiming to sell at least 35 million units of the new flagships by the end of 2024, 4-5 million more than the Galaxy S23.

If the report is correct, Samsung’s 2024 flagship trio will debut with a starting price of $799, $999, and $1,199, respectively. This is aggressive pricing when you consider the new AI features. Leaks have revealed that the company has baked AI into the system software for almost every function. From live translation and transcription of calls and audio recordings to AI wallpapers and lockscreen effects, there are a lot of new tools to explore.

Samsung believes the Galaxy S24 will redefine the smartphone with its unprecedented on-device AI capabilities. It sees the new flagships as the “best AI phones” yet. Unchanged pricing will certainly increase the chances of success for the devices. That is if the prices remain the same in all major markets and not just in South Korea. The Galaxy S23 series saw a price increase by up to KRW 200,000 (approx. $154) in Korea but not in the US and some other markets.

A dual-chip strategy helped Samsung lower the manufacturing cost

The new report confirms the rumors that Samsung will ship the Galaxy S24 phones with two different chips. The base model and the Galaxy S24+ will feature the Exynos 2400 SoC in most parts of the world and the Snapdragon 8 Gen 3 in the US. The Ultra model, on the other hand, will be powered by the Snapdragon chip everywhere. Samsung used the Snapdragon 8 Gen 2 for the Galaxy S23 series globally.

This dual-chip strategy for the new flagships helped the Korean firm lower the average manufacturing cost—its in-house Exynos chips cost less than the Snapdragon. Effectively, it could keep the prices unchanged despite all the new features and upgrades brought by the Galaxy S24 lineup. Time will tell whether Samsung will reap the benefits of this aggressive pricing. Just over a month to go now for the official launch.


[ad_2]
Source link

Acer’s latest gaming laptop is powered by Intel’s Core Ultra CPUs

0
[ad_1]

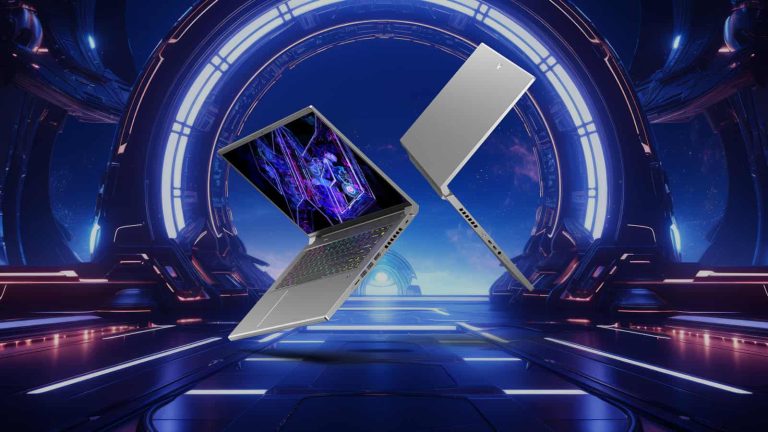
This morning Intel announced the next generation of its CPU offerings, Intel Core Ultra, and Acer is among some of the first brands to introduce laptops featuring these new chips with its announcement of the Predator Triton Neo 16. This is Acer’s latest gaming laptop and it’s poised to be one of the company’s best laptops in a while. That’s not to say it’ll have better raw performance than everything else Acer currently sells.

It’s simply been set up to deliver a great experience. And a core reason (no pun intended) for that is the Intel Core Ultra CPUs inside. These new chips are designed to deliver better power efficiency and performance. Intel says that performance-wise, the Core Ultra CPUs have 2x the performance per watt compared to 13th Gen Intel Core i CPUs. All while being more efficient with the power. The chips are also designed with a new fabrication using Intel’s 4 process technology and they offload more mundane tasks to the efficiency and low-power efficiency cores to improve battery life. In the end, Intel says this can “stretch the battery life by hours.”

In short, The Predator Triton Neo 16 should last longer on the battery even while gaming. How much longer is unclear since we haven’t tested one. But any improvement to battery life while gaming without the charger is a welcomed improvement.

Acer’s Predator Triton Neo 16 is built to perform

The Intel Core Ultra CPUs are just the beginning for this laptop. On the GPU side, Acer is outfitting the Predator Triton Neo 16 with up to an NVIDIA GeForce RTX 4070 GPU. That means DLSS 3.5 support for things like advanced ray tracing. All while the Core Ultra CPU’s Neural Processing Unit feeds in AI-enhanced visuals.

The Predator Triton Neo 16 can also come with up to 32GB of RAM and up to 2TB of internal SSD storage. Combine that with the 165Hz refresh rate display with a 3.2K resolution and you have a beast of a laptop. Naturally, there are other factors to take into account. For instance, the laptop has all these powerful components but if they’re to perform optimally, the laptop will need to stay cool.

Acer is tackling this issue with its new cooling system. The makeup includes liquid metal thermal grease on the CPU and vector heat pipes for airflow. There’s also Acer’s 5th Generation AeroBlade 3D fan to assist. All-in-all the laptop will hopefully stay relatively cool even under heavier loads.

The laptop will go on sale in March starting at $1,499

I’ve always been a fan of Acer’s gaming laptops but the company has really been bringing its A-game lately. If you’re like me and you enjoy what Acer’s been putting out, you’ll be able to grab the Predator Triton Neo 16 starting in March 2024. The laptop will have a starting price of $1,499.99. With the price going up from there depending on the configuration options you choose.

Acer appears to have stuck with a design similar to its Predator Triton 14 SE. Featuring a slim profile with a very subtle look that doesn’t go too hard on the gaming aesthetic. It does still have RBG backlighting for the keys though so don’t worry. You can check out some real-life shots of the laptop courtesy of Tom’s Hardware.

In addition to Acer, Samsung has announced its Galaxy Book 4 powered by Intel’s new chips. And Lenovo has a new IdeaPad coming with them as well.


[ad_2]
Source link

ALPHV ransomware gang returns, sorta

0
[ad_1]

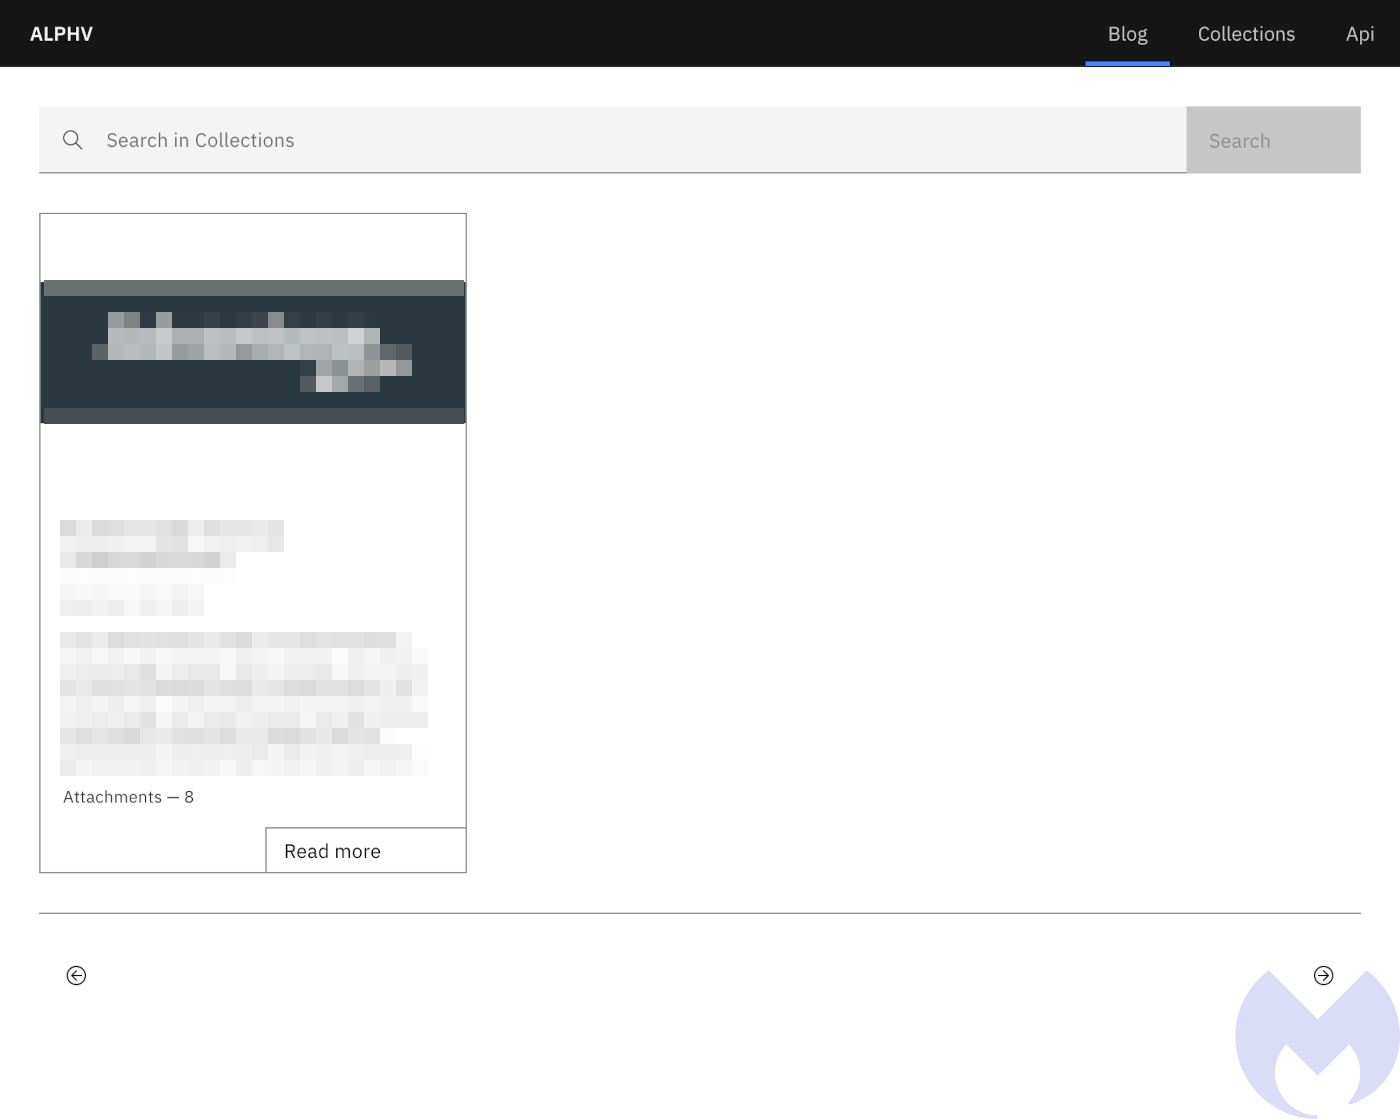
The ALPHV ransomware gang, arguably the second most dangerous “big game” ransomware operator, appears to be back in business after its infrastructure went down for five days. But all does not appear to be going well for group.

ALPHV’s dark web leak site may be back but it is only showing a single victim with no sign of any of the hundreds of others it normally lists. The solitary listing on the site is dated December 13, which is after the site was restored.

Many of the group’s negotiation links are reportedly not working either, meaning that victims looking to pay off the gang are stuck in limbo, and its likely that neither the ALPHV group, nor the affiliates who use its ransomware to carry out attacks, are being paid.

The ALPHV leak site currently lists a single victim
The ALPHV leak site currently lists a single victimcreenshot

When the gang’s infrastructure went down a week ago, many suspected the hand of law enforcement, despite no official word on the subject. According to VX Underground, APLHV’s own explanation is that it suffered a hardware failure. If the group really has lost access to the data its business relies on, then it’s now getting a first hand look at what its victims go through when they’re attacked and their data is encrypted.

ALPHV wouldn’t be the first ransomware gang to suffer problems behind the scenes. Earlier this year, Analyst1 reported that LockBit, the 800-lb gorilla in the ransomware space “cannot consistently publish stolen data … due to limitations in its backend infrastructure and available bandwidth.”

However, while it’s perfectly plausible that ALPHV is suffering hardware woes, law enforcement action can’t be ruled out. ALPHV would likely lose affiliates if it admitted to a brush with the law, so the ransomware gang is likely going to attribute the outage to something benign—whether that is true or not. Equally, the silence from the FBI could mean everything and nothing. In January, the agency took down one of ALPHV’s contemporaries, Hive, and revealed it had penetrated the group’s infrastructure six months prior:

Since late July 2022, the FBI has penetrated Hive’s computer networks, captured its decryption keys, and offered them to victims worldwide, preventing victims from having to pay $130 million in ransom demanded. Since infiltrating Hive’s network in July 2022, the FBI has provided over 300 decryption keys to Hive victims who were under attack. In addition, the FBI distributed over 1,000 additional decryption keys to previous Hive victims.

There were infiltration rumors about LockBit later in the year too, after it went inexplicably dark for two weeks. Analyst1’s undercover investigator revealed they had “received another message from a third party who indicated they may have hacked the gang’s infrastructure … I believe the gang went dark to clean up the intrusion into its infrastructure.”

Analyst1 didn’t say whether the third party that claimed to have hacked LockBit was a law enforcement agency, a criminal hacker, or another ransomware gang, but all are possible—there is no honor among thieves.

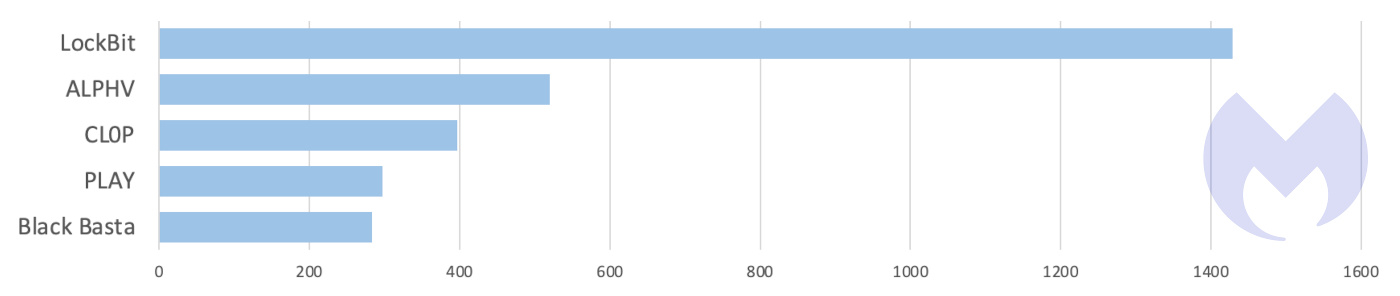
ALPHV would certainly be of great interest to both law enforcement and its rivals. Over the last 18 months it has been the second most dangerous ransomware group in the world, listing more victims on its leak site than every other group apart from LockBit.

The five most active ransomware groups by known attacks over the last 18 months.

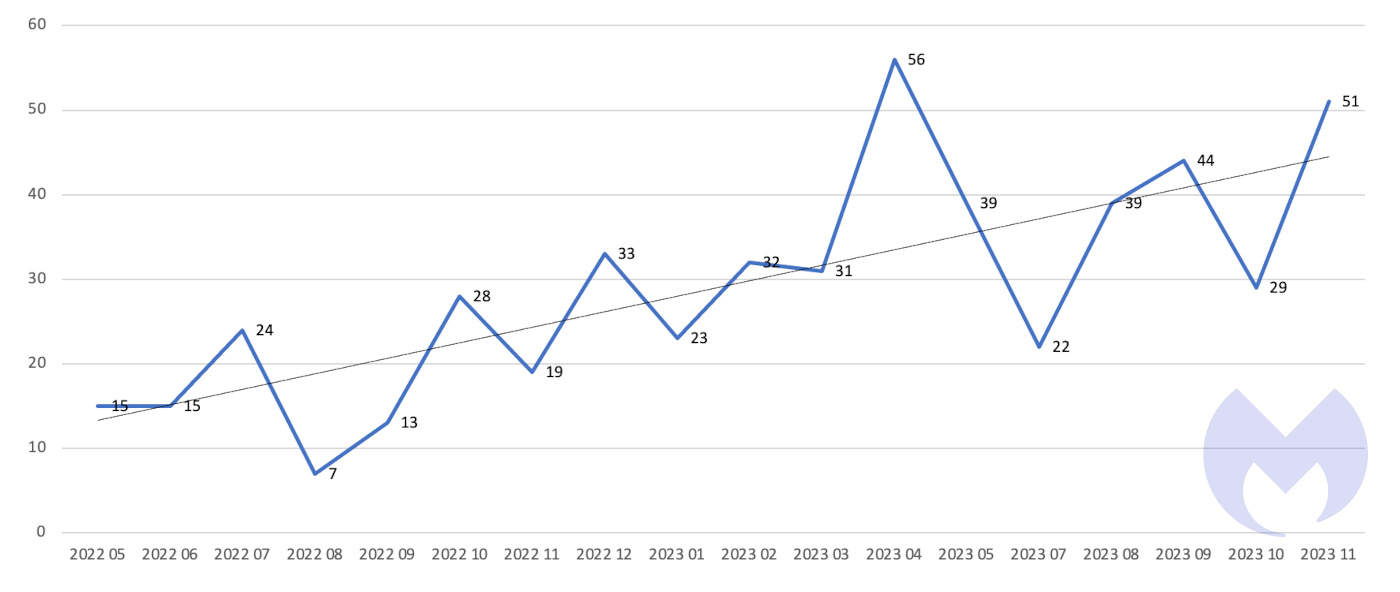
The number of known monthly attacks by the group has increased steadily over the last 18 months, too.

Known ransomware attacks per month by ALPHV

Even if another ransomware gang isn’t behind ALPHV’s woes, one of them is certainly looking to profit from it.

Bleeping Computer reports that LockBit has been attempting to recruit affiliates from ALPHV. The gang is reportedly offering the use of its data leak site and negotiation panel to ALPHV affiliates so they can resume negotiations with victims that have been disrupted. At least one victim previously listed on the ALPHV site is now listed on the LockBit site.

Whether ALPHV’s troubles are caused by tight-lipped law enforcement, an ironic lack of disaster recovery planning, or some other sleight of hand, any disruption to the ransomware ecosystem is a welcome early Christmas present in our book.

How to avoid ransomware

  • Block common forms of entry. Create a plan for patching vulnerabilities in internet-facing systems quickly; and disable or harden remote access like RDP and VPNs.
  • Prevent intrusions. Stop threats early before they can even infiltrate or infect your endpoints. Use endpoint security software that can prevent exploits and malware used to deliver ransomware.
  • Detect intrusions. Make it harder for intruders to operate inside your organization by segmenting networks and assigning access rights prudently. Use EDR or MDR to detect unusual activity before an attack occurs.
  • Stop malicious encryption. Deploy Endpoint Detection and Response software like ThreatDown EDR that uses multiple different detection techniques to identify ransomware, and ransomware rollback to restore damaged system files.
  • Create offsite, offline backups. Keep backups offsite and offline, beyond the reach of attackers. Test them regularly to make sure you can restore essential business functions swiftly.
  • Don’t get attacked twice. Once you’ve isolated the outbreak and stopped the first attack, you must remove every trace of the attackers, their malware, their tools, and their methods of entry, to avoid being attacked again.

Our business solutions remove all remnants of ransomware and prevent you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.


[ad_2]
Source link

Instagram now lets users change Stories background using AI

0
[ad_1]

Instagram is rolling out a Generative AI-powered background editing tool for Stories for U.S.-based users. It’s called Backdrop, and it can help users change the background of their Story. Meta’s Generative AI chief, Ahmad Al-Dahle, couldn’t contain his excitement. He announced the feature with a sneak peek on Instagram’s X rival platform, Threads. “Our AI media editing tool, Backdrop, is available on Instagram in the U.S.! With backdrop, you can reimagine your image’s background with just a few taps and a prompt.”

Instagram makes AI-powered background editing tool available in the U.S.

Instagram first launched Stories in 2016, and ever since then, it has received several updates to date, including AI stickers and an aesthetic overhaul for reposts. While the last few announced by Meta have been quite technical, this one is creative, fun, and a must-try for all users. It is currently available for U.S.-based users, but it will roll out to other regions gradually.

But how does this work? Once you’ve captured or uploaded content for your Story, the Backdrop tool, highlighted by an icon at the screen’s top, shows up. Clicking on the icon displays a grid of squares stretching across the screen, similar to picture editors like Photoshop. Next, a text box prompts you to “describe the backdrop you want.” You could add anything from “surrounded by puppies,” as Dahle showed, or even “surrounded by stars in a dreamy sky.” The AI tool brings diverse scenarios to life in the background.

Instagram will tell others that you edited this using AI, so no fooling around

Your Story won’t fool anyone into thinking you’re really flying in the sky (another potential prompt). Instagram tags the content with AI·Backdrop and adds a sticker encouraging others to try it, along with your description in quotation marks.

Just recently, Snapchat pushed a similar tool that lets users create and send AI-generated images. However, it is a Snapchat+ subscriber exclusive. It comes with a similar approach where users have to describe an image, and it creates one that can be shared with friends or family. Other than that, there are a couple of AI-powered editing tools.


[ad_2]
Source link

How Can DSPM Prevent High-Profile Breaches?

0
[ad_1]

In early October 2023, a DNA testing company for ancestry discovery purposes, 23andMe, disclosed that it suffered a data breach.

On the 5th of December 2023, the company shared that the data breach was more damaging than was initially reported.

At first, they claimed that the data of 14,000 users was compromised. On Tuesday, the company revealed that hackers had stolen the data of 6.9 million users.

For reference, 14 million users use their services. Bad actors obtained sensitive data from almost half the users.

Stolen information includes ancestry, family trees, names, user locations, years of birth, and relationship labels. And this data is already being sold on the dark web.

How can big companies keep their user’s data safe and avoid potential data breaches?

  1. Set multiple layers of security
  2. Learn from high-profile data breaches such as 23andMe and LastPass
  3. Manage security posture with enterprise-grade solutions that can support your growing infrastructure

Cloud Data Security Posture Management (DSPM), for example,  is a security solution designed to prevent data breaches for companies that handle a large amount of sensitive information.

What Is DSPM?

Data Security Posture Management is a cloud-based cybersecurity solution designed to discover, classify, and manage access to important data.

Also, it detects vulnerabilities and threats that could lead to exploitation or escalate into hacking incidents such as data breaches.

For companies, DSPM:

  • Uncovers which data a business has
  • Classifies information based on the type
  • Finds vulnerabilities that might compromise data
  • Enforces compliance that follows industry standards

As a result, it keeps an eye on and manages the security and privacy of data across the complete IT architecture of a company.

Discover and Classify Data

The first step of the DSPM data protection process is to find out which data is stored within the system. It continually learns which data the company has to monitor and who is accessing this data later.

Once it knows which data is there, it classifies it based on the type — to pinpoint sensitive data.

As a result, security teams have complete visibility of which data is within the system and who has access to it. They get a clear image of what needs to be protected from hackers looking to steal data.

The process of mapping and discovery is ongoing and continual. 

This is essential for large businesses that enrich their databases with new data, change it, and move from one part of the infrastructure to the next every day. 23andMe fits that profile.

Access Control Management

In October, 23andMe disclosed that the hacking was possible because users reused weak passwords. Threat actors relied on brute force attacks (specifically credential stuffing) since they had user passwords from other breaches.

Once they guessed the correct login, the hacker would access not only that user’s information but also the data of all its relatives with whom the user matched on the site.

How do you uncover the hacking activity once the bad actor is in?

Access management is one of the core capabilities of DSPM. It enforces stricter controls and makes sure that the user who is logging in is genuine. 

It enforces the best access practices — from making sure that the users use 2-factor authentication to using machine learning to finding anomalies within the infrastructure of a business.

For instance, it can enforce the zero trust model that assumes every person attempting to log in could be a cyber criminal — even if they have the right credentials.

23andMe did have 2-factor authentication, but it made this step obligatory for all users only after the breach.

Ensure Compliance

A class action lawsuit has already been filed because the hacker shared the data on hacking forums in October.

Although not all users are concerned about data privacy, thousands of users already contacted the Canadian law firm that prepared the case and asked to join the fight.

The firm claims that 23andMe didn’t adhere to proper data privacy practices and, with it, put the sensitive data of Canadian citizens at risk.

How could DSPM help?

DSPM aids big enterprises that store large volumes of data to enforce regulatory compliance across the entire infrastructure. They make sure it follows the best cybersecurity and privacy practices.

The types of compliance or the best cybersecurity practices a business needs to meet will depend on the industry. In the case of 23andMe, we’re talking about a company that holds a lot of sensitive data.

The company’s official site states that they follow the GDPR — data privacy for EU users. It’s not yet clear if they followed the prescribed practices of other relevant regulatory laws.

Data Security Fit for Enterprises

After a data breach occurs, the most a company can do is try to reduce the reputational and financial damage. The data is already out in the world — in most cases, available on hacking forums.

So how can you mitigate damage when cybercriminals have already compromised a company?

Rebuild the trust by offering free identity protection services if the sensitive data has been leaked.

Trust is difficult to rebuild, especially for companies such as 23nadMe that claim, “At 23andMe, Privacy is in our DNA.” Big promises have to be backed up with good security practices.

How a company handles a data breach is also important. 23andMe took some time until they began notifying affected users.

Data security is different for smaller companies vs those that have complex infrastructure, millions of users, and databases filled to the brim with personally identifiable information.

The truth is — both cybersecurity and data privacy are more complex and challenging at scale.

Therefore, larger enterprises that handle sensitive information require more robust security and tools that can continually monitor the entire architecture, such as DSPM.
[ad_2]
Source link

Threads finally welcomes European users

0
[ad_1]

Welcome to Threads, European users. Now, YOU can dunk on Elon Musk in style! Threads, the newest social media app from Meta. It made waves through the tech world for being just the breath of fresh air from X. It reached over 100 million users shortly after launching, but there was one market that was. According to a new report, Threads is finally available to European users.

The platform wasn’t available in Europe, but it’s not because Mark Zuckerberg doesn’t like the continent. The EU is very strict about the data privacy of its citizens, and that’s gotten in the way of Meta’s plans from time to time. This is why the company didn’t launch Threads in Europe.

Threads is now available in Europe

While the platform wasn’t available in Europe for the longest time, we knew that it wasn’t going to be forever. The company has been doing what it could to play by the EU’s rules to bring Threads to the continent. On Thursday, Mark Zuckerberg posted that Threads is now available to use in Europe.

This will undoubtedly increase the monthly active user count will sky-rocket. After it peaked at over 100 million users, the count dropped considerably. This is natural for any platform. It was more significant for Threads because it was the fastest-growing social media platform on the market.

Many people dropped off because of the lack of features. When it launched, it was bare bones without the ability to post GIFs, use hashtags, DM people, etc. However, the company is working on bringing in some useful features to the platform. It’s getting better as time goes on, and people in Europe will be able to try them out for themselves now.

As time goes on, we’ll see more changes will come to Threads. Right now, X (formerly Twitter), is still much more feature-rich than threads. It’s going to remain that way for a while, so here’s hoping that Threads will be a more complete platform.


[ad_2]
Source link

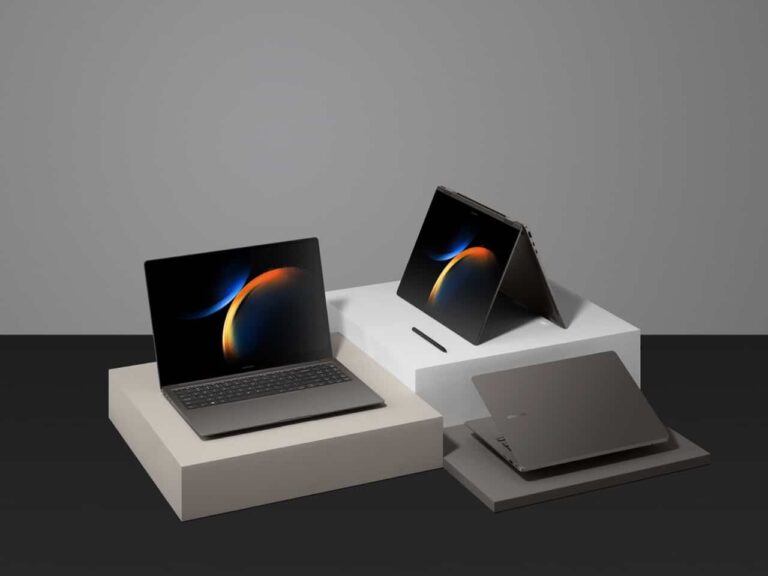
Samsung launches Galaxy Book 4 series with AI integration

0
[ad_1]

Samsung has launched the Galaxy Book 4 series. The company today announced three models of its next-gen Windows laptops: Galaxy Book 4 Pro, Galaxy Book 4 Pro 360, and Galaxy Book 4 Ultra. We were also expecting a vanilla Galaxy Book 4 and Galaxy Book 4 360 but those were missing from today’s press release.

Samsung’s Galaxy Book 4 series begins a new era of AI PCs

According to Samsung, the Galaxy Book 4 series is its most powerful and intelligent PC lineup yet. The company has empowered the new laptops with artificial intelligence (AI). Thanks to Intel’s AI PC Acceleration program and the latest Intel Core Ultra processors, the devices bring new AI capabilities that help boost productivity.

Speaking of the processor, the Galaxy Book 4 Ultra comes in Intel Core Ultra 9 and Core Ultra 7 variants. The CPU is paired with NVIDIA’s GeForce RTX 4070 Laptop GPU 8GB GDDR6 or 4050 Laptop GPU 6GB GDDR6. The laptop boasts generative AI-based creation tools powered by the NVIDIA Studio technology. It also features NVIDIA Deep Learning Super Sampling (DLSS) technology for high-quality graphics.

The Galaxy Book 4 Ultra sports a 16-inch AMOLED touchscreen display with a 16:10 aspect ratio, WQXGA+ resolution (2880×1800 pixels), 400nits of peak brightness, 48-120Hz variable refresh rate, and 120% DCI-P3 color volume. Samsung is offering up to 64GB of LPDDR5X RAM and 2TB SSD (PCle) with an expansion slot. The device features a new optimal cooling system with an 11 percent wider vapor chamber and a dual fan with uneven blade spacing.

For connectivity, you get Wi-Fi 6E and Bluetooth v5.3. There are two Thunderbolt 4 ports, a USB Type-A, an HDMI 2.1, a Micro SD, and a headphone/microphone jack. Samsung has equipped the PC with studio-quality dual microphones and AKG-tuned quad speakers featuring two 5W woofers and two 2W tweeters. You get Dolby Atmos and bi-directional AI noise canceling for crystal clear voice during video calls.

The new Samsung laptop has a 2MP front-facing camera with 1080p resolution. It features a large touchpad and a backlit Pro keyboard with numeric keys. The Galaxy Book 4 Ultra is fueled by a 76Wh battery with support for 140W USB Type-C charging. The Korean firm says it can charge from 0 to 55 percent in just 30 minutes. The company also touts “a new discrete Samsung Knox security chip that secures critical system data separately.”

The two Pro models are slightly less powerful

Samsung’s Galaxy Book 4 Pro and Galaxy Book 4 Pro 360 are slightly less powerful laptops than the Ultra. For starters, they feature Intel’s Core Ultra 7 and Core Ultra 7 processors with Intel Arc graphics. They are also limited to 32GB of LPDDR5X RAM and 1TB SSD (PCIe) with an expansion slot. The rest of the specs mostly remain unchanged, though.

You get the same set of ports, connectivity features, studio-quality dual microphones, AKG-tuned quad speakers with Dolby Atmos, and a 2MP front-facing camera. The AMOLED display also carries over unchanged, and so does the backlit Pro keyboard. However, the Pro model is available in a 14-inch variant (with the same display specs) and lacks numeric keys.

The smaller Galaxy Book 4 Pro also has a smaller battery (63Wh) than the 16-inch version (76Wh). Samsung is offering a 65W USB Type-C charger with both versions. The Galaxy Book 4 Pro 360, which features a rotatable hinge and offers a tablet-like experience, supports the S Pen. The Korean firm has included the accessory in the box. The two Pro models also feature the Samsung Knox security chip.

Samsung has readied the Galaxy Book 4 Ultra in Moonstone Gray color and the other two models in Moonstone Gray and Platinum Silver colors. All three laptops ship with Windows 11 Home. The company says the new laptops will go on sale through its official website in January 2024. They will be initially available in South Korea and will gradually make their way into more markets. Samsung will share the pricing details closer to the market release.


[ad_2]
Source link