Google app for Android will soon add a Sports widget

0
[ad_1]

Google is working on a new Sports homescreen widget for the Google app for Android. The widget will keep you up to date on the latest scores for your favorite sports teams. You can see live scores as well as upcoming and past matches, complete with the date, time, and sports league. It should soon be available to everyone.

Google readies a Sports widget for your Android homescreen

The in-development Android widget shows scores for sports teams you follow on Google Search. You can customize the list from the widget settings page or directly through Search. The widget lets you keep a single- or double-column view on the homescreen. The former view gives you a single scrollable list of games, while the latter view prominently shows one game at the top followed by a dual-columned scrollable list.

While scores are updated automatically, you can manually refresh the scores via a dedicated button at the very top of the widget, next to the “Last updated” timestamp. Tapping on a scorecard opens Google Search with the full Knowledge Graph card for the game. The widget offers scores for “Your games” and “Trending games.” The former list appears to be games in which your favorite teams are involved.

The latter, on the other hand, could be games involving sports, teams, or leagues you frequently search on Google but don’t follow. The widget settings page has a toggle to enable recommendations for such games. The whole thing leverages Dynamic Color for a consistent UI. Google can already keep you informed about your favorite sports teams via notifications. The new widget will make live scores more accessible.

Google may soon roll out the feature to everyone

The unreleased Google widget was discovered by 9to5Google during the latest APK Insight where it decompiles the APK files for Android apps to look for new features and changes. The publication could enable the homescreen widget with version 14.49.38.29 of the Google app for Android. It is currently in the beta channel.

If everything goes according to plan, Google may soon push the Sports widget to beta users (the feature is present in the latest beta version but not officially enabled). A public rollout may follow in the coming weeks. Keep the Google app updated to ensure that you don’t miss out on the latest features. You can click the button below to check for updates on the Google Play Store.

DOWNLOAD GOOGLE


[ad_2]
Source link

Google’s secret weapon in Chatbot debates

0
[ad_1]

After many months of talk, Google has finally released Gemini. This is a new AI model from Google, which the company claims outperformed GPT-3.5 in six out of eight benchmarks. GPT-3.5 powers ChatGPT and Microsoft AutoPilot. Google says that they have also specifically tuned Gemini Pro in Bard to be far more capable of understanding, summarizing, reasoning, coding, and planning.

In blind evaluations with Google’s third-party raters, Bard was found to be the most preferred free chatbot compared to leading alternatives. That is quite the feat for Google, considering how many competitors there are on the market today.

Bard, now available to English-speaking users in 170 countries today, is now powered by the new Gemini model. Google stated that Gemini would be coming to more languages and countries “soon.” It’s running on Gemini Pro, the middle tier of the Gemini Series. A “nano” and an “ultra” tier are also available for Gemini. It should be the best tier of the three, as it sits in the middle of being fast and efficient and as capable as possible.

Bard with Gemini Pro is available today for text-based prompts. Google says that support for other modalities are coming soon.

Bard is still just a chatbot, but “Bard Advanced” will launch next year

Next year, Google plans to release a preview of “Bard Advanced, which Gemini Ultra will power. This is the most capable and powerful version of Google’s new AI model. It is also the multimodal version of the model. This means that it can accept and create images, audio, and video in addition to just text.

This is where Gemini is set to really shine, outside of just text responses. The head of Google’s DeepMind, Demis Hassabis, said “we built it to be natively multimodal from the ground up. That’s one of the new capabilities it has…. the kind of seamless integration and reasoning it can do across modalities.”

One of the demos that Google showed off with Gemini was with YouTuber Mark Rober using Bard to make the perfect paper airplane. This included taking photos of his designs to get AI-provided feedback. Another example was of parents uploading pictures of their children’s homework to get help figuring out where their math went wrong.

Google believes that with Gemini, we are “one step closer to our vision of making Bard the best AI collaborator in the world.”

Google has finally caught up to ChatGPT

Last year, when OpenAI introduced the world to ChatGPT, Google was caught flat-footed. The company that had been working on AI for many, many years had nothing to compete with ChatGPT. So it rushed to put out Google Bard in March of 2023. At first, it wasn’t all that great. However, Google has continued to improve on it, with plenty of new features announced at Google I/O in May 2023.

A month after launching Bard, Google announced that it had combined its two AI labs – Google Brain and DeepMind. This brought together more than 2,000 researchers and engineers, helping to improve Bard at a rapid pace.

Now, with Gemini, Bard is taking the next step and is surpassing ChatGPT. Of course, Google is comparing it to GPT-3.5, which is not the latest version of ChatGPT right now. However, GPT-4 is a paid subscription with a waitlist. So, there are very few people actually using GPT-4.


[ad_2]
Source link

Beeper Mini is a new app for iMessage on Android that turns your phone number into a blue bubble

0
[ad_1]

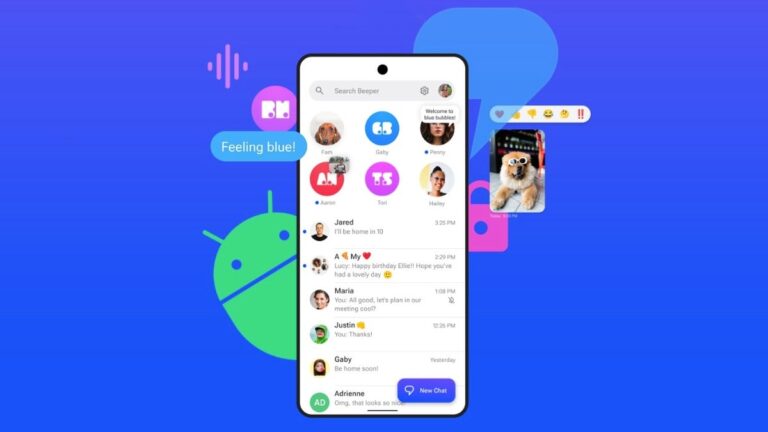
Blue bubble mania continues with the release of a new app that lets you use iMessage on Android. However, this app differs from the rest in that it allows you to use your actual phone number, instead of an email address, so you can really fool your iPhone friends into thinking you’re part of the same ecosystem.

What is Beeper Mini and how does it work?

Beeper Mini is a new app from the folks at Beeper, the unified chatting app with a mac app companion, which lets you use iMessage, Telegram, Discord, RCS, and others on your Android device. Beeper Mini, however, allows Android users to send and receive only iMessages without having to provide their Apple ID credentials. The app is still in its early stages, but it already supports many of the most important iMessage features, such as group chats, high-resolution media sharing, emoji reactions, voice messages, and more.
Setting up Beeper Mini is simple. Just download the app from Google Play, tap on “continue with Google” to sign in with Google, grant the app permission to access your SMS conversations and contacts list, and then you’re on your way. Once you’ve finished setting things up, the app will seamlessly pull in your previous SMS conversations with iPhone users and upgrade them to iMessage.

These conversations will be arranged in a list like most chat apps, though you can pin certain conversations to the top. From the home screen, you can tap on the “New chat” button, swipe right to mark a conversation as unread, or swipe left on a conversation to mute it. From the top bar, you can change your display name and profile picture or access the app’s settings, where you can modify the theme, toggle read receipts, mute sounds, toggle push notifications, or connect your Apple ID — a step that is not completely necessary.

Is this secure?

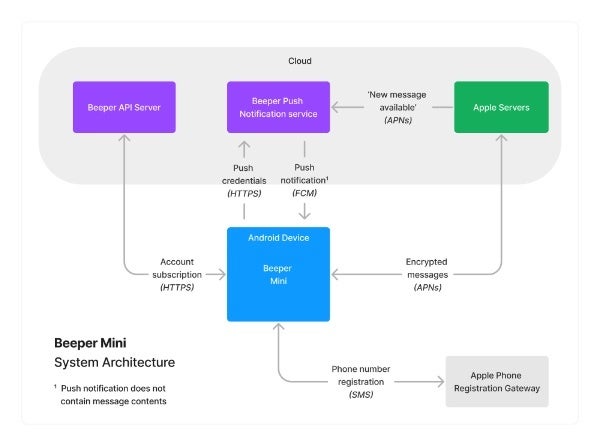
After the Nothing Chats and Sunbird debacle, you would be one hundred percent justified in questioning the security of this app, and so Beeper has taken several steps to gain the trust of its security-conscious users. The Beeper Mini team published a technical deep dive into how the app works, along with other more technical documents and source code shared by the developer.
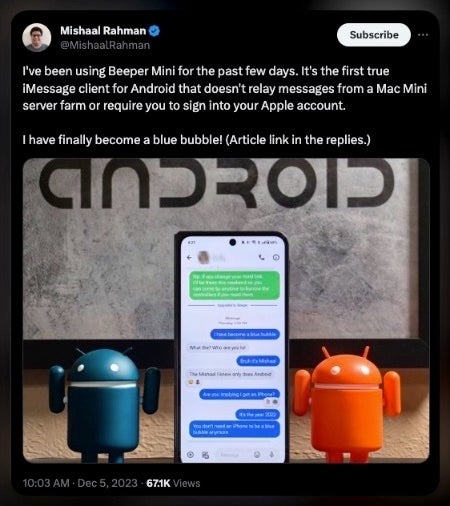
It is the opinion of those that know more about code than yours truly, such as Journalist and Android expert Mishaal Rahman, that the app is the first truly successful reverse-engineering of iMessage that doesn’t relay messages from a Mac Mini server farm or that requires you to sign in to your iCloud account.

In fact, the Beeper Mini team is so sure that their app is air-tight, that they’ve even gone as far as extending an invitation to security researchers to verify all of their claims. Boldly claiming the below and stating that they’re different from those “other apps”.


Is it free?

Beeper Mini will be free for the first seven days. After the 7-day free trial expires, the app will cost $1.99 per month. Beeper says the monthly cost of the app is so that the team can continue to improve the app by adding new features, and of course, to earn money since the app will be ad-free. This is a small price to pay if having the ability to use iMessage on Android is important to you.

What’s going to happen to the original Beeper app and my RCS messages?

Beeper Mini can work alongside the Messages app on your Android device (or whichever your default SMS/RCS app is). Beeper Mini will only handle iMessage conversations and anything that is not iMessage will continue to come in through your default SMS/RCS app. This means that you might need to use two apps — one for RCS and one for iMessage — on your Android device for now.

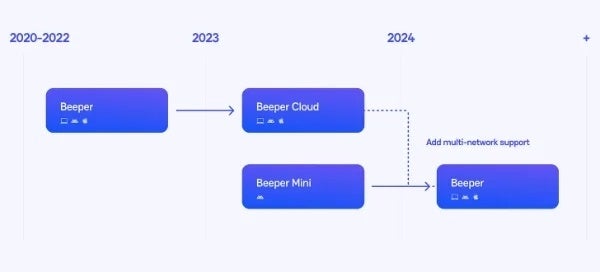
If this is an issue for you, you can always use Beeper Cloud, which is the new name for the original Beeper app. This app can incorporate iMessage, RCS, and many other messaging apps you may be using. However, please note that the cloud app will require you to sign in with your Apple ID and to have access to a Mac or PC for the initial setup. These extra steps are not needed on the Beeper Mini app since it connects directly to the remote network instead of using a server.

However, Beeper’s product roadmap states that Beeper Mini will continue to expand by adding more iMessage features such as importing past chat history, Facetime audio and video calls, and scheduled messages. Additionally, the app will gain support for Android OS chat bubbles, SMS, WhatsApp, and Signal, plus the other 10 non-encrypted chat networks that are currently supported on the Beeper Cloud app — among other planned features.

Eventually, Beeper Mini will replace Beeper Cloud and it will all become just one app again called “Beeper.” A new unified messaging app that uses a more advanced security protocol and was developed with Android’s Material Design in mind. You can download the app right now from the Google Play Store without having to go through a waitlist.

[ad_2]
Source link

New Malware Attacking MacOS Users

0
[ad_1]

Researchers have uncovered a new Trojan-attacking macOS user that is associated with the BlueNoroff APT group and their ongoing RustBucket campaign. 

As a subgroup of Lazarus, BlueNoroff possesses reverse engineering expertise because they spend time analyzing and patching SWIFT Alliance software as well as breaking apart legitimate software to uncover ways to steal a significant amount of money.

This financially driven threat actor targets ATMs, POST software and cryptocurrency businesses, banks, casinos, and fin-tech organizations. Major financial attacks, such as the theft of the Bangladesh Central Bank, were associated with this actor.

BlueNoroff Targeting macOS Users

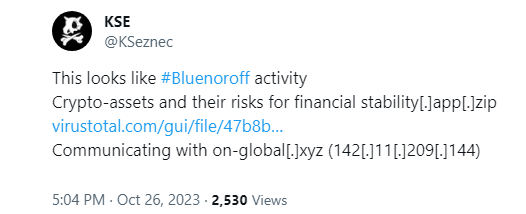
The new loader variation was initially mentioned in a post on X (formerly Twitter).

The new loader variation mentioned on X

A malicious payload was disseminated via earlier RustBucket versions using an app that pretended to be a PDF viewer. 

According to Kaspersky, this new type was discovered within a ZIP package containing a PDF file with the title “Crypto-assets and their risks for financial stability,” and a thumbnail of the matching title page.

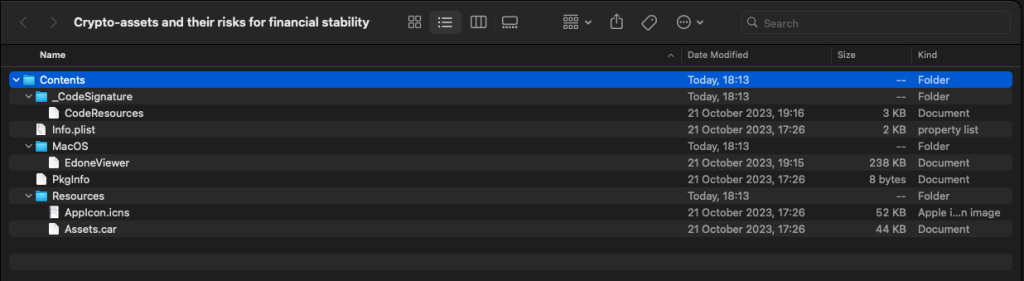
App structure
App Structure

According to researchers, it’s unclear exactly how the archive spread. The targets may have received an email from the criminals, similar to previous attacks. At the time of discovery, the app’s signature was still valid, but the certificate has since expired. 

“EdoneViewer,” an executable in universal format with versions for Apple and Intel silicon chips, was written in Swift. The main function, CalculateExtameGCD, is responsible for decrypting the XOR-encrypted payload. 

The app attempts to reduce the analyst’s attention by sending irrelevant notifications to the terminal while the decryption procedure is underway.

The .pw file is a Trojan that was discovered; it is a universal format file, just like the loader. The file collects and communicates to the C&C the following system information:

  • Computer name
  • OS version
  • Time zone
  • Device startup date
  • OS installation date
  • Current time
  • List of running processes

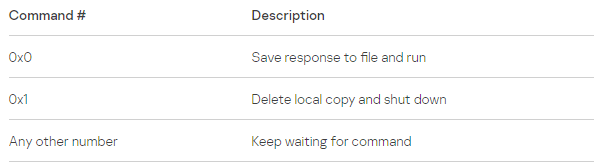
In response, the Trojan expects one of three commands:

However, during the investigation, researchers did not get a single command from the server, which prevented them from learning the content for the next attack phase. Right now, the majority of anti-malware programs can identify the Trojan.


[ad_2]
Source link

Adobe ColdFusion Flaw Used by Hackers to Access US Govt Servers

0
[ad_1]

Authorities urge Adobe ColdFusion customers to promptly install patches and update their systems.

The Cybersecurity and Infrastructure Security Agency (CISA) has issued a Cybersecurity Advisory (CSA) alerting organizations to the exploitation of a critical vulnerability in Adobe ColdFusion by unidentified threat actors.

The vulnerability, CVE-2023-26360, affects Adobe ColdFusion versions 2018 Update 15 (and earlier) and 2021 Update 5 (and earlier), as well as older ColdFusion installations that Adobe no longer supports.

Exploitation of CVE-2023-26360 allows threat actors to execute arbitrary code on affected systems, posing a significant security risk. The vulnerability was added to CISA’s known exploited vulnerability (KEV) catalogue right after its discovery, and an April 5 deadline was given to agencies to fix the issue. 

Adobe ColdFusion is a widely used software suite for web application development. Hackread has been reporting this vulnerability ever since it was discovered in March. We reported in August 2023 that this critical remote code execution (RCE) flaw, which impacts both Windows and macOS platforms, allows attackers to seize control of affected systems, making it a high-severity cybersecurity risk. Adobe released security patches to address the following vulnerabilities:

  • APSB23-40
  • APSB23-41
  • APSB23-47

However, FortiGuard Labs observed continued exploitation attempts at that time, indicating that some users had not yet applied the patches.

Now, the same vulnerability has been exploited by unidentified hackers to gain access to two systems within a Federal Civilian Executive Branch (FCEB) agency. Reportedly, the FCEB was running outdated versions, including ColdFusion, which made it vulnerable to the exploit. The hackers were able to gain initial access to two public-facing web servers within the agency’s pre-production environment.

At least two public-facing servers within a Federal Civilian Executive Branch (FCEB) agency were targeted with this vulnerability between June and July 2023. Here are the details of the attacks:

June 2: Initial access, reconnaissance activities (local/domain admin information, network configurations, user details), and deployment of a remote access trojan (RAT). Attempts to exfiltrate data, obtain credentials, download data from C2 infrastructure, and change policies were unsuccessful.

June 26: Attackers connected through a malicious IP address, exploited the vulnerability, and analysed running processes. They navigated the filesystem, deleted logs, and executed malicious code designed for ColdFusion versions 9 and below (targeting usernames, passwords, and URLs).

The code could enable future attacks and upload additional files from an unknown source. Password decryption was not possible due to the agency’s newer ColdFusion version. Attempts to conceal the web shell also failed.

While the hackers could insert malware and launch a reconnaissance campaign, there is no evidence of data exfiltration or lateral movement. The agency removed the compromised servers from the network within 24 hours of receiving the alert. CISA is yet to clarify whether the two attacks originated from the same operators.

  1. 68% of US Websites Exposed to Bot Attacks
  2. Fake Lockdown Mode Exposes iOS Users to Malware Attacks
  3. Cyberattack Defaces Israeli-Made Equipment at US Water Agency
  4. Hackers Leak Thousands of Idaho National Lab Employees’ PII Data
  5. USPS Delivery Phishing Scam Exploits SaaS Providers to Steal Data

[ad_2]
Source link

Google Calendar is set to simplify event & task creation

0
[ad_1]

Google Calendar for Android may soon get a much-needed quality-of-life update. The company is readying chips to quickly switch between Event and Task when creating a new calendar entry. Currently, you have to decide up-front whether you want to add an event or a task. If you accidentally pick the wrong option, you will have to start over and lose all the information you have already entered.

Google Calendar will make it easier to switch between Event and Task

Google’s Calendar app is a powerful tool for keeping track of events and tasks. Along with calendar events, it shows tasks from the Google Tasks app. Creating new entries is fairly simple too. You tap on the “Plus” FAB (floating action button) in the bottom right corner of the screen, select between Event and Task, and proceed to enter the details such as reminder time, repeat settings, and more.

However, the current method has a quirky flaw that can be annoying at times. You cannot switch between Event and Task once you start entering the details. The option you selected from the FAB is final. If you incorrectly picked one when you meant the other, you must go back and start afresh. Details you have already entered are lost and cannot be preserved.

Google is fixing this with new chips for Event and Task on the creation page. The chips appear below the Title field at the top. The default option is Event but you can quickly switch to Task with a tap. Most importantly, this switch doesn’t erase the information you have typed up, including the title and date. Even if you select the wrong option at first, you can correct your pick without losing anything you have entered before.

The chips are still in development

The new chips were spotted inside version 2023.48.0 of the Google Calendar app for Android. The feature isn’t live for users but app researcher @AssembleDebug could enable it. Subsequently, 9to5Google got it up and running. This suggests the feature is almost ready for a public rollout. However, there’s no timeline available yet. We will let you know when we have more information.

Meanwhile, make sure to keep the Calendar app updated to get new features early. The existing FAB isn’t going away, so there’s no change to how you do things currently. But if you ever need to quickly change a calendar entry from an event to a task, the new chips will come in handy. You can click the button below to install the latest version of Google Calendar from the Play Store.

DOWNLOAD GOOGLE CALENDAR


[ad_2]
Source link

Google just announced Gemini, its GPT-4 competitor!

0
[ad_1]

The battle between Google and OpenAI just got more intense, as Google finally released its answer to OpenAI’s GPT-4. It’s something that we’ve been waiting for, as its launch was actually delayed until January 2024. Well, it looks like there’s no delay, as Google just announced Gemini, its latest multimodal AI model.

Google Bard is already pretty powerful, but the company wanted to create something much more capable. At the beginning of the generative AI race, it was all about creating the most powerful AI chatbot. However, times have changed over the year since ChatGPT launched. Companies are all looking to create the most capable all-in-one AI model that can create text and images.

Google just announced Gemini, and it’s pretty powerful

Gemini is a major step forward for Google’s AI, and it doesn’t only go up against GPT-4, it also goes up against human brains- scary, right? Google ran Gemini through some fundamental benchmarks that pit it against human-level thinking, and it was able to make history. It’s the first model to ever best human experts in the MMLU (massive multitask language understanding benchmark; it scored 90.0%.

Below, we see a table with eight benchmarks. The table has Gemini’s scores compared to GPT-4’s scores, and we see it best the latter in most of them.

gemini benchmark

The one area where it fell to OpenAI’s model was in the “common sense reasoning for everyday tasks” area. While it scored lower, it wasn’t by much. We can bet that Gemini has plenty of common sense.

What can Gemini do?

The main difference between Gemini and Bard is the fact that the former is multimodal. This means that it can understand and give you results that are different forms of media. It’s built from the ground up to be multimodal, so the image, text, and audio models will seamlessly communicate in order to deliver the most relevant response.

This also means that it will be able to use different forms of media as input. Most models are only trained on text. As stated by Meta’s chief AI scientist, Nick Clegg, during a recent Meta event, “Text is a very poor source of information.” The ability of Gemini to understand so many different forms of media lets it understand the world that much more efficiently.

Three sizes fit all

Gemini will come in three different sizes depending on what you’re going to be using it for. The largest size is called Gemini Ultra, and it will be for the most complex and taxing tasks. You’ll expect enterprise-level entities to benefit from this model. Ultra should have access to all of the model’s features.

Next, we have Gemini Pro. This is the sweet spot of the three tiers. So, you can expect to get a fair amount of power with just the right number of compromises to keep it lightweight enough. It seems like this will be the most effective for advanced tasks; maybe people making a start-up could benefit the most from it.

Lastly, we have Gemini Nano. As you can tell by the name, it’s the smallest and most power-efficient model. Google says that this is the most efficient model for on-device AI tasks. In fact, the Google Pixel 8 will get access to this model.

Availability

This multimodal model will have a multi-stage rollout. Today, Google is releasing a “fine-tuned” version of Gemini Pro for Bard. This is the biggest update to Bard since its launch, and users should see an improvement in the chatbot. This is launching in English in more than 170 countries.

Also today, Google will launch Gemini Nano to the Pixel 8 Pro. This will only boost the phone’s AI power. Bear in mind that we’re talking about the Pro version of the Pixel 8. The regular variant won’t get it. However, you can grab a Pixel 8 Pro if you don’t want to miss out.

You’ll start seeing Gemini make it to other services like Search, Duet AI, and Chrome over the coming months. On December 13th, developers will be able to gain access to Gemini Pro.

Lastly, Google will launch Gemini Ultra sometime early next year. The company didn’t give us a specific month or fiscal quarter. We had rumors that the company delayed the entire Gemini project until January 2024. However, there’s a chance that only Gemini Ultra was delayed. In any case, we can expect some major changes to come to Google’s AI landscape with the launch of Gemini.


[ad_2]
Source link

X / Twitter acknowledges and is investigating performance issues on Google Pixel devices

0
[ad_1]
X, the app and social media site formerly known as Twitter, is facing potential performance issues on Google Pixel devices, according to user reports and recent acknowledgements from Twitter itself. Users have been noticing sluggish performance, including slow loading times, image issues, and delayed tweet sending.This comes amidst concerns about the general lack of attention given to the Android version of the app compared to its iOS counterpart. The Android app has traditionally lagged behind in features, such as a dedicated tablet layout.

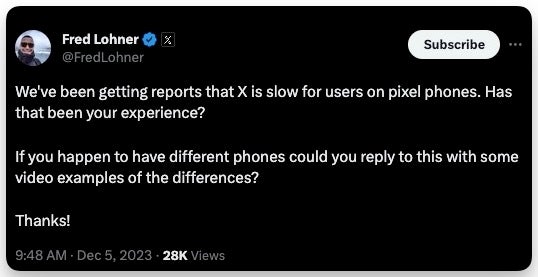
As noted by 9to5Google, Fred Lohner, a member of the Twitter/X mobile development team, acknowledged the reports on the platform and requested user examples of the slow app performance. While some users haven’t encountered major issues, others report sluggish performance even on fast internet connections. Specific issues mentioned include:

  • Slow loading times: The app takes a long time to load initial content and refresh feeds.
  • Image loading issues: Images randomly stop loading or fail to display altogether.
  • Delayed tweet posting: New tweets take significantly longer to post than usual.
Additionally, one user experienced slow notification opening times on Android 14, though this may be a broader Android issue not specific to Twitter/X. It’s important to note, though, that the overall functionality of the Twitter/X Android app is generally good. However, these reported performance problems highlight the need for optimization and improvement on Pixel devices.

With Twitter/X actively seeking user examples, it’s expected that the team will investigate and address these issues in future app updates, even though X has yet to provide a timeline for a fix. Regardless, knowing that the issue is actively being worked on, is good news for Pixel users who rely on the Twitter/X app for their social media needs. Users experiencing slow performance are encouraged to report their experiences through the Twitter/X app’s feedback channels to help identify the root cause and expedite a solution.


[ad_2]
Source link

Adobe Coldfusion vulnerability used in attacks on government servers

0
[ad_1]

The Cybersecurity and Infrastructure Security Agency (CISA) put out a Cybersecurity Advisory (CSA) to alert government agencies about cybercriminals using a vulnerability in Adobe Coldfusion to gain initial access to servers.

Adobe ColdFusion is a platform for building and deploying web and mobile applications. It can often be found on internet-facing servers.

The Common Vulnerabilities and Exposures (CVE) database lists publicly disclosed computer security flaws. The exploited vulnerability is listed as CVE-2023-26360, which affects Adobe ColdFusion versions 2018 Update 15 (and earlier) and 2021 Update 5 (and earlier). The vulnerability is an Improper Access Control vulnerability that could result in arbitrary code execution in the context of the current user. Exploitation of this issue does not require user interaction.

A patch for this vulnerability has been available since March 14, 2023. As we reported at the time, Adobe stated it was aware  that CVE-2023-26360 had been exploited in the wild in very limited attacks.

The due date for patching the vulnerability set by CISA was April 5, 2023. The problem is that the vulnerability also affects ColdFusion 2016 and ColdFusion 11 installations, which have reached end-of-life (EOL) and are no longer supported with security patches.

According to the CSA, CISA now has confirmation that the vulnerability has been used in attacks on two Federal Civilian Executive Branch (FCEB). An analysis of network logs has reportedly confirmed the compromise of at least two public-facing servers within agencies’ environments between June and July 2023. Both servers were running outdated versions of the software that were vulnerable due to several unpatched flaws.

The investigation learned that it was a reconnaissance attack, and there was no evidence of data theft or lateral movement in the network. After initial access, the criminals started process enumeration to obtain currently running processes on the web server and performed a network connectivity check, likely to confirm their connection was successful.

In the CSA, CISA shares several indicators of compromise (IOCs) and tactics, techniques, and procedures (TTPs) used in the two attacks. It is not clear whether they were done by the same threat actor.

Mitigation

CISA recommends organizations:

  • Upgrade all versions affected by this vulnerability.
  • Prioritize remediation of vulnerabilities on internet-facing systems.
  • Prioritize secure-by-default configurations, such as eliminating default passwords and implementing single sign-on (SSO) technology via modern open standards.
  • Employ proper network segmentation, to separate internet-facing servers from systems that are crucial or contain sensitive information.
  • Deploy application-aware network defenses to block improperly formed traffic and restrict content.

And a lot of other security measures that are less threat-specific.

From our end we’d like to add:

  • Block common forms of entry. Create a plan for patching vulnerabilities in internet-facing systems quickly; and disable or harden remote access like RDP and VPNs.
  • Prevent intrusions. Stop threats early before they can even infiltrate or infect your endpoints. Use endpoint security software that can prevent exploits and malware used to deliver ransomware.
  • Detect intrusions. Make it harder for intruders to operate inside your organization by segmenting networks and assigning access rights prudently. Use EDR or MDR to detect unusual activity before an attack occurs.
  • Stop malicious encryption. Deploy Endpoint Detection and Response software like ThreatDown EDR that uses multiple different detection techniques to identify ransomware, and ransomware rollback to restore damaged system files.
  • Create offsite, offline backups. Keep backups offsite and offline, beyond the reach of attackers. Test them regularly to make sure you can restore essential business functions swiftly.
  • Don’t get attacked twice. Once you’ve isolated the outbreak and stopped the first attack, you must remove every trace of the attackers, their malware, their tools, and their methods of entry, to avoid being attacked again.

We don’t just report on vulnerabilities—we identify them, and prioritize action.

Cybersecurity risks should never spread beyond a headline. Keep vulnerabilities in tow by using ThreatDown Vulnerability and Patch Management.


[ad_2]
Source link

Android 14 update available for Galaxy Tab S9 FE, Galaxy M33

0
[ad_1]

Another day, another Samsung device received Android 14. Three of them, to be precise. The Galaxy Tab S9 FE, Galaxy Tab S9 FE+, and Galaxy M33 are all picking up the big update today, with One UI 6.0 on top. The company has already updated about 30 other Galaxy devices to Android 14.

Galaxy Tab S9 FE receives Android 14 less than two months after launch

Samsung released the Galaxy Tab S9 FE series on October 16. The two premium Fan Edition (FE) tablets came with Android 13 onboard. Less than two months after they first hit the market, the devices are jumping to Android 14. The Korean firm is rolling out the big update in Europe with the firmware build number X516BXXU1BWK9 for the base model and X616BXXU1BWK9 for the Plus.

The Galaxy Tab S9 FE and Galaxy Tab S9 FE+ are receiving the November 2023 Android security patch with this update. Last month’s security release contains more than 60 vulnerability patches, five of which are confirmed to be critical issues. However, these security fixes are of little interest in the grand scheme of things. After all, Android 14-based One UI 6.0 is a massive update with tons of goodies.

Samsung has made some UI adjustments to make the Quick Settings buttons more accessible. It has also updated the notification panel and improved system animations for a smoother user experience. Additionally, One UI 6.0 improves multi-tasking features, Samsung DeX, Samsung Keyboard, homescreen widgets, Calendar, Samsung Internet, Samsung Health, and Bixby Text Call. There are new camera features and editing tools too.

This is the first of four major Android OS updates Samsung promised for the Galaxy Tab S9 FE and Galaxy Tab S9 FE+. They will receive updates up to Android 17. If you have purchased the FE tablet, you can rest assured that it will get official software support for a long time. You can check for new updates through the Settings app on your Samsung device. Go to the Software update menu and tap on Download and install.

Android 14 is available for more M-series phones

Samsung’s M-series mid-range phones aren’t available as widely as the A-series. They are primarily sold in price-sensitive markets such as India. These phones get decent support from the company. It has already updated the Galaxy M53 to Android 14. The Galaxy M33 is now following suit. The update is currently available in Russia and Ukraine with the build number M336BXXU5DWK6. A wider rollout should follow soon.


[ad_2]
Source link