Explained: Privacy washing | Malwarebytes

0
[ad_1]

Question: Who said the sentence below?

“Privacy is at the heart of everything we do.”

Answer: Sundar Pichai, the CEO of Alphabet and its largest subsidiary Google. And if you look at the recent actions Google has announced, you’d be tempted to take his word for it:

But at the same time, Google is under fire because some of its actions seem half-baked. Allegedly Google’s option to “browse privately” is nothing more than a word play.

Let’s be fair. Google makes lots and lots of money by knowing what we are looking for. And to achieve that goal it needs to gather as much information as possible about us. Maybe not specifically about us as a person, but at least about us as a group.

Data are the most coveted currency of our era, and technology giants like Facebook, Google, and Amazon are considered the behemoths of the data gathering industry. If they don’t already, they want to know everything about each and every one of us.

We’re not all equally valued though. Certain milestones in a person’s life prompt major changes in buying patterns, whether that’s becoming a parent, moving home, getting married, buying a car, or going through a divorce. Some of the most personal and secretive troves of data rank as the most expensive.

In a recent blog, privacy company Proton explained how Google is spending millions lobbying and actively fighting against privacy laws that would protect you from online surveillance.

Proton used the expression, “privacy washing” which compares Google’s disparity between actions and words to those of the world’s largest environmental polluters who portray themselves as eco-conscious, known as “green washing.“

According to lobbying reports and other records, Alphabet and its subsidiaries have spent more than $125 million on federal lobbying, campaign contributions, and trade associations since 2019.

This is done under the guise that Google wants regulators to let companies decide themselves what’s good for you and for society. But so far, big tech is consistently letting us down in this regard.

A small but telling example was a recent court case where a judge ruled that car manufacturers collecting users’ text messages and call logs did not meet the Washington Privacy Act’s (WPA) standard that a plaintiff must prove that “his or her business, his or her person, or his or her reputation” has been threatened.

In other words they can steal all the data they want as long as you can’t prove that it doesn’t hurt your business, yourself or your reputation. Does that sound fair to you?

Several US states are going through the process of passing new comprehensive consumer privacy laws, in an attempt to give American citizens more control over their personal data. Privacy advisor IAPP reckons that by 2026, 13 state privacy laws will have taken effect, as newly enacted laws in Delaware, Florida, Indiana, Iowa, Montana, Oregon, Tennessee, and Texas will join California, Colorado, Connecticut, Utah, and Virginia.

The European Union (EU) is a pioneer when it comes to privacy laws, so it’s easy to see why Big Tech has spent so much money (about $30 million in 2021) lobbying European lawmakers to protect their data gathering practices. Google has been among the most aggressive to water down or slow down the expansion of consumer protections through additional regulations — in particular the Digital Markets Act, Digital Services Act, and ePrivacy Regulation. Google happily bragged about stalling the ePrivacy Regulation, which would crack down on tracking cookies.

It’s common for industries to lobby lawmakers on issues affecting their business. But there is a massive disparity in the state-by-state battle over privacy legislation between well-funded, well-organized tech lobbyists and their opposition of relatively scattered consumer advocates and privacy-minded politicians, The Markup has found.

So, Sundar Pichai, we would like you to put your money where your mouth is. And make some real changes to improve our privacy, rather than engage in privacy washing.


We don’t just report on threats – we help safeguard your entire digital identity

Cybersecurity risks should never spread beyond a headline. Protect your and your family’s personal information by using Malwarebytes Identity Theft Protection.


[ad_2]
Source link
Snapdragon 8 Gen 3 gets hot while benchmarking

0
[ad_1]

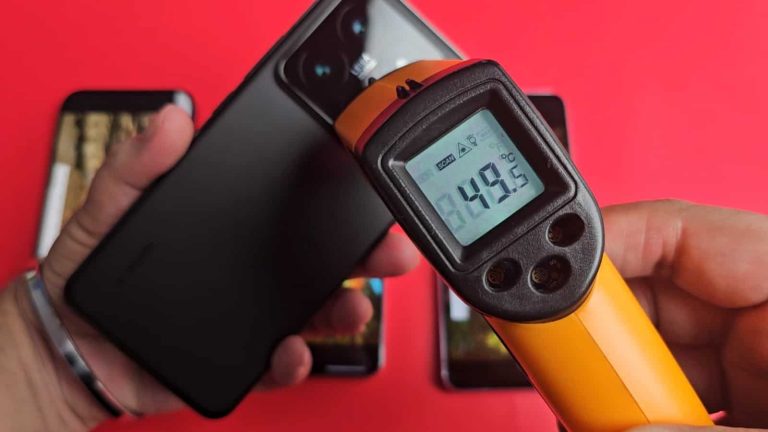
The Snapdragon 8 Gen 3 got quite hot while benchmarks were running on phones equipped with this chip. This has happened on more than one smartphone model, actually, which is a bit concerning.

The Snapdragon 8 Gen 3 got quite hot during benchmark tests, and that is concerning

On one hand, it happened on the Xiaomi 14 and Xiaomi 14 Pro while they were running benchmarks. The same goes for Vivo’s iQOO 12, actually. The Xiaomi 14 reached a temperature of 49.4°C, while its sibling went up to 49.5°C.

The iQOO 12, on the other hand, managed to beat that with 52.3°C. All of these tests were shared by Sahil Karoul on X. Needless to say, this is a bit high, and it’s a bit concerning.

iQOO 12 heat during benchmarks

On the other hand, these are benchmarks only, and they do push the SoC to its limits. It will be interesting to see how the phones behave during gaming testing and whatnot.

The Snapdragon 8 Gen 3 is not as power-efficient as its predecessor

We’ll test out the devices once the global variants arrive, of course. The Snapdragon 8 Gen 3 was announced quite recently, and based on the latest information, it is not as power-efficient as its predecessor.

It is, of course, more powerful than the Snapdragon 8 Gen 2, though. We just hope that heat won’t be an issue when it comes to this processor, as many smartphones are expected to utilize it moving forward.

The Snapdragon 8 Gen 1 did heat up a bit too much, the same cannot be said for the Snapdragon 8+ Gen 1 and Snapdragon 8 Gen 2. We were hoping for great results from the Snapdragon 8 Gen 3, but this does concern us a little bit.

A ton of smartphone OEMs are expected to utilize this processor (aside from Xiaomi and Vivo), including Samsung, Motorola, OnePlus, Sony, OPPO, Vivo, and much more. So let’s just hope that the heat won’t be a serious issue.


[ad_2]
Source link

You can now talk to ChatGPT for free

0
[ad_1]

ChatGPT is great and all; you type your query and get text-based responses. However, some people would find that to be pretty impersonal. What if you could actually speak to ChatGPT? Well, paying customers have had the ability to do that since September. Now, it’s the little guy’s turn; GPT voice is now available for free.

In case you didn’t know, OpenAI has been working on adding a voice to ChatGPT. This way, people could have access to a voice assistant that’s powered by the same LLM writing everyone’s college essays. This feature is now available in the Android and iOS apps, so you can access it now. If you haven’t downloaded the app, you can download it from your respective app store. If you already have the app, just update it.

GPT Voice is now free to use

OpenAI offered this functionality for quite some time, but it was locked behind a paywall. Using this feature is pretty straightforward. Just pretend that ChatGPT became sentient, developed one of four relaxing voices, and started talking to you. In the interface, you’ll see a little headphones icon next to the text field. When you tap on it, you’ll see the screen change.

If this is your first time, you’ll go through a one-time setup process. You’ll grant the app access to your microphone, accept all of the relevant terms of service, and choose which voice you want GPT to have.

After that, you’ll see a large dot appear on the screen. That’s the beautiful face of ChatGPT. You’ll see this dot morph along depending on what it’s doing. The dot will remain circular when it’s listening to you. When it’s “thinking” (developing the response), you’ll see it turn into a thought bubble. Lastly, you’ll see it turn into a waveform when it’s responding to you.

It’s good to see that things at OpenAI are starting to return to normal after the hectic weekend it just had. If you want to know more about that, read about the OpenAI situation.


[ad_2]
Source link
North Korean Hackers Posed as Job Recruiters and Seekers

0
[ad_1]

Two ongoing efforts, Contagious Interview and Wagemole, have been identified to target job-seeking activities connected to North Korean Hackers and state-sponsored threat actors.

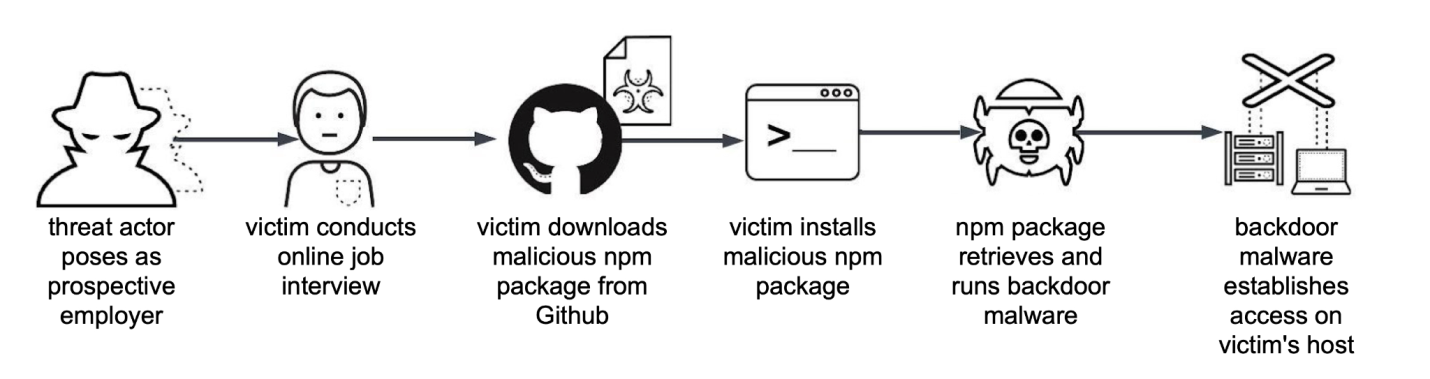
Threat actors use the interview process in “Contagious Interview” to trick developers into installing malware by posing as employers.

In the case of “Wagemole,” threat actors look for unauthorized employment with companies headquartered in the US and other countries, with the possibility of both espionage and financial gain.

Document
Free Webinar

In the upcoming webinar, Karthik Krishnamoorthy, CTO and Vivek Gopalan, VP of Products at Indusface demonstrate how APIs could be hacked. The session will cover: an exploit of OWASP API Top 10 vulnerability, a brute force account take-over (ATO) attack on API, a DDoS attack on an API, how a WAAP could bolster security over an API gateway

Overview of Contagious Interview

According to Unit 42 researchers, the threat actor behind this campaign targets software developers by impersonating a potential employer in advertisements on job search networks. The ads are frequently deceptively ambiguous or anonymous, and they don’t say who the employer is that they represent.

“The advertisements we can tie to this campaign are often anonymous or purposefully vague, with no real indicator of the employer they represent,” Unit 42 said in a report shared with Cyber Security News.

“This threat actor might also impersonate legitimate AI, cryptocurrency, and NFT-related companies or recruitment agencies.”

This threat actor might potentially contact victims via email, social media, or chat rooms on software developer community forums, just like other threat actors.

Contagious Interview Campaign

Following contact, the threat actor encourages the victim to take part in an online interview. For the interview, they probably employ online collaboration tools like video conferencing. 

The threat actor convinces the victim during the interview to download and install an NPM-based package published on GitHub.

The malicious JavaScript in the package is intended to infect the victim’s host with backdoor malware. BeaverTail is JavaScript-based malware hidden inside Node Package Manager (NPM) packages.

According to the NPM website, NPM is a global hub for numerous JavaScript projects, with 17 million developers using it.

Wagemole Campaign

In this campaign, a variety of US businesses and freelancing employment marketplaces are among the targets. This behavior is probably connected to a recent study that claims North Korea funnels wages from remote workers into its weapons programs.

For personal contact, each fake résumé contains a separate US phone number, specifically employing Voice over Internet Protocol (VoIP) numbers. Certain resumes have links to GitHub content and to a LinkedIn page.

This threat actor targets a wider range of international markets, including those in Africa, by looking for freelancing work across a variety of platforms. 

“These fraudulent job seekers have maintained multiple accounts for email, freelance websites, source code repositories, and job agency platforms,” researchers said.

“Recruiting jobs could provide more personal identity materials such as job applicant IDs, resumes, and other personal data that attackers could further use in the Wagemole campaign”.

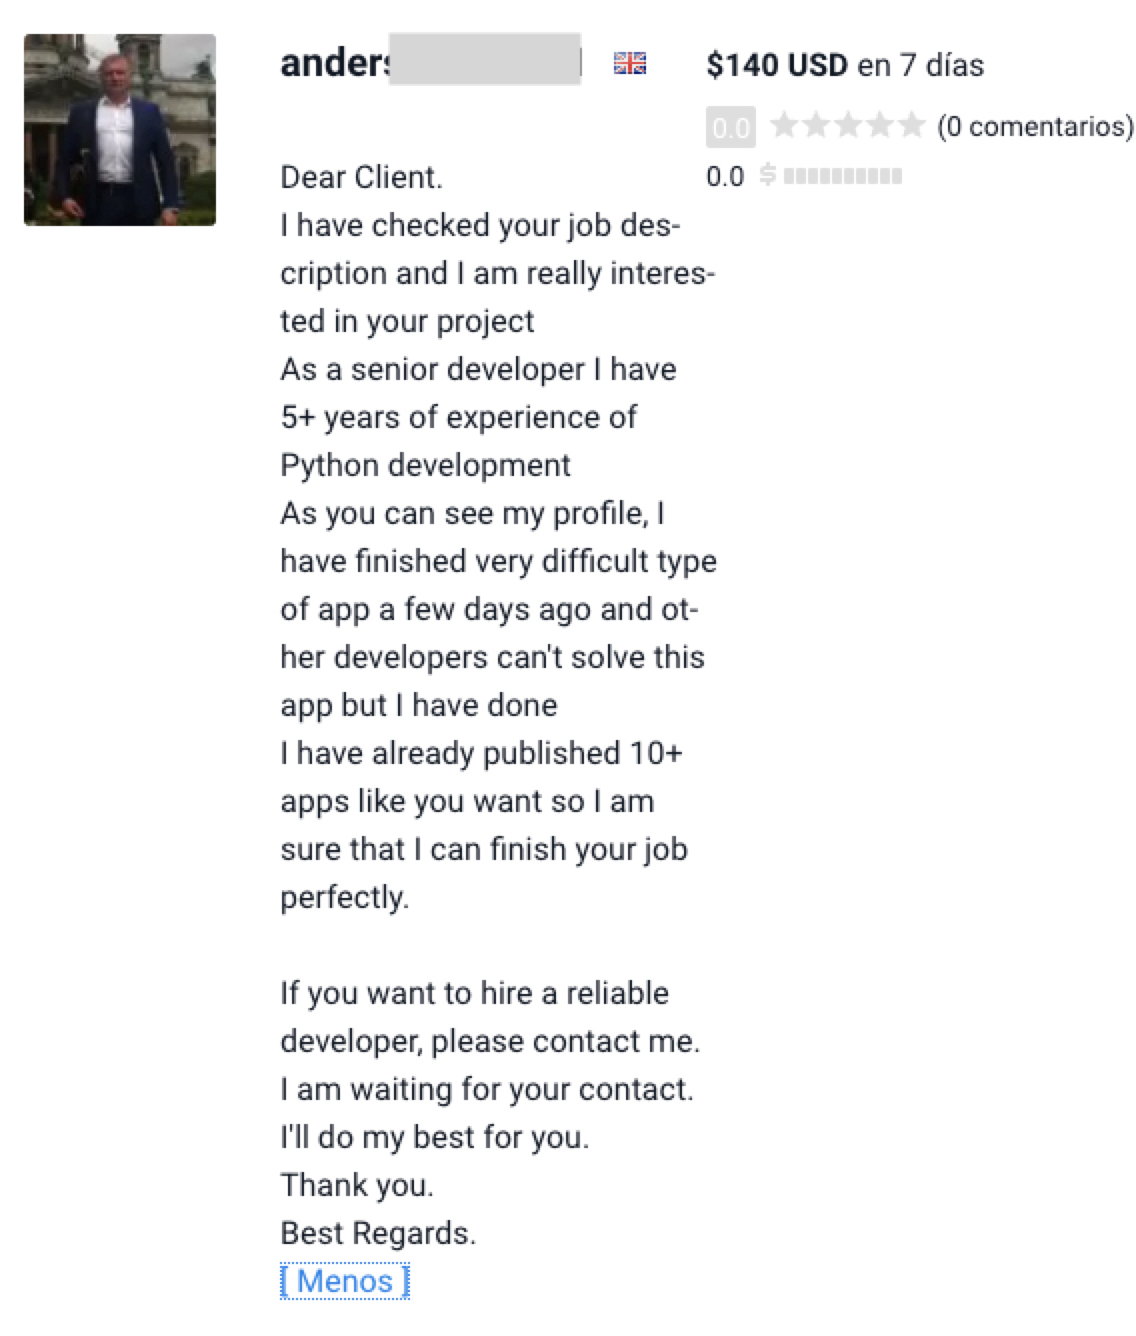
Actor seeking work on a freelance job platform

It is highly recommended for employers and job seekers to take into account the implications of remote work when interviewing or applying for such positions.

Experience how StorageGuard eliminates the security blind spots in your storage systems by trying a 14-day free trial.


[ad_2]
Source link

Malwarebytes consumer product roundup: The latest

0
[ad_1]

At Malwarebytes, we’re constantly evolving to protect our customers. These days, our products don’t just protect you from malware, we protect your identity, defend you from ads, safeguard your social media, and keep your mobile safe too.

Here are the innovations we’ve made in our products recently. Are you making the most of them?

Malwarebytes Premium

Windows

Tamper / Uninstall Protection. This allows you to password protect your software so that it can’t be removed remotely.

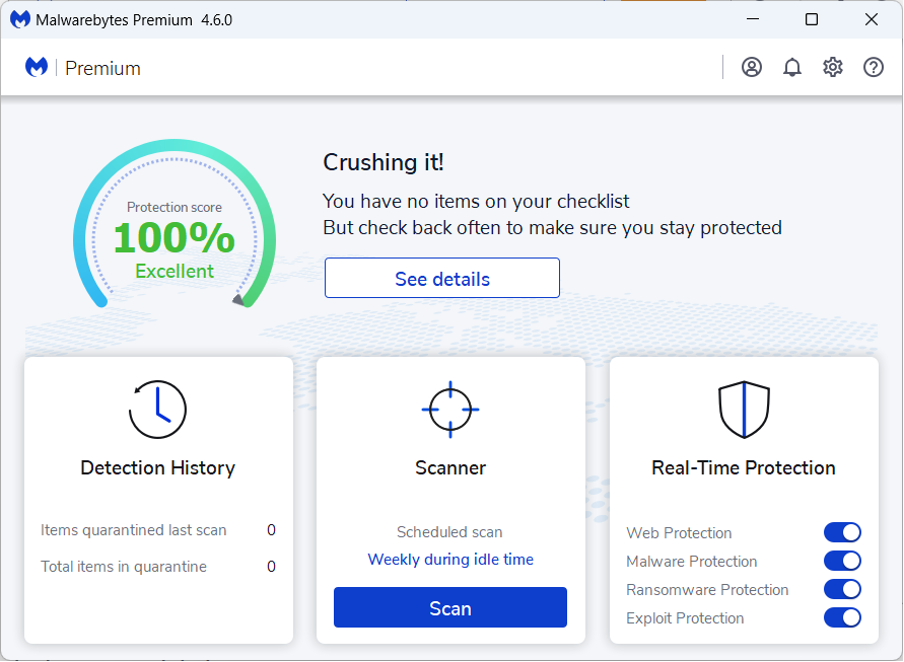
Trusted Advisor. This dashboard provides an easy-to-understand assessment of your computer’s security with a single comprehensive protection score, and clear, expert-driven advice.

Brute Force Protection. This blocks Remote Desktop Protocol (RDP) attacks, which are attempts by cybercriminals to access a computer remotely. We do this by blocking IP addresses that exceed a threshold of invalid login attempts.

Smart Scan. This enables you to schedule scans at a time when you’re not using your computer, which is best for productivity.

Mac

The old adage about Macs not getting viruses is simply not true. Macs need protection too and our Premium for Mac is now compatible with Sonoma macOS v. 14.

Mobile Security

Whether you’re on iOS or Android, our Mobile Security app just got an upgrade. Our Premium Plus plan now includes a full-featured VPN to help keep your connections private, no matter where you are. Using the latest VPN technology, WireGuard® protocol, you can enjoy better online privacy at a quicker speed than traditional VPNs.

What you get with our apps:

  • Android: Scan for viruses and malware, and detect ransomware, android exploits, phishing scams, and even potentially unwanted apps.
  • iOS: Detect and stop robocalls and fake texts, phishing links, malicious sites, and annoying ad trackers (while browsing in Safari).

Browser Guard

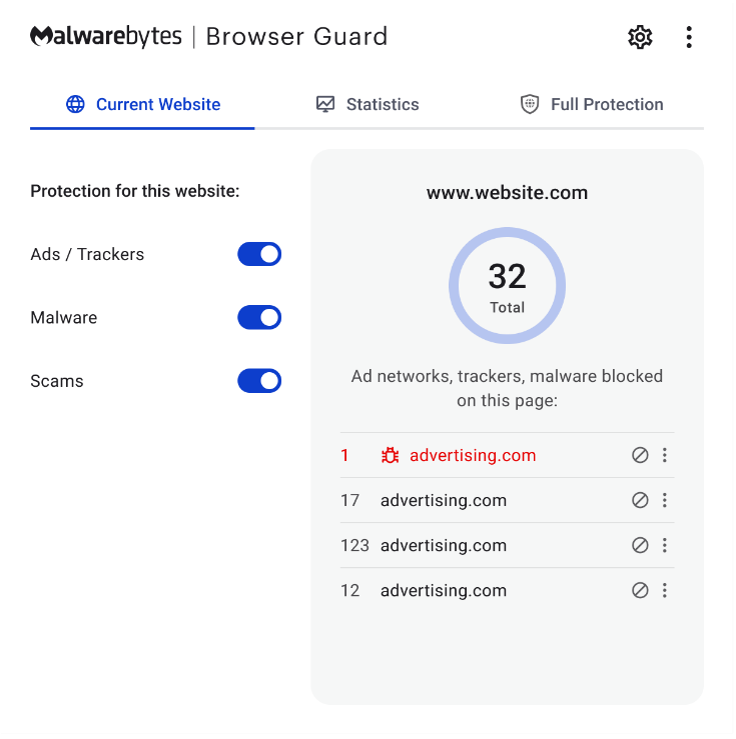
Available for both Windows and Mac, Malwarebytes Browser Guard is our free browser extension for Chrome, Edge, Firefox, and Safari that blocks unwanted and unsafe content, giving users a safer and faster browsing experience. It’s the world’s first browser extension to do this, while at the same time identifying and stopping tech support scams.

Browser Guard adds an extra layer to your personal security, on top of your antivirus or firewall. Because it’s a browser extension, it can offer protection in the browser that other means of protection do not have access to.

Screenshot of Malwarebytes Browser Guard

We’ve recently made enhancements to Browser Guard:

  • Improved protection: Stops even more threats with enhanced phishing detection. 
  • New scanning blocks: Prevents websites from scanning for vulnerable network ports. 
  • Facebook support: Blocks ads and sponsored content from appearing on Facebook feeds. 
  • Monthly overview: Summary showcases what has been blocked. 

On top of that, Malwarebytes Premium Security users (Windows only) can now take advantage of:

  • Content control: Take control of your browsing experience and define what’s appropriate for you and your family. Fully customize the content you want to block while browsing.
  • Import and export: Use your preferences and customized rules with all your browsers, even on other devices. This helps you to experience a consistent and clean web experience. Discover on this video how to transfer Malwarebytes Browser Guard settings to another browser.
  • Historical Detection Statistics: View past detections and see what we’ve protected you from.  

Want to see Browser Guard in action? Read the 25 most popular websites vs Malwarebytes Browser Guard

Malwarebytes Identity Theft Protection

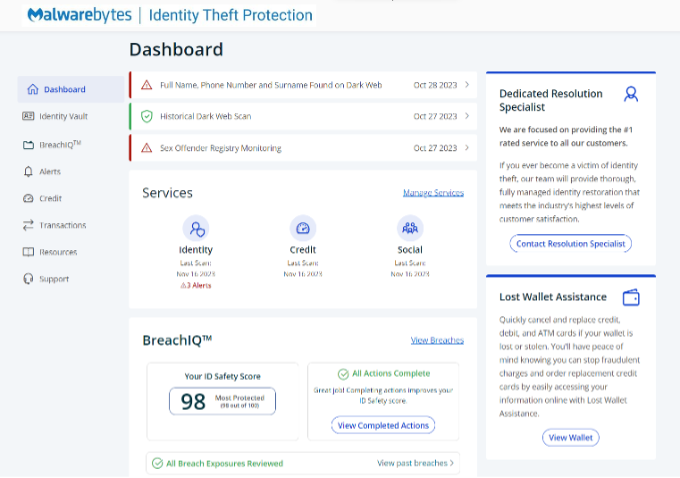
Newly released, Malwarebytes Identity Theft Protection scours the dark web for your personal information, prevents your social media account from being hacked, and even keeps an eye on your credit (US only) — and it’s all backed by an up-to-$2 million identity theft insurance. (Insurance coverage is $1 or $2 million depending on selected package (latter only available in the US plan Ultimate))

Here’s what you get (based on your selected plan):

  • Ongoing monitoring: Peace of mind that we are actively working in the background to keep you safe
  • Real-time alerts: Immediate notifications if we identify suspicious activity
  • Recommendations and best practices: Advice on how to prevent identity theft, and help if it happens
  • Identity restoration helpline and top-notch customer support.
Screenshot of Malwarebytes Identity Theft Protection

[ad_2]
Source link

RedMagic 9 Pro will offer class-leading fast charging & more

0
[ad_1]

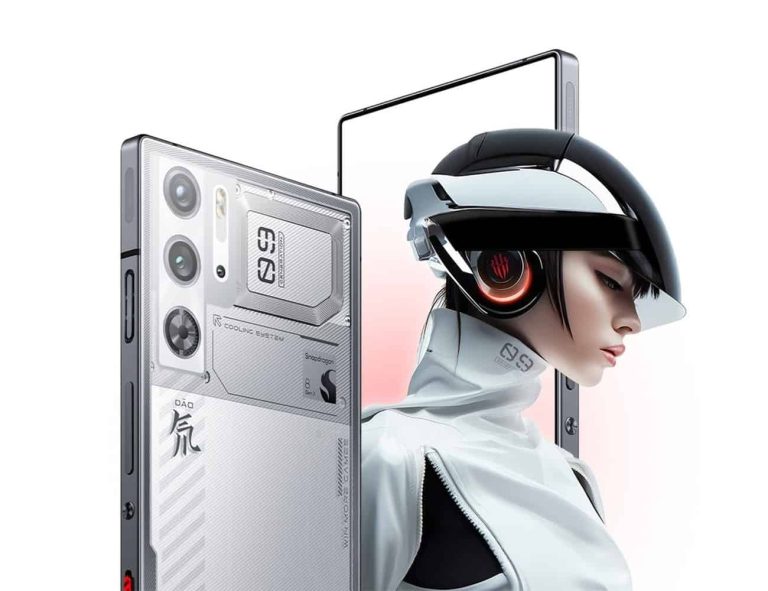
RedMagic’s new gaming smartphone will launch tomorrow, and the company did confirm some more info as we’re waiting for the launch event. The RedMagic 9 Pro will feature class-leading fast charging, much faster than its predecessors offered.

The RedMagic 9 Pro will offer blazing fast fast charging, much faster than its predecessor

This phone’s predecessor, the RedMagic 8S Pro, supports 80W wired charging in China, and 65W wired charging globally. That is plenty fast, and not many people complained. The RedMagic 9 Pro, however, will support 165W wired charging.

That will most certainly be the case in China, while we’re not sure about the global variant. This is something RedMagic officially confirmed, so it’s basically set in stone at this point.

The company also said that this charging is so fast, you can get this phone from 0 to 100% in only 16 minutes. Yes, the charger will be included in the box, and no, wireless charging likely won’t be on offer.

The BOE Q9+ display will be used

In addition to that, RedMagic also confirmed that the phone will feature the BOE Q9+ display. That panel will offer 2,160Hz PWM dimming, and this panel comes with a number of improvements over the BOE Q9 display.

It brings visual enhancements such as improvements to color deviation, better performance in low light, improved brightness, and so on. It can project 1.07 billion colors, and has a peak brightness of 1,600 nits. DC dimming and HDR10+ are also supported.

We already know what the RedMagic 9 Pro will look like. That’s something that RedMagic already confirmed. It will include an under-display camera, very thin bezels, and it won’t have a camera bump on the back.

The Snapdragon 8 Gen 3 SoC will fuel the phone, while RedMagic will use the latest and greatest RAM and flash storage. It will also have shoulder triggers for gaming, along with advanced cooling, and various other gaming features. This phone will also launch globally at some point.


[ad_2]
Source link

Sam Altman is now back at OpenAI, break out the champaign!

0
[ad_1]

Well, all the fighting has stopped, and the weekend of drama is finally over. After nearly a week of drama, Sam Altman is now back at OpenAI. This is something that we pretty much saw coming, but it’s good to see it happen.

In case you haven’t been following the news, OpenAI fired its CEO Sam Altman last Friday, and it’s been a storm of drama ever since. Hours after the news, the company’s co-founder and president Greg Brockman left the company. He and Altman started planning for a new company before Microsoft hired them.

In the process, Microsoft’s CEO Satya Nadella said that Microsoft would provide a home for everyone who left OpenAI due to Altman’s firing. That was one of the most notable things about this whole situation.

Well, the drama is over, as Sam Altman is back at OpenAI

Microsoft hiring Altman almost seems like a ploy used by a person to make their ex jealous (well, the ex and their 700 employees). Soon after we heard the news that Microsoft had hired Altman, we got the news that he was still open to returning to OpenAI. During the beginning of the week, he was still in talks with the company, more specifically the non-profit board overseeing the company, about returning.

Upon returning, that board would need to resign. The board originally consisted of four people: OpenAI Chief scientist Ilya Sutskever, Quora CEO Adam D’Angelo, director of strategy at Georgetown’s Center for Security and Emerging Technology Helen Toner, and Former GeoSim System CEO Tasha McMauley. However, shortly after the drama, Ilya Sutskever willingly left the board.

Well, according to a post on the OpenAI X account, it looks like the board was wiped clean, and a new board, consisting of Bret Taylor (Chair), Larry Summers, and Adam D’Angelo has been formed. We’re sure that this board won’t be so keen on firing Altman in the future.

So, that puts a cap on the situation now, the ordeal, as a whole, is not over. OpenAI still has to deal with the company’s financial status which upset investors probably made worse. All we can do is hope that the newly reunited company can find a solution to this issue.


[ad_2]
Source link

ChatGPT goes hands-free: Voice conversations now available for all users on iOS and Android

0
[ad_1]

In recent headlines, the spotlight has been on OpenAI and Microsoft amid the CEO saga involving Sam Altman, who was fired and then rehired days later. Amidst the high-level maneuvers at OpenAI, the owner of one of the most popular chatbots, ChatGPT, managed to introduce a new feature for its free users.

As spotted by Android Authority, ChatGPT’s latest update brings voice-based conversations to all users on the ChatGPT app, available on both iOS and Android. So, instead of typing your query, you can now simply tap the headphones button and start a conversation with ChatGPT.The AI chatbot seamlessly converts your spoken words into text, processing it through its Large Language Model (LLM). Similarly, it transforms text-based responses into spoken words, echoing back the answers to your queries. This functionality mirrors the experience of voice assistants like Siri, Alexa, or Google Assistant.

Users have the flexibility to choose from 5 distinct voices by navigating to Settings and selecting the Voice option. Additionally, there’s a wide array of over 35 languages to choose from.

The conversational feature was initially introduced in September, exclusively for ChatGPT Plus and Enterprise users. However, the latest update extends this capability to all users of the mobile app.

AI is undoubtedly making its way into the mobile tech world, with generative AI making waves in devices like the Pixel 8 and Pixel 8 Pro. Samsung, gearing up for the Galaxy S24 launch, is set to incorporate on-device generative AI features, including AI Live Translate Call, powered by Samsung’s own AI model, Gauss.

This trend is not exclusive to Google and Samsung, as anticipation builds for Apple to integrate AI into the upcoming iPhone 16. OnePlus, too, is exploring new generative AI-powered features and recently launched its own AI Music Studio, which allows you to generate songs based on prompts directly from your smartphone.


[ad_2]
Source link

Canada Government Admits Data Breach Impacting Employees

0
[ad_1]

The Government of Canada recently admitted suffering a security breach that impacted data of current and former public employees. The incident even affected the staff from the Royal Canadian Mounted Police and Canadian Armed Forces.

Canada Government Faced Data Breach Following Third-Party Breaches

Through a recent statement, the Canadian government has admitted enduring a cyber attack leading to data breach.

As elaborated, the incident didn’t directly hit the Canadian government systems. Instead, the criminal hackers breached the networks of two third-party contractors, hence causing indirect impact to the government data.

Specifically, the two services suffering the cyber attack include Brookfield Global Relocation Services (BGRS) and SIRVA Worldwide Relocation & Moving Services. Given these services’ years-long association with the Canadian government, the affected data dates back to 1999. This huge span highlights the diversity of information and affected individuals breached during the incident.

As stated in the official statement, the individuals affected by this incident include “current and former Government of Canada employees, members of the Canadian Armed Forces and Royal Canadian Mounted Police personnel.”

For now, the Canadian authorities could not identify the affected individuals. However, they believe the breached information may belong to anyone using the relocation services as early as 1999.

Nonetheless, the authorities have already taken proactive measures to facilitate impacted individuals. As stated in the statement,

Services such as credit monitoring or reissuing valid passports that may have been compromised will be provided to current and former members of the public service, RCMP, and the Canadian Armed Forces who have relocated with BGRS or SIRVA Canada during the last 24 years. Additional details about the services that will be offered, and how to access them will be provided as soon as possible.

Besides, the authorities also urge all potential victims to remain vigilant about their personal information. Specifically, they advise updating login credentials, especially for accounts with similar credentials to their BGRS or SIRVA Canada accounts, enabling MFA for all accounts, particularly those involving financial data, and monitoring their personal and financial accounts for suspicious activities.

While the Canadian authorities haven’t stated anything about the exact nature of the incident, reports suggest that SIRVA possibly fell victim to the notorious LockBit ransomware.

Let us know your thoughts in the comments.


[ad_2]
Source link

The US President Joe Biden joined Threads on his birthday

0
[ad_1]

After plummeting growth, the Meta-owned Threads is gaining more traction in app stores, and more users are joining the X rival platform. Meta CEO Mark Zuckerberg has recently said Threads has just under 100 million monthly active users. Over four months after the initial launch, more prominent users, including the President of the United States Joe Biden, are joining the platform.

Joe Biden’s first post on Threads alludes to his keynotes in the 2020 presidential victory speech. He speaks about the US situation and the “inflection point.” Biden is the third prominent member of the White House to join Threads, following Vice President Kamala Harris and her husband Douglas Emhoff, aka the second gentleman of the United States. The White House also has an official account on Threads.

The US President Joe Biden joins Threads

Kamala Harris’s first post on Threads is about her travels across the US, meeting with American people and over 100 world leaders. Likewise, Emhoff’s first post was focused on gender equity and “countering hate of all kinds.”

The White House account on Threads welcomed the President’s first post, saying, “The wait is Joe-ver.” Biden’s decision to join Threads coincides with his 81st birthday. Former President Barack Obama also posted a birthday message to Biden.

Political figures joining Threads is good news for the Meta, showing the platform is on the right track. Meanwhile, Elon Musk and X should not be happy with this. X (formerly Twitter) has been the main venue for political and prominent figures to connect with their fans and share messages.

Instagram CEO Adam Mosseri has recently said he expects Threads to become a “de facto platform” for online public conversations. Meanwhile, Mosseri tries to keep Threads away from becoming a news hub, claiming the platform is ‘not going to amplify news.”

While the White House said in a statement that involvement on Threads won’t affect the POTUS activity on X, Musk’s owned platform could see itself in a critical situation. Following the recent controversies over Musk’s public endorsement of a supposedly anti-Semitic post, Apple decided to pull its ads from the platform for an unknown term.


[ad_2]
Source link