Twitter’s offshoot Bluesky hits 2 million users ahead of expansion

0
[ad_1]

Many of you have probably heard of Bluesky at this point. Bluesky is a decentralized social media app, and technically a competitor to X. Well, Bluesky actually managed to reach 2 million users ahead of its expansion.

Bluesky has reached 2 million users, and it will soon be available to the public, kind of

Now, do note that Bluesky was founded by Jack Dorsey, Twitter’s co-founder. Those 2 million users may not seem like a lot compared to X and other social media networks, but do note that Bluesky is not available to the public, not openly.

You still need an invite in order to join Bluesky, which is the main thing that has been preventing the company from growing. Bluesky wanted to take things one step at a time, rather than risking everything falling apart.

Now, the company seems to be ready for the next step. Bluesky will soon be able to reach a much bigger audience. The upcoming public web interface will allow everyone to see the posts, even if they’re not signed in.

More changes are coming early next year

That interface will become available towards the end of this month. Early next year, the company will also open its doors for federation. We just don’t know when exactly.

Those of you who have used Bluesky thus far probably get Twitter vibes from it. That’s likely a good thing, and something that Bluesky is well aware of. It will be extremely difficult to compete with X and Threads, though.

Now, Bluesky is a decentralized social media network, kind of. It’s built on top of the AT Protocol, but registered users still must sign up via the company’s bsky.social network, so… yeah.

In addition to announcing what we said, Bluesky also wanted to highlight some other changes. The company added new features recently, such as mobile push notifications, email verification for accounts, and accessibility improvements.


[ad_2]
Source link
FortiSIEM Injection Flaw – Attackers Execute Malicious Commands

0
[ad_1]

Fortinet notifies users of a critical OS command injection vulnerability in the FortiSIEM report server that might enable an unauthenticated, remote attacker to execute malicious commands via crafted API requests.

FortiSIEM is Fortinet’s security information and event management (SIEM) solution, which assists in identifying insider and incoming threats that could pass standard defenses.

 “An improper neutralization of special elements used in an OS Command vulnerability [CWE-78] in FortiSIEM report server may allow a remote unauthenticated attacker to execute unauthorized commands via crafted API requests”, reads the advisory published by Fortinet.

Specifics of the Critical OS Command Injection Vulnerability

The OS command injection vulnerability in FortiSIEM, with a CVSS Score of 9.3, is tracked as CVE-2023-36553.

The execution of arbitrary commands on a host operating system (OS) is called command injection. Typically, the threat actor injects the commands by taking advantage of an application flaw, such as insufficient input validation.

The command injection vulnerability can result from unauthorized access, data breaches, and even system compromise.

Additionally, it was discovered that this critical FortiSIEM injection vulnerability (CVE-2023-36553) is a variant of CVE-2023-34992, another critical vulnerability previously fixed in October of this year.

In Fortinet FortiSIEM versions 7.0.0, 6.7.0 through 6.7.5, 6.6.0 through 6.6.3, 6.5.0 through 6.5.1, and 6.4.0 through 6.4.2, improper neutralization of special elements used in an OS command (also known as “os command injection“) tracked as  CVE-2023-34992 allows an attacker to execute unauthorized code or commands via crafted API requests.

Improper input sanitization allows OS command execution, which increases the risk of unauthorized data access, modification through API requests, and deletion through API requests.

Affected Products:

  • FortiSIEM 5.4 all versions
  • FortiSIEM 5.3 all versions
  • FortiSIEM 5.2 all versions
  • FortiSIEM 5.1 all versions
  • FortiSIEM 5.0 all versions
  • FortiSIEM 4.10 all versions
  • FortiSIEM 4.9 all versions
  • FortiSIEM 4.7 all versions

Solutions:

  • FortiSIEM version 7.1.0 or above
  • FortiSIEM version 7.0.1 or above
  • FortiSIEM version 6.7.6 or above
  • FortiSIEM version 6.6.4 or above
  • FortiSIEM version 6.5.2 or above
  • FortiSIEM version 6.4.3 or above

It is unclear whether the vulnerability is actively exploited in attacks in the wild. The users of Fortinet are advised to upgrade to the latest version released.

Patch Manager Plus, the one-stop solution for automated updates of over 850 third-party applications: Try Free Trial.


[ad_2]
Source link

Benchmark reveals some Galaxy Xcover 7 specs ahead of launch

0
[ad_1]

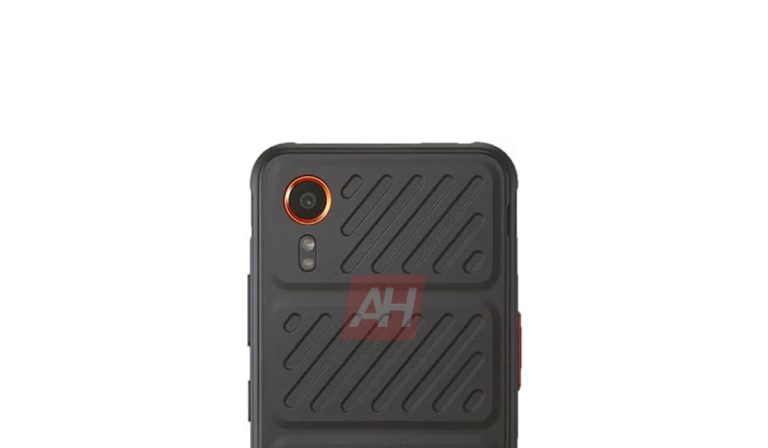
Earlier this week, we gave you an early look at Samsung‘s next rugged smartphone, the Galaxy Xcover 7, through exclusive official renders. The images revealed the phone’s design but we didn’t have its specs or a launch date to share with you. While the launch date is still a mystery, a new benchmark listing has given us a few key specs of the upcoming handset.

Galaxy Xcover 7 shows up at Geekbench

The Galaxy Xcover 7 is known to carry the model number SM-G556B. This device has popped up on the popular benchmarking website Geekbench. We can see that the unannounced Samsung phone runs Android 14 out of the box with 6GB of RAM. There may be other RAM variants (Galaxy devices usually come in multiple RAM and storage configurations), but we don’t have any evidence yet.

The Geekbench entry also confirms an octa-core chipset for the Galaxy Xcover 7, with two CPU cores operating at a maximum frequency of 2.2GHz. The other six cores operate at a 2.0GHz frequency. The chipset appears to feature ARM’s Mali-G57 MC2 GPU. As pointed out by MySmartPrice, which first spotted this benchmark listing, this could be a MediaTek processor.

The needle is pointing towards the Helio G99 or the Dimensity 6100+. These are essentially the same chipset, with the latter adding 5G cellular connectivity. So if Samsung decides to ship the Galaxy Xcover 7 with 5G, it will use the Dimensity. If not, the Helio-series chip could power the next-gen rugged Galaxy smartphone. The Korean firm is using the two processors in Galaxy A15 and Galaxy A15 5G, which are expected to break cover in the coming months.

Since these are budget phones, don’t expect a powerful performance from the upcoming Xcover model too. The Geekbench scores of 663 (single-core) and 1,867 (multi-core) already hint at a mediocre performance, though these scores don’t always reflect the real-world performance of a phone. Nonetheless, the Galaxy Xcover 7 won’t be a top performer, certainly not at the level of the Galaxy XCover 6 Pro.

It won’t compromise on ruggedness

Samsung’s next Xcover phone may be a budget offering (in the rugged segment) but it would not compromise on ruggedness. It should boast MIL-STD-810H-compliant build quality, IP68 dust and water resistance, and drop-to-concrete resistance. The device will also feature customizable hardware buttons, a removable battery, and enhanced touch sensitivity. More details about the Galaxy Xcover 7 should surface in the coming weeks as Samsung prepares for its launch.

Samsung Galaxy Xcover 7 Geekbench


[ad_2]
Source link

New features are now rolling out to Google Play Games on PC

0
[ad_1]

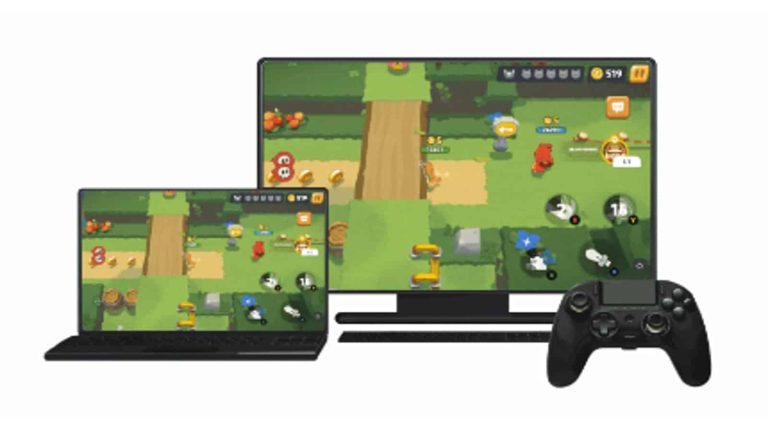
Google has taken to the Android Developers Blog to announce the new features coming to Play Games on PC. This service went into beta testing last year and rolled out after passing the testing, attracting PC users to the gaming platform. The new features rolling out to the platform include support for more gaming hardware, display improvements, and easier access.

Users will be able to utilize these new features to help improve their gaming experience on the platform. For the gaming hardware side of the upgrade, users will be able to use more game controllers and microphones. This will not only improve their play but also enable them to engage with other players through streaming games or playing online.

Gamers using a 4K resolution monitor will be able to play in better resolutions using the new dynamic display options. Lastly, accessing games directly from the Google Play Games on PC homepage is now easier. If you play Android games on your PC or if you’re planning to start playing, then you’ll find these new features impressive.

Users can now benefit from the three new features rolling out to the Google Play Games on PC platform

Google is rolling out three new features to the Google Play Games on PC platform. These features will help improve the gaming experience while playing on this platform for users. The new features bring support for game accessories, improvement to display quality, and easy access to games.

If you aren’t already aware, Google Play Games on PC is a platform that lets users experience Android games on a PC. With this feature, users can play their favourite Android games on a laptop or a PC by just accessing the Play Game on the PC platform via their browser. From here they can install games to play and enjoy from their laptop or PC.

With over 3,000 gaming titles on this platform, there is something for everybody. The catalogue is always growing with developers bringing more games to the platform. For this reason, there is a need to add controller support for users to help make gaming more enjoyable.

In addition to this new feature, players on the Google Play Games on PC platform can enjoy 4K content on their screens. Lastly, the previous struggle to find PC-optimized games is a thing of the past. This is because Google is bringing PC-optimized games to the homepage for easy access when searching for games to download and play.

The Google Play Games on PC platform is available in 120+ countries. Developers can also benefit from the new in-game ads feature that Google is making available to them. There is something for everyone with the addition of these new features to the gaming platform.


[ad_2]
Source link

Microsoft and Oppo team up to bring Phone Link to a trio of brands

0
[ad_1]

Oppo had a pretty major event this week, during which the Chinese company introduced the global version of ColorOS 14, its own take on Android 14, and provided timelines for the delivery of the beta iteration of the update.

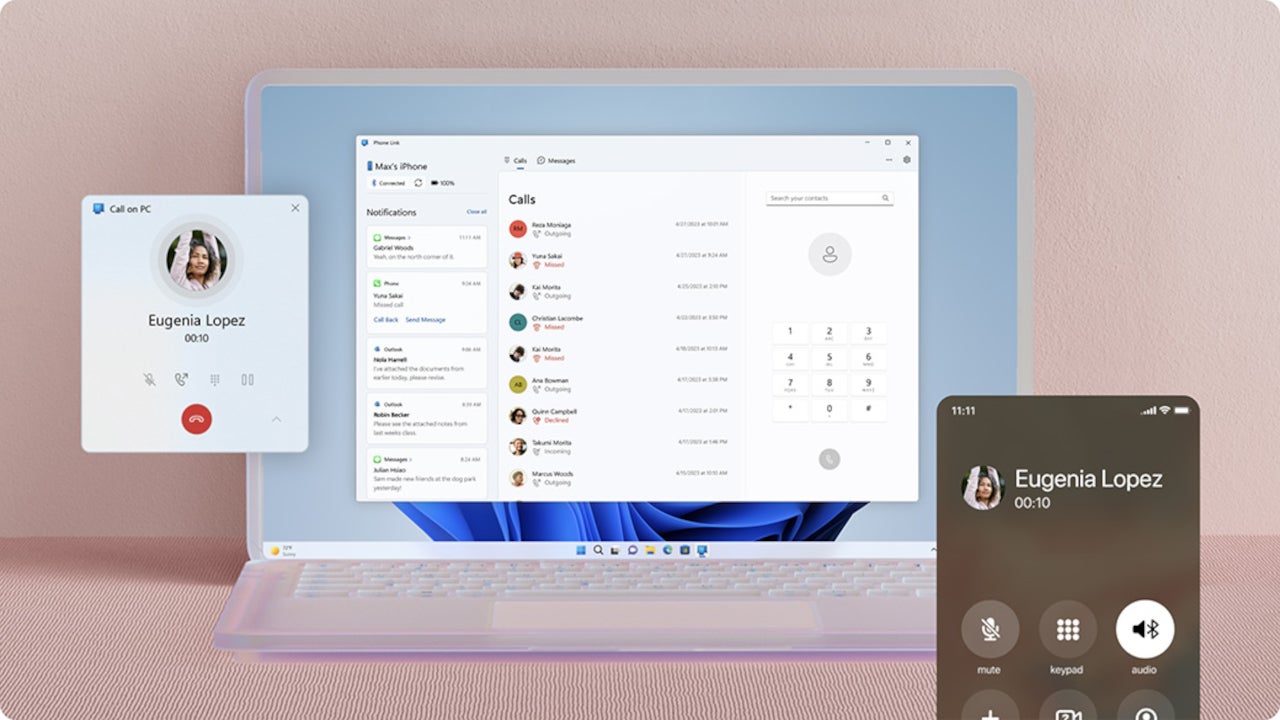
In addition, Oppo and Microsoft confirmed they have teamed up to bring Phone Link and Link to Windows support to a trio of brands: Oppo, OnePlus, and Realme (via MSPU).

Under the agreement, the OnePlus series, Oppo Find and Reno series, as well as Realme series will be getting support for Microsoft Phone Link and Link to Windows in the coming months.

It’s important to mention that the Link to Windows app will come pre-installed on select Oppo smartphones powered by ColorOS 14 or OxygenOS 14 and above. This means that none of the current phones have the feature until they’re updated to Android 14.

With Microsoft Phone Link, Oppo, OnePlus and Realme smartphone users will be able to handle their Android app (and any other content on the phone) directly from the PC via Wi-Fi connection. The app allows users to take advantage of a PCs mouse or keyboard to interact with any of the Android app installed on the phone.

Additionally, compatible phones from this trio of brands will support instant hotspot, so when these devices are near a Windows 11 PC, they will pop up in the Wi-Fi network list on the PC allowing users to connect to it instantly.


[ad_2]
Source link

20+ Companies Hacked in Massive Cyber Attack on Infrastructure

0
[ad_1]

In an alarming development, Denmark faced its most extensive cyber attack in May 2023, targeting crucial components of its energy infrastructure. 

A total of 22 companies fell victim to a meticulously coordinated attack, breaching their industrial control systems and prompting some to activate island mode operation.

This cyber onslaught marks an unprecedented scale of attack on Danish critical infrastructure, signaling a new level of threat. 

The assailants exhibited a deep understanding of their targets, successfully infiltrating 22 companies within a short timeframe, indicating a level of preparation rarely witnessed.

The sophistication of the attack prompts speculation about state involvement, with indications suggesting a possible connection to one or more nation-states. 

This revelation adds a layer of complexity to the incident, requiring careful examination of geopolitical implications.

SektorCERT’s sensor network and collaborative efforts with members, suppliers, and authorities made rapid detection and response to the attacks possible.

Massive Cyber Attack
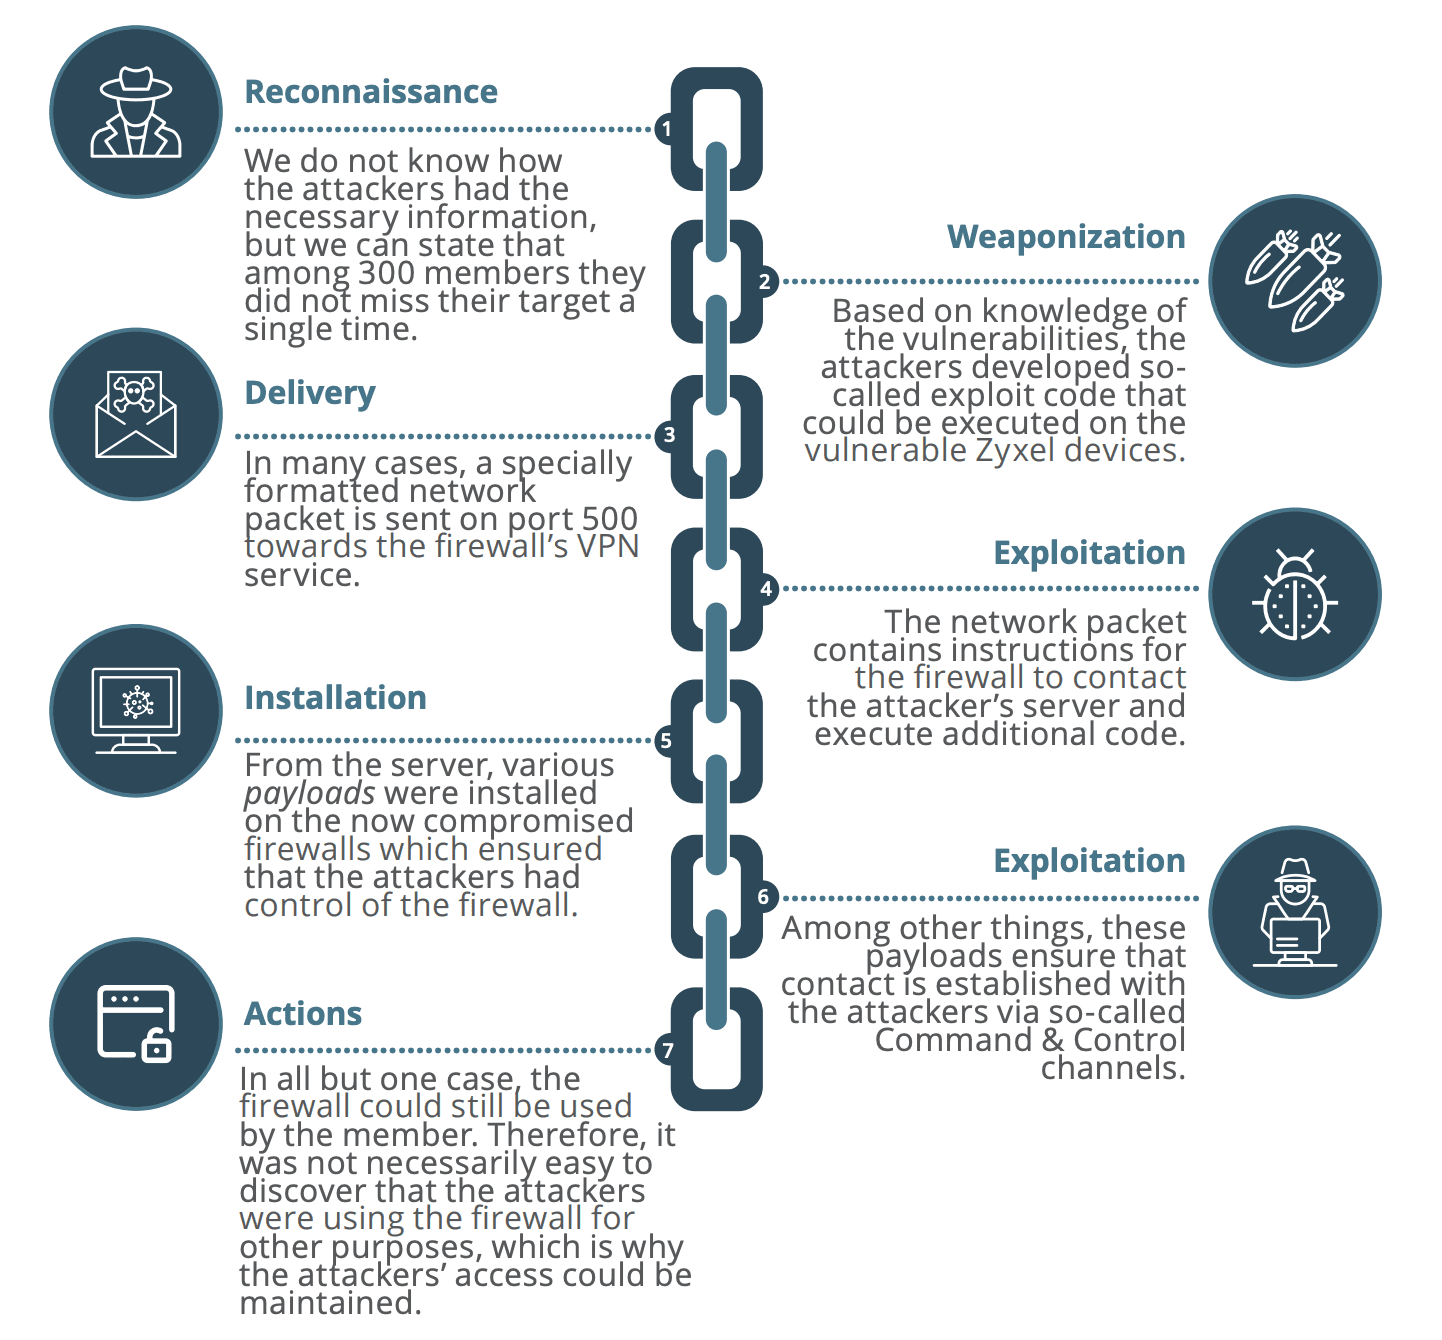
Cyber Kill Chain of the overall attack

Without this proactive approach, the consequences for Denmark’s infrastructure could have been severe.

SektorCERT’s post-attack recommendations emphasize the importance of implementing all 25 of their proposed measures for those operating critical infrastructure in Denmark. 

The focus extends beyond the specific attack techniques, addressing systemic vulnerabilities and enhancing overall cybersecurity resilience.

Detailed Analysis and Objective Timeline

The report provides a comprehensive cyber attack analysis, distinguishing between subjective analysis and objective timelines. 

This division ensures a nuanced understanding of the events, enabling readers to delve into technical details or opt for a broader perspective.

SektorCERT’s sensor network was pivotal in detecting and responding to attack patterns across multiple companies. 

The ability to analyze data collectively enabled the identification of attackers and their methods, preventing potential damage to critical infrastructure.

The report acknowledges the difficulty in attributing the attack to specific actors, highlighting the intricate nature of cybersecurity. 

While indicators may point to entities like Sandworm, definitive conclusions remain elusive, emphasizing the need for vigilant monitoring and advanced analysis.

Systemic Vulnerabilities and Societal Impact

The attack exposed systemic vulnerabilities within Denmark’s decentralized energy system. 

The report underscores the potential societal impact when a common vulnerability exists across multiple companies, urging a collective focus on addressing these vulnerabilities.

Highlighting the perpetual threat to Denmark’s critical infrastructure, the report urges heightened attention and proactive measures to prevent, detect, and respond to cyber-attacks. 

SektorCERT’s role in swiftly shutting down attackers’ access averted potentially severe consequences.

The successful cooperation between SektorCERT, members, suppliers, and authorities minimized the consequences of the attacks on critical infrastructure. 

The report acknowledges the collaborative efforts that played a crucial role in mitigating the impact.

While indications suggest state actor involvement, the report refrains from delving into geopolitical consequences, focusing on technical aspects. 

SektorCERT’s analysis concludes with recommendations, emphasizing the need for a collective effort to secure Denmark’s critical infrastructure.

Patch Manager Plus, the one-stop solution for automated updates of over 850 third-party applications: Try Free Trial.


[ad_2]
Source link

Ddostf Botnet Resurfaces in DDoS Attacks Against MySQL and Docker Hosts

0
[ad_1]

Researchers claim that the Chinese Ddostf botnet is specifically designed for launching DDoS attacks and that the threat actors are operating a DDoS-for-hire service.

AhnLab Security Emergency Response Center (ASEC) researchers have shared alarming details of a new campaign targeting MySQL servers and Docker hosts with DDoS malware.

AhnLab noted that attacks targeting MySQL servers on Windows systems have increased sharply, and vulnerable servers are infected with the Chinese botnet Ddostf, discovered in 2016.

Researchers claim that this malware is specifically designed for launching DDoS attacks and that the threat actor is operating a DDoS-for-hire service.

According to the AESC blog post, threat actors scan for exploitable MySQL servers. After compromising the servers, threat actors install the Ddostf DDoS botnet to launch distributed denial-of-service (DDoS) attacks against other servers.

MySQL servers are a common target in such campaigns because of their widespread use in Windows and Linux environments. Although MS-SQL is a preferred database service for Windows users, MySQL servers are also commonly used on Windows, which makes the systems running them a prime target for cybercriminals.

Based on data from AhnLab’s Smart Defense (ASD) logs, most malware targeting vulnerable MySQL servers were Gh0st RAT variants, but instances of AsyncRAT were also observed and recently, there’s been an uptick in the use of the Ddostf botnet.

Ddostf is a powerful malware that copies itself with a random name in the %SystemRoot% directory and registers as a service before decrypting the encrypted C2 server URL string to connect to the attackers’ server. It can collect system data and transfer it to the C2 server. Then it waits for specific commands (e.g., SYN, UDP, and HTTP GET/POST floods) to launch the DDoS attacks.

The botnet is unique because it can connect to a new address from the C2 server and execute commands there for a limited time. This helps the Ddostf botnet operator to infect multiple systems and sell DDoS attacks as a service. Ddostf can target Linux and Windows systems because of supports both ELF and PE formats and can achieve persistence. 

Attackers first scan for publicly accessible systems using port 3306/TCP and after accessing the server (those with known vulnerabilities or weak credentials), they use brute-force or dictionary attacks on the system.

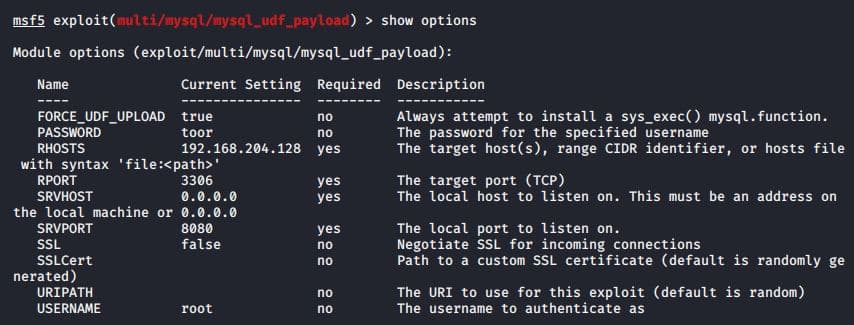
If the system has signs of poor credential management, attackers can gain access to administrator account credentials. If the system runs an unpatched version with vulnerabilities, attackers can exploit them to execute commands without needing these processes. Unlike MS-SQL, which entails direct OS command execution methods, MySQL relies on UDFs (User-Defined Functions) that can allow threat actors to execute commands.

They can also install malicious UDF DLLS on infected MySQL servers and execute commands. Like CLR Stored Procedure WebShell work, these DLLs can provide threat actors complete control of the infected system. In the case of the Ddostf DDoS bot, attackers use the UDF malware as a tool to install it on poorly managed MySQL servers.

Database servers get frequently targeted because of poorly managed account credentials. Administrators must use strong passwords apart from applying the latest patches to protect their servers. Firewalls can be used to restrict access to external actors, and a DDoS mitigation service can help protect against large-scale attacks.

  1. Who Killed the Mozi IoT Zombie Botnet – India or China?
  2. Chinese APT Posing as Cloud Services to Spy on Cambodia
  3. Dark.IoT & Custom Botnets Exploit Zyxel Flaw in DDoS Attacks
  4. How Chinese Hackers Stole Signing Key to Breach Outlook Accounts
  5. Chinese Scammers Exploit Cloned Websites in Vast Gambling Network

[ad_2]
Source link

Judge will make a decision on Google vs DOJ in early May 2024

0
[ad_1]

As reported earlier, the Google vs DOJ antitrust trial is now over. Yesterday was the last day of actual court appearances. Up until now, we were aware that the decision is coming in 2024, but we did not know when. Well, the Judge on the case, Amit Mehta, has announced that the Google vs DOJ decision will be made in early May 2024.

Judge will make a decision on Google vs DOJ antitrust case in May 2024

To be more precise, the Judge set closings for May 1-3 next year. Needless to say, that’s quite a long wait for a decision, basically over half a year. It’s not unusual considering the size of this case, actually.

This antitrust case was going on for a little over two months, as it started on September 12 and ended on November 16. We have a rather lengthy article in which we covered this trial since it began, in case you’re interested.

During the trial, the DOJ tried to prove that Google took advantage of its position, and illegally kept its place in the market. Google has a huge market share percentage when it comes to search, close to 90%.

The company had deals with various companies over the years, including both Google and Apple, amongst others. It paid Apple, for example, a staggering amount of $18 billion to stay the default search engine on Safari… and that was just in 2021.

The company paid out over $26 billion to partners in 2021

Overall that same year, Google paid out over $26 billion to partners, as it was revealed during the trial. The DOJ did its best to prove Google’s wrongdoings, and during the trial, various other info popped up.

Do note that the trial itself was semi-private, so we did not get access to all the information, just some tidbits. Plenty of documents passed through the courtroom, though.

Chances are we won’t hear much about this trial since May next year, if at all. It remains to be seen what will the decision be.


[ad_2]
Source link

Meta works on Emu Video and Emu Edit: Generative AI tricks for GIFs, photos and 4-second videos

0
[ad_1]

Meta is announcing through a blog post that they’re busy working on new research into “controlled image editing based solely on text instructions and a method for text-to-video generation based on diffusion models”.

Which, in simpler words, means they want to put in Facebook and Instagram generative AI tools. The projects Meta is developing are called Emu Video and Emu Edit.

What is Emu Video?


This tool, as the name suggests, is for generating video. Meta describes it as “a simple method for text-to-video generation based on diffusion models”. Emu Video should respond to a variety of inputs: text only, image only, and both text and image. The process is split into two steps, Meta clarifies: first, generating images conditioned on a text prompt, and then generating video conditioned on both the text and the generated image.

What is Emu Edit?


This one should allow “precise image editing” via recognition and generation tasks. Like Meta says, the use of generative AI is often a process, not a single task.

“Emu Edit is capable of free-form editing through instructions, encompassing tasks such as local and global editing, removing and adding a background, color and geometry transformations, detection and segmentation, and more. Current methods often lean towards either over-modifying or under-performing on various editing tasks. We argue that the primary objective shouldn’t just be about producing a ‘believable’ image. Instead, the model should focus on precisely altering only the pixels relevant to the edit request. Unlike many generative AI models today, Emu Edit precisely follows instructions, ensuring that pixels in the input image unrelated to the instructions remain untouched. For instance, when adding the text ‘Aloha!’ to a baseball cap, the cap itself should remain unchanged”, says the Meta team.

The potential use cases


The road ahead is definitely AI-driven for Meta.

“Although this work is purely fundamental research right now, the potential use cases are clearly evident. Imagine generating your own animated stickers or clever GIFs on the fly to send in the group chat rather than having to search for the perfect media for your reply. Or editing your own photos and images, no technical skills required. Or adding some extra oomph to your Instagram posts by animating static photos. Or generating something entirely new”, the blog post concludes.


[ad_2]
Source link

Samsung chief faces five years in jail over fraud, stock manipulation

0
[ad_1]

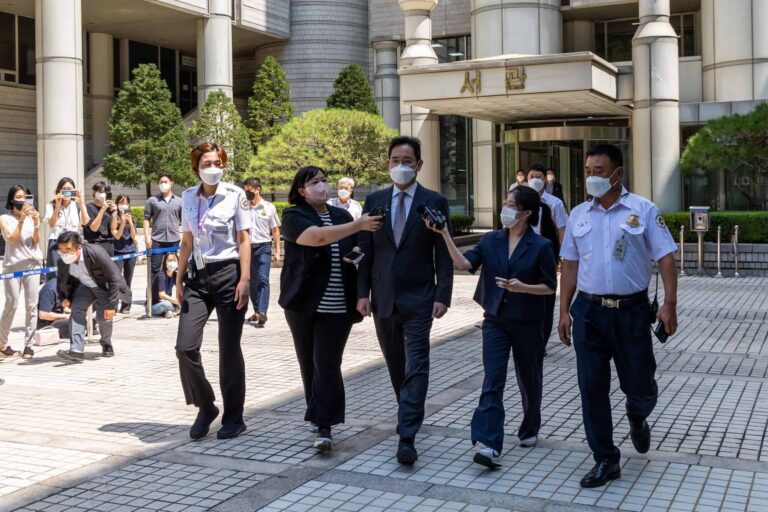
Samsung chairman Lee Jae-yong might have to head back to prison again. South Korean prosecutors have demanded a five-year jail term for the Samsung chief in connection to the controversial merger of two company affiliates in 2015. He previously went to jail twice in a separate bribery case involving former South Korean President Park Geun-hye.

Legal troubles for Samsung chief Lee Jae-yong haven’t ended yet

Samsung completed a high-profile merger of its affiliates Samsung C&T and Cheil Industries in 2015. Since Lee had a 23.2 percent stake in the latter, the $8 billion merger—where three Samsung C&T shares were offered for one Cheil share—helped him tighten his control of the merged entity. Effectively, Lee made a strong case for himself to succeed his father as the leader of the family-controlled conglomerate, the Samsung Group.

However, the state prosecution accused Lee of stock price manipulation and accounting fraud to help facilitate the merger (via Yonhap). He allegedly inflated the prices of Cheil and deflated the prices of Samsung C&T through unfair and illegal practices. The Samsung chief is suspected of having disseminated false market information and mass purchasing stocks among other unlawful actions.

Prosecutors have also accused him of accounting fraud at Samsung Biologics, a subsidiary of Cheil Industries. His actions, particularly the devaluation of Samsung C&T, resulted in massive financial losses to other investors. Since Lee was the final decision-maker (he was leading the company after his father suffered a heart attack the previous year), he allegedly approved all the malpractices for his benefit.

The prosecution demanded a five-year jail term and a fine of KRW 500 million (approx. USD 386,000) for Lee in the case. Prosecutors have also demanded a 4.5-year prison sentence and a similar fine for two senior Samsung executives on related charges. Choi Gee-sung, a former head of the Korean conglomerate’s now-disbanded control tower Future Strategy Office, is one of them.

The court will announce its ruling next year

Lee Jae-yong and the two Samsung executives were indicted in this case in September 2020. Following years of hearings where the accused denied wrongdoing, prosecutors finally presented a sentence request during the final hearing held at the Seoul Central District Court earlier today. Lee attended the hearing, with his lawyers expected to present their final arguments in his defense later today.

The court may not announce its ruling in the case before 2024. If it finds Lee guilty on one or more accounts, he may have to head back to prison less than two years after receiving a presidential pardon in the aforementioned bribery case. He spent more than a year in jail between 2017 and 2021 before walking out on parole and eventually receiving a pardon. Time will tell if the Samsung chief will manage to avoid a third term in jail.


[ad_2]
Source link