Android Beta testers are now trying out the WhatsApp AI chatbot

0

[ad_1]

In the most recent WhatsApp Android beta update, users are getting to try out the new AI chatbot. This feature is currently accessible to some beta testers via the Chats Tab within the app interface. The icon used to access this new feature sits on the “New Message” icon that sits on the app’s home page.

A few weeks ago, Mark Zuckerberg announced that this new feature is going to hit beta testing on devices. At the moment, only beta testers in the US have access to this feature for usage. Its function is to help assist users with daily activities and a handy companion that people can start conversations with at any time of the day.

Soon, more users will get access to this AI-powered feature for usage in their day-to-day activities. The new AI-powered feature can also keep users entertained when they don’t have any friends online to chat with. Here are more details on this new feature that is now in beta testing for Android devices.

The WhatsApp AI chatbot is now available for usage to Android beta testers

This new AI-powered feature that beta testers are trying, outcomes with its shortcut. As pointed out a few paragraphs away, this shortcut sits above the “New Message” button and provides users with quick access to the AI chatbot. From the images WABetaInfo shared, this shortcut’s icon is a circle with some color blends.

The shortcut key stands out from the entire WhatsApp interface and can be easily spotted. Tapping on it will pull up the AI chatbot for users to ask questions or start conversations and get follow-up answers. They can use this to find out things or just to pass the time while using the app daily.

WhatsApp isn’t the first social media application to launch an AI chatbot for usage. Snapchat also has something similar to this known as “My AI” and it is currently available for usage. Users of this social media platform have had access to this AI chatbot for quite a while and they use it for various reasons.

Something similar to this is now preparing to roll out for usage by the WhatsApp community. There’s no information on how long this feature will remain accessible to only beta testers. But WhatsApp users can have it at the back of their mind that they’ll soon get an AI companion.

At the moment, not all beta testers in the US have access to this feature, as it’s still rolling out. In the coming days, more beta testers will get to try out the new WhatsApp AI chatbot. With time, this new AI-powered feature will become available for usage to the global audience via a Google Play Store or Apple App Store update.

[ad_2]

Source link
Google Explains How Hackers Exploited The Zimbra Zero-Day

0

[ad_1]

Months after ensuring that the patch actually works, Google has now disclosed more details about active exploitation of a Zimbra zero-day vulnerability. The tech giant explained how the threat actors exploited the Zimbra zero-day in various malicious campaigns before and after the patch release.

Zimbra Zero-Day Flaw Exploited To Target Govt. Orgs – Says Google

In a recent post, Google elaborated on different malicious campaigns exploiting the Zimbra zero-day vulnerability patched earlier this year.

Specifically, in July, Zimbra addressed a severe zero-day flaw in Zimbra Collaboration Suite (ZCS) email servers, allowing XSS attacks. At that time, Zimbra didn’t share any details about actively exploiting the flaw. However, Google researchers disclosed detecting active exploitation attempts of the vulnerability. Yet, there weren’t many details about the attacks.

However, Google has now shared insights about the repeated exploitation of vulnerability to target different government organizations. As explained in their post, Google’s Threat Analysis Group (TAG) discovered this XSS vulnerability a month before the patch release. They observed three threat groups exploiting the flaw before the stable patch release.

Following the first exploitation against government organizations in Greece, Zimbra deployed a hotfix on GitHub. Nonetheless, it appeared that this hotfix brought the zero-day to the attention of other threat actor groups. Consequently, Google detected two more malicious campaigns exploiting this flaw to target users in Moldova and Tunisia. Google TAG attributed these campaigns to the Winter Vivern (UNC4907) APT Group.

Then, a third malicious campaign also caught Google’s attention as another, unidentified threat actor group exploited the zero-day to target a Vietnamese government firm. This phishing campaign aimed to steal webmail credentials.

While Zimbra released a working patch for the zero-day following the Vietnam campaign, the criminal hackers seemingly continued hunting for vulnerable systems. Consequently, a fourth malicious campaign to steal Zimbra authentication tokens surfaced online, targeting a Pakistani government organization.

Users Must Always Keep Their Systems Up-to-date

Besides disclosing the countries, Google hasn’t shared precise details about the victims and the outcome of these attacks. Yet, with the latest disclosure, Google emphasized on the importance of swift system updates to receive the latest security fixes.

Moreover, Google also highlighted how the threat actors keep monitoring open-source repositories to know about the latest vulnerability fixes so as to hunt for vulnerable systems.

Let us know your thoughts in the comments.

[ad_2]

Source link

Leaked Galaxy S24 screen protectors visualize size difference

0

[ad_1]

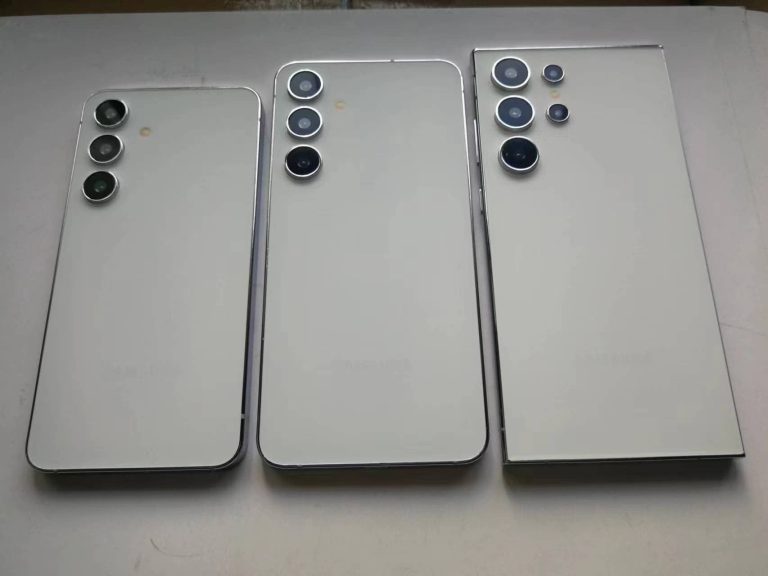
Samsung is preparing to launch the Galaxy S24 series in January 2024. While the devices are still two months away, leaks have already revealed their key specs and design. The upcoming Galaxy flagships will bring a handful of upgrades to the table, along with a notable design overhaul for the Ultra model. Leaked screen protectors have now visualized the size difference between the three models and confirmed a flat display for the Galaxy S24 Ultra.

Galaxy S24 screen protectors show up early

The latest Galaxy S24 leak comes from a noted industry insider known by the pseudonym Ice Universe on X (formerly Twitter). The tipster recently posted a picture that allegedly shows the screen protectors for the upcoming Samsung flagship trio. While the source didn’t share further information, the picture gives us a visual representation of the sizes of the phones.

As expected, the Galaxy S24 is the smallest of the lot. It is rumored to sport a 6.2-inch display with rounded corners. The Galaxy S24+ and Galaxy S24 Ultra will feature 6.6-inch and 6.8-inch screens, respectively. However, while the former has rounded corners, the latter sports a boxy design with sharp corners. This leak also confirms that all three models have slim and symmetrical bezels. This year’s Galaxy S23 Ultra has a thicker bottom bezel.

Additionally, we can see that the screen protector meant for the Galaxy S24 Ultra is a flat piece of glass. This is a further confirmation that the phone features a flat display. Samsung has moved over from the curved screen it used on its flagship phones for the past several years. The company is prioritizing functionality over aesthetics. A curved display looks sleek and is more comfortable to hold, particularly when the phone is as big as the Galaxy S24 Ultra.

However, it is prone to accidental touches and may break easily during a fall. Putting a screen protector on a curved display is also a pain. Moreover, the S Pen works perfectly on the edges if the screen is flat. Considering this all, not many may dislike this change from Samsung. The Galaxy S24 Ultra should be the most popular model among the three new Samsung flagships.

Samsung will unveil the devices in mid-January

The Galaxy S24 series doesn’t yet have a launch date. Samsung will reveal the date just a few weeks before the big launch event. However, leaks have hinted at a January 17 unveiling of the phones, with the event taking place in San Jose, USA. With two more months to go, we should see many leaks about the Galaxy S24 lineup in the build-up to its launch, so stay tuned.

Samsung Galaxy S24 screen protector leak


[ad_2]

Source link

Apple Vision Pro could launch in March 2024, alongside new MacBooks

0

[ad_1]

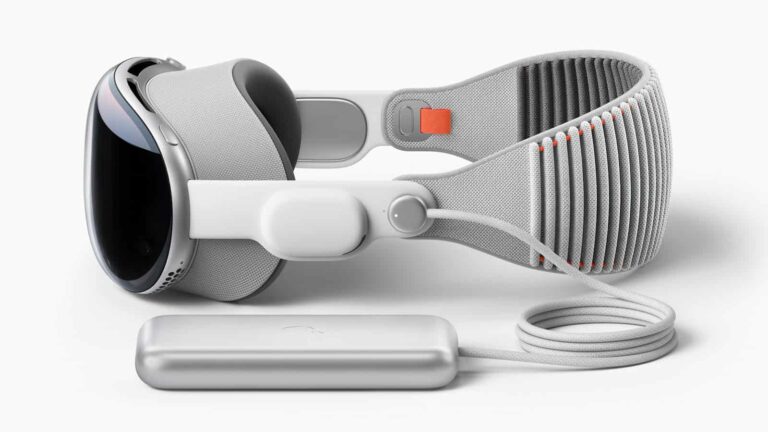
Apple seems to have set the launch date for the upcoming Vision Pro VR headset to March. Earlier this year, the company showed off its coming VR product, which will be the first of its kind and usher the company into the VRI industry. However, despite showing off the product to the global community, fans have to wait for months before they can get their hands on it.

A new report now defaults to previous info that this VR headset would hit the launch stage in January. A report from Mark Gurman points to March as the launch month of the upcoming Apple VR products. This launch will take place in the US before expanding access to other regions in the months following.

Apple initially thought that it could make this coming VR headset available for purchase in January 2024. However, this plan of the tech giant doesn’t seem to be possible as they are now pushing the launch date a few months further. This will give the company time to finalize things with the coming VR product before making it available for retail.

The Apple Vision Pro will become available for purchase in March 2024 along with some MacBooks

Apple is preparing its first product for the VR industry and it’ll launch in a few months. March 2024 has been set as the launch date of the coming products and it’ll be accompanied by MacBook Pro models. Just like the coming VR products, these MacBook Pro models will be the first of their kind to hit the global audience.

The MacBook Pro models to launch in March 2024 will feature OLED screen display technology. They might also bring some performance improvements thanks to a new processor. But the coming Vision Pro VR headsets don’t have a predecessor to outperform.

They are the first of their kind, and Apple will retail this product unlike they would any other product. Third-party sales of the Vision Pros might not be possible, as Apple will require buyers to customize their headsets. This customization will include prescription lenses, fitted headbands and so much more.

Giving third-party retailers access to all these customization parts might be quite daunting. For this reason, Apple will perform retails on their official website or physical stores via appointments. So getting one of these headsets might be a bit of a hassle for some buyers.

At the moment, the visionOS that’ll run on the coming VR headsets is in testing. Developers are getting their apps and services to run smoothly here for a great user experience. More details on this coming product will become available as its launch approaches.

[ad_2]

Source link

Apple Music found out how to deal with phony streams and the fraud fell by 30%

0

[ad_1]

Apple is keeping a close eye on Apple Music and for the last year, it has cranked up its protection against so-called streaming manipulation (via 9to5Mac).

The anti-fraud measures have been so successful that the fraud rate has fallen by 30%, says a new report by Billboard.

Streaming fraud can take many forms, the most obvious one is where a musician uses bots to stream their music 24/7 in order to obtain royalties. Apple says it has detected other examples as well!

“Apple Music quietly rolled out its own strengthened fraud protections — including hitting repeat offenders with “financial adjustments” — more than a year ago, according to an email obtained by Billboard that the platform sent to music industry partners in March. Apple Music’s internal metrics indicate that the policy has already led to a 30% drop in streaming manipulation”, reads the report from Billboard.Another type of fraud is the 31-second song albums – Apple pays a royalty per track, with a proviso that a track of 30 seconds or less isn’t included in the deal. Some have created entire albums of 31-second songs just to hop over the 30-second limit.

“To help labels and distributors figure out where fraud is occurring, Apple Music’s email says the platform started sending daily reports detailing “a content provider’s albums with streams held in review.” “After each review,” the email goes on, “we remove manipulated streams and release legitimate plays. At the end of each month, content providers also receive a report with all excluded streams.” (Spotify has now also ramped up the reporting it provides to labels and distributors, according to one executive at a distribution company, “adding a new dimension of seeing repeat offenders.”)”, says the Billboard report that quotes Apple Music officials.

[ad_2]

Source link

Open Detection System Uncover SIEM Blind Points

0

[ad_1]

Cyberattacks pose a significant risk, and prevention alone isn’t enough, so timely detection is crucial. That’s why most organizations use SIEM (Security Information and Event Management) systems to centrally collect and analyze security events with expert-written rules for detecting intrusions.

Organizations use SIEM rulesets for intrusion detection, focusing on misuse patterns for known attacks. It’s effective, simple, and aids investigation with detailed alerts.

AMIDES, an open-source Adaptive Misuse Detection System, spots attack-like behavior not caught by SIEM rules.

The following cybersecurity researchers from the respective organizations and universities introduced this new detection system:-

  • Rafael Uetz from Fraunhofer FKIE
  • Marco Herzog from Fraunhofer FKIE
  • Louis Hackländer from Fraunhofer FKIE
  • Simon Schwarz from University of Göttingen
  • Martin Henze from RWTH Aachen University, Fraunhofer FKIE

It uses supervised learning, classifying events based on similarity to known-malicious or known-harmless activity without the need for a manually extensive attack set. Besides this, the AMIDES identifies potential evasion and suggests the likely evaded SIEM rules.

Document

Free Webinar

In the upcoming webinar, Karthik Krishnamoorthy, CTO and Vivek Gopalan, VP of Products at Indusface demonstrate how APIs could be hacked. The session will cover: an exploit of OWASP API Top 10 vulnerability, a brute force account take-over (ATO) attack on API, a DDoS attack on an API, how a WAAP could bolster security over an API gateway

AMIDES

SIEMs collect data from source systems in Syslog and Windows Event Log format. Due to data volume, automated threat analysis is essential. 

If a threat is detected, a human analyst in a security operations center reviews the alert. Misuse detection, using expert-written rules and signatures, is the primary method for SIEMs to automatically spot malicious activity.

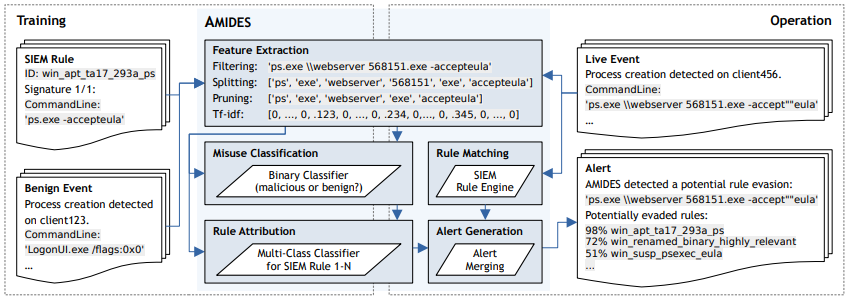
AMIDES process chain (Source - Usenix)
AMIDES process chain (Source – Usenix)

AMIDES enhances SIEM misuse detection in enterprise networks by adding machine learning components to identify rule evasions alongside traditional rule matching.

SIEM events undergo rule matching and feature extraction. The misuse classification component classifies the feature vector as malicious or harmless.

For the training process, this complete system needs the following two key elements:-

  • SIEM rules 
  • Harmless events

It works with existing SIEM rules in organizations using traditional misuse detection, and at the moment, it supports Sigma rules, with potential for Splunk in the future.

This open-source detection system is freely accessible under the GPLv3 license, and it prioritizes performance for large enterprise networks, implemented in Python using:-

By auto-detecting the SIEM rule evasions, AMIDES reduces network blind spots significantly, but effective detection isn’t enough alone.

This work targets SIEM rule evasions creating critical blind spots in enterprise networks. Analyzing open-source SIEM rules, experts found 110 fully evadable and 19 partially evadable rules out of 292, exposing networks to undetected attacks.

This open-source solution is adaptive for misuse detection, extending rule-based detection to identify evasions and bypassed rules. This approach utilizes existing data, making it convenient for enterprise networks.

Experience how StorageGuard eliminates the security blind spots in your storage systems, try a 14-day free trial.

[ad_2]

Source link

RedMagic 9 Pro to offer up to 24GB of RAM, benchmark reveals

0

[ad_1]

The RedMagic 9 Pro is an upcoming gaming smartphone, and it will offer up to 24GB of RAM. This info has been revealed by the AnTuTu benchmark. That’s not all that was revealed, of course.

The RedMagic 9 Pro will feature 24GB of RAM & Android 14

That listing also reports that the phone scored 2,290,773 points on AnTuTu. Needless to say, this is way, way up there. This benchmark also confirms that the Snapdragon 8 Gen 3 will fuel this smartphone.

RedMagic will utilize LPDDR5X RAM, and UFS 4.0 flash storage. Speaking of which, the model that got benchmarked is also equipped with 1TB of storage. Android 14 was also mentioned here. AnTuTu also confirmed that a 120Hz panel will be in use.

Now, we do know the launch date of this smartphone. The RedMagic 9 Pro will become official on November 23, so only three days from now. RedMagic also confirmed the design of the phone already, by releasing a bunch of images.

The phone won’t include a camera bump at all

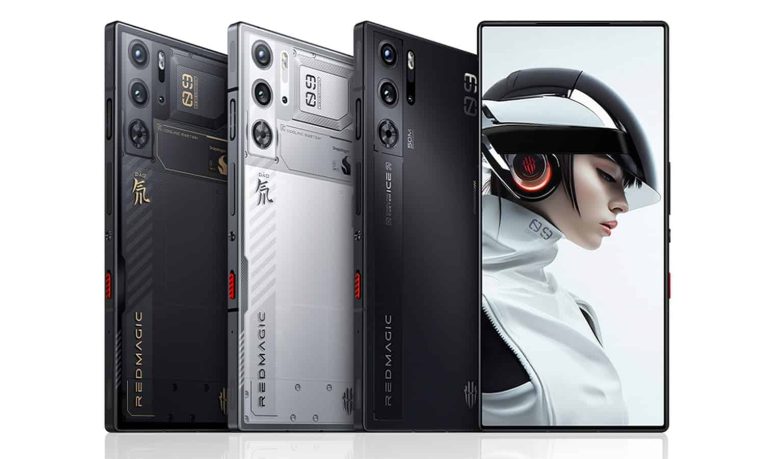
The RedMagic 9 Pro will resemble the RedMagic 8 Pro and RedMagic 8S Pro. There will be one major difference, though… the new phone won’t have a camera bump, at all. Its rear cameras will be flush with the backplate.

The variants that the company showed off via its official social media channels have a see-through backplate. It’s basically a custom for RedMagic to release at least one model with a see-through backplate.

In any case, this handset will have a bunch of gaming features, including shoulder triggers on the right-hand side. When you hold the device in landscape orientation, those will basically be there for your index fingers.

This phone will also have some form of advanced cooling, including a fan, almost certainly. It is launching in China on November 23, but the device will become available globally too.

RedMagic 9 Pro AnTuTu


[ad_2]

Source link

iPhone 16 Pro Max will have a bigger display than Galaxy S24 Ultra

0

[ad_1]

The iPhone 16 Pro Max, which Apple is expected to launch next year, will have a bigger display than the Galaxy S24 Ultra. Samsung will announce its ‘Ultra’ phone in Q1 next year, it seems, while Apple’s will arrive towards the end of Q3 2024.

The iPhone 16 Pro Max will have a bigger display than the Galaxy S24 Ultra

In any case, this display info comes from two sources, Anthony and Ice Universe, two tipsters. Anthony mentioned that the iPhone 16 Pro Max will have a 6.86-inch display, while he also added that it will be the biggest on an iPhone yet, and even bigger than the Galaxy S24 Ultra’s.

Ice Universe reshared that post on X, and added the exact display size of the Galaxy S24 Ultra. He said that the exact size is 6.7913385827 inches. Samsung will market this as a 6.8-inch display, though.

The difference in size between these two panels is, of course, not that big. Both are kind of huge, so you’ll have a gigantic canvas to work with no matter what device you end up getting.

Both devices will include flat displays

For the first time in a long time, both Apple and Samsung flagship smartphones will also have flat displays. Samsung is going flat this time around. All three of its flagship-grade phones will have flat displays, even the ‘Ultra’.

Speaking of which, the Galaxy S24 Ultra will launch alongside the Galaxy S24 and Galaxy S24+. All three of those devices are expected to arrive in January next year. January 17 is tipped, and the launch event is expected to take place in San Francisco.

Designs of all three phones already surfaced. As expected, the Galaxy S24 and Galaxy S24+ will look the same, but differ in terms of size. The ‘Ultra’ model will once again stand apart, with a different design. It will be less different than before, though, mainly due to the flat display.


[ad_2]

Source link

Apple’s OLED iPad plans have leaked out

0

[ad_1]

A recent leak points out that OLED display iPad entries will hit the global market sometime next year. This impressive design option for Apple’s iPads will be exclusive to the Pro models. Following this, the leak also claims that the iPad Air and Mini entries will also get OLED displays two years after the Pro models.

For the iPad Pros that are said to get OLED screens by next year, their display will be superior to the Air and Mini models. This is because the Pro models might use a two-stack dual-emission OLED panel. As for the more affordable and smaller Air and Mini models, they’ll stick with a single-stack single-emission OLED display.

Despite the difference in OLED displays across the iPad model line-up and their time of availability, this is a great improvement. Currently, the available iPads make use of Liquid Retina XDR mini-LED LCD screens for the Pro models. The more affordable iPads use a similar display to the Pro models but drop off the XDR display technology. If this leak is anywhere close to being accurate, then iPad users can expect an impressive display upgrade by next year.

A significant upgrade is coming to the iPad Pro models with the introduction of OLED display panels

Currently, the available iPad Pro models use LED and mini-LED display technology. This display technology is exclusive to the Pro models on Apple’s more recent iPads. But leaks point out that this will change by next year with the launch of newer iPad Pro models.

The upgrade on these modes will not only bring improvements to the M2 chips onboard but also new screen displays. At this moment, Apple offers its iPad Pros in two different screen sizes, 12.9 and 11 inches. Both of these screen sizes come with LED and mini-LED displays, respectively. However, Apple has been working hard to switch over to OLED displays with its top display suppliers.

For next year, the OLED panel on the iPad Pro models might feature a single-stack single-emission OLED display. By 2027, reports have it that this single-stack display will only be available for the Air and Mini iPad models. Apple will then switch over to the two-stack dual-emission OLED display for the Pro models.

Available reports have it that the iPad Air and Mini models won’t get OLED displays until 2026. A year after this, the Pro models will improve upon the OLED display technology that they offer users. For these upgrades to be possible, Apple might change the suppliers of its OLED panels for coming iPads.

Samsung, one of the brand’s major display suppliers, might not be part of the suppliers for the two-stack OLED display. Apple might switch its attention to other suppliers that’ll make these displays available for future iPad models. With this news, it becomes clear that Apple is gearing up to compete with Android tablets that already use OLED displays.

[ad_2]

Source link

Critical AI Tool Vulnerabilities Let Attackers Execute Arbitrary Code

0

[ad_1]

Multiple critical flaws in the infrastructure supporting AI models have been uncovered by researchers, which raise the risk of server takeover, theft of sensitive information, model poisoning, and unauthorized access.

Affected are platforms that are essential for hosting and deploying large language models, including Ray, MLflow, ModelDB, and H20. While some vulnerabilities have been addressed, others have not received a patch.

Researchers discovered a wide range of vulnerabilities in the tools used in the supply chain for building chatbots and other kinds of AI/ML models, according to Protect AI’s November Vulnerability Report.

“Many of these OSS tools, frameworks, and artifacts, come out of the box with vulnerabilities that can lead directly to complete system takeovers such as unauthenticated remote code execution or local file inclusion vulnerabilities”, reads the report.

Details of the Affected Platforms

Large language models (LLM), as well as other ML platforms and AIs, are hosted, deployed, and shared via the impacted platforms.

Document

Free Webinar

In the upcoming webinar, Karthik Krishnamoorthy, CTO and Vivek Gopalan, VP of Products at Indusface demonstrate how APIs could be hacked. The session will cover: an exploit of OWASP API Top 10 vulnerability, a brute force account take-over (ATO) attack on API, a DDoS attack on an API, how a WAAP could bolster security over an API gateway

These consist of the machine learning management platform ModelDB, the machine learning lifecycle platform MLflow, the machine learning platform Ray, which is used for the distributed training of machine learning models, and the open-source Java-based H20 version 3 machine learning platform.

List of Critical Vulnerabilities Patched

  • CVE-2023-6021 with CVSS Score 9.3, Ray Log File Local File Include. 
  • CVE-2023-6020 with CVSS Score 9.3 Ray Static File Local File Include.
  • CVE-2023-6019 with CVSS Score of 10, Ray Command Injection in cpu_profile parameter.
  • CVE-2023-1177 with CVSS Score of 9.3, MLflow Local File Include via Model Versions API.
  • CVE-2023-6014 with CVSS Score of 9.1, MLflow Authentication Bypass.
  • CVE-2023-6015 with CVSS Score of 10, MLflow Arbitrary File Upload.

List of Critical Vulnerabilities Unpatched

  • CVE-2023-6013 with CVSS Score of 9.3, H2O Stored XSS/LFI.
  • CVE-2023-6038 with CVSS Score of 9.3, H2O Local File Include.
  • CVE-2023-6016 with CVSS Score of 10, H2O Remote Code Execution via POJO Model Import.
  • CVE-2023-6018 with CVSS score of 10, MLflow Arbitrary File Write.

Recommendation

Users are recommended to “Upgrade to the latest non-vulnerable version” for fixed vulnerabilities. “Restrict access to the web application” for unpatched vulnerabilities. 

Experience how StorageGuard eliminates the security blind spots in your storage systems, try a 14-day free trial.

[ad_2]

Source link