This is what Samsung’s Galaxy S24 Ultra may look like

0
[ad_1]

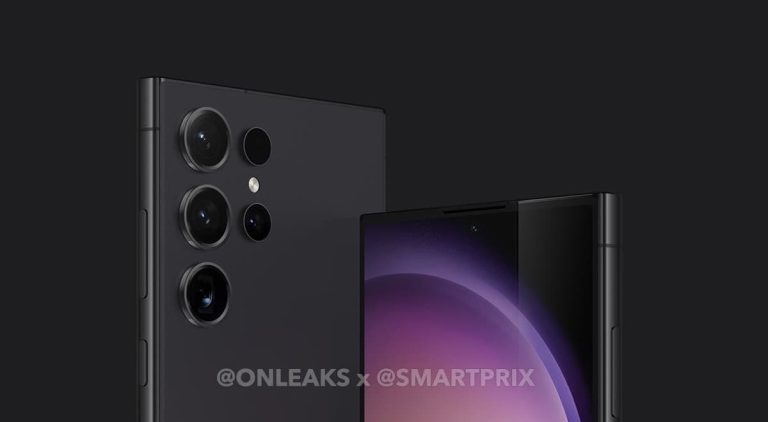
As we approach the end of 2023, the excitement around Samsung‘s new flagship smartphones is increasing. The company is readying three Galaxy S24 models, with the Ultra heading the lineup. Thanks to a flat display, the Galaxy S24 Ultra will look different from its predecessor. We have already seen the phone in leaked renders and concept images. A tipster has now shared what he claims to be the “closest rendering” of the upcoming Samsung flagship.

The Galaxy S24 Ultra shows up in new renders

For years, Samsung has released at least one flagship smartphone every year with a curved display. That’s changing next year with the Galaxy S24 Ultra moving to a flat display. The Korean firm is keeping the screen size unchanged (from the Galaxy S23 Ultra) at 6.8 inches, making the phone wider and shorter. Not by much—1.1mm shorter and 0.9mm wider—but enough to make for a notable difference when the two phones are kept side-by-side.

However, the design changes don’t end there. The 2024 model also features symmetric bezels, something fans have been long asking for. The chin is no longer thicker than the side and top bezels, making for a uniform look. Moreover, the punch hole is now smaller and sits a little lower than before. All of these changes are visualized in new Galaxy S24 Ultra renders shared by noted tipster Ice Universe on X.

Samsung Galaxy S24 Ultra closest renders 2

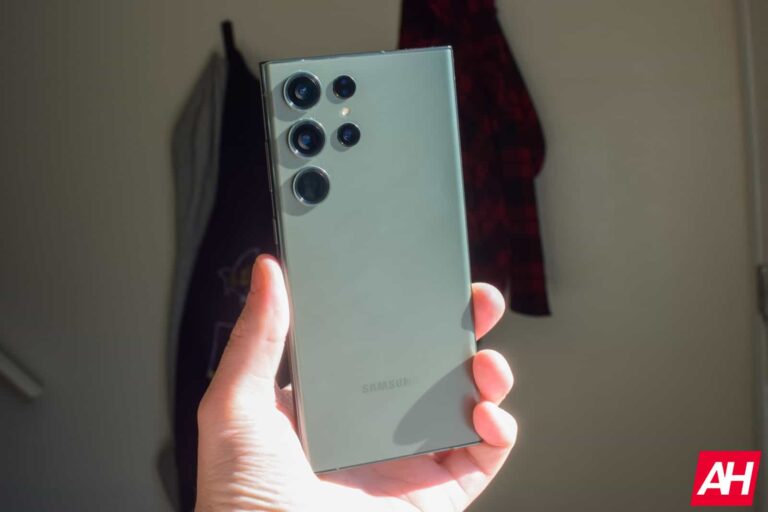
The tipster created these renders based on the data available to him, including the dimensions, display aspect ratio, and bezel width. As you can see in the photo above, the rear design is unchanged. We have three cameras aligned vertically in one column, with the laser sensor, LED flash, and a fourth camera sitting next to them. Both front and rear panels are slightly curved at the edges where they meet the titanium frame. However, the screen itself is flat.

The rear camera setup will see internal changes

The Galaxy S24 Ultra’s rear camera setup may look the same as the Galaxy S23 Ultra from the outside but it will see some changes on the inside. Most notably, Samsung is replacing the 10MP 10x optical zoom camera with a 50MP 5x lens. The 10 3x zoom lens has a slightly improved sensor and so does the 200MP main camera. The 12MP ultrawide lens appears to be unchanged, though. The Galaxy S24, Galaxy S24+, and Galaxy S24 Ultra may go official on January 17 next year.

Samsung Galaxy S24 Ultra closest renders 1


[ad_2]
Source link

Six cryptocurrency tips (and five mistakes to avoid)

0
[ad_1]

Cryptocurrency has taken the financial world by storm in recent years. What started as an experiment in digital currency has grown into a global phenomenon with millions of users and a market capitalization in the trillions. However, with great potential comes great risk, and it’s crucial to navigate this complex landscape with care and knowledge. In this article, we’ll delve deep into the world of cryptocurrency, providing you with six valuable tips to maximize your success and highlighting five common mistakes to avoid. Platforms like Immediate Definity Ai offer bitcoin trading features like accurate and précised strategies for becoming an independent trader

Understanding Cryptocurrency

What is Cryptocurrency?

Cryptocurrency is a digital or virtual form of currency that uses cryptography for security. It operates independently of any central authority, such as a government or bank, making it decentralized and resistant to censorship. The concept of cryptocurrency emerged in 2009 with the creation of Bitcoin by an anonymous individual or group known as Satoshi Nakamoto. Since then, thousands of cryptocurrencies have been developed, each with its own unique features and purposes.

The Blockchain Technology

At the heart of cryptocurrency is blockchain technology. A blockchain is a decentralized ledger that records all transactions across a network of computers. Once a transaction is added to a block, it is cryptographically sealed, making it nearly impossible to alter. This transparency and security are what make cryptocurrencies trustworthy and tamper-proof.

Six Cryptocurrency Tips

Tip 1: Start with Research

Before diving headfirst into the world of cryptocurrency, it’s crucial to equip yourself with knowledge. Understand the technology, the history, and the different cryptocurrencies available. Research the teams behind the projects, read whitepapers, and stay informed about the latest developments. Cryptocurrency is a rapidly evolving field, and staying up-to-date is essential for making informed decisions.

Tip 2: Diversify Your Portfolio

One of the fundamental principles of investing is diversification. Instead of putting all your eggs in one basket, consider spreading your investments across different cryptocurrencies. This strategy helps mitigate risk. While Bitcoin and Ethereum are well-known, exploring smaller, promising projects can yield substantial returns. However, always conduct thorough research before investing in any cryptocurrency.

Tip 3: Choose a Secure Wallet

A cryptocurrency wallet is a digital tool that allows you to store, send, and receive cryptocurrencies. There are various types of wallets, including hardware wallets, software wallets, and paper wallets. Hardware wallets are considered one of the most secure options as they store your private keys offline, making them less vulnerable to hacking. Regardless of your choice, safeguard your wallet and backup your keys. Losing access to your wallet means losing your assets.

Tip 4: Stay Informed and Updated

The cryptocurrency market is highly volatile, and prices can change dramatically in a matter of minutes. To navigate this volatility, you must stay informed. Follow reputable cryptocurrency news sources, join online communities, and engage with fellow enthusiasts. Additionally, regularly check market analysis and trends to make informed decisions about when to buy, sell, or hold your assets.

Tip 5: Practice Safe Trading

Cryptocurrency markets are rife with scams and fraudulent schemes. Be cautious and skeptical of offers that seem too good to be true. Avoid investing in projects with unrealistic promises or anonymous teams. Use trusted exchanges and double-check web addresses to prevent falling victim to phishing attacks. Always perform due diligence before investing your hard-earned money.

Tip 6: Long-Term vs. Short-Term Investments

When it comes to cryptocurrency investments, you have two primary options: long-term and short-term. Long-term investors, often referred to as “HODLers,” buy and hold cryptocurrencies for an extended period, believing in their long-term potential. Short-term traders aim to profit from price fluctuations by buying low and selling high. Both approaches have their pros and cons, and the right strategy depends on your risk tolerance and investment goals.

Five Common Cryptocurrency Mistakes to Avoid

Mistake 1: FOMO (Fear of Missing Out)

FOMO is a psychological phenomenon that often leads individuals to make impulsive decisions in the cryptocurrency market. When prices are soaring, FOMO can drive people to buy at peak prices, only to witness a sudden drop shortly afterward. To avoid FOMO-driven mistakes, maintain a rational and disciplined approach to investing.

Mistake 2: Neglecting Security

Security is paramount in the world of cryptocurrency. Neglecting to secure your assets can lead to devastating losses. Numerous stories exist of individuals who lost their holdings due to hacks or fraud. Always enable two-factor authentication (2FA), use strong passwords, and consider hardware wallets for added security.

Mistake 3: Ignoring Taxes

Cryptocurrency transactions may have tax implications, and failing to report your income accurately can lead to legal issues. Keep records of all your cryptocurrency transactions, including dates, amounts, and counterparties. Consult with a tax professional to ensure compliance with your country’s tax laws.

Mistake 4: Overtrading and Emotional Decisions

Overtrading, driven by emotions such as greed and fear, can lead to significant losses. It’s essential to develop a well-thought-out trading strategy and stick to it. Avoid making impulsive decisions based on short-term price movements, as this can often lead to financial distress.

Mistake 5: Lack of Patience

Cryptocurrency markets can be highly volatile, with prices experiencing rapid fluctuations. Some investors panic during downturns and sell their assets at a loss. Patience is key in cryptocurrency investing. By adopting a long-term perspective and HODLing through market fluctuations, you increase your chances of realizing significant gains.

Success Stories and Lessons Learned

Notable Cryptocurrency Successes

While the cryptocurrency market can be challenging, there have been numerous success stories. Early Bitcoin adopters, such as the Winklevoss twins and Chris Larsen, became billionaires through their investments. Additionally, projects like Ethereum and Binance Coin have generated substantial returns for their early backers.

Key Takeaways from Success Stories

Success in the cryptocurrency world often hinges on a few key principles. Persistence, belief in the technology, and a willingness to take calculated risks are common traits among successful cryptocurrency enthusiasts. Learning from their experiences can provide valuable insights for newcomers.

Conclusion

In the dynamic realm of cryptocurrency, possessing knowledge is paramount. Adhering to the six expert tips outlined in this article while sidestepping the five typical pitfalls will empower you to carve a path toward success in this ever-evolving and revolutionary sector. It’s vital to stay well-informed, safeguard your assets, and maintain a measured perspective when engaging with cryptocurrency.

[ad_2]
Source link

Apple reportedly plans to appeal Europe’s inclusion of iMessage as a gatekeeper in the DMA

0
[ad_1]

As many of you may probably know, the European Union has been pushing hard on tech giants in recent years, aiming to regulate their evergrowing power. One such effort by the EU is called the Digital Markets Act (DMA), which aims to combat monopoly and gatekeeping in the tech market. Now, 9to5Mac reports that Apple is working on appealing to the EU about the inclusion of the App Store and iMessage in the DMA.

Apple (not surprisingly) working on an appeal to the EU about the DMA


The EU has claimed that the App Store and iMessage are gatekeeper monology services. The fact that those two fall into that category means Apple will be forced to allow alternatives to In-App Purchases, sideloading, and many other changes to how Apple does things. Apple’s dispute is reportedly focused on the fact that iMessage is not big enough in Europe to be considered a gatekeeper service. The Cupertino giant also wants to debate exactly what part of the App Store will fall under the regulations.

The appeal has not yet been officially filed. The deadline for that is Thursday, November 16. By then, it should be more clear exactly what Apple’s arguments for the appeal will be.

This appeal doesn’t delay the need to follow the rules though, and the deadline for Apple to comply with the DMA is still by March 2024. We’ll probably soon know where this is going, but Apple will not be able to fully escape these new rules. For one, we already know (kind of) that Apple is working on a way to allow side-loading on iPhones. The changes to iMessage are still under wraps (if any are being worked on yet). If iMessage ends up staying under the DMA as a gatekeeper, Apple could be forced to make it compatible with smaller chat apps.

[ad_2]
Source link

OracleIV DDoS Botnet Malware Targets Docker Engine API Instances

0
[ad_1]

The OracleIV botnet malware employs various tactics, with a primary focus on executing DDoS attacks through UDP and SSL-based floods.

Cybersecurity researchers at Cado Security Labs have exposed a novel (Distributed Denial of Service) DDoS botnet malware dubbed OracleIV targeting publicly exposed Docker Engine API instances.

The findings were part of an investigation into a malicious campaign exploiting misconfigurations in Docker containers to deliver Python malware, compiled as an ELF executable.

Lately, Docker Engine APIs have been frequent targets of cybercriminals since the method has gained popularity due to the increasing adoption of microservice-driven architectures. Attackers exploit the unintentional exposure of the Docker Engine API, often scanning for vulnerable instances to deliver payloads with nefarious objectives.

In the case of the new OracleIV DDoS botnet malware, the attackers initiate access with an HTTP POST request to Docker’s API, specifically the /images/create endpoint. This triggers a docker pull command, fetching a specified image from Dockerhub. Once the malicious image is retrieved, a container is launched to carry out the attacker’s objectives.

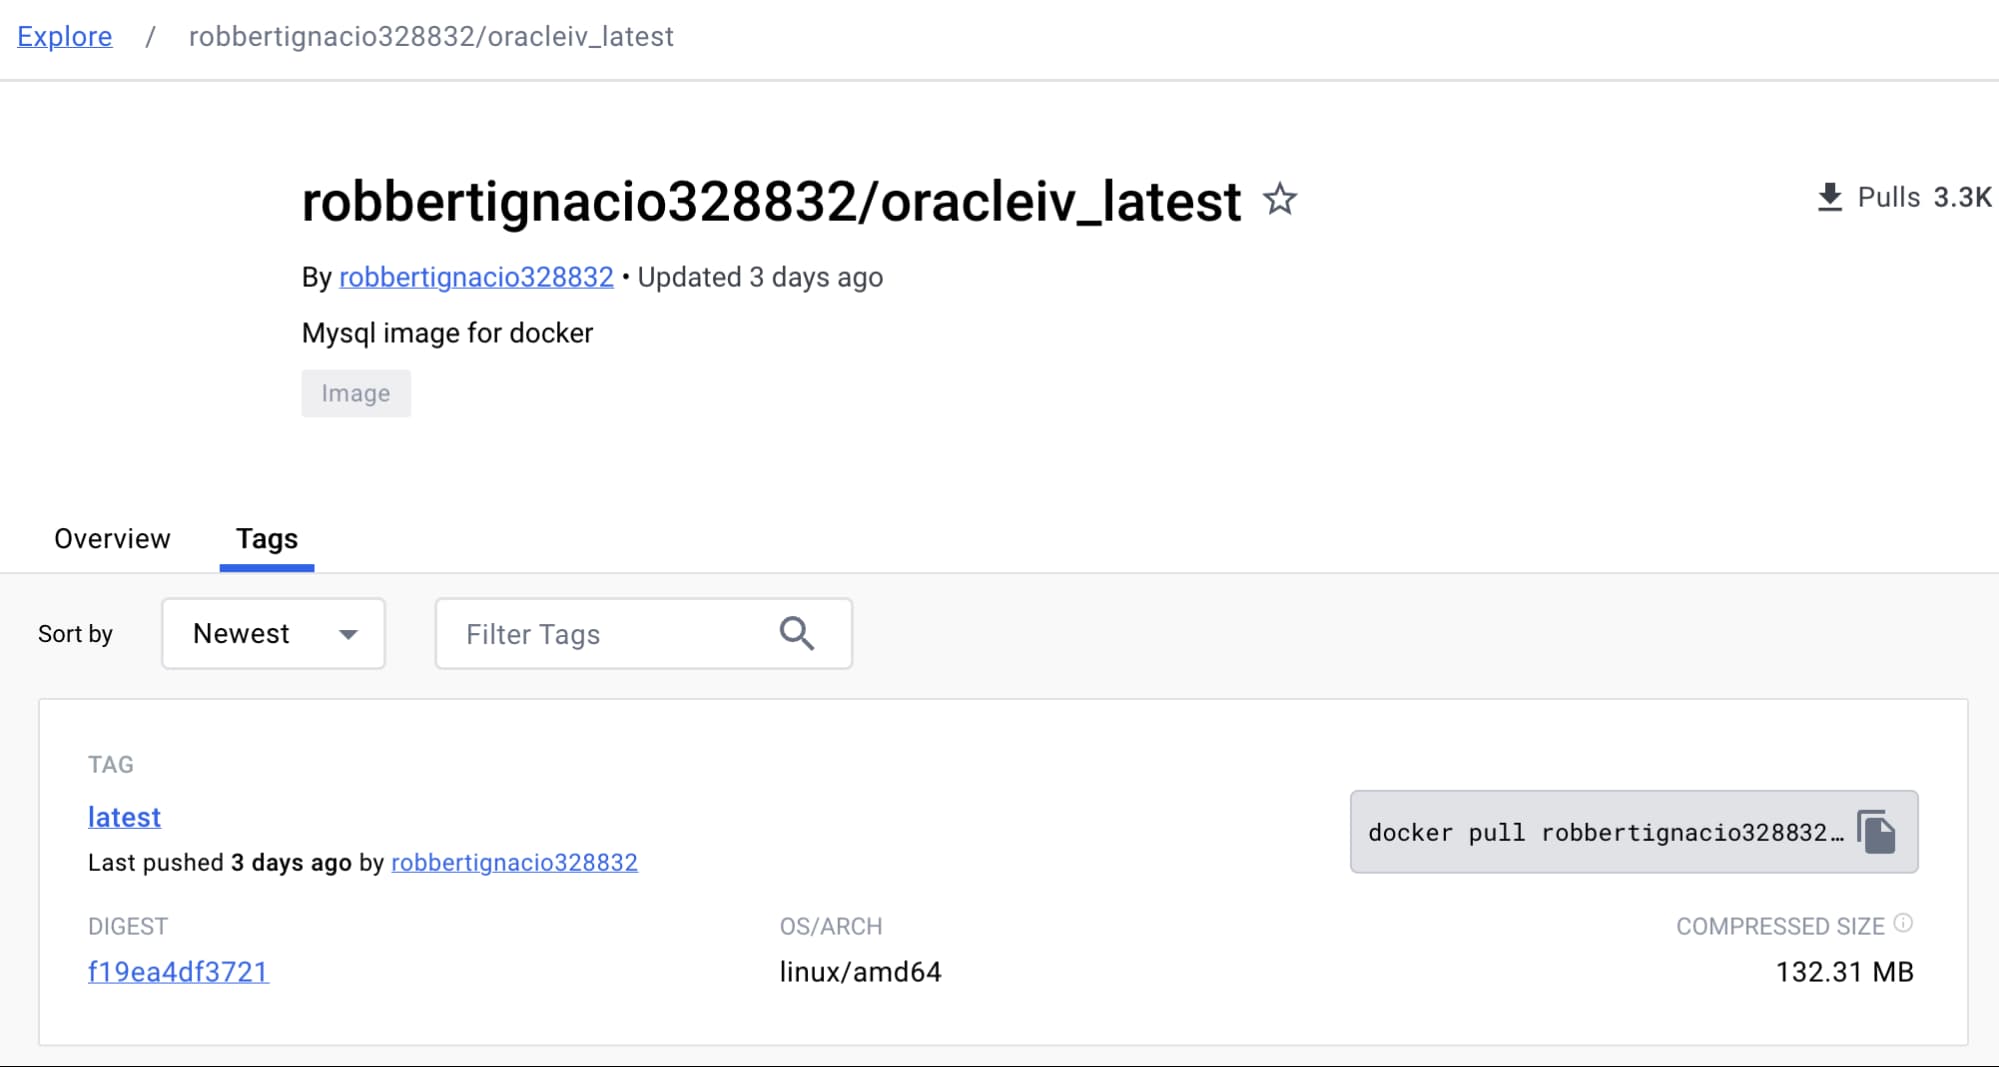
Cado Security researchers uncovered a live Dockerhub page for an image named “oracleiv_latest” uploaded by the user “robbertignacio328832.” The image, seemingly harmless as a “Mysql image for docker,” included a malicious payload named “oracle.sh,” an ELF executable acting as a DDoS bot agent. Further analysis revealed additional commands to retrieve XMRig and a miner configuration file.

Static analysis of the executable exposed a 64-bit ELF compiled with Cython, confirming the OracleIV malware’s Python code origin. The malware code, succinct yet potent, contains various functions dedicated to different DDoS methods.

“This image was still live at the time of writing and had over 3,000 pulls,” researchers explained in a blog post. Additionally, it seems to be undergoing frequent updates, with the latest modifications pushed just three days prior to the publication of Cado’s blog.

OracleIV DDoS Botnet Malware Targets Docker Engine API Instances
Dockerhub page for oracleiv_latest (Cado Security)

The bot connects to a Command and Control server (C2), performing basic authentication with a hardcoded password. Cado Security Labs monitored the botnet’s activity, witnessing DDoS attacks on various targets, primarily using UDP and SSL-based floods.

The C2 commands for initiating DDoS attacks follow a specific format, specifying attack type, target IP/domain, attack duration, rate, and target port. The botnet’s capabilities include UDP floods, SSL-based attacks, SYN floods, slowloris-style attacks, and protocol-specific floods targeting the FiveM server and Valve source engine.

While OracleIV is not a supply chain attack, it highlights the ongoing threat of misconfigured Docker Engine API deployments. The portability of containerization enables attackers to execute malicious payloads consistently across Docker hosts.

Although Cado Security has reported the malicious user to Docker, users are urged to conduct periodic assessments of pulled images from Dockerhub, emphasizing the need for vigilance against malicious code.

In conclusion, the OracleIV campaign highlights the importance of securing internet-facing services and implementing strong network defences. Users of Docker and similar services are encouraged to regularly review their exposure and take necessary precautions against potential cybersecurity threats.

  1. SSH Remains Most Targeted Service in Cado’s Cloud Threat Report
  2. Change your password: Docker suffers breach; 190k users affected
  3. Hackers Exploit Adobe ColdFusion Vulnerabilities to Deploy Malware
  4. Cryptomining and Malware Flourish on Misconfigured Kubernetes Clusters
  5. ShellTorch Attack Exposes Millions of PyTorch Systems to RCE Vulnerabilities

[ad_2]
Source link

Galaxy S24 Ultra’s new 50MP 5x zoom camera is bigger

0
[ad_1]

Samsung‘s next-gen flagship smartphones are just about two months away now. The Galaxy S24 series will arrive in January 2024, with the company releasing three models. As usual, the Ultra model will top the line, offering industry-leading cameras and more. Leaks have already revealed the phone’s camera setup. A noted industry insider has now detailed the new 5x optical zoom camera for the Galaxy S24 Ultra.

Galaxy S24 Ultra’s 5x zoom camera specs revealed

If you’re familiar with Samsung’s Ultra flagships, you may be aware that those phones have featured two telephoto cameras for the past few years. The Korean firm included one lens with 3x optical zoom and the other with 10x optical zoom. In an unexpected change, it is removing the latter next year and replacing it with a 5x lens. The Galaxy S24 Ultra will still feature two telephoto cameras but with 3x and 5x optical zoom capabilities.

Previous leaks have revealed that the new lens will be a 50MP sensor, which should mean higher resolution zoom photos (the 10x lens on the Galaxy S23 Ultra is a 10MP sensor). It is Sony’s IMX854 sensor featuring 0.7µm pixels. With an optical format of 1/2.52 inches, the new sensor is slightly bigger. The 2023 Ultra model’s 10x zoom camera has a 1/3.2-inch optical format with 1.12μm pixels.

Despite missing a 10x zoom lens, industry insiders believe Samsung will be able to maintain the same image quality at zoom levels higher than 5x thanks to the newer sensor and software processing. The Galaxy S24 Ultra is expected to keep the 100x hybrid zoom as well. On top of this, the phone may bring improvements in some other areas, like seamless 4K video recording at higher frame rates with all rear cameras.

The Galaxy S24 Ultra may also debut Samsung’s ISOCELL Zoom Anyplace system. It is a revolutionary zoom tech for 200MP cameras. It can automatically track and zoom in on a selected subject as it moves around. Your phone will simultaneously capture the zoomed footage and the full field of view. You can even see both footage on the screen. The new tech also maintains 4K video resolution up to 4x zoom and cuts the processing time by up to 50 percent.

The 2024 Samsung flagships may go official on January 17

Samsung has yet to confirm the launch date for the Galaxy S24 series. It isn’t time for the official media invites. However, the Korean media recently reported that the company has already finalized the date. It plans to unveil the 2024 flagships on January 17, 2024. While Samsung’s last Galaxy Unpacked event happened in South Korea, the company is going back to the US for the Galaxy S24 launch. Stay tuned for the official confirmation.


[ad_2]
Source link

Huawei achieves record-setting Wi-Fi 7 speed in lab test

0
[ad_1]

Huawei has achieved a record-setting Wi-Fi 7 speed in a lab test of its Wi-Fi 7 Access Point (AP). Conducted at Tolly Lab in the US, the first-ever industry test of the AP delivered a peak total throughput of 13.25Gbps and individual speeds of up to 4.33Gbps. The Chinese firm set new speed records for the next-gen wireless standard in the process.

Huawei breaks Wi-Fi 7 speed record in lab test

This lab test was the first successful performance testing of Huawei’s AirEngine 8771-X1T Wi-Fi 7 AP. The solution takes full advantage of the next-gen wireless standard with support for the 6GHz frequency band, up to 320MHz channel bandwidth, and 4096-QAM modulation. It boasts a dynamic zoom antenna array and supports 12 spatial streams.

For the uninitiated, spatial streams are a way of transmitting data over Wi-Fi using multiple antennas. The data you’re sending and receiving is split into multiple streams for simultaneous transmission of more data at high speed, making Wi-Fi networks more efficient. Wi-Fi 6/6E supports up to 8 spatial streams, while Wi-Fi 7 doubles that to 16.

Huawei’s new Wi-Fi 7 AP may not go to the full extent to support 16 spatial streams but it is still capable of delivering a throughput of up to 18.67Gbps. Tolly Lab managed to achieve a record-high speed of over 13Gbps in a controlled testing environment. According to Tolly, the single-device speed of 4.33Gbps is the fastest real-world Wi-Fi throughput tested to date (via Gizmoweek).

The firms could also reduce latency by 50 percent compared to Wi-Fi 6, dropping latency to just two milliseconds. This almost real-time responsiveness, coupled with advancements in speed, highlights the potential to unlock new capabilities for wireless networks. Huawei has given us an early glimpse of what the future holds for wireless connectivity.

Wi-Fi 7 can reach a theoretical top speed of over 40Gbps

The final Wi-Fi 7 standard is not official yet but is expected next year. At its full capacity (maximum channel bandwidth and spatial streams), the next-gen wireless standard can deliver a peak speed well over 40Gbps. However, the real-world speed is far less than the theoretical speed.

This is because of the way commercial solutions implement Wi-Fi specs, factoring in power consumption and other parameters. With a quad-stream (4×4) 320MHz client device, Wi-Fi 7 can reach a practical speed of about 11.5Gbps. That’s still more than four times faster than the peak real-world speed of 2.4Gbps delivered by Wi-Fi 6/6E. A generational leap in Wi-Fi speeds is now just around the corner.


[ad_2]
Source link

Channel usernames to come to WhatsApp (days after Signal introduced profile usernames)

0
[ad_1]
It’s the start of the week and WhatsApp has something new going on: soon, users may set usernames for channels on the popular messaging app.

WhatsApp’s plans come to light mere days after another messaging app – Signal – announced that it’s testing public usernames for individuals (via Android Police). Using usernames instead of phone numbers is a move in the direction of enhancing anonymity.

The last time we discussed WhatsApp and the possibility of introducing a usernames-instead-of-number feature, was in May. Back then, the rumor had it that WhatsApp could enable usernames and thus make it safer by no longer needing to reveal one’s phone number to other contacts within WhatsApp.

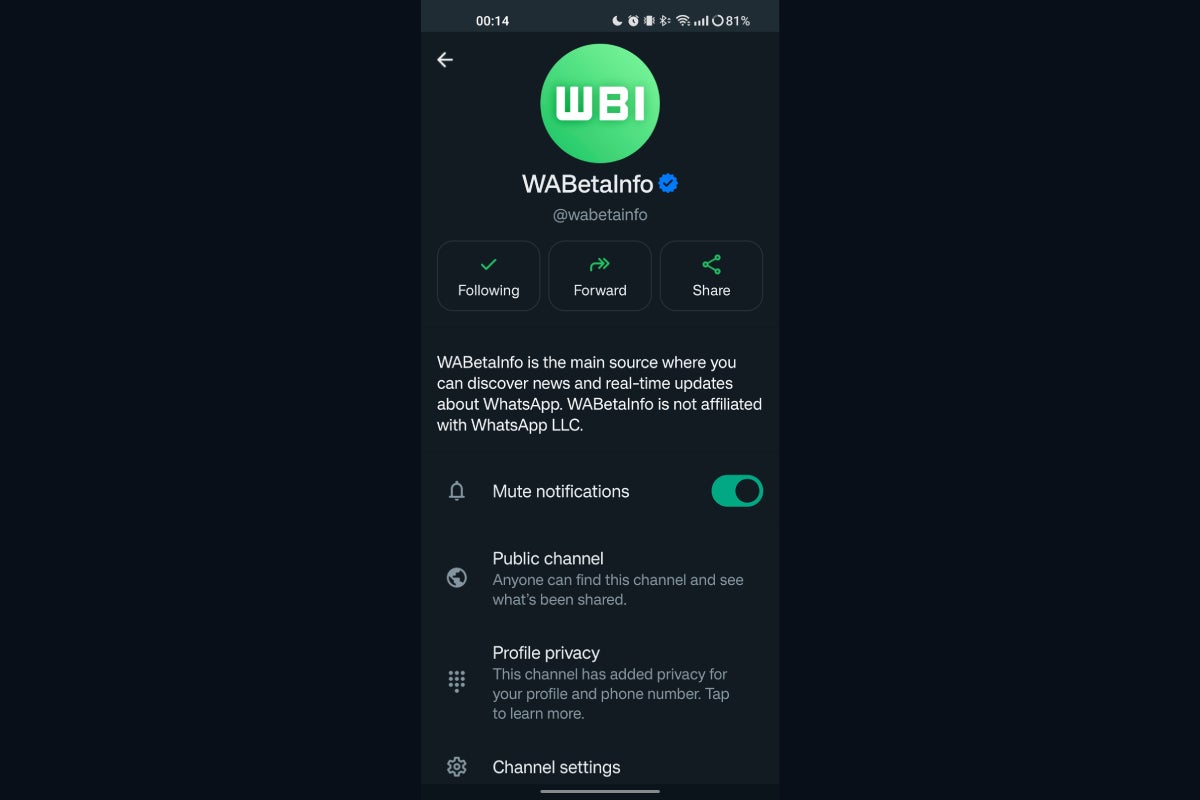
Half a year later, things have changed a bit. On the WABetaInfo site, there’s information that WhatsApp (that’s the beta for Android version 2.23.24.17) will not embrace profile usernames (for now; this feature is still being developed, but saved for a later point in the future), but usernames could arrive on channels.

This feature is under development so it’s not ready for beta testers, but you can get a glimpse, as there’s a preview from WABetaInfo, here it is:

“We believe that this feature brings important advantages to the user experience. Users will be able to share channel information more consistently by using usernames, since this finally eliminates the need to share complex channel links. In addition, channels can establish a more recognizable presence by having a unique username. We think that this is especially beneficial for anyone who want to build a distinct identity and make its channel easily accessible”, the team at WABetaInfo says.

WhatsApp ads should stay out of the inbox


Just the other day, WhatsApp once again reassured users that they won’t see ads in the super popular messaging app – at least not in their chat inbox section.

In an interview for a Brazilian news media, WhatsApp boss Will Cathcart elaborated on the app’s future and how Meta, which acquired WhatsApp, makes money with the free WhatsApp

When asked about displaying ads in the app, Cathcart emphasized that the company “will not place ads in the inbox or chats”.

“We don’t think that’s the right model. People, when they open their inbox, don’t want to see advertising,” he said. However, the executive doesn’t rule out the idea of WhatsApp showing ads in other parts of the app.


[ad_2]
Source link

Top Cybersecurity Threats for Employee Data

0
[ad_1]

Employee data—it contains some of your company’s most sensitive information. Salaries, social security numbers, health records…this stuff is like gold to cybercriminals. 

While you need access to employee data to run your business, keeping it secure is seriously tricky with today’s sophisticated hacking threats. A data breach could wreck your operations and demolish trust with staff. 

So how do you lock down employee data and protect your organization? Well, why not turn to the people who are responsible for holding and protecting hundreds of thousands of employee records across a wide range of industries? As a leading HR platform for over 3,000 companies, HiBob helps organizations manage sensitive employee information each and every day. 

It’s safe to say these folks know employee data security inside and out as they tirelessly work to minimize and eliminate every HiBob vulnerability they can find. In this guide, we’ll share HiBob’s recommendations on the biggest threats to watch out for and best practices to boost security. So, whether you’re in HR, IT, or the executive suite, use these tips from employee data pros to secure your systems. Let’s dive in!

The Rising Threat of Phishing

“Phishing and social engineering represent one of the biggest cybersecurity threats to employee data. Hackers are getting extremely sophisticated with personalized phishing emails and social media scams aimed at specific employees. If they can trick one person into giving up their login credentials, it can give access to tons of sensitive company information.” – Tamir Ronen, HiBob’s CISO.

Today’s phishing attacks are highly personalized based on reconnaissance of employees on social media. This makes the phishing attempts seem authentic, tricking employees into giving up login credentials or sensitive data.

Once hackers gain an employee’s login information through phishing, they can access company systems and steal troves of confidential employee records, financial data, intellectual property, and more. To protect against phishing threats, try:

  • Ongoing security awareness training to educate employees on phishing identification
  • Multi-factor authentication across all systems to secure accounts
  • Email security tools to detect and block phishing attempts
  • Monitoring for spikes in phishing activity during high-threat periods
  • Keeping antivirus and spam filters up-to-date to catch the latest phishing tactics

With a layered defence strategy, you can develop strong protections against rising phishing risks.

The Password Problem

“Many data breaches happen not because of fancy hacking techniques, but simply employees using weak, reused passwords. Organizations need to implement strong password policies and multi-factor authentication across all systems containing sensitive data.” – Tamir Ronen, HiBob’s CISO.

HiBoB points out that weak and reused passwords are behind many data breaches. Employees often use simple passwords across multiple sites, and hackers take advantage of this through credential-stuffing attacks. 

Using usernames and emails from breached databases, hackers can gain system access using compromised passwords. This allows them to steal employee data, implant malware, or hold data hostage for ransom. To improve password hygiene, try:

  • Enforcing strong password policies with complexity requirements
  • Requiring regular password changes to thwart stale credentials
  • Providing a password manager to generate and store strong passwords
  • Enabling multi-factor authentication across sensitive systems
  • Conducting brute force attack monitoring to identify compromised accounts

With proactive password best practices, companies can shut the door on data breaches through poor password hygiene.

The Remote Work Risks

“With the rise of remote and hybrid work environments, more employee data is being accessed and stored outside of corporate firewalls. Without proper encryption, this data can be easily compromised if a device is lost or stolen. Encrypting employee data should be a top priority for data security.” – Tamir Ronen, HiBob’s CISO.

More employee data is now accessed remotely and stored on devices outside of corporate networks than ever before. This introduces risks of data exposure if devices are lost, stolen, or otherwise compromised.

Unencrypted data on remote devices can provide access to employee records, emails, system credentials, and other sensitive information. A single compromised device can lead to a disastrous data breach. To reduce remote work risks, try:

  • Enabling hard drive and file encryption on all endpoints to protect data
  • Using a virtual private network (VPN) for secure remote access
  • Restricting data and system access to only what is needed
  • Providing remote security training on safe device usage
  • Implementing robust device wipe capabilities in case devices are lost

With strong encryption, access control, and remote security measures, companies can embrace flexible work while preventing the leakage of sensitive employee data.

The Overprivileged Account Danger

“Not everyone in an organization needs access to employee data like HR records, payroll info, etc. However, overprivileged credentials are a common issue,” warns Tamir Ronen, HiBob’s CISO. “Companies need to implement least privilege access and role-based permissions to limit exposure.” – Tamir Ronen, HiBob’s CISO.

HiBoB points out that overprivileged credentials give employees unnecessary access to sensitive systems and data. This creates significant risks of insider threats, whether through intentional misuse or accidental leakage.

Overly permissive access enables employees to view, share, or modify confidential employee information like salaries, health records, and performance data beyond what their role requires. To limit data exposure, try:

  • Conducting access reviews to identify and revoke unnecessary permissions
  • Implementing role-based access controls and least privilege policies
  • Limiting access to strictly need-to-know data per job duties
  • Enabling detailed access audit logging for regular review
  • Cutting off system/data access immediately for employees who leave the company

With strong access governance, companies can significantly reduce risks associated with overentitled employee credentials.

In Closing

Protecting employees’ data is getting tougher every day. Between insidious phishing scams, weak passwords being too easily guessed, and sensitive info flying around unencrypted—it’s a real challenge securing all that critical information.

While no single product is foolproof against today’s cyber threats, combining aware users, tough tech safeguards, and sound policies can make your company resilient. Layering on different defences strengthens your protections, and guiding employees on security best practices pays off down the road by keeping data—and your company’s reputation—safe. 

  1. Google Employees Data Stolen After Data Breach
  2. Data of Israeli Employees from 29 Logistics Firms Sold Online
  3. Killnet Claim They’ve Stolen Employee Data from Lockheed Martin
  4. Stolen: Unencrypted drives with data of 29K Facebook employees
  5. Private Data of 240,000 DHS Employees Accessed after Data Breach

[ad_2]
Source link

Google sees huge growth in the US smartphone market: Canalys

0
[ad_1]

Google has marked huge growth in the US smartphone market, based on the latest report from Canalys. The company has released its ‘Smartphone Market Pulse’ report for Q3 2023, revealing the top smartphone OEMs, and their numbers.

Google managed to secure huge growth in the US smartphone market thanks to its Pixel phones

Let’s start from the top. Apple is still the number one smartphone OEM, and it’s not even close. The company managed to sell 17.2 million smartphones in the third quarter, and holds a 55% market share.

Canalys US smartphone market Q3 2023

Samsung is second-placed with 6.8 million units sold, and 22% of the market. Motorola sits in third place with 2.8 million units sold, and 9% of the market. TCL is fourth with 1.3 million units sold, and is currently holding 4% of the market.

Google is in fifth place, with 1.2 million smartphones sold, and the company is also holding 4$ of the market, just like TCL. All the other companies are holding 5% together, which truly shows the dominance of Apple and Samsung.

Motorola & Google are the only ones who grew YoY

Now, the only two companies that marked annual growth are Motorola and Google. In Q3 2023, Motorola grew 14% compared to the same period last year. Google, on the other hand, marked a staggering growth of 117%.

That growth was quite visible in Q2 2023 as well, when it was 59% compared to the same period last year. Google is obviously doing something right as it managed to attract consumers in the States.

Of course, that’s nowhere near what Apple and Samsung are able to achieve, but that is to be expected. Google needs to do the same outside of its homeland too, though, where things look entirely different.

It will be interesting to see if those numbers can improve further by the end of the year. The holidays are coming, and along with them a ton of discounts, not to mention the fact that Black Friday is right around the corner.


[ad_2]
Source link

Huawei’s first EV is now available to preorder at $35,400

0
[ad_1]

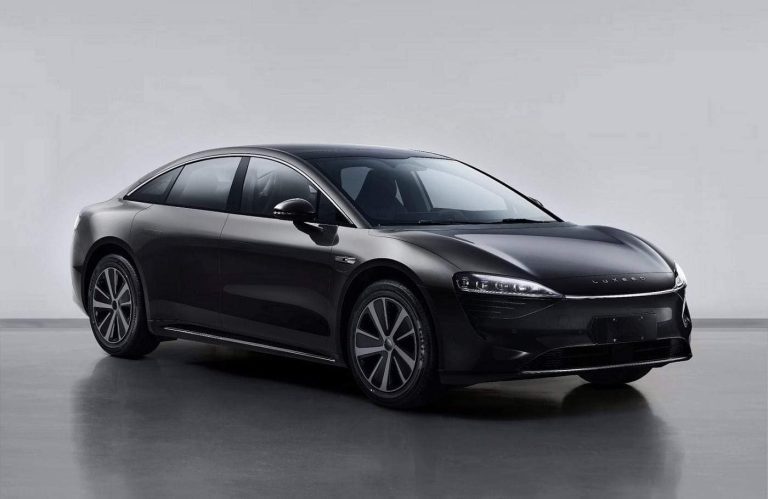
We’ve been hearing rumblings about Huawei’s EV for years, and now it is finally here. Huawei Luxeed S7 is a sedan launched jointly by the Chinese OEM and Cherry. It aims to challenge Elon Musk’s Tesla Model S.

Following the United States sanctions on Huawei, the tech firm decided to diversify its portfolio and enter new business segments. We first heard about Huawei’s adventure in the EV segment a few years ago when it turned to different Chinese automakers for its project.

On November 9, Richard Yu, chairman of Huawei’s intelligent vehicle solutions business unit, finally unveiled the Luxeed, a joint EV brand between Huawei and Cherry. This is Huawei’s second take in the EV segment after Aito M9, which emerged in 2021.

While the official launch and regular sale is scheduled for the end of this month, the Luxeed S7 is now open for pre-orders at just 258,000 yuan ($35,400). Richard Yu formerly said the Luxeed S7 can surpass Model S “in every specification.”

Huawei Luxeed S7 is a competitor to Tesla Model S

As a mid-to-large sedan, the Luxeed S7 is available in Pro, Max, Max+, and Max RS variants. Each model launches with its specifications and range. The most expensive model is Max RS, which costs around 358,000 yuan ($49,000). The four versions have CLTC ranges of 550 km, 705 km, 800 km, and 630 km, respectively.

The Luxeed S7 is also available in single-motor (215 kW) and dual-motor (215 kW + 150 kW) four-wheel drive variants. The dual motor model can hit the 100 KM milestone in just 3.3 seconds.

The vehicle is built based on Huawei’s “Giant Whale” 800 V high-voltage platform and uses the thinnest 800 V battery pack ever made. While we don’t know how much it takes to charge the vehicle fully, Yu said the Luxeed S7 has a range of 200 KM with just five minutes of charging. It can also travel 400 km with 15 minutes of charging. In comparison, the Tesla Model S ranges 347 KM after the same charging period.

On paper, Huawei Luxeed S7 mileage and specification seem irresistible, and it could certainly take on the Tesla Model S. Huawei’s EV also has an easier job convincing local customers as the basic Model S in China costs around 698,900 (($95,800).


[ad_2]
Source link