Multiple Vulnerabilities Found In PureVPN

0
[ad_1]

Researchers spotted a couple of security vulnerabilities in PureVPN Desktop clients for Linux that impact users’ privacy. While PureVPN patched one flaw, another RCE vulnerability remains unpatched.

Numerous PureVPN Vulnerabilities Affected Linux Clients

Security researchers Rafay Baloch and Muhammad Samaak discovered two different vulnerabilities when analyzing PureVPN Linux clients. In his blog post, Baloch specified the two issues as an IP leak and a remote code execution (under certain conditions).

The IP leak issue was caused by the improper handling of DNS queries by the PureVPN Linux client. Consequently, the vulnerability allowed VPN tunnel bypass, exposing the DNS queries to the ISP or the default DNS servers leaking users’ original IP addresses.

The researchers could verify this vulnerability through a simple IP leak test via Ipleak.net. As demonstrated, the original IP address from Pakistan clearly appeared in the DNS leak test despite being connected to a PureVPN server with Indian IP.

Talking to LHN, Baloch deemed this vulnerability “as severe as an RCE” because it fails to serve the entire purpose of using a VPN.

The second vulnerability is a remote code execution that existed due to how the PureVPN Linux client works. An adversary could exploit this vulnerability for malicious purposes, such as stealing credentials, bypassing app whitelists, and triggering denial of service. Describing the exact issue, the post reads,

When the login button is activated, a system call called ‘opennat()’ is initiated. This system call aims to load the ‘libnssckbi.so’ shared library file from a location that allows user-writable access… However, it is essential to note that the specified path lacks the existence of the ‘libnssckbi.so’ file.
This presents a security vulnerability, potentially enabling malicious actors to execute arbitrary code by placing a file named ‘libnssckbi.so’ in the designated path.

The following video serves as a PoC for the PureVPN remote code execution flaw.

PureVPN Patched The IP Leak – But The RCE Awaits An Appropriate Fix

Upon discovering the flaws, the researchers reported the matter to PureVPN. In response, PureVPN fixed the IP leak issue but refused to address the RCE flaw.

Despite being a severe issue, exploiting the RCE flaw requires local access to the target system. Besides, analyzing the root cause of this code execution vulnerability made evident a broader issue affecting many other applications too. This vulnerability didn’t typically affect PureVPN; rather, it existed in Chromium’s Electron software framework that powers PureVPN, Google Chrome, Slack, and more, making all the apps similarly vulnerable.

That’s what PureVPN and Google Chrome highlighted in their responses to Baloch’s report. Consequently, while PureVPN put the onus of addressing the flaw on Google, the latter simply deemed the matter as out of the scope of its threat model.

However, Baloch noted that the vulnerability shouldn’t be taken lightly for a critical application like PureVPN.  Commenting on his interaction with PureVPN regarding the bug disclosure, Baloch told LHN,

The response was satisfactory; however, I expected a more aggressive response given that they are a security company, and user privacy is their primary concern. The RCE has been marked as “Won’t fix.” However, especially for a VPN service that users rely on for enhanced privacy and security, this should have been addressed.

Watch Out For VPN Issues

While security vulnerabilities are always risky, they are particularly dangerous for VPN users as they directly impact users’ online privacy. Therefore, whenever such reports surface online, users must pay attention to the matter and ponder over continuing their VPN use until bug fixes.

For example, in September, AtlasVPN made it to the news for a zero-day affecting its Linux clients. While the service pledged to deliver a fix, it took them a few days to release the patch. Until then, the users remained vulnerable to exploits unless they stopped using the service.

In the case of the recently discovered PureVPN vulnerabilities, the unpatched RCE flaw isn’t as dangerous since it typically requires local access from an attacker. Nonetheless, users who cannot surely prevent unwarranted local access to their devices must remain careful about PureVPN’s use until the matter gets fixed.

Let us know your thoughts in the comments.


[ad_2]
Source link
Galaxy A25 5G specs and alleged price leaked early

0
[ad_1]

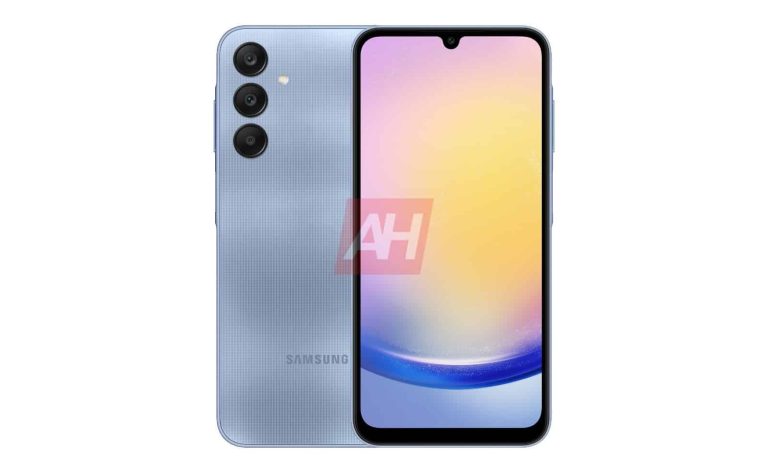
Samsung‘s Galaxy A25 5G might go official sooner than expected. Following our exclusive leak last week where we revealed the phone’s official renders, the device picked up the FCC certification. It confirmed some specs, including the charging speed. Now, most of its key specs have been leaked. The new report also gives us a rough pricing structure for the phone.

Galaxy A25 5G specs leaked ahead of launch

Rumors about the Galaxy A25 5G have been around for a few months now. During this time, we saw the phone in a few benchmark listings as well. So we already have a fair idea of its specs. A new report by Appuals now gives us a round-up of all the available information, along with some additional details.

For starters, the upcoming mid-range Samsung phone will be powered by the company’s in-house Exynos 1280 processor. It’s a 5nm chipset with a peak CPU speed of 2.4GHz. The Korean firm will sell the phone in 6GB+128GB and 8GB+256GB memory and storage configurations. The FCC recently revealed that the Galaxy A25 5G will feature a microSD Card slot, so you can expand the storage space externally.

The phone sports a 6.5-inch display with an FHD+ resolution. It should be a Super AMOLED panel with at least a 90Hz refresh rate, if not 120Hz. As for cameras, Samsung is keeping the same 50MP primary shooter as the Galaxy A24. It’s paired with an 8MP ultrawide lens, a 2MP macro camera, and a 13MP selfie camera. The main rear camera should support OIS (Optical Image Stabilization).

The new report adds that the Galaxy A25 5G will pack a 5,000mAh battery with 25W wired charging, something the FCC certification has already confirmed. Samsung is readying the handset in Black, Blue, Silver, and Yellow colors. We have already revealed its renders in all four shades. It plans to price both storage versions of the phone between €300 and €400. If the device is sold in the US, it may start at around $300.

Samsung might unveil the new phone earlier than its predecessor

Interestingly, the report says that the Galaxy A25 5G will ship with Android 13 onboard rather than Android 14. If this is true, Samsung may be planning to launch the phone earlier than its predecessor. The Galaxy A24 debuted in April this year. While the company usually follows up with a succeeding model a year later, we don’t see the Korean firm releasing a phone with Android 13 in April 2024. We will let you know when we have more information.


[ad_2]
Source link

OpenAI is reaching out to organizations to build new data sets

0
[ad_1]

OpenAI’s LLM is already insanely packed with knowledge, but the company is not stopping the pursuit of knowledge. It’s still looking for new ways that it can train its AI to bring it closer to human sentience. According to a new report, OpenAI is working with different organizations to help create new datasets to train its AI.

This is something that all AI companies are trying to do; stuff as much knowledge into their LLMs to keep up with the competition and protect their revenue (oh yeah, and maybe push AI forward). There’s a massive amount of human data floating around in these LLMs from Meta, Google, OpenAI, Anthropic, X Corp, and others. However, there’s not enough for them to be satisfied.

The dream for most of these companies is to develop AGI (artificial general intelligence). When that’s achieved, an AI will basically be as smart as a human being. That’s still several years away, however.

OpenAI is looking to create new datasets to train its LLM

OpenAI is on the prowl for more information to train ChatGPT and other products. It recently began reaching out to private and public organizations for them to submit datasets. These datasets could really be about anything, according to the company. They just need to represent human knowledge. That’s pretty broad, and it shows that the company isn’t being picky about the data.

However, it is looking mostly for data in the Icelandic language. So, it looks like the company is addressing a gap in its knowledge. Representatives from public and private organizations can submit their datasets to OpenAI today.

This is all a step forward to help the company improve ChatGPT and other chatbots. It’s also a way for the company to obtain data with the consent of others. Right now, companies acquire their data by scraping websites for their data. This is something that these companies have gotten in trouble for doing.


[ad_2]
Source link

Lockbit Ransomware Leaks Boeing Data Trove

0
[ad_1]

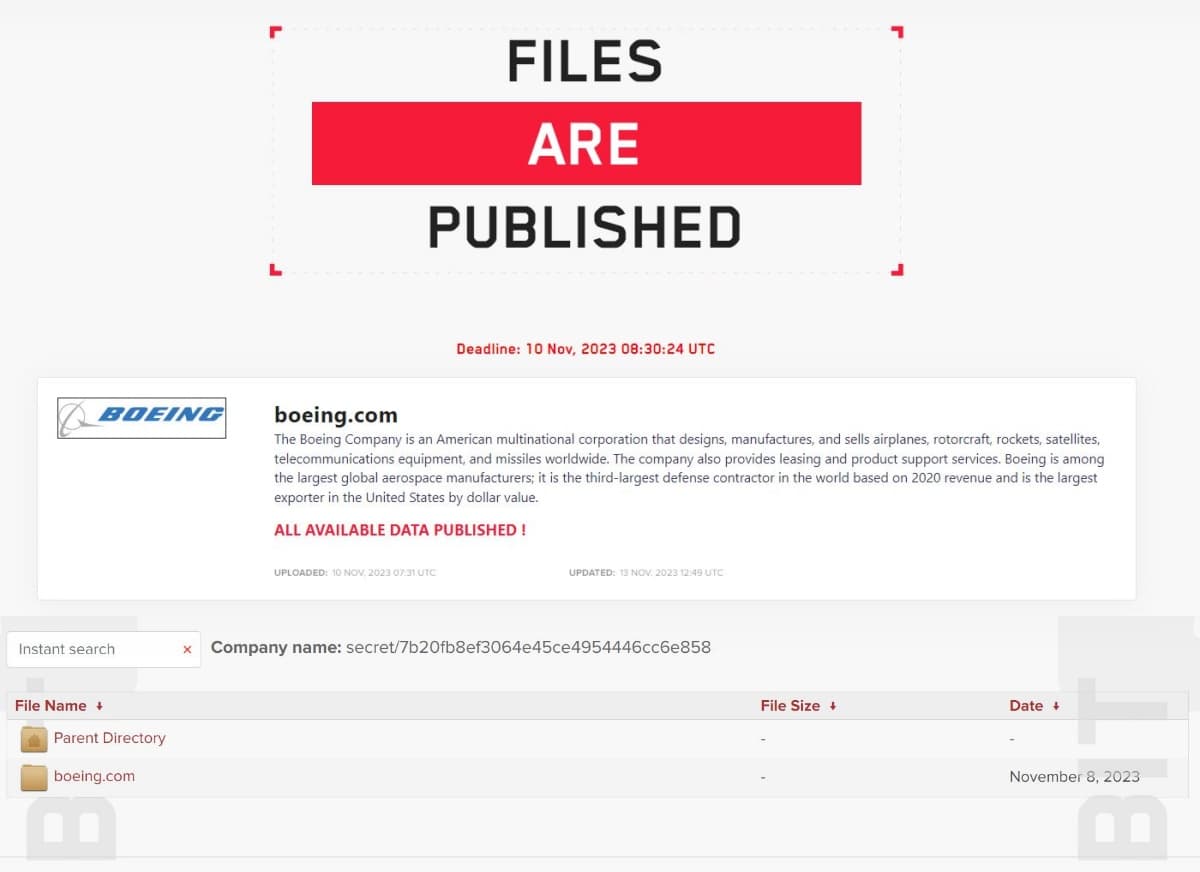
The notorious Lockbit ransomware group has leaked a trove of data belonging to the leading global aerospace company Boeing, apparently following failed ransom negotiations.

The notorious LockBit ransomware group has struck again, and this time, its victim is aerospace giant Boeing. The ransomware gang infiltrated Boeing’s systems and stole a significant amount of sensitive data. 

Timeline of the attack and data leak

On October 27, 2023, the hackers mentioned Boeing on their data leak website, and gave the firm a 2nd November deadline, revealing to have exfiltrated a tremendous amount of sensitive archive and backup data. The company was given 48 hours to contact LockBit.

On November 2nd, 2023, as reported by Hackread.com, Boeing acknowledged that it suffered a cyberattack but did not confirm whether it was a ransomware attack and if Lockbit’s claims were authentic.

Later, the group removed Boeing from its site, claiming that negotiations had started. Then, the company reappeared on November 7 with another message from LockBit stating that the company ignored warnings. 

The hackers then published 4GB of data as a sample, which comprised backup files of different systems featuring an October 22 timestamp. Boeing’s continued silence on the incident prompted LockBit to release all the stolen data on their website on November 10.

Lockbit Ransomware Leaks Boeing Data

This included Boeing’s IT management software’s configuration backups, and auditing/monitoring tools logs. It also included Citrix appliances’ backups, sparking speculation that the hackers might have exploited the Citrix Bleed vulnerability (CVE-2023-4966).

According to MalwareHunterTeam’s assessment, most of the exposed files are associated with a Boeing-owned aviation and aerospace parts manufacturer called Aviall.

Boeing, one of the world’s leading aerospace firms that operate defence systems and commercial aeroplanes, has confirmed the hacking, stating that it is investigating the incident to verify LockBit’s claims and “determine the scope of any potential data breach.”

The company intends to take “appropriate steps” to protect its customers and information. Boeing has also stated that the incident doesn’t threaten aircraft or flight safety. 

Boeing’s services website is down currently. This is a developing story, and Hackread will update you about the incident when there’s some clarity about the root cause of the hacking.

The LockBit ransomware gang has been active since 2020 and claimed several high-profile victims, including DXC Technology, Accenture, and the German government, via double extortion. As per CISA’s advisory, since 2020 LockBit targeted 1,700 US firms and made around $91 million in ransom payments.

What Experts Have to Say!

Comparitech’s head of data research, Rebecca Moody, shared an exclusive comment on this incident with Hackread.com, stating that LockBit has emerged as one of the most prevalent ransomware-as-a-service operators this year.

“LockBit has been particularly prevalent this year when it comes to the confirmed ransomware attacks we’ve tracked worldwide. So far this year, we’ve recorded 122 confirmed LockBit attacks,” Rebecca said.

Rebecca further revealed that “In 2022, we recorded 97 LockBit attacks throughout the entire year. The number of confirmed records impacted by these breaches has skyrocketed, too. In 2022, LockBit is confirmed to have stolen 957,438 records across 26 attacks (creating an average of 36,825 records per attack).”

“This year, just over 9.3 million records are confirmed to have been impacted in 20 attacks (465,194). Adding to this are the huge ransom demands being made by the cybercriminals. So far, LockBit has demanded a whopping $196.6 million in ransoms across 15 attacks alone (an average of $13.1 million per case). In 2022, $137.4 million was demanded across 18 cases (an average of $7.63 per case),” she explained.

Nevertheless, while not new to cyberattacks, when it comes to cybersecurity, it is a challenging day for Boeing. It will be crucial to see how the company responds to the situation.

  1. Bangkok Airways hit by Lockbit ransomware; leaks 103GB of data
  2. Accenture claims to fight off LockBit ransomware gang with backup
  3. LockBit ransomware gang blames victim for DDoS attack on its website
  4. LockBit 3.0 Posts Dubious Claims of Breaching Darktrace Cybersecurity Firm
  5. Cyber Security Giant Mandiant Denies Hacking Claims By LockBit Ransomware

[ad_2]
Source link

WhatsApp Enhances Call Security With Location Hiding, Unknown Call Block

0
[ad_1]

Stepping ahead to enhance users’ privacy, WhatsApp improvises its call feature security by launching two new features. These features facilitate users in hiding their location during calls and block calls from unknown numbers.

WhatsApp Rolls Out Location Hiding And Spam Call Block

Earlier this year, WhatsApp launched the “Silence Unknown Callers” to let users block unknown calls. First announced in June, the new feature appears in the WhatsApp Privacy settings under the “Calls” section as a toggle on/off menu.

Enabling this feature prevents calls from unknown numbers from ringing, saving the users from unwanted interruptions. Moreover, this feature also protects users from potential cyber threats originating from malicious calls, such as social engineering and malware/spyware attacks.

Explaining this feature’s importance in a blog post, Meta stated that the loads of protocols used in calling software increase the attack surface as criminal hackers can exploit unpatched vulnerabilities for malicious purposes. At times, the target users don’t have to interact with incoming calls as the attackers trigger zero-click attacks.

Although numerous call-silencing features already exist with calling software, they merely silence the incoming calls from ringing without preventing potential bug exploits.

However, WhatsApp’s “Silence Unknown Callers” not only prevents calls from unlisted numbers but also bypasses the normal call flow. WhatsApp implements a “specialized protocol for delivering stripped-down, silenced call notifications to recipients,” protecting the recipient device from attacker-controlled data.

After successfully launching this feature, WhatsApp has introduced the location hiding feature during a WhatsApp call. Specifically, this feature hides the users’ IP addresses by relaying calls via WhatsApp servers without disturbing the usual end-to-end encryption.

However, this feature isn’t specific to WhatsApp since other messaging apps like Signal and Telegram offer call relays already. Nonetheless, it will serve as another good reason for privacy-savvy WhatsApp users to continue using the app, besides the Proxy feature rolled out in early 2023.

Let us know your thoughts in the comments.


[ad_2]
Source link
Samsung Galaxy Xcover 7 Official Renders

0
[ad_1]

Last week, we gave you exclusive official renders of Samsung’s upcoming mid-range smartphone, the Galaxy A25 5G. Today, we bring you an exclusive look at another upcoming Samsung handset courtesy of our trusted, confidential source. This time, we have official renders of the company’s next rugged phone, the Galaxy Xcover 7.

Galaxy Xcover 7 exclusive official renders

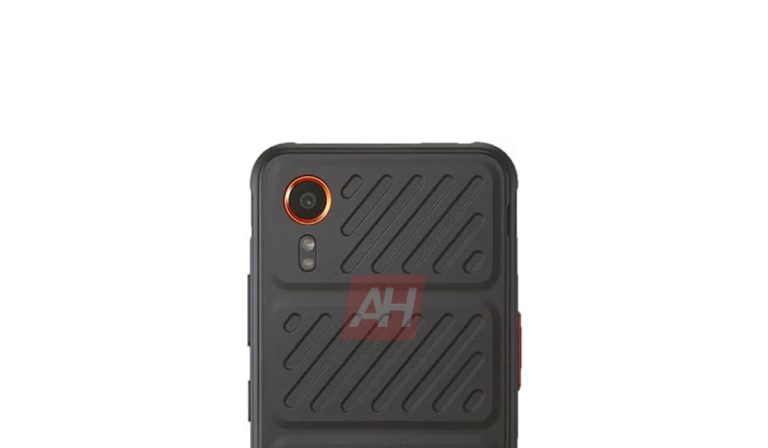
Samsung’s Xcover lineup has given us some of the most durable Android smartphones over the years. The Galaxy Xcover 7 fits the bill perfectly with its rugged build. It features a sturdy frame and rear panel with a grooved design and raised corners for better grip and shock absorption. The rear panel is user-removable, which should mean a removable battery too. The battery capacity and charging speed are not known.

The phone has a single camera on the back, along with a dual-LED flash unit. The camera ring has a red accent, something we have seen on previous Xcover phones too. The same hue is also found around the customizable Xcover key on the left side. Users can set the key to execute a specific function, including opening apps, Push-to-Talk, barcode scanning, and more. The power and volume buttons are on the right side.

The Galaxy Xcover 7 has sizable display bezels, which is common on rugged smartphones. Like the rest of the specs, we don’t have details about the display size and resolution. However, Samsung should offer heightened touch sensitivity so the screen is usable with wet hands or with gloves on. Overall, we are expecting a MIL-STD-810H-compliant build quality with IP68 dust and water resistance and drop-to-concrete resistance.

It might be an affordable rugged smartphone

The Galaxy Xcover 7 will succeed Samsung’s Galaxy Xcover 6 Pro launched in June last year. While we don’t have the specs of the upcoming phone, it might not be a direct sequel to the 2022 model. The new Xcover bears the model number SM-G556B, while that of the previous-gen device is SM-G736B. Based on the Korean firm’s convention, we might be looking at the sequel to 2021’s Galaxy Xcover 5 (SM-G525F). This is perhaps why it lacks the Pro branding.

Of course, this is not set in stone yet. But if things turn out this way, the Galaxy Xcover 7 should cost less than the Galaxy Xcover 6 Pro, which debuted with a price tag of $600. A single camera on the back is another hint that the new model is a more affordable rugged smartphone. However, we will know for sure only when more details about the phone emerge. Stay tuned and we will let you know as soon as we have additional information.


[ad_2]
Source link

Court orders Amazon to pay $46.7 million over Alexa patent infringements

0
[ad_1]

Amazon patent infringements are again costing the giant retailer a sum of money. A Delaware federal court has ruled that Amazon should pay $46.7 million to Nuance Communications-owned VB Assets over violating the rights of four patents used in Amazon’s Echo smart speakers and Alexa. VB Assets says it had a meeting with Amazon in 2017 to discuss the patent rights.

VB Assets, previously known as VoiceBox Technologies, filed its lawsuit in 2019. The company then claimed it held the rights to a circular speaker that can connect to the web and answer questions with a female voice. This is similar to Amazon’s Echo speakers and Alexa voice assistant. VB Assets claims it had developed the prototypes of such a product long before Amazon announced its products.

Alexa and Echo smart speakers cost Amazon $46.7 million in a patent infringements case

The VB Assets’ prototype, dubbed “Cybermind,” already appeared in a YouTube video. In that video, someone asks a speaker, “Computer, what is the NBA schedule?” and “Computer, what is the forecast for Sunday?”. Other prompts such as “Computer, find me a good recipe for chocolate cheesecake.” are also asked from the alleged speaker. The speaker then answers the questions by finding responses on the Internet.

As per the lawsuit, VoiceBox has developed a voice assistant for Lexus cars called Alexus “that showcased the power of its conversational Voice technology.” The company now argues the Alexus concept was made public over six months before Amazon introduced its Alexa voice assistant. Additionally, VoiceBox’s founders reportedly started to add natural language processing to computer applications in 2001.

The lawsuit further adds that the VoiceBox team met with Amazon in 2011 “to explore a potential business relationship where VoiceBox Technologies would provide core [natural language understanding] services to Amazon.” Echo speakers and Alexa were launched in 2014.

The Delaware federal court ordered Amazon to pay the compensation through running royalty rather than a lump sum. While VoiceBox had previously accused Amazon of infringing six patents, the court found the retailer guilty of infringing only four patents. Amazon didn’t respond to requests for comment, but it still has time to appeal the ruling. VoiceBox can also seek reimbursement for related costs.


[ad_2]
Source link

Samsung unveils Android 14 update calendar for Galaxy devices

0
[ad_1]

Samsung has released its official Android 14 update calendar for Galaxy devices. The big update, which comes with One UI 6.0, will roll out to most eligible devices before the end of the year, at least according to the current roadmap. The company may delay the update for some models if it discovers major bugs or other issues.

Android 14 will reach most Samsung phones this year

Samsung started pushing the stable Android 14-based One UI 6.0 update to its phones in late October. To be precise, the Galaxy S23 series got the update on October 30. The company has yet to release the new Android version for any other model. It appears that was the plan all along. The roadmap, posted by a Samsung Community Manager shortly after the update was released for the Galaxy S23 series, says so.

According to the official calendar, the next Galaxy devices to receive Android 14 are Galaxy Z Fold 5, Galaxy Z Flip 5, Galaxy A34 5G, and Galaxy A54 5G. Both of these devices are supposed to get the update today, November 13. As of this writing, the rollout hasn’t begun, but there’s still time. Hopefully, Samsung hasn’t delayed the update, as it did for the Galaxy S23 lineup in its home country.

Following the latest foldables and mid-rangers is the Galaxy S22 series, which should pick up Android 14 later this week. The Galaxy S21 series, Galaxy Z Fold 4, Galaxy Z Flip 4, Galaxy Z Fold 3, Galaxy Z Flip 3, Galaxy S23 FE, Galaxy S21 FE, and all eligible A-series phones from the past couple of years are also expected to make the jump to Android version 14 this month. The remaining few devices will follow in December. You can see the full calendar below.

Samsung Android 14 One UI 6 release timeline calendar roadmap

This roadmap may not apply globally

It’s worth mentioning that Samsung released this Android 14 update calendar specifically for Europe. The roadmap may not apply globally. Some of these devices weren’t sold in other markets, while a few phones sold in other regions never arrived in Europe. The precise release date could differ depending on the total number of eligible devices and other factors.

However, the One UI 6.0 release timeline should roughly match this calendar in most countries. Samsung appears to be planning to push the big update to most of the eligible Galaxy phones and tablets before stepping into 2024. It will begin the new year with the Galaxy S24 launch, reportedly on January 17. We will keep you posted as Samsung updates more phones to Android 14.


[ad_2]
Source link

Streamlining Bitcoin’s data queries: Graph’s indexing

0
[ad_1]

In the ever-evolving world of cryptocurrencies, Bitcoin stands as a pioneer and the most recognized digital currency. Its decentralized nature and transparency through a public ledger, known as the blockchain, have made it a subject of intense study and scrutiny. With millions of transactions occurring on the Bitcoin network every day, efficiently querying and analyzing this vast dataset has become a critical challenge. In this article, we delve into the world of Bitcoin data querying and explore how graph indexing plays a pivotal role in streamlining this process. If you are a beginner and are looking for an ideal platform for crypto, Altex Momentum is an excellent choice.

Understanding Bitcoin’s Data Structure

The Blockchain as a Distributed Ledger

At the heart of Bitcoin lies the blockchain, a distributed ledger that records all transactions made on the network. This blockchain is composed of a series of blocks, each containing a set of transactions. These blocks are linked together in a chronological order, forming a continuous chain of data.

Transaction Graph and Its Complexity

To visualize Bitcoin data, one can think of it as a transaction graph. Each transaction creates inputs and outputs, and these are interconnected to form a complex web of data. This structure, while essential for maintaining the integrity of the network, poses a significant challenge when it comes to querying and analyzing data efficiently.

Challenges in Querying Bitcoin Data

The sheer volume of data generated by Bitcoin transactions, coupled with the intricate relationships between inputs and outputs, presents several challenges for data analysts and researchers. Traditional database querying methods are often ill-suited to handle the complexities of the Bitcoin transaction graph.

Graph Indexing: A Fundamental Approach

What is Graph Indexing?

Graph indexing is a specialized technique for organizing and optimizing the retrieval of data within a graph database or a graph-like structure. Unlike traditional indexing methods used in relational databases, graph indexing takes into account the interconnectedness of data points.

Traditional Indexing vs. Graph Indexing

In traditional indexing, data is organized using B-trees or hash tables, which work well for structured data but fall short when dealing with unstructured or semi-structured data like the Bitcoin transaction graph. Graph indexing, on the other hand, leverages the relationships between data points to enable efficient queries.

Advantages of Graph Indexing in Bitcoin Data Queries

Graph indexing offers several advantages when it comes to querying Bitcoin data:

– Efficient Traversal: Graph indexing enables quicker traversal of the Bitcoin transaction graph, allowing for faster query execution.
– Relationship Awareness: It takes into account the relationships between transactions and addresses, providing context to the data.
– Scalability: As the Bitcoin network grows, graph indexing can scale horizontally to handle the increasing volume of data.

Techniques for Bitcoin Data Graph Indexing

Hierarchical Indexing

– Merkle Trees in Bitcoin
One of the fundamental hierarchical indexing techniques used in Bitcoin is the Merkle tree. Merkle trees are binary trees that summarize sets of data efficiently. In the Bitcoin blockchain, Merkle trees are used to consolidate transactions within a block.
– Benefits of Hierarchical Indexing
Merkle trees provide a way to verify the integrity of data efficiently. By including a Merkle root in each block header, Bitcoin nodes can quickly verify whether a specific transaction is included in a block without needing to download the entire block.

Graph Database Systems

Neo4j and Bitcoin

Neo4j is a popular graph database system that has found applications in various fields, including Bitcoin data analysis. It represents data as nodes and relationships, making it ideal for querying the transaction graph.

Querying Benefits with Graph Databases

Graph databases like Neo4j excel at traversing complex, interconnected data structures. This capability is invaluable when exploring the Bitcoin transaction graph, as it allows for efficient queries that consider the relationships between transactions and addresses.

Optimized Graph Traversal Algorithms

Breadth-First vs. Depth-First Search

Graph traversal algorithms play a vital role in the efficiency of data queries. Two common algorithms used in Bitcoin data analysis are breadth-first search (BFS) and depth-first search (DFS).

Reducing Time Complexity in Graph Traversal

Efforts are ongoing to optimize these algorithms and reduce their time complexity. By doing so, analysts can query large portions of the Bitcoin transaction graph in a shorter amount of time.

Real-World Applications of Graph Indexing in Bitcoin

Tracking Bitcoin Transactions

– Anonymity and Privacy Challenges
Bitcoin is often touted as a pseudonymous currency, but achieving true anonymity can be challenging due to the transparent nature of the blockchain. Graph indexing can aid in de-anonymizing certain transactions.
– How Graph Indexing Aids in Tracking
Graph indexing allows analysts to follow the flow of funds through the Bitcoin network. By examining the relationships between addresses and transactions, patterns of behavior can be identified, helping to track down illicit activities.

Analyzing Bitcoin Network Behavior

Identifying Patterns and Anomalies

Graph indexing can be instrumental in understanding the behavior of the Bitcoin network as a whole. By analyzing patterns and anomalies in the transaction graph, researchers can gain insights into market dynamics, adoption trends, and potential security threats.

Case Studies on Network Analysis

Real-world case studies demonstrate the power of graph indexing in Bitcoin network analysis. Examples include the identification of market manipulation schemes and the detection of suspicious wallet addresses.

Challenges and Future Developments

Scalability Concerns

As the Bitcoin network continues to grow, scalability becomes a pressing concern. Graph indexing techniques must adapt to handle increasingly large and complex transaction graphs efficiently.

Balancing Decentralization with Performance

Bitcoin’s core principles include decentralization and censorship resistance. However, achieving high-performance data querying while maintaining these principles is a delicate balance that developers and researchers must navigate.

Emerging Trends in Graph Indexing for Cryptocurrencies

The world of cryptocurrencies is dynamic, with new technologies and research emerging regularly. The field of graph indexing for cryptocurrencies is no exception, with ongoing developments that promise to further streamline data querying and analysis.

Conclusion

In the age of cryptocurrency, data is king, and efficient querying of Bitcoin data is crucial for various stakeholders, from regulators to researchers and analysts. Graph indexing has emerged as a powerful tool to navigate the intricacies of the Bitcoin transaction graph. By harnessing the capabilities of graph indexing, we can gain deeper insights into the world of Bitcoin and cryptocurrencies, ultimately paving the way for a more transparent and secure digital financial ecosystem.


[ad_2]
Source link

Intel is Being Sued Over the ‘Downfall’ CPU Vulnerability

0
[ad_1]

A class-action lawsuit had been filed against Intel due to a critical “Downfall” vulnerability in Intel CPUs, a defect that Intel was aware of since 2018 but neglected to report.

According to Intel, the only way to “fix” it is to apply a patch that reduces CPU performance by up to 50% when performing some common computing tasks, such as encryption, gaming, and photo and video editing.

The plaintiffs are purchasers of Intel Central Processing Units (or “CPUs”). As a result, they are left with defective CPUs that are either extremely exposed to attacks or require drastic slowdowns.

Reports say they are not the CPUs that the class members and plaintiffs bought. They are significantly less valuable and perform very differently.

Five representative plaintiffs have filed a 112-page complaint in the San Jose Division of the Northern District of California United States District Court, claiming that Intel was aware of faulty instructions that allowed for the “Downfall” bug half a decade before any sort of fix was made available.

Plaintiffs seek compensation for Intel’s willful choice to sell processors with an obviously flawed design without disclosing the fact, as well as for a purported “fix” that destroys their CPU’s performance.

Downfall Attacks Found in Billions of Modern Processors

The vulnerability was identified as CVE-2022-40982, a 6.5 medium CVSS-rated information disclosure vulnerability in Intel’s sixth to eleventh-generation CPUs.

“Attackers can exploit the vulnerability and read data from other programs and memory areas,” the report said.

Document
Protect Your Storage With SafeGuard

StorageGuard scans, detects, and fixes security misconfigurations and vulnerabilities across hundreds of storage and backup devices.

Downfall attacks target a critical flaw identified in billions of modern CPUs used in personal and cloud systems. This vulnerability allows a user to get access to and steal data from other users who share the same machine.

Daniel Moghimi, a security expert at Google, reported the vulnerability to Intel on August 24, 2022, but only made the vulnerability public on August 9, 2023.

High-end CPUs started to use branch prediction in the 1990s. This speculative process was meant to keep the CPU from stalling while it waited for data from relatively slow system memory. 

This technique made significant gains in computing power and efficiency possible, which also paved the way for the development of additional “speculative execution” strategies, such as subsystems that let CPUs carry instructions out of order and even anticipate how they will be executed in the future.

All modern CPUs have had these execution features in place for over ten years. These days, they are an essential component of every CPU produced by Intel and its rivals, and without them, the CPU performance cannot be anticipated to be high enough.

Modern CPUs also require “segmentation,” which means that privileged computer programs and the resources they consume (such as system memory and hardware) must be kept separate from user-run programs. This is also a fundamental feature of all modern CPUs.

However, Intel defectively designed these critical systems in billions of their CPUs. Intel CPUs are designed to discard the results of an execution if the CPU makes an incorrect assumption when speculatively executing instructions.

Rather, Intel’s CPUs leave behind “side effects”—data that persists in the CPU’s cache memory or temporary buffers even after the outcomes of the speculative execution are discarded.

“For years, Intel knowingly sold billions of CPUs with this massive vulnerability, which imperiled the foundation of secure networking, secure communications, and secure data storage for Intel CPUs used in PCs, in cloud servers, and in embedded computers used across the country in functional MRIs, power grids, and industrial control systems,” the report said.

After disclosing the Downfall vulnerability, Intel released a microcode upgrade that purportedly addressed the vulnerability. 

The truth is that Intel’s “mitigation” severely restricted the same systems—speculative execution and branch prediction—that are essential to the operation of any modern CPU, causing impacted CPUs to perform as much as 50% worse.

To “mitigate” their vulnerability to Downfall, plaintiffs are left with defective CPUs that must have significant performance and functionality impairments. These are not the CPUs they purchased.

Hence, the prosecution is seeking “monetary relief against Intel measured as the greater of (a) actual damages in an amount to be determined at trial or (b) statutory damages in the amount of $10,000 for each plaintiff.”

Patch Manager Plus, the one-stop solution for automated updates of over 850 third-party applications: Try Free Trial.


[ad_2]
Source link