Buffer Overflow Flaws Trusted Platform Allow Malicious Commands

0
[ad_1]

Trusted Computing Group’s Trust Platform Module 2.0 reference library specification has been discovered with two buffer overflow vulnerabilities that threat actors can exploit to access read-only sensitive data or overwrite normally protected data, which is only available to the TPM.

A malicious individual who has gained access to the TPM 2.0’s Command interface has the capability to take advantage of this vulnerability by sending specifically crafted commands to the module.

As a result, they can cause harm by exploiting these vulnerabilities.

The Trusted Computing Group (TCG) has released a security advisory for users to mitigate and patch these vulnerabilities. 

CVE-2023-1017: Out-of-Bounds Write Vulnerability

This vulnerability exists in the TPM2.0’s Module Library, which could allow a threat actor to write 2-byte data beyond the end of TPM2.0 command in the CryptParameterDecryption routine.

Successful exploitation of this vulnerability can lead to denial of service or arbitrary code execution.

The severity of this vulnerability has been given as 7.8 (High).

CVE-2023-1018: Out-of-Bounds read vulnerability

This vulnerability exists in the TPM2.0’s Module Library, which could allow a threat actor to read 2-byte data beyond the end of TPM2.0 command in the CryptParameterDecryption routine.

Successful exploitation of this vulnerability can allow a threat actor to read or access sensitive data.

The severity of this vulnerability has been given as 5.5 (Medium).

Affected Vendors Products

Some of the Product Vendors affected by these vulnerabilities include libtpms IBM sponsored, NetBSD, NixOS, Red Hat, Squid, SUSE Linux, and Trusted Computing Group.

However, these vendors have released security patches to address these vulnerabilities.

Users of these products and vendors should upgrade to the latest versions to prevent these vulnerabilities from getting exploited.

Secures your storage & backup systems With StorageGuard – Watch a 40-second Video Tour.


[ad_2]
Source link

Android 14 update released for Samsung Galaxy S23 in the US

0
[ad_1]

Samsung has released the One UI 6.0 stable update for the Galaxy S23 series in the US. The rollout began recently for the carrie-loced units. It should soon be available for unlocked units too. The update brings all new features of Android 14 along with some add-ons and customizations from Samsung. The November security patch is also part of the package, introducing over 60 vulnerability fixes.

Galaxy S23 series gets Samsung’s Android 14 update in the US

After nine beta builds, Samsung released the stable version of Android 14-based One UI 6.0 for the Galaxy S23, Galaxy S23+, and Galaxy S23 Ultra at the end of October. It wasn’t a global release but the company has gradually expanded the rollout to more regions. It’s now available in many countries in Europe, Asia, Africa, Latin America, and Australia. The US versions are joining the party today.

One UI 6.0 comes with the firmware build number S91*USQU1BWK4 for the carrier-locked Galaxy S23 phones stateside. A screenshot shared by SamMobile, which first reported this rollout, shows that the OTA (over the air) download size is close to 3.3GB for the Plus model. Other models should also be getting a similar-sized update package. Beta users may get a smaller package, though.

As of this writing, the update appears to be limited to users on T-Mobile and Metro networks. However, it shouldn’t be long before Samsung pushes Android 14 to Galaxy S23 phones on other networks, including unlocked units. You should get a notification when the update reaches your phone. You can also manually check for new OTA releases from the Settings app.

Since this is a major Android OS upgrade, your Galaxy S23 phone will get a lot of new features and UI changes. Samsung has revamped the notification panel and Quick Settings for a cleaner and more organized look. System animations and widgets have been improved to give you a smoother experience. Stock apps such as camera and gallery are getting improvements too. One UI 6.0 also brings new camera features and editing tools.

The update is delayed in some markets

It’s been almost two weeks since Samsung started pushing the Android 14 update to the Galaxy S23 series. Unfortunately, it has yet to complete the rollout. The update has been delayed in South Korea. The company says it still needs 1-2 weeks to release One UI 6.0 in its home country. Hopefully, this won’t affect the rollout schedule for other models. We will let you know as soon as Samsung releases Android 14 for more Galaxy devices.

Samsung Galaxy S23 US Android 14 update screenshot


[ad_2]
Source link

Google proposed $147 million to Epic Games to launch Fortnite on the Play Store

0
[ad_1]

In the past couple of years, Epic Games (the creator of Fortnite) started a significant lawsuit saga with Apple, and not only. In 2020, the gaming company filed its first lawsuit against Google. This week, a second legal skirmish has kicked off, with Epic Games alleging that Google is shelling out substantial sums to big developers, enticing them to keep their apps on the Play Store.According to court revelations reported by The Verge, Google has confirmed that it proposed a $147 million deal to Epic Games to launch Fortnite on the Android Google Play Store. Purnima Kochikar, Google’s VP of Play partnerships, stated that the deal, approved and presented to Epic, was rejected by the gaming company.

The proposed deal involved the gradual disbursement of funds over three years, concluding in 2021, as incremental support for the game’s publisher.

The underlying motive for this deal, as reported, was Google’s attempt to prevent a potential trend of popular apps bypassing the official Android store and, in turn, avoiding Google’s in-app purchase fees.

Epic Games vs Google


Epic Games has been vocal about its discontent with the 30% revenue cut imposed by Google (and Apple, for that matter) on Play Store transactions. This led Epic to take an unconventional route, releasing Fortnite for Android independently and offering the game’s download file directly on its website.

While Fortnite eventually landed on the Google Play Store in April 2020, Epic persisted in distributing it independently, circumventing Google’s 30% cut on in-app purchases. The tension escalated in August 2020 when Epic allowed direct in-game currency purchases, which violated Google’s Play Store policies.

In response, Google removed Fortnite from the Play Store, prompting Epic Games to file an antitrust lawsuit against Google for alleged abuse of monopoly power. The case started last year and is still ongoing.

In the antitrust case, Epic Games claimed that Google reacted anxiously to Epic’s initial decision, fearing a potential domino effect with other game developers. Internal documents presented in court hinted at Google’s apprehension of a “contagion risk” and revealed attempts to entice or acquire Epic to prevent such a scenario.

In the courtroom drama, the “contagion” documents took center stage this week as Lawrence Koh, the ex-head honcho of Google Play’s games business development, took the stand. They painted a picture of Google’s worry scenario, predicting that, within a couple of years of Epic’s move, nearly all top game developers could jump ship from the Play Store.

The forecast is a financial nightmare for Google, with potential losses soaring into the billions of dollars in revenue. The documents shown in court suggested a direct revenue loss between $130 and $250 million, with a broader downstream loss of up to $3.6 billion if the feared mass defection occurred.

In court, Google asserted its position with Purnima Kochikar clarifying that Google’s worry was about potential game losses on the Play Store, and there was no nefarious intent. “We just wanted developers to choose Play,” said Kochikar.

Lawrence Koh concurred in his testimony that the investment to secure games on the Play Store was considered worthwhile, especially given the scenario where developers might opt for an initial launch on Apple’s iOS.

Since its 2017 release, Fortnite has surged in popularity, boasting around 400 million registered users. Note that this count includes sign-ups from occasional players, not solely reflecting the number of regular active Fortnite gamers.


[ad_2]
Source link

New Gootloader Malware Abuses RDP to Spread Rapidly

0
[ad_1]

Hackers target Remote Desktop Protocol (RDP) via malware because it provides them with remote access to a victim’s computer or network, allowing them to:-

  • Steal data
  • Deploy ransomware
  • Conduct other malicious activities

Cybersecurity researchers at IBM X-Force affirmed recently that in place of conventional frameworks like CobaltStrike, the Gootloader group unveiled GootBot, a new tool for C2 and lateral movement.

Gootloader Malware Abuses RDP

GootBot, a stealthy Gootloader variant for lateral movement, complicates detection. The group uses SEO poisoning to target victims, introducing their custom bot to avoid detections while rapidly spreading and deploying payloads.

GootBot is expanding its post-infection capabilities, enabling threat actors to remain hidden for longer by running encrypted PowerShell scripts. Besides this, Gootloader was previously usually utilized for initial access.

GootBot is a lean PS script with a single C2 server that infiltrates enterprise domains via hacked WordPress sites, posing a risk with undetected activity, reads the IBM X-Force report.

Hive0127 (aka UNC2565) has been active since 2014 and deploys Gootloader via SEO poisoning and hacked WordPress sites, enabling ransomware and more.

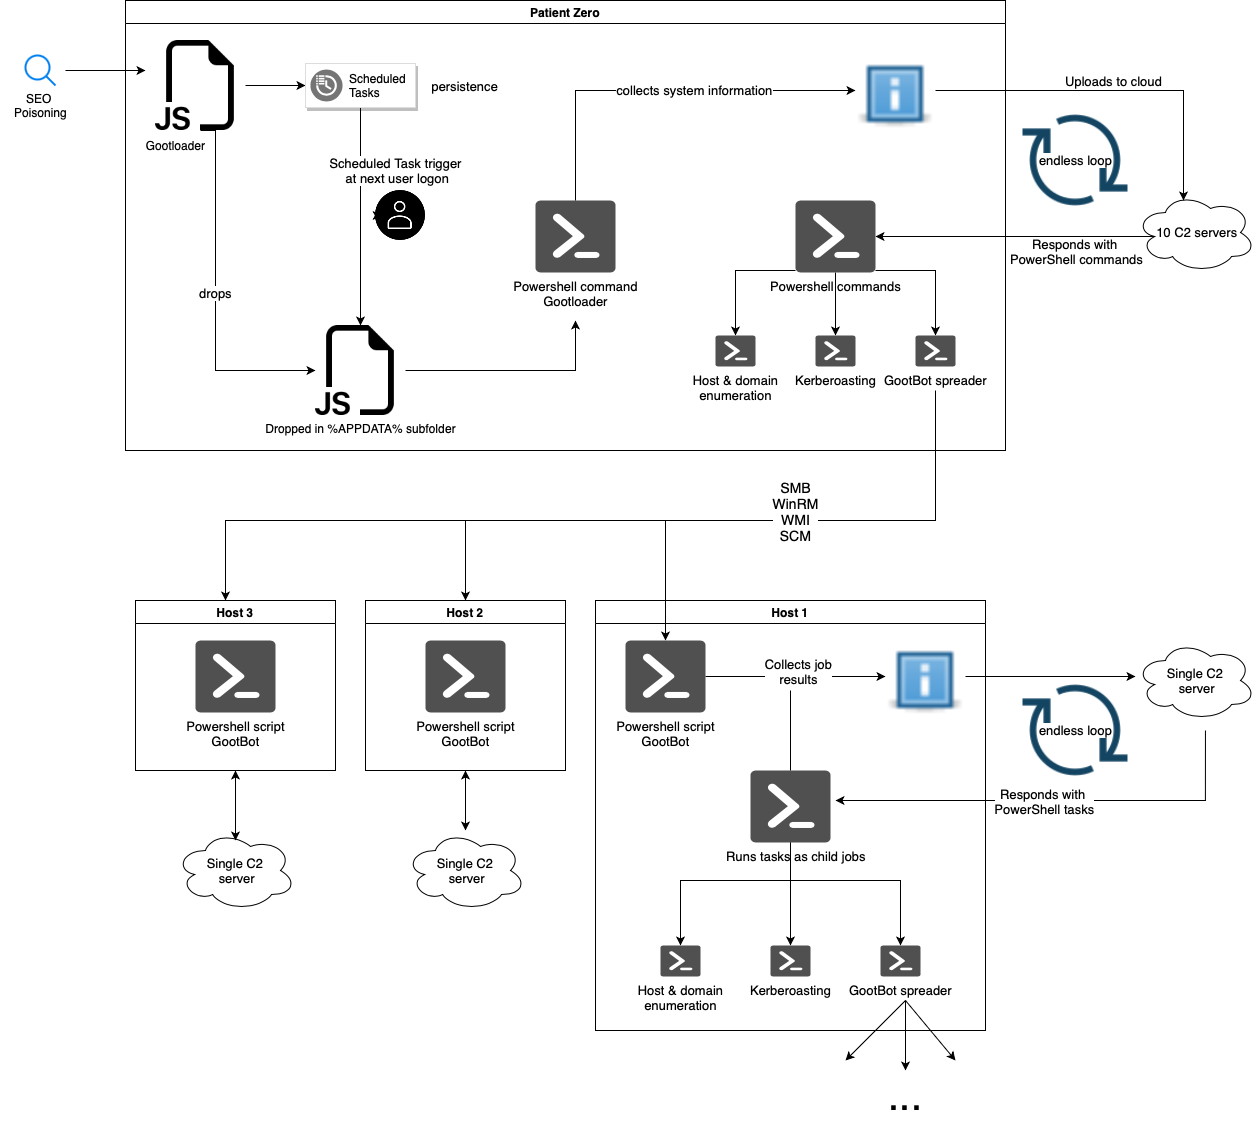
Gootloader begins with a user downloading an infected archive, leading to obfuscated JavaScript files placed strategically in %APPDATA%.

Gootloader Malware Abuses RDP
Infection chain (Source – SecurityIntelligence)

This virus uses stages that collect data and connect with compromised WordPress-based C2 servers to schedule activities for persistence and allow dynamic PowerShell execution.

Moreover, this new variant is a lightweight PowerShell script with a single C2 server, enabling:-

  • Asynchronous execution
  • Lower EDR detection
Gootloader Malware Abuses RDP
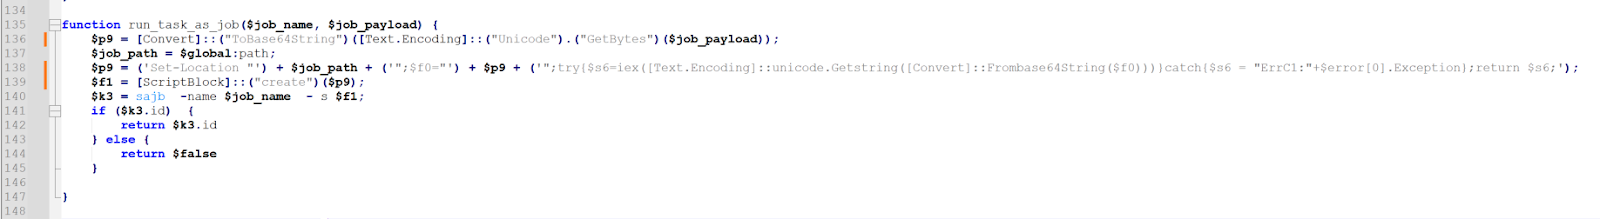
Deobfuscated code running the C2 task (Source – SecurityIntelligence)

GootBot beacons every 60 seconds, adjustable with a specific string. It handles task results for child jobs from the C2, sending ‘E1’ for incomplete jobs and ‘E2’ for missing ones.

A modulo-based approach is used to obscure the string after Base64 encoding, which is similar to the trick used by Gootloader.

GootBot sends POST requests to its C2 server, splitting data if it’s over 100,000 chars. It spreads laterally, using various techniques to infect hosts. 

Its C2 generates diverse payloads and deploys them automatically. WinRM, SMB, and WinAPI are used for lateral movement. 

Environment variables store encrypted strings, reducing script size. GootBot spoofs PowerShell process arguments by creating new processes.

Document
Protect Your Storage With SafeGuard

StorageGuard scans, detects, and fixes security misconfigurations and vulnerabilities across hundreds of storage and backup devices.

GootBot also runs a reconnaissance script that collects the following data:-

  • Domain user name
  • OS (from registry key)
  • If 64bit architecture (checking for x86 dir and also size of int ptr)
  • Domain controllers
  • Running processes
  • SID
  • Local IP address
  • Hostname

Recommendations

Here below, we have mentioned all the recommendations offered by the security researchers:-

  • Make sure to keep the AV tools updated with the latest available security updates.
  • Enable script block logging.
  • Monitor Windows event logs for security indicators.
  • Watch for JavaScript file execution in downloaded ZIPs.
  • Make sure to keep your eyes on “wscript.exe” launching JavaScript files with short names like (*~1.JS) in scheduled tasks.
  • Monitor HTTP traffic for suspicious requests ending in “xmlrpc.php” URLs.
  • Suspicious cookie value: <BOT_ID>=<If user is admin: 0/1>
  • Suspicious content format: <BOT_ID>=[sX<<random_int>><packet_seq_number>]<data>
  • Always remain vigilant for lateral movement through WinRM, WMI or SCM.
  • Within your environment, make sure to disable or monitor the “Start-Job” Cmdlet.

Patch Manager Plus, the one-stop solution for automated updates of over 850 third-party applications: Try Free Trial.


[ad_2]
Source link

Samsung’s Android 14 update delayed for some Galaxy S23 users

0
[ad_1]

Samsung has delayed the One UI 6.0 stable release for the Galaxy S23 series in South Korea. The company has revealed that the big update, which brings Android 14, is delayed by “1-2 weeks” in the country. The update has yet to arrive in the US too, though there’s no word yet on the expected release date stateside.

Some Galaxy S23 users may have to wait longer for Android 14

Samsung released Android 14-based One UI 6.0 stable update for the Galaxy S23, Galaxy S23+, and Galaxy S23 Ultra at the end of October. The rollout began in Europe and quickly expanded to other regions, including Asia, Africa, Latin America, and Australia. However, almost two weeks later, the new Android version has yet to be available for Galaxy S23 users in Canada, China, South Korea, the US, and a few other countries.

Users have been impatiently waiting for the update but it hasn’t come. Now, Samsung has confirmed that it has delayed the update, at least in South Korea. Responding to a user’s request for clarity on the situation, a forum moderator said that the stable One UI 6.0 build would take about two more weeks to arrive. As usual, Android 14 beta users will get it first, followed by the Galaxy S23 units still on Android 13.

The moderator didn’t reveal the cause of the delay but suggested that phone carriers have yet to complete the inspection of the update. There don’t seem to be major issues or bugs remaining to fix, as the company has no plans for the tenth beta build (Galaxy S23 received nine One UI 6.0 beta updates). The stable build released in other markets doesn’t have any notable problems either.

The Samsung representative said the final release in South Korea would come before the end of November but avoided providing a precise schedule. It’s unclear if the same delay is applicable in the US and other remaining markets too. Hopefully, the Korean firm will sort things out sooner rather than later and push Android 14 to all Galaxy S23 users around the world at the earliest. You can check for new updates from the Settings app.

Other Galaxy models should soon join the party

Samsung’s One UI 6.0 update will soon be available for other Galaxy models too. The company is expected to push Android 14 to all eligible S-series flagships and Z-series foldables before the end of the year. Some premium A-series models may also get the big update within the next few weeks. We will keep a close eye on the official Samsung channels and let you know as soon as we have more information.


[ad_2]
Source link

WhatsApp New Privacy Feature Hide Location During Calls

0
[ad_1]

WhatsApp has begun to roll out the ‘Protect IP Address in Calls’ feature, which conceals your IP address during calls.

Upon using this feature, all your calls will be relayed through WhatsApp’s servers, protecting your IP address and preventing other callers from figuring out your geographical location.

These features reduce the impact of real-world attacks while respecting and enhancing user privacy.

‘Silence Unknown Callers’ is another privacy feature WhatsApp announced in June 2023. Once activated, calls from unknown numbers stop ringing on your phone.

This feature protects users from unknown contact, cyberattacks, and spyware by reducing the attack surface and external data processing.

Protect IP Address During Calls

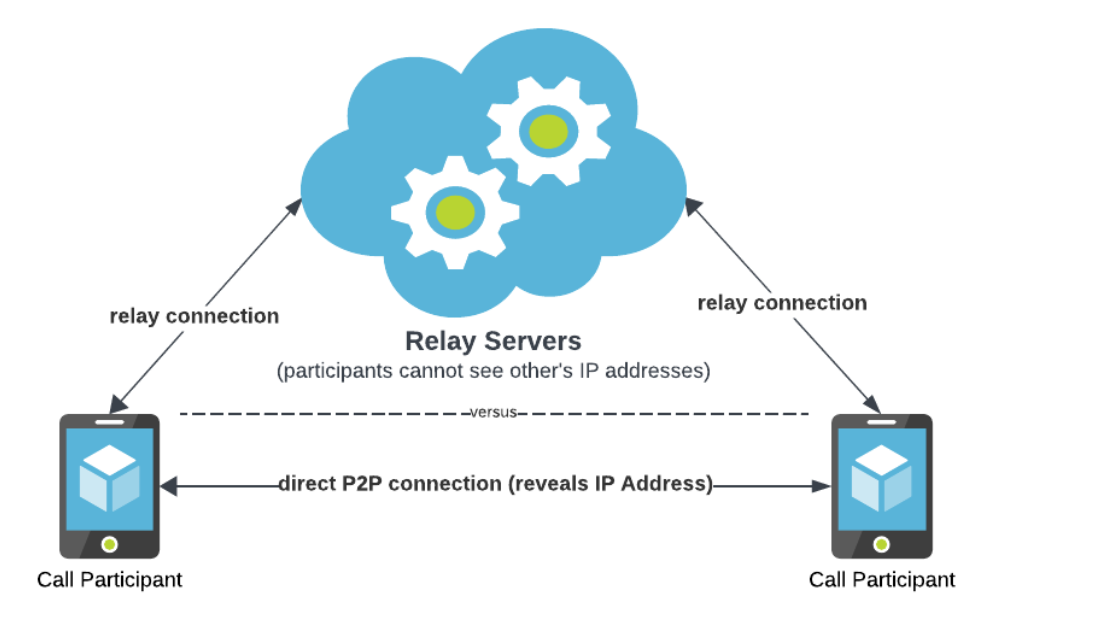
Peer-to-peer and relay-based connections are the two most popular ways of connecting call participants.

Peer-to-peer connections are present in most calling products used by users today. Faster data transfers and higher call quality are made possible by this direct connection, but it also implies that for all data packets to be delivered to the right device, participants must be aware of each other’s IP addresses.

Both callers may see each other’s IP addresses in a one-to-one conversation. IP addresses may contain information that some of our most privacy-conscious users are aware of, such as a wide geographical area or internet provider.

Diagram of a relay serverDescription automatically generated
Peer-to-peer and via a relay connection

In response to this concern, WhatsApp released the “Protect IP Address During Calls” feature that lets you hide your IP address during calls.

Document
Protect Your Storage With SafeGuard

StorageGuard scans, detects, and fixes security misconfigurations and vulnerabilities across hundreds of storage and backup devices.

“We introduced a new feature on WhatsApp that allows you to protect your IP address during calls,” WhatsApp said.

Protect IP address

“With this feature enabled, all your calls will be relayed through WhatsApp’s servers, ensuring that other parties in the call cannot see your IP address and subsequently deduce your general geographical location.”

This new feature adds another degree of protection and privacy. WhatsApp doesn’t have the ability to listen in on your calls because, as usual, all your calls are encrypted end-to-end. This includes calls that are relayed through its servers.

How to Activate it?

To access this setting:

  • Tap Settings, then Privacy.
  • Tap Advanced.
  • Turn Protect IP address in calls on or off.

This year, WhatsApp developed and released “Silence Unknown Callers” and “Protect IP Address in Calls” as part of our continuous, all-encompassing efforts to keep users safe.  In addition to numerous other safeguards, these additional security features help to keep users safe on WhatsApp.

Secures your storage & backup systems With StorageGuard – Watch a 40-second Video Tour.


[ad_2]
Source link

The importance of reliable business telephone services

0
[ad_1]

Communication is the key to running your business. However, knowing how to overcome the barriers that may hinder effective communication is essential.
Overcoming these obstacles allows you to enhance productivity, improve employee performance, and resolve issues that could arise from miscommunication. Some of the common barriers include: –.

Technology

In modern business, communication is often conducted through various digital tools and systems. Sometimes, these systems can create barriers that prevent effective communication between team members. For example, using acronyms or jargon during conversations can make it difficult for others to understand what is being said. Similarly, physical barriers can deter effective communication, such as not having enough space to speak or being uncomfortable.

Psychological barriers can also hinder the flow of communication, resulting in misunderstandings and frustrations. Overcoming these barriers requires identifying the source of the problem and finding ways to address it. This could involve self-reflection, therapy, or stress management techniques.

Using an advanced phone system like VoIP can eliminate some communication barriers, allowing you to communicate with your customers more effectively and boost sales. Choose reliable business telephone services with advanced features like call forwarding and automatic voicemail transcriptions. It should also allow you to monitor and report on customer trends and sales performance easily.

Culture

Communication is essential for successful business operations. It enables the effective relay of information and helps foster understanding within your team, which is vital for collaboration, decision-making, and overall success. However, overcoming barriers to effective communication in the workplace can be challenging.

The most common barriers include language, cultural, and emotional roadblocks. This is mainly because of the differences in communication styles across cultures and perceptions and interpretations of certain information.

For example, body language and gestures are highly influenced by culture. In some conservative societies, greeting the opposite gender by shaking hands is considered an ill manner or even a moral crime, whereas, in the West, this is a common practice.

It is, therefore, essential to promote a culture of open communication and respect for diverse viewpoints to reduce the impact of these barriers on your business operations. This can be done by promoting cultural awareness, encouraging empathy, and fostering inclusivity.

Language

The most common communication barrier is language, which may include a lack of vocabulary and understanding of specific terms or concepts. Clear and simple language can help reduce this barrier by making it easier for the receiver to decipher and interpret the message. In addition, avoiding technical jargon can facilitate the process.

Active listening and focusing on the speaker’s intention can also reduce this barrier. Asking clarifying questions can help bridge the gap between interpretations and ensure the message is understood.
Attitudinal barriers can include a lack of respect for the ideas and opinions of others, assumptions about the other person’s knowledge or understanding, and resistance to change and new ideas.

These can be overcome by actively listening, being aware of cultural and emotional differences, and seeking professional help to address the underlying causes. Identifying and overcoming communication barriers can enhance productivity and efficiency, eliminate confusion and misunderstandings, and foster stronger relationships.

Attitude

Overcoming communication barriers involves changing one’s attitude or mindset. This is essential in fostering effective and productive communication with others. Some examples of attitudinal obstacles include defensive or closed-minded attitudes, overconfidence and arrogance, power dynamics and hierarchical attitudes, and resistance to change and new ideas.

Emotional barriers can also impede effective communication. When individuals are passionate, they may not be able to clearly articulate their thoughts or emotions, which can lead to misinterpretation and misunderstandings. Additionally, some people may find it difficult to express their feelings, and some topics are taboo or off-limits, hindering two-way communication.

Another common communication barrier is a need for more active listening. To overcome this, pay attention to the person speaking and avoid distractions. Avoid interrupting them, and don’t jump to conclusions, as they are probably still processing what was said. This will allow the speaker to feel that their perception is equally important and help you to understand their message better.
[ad_2]
Source link

Hacker Leaks 800,000 Scraped Chess.com User Records

0
[ad_1]

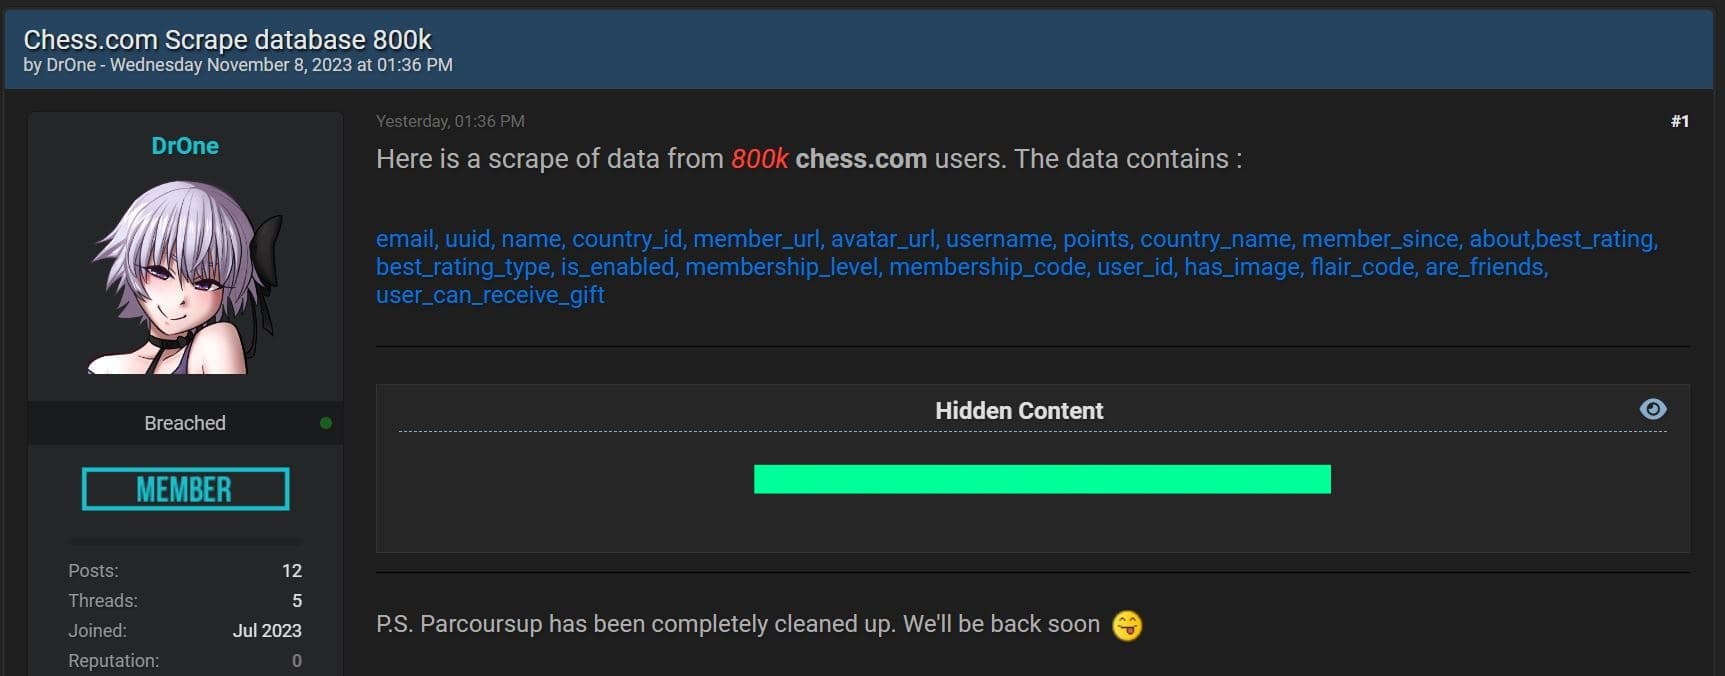
The scraped Chess.com data was leaked on Breach Forums on November 8th, 2023 by a threat actor operating under the alias ‘DrOne.’

A threat actor operating under the alias ‘DrOne’ has claimed responsibility for leaking the scraped database of Chess.com containing the personal data of more than 800,000 registered users.

Hacker Leaks 800,000 Scraped Chess.com User Records
Announcement on the Breach Forums (Screenshot credit: Hackread.com)

Chess.com is a highly popular online platform for chess enthusiasts and a social networking website. As of 2023, the platform boasts more than 150 million registered users, indicating that the leaked records account for approximately only 0.533% of the total user base.

The database was disclosed on November 8th, 2023 on Breach Forums, a well-known platform for hackers and cybercrime activities. Interestingly, this forum recently saw another threat actor leaking a scraped database from LinkedIn just a couple of days prior, which contained information from 25 million users.

The Leaked Data

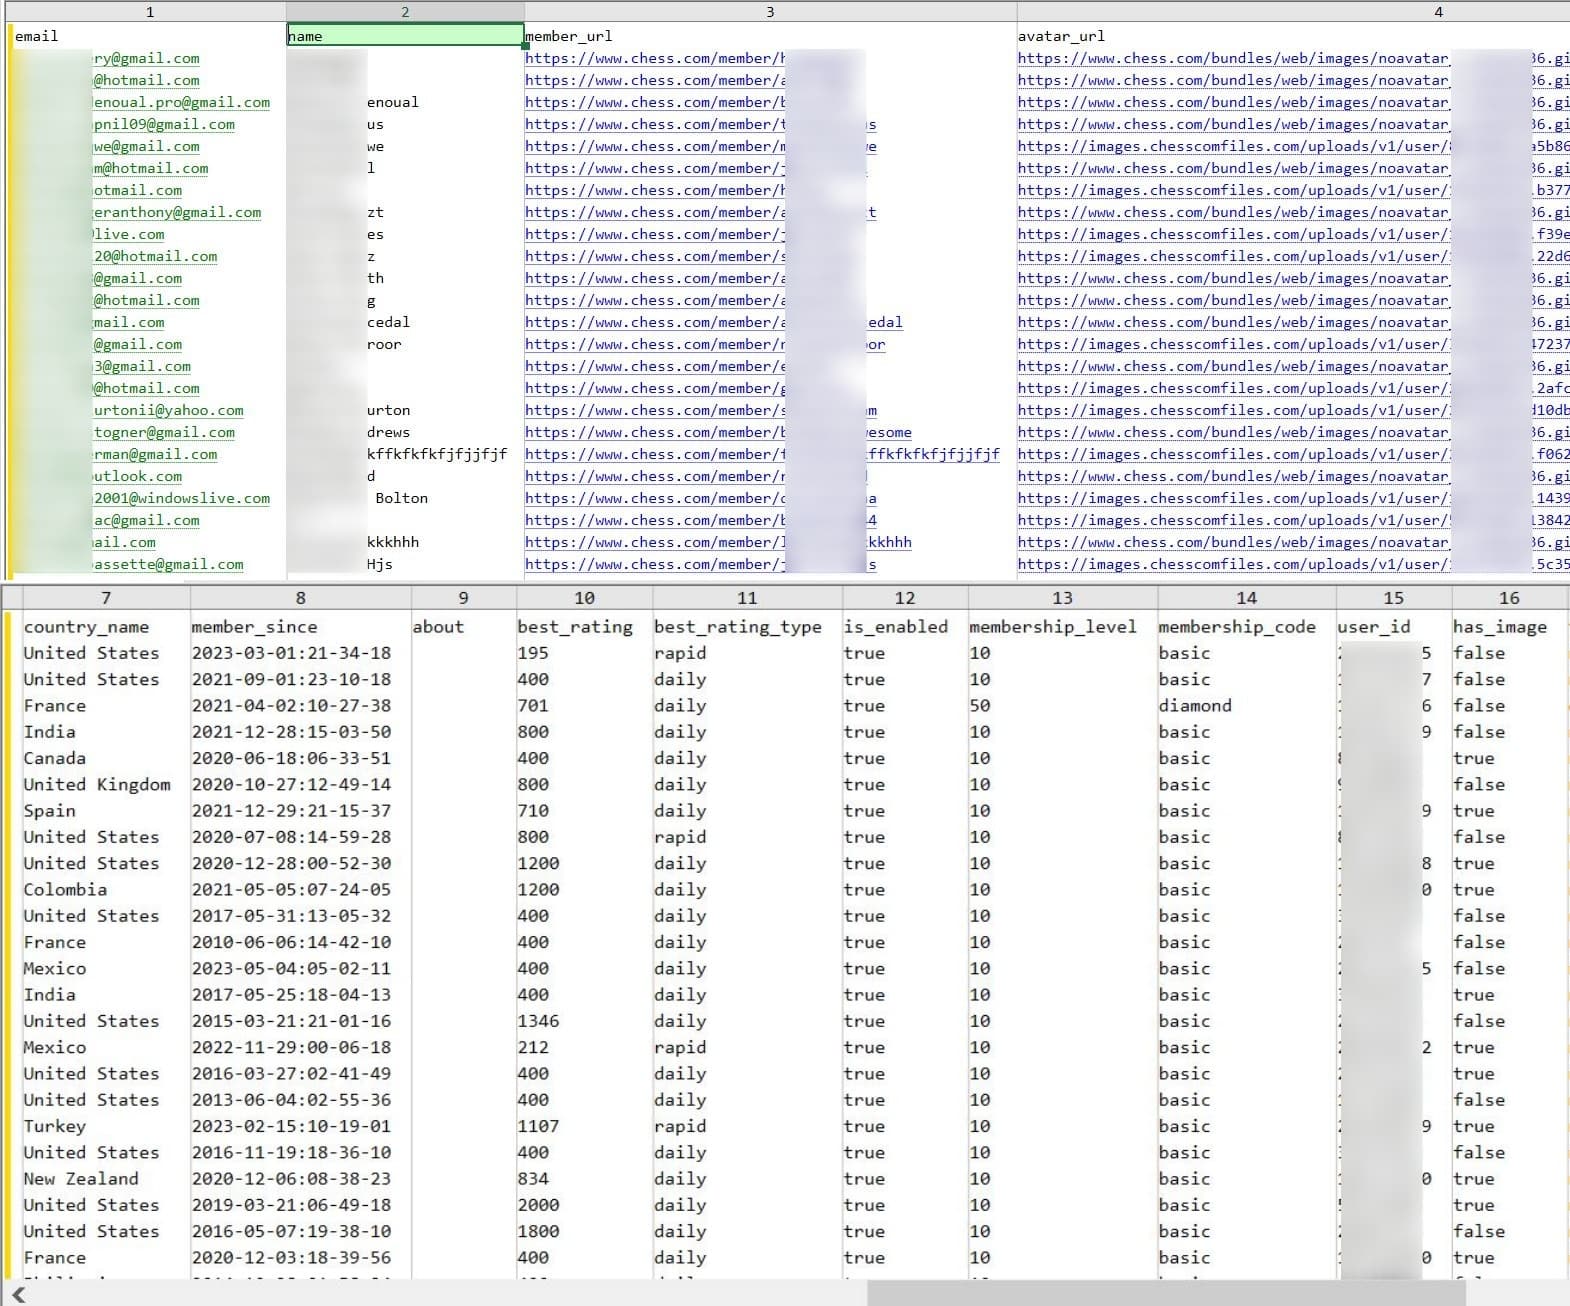
After a comprehensive scan of the Chess.com database by Hackread.com, our analysis confirms the exposure of personal data from 828,327 registered users. The leaked information includes:

  • Full names
  • Usernames
  • Profile links
  • Email addresses
  • Users’ originating countries
  • Avatar URLs (containing profile pictures)
  • Universally Unique Identifier (UUID) and User IDs
  • Date of registration (with the most recent sign-up in September 2023)

If combined, the leaked information can serve as a treasure trove for cybercriminals. This data could be utilized for identity theft, phishing scams, social engineering attacks, or even to cross-reference previously leaked login credentials in order to obtain passwords.

Hacker Leaks 800,000 Scraped Chess.com User Records
Announcement from the leaked Chess.com data – Clicking on links would open the user profile and profile images (Screenshot credit: Hackread.com)

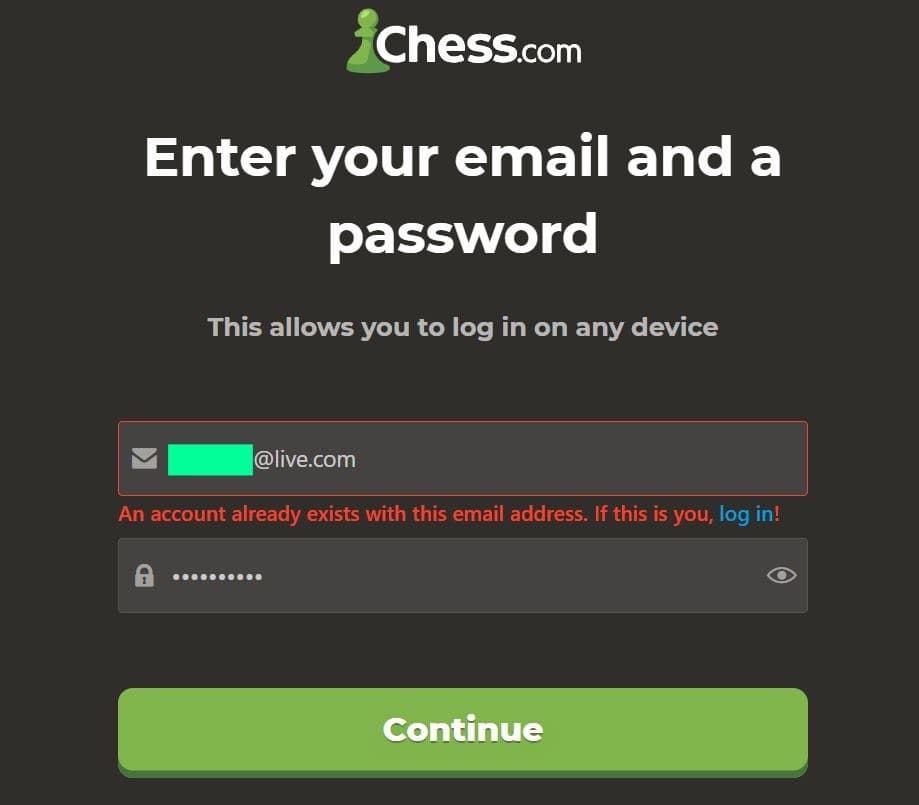
Fortunately, the leaked data does not include passwords. However, when Hackread.com attempted to sign up using the leaked email addresses, nearly every email address used prompted the message ‘An account already exists with this email address.’ This suggests that the leaked database contained valid and active email addresses associated with existing Chess.com accounts.

Hacker Leaks 800,000 Scraped Chess.com User Records
(Screenshot credit: Hackread.com)

Web Scraping is Hard to Avoid/Block

Web scraping or data scraping, is an automated process utilized by software to extract data from websites, primarily for gathering specific information from web pages. The process is almost impossible to block since Chess.com is a large website.

Large websites use a variety of measures to prevent scraping, such as rate limiting and captcha challenges. However, scrapers are constantly developing new techniques to circumvent these measures and some scrapers may collect the data for research purposes, such as to study social networks or to develop machine learning models.

Chess.com and Cybersecurity

This is not the first time Chess.com has made headlines for cybersecurity-related issues. In February 2021, a well-known ethical hacker, Sam Curry, discovered and reported a critical vulnerability within the platform. This flaw allowed the researcher to potentially access any account on the site, including the administrator account.

This new breach poses a significant threat to Chess.com users, potentially facilitating various scams such as identity theft and phishing. For Chess.com users, it is strongly recommended to change your password not only on the platform but also across any other online accounts where the same password is used.

Cybercriminals might deploy phishing tactics, sending emails with links leading to malicious websites mimicking Chess.com or other legitimate platforms. It is crucial to refrain from clicking on any such links. However, you can safely check the real URL by hovering over the link before clicking it.

  1. Hackers leak scraped data of 87,000 GETTR users
  2. Scraped data of 1.3 million Clubhouse users published online
  3. Twitter Scraping Breach: 209M Accounts Leaked on Hacker Forum
  4. API Misuse: Hacker Exposes 2.6M Duolingo Users’ Emails & Names
  5. Data scraping firm leaks 235m Instagram, TikTok, YouTube user data

[ad_2]
Source link

Google ads are being used to spread malware

0
[ad_1]

Malicious actors are using Google advertisements and SEO tactics to entice victims into clicking on links poisoned with malware.

According to cyber security company Secureworks, malicious actors have been using poisoned ad installers as Trojans, specifically to spread Bumblebee malware. These ad installers are associated with a number of well-known companies including Zoom, Citrix Workspace, Cisco AnyConnect and OpenAI’s ChatGPT. For example, Secureworks researchers found that a malicious actor had not only created a poisoned ad installer for Cisco AnyConnect, but a fake download page for the malware as well. They were able to do this by exploiting a compromised WordPress site.

Once Bumblebee malware is downloaded, malicious actors most often use it to launch ransomware within the infected device. In one case, Secureworks researchers found that the malicious actor moved laterally across the device, downloading and launching a number of applications and software programs including legitimate remote access tools AnyDesk and Dameware as well as penetration testing malware Colbalt Strike.

By using paid Google ads as well as SEO tactics in their fake download pages, malicious actors are able to ensure that their Trojanized and poisoned uploads are at the top of the Google search results page, meaning victims are more likely to click on them.

An example of this was seen on January 15, 2023, when a cryptocurrency and NFT influencer known as NFT God said that their “entire digital livelihood was violated” after hackers gained access to and stole “a life changing amount of [their] net worth” in funds and NFTs from their digital wallet. The hackers were able to gain access to their funds through a poisoned ad installer masquerading as a legitimate video streaming software, OBS. 

After downloading and attempting to run the software, NFT God noticed that it had not properly installed, but dismissed this as a technical difficulty. In actuality, they had introduced malware to their device which allowed malicious users access to their social media accounts and digital wallet.

According to NFT God, the hackers stole “at least 19 ETH, worth almost US?$27,000 at the time, a Mutant Ape Yacht Club (MAYC) NFT with a current floor price of 16 ETH ($25,000), and several other NFTs”.

To prevent falling prey to poisoned ads, only download software and updates from trusted sites and go to the sites directly to avoid clicking on a Trojanized link. 


[ad_2]
Source link

US federal agencies hit with MOVEit cyber attack

0
[ad_1]

A Russian-speaking hacking group successfully gained access to the email addresses of approximately 632,000 US federal employees within the US Departments of Defense and Justice during an extensive hack, according to a report obtained through a Freedom of Information Act.

The report, released by the US Office of Personnel Management (OPM), sheds light on the cyber attack’s specifics, with the hackers exploiting vulnerabilities within the file-transfer tool MOVEit. However, little information was provided in the report about the attack’s scale or the affected agencies.

Government email addresses breached

Reporting to a congressional committee, the OPM revealed that an unauthorized actor had breached government email addresses, links to government employee surveys administered by the OPM, and internal OPM tracking codes.

The impacted employees were reportedly spread across the Department of Justice and various sectors of the Defense Department, including the Air Force, Army, US Army Corps of Engineers, and the Office of the Secretary of Defense among others.

The eight-page report by the OPM, originally presented to the House Science, Space, and Technology Committee in July, disclosed that the attack occurred on May 28-29, with hackers exploiting a vulnerability within the MOVEit file transfer program used by Westat Inc., a vendor that the OPM engages for federal employee viewpoint surveys. However, there was “no indication” that any unauthorized user had accessed the survey links.

Despite characterizing the hack as a “major incident,” the OPM clarified that it did not perceive it as posing a significant risk, and the compromised data was “generally of low sensitivity” and unclassified.

The OPM’s disclosure was reported on 30 October by Bloomberg and Forbes, but the Department of Justice and the Department of Defense did not immediately respond to requests for comment.

MOVEit users targeted in cyber attack

According to reports, other US agencies such as the Department of Health and Human Services, the Department of Agriculture, and the General Services Administration, had previously confirmed their exposure to the MOVEit hack. Additionally, the Energy Department was said to have received ransom requests from the hackers after two of its entities had been victimized by the breach.

Progress Software Corp., the parent company of MOVEit, gave assurances that they have taken measures to mitigate the cyber attack’s impact. The company said it empathized with the affected users and pledged to play a collaborative role in the industry-wide effort to combat cyber criminals.

According to reports, Westat responded to the attack by conducting a comprehensive investigation and collaborating with third-party specialists to enhance system security and reduce the likelihood of similar incidents occurring in the future.

Who is Clop?

The attack has been attributed to a Russian hacking group known as Clop, or ClOp. The group has been active since February 2019 and has a website located on the dark web where it routinely posts warnings or uploads data dumps from the organizations it has breached.

In June 2023, Clop posted a notice on the dark web warning firms it had exploited MOVEit to obtain data, giving the affected organizations a deadline to email them before the stolen data would be published. More than 100,000 staff at the BBC, British Airways and Boots were subsequently told that payroll data may have been taken. However, the BBC later reported that Clop, speaking over email, claimed ”we don’t have that data” – raising the possibility that either another unknown hacking group had the stolen data or that Clop was lying.

Clop has reportedly survived multiple attempts to break its activities, including server raids by Ukrainian police in June 2021, which included arrests of multiple alleged hackers working for the group.

According to estimates, Clop has successfully attacked more than 230 organizations to date.


[ad_2]
Source link