8 vital steps to enhance security

0
[ad_1]

In today’s interconnected world, the mobile device has become the ubiquitous tool for practically everything, from playing games like blackjack live and streaming Netflix to seamless financial transactions. Its versatile functionality has woven itself into the fabric of our daily lives, serving as both a source of entertainment and a gateway to essential digital activities.

However, this growing reliance on mobile devices also exposes us to increased security risks. Hackers are constantly seeking ways to exploit vulnerabilities and access our personal data. Consider implementing these eight essential security measures to shield your Android device from potential threats.

Choose a Strong Password

When it comes to fortifying your Android device’s security, selecting a robust password is paramount. Create a robust password that should be at least eight characters long. You must incorporate a mix of uppercase and lowercase letters, numbers and special characters. Avoid easily guessable data like your name or birthdate.

Moreover, refrain from using the same password across multiple accounts. Consider generating a random password using a password manager or crafting a unique passphrase. Periodically changing your password adds an extra layer of security to thwart unauthorized access.

Enable Two-Factor Authentication

To bolster your Android device’s defenses, enable two-factor authentication (2FA). This adds an additional layer of protection by requiring two verification forms before granting access. To enable 2FA:

– Open the Settings app.
– Scroll down and tap “Security” or “Biometrics and Security.”
– Find “Two-factor authentication” or a similar option.
– Choose an authentication method, such as an authentication app.

With 2FA, even if someone manages to steal your password, they won’t gain access without the secondary verification code.

Install a Reliable Antivirus

To secure your Android device against malware and security threats necessitates the installation of a dependable antivirus app. Given the rising number of threats, this step is critical. Opt for reputable antivirus apps with high ratings, such as Avast, Bitdefender, McAfee or Norton.

These apps may require specific permissions, such as access to files, contacts and network settings. Once installed, run an entire device scan and follow the app’s guidance to remove or quarantine any malicious files or apps. Activate real-time protection for continuous monitoring of your device’s security.

Encrypt Your Android Device’s Data

Encrypting your Android device’s data is fundamental to enhancing its security. Encryption safeguards your sensitive information from unauthorized access, even if you lose your device. To encrypt your device:

– Access the Settings app.
– Navigate to “Security” or “Security & Privacy.”
– Locate “Encrypt phone” or “Encrypt tablet” and select it.
– Enter your PIN, password or pattern if you have a screen lock.

While encryption may slightly impact device performance, its unparalleled protection is well worth the trade-off. With your Android device encrypted, your personal information remains shielded from prying eyes.

Secure Your Wi-Fi Connection

Your Android device’s security is also contingent on the safety of your Wi-Fi connection. When linked to an unsecured network, your device becomes vulnerable to various attacks. To bolster Wi-Fi security:

1. Ensure your Wi-Fi network uses WPA2 encryption, the most secure option.
2. Disable auto-connect to prevent connecting to unsecured or malicious networks.
3. Consider using a VPN service for encrypted internet traffic on public networks.
4. Regularly update your device’s operating system and apps to patch vulnerabilities.
5. Turn off Wi-Fi when not in use to minimize the risk of unauthorized access.

Adhering to these approaches can significantly diminish the chances of compromising your Android device’s security.

Update Your Android Operating System

Regularly updating your Android operating system is a proactive step to keep your device secure. Manufacturers release updates that include security patches and bug fixes. These updates address vulnerabilities that hackers might exploit. To ensure your device’s safety:

– Open the Settings app.
– Scroll to “Software Updates” or a similar option.
– Check for available updates and install them promptly.

Enabling automatic updates, if available, is a convenient way to stay protected without manual intervention.

Exercise Caution While Downloading Apps

When downloading apps on your Android device, opt for trusted sources like the Google Play Store, as these platforms have robust security measures to screen apps for malware and other threats.

Avoid downloading apps from third-party sources, as these can be risky. Additionally, review an app’s permissions before installing it. If an app demands access to sensitive data or features unrelated to its functionality, consider it a red flag and proceed cautiously.

Educate Yourself About Phishing Scams

Phishing scams, the deceptive art of luring individuals into divulging confidential information, have increased in our digital age. These cunning tactics can take many forms, often arriving as seemingly innocuous emails, text messages or even phone calls, masquerading as trusted sources.

Staying informed about the evolving landscape of phishing schemes is crucial to protect yourself. Familiarize yourself with red flags, such as misspelled URLs, generic greetings and urgent demands for personal data. Additionally, always verify the legitimacy of messages from financial institutions or service providers. Rather than clicking on links, access official websites independently and contact these organizations directly to confirm any unusual requests.

Remember, in the digital realm, knowledge is your most potent defense against phishing attempts, ensuring your personal and financial information remains safeguarded.

Final Note

In a digital age where our Android devices are the gateways to our most personal and vital information, safeguarding them from potential threats is paramount. The eight essential steps outlined here form a comprehensive shield against hacking attempts and data breaches.

Selecting a solid password, enabling two-factor authentication and installing a reliable antivirus app will fortify your device’s defenses. Encrypting your Android device’s data ensures that your sensitive information remains locked away even if it falls into the wrong hands. Additionally, securing your Wi-Fi connection, regularly updating your Android operating system and practicing caution while downloading apps protect against external threats.

Education is another vital component of your security arsenal. Understanding phishing scams and exercising caution when encountering suspicious emails or messages can thwart social engineering attempts.

By integrating these security measures into your daily routine, you confidently empower yourself to navigate the digital landscape, knowing that your Android device is a fortress against hacking and that your personal information remains safe. Stay vigilant, stay informed and enjoy the full potential of your Android device with peace of mind.


[ad_2]
Source link
Spotify thrives: Subscribers rise despite price hikes

0
[ad_1]

Streaming services are hitting us with price hikes left and right these days, and Netflix is the latest culprit, just announcing another bump in its prices. Spotify joined the party earlier this year by cranking up its subscription fees, but oddly enough, it doesn’t seem to be scaring us away.

According to a new report (via The Verge), Spotify Premium snagged a three percent increase in subscribers, reaching a solid 226 million on a quarterly basis. This boost comes even as Spotify dropped the bomb of price hikes across the US and various global markets.

Not stopping there, Spotify’s monthly active users climbed to 574 million as of September 30th, showing a four percent rise from the last quarter. Surprisingly, these numbers went a bit beyond what Spotify had predicted.

When you compare these figures to the same time last year, it gets even more impressive. Spotify’s subscriber count shot up by 16% year over year, and its monthly active users skyrocketed by 26% year over year.

In the profit department, Spotify raked in around $69 million for the recent quarter, a stark contrast to the $177 million loss from the previous year. Operating income stood at around $34 million, quite the turnaround from the operating loss of about $243 million in the same quarter the year before.

Back in late July, Spotify threw its hat into the price increase ring, marking its first hike in the US in over a decade. The standard Spotify Premium subscription tagged on an extra buck, now sitting at $10.99. Other markets and subscription plans, like Duo, Family, and Student, also got a taste of the price adjustment.

Meanwhile, Spotify is keeping the momentum going by fine-tuning its podcast and audiobook offerings. The company recently launched audiobooks for its premium subscribers, which promptly stirred the pot. The Swedish company fired shots at Apple, accusing it of playing dirty with its App Store restrictions.

This tiff between Spotify and Apple isn’t new; it dates back to 2019 when Spotify accused Apple of anti-competitive behavior in the European Union.


[ad_2]
Source link

MGM Resorts Cybersecurity Issue: A Review of Potential Vulnerabilities in the Hospitality Industry  – GBHackers on Security

0
[ad_1]

The hospitality industry is increasingly under the microscope due to rising cybersecurity concerns. The MGM Resorts data breach in 2023 stands as a stark illustration of the significant risks faced by the sector. This episode highlighted the vulnerabilities of the hospitality industry and served as a wake-up call for institutions globally.

Over six million data records were exposed worldwide through data breaches in the first quarter of 2023 alone. The last months of 2020 saw a staggering 125 million data sets exposed, the highest number to date. These numbers paint a disturbing picture and underscore the need for heightened cybersecurity measures in the hospitality sector.

As we delve deeper into this issue, we aim to shed light on the dangers, the importance of strong cybersecurity measures, and strategies for mitigating such threats.

The MGM Resorts Cybersecurity Issue 

On September 11, 2023, an unauthorized entity breached the security of MGM Resorts International systems. Confidential customer data was compromised, highlighting serious cybersecurity concerns. This event occurred despite the hospitality industry’s growing emphasis on data protection.

The breach has raised eyebrows and concerns about the effectiveness of current cybersecurity measures at MGM Resorts. It has underlined the need for more robust and comprehensive cybersecurity strategies. This incident has put MGM Resorts under scrutiny and emphasized the importance of proactive action in preventing future data breaches.

Compromised customer information

The company issued a forward-looking statement following the announcement of the breach. The types of impacted information varied by individual. According to a press release, these are the affected customer information:

  • Name
  • Phone number
  • Email address
  • Postal address
  • Gender
  • Date of birth
  • Driver’s license number

For some customers:

  • Social security number
  • Passport number

Despite the breach, the company does not believe customer passwords, bank account numbers, or payment card information was affected by this issue. This is a significant reassurance for customers concerned about financial fraud.

Damage control: MGM’s rapid response

In the face of the cybersecurity breach, MGM Resorts promptly initiated steps to secure its systems and data. They swiftly launched an investigation, enlisting the help of leading cybersecurity experts and law enforcement agencies. Customers affected by the breach were promptly notified via email about the incident.

Beyond this, MGM Resorts facilitated credit monitoring and identity protection services for all customers impacted by the breach. A dedicated call center was established to address queries and concerns, operating extensively throughout the week, including weekends, further cementing MGM’s commitment to its patrons during this challenging time.

The Hospitality Industry at the Cyber Crossroads   

The hospitality industry stands at a decisive juncture, grappling with escalating cybersecurity threats. With colossal data sets and sensitive customer information at stake, these sectors are becoming lucrative targets for cybercriminals. This impending danger necessitates an urgent review and reinforcement of existing cybersecurity measures.

Why the hospitality sector remains vulnerable 

The hospitality sector is acutely vulnerable to cybersecurity threats for several reasons.

  • First, the industry harbors vast amounts of sensitive customer data, making it an enticing target for cybercriminals.
  • Second, it relies heavily on digital platforms for transactions, bookings, and customer interactions, escalating the potential for data breaches.
  • Third, the widespread use of third-party vendors for services like Wi-Fi, payment processing, and booking systems creates additional entry points for hackers.
  • Lastly, rapid technological advancement often outpaces cybersecurity measures, leaving gaps in protection.

These factors collectively contribute to the industry’s heightened vulnerability to cyber threats.

Previous cybersecurity incidents in the industry 

Cybersecurity issues have previously marred the hospitality industry. For instance, Marriot Hotel Group faced severe criticism in 2018 after a significant data breach. This incident compromised the personal information of about 500 million guests. Similarly, British Airways suffered a significant cybersecurity incident in 2018, exposing the details of around 380,000 bookings.

Both instances resulted in hefty regulatory fines, tarnishing the reputation of these prominent industry players. These episodes underline the growing threat of cybersecurity breaches in the hospitality sector.

Protecting Personal Data: A Shared Responsibility 

In this era of digital dominance, safeguarding personal data is not just a technical issue but a shared responsibility. It’s a complex task involving consumers, businesses, and regulatory bodies. Here, we explore some practices to improve data protection in the hospitality industry.

What businesses can do to fortify their defenses 

Businesses can bolster their defenses with regular system upgrades and deployment of advanced firewalls. Implementing multi-factor authentication is an excellent way to add an extra layer of security. Regular staff training for recognizing and avoiding phishing attempts is crucial. Lastly, regular audits of third-party vendors can help identify potential vulnerabilities.

Actions customers can take to safeguard their data 

Customers play a vital role in protecting their data. Here are a few things you can do as a customer:

  • You can start by creating strong, unique passwords for each online account. Regularly updating these passwords further enhances security.
  • Where available, two-factor authentication through mobile devices offers additional protection.
  • It’s also advisable for customers to be wary of unsolicited communication asking for personal details.
  • Limiting the amount of sensitive information shared online can significantly decrease the risk of compromised personal data.
  • Finally, customers should regularly monitor their accounts for unusual activities and immediately report discrepancies to the service provider.

Taking these steps can help customers safeguard their data in the digital landscape of the hospitality industry.

A Call To Action for a More Secure Digital Future in Hospitality 

As we navigate the digital landscape, the hospitality industry must take bold strides towards bolstering cybersecurity measures. Let’s view security breaches not as setbacks but as catalysts for change. 

This is an invitation to hoteliers, guests, and cybersecurity professionals alike to invest time, resources, and energy in fortifying our digital walls. The fight against cyber threats is not a solitary one.

So, let’s transform vulnerabilities into strengths and build an impregnable cybersecurity fortress in hospitality. Let’s not just envisage a more secure future; let’s engineer it. Remember, cybersecurity is not a destination but a constant vigilance and adaptation journey.

Together, we can ensure that the hospitality industry remains a physically and digitally welcoming space. In an era where data is currency, let’s prioritize its protection. Our collective action today will pave the way for a secure, resilient, and thriving hospitality industry tomorrow.


[ad_2]
Source link

New Motorola concept is a phone that bends around your wrist

0
[ad_1]

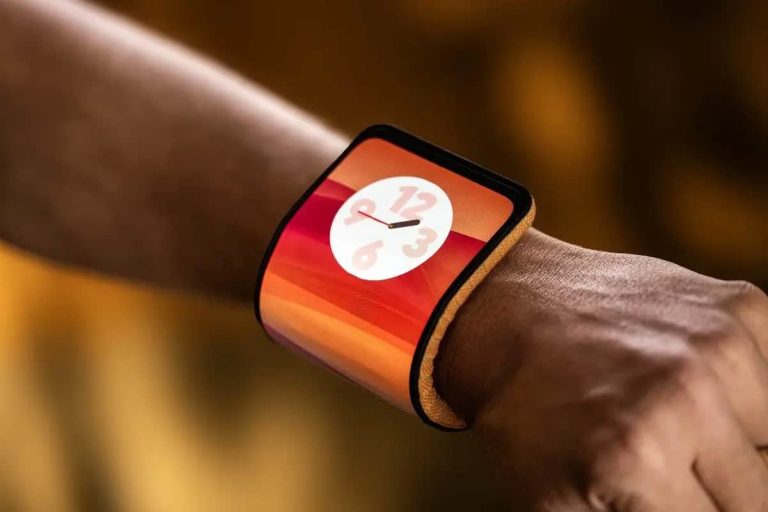
Motorola has shown off a new concept phone during Lenovo Tech World ‘23, and this one bends around your wrist. It’s a smartphone hybrid of sorts, which acts as a bracelet or a smartwatch, if you will.

New Motorola concept is an odd phone that bends around your wrist

The star of the show here is a fullHD+ pOLED display. It can “be bent and shaped into different forms depending on users’ needs”, says the company. That display is actually the whole point of this concept, even though Motorola did include Android OS on this thing.

This device was made basically just to highlight the display itself, and its possibilities. Motorola says that the display can serve as a regular display on a phone, and also wrist worn, or “positioned in several stand modes”.

This is a 6.9-inch panel, and when it’s laid flat, it runs “full Android experience”. It can also run a more compact form of full Android on a 4.6-inch display, when you bend it into a different shape. The company says that this experience is similar to what the cover display on the Motorola Razr+ offers.

Motorola phone concept wrist 2 2023

The company showed off something similar back in 2016

If you take a closer look at the device, you’ll notice that it has a fabric back. This does remind us of a device that Lenovo showed off back in 2016, but it does seem to be more advanced than that. That is not surprising, as it has been 7 years since then.

This particular device will not become available for purchase, not at all. This is just a concept to show off what the possibilities are. It remains to be seen if we’ll ever see something similar on the market, to be quite honest.

True, it can be bent to fit on a wrist, but it does look very odd still, and at this point in time, it’s difficult to imagine people actually wearing this. Who knows, though, perhaps the company will figure out a different form factor that works in such scenarios.


[ad_2]
Source link

BNB vs. MATIC: Analyzing Historical Trends

0
[ad_1]

Intuition can only get you so far in crypto trading. You can get lucky once or twice, but extensive analysis is necessary when exchanging coins. So, before you go ahead and swap BNB to MATIC, read our guide on the importance of historical analysis and how these tokens compare.

MATIC Review

Initially known as the Matic network, this blockchain is now named Polygon. It’s famous as a plasma chain that aims to improve on Ethereum’s drawbacks, primarily scalability. The network uses a consensus mechanism based on the PolyBFT concept. Together with its unique structure, it increases transactions per second from about 20 on Ethereum to over 50,000.

MATIC has the basic use case of paying for transaction fees, considering it’s the Polygon’s native token. Owning MATIC also gives you voting rights to express your opinion on proposals to improve the network.

BNB Review

BNB is the native token of the Build N Build (BNB) Chain launched by the famous crypto exchange Binance. The coin’s history goes back to 2017 when it was released along with the swapping platform. Today, Binance is the largest exchange, and BNB is among the best-positioned coins in the crypto rankings.

You can use BNB to pay for transaction fees, and Binance will secure discounts if you use this currency. Thanks to the support of such a major company, BNB is widely adopted and used for different use cases. That includes staking, using it for payment purposes on various websites, and using it for other DeFi services offered by Binance.

Comparing Historical Performance

MATIC currently has 9.31 billion tokens in circulation, which is close to the maximum of ten billion. The token was worth only $0.003 in May 2019, so you could say it took some time to kick off. It had the best days in 2021 when it reached an all-time high of $2.92. Unfortunately, the crypto crash also knocked down MATIC’s value, and it is now worth $0.548. During the last 12 months, the coin’s value went down from the local high of $1.48, so there’s a noticeable negative trend.

As for BNB, it doesn’t have a maximum supply, and the auto-burning process contributes to scarcity. You can currently find around 153 million BNB coins in circulation, with the current price set at $214.13.

Binance Coin entered the market in 2017, and that’s when it also had the all-time low — $0.09611. The token had a positive trend and increased to a whopping $690.93 in May 2021. After the crypto crash, BNB recovered a significant portion of its value to reach today’s worth. In the last 12 months, it lost about 22% of its value, but predictions for the future are promising.

Apart from tracking the coins that exist on your watchlist, identifying exciting new tokens before others can be imperative. That’s why we advise monitoring the XxXCoin price and other coin fluctuations to determine new trading options.

Significant Historical Events

The launch of the Binance exchange in July 2017 revamped the crypto industry since it only took six months for the platform to become the biggest exchange in terms of trading volume. Creators offered BNB tokens via the initial coin offering, which lasted from June 26th to July 3rd.

The platform sold 100 million tokens via the ICO and raised $15 million. Ethereum platform was the place where the offering occurred, and you could purchase 2,700 BNB tokens for a single ETH. In 2019, the BNB coin also became available on the BNB Chain as a BEP2 token, and all users could acquire those coins at a 1:1 exchange rate.

As for Polygon, its critical historical event was the mainnet launch that occurred In 2017. The coin was almost immediately listed on Binance, and the following years only brought improvements to this plasma chain. In 2021, the blockchain merged with Hermez, the zk-roll-up platform. zkEVM Mainnet Beta went live in March 2023, and this EVM equivalent seems to secure a promising future for the Polygon project.

BNB vs MATIC: Considering for Future Investments

The crypto market has recovered from a huge crash, and investors agree better times lie ahead. Experts are excited regarding both BNB and Matic. Binance supports the BNB Coin, so it’s likely it will maintain a high position in the rankings. The new zkEVM Mainnet Beta makes MATIC particularly attractive, indicating it could be the right moment to invest in this coin.


[ad_2]
Source link

Meta starts promoting Threads posts on Facebook, no opt-out option (what?!)

0
[ad_1]

Are you on Threads yet? Are you? Are you? Well, it seems that’s the question that’s been bugging Meta, and it’s now pushing hard to get Threads some of that juicy popularity. Android Headlines reportst that Meta has started to promote Threads posts on Facebook feeds.

Meta starts promoting Threads posts on Facebook, no opt-out option just yet


Threads’ daily active users have been plummeting recently, but Meta is not giving up on the Twitter-like platform just yet. Meta plans to boost Threads’ engagement by including Threads’ posts to your Facebook feed to lure you in.The new feature is called “For you on Threads”, and it appears on the Facebook feed with popular Threads posts. The posts are automatically recommended, so you can’t just share your Thread post to Facebook by yourself.

It is still unclear how Meta chooses what Threads posts to recommend on Facebook. On the other hand, some are concerned about how this feature may affect user privacy. Threads is built for sharing stuff with a limited circle of friends, while getting a Threads post on Facebook may bring more attention to it, and expose it to a broader audience.

Currently, there seems no way for you to keep Threads posts off of Facebook. The company has said it’s “listening to feedback” and still adjusting the feature.

This growth strategy is not new to Meta. It’s previously promoted Instagram Reels on Facebook’s feed as well. Threads are currently also promoted on Instagram, but it’s optional, while the Facebook promo doesn’t currently allow you to opt-out.

So far, Threads has over 130 million users. It had a few months of stagnation in its growth, and also a decline in usage. We’ll see how the latest move by Meta will influence things.


[ad_2]
Source link

Android Malware Masquerades as Chrome Browser Reads SMS

0
[ad_1]

Threat actors primarily target remote access and control of victims’ devices by employing deceptive tactics. They often create fake apps or pose as legitimate ones to trick users into downloading malicious software, compromising the targeted devices’ security and privacy. 

This approach allows them to gain unauthorized access, potentially steal sensitive information, or carry out other malicious activities. 

Cybersecurity researchers at K7 Security Labs recently identified Rusty Droid RAT, a stealthy Android malware masquerading as a Chrome browser to read SMS and intercept emails.

The malware masquerades as ‘Chrome’

Technical Analysis

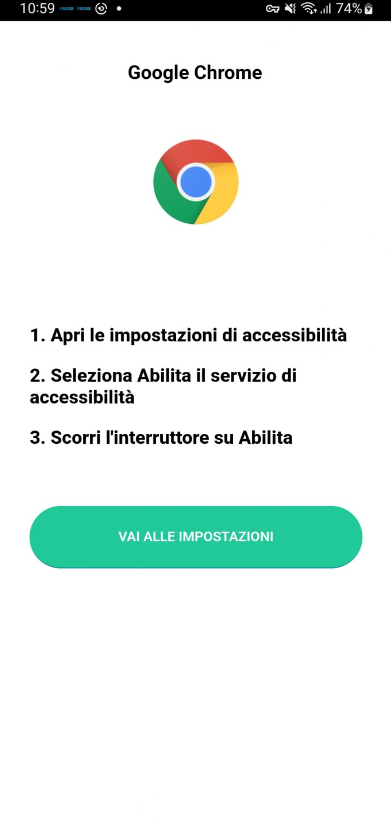
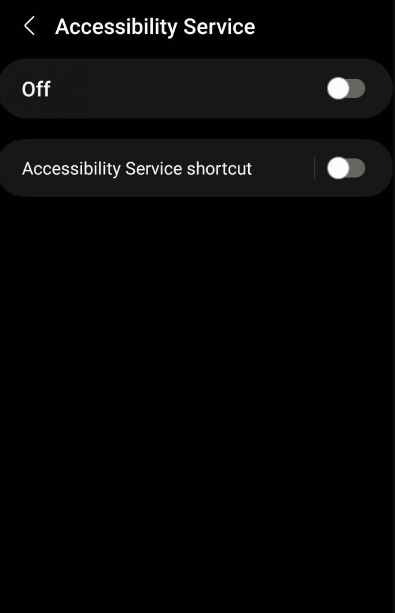
Rusty Droid persists by repeatedly prompting the user to enable Accessibility Service, concealing its icon from the app drawer once granted.

Accessibility permission request (Source – K7 Security Labs)

Before linking to C2, the Rusty Droid malware collects the following data:

  • Contact info
  • Accounts
  • App list

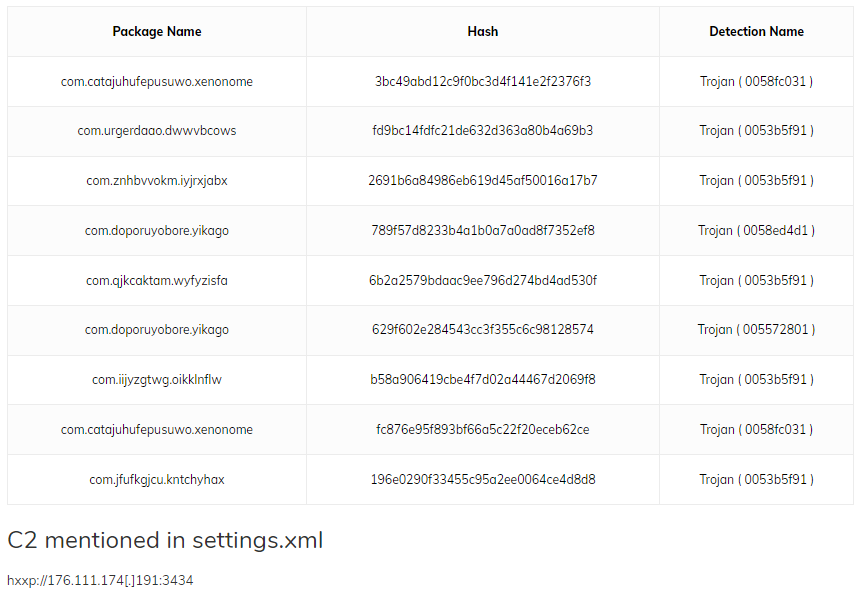
With accessibility permissions, it decrypts ‘LqL.json’ to an executable DEX file and deploys ‘settings.xml’ with the C2 server IP and bot ID.

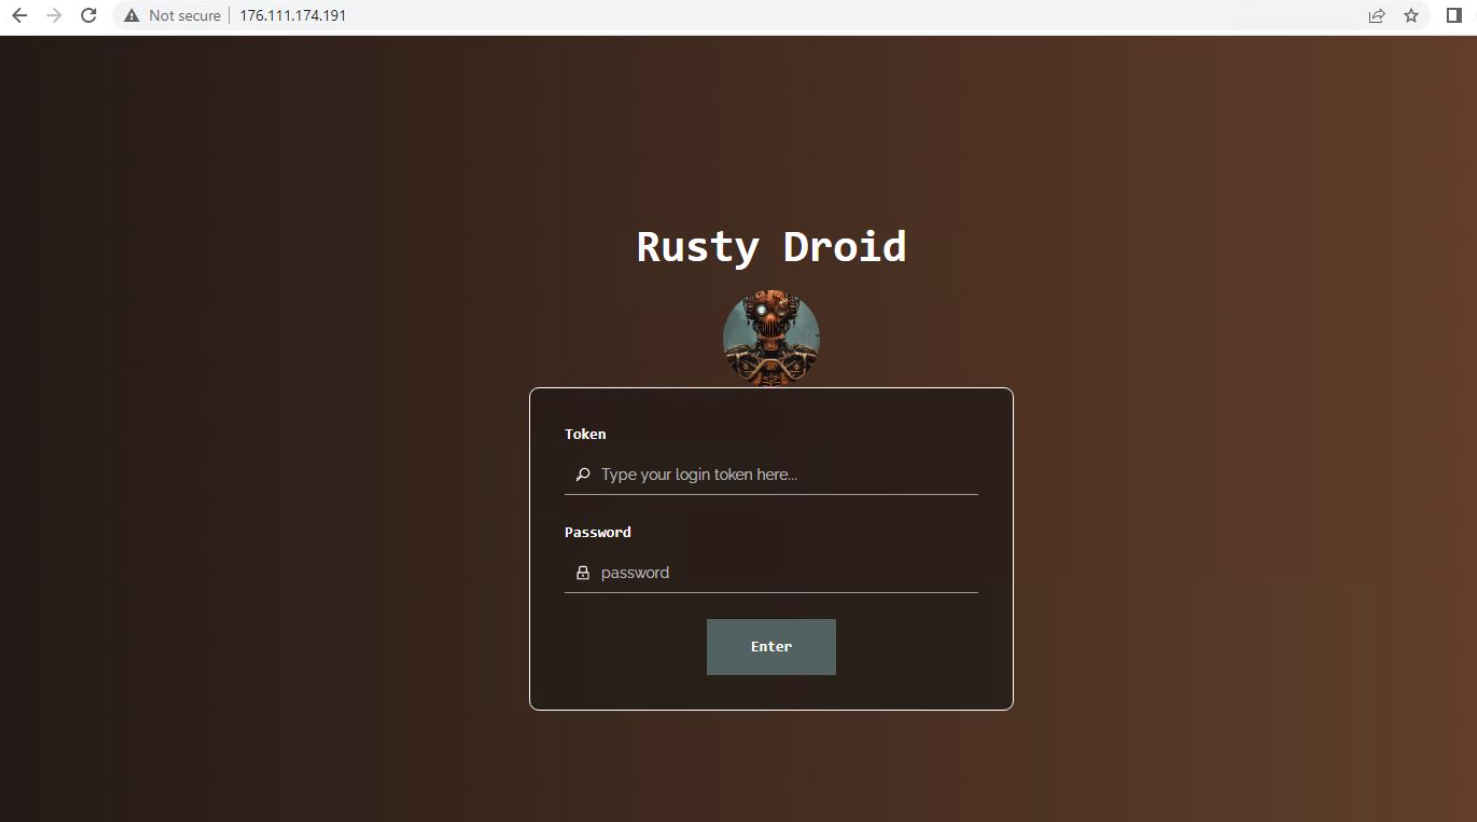
This Trojan abuses the Android Accessibility Service as a keylogger, stealing victims’ data like passwords, credit card details, and messages and sending it to cybercriminals for identity theft and fraud, with a connection to C2 server “176.111.174[.]191.

Malicious C2 Panel (Source – K7 Security Labs)

This malware can collect keystrokes during user interaction with those applications to steal login information, including cryptocurrency wallet seed phrases, by connecting to a control server to get a list of targeted programs.

Apps Targeted

Here below, we have mentioned all the targeted applications:

  • com.android.vending
  • ar.bapro
  • ar.com.santander.rio.mbanking
  • ar.macro
  • at.spardat.bcrmobile
  • at.volksbank.volksbankmobile
  • au.com.amp.myportfolio.android
  • au.com.bankwest.mobile   
  • au.com.cua.mb   
  • au.com.ingdirect.android   
  • au.com.macquarie.banking   
  • au.com.mebank.banking   
  • au.com.newcastlepermanent   
  • au.com.suncorp.SuncorpBank   
  • com.BOQSecure   
  • com.BankAlBilad   
  • com.CredemMobile   
  • com.EurobankEFG   
  • com.IngDirectAndroid   
  • com.a2a.android.burgan   
  • com.abnamro.nl.mobile.payments   
  • com.adcb.bank   
  • com.advantage.RaiffeisenBank   
  • com.akbank.android.apps.akbank_direkt   
  • com.anz.android.gomoney   
  • com.aol.mobile.aolapp   com.appfactory.tmb   
  • com.bancodebogota.bancamovil   
  • com.bancomer.mbanking   
  • com.bancsabadell.wallet   
  • com.bankaustria.android.olb   
  • com.bankinter.launcher   
  • com.bankinter.portugal.bmb   
  • com.bankofqueensland.boq   
  • com.barclays.android.barclaysmobilebanking   
  • com.barclays.ke.mobile.android.ui   
  • com.bbva.bbvacontigo   
  • com.bbva.netcash   
  • com.bbva.nxt_peru   
  • com.bcp.bank.bcp   
  • com.bendigobank.mobile  
  • com.boubyanapp.boubyan.bank   
  • com.boursorama.android.clients   
  • com.kutxabank.android   
  • com.kuveytturk.mobil   
  • com.latuabancaperandroid 
  • com.caisseepargne.android.mobilebanking   
  • com.cajasur.android   
  • com.cbd.mobile   
  • com.cbq.CBMobile   
  • com.chase.sig.android   
  • com.cibc.android.mobi   
  • com.cic_prod.bad   
  • com.citi.citimobile   
  • com.citibanamex.banamexmobile   
  • com.citibank.mobile.citiuaePAT   
  • com.clairmail.fth   com.cm_prod.bad   
  • com.coinbase.android   
  • com.comarch.mobile.banking.bgzbnpparibas.biznes   
  • com.comarch.security.mobilebanking   
  • com.commbank.netbank   
  • com.csam.icici.bank.imobile   
  • com.db.mm.norisbank   
  • com.db.mobilebanking  
  •  com.db.pbc.miabanca   
  • com.db.pbc.mibanco   
  • com.dib.app   
  • com.discoverfinancial.mobile   
  • com.finansbank.mobile.cepsube   
  • com.finanteq.finance.ca   
  • com.fullsix.android.labanquepostale.accountaccess   
  • com.fusion.banking   
  • com.fusion.beyondbank   
  • com.garanti.cepsubesi   
  • com.getingroup.mobilebanking   
  • com.greater.Greater   
  • com.grppl.android.shell.BOS   
  • com.grppl.android.shell.CMBlloydsTSB73   
  • com.grppl.android.shell.halifax   
  • com.htsu.hsbcpersonalbanking   
  • com.imaginbank.app  
  •  com.infonow.bofa   
  • com.ingbanktr.ingmobil   
  • com.isis_papyrus.raiffeisen_pay_eyewdg   
  • com.itau.empresas   com.kasikorn.retail.mbanking.wap   
  • com.konylabs.capitalone   
  • com.konylabs.cbplpat   
  • Com.magiclick.odeabank   
  • com.moneybookers.skrillpayments   
  • com.mobileloft.alpha.droid

IOCs

IOCs (Source – K7 Security Labs)

Protect yourself from vulnerabilities using Patch Manager Plus to quickly patch over 850 third-party applications. Try a free trial to ensure 100% security.


[ad_2]
Source link

Don’t like your Youtube Music playlist art? You can generate it using AI

0
[ad_1]

Sometimes, you don’t read the names of your playlists on YouTube Music. Rather, you just look at the cover art. The app crafts the cover image based on the album art of the songs in it. It’s a neat idea, but the company wants you to make your own. According to a report, YouTube Music will let you generate new playlist cover art using AI.

This is most likely making use of Google’s Imagen image model. This is Google’s image model and it’s been in production for quite some time. It’s what will power the image generation behind Google’s Gemini multimodal LLM. We’ve seen examples of what it can do here and there, but this will give you a more direct showcase of what Imagen can do.

YouTube Music will let you use AI to craft new playlist art

This feature is currently rolling out, but we’ve yet to see it. If you don’t see it just yet, then you’ll want to wait a day or two.

In order to use this feature, you’ll go to the playlist that you want to generate art for. There, you’ll tap on the Edit Playlist button. In the edit menu, you’ll see a picture of the playlist art. Tapping on that will open a UI that will let you choose a category. These categories will be pretty general like animals or nature. When you choose a category, the app will then generate an image based on it.

From the way it sounds, it doesn’t seem like you’ll be able to type in a prompt. If not, then that will be a bummer. That would give people more flexibility. If you have a taste for music that is not properly represented by general categories, then it would be hard to find art for it. In any case, this is a nice feature to have if you want to switch things up.


[ad_2]
Source link

Why every mobile user needs a VPN

0
[ad_1]

With the proliferation of free public Wi-Fi hotspots at coffee shops, airports, hotels, and other public places, it’s tempting to connect to them for convenience and to avoid eating into your mobile data allowance.

However, using public Wi-Fi networks comes with significant security risks that can make your personal information and mobile devices accessible to bad actors. Using a virtual private network (VPN) is an effective way to protect your mobile devices when using public Wi-Fi and, in this article, we explain what VPNs are, how they work, and how can you install one on your smartphone.

What is Public Wi-Fi?

Public Wi-Fi refers to wireless internet networks that are open and available for the general public to use. For example, many coffee shops offer free Wi-Fi that anyone nearby can connect to without needing a password. While public Wi-Fi networks are a convenient way to access the internet on the go, they also pose security risks for users.

Risks of Public Wi-Fi

Public Wi-Fi can be accessed and infiltrated by criminals to compromise your privacy and expose your personal data. The main risks of using these networks include:

– Snooping and hacking: Data sent over public Wi-Fi can easily be intercepted and monitored by hackers through snooping and sniffing. They can steal sensitive information like credit card details, login credentials, emails, etc.
– Evil twin attacks: Hackers create fake hotspots impersonating legitimate networks to trick users to connect. All data is then directly sent to the hacker.
– Man-in-the-middle attacks: Hackers insert themselves between your device and the router. This allows them to monitor communications and steal data.
– Unsecured connections: Public Wi-Fi networks often have no password or weak security. This gives hackers easy access to infiltrate the network and user’s devices.
– Malware spreading: Connecting to public networks exposes you to potential malware that can infect your device. Viruses, worms, spyware, and more can be installed without you knowing.
– Unencrypted networks: Data sent over unencrypted networks has no protection. Hackers on the network can see all transmitted information and activity in plain text.
– Session hijacking: Hackers can take over your session, impersonate you, and gain access to sensitive accounts. Financial, business, and email accounts could all be compromised.
– Traffic sniffing: Specialized software allows hackers to intercept and record data packets transmitted over the network, even if they’re encrypted.

What is a virtual private network (VPN)?

A virtual private network, or VPN, is a service that creates a secure, encrypted connection over the internet between your device and a server operated by the VPN provider. This allows you to safely access the internet, share data, and browse privately while protecting your online activities from prying eyes. There are a few different types of VPNs:

Remote access VPN: This type of VPN allows individual devices to connect to a private network over the internet. It essentially extends the network to you regardless of your location, allowing secure remote access. Many mobile VPN apps utilize remote access VPNs.

Site-to-site VPN: Site-to-site VPNs make networks come together safely. For example, you can use this type of VPN to connect your office and home network so you can access your office network from the convenience of your home.

Multi-protocol label switching (MPLS) VPN: An MPLS VPN allows various sites to interconnect through an MPLS provider’s network. It offers a secure way for enterprises to connect geographically dispersed offices.

To use a VPN on a mobile device, you first need to select and install a trusted VPN app for Android or iOS. Look for VPNs with robust encryption, strict no-logging policies, and excellent performance. After installing the app, you’ll need to create an account with the provider if you don’t already have one.

Once you log in, simply tap the app to connect to the VPN server of your choice. The VPN will encrypt and reroute your phone’s internet traffic through the server, hiding your IP address and securing your connection.

Make sure that the VPN app is running whenever you use public Wi-Fi for full protection. You can even set your phone to automatically connect to the VPN whenever it joins an unsecured wireless network. With the VPN protecting your mobile devices, you can safely use public Wi-Fi without worrying about your privacy and security.

Benefits of a Mobile VPN

Installing a VPN on your mobile device provides several important benefits when using public Wi-Fi:

– Encrypts data: Encrypting your internet traffic keeps your online activities, information, and identity secure from hackers, cybercriminals, and other users on the same network. This prevents sensitive info from being compromised.
– Hides IP address: VPNs mask your IP address so that your mobile devices cannot be tracked or identified while using public Wi-Fi. Your location and identity stay private.
– Bypasses geographic restrictions: Connecting through a VPN server in another country lets you bypass location-based restrictions and censorship to access content not available in your area.
– Secures public Wi-Fi: VPN protection secures your connection on public networks and safeguards you from common threats like man-in-the-middle attacks. Using public Wi-Fi is much safer with a VPN.
– Safer remote access: When accessing your work or office network remotely over public Wi-Fi, a VPN keeps the connection secure and data protected from exposure.

Bottom Line

Public Wi-Fi is risky and can potentially expose your sensitive personal information as well as leave your mobile devices vulnerable to security threats. Encrypting your connection with a VPN is vital for staying safe and private while using public wireless networks. VPNs are an essential security tool in the modern digitally-connected world.


[ad_2]
Source link

The Fallout series on Prime Video has an official release date

0
[ad_1]

The Fallout series that will be coming to Amazon’s Prime Video service has an official release date. After at least one official tease, multiple leaks, and numerous reports about the show and its casting choices, Amazon is lifting the curtain on when you can watch the upcoming series. And it’s coming early next year. Fallout will be based on the video game series of the same name from Bethesda Game Studios and will feature characters played by a variety of prominent actors and actresses. Including Walton Goggins, Ella Purnell, Aaron Moten, Xelia Mendes-Jones and more.

Amazon has yet to push out an official trailer for the series, though one has leaked in a very brief clip before. The show’s story has also been kept under wraps. But it has been confirmed that the TV series will not be following the story of the games. Instead of retelling those stories, the show will have its own story set in the same universe. Though it will still reference things from the games and is very clearly still going to be “Fallout.”

Fallout will release on Prime Video in mid-April

There’s still more than a few months to go before the series is ready. But the wait will surely be easier now that Amazon has put down a date to look forward to. Fallout will officially release on April 12 of 2024. The confirmation about the release date was put out by the Prime Video account over on X.

As with all of Amazon’s original series, Fallout will follow a weekly release cycle for each episode. Though it’s possible that it releases two episodes from the start. Amazon did this last year with the release of Rings of Power. Which debuted on September 1 of 2022 with both episode one and episode two being available to watch. Then moving to a weekly release cycle for all remaining episodes after that.

There’s no guarantee it’ll do the same thing here of course. In addition to Fallout, Amazon has also reportedly ordered a God of War series based on the hit video games from Santa Monica Studios.


[ad_2]
Source link