Apple’s HomePod speakers finally getting YouTube Music support

0
[ad_1]

It might seem weird that HomePod owners can’t listen to their favorite tunes via YouTube Music, but Apple’s speakers don’t actually feature support for this specific streaming service.

Thankfully, that’s about to change, so if you’re subscribed or consider subscribing to YouTube Music, you’ll finally be able to use your subscription with the Apple HomePod speakers.

YouTube Music announced over the weekend that it has officially launched support on Apple HomePod to all Premium and Music Premium members globally, so it’s not just in the United States or a select number of countries.

The streaming service didn’t offer a timeline for the rollout, so we can probably assume that support for HomePod speakers is already live. To check if you can listen to music via Google’s streaming service, simply head to Settings / Connected Apps / Connect with HomePod.

As soon as the setup is complete, say “Hey Siri, play music on YouTube Music” to get started. Of course, you’ll also be able to set YouTube Music as your default music provider to avoid saying “… on YouTube Music” every time you want to listen to your favorite music.

In order to do that, you’ll have to go to Home app on your iOS device, then Settings / Username / Default Service and choose YouTube Music as your default music provider.

Keep in mind that you’ll have to update your YouTube Music app to the latest version to get it running on your HomePod speakers.


[ad_2]
Source link

North Korean Hackers Exploiting TeamCity Flaw

0
[ad_1]

Microsoft has detected two North Korean nation-state threat actors, Diamond Sleet and Onyx Sleet, exploiting CVE-2023-42793. This vulnerability allows remote code execution on various JetBrains TeamCity server versions widely used for DevOps and software development activities.

Diamond Sleet and other North Korean threat actors executed software supply chain attacks through build environment infiltration, posing a high risk to affected organizations. 

JetBrains has issued an update to fix the vulnerability and offers mitigation for users unable to update to the latest version.

Document
FREE Demo

Implementing AI-Powered Email security solutions “Trustifi” can secure your business from today’s most dangerous email threats, such as Email Tracking, Blocking, Modifying, Phishing, Account Take Over, Business Email Compromise, Malware & Ransomware

North Korean Hackers Exploiting TeamCity Flaw

Diamond Sleet (ZINC) is a North Korean threat actor focusing on espionage, data theft, and network disruption, often targeting global media, IT, and defense entities. 

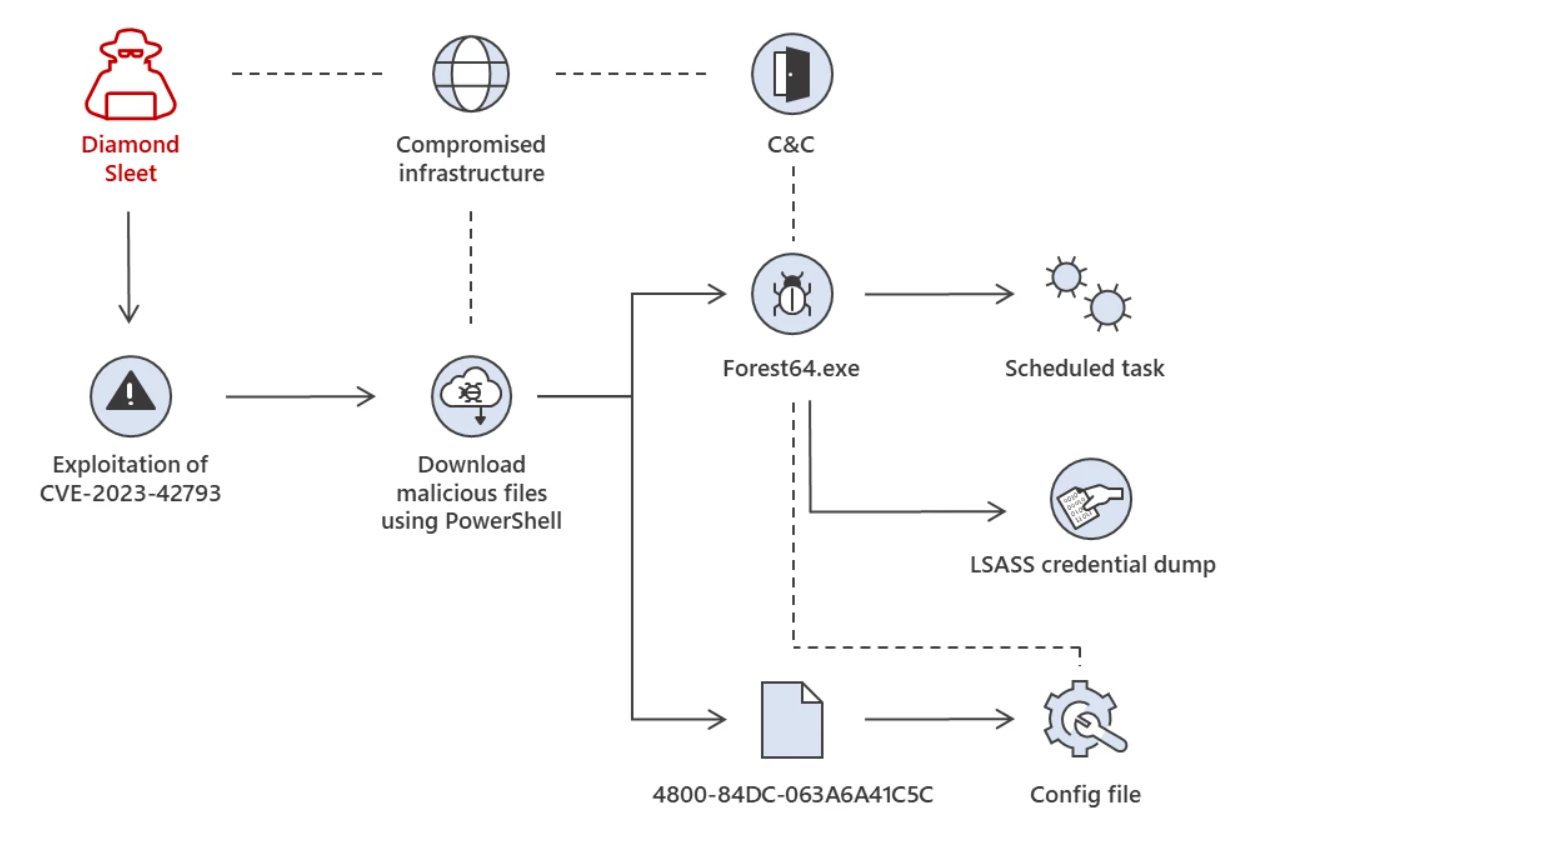
Diamond Sleet attack chain 1
Diamond Sleet attack chain 1 (Source – Microsoft)

Moreover, Onyx Sleet (PLUTONIUM), also North Korean, primarily targets defense and IT services in South Korea, the U.S., and India, using advanced tools for persistent, stealthy access.

Diamond Sleet and Onyx Sleet exploit the same vulnerability but employ distinct tools and tactics after successful infiltration. Microsoft believes these actors opportunistically target vulnerable servers, deploying malware and techniques for persistent access. 

Microsoft notifies affected customers directly to help secure their environments. Diamond Sleet, after breaching TeamCity servers, employs PowerShell to fetch two payloads from previously compromised legitimate infrastructure stored in C:\ProgramData:-

  • Forest64.exe
  • 4800-84DC-063A6A41C5C
Diamond Sleet attack chain 2
Diamond Sleet attack chain 2 (Source – Microsoft)

Forest64.exe creates a scheduled task for persistence, and Diamond Sleet uses the ForestTiger backdoor to extract LSASS memory credentials, detected by Microsoft Defender Antivirus as ForestTiger.

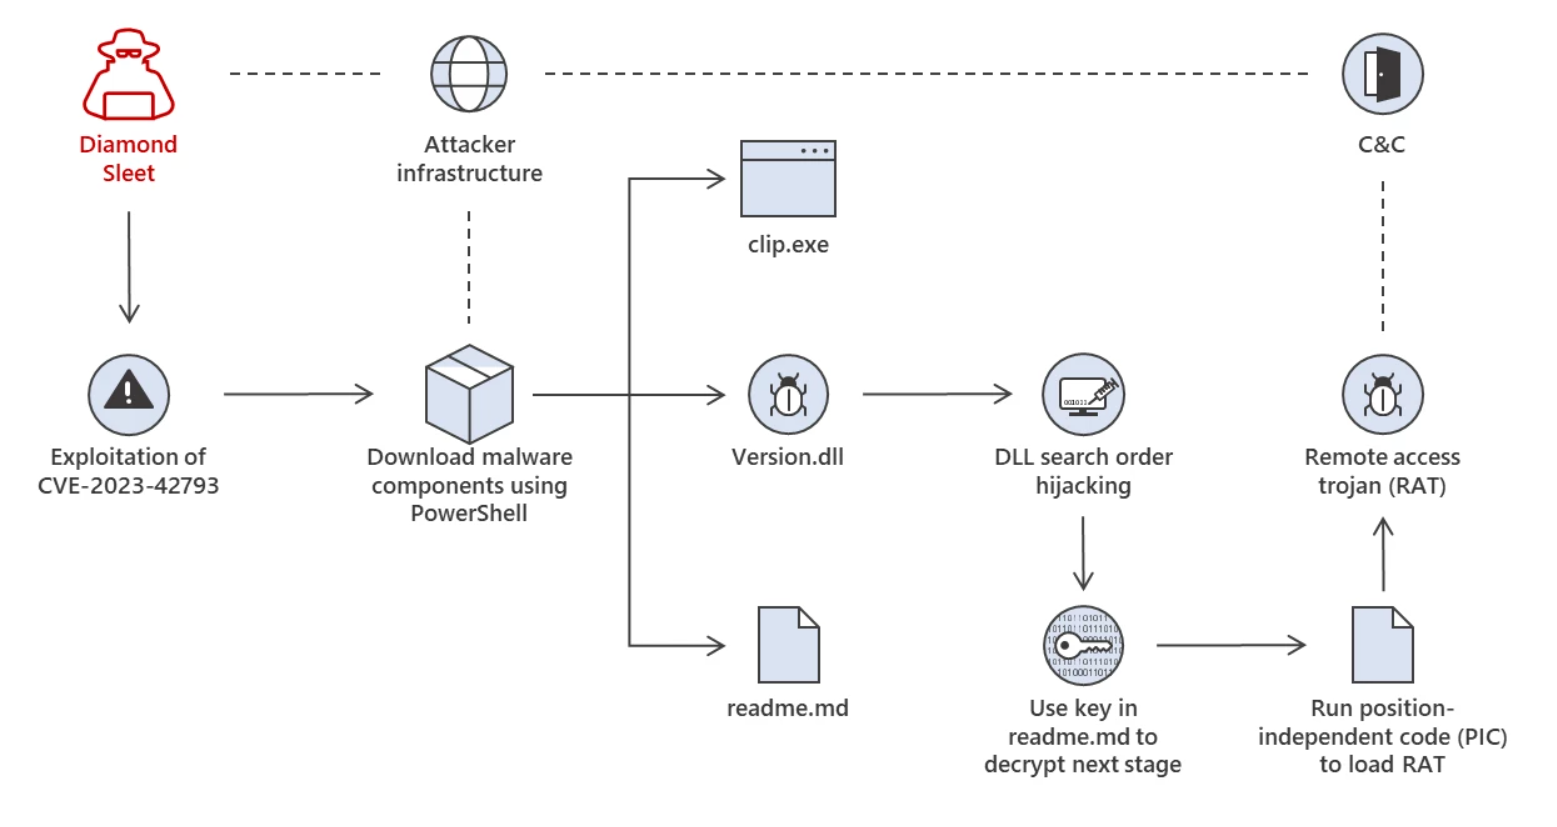
Diamond Sleet uses PowerShell to fetch a malicious DLL on compromised servers. The DLL is placed in C:\ProgramData, where it engages in DLL search-order hijacking alongside a legitimate .exe file, specifically DSROLE.dll and Version.dll, as seen by Microsoft.

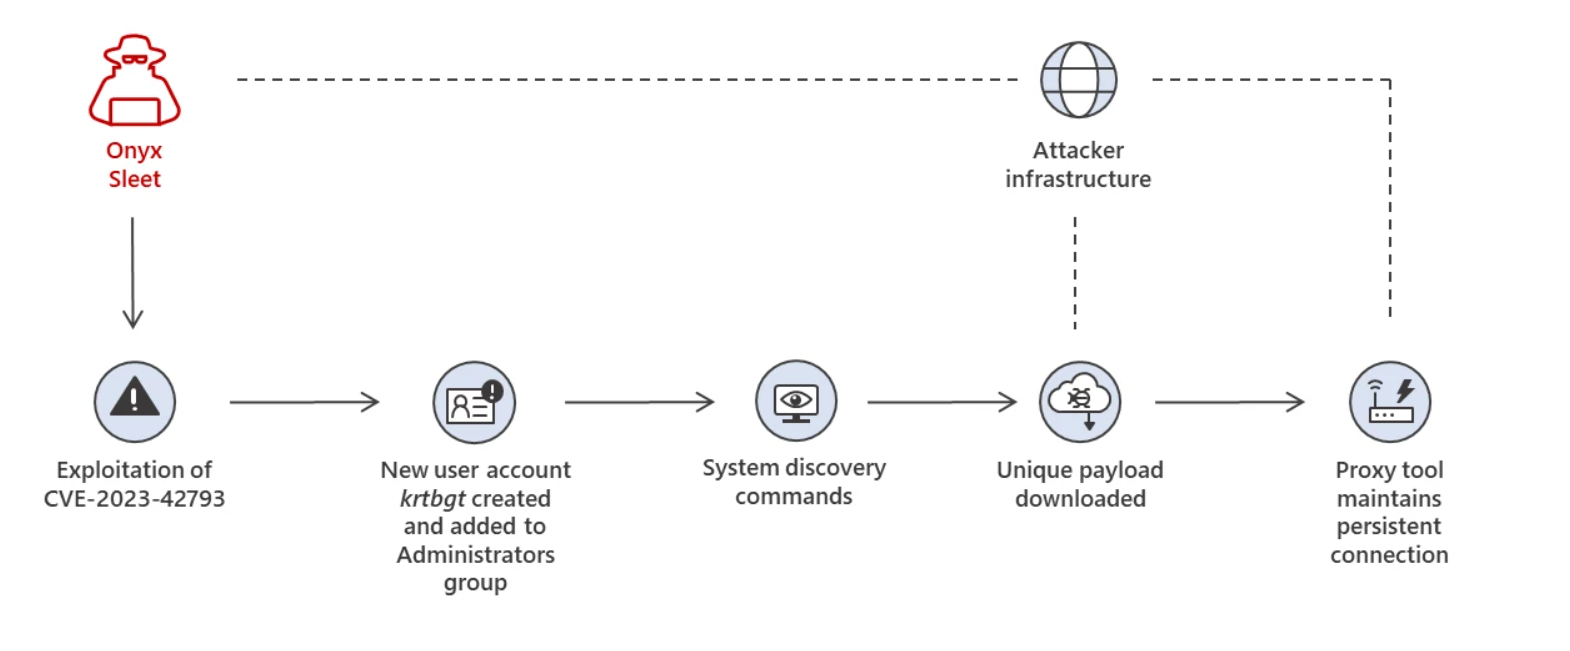
Onyx Sleet creates a new user account, ‘krtbgt,’ on compromised systems, impersonating ‘KRBTGT.’ 

Onyx Sleet attack chain
Onyx Sleet attack chain (Source – Microsoft)

They add it to the Local Administrators Group, perform system discovery, and deploy a unique payload using PowerShell, establishing a persistent connection with attacker-controlled infrastructure.

Recommendations

However, here below, we have mentioned all the recommendations that the security researchers are recommending:-

  • Implement JetBrains’ update or mitigations for CVE-2023-42793.
  • Check for the provided indicators of compromise in your environment to detect potential intrusions.
  • Block incoming traffic from IPs listed in the IOC table.
  • Defend against this threat with Microsoft Defender Antivirus.
  • Act swiftly to counter malicious activity on the affected device. If malicious code is active, the attacker may have full control.
  • Examine the device timeline for signs of lateral movement via one of the compromised accounts.
  • Verify that ‘Safe DLL Search Mode’ is enabled.

Protect yourself from vulnerabilities using Patch Manager Plus to patch over 850 third-party applications quickly. Take advantage of the free trial to ensure 100% security.


[ad_2]
Source link

Indian Authority Crackdown Microsoft, Amazon support scammers

0
[ad_1]

Technical support fraud, also called tech and customer support fraud, is when someone pretends to be technical or customer support to trick people into giving them money.

Criminals may offer help to fix problems like updating the computer Antivirus or the need to update a software license.

Microsoft and Amazon supported CBI (Central Bureau of Investigation) and Federal enforcement agencies to raid multiple sectors in India on 19th  October.

Document
FREE Demo

Implementing AI-Powered Email security solutions “Trustifi” can secure your business from today’s most dangerous email threats, such as Email Tracking, Blocking, Modifying, Phishing, Account Take Over, Business Email Compromise, Malware & Ransomware

Tech support fraud is a costly and significant issue. Every year, criminals operating illegal call centers prey on the vulnerable and scam thousands of victims. 

Tech Support Fraud resulted in more than 30 raids on call centers and more than 100 charges so far. By the Investigation, there are more than $1 billion in losses to victims.

The scammers targeted over 2,000 customers across Amazon and Microsoft, primarily based in the U.S., but also in Canada, Germany, Australia, Spain, and the UK.

The partnerships also support the importance of improving the internet and protecting more people. 

However, criminals will try to rebuild their businesses and open up new illegal call centers. 

The CBI, Amazon, and other international law enforcement agencies are committed to staying alert, sharing important information, and working closely with Indian law enforcement agencies and authorities from the countries attacked to help them with their investigations.

The CBI Tweeted that “CBI LAUNCHES OPERATION CHAKRA-II TO COMBAT AND DISMANTLE ORGANIZED CYBER ENABLED FINANCIAL CRIMES; DURING NATIONWIDE CRACKDOWN, SEARCHES CONDUCTED AT AROUND 76 LOCATIONS; LARGE NUMBER OF DIGITAL GADGETS INCLUDING LAPTOPs, HARD DISC ETC RECOVERED.”

The government requests to be aware of these scammers to protect our money and personal information.

Protect yourself from vulnerabilities using Patch Manager Plus to patch over 850 third-party applications quickly. Take advantage of the free trial to ensure 100% security.


[ad_2]
Source link

How to Install Microsoft Exchange Updates with Reliability

0
[ad_1]

Installing Microsoft Exchange Updates can be a challenging task, as it may lead to various issues in the process, such as compatibility problems, data loss, service disruptions, security vulnerabilities, update failures, dependency conflicts, or backup and recovery challenges.

There are several things that can go wrong when installing Cumulative Updates (CU) or Security Updates on your Exchange Server. You may encounter issues during and after installation or even the installation of updates may fail or stop.

The installation of updates could be hindered due to underlying issues with the operating system, damaged hardware, incorrect network configuration, conflict with third-party applications, corrupted updates, or human errors. In this article, we will be going through the things that you can do to prevent issues when installing updates and how to resolve issues (if occur) as fast as possible and with no data loss.

Prerequisites before Installation

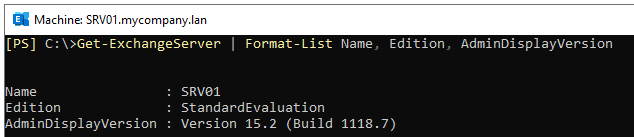
To avoid any issues during updates installation, you need to first identify the currently installed version of the Cumulative Updates on your server. For this, you can use the Get-ExchangeServer command as given below.

Get-ExchangeServer | Format-List Name, Edition, AdminDisplayVersion

A screenshot of a computer

Description automatically generated

This will give information about the version of the Exchange Server installed, along with the build number. On the Exchange Server updates download page, you can check the version you are downloading and confirm the installation matrix compatibility. Sometimes, you need to hop to a specific version before installing the latest one.

Before downloading the updates, it’s important to double-check with your Exchange Server consultant or supplier that you are installing the right update.

Read the release notes

It’s important to read the notes to know about any known issues, restrictions, or other information which is crucial for installing your update. There might be possible solutions to known issues while installing the update in question. Although it might be an administrative burden, you must check the release notes before installing the updates.

Installing the Updates

You should not rush through any installation or confirmation. All things must be documented and audited. This will help in troubleshooting if something goes wrong. Such documents help find out where the problem is. If you would involve your supplier or Microsoft support, then this will help them to resolve the problem easily.

Cumulative Updates take time to install, depending on the performance of the server. Ideally, you should restore a copy of the server in a sandbox environment and install the updates to test it if you have a single Exchange Server. If you have a Database Availability Group (DAG), you should first install the updates on the passive server. After a week of testing and ensuring that nothing was broken, you can go ahead and install them on the live server. 

Ensure Redundancy

When installing updates or changing the configuration of your environment, you should always have a failover plan. If you have a single instance of the server, you might consider testing the daily backup and performing a restore test to ensure that you can roll back if something happens.

If you have a Database Availability Group (DAG) with two or more servers, you need to make sure that the failover process is functioning properly and that the replication of databases is healthy.

Although it might not always be possible, it is highly recommended to take a backup before installing the updates or making any changes.

Contingency Plan

There is always a contingency plan before proceeding with the installation. In case the installation fails, there should be a set of instructions that need to be followed to recover from such a situation, such as:

  • Who to inform
  • Who to engage
  • What is to be done
  • Data loss parameters

What to do if something goes wrong during or after the update installation?

As mentioned, there are a lot of things that could go wrong when installing Cumulative Updates (CU), Security Updates (SU), or making any other changes to your infrastructure. If power is lost during the installation, storage is full, or an antivirus scan is executed, then these things can put the database in a dirty shutdown state and possibly corrupt the database or transaction logs. The Exchange Server will not boot or the Exchange Server services will not start due to corrupt installation files. In such situations, you can do the following:

1. Restore the Server from Backup

You can restore the server from backup. This will easily resolve the problem. However, if there were any changes during the installation, then these will be lost. 

2. Rebuild the Server and Recover the Data

The other option is to rebuild the Exchange Server. As all the configuration of the Exchange Server is in the Active Directory Schema, installing the server with the recovery mode and keeping the same IP Address and computer name will help recover the services.

To recover the data from corrupted databases or transaction logs, you can take the help of a specialized Exchange server recovery tool, like Stellar Repair for Exchange. This tool can open any version of an EDB file and in any state. It allows you to granularly export the data from the EDB file directly to a live mailbox database on your rebuilt Exchange Server while ensuring no data loss. The application can also export the EDB data to PST and other file formats.

Conclusion

Ensure a smooth Exchange Server update process involves thorough preparation, documentation, testing, and having contingency plans in place. Adhering to the best practices outlined in this article will significantly help you to avoid issues and minimize the impact of any problems that may arise during or after Cumulative Updates (CU) or Security Updates.

  1. Software Review: Stellar Repair for Exchange
  2. How to Create ISO Files from Discs – 3 Best Ways
  3. How to Remove Duplicate Lines in EmEditor (2023)
  4. How to configure cPanel and WHM Panel on your VPS
  5. How to Hide Tables in SQL Server Management Studio
  6. Microsoft’s Windows File Recovery tool recovers your lost data
  7. PDF Security – How To Keep Sensitive Data Secure in a PDF File
  8. MySQL Performance Tuning: Top 5 Tips for Blazing Fast Queries
  9. How to Craft Rich Data-Driven Infographics with Powered Template
  10. 5 Common Database Management Challenges & How to Solve Them
  11. Stellar Data Recovery Professional – Most user-friendly data recovery software

[ad_2]
Source link

Installing Microsoft Exchange Updates with Precision and Reliability

0
[ad_1]

Installing Microsoft Exchange Updates can be a challenging task, as it may lead to various issues in the process, such as compatibility problems, data loss, service disruptions, security vulnerabilities, update failures, dependency conflicts, or backup and recovery challenges.

There are several things that can go wrong when installing Cumulative Updates (CU) or Security Updates on your Exchange Server. You may encounter issues during and after installation or even the installation of updates may fail or stop.

The installation of updates could be hindered due to underlying issues with the operating system, damaged hardware, incorrect network configuration, conflict with third-party applications, corrupted updates, or human errors. In this article, we will be going through the things that you can do to prevent issues when installing updates and how to resolve issues (if occur) as fast as possible and with no data loss.

Prerequisites before Installation

To avoid any issues during updates installation, you need to first identify the currently installed version of the Cumulative Updates on your server. For this, you can use the Get-ExchangeServer command as given below.

Get-ExchangeServer | Format-List Name, Edition, AdminDisplayVersion

A screenshot of a computer

Description automatically generated

This will give information about the version of the Exchange Server installed, along with the build number. On the Exchange Server updates download page, you can check the version you are downloading and confirm the installation matrix compatibility. Sometimes, you need to hop to a specific version before installing the latest one.

Before downloading the updates, it’s important to double-check with your Exchange Server consultant or supplier that you are installing the right update.

Read the release notes

It’s important to read the notes to know about any known issues, restrictions, or other information which is crucial for installing your update. There might be possible solutions to known issues while installing the update in question. Although it might be an administrative burden, you must check the release notes before installing the updates.

Installing the Updates

You should not rush through any installation or confirmation. All things must be documented and audited. This will help in troubleshooting if something goes wrong. Such documents help find out where the problem is. If you would involve your supplier or Microsoft support, then this will help them to resolve the problem easily.

Cumulative Updates take time to install, depending on the performance of the server. Ideally, you should restore a copy of the server in a sandbox environment and install the updates to test it if you have a single Exchange Server. If you have a Database Availability Group (DAG), you should first install the updates on the passive server. After a week of testing and ensuring that nothing was broken, you can go ahead and install them on the live server. 

Ensure Redundancy

When installing updates or changing the configuration of your environment, you should always have a failover plan. If you have a single instance of the server, you might consider testing the daily backup and performing a restore test to ensure that you can roll back if something happens.

If you have a Database Availability Group (DAG) with two or more servers, you need to make sure that the failover process is functioning properly and that the replication of databases is healthy.

Although it might not always be possible, it is highly recommended to take a backup before installing the updates or making any changes.

Contingency Plan

There is always a contingency plan before proceeding with the installation. In case the installation fails, there should be a set of instructions that need to be followed to recover from such a situation, such as:

  • Who to inform
  • Who to engage
  • What is to be done
  • Data loss parameters

What to do if something goes wrong during or after the update installation?

As mentioned, there are a lot of things that could go wrong when installing Cumulative Updates (CU), Security Updates (SU), or making any other changes to your infrastructure. If power is lost during the installation, storage is full, or an antivirus scan is executed, then these things can put the database in a dirty shutdown state and possibly corrupt the database or transaction logs. The Exchange Server will not boot or the Exchange Server services will not start due to corrupt installation files. In such situations, you can do the following:

1. Restore the Server from Backup

You can restore the server from backup. This will easily resolve the problem. However, if there were any changes during the installation, then these will be lost. 

2. Rebuild the Server and Recover the Data

The other option is to rebuild the Exchange Server. As all the configuration of the Exchange Server is in the Active Directory Schema, installing the server with the recovery mode and keeping the same IP Address and computer name will help recover the services.

To recover the data from corrupted databases or transaction logs, you can take the help of a specialized Exchange server recovery tool, like Stellar Repair for Exchange. This tool can open any version of an EDB file and in any state. It allows you to granularly export the data from the EDB file directly to a live mailbox database on your rebuilt Exchange Server while ensuring no data loss. The application can also export the EDB data to PST and other file formats.

Conclusion

Ensure a smooth Exchange Server update process involves thorough preparation, documentation, testing, and having contingency plans in place. Adhering to the best practices outlined in this article will significantly help you to avoid issues and minimize the impact of any problems that may arise during or after Cumulative Updates (CU) or Security Updates.

  1. Software Review: Stellar Repair for Exchange
  2. How to Create ISO Files from Discs – 3 Best Ways
  3. How to Remove Duplicate Lines in EmEditor (2023)
  4. How to configure cPanel and WHM Panel on your VPS
  5. How to Hide Tables in SQL Server Management Studio
  6. Microsoft’s Windows File Recovery tool recovers your lost data
  7. PDF Security – How To Keep Sensitive Data Secure in a PDF File
  8. MySQL Performance Tuning: Top 5 Tips for Blazing Fast Queries
  9. How to Craft Rich Data-Driven Infographics with Powered Template
  10. 5 Common Database Management Challenges & How to Solve Them
  11. Stellar Data Recovery Professional – Most user-friendly data recovery software

[ad_2]
Source link

Google Discover now shows you the air quality in your area

0
[ad_1]

The AQI (air quality index) of our area is often overlooked. Naturally, we want to make sure that the air in our area is breathable, so Google is giving us another way to check on that. According to a new report, the Google Discover feed will show you the air quality in your area.

Google already offers other ways for you to view the AQI in your area. For starters, if you own a Pixel phone, then you can access that information via your At a Glance widget. This is the widget on the top left of your home screen. You can set it to show your AQI from the settings.

Also, you can see your AQI on Google Maps. It’s one of the map layers that show you different views of the map. If you want to know the air quality in your area, you should look at those methods.

The Google Discover feed now shows the air quality in your area

You can access the Google Discover feed from the Google app or by swiping to the right on your phone’s home screen (that is if you have the feature enabled). You’ll be greeted with a feed of the latest headlines on news topics you’re interested in. Above those, you’ll see some tiles showing you the current weather in your area, sports, and finances.

Well, Google is now rolling out the AQI as part of an update that’s coming out. The tiles are on a carousel, so you’ll have to swipe to see the AQI. It will show you the number along with a dot. The dot next to the number will correspond to how breathable the air is. A green dot means that the air is safe to breathe and a red one means that it’s unsafe. A yellow dot is right in the middle.

If you don’t want to see the AQI, tap on the edit button on the far right of the carousel. Just uncheck it if you don’t want to see it, and that goes for the weather, sports, and finances.


[ad_2]
Source link

Gmail on larger screens now opens links in split-screen mode

0
[ad_1]

Google is trickling more tweaks and updates to its apps to make them better on larger screens. The next update comes to the Gmail app, and it will make using it easier if you need to open a link. According to a new report, Gmail on larger-screen devices now opens links in split-screen mode.

Android is becoming a much friendlier platform for tablets as time goes on. First-party apps like Gmail, Docs, Calendar, and more have been changing in order to work better on tablets and foldables. This is great, seeing as Google now has a foldable and a tablet on the market. More changes are on the way, so you should expect to see more stories like this.

Gmail on larger screens will open links in split-screen mode

This is a useful feature to come to the app. The trick to multitasking is being able to access more than one thing at a time. Previously, when you would tap on a link it Gmail, the browser would fill the screen. That’s not a bad thing, but if you’re focused on multitasking, then you probably won’t want that.

Rather than filling the screen, Gmail will open the link in split-screen mode on foldables and tablets. This way, you’ll still have access to the original email. There could still be information on the email that you need access to. It’s better that you have access to both.

When you tap on the link, you’ll see a Chrome tab open on the right side of the screen. Gmail will condense to the left side of the screen. When that happens, you’ll see Gmail change to a more familiar mobile view with the contents of the email filling the left column. If you want to access the inbox, tap on the arrow in the top left corner of the screen.

Gmail split screen links

This is currently rolling out, so you should be able to see it now. If not, then you might want to wait a bit for it to make it to you. Make sure that the Gmail app is fully updated.


[ad_2]
Source link

Google wrote a 400-word editorial on the Play Store about RCS

0
[ad_1]

“RCS is the modern industry standard for messaging, and it’s already been adopted by most of the industry.” Brian Rakowski said this during last year’s Pixel event, and Google has been echoing this sentiment. The company is not done pushing the benefits of RCS (Rich Communication Services), as you can imagine. In fact, Google wrote a whole article on the Google Play Store touting the benefits of RCS.

The quote above isn’t exaggerating, RCS is the latest industry standard of messaging. It offers benefits such as end-to-end encryption, read receipts, group chats, and much more. It’s a replacement for the older SMS standard, which is decades old. So, it makes sense that Google and many other companies are pushing for this to be the standard.

However, not all companies are keen on hopping to RCS. Apple, the smartphone king, still insists on using the older standard, and it makes things harder for everyone else. Apple, while it’s pretty much stepping on everyone’s toes, has the status and size to remain stubborn. It has a massive user base that supports the stay on SMS, and they all think that it’s because of the Blue Bubble vs. Green Bubble debate.

Google wrote a whole article on the Play Store talking about the benefits of RCS

Google is making the Play Store more than a place to pick up your next mobile app. You can find apps for Chromebooks, manage your payment methods/subscriptions, and more. Well, what if we told you that you can read articles on the platform, as well?

As per the report, Google wrote a whole article explaining why RCS is the way of the future. You’ll only see this if you’re on the web version of the Play Store. When you load up the page and go to the Apps tab, you’ll see a carousel of large tiles on the top of the screen. Click on the arrow to the right of the carousel to scroll through it.

The third tile should read “7 Ways RCS makes Messages by Google even better”.  When you click on it, you’ll see a short editorial about how RCS is the best thing since sliced bread. At the bottom of the post, you’ll see the app page for the Google Messages app where you can download it.

The post lists some legitimate reasons as to why RCS is a great technology, so feel free to read it.


[ad_2]
Source link

Facebook and Instagram are testing themed icons for their Android apps

0
[ad_1]
The most recent Alpha and Beta versions of the Facebook and Instagram apps on Android now support Android’s themed icons. This supports recent rumors that Meta was working on finally adding this functionality to its apps’ icons, years after it became available throughout the operating system.

Automatic theming, including themed icons, were introduced to Android with version 12 of the operating system. This feature extracted the dominant colors of your wallpaper and applied them throughout the interface, making for a more minimal and cohesive look.

Fortunately, this is now changing as both the Instagram and Facebook icons are now supporting automatic theming on Android in their Beta and Alpha apps, meaning that this will likely be rolled out to their stable versions soon. This was spotted by users currently using these versions and reported by Mishaal Rahman on X.
This is available right now in versions 307.0.0.0.42 (beta) of Instagram and 439.0.0.0.30 (alpha) of Facebook and signals a turning point to how Meta handles the implementation of new Android features. This was evident more recently by the limited rollout of a new Instagram layout for tablets, which can be tested now using a larger screen device, such as the Google Pixel Fold on Android 14 QPR1 Beta.
For those that enjoy having matching icons on their Android’s home screen, support for a matching themed icon for both of these applications could finally stop the issue of having to hide them inside a folder or pushing them to a secondary stream (if not hide them altogether). Hopefully, this feature makes it to the stable channels sooner rather than later, perhaps just in time for the next Android security update or the December Pixel Feature Drop.

[ad_2]
Source link

What is the Dark Web, Search Engines, and What Not to Do on the Dark Web

0
[ad_1]

In this article, we will delve deeper into what is the dark web, exploring its definition, the top dark web search engines, and, crucially, the key precautions to observe when venturing into this hidden side of the Internet.

In the hidden part of the internet, there’s a mysterious place called the “Dark Web.” It’s like a secret world where people go to find things that are not allowed on the regular internet but it is an ideal place for whistleblowers, journalists, researchers, dissidents, etc., to protect their privacy online.

In this article, we’ll try to explain what is the Dark Web, how you can get there, and the things you should and shouldn’t do if you decide to check it out.

What Is the Dark Web?

The Dark Web, often mistakenly used interchangeably with the “Deep Web,” constitutes a small but significant portion of the vast internet. Unlike the Surface Web, which encompasses websites indexed by search engines, the Deep Web includes all web pages that aren’t indexed, such as your personal emails and private databases. The Dark Web, however, goes further into obscurity.

It operates on anonymous networks, most notably Tor (The Onion Router), which reroutes internet traffic through multiple servers, making it exceedingly difficult to trace. This inherent anonymity has led to the proliferation of both legal and illicit activities within this clandestine world.

How to Access the Dark Web

Accessing the Dark Web is not as straightforward as using mainstream web browsers like Chrome or Firefox. To begin your journey, follow these steps:

  1. Download and Install Tor: Visit the official Tor Project website to download and install the Tor Browser, specifically designed for anonymous web browsing.
  2. Stay Updated: Keep the Tor Browser updated to ensure you have the latest security patches.
  3. Use a VPN (Optional): For an extra layer of anonymity, consider using a virtual private network (VPN) alongside Tor.
  4. Stay Informed: Familiarize yourself with the intricacies of Tor and its safety measures to minimize risks.

You can also use the Brave browser to access the Dark Web and Onion domains because the browser has its own Tor Onion service accessible through the Tor gateway.

1. Ahmia.fi

Ahmia.fi, a search engine tailored for the “dark web” or “dark net,” grants access to the hidden layers of the internet, exclusively reachable via specific software like the Tor browser. Ahmia stands among the select few dark web search engines that make this secretive online domain more accessible.

Notably, Ahmia maintains a strict policy against “abuse material,” distinguishing it from many other dark web search engines that also index content related to child sexual abuse. Ahmia is available on the surface web and supports searches on the i2p network as well. You can visit Ahmia’s .Onion domain here. 

Deep Search, an open-source dark web search engine, is dedicated to indexing and searching the onionspace, the concealed services section of the Tor network. Users have lauded Deep Search for providing precise and valuable results, a notable departure from the spammy links often encountered on other platforms.

Additionally, Deep Search offers a comprehensive list of marketplaces, exchanges, and websites involved in fraudulent activities. To explore Deep Search, you can access its Onion domain here.

3. Haystak

Haystak, designed for the Tor network, is a dark web search engine boasting an impressive index of over 1.5 billion pages, encompassing more than 260,000 websites. This makes Haystak a valuable resource on this list.

Haystak also offers a paid version with added features, including the ability to search using regular expressions, access now-defunct onion sites, and utilize their API. For those interested, Haystak’s Onion link can be found here.

4. The Hidden Wiki

The Hidden Wiki serves as a dark web directory exclusively accessible through the Tor network. This site contains links to a variety of different websites, making it a valuable resource for those seeking to navigate the dark web safely and conveniently. Additionally, there is a surface web version available. You can visit The Hidden Wiki by following its Onion link here.

5. Torch

Torch, a long-standing dark web search engine in operation since 1996, performs the essential task of crawling addresses and indexing their content, making it searchable for users. However, it falls short in terms of search results accuracy, as observed from personal experiences. Despite this, it remains a fast and useful tool. You can explore Torch through its .Onion link here.

What Not to Do on the Dark Web

The main purpose of the Dark Web was not to serve a specific single intent. Instead, it evolved as a hidden part of the internet where users could have increased privacy and anonymity. It was initially developed by the U.S. Naval Research Laboratory for secure communications.

Over time, it has been used for various purposes, including protecting free speech, circumventing censorship, and enabling confidential and anonymous communication. However, it has also gained notoriety for being a space where illegal activities can occur due to the high degree of anonymity it offers.

Therefore, it’s important to note that while the Dark Web has legitimate uses, it has also become associated with illegal trade, hacking, and other illicit activities including the following:

  1. Engage in Illegal Activities: The Dark Web is infamous for hosting illegal marketplaces where you can find everything from drugs and stolen data to counterfeit passports. Engaging in such activities is not only unethical but also exposes you to legal repercussions.
  2. Share Personal Information: Protect your identity on the Dark Web. Do not disclose your real name, location, or any personally identifiable information.
  3. Trust Blindly: The Dark Web is rife with scams and deceit. Always exercise caution and scepticism when interacting with others.
  4. Download Files Recklessly: Downloading files from the Dark Web can be risky. Only obtain content from sources you trust, and use strong antivirus software to scan downloads.
  5. Venture Unprepared: Before exploring the Dark Web, educate yourself about the risks and equip your device with security measures.
  6. Participate in cybercrime: Participating in cybercrime or black hat activities on the Dark Web is both illegal and unethical, carrying serious consequences. Black Hat Hackers engage in activities that compromise computer systems, steal sensitive data, and cause harm to individuals, organizations, and even governments. These actions violate not only the law but also principles of digital ethics. Engaging in such activities can lead to severe legal repercussions, including imprisonment and hefty fines, not to mention damage to one’s reputation.
  7. Keeping Java enabled: Enabling Java in the Tor Browser is strongly discouraged for several reasons, including security risks, fingerprinting, and reduced anonymity. As Java is known to have security vulnerabilities, it can be exploited by cybercriminals to potentially steal your cryptocurrency funds and by state-sponsored hackers to conduct surveillance on your activities.
  8. Using Google as a search engine: Google utilizes various tools, such as Google Analytics, to construct comprehensive profiles of its users. While this approach contributes to improving search results and the overall user experience, it necessitates the collection of substantial personal information, including names and locations.
  9. STOP and NEVER Distribute Child Sexual Abuse Material (CSAM): According to a recent report, Dark Web paedophiles are already using Open-Source AI to generate CSAM. However, engaging in malicious activities, such as distributing Child Sexual Abuse Material (CSAM), is abhorrent and illegal, whether on the clearnet (the visible internet) or the Dark Web, for a multitude of compelling reasons:
  • Criminal Offense: The distribution and possession of CSAM is a serious criminal offence, and those involved can face severe legal consequences, including lengthy prison sentences. It’s an indefensible crime that causes immense harm to children.
  • Victim Exploitation: CSAM involves the exploitation and abuse of children. Sharing such material perpetuates the suffering of the victims, who are often subjected to horrific abuse and harm.
  • Ethical Repugnance: Engaging in CSAM activities is fundamentally unethical and morally reprehensible. It violates the rights and well-being of innocent children, causing irreparable harm.
  • Destruction of Lives: Those who create, distribute, or consume CSAM contribute to the destruction of young lives and their long-term psychological and emotional trauma.
  • Negative Consequences for the Internet: Engaging in such activities not only ruins lives but also leads to stricter regulations and monitoring of online activities. This compromises the privacy and freedoms of all internet users.
  • Anonymity Doesn’t Guarantee Immunity: While the Dark Web offers a higher degree of anonymity, it is not foolproof. Law enforcement agencies have successfully tracked down and apprehended individuals involved in CSAM activities on the Dark Web.
  1. What is an OSINT Tool – Best OSINT Tools 2023
  2. DarkBERT: Enhancing Cybersecurity Efforts on the Dark Web
  3. Unreleased Music Stolen and Sold on Dark Web: Hacker Fined
  4. Russian Dark Net Markets Dominate the Global Illicit Drug Trade
  5. 10 Top DDoS Attack Protection and Mitigation Companies in 2023
[ad_2]
Source link