Another Chrome Zero-Day Under Attack Received A Fix

0
[ad_1]

Heads up, Chrome users! Google has just released a major security update for its Chrome browser as it patched an actively exploited zero-day. All Chrome desktop users must rush to update their systems to avoid potential threats.

Google Patched Actively Exploited Chrome Zero-Day Flaw

According to the recent security release update, Google has rolled out a major update for its Chrome for Desktop browser, patching several vulnerabilities. But this update is crucial for Chrome users as the tech giant has patched a Chrome zero-day flaw actively exploited in the wild.

As stated, the update includes ten security fixes, addressing the issues across various browser components. Three of these ten vulnerabilities caught the attention of external researchers, who reported the matter to Google for patches. Whereas the remaining seven appeared on the radar of Google’s internal security team.

The release update for Chrome 117.0.5938.132 for Windows, Mac, and Linux lists the three vulnerabilities reported by external researchers, which include the following.

  • CVE-2023-5217: a high-severity heap buffer overflow in vp8 encoding in libvpx. This vulnerability gained traction when Google’s Threat Analysis Group (TAG) and The Citizen Lab discovered active exploitation of this flaw, alongside iOS vulnerabilities, to install the Predator spyware. Apple also patched the respective iOS zero-days with the recently released iOS 17.0.1.
  • CVE-2023-5186: another high-severity vulnerability reported by a researcher with alias “pwn2car.” Google described this vulnerability as a use after free affecting Passwords. The tech giant is yet to decide the bug bounty for this report.
  • CVE-2023-5187: A high-severity use after free vulnerability existed in Chrome Extensions, which caught the attention of the researcher Thomas Orlita. The firm awarded the researcher a $2000 bounty for this bug report.

Continuing its practice to keep the technical details of the vulnerabilities hidden until a maximum of users patch their devices, Google hasn’t shared further details about these flaws. Nonetheless, it has rolled out the Chrome 117.0.5938.132 update to the respective users to avoid risks.

The present update simply adds to the growing list of Chrome vulnerabilities patched this year.

Let us know your thoughts in the comments.


[ad_2]
Source link
Google Pixel 8 pre-order freebies won’t be limited to the US

0
[ad_1]

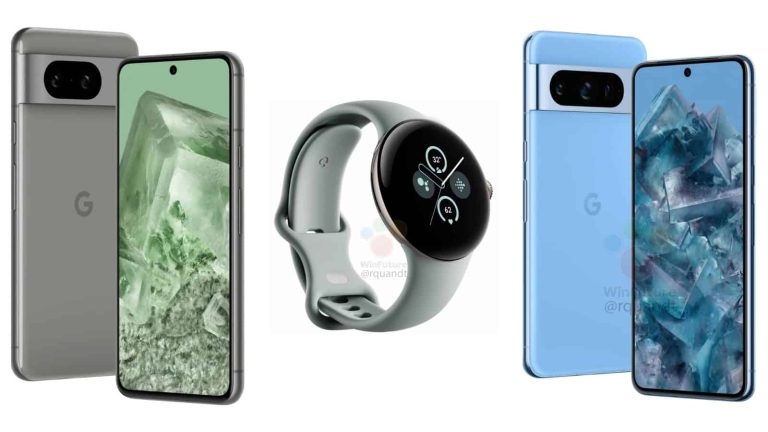
As many of you already know, the Google Pixel 8 series will come with some pre-order gifts from Google. Well, initial reports shared that info in regards to the US market, of course. Well, it seems like those Pixel 8 pre-order freebies won’t be limited to the US market.

The Google Pixel 8 & Pixel 8 Pro pre-order freebies won’t be limited to the US

According to a report from Ishan Agarwal, a well-known tipster, some other markets will get them too. He was rather specific in his X post, he said that the Pixel 8 Pro pre-order in some European countries will include the Pixel Watch 2.

That being said, do note that the Pixel 8 is reported to come with a free pair of Pixel Buds Pro in the US, if you pre-order it. The Pixel 8 Pro, on the other hand, will include the Pixel Watch 2.

Having said that, we presume that the Pixel 8 pre-order in some European countries will include the Pixel Buds Pro. The tipster did not list what countries he’s talking about, but it’s possible that offer is coming to all the countries where the phones will be officially available in.

So, we’re likely looking at the UK, Germany, Italy, Spain, France, and a handful of other countries. We’ll have to wait for the launch in order to confirm that, though, of course.

The phones will launch on October 4

Speaking of which, the Pixel 8 and Pixel 8 Pro will become official on October 4. The aforementioned Pixel Watch 2 will launch alongside them, while the Pixel Buds Pro have been on the market for quite some time now.

The Pixel 8 series has been leaking for a long time now, and a ton of info surfaced already. We already know what the devices will look like, many of their specs, and more. The Pixel 8 and Pixel 8 Pro unboxings surfaced recently, and did Google’s official cases.


[ad_2]
Source link

Two next-gen Snapdragon VR chips have been unveiled

0
[ad_1]

The new Snapdragon next-gen VR chips, the XR2 Gen 2 and the AR1 Gen 1 are now official. These chips will power the next generation of VR products that will hit the market soon. Some said VR products include headsets and smart glasses from various tech companies around the world.

Meta collaborated with Qualcomm to launch these chips, making them more suitable for VR products. This collaboration is remarkable because Meta is one of the leaders in the VR industry and already has a ton of VR products available and some in the pipeline. Already, the more powerful Snapdragon XR2 Gen 2 processor is in use on the new Meta Quest 3 VR headset.

As for the less powerful AR1 Gen 1 processor, it’ll find its way to smaller VR products that will launch in the future. An example of a VR product that already uses this new processor is the Ray-Ban Meta smart glasses. Here are the technical specifications of these new Snapdragon next-gen VR chips that are making a wave.

Specifications of the new Snapdragon next-gen VR chips that will be in use on VR products

Let’s start with the new XR2 Gen 2 processor that is built for XR devices. This new processor comes with a single-chip architecture that helps improve user experience on XR devices. It helps to improve battery capacity and graphics quality and brings faster response time for improvements to the user experience.

With Qualcomm adding AI capabilities to their processor, the new XR2 Gen 2 also features some on-device AI technology. The new chip also improves upon the video-see-through quality on XR headsets, helping users stay in touch with their environment. It also packs a faster GPU in comparison with its predecessor, and this helps bump up performance.

As for the new AR1 Gen 1 processor, it is built for usage on smart eyeglasses. It brings Dual ISPs, which help to improve picture (12MP) and video (6MP) quality. There is also an upgrade to the binocular display quality, which is important for reading notifications.

Just like on the XR2 Gen 2 processor, the new AR1 Gen 1 processor also comes with next-gen AI capabilities. Qualcomm also made improvements to the audio capabilities of this new AR processor. Battery life here is also more efficient and better designed to suit the smaller AR glasses and eyewear.

If you hope to try out these new processors in real life, then you can consider getting any of the new Meta VR products. In the coming months, more XR brands will launch more products that will make use of these two new Snapdragon next-gen VR chips. This marks the start of a new era for the VR industry and might attract even more competitors.


[ad_2]
Source link

Spotify rolls out new podcast-related features and improvements

0
[ad_1]

Every major music streaming service is doubling down on podcasts, a sign that more and more people are finding podcasts entertaining and worth listening to on a regular basis.

Over the weekend, Spotify announced a couple of Podcast-related features that are expected to make the experience more enjoyable. These features are already rolling out to Free and Premium users globally, although it will probably take a few days for everyone to get them.

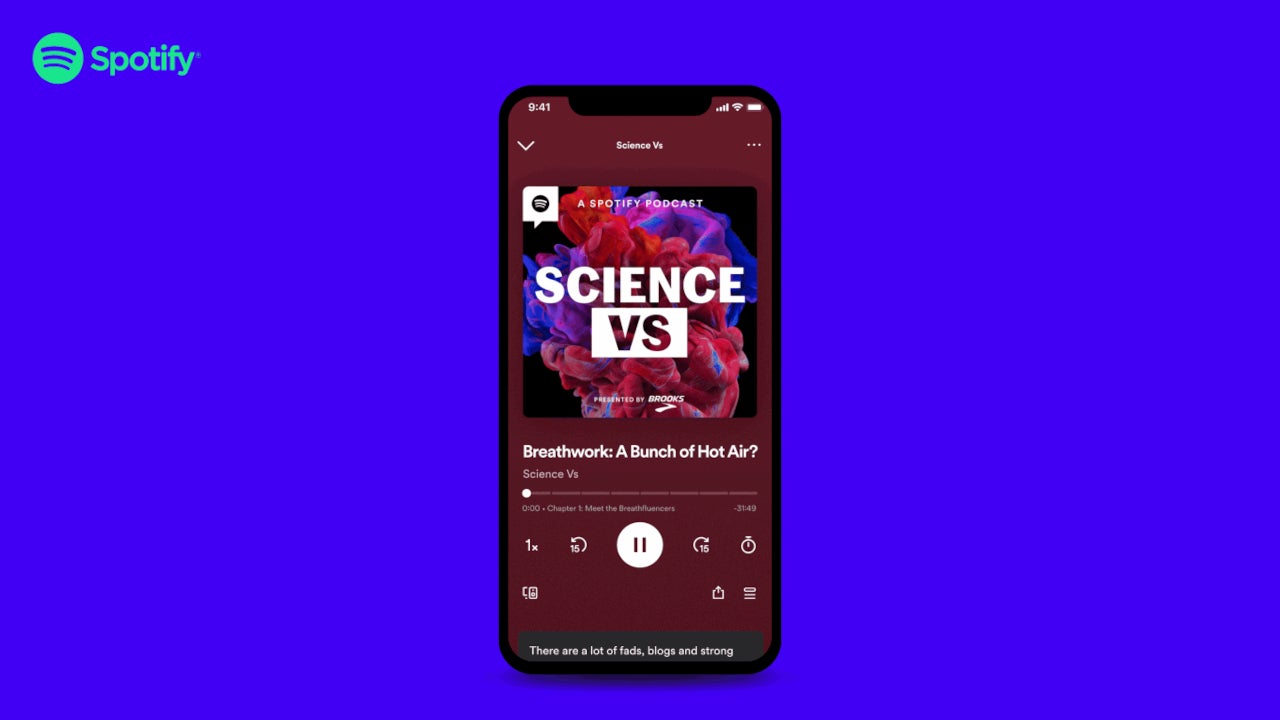
First and foremost, Spotify is adding auto-generated and time-synced transcripts to podcasts. It will allow users to read along with an episode, thus making the transcripts more visually and textually accessible.

While listening to a podcast on Spotify, users can now scroll down the Now Playing View to find the transcript, then tap the card to follow along on full screen as you listen to the episode.

Not every podcast episode will have transcripts available at launch, but Spotify says that it will roll out transcripts to millions of episodes in the coming weeks. Also, the US-based company promised to further add improvements to the feature, including ways to add media to transcripts.

In addition to auto-generated and time-synced transcripts, Spotify announced that mobile users all over the world can now find the full list of Podcast Chapters by scrolling down the Now Playing View. It will make it easier to choose what to listen to since this will provide them with more info about every episode.

Finally, the Podcast Show pages have been updated with a new “About” tab where Spotify users can find descriptions, images, and episode recommendations from creators. On top of that, Spotify users will get recommendations for other shows in the “More Like This” tab.


[ad_2]
Source link

Cisco Patches IOS software Zero-day Exploited in Attacks

0
[ad_1]

Cisco has issued fixes to address a vulnerability in the GET VPN feature of IOS and IOS XE software that has been exploited in attacks.

A remote attacker who has administrative access to a group member or a key server can exploit this vulnerability to run arbitrary code or bring down an affected device.

Cisco GET VPN is a set of features required for secure IP multicast group communication or unicast traffic over a private WAN that originates or flows through a Cisco IOS device. 

GET VPN integrates the group key management protocol with IPsec encryption to offer users an efficient way to secure IP multicast or unicast communication.

Document
FREE Demo

Implementing AI-Powered Email security solutions “Trustifi” can secure your business from today’s most dangerous email threats, such as Email Tracking, Blocking, Modifying, Phishing, Account Take Over, Business Email Compromise, Malware & Ransomware

Details of the Vulnerability

With a CVSS base score of 6.6, the Out-of-Bounds Write Vulnerability reported by Cisco is tracked as CVE-2023-20109 and has a ‘medium’ severity range.

“This vulnerability is due to insufficient validation of attributes in the Group Domain of Interpretation (GDOI) and G-IKEv2 protocols of the GET VPN feature”, Cisco said in its advisory.

A hacker could take advantage of this vulnerability by compromising an installed key server or changing a group member’s settings to point to a key server under the attacker’s control.

If the exploit is successful, the attacker may be able to run arbitrary code and take complete control of the target system, or they may force the target system to reload and create a DoS.

Affected Products

If a Cisco product had the GDOI or G-IKEv2 protocol enabled and was running a vulnerable version of the Cisco IOS software or Cisco IOS XE software, it is considered vulnerable.

Products Not Vulnerable

  •     IOS XR Software
  •     Meraki products
  •     NX-OS Software

This vulnerability, according to Cisco, can only be exploited in one of two ways:

  • The attacker compromises the existing key server and gains access to the GDOI or G-IKEv2 packets sent by the key server to the group member.
  • The attacker creates and installs their own key server and then reconfigures the group member to interact with the attacker-controlled key server.

Mitigation Measures

As stated in the advisory, Cisco recommends that affected users apply software updates as early as possible.

Cisco confirmed that there are no workarounds that address this vulnerability.

Protect yourself from vulnerabilities using Patch Manager Plus to quickly patch over 850 third-party applications. Take advantage of the free trial to ensure 100% security.


[ad_2]
Source link

Google Pixel 8 series unboxed ahead of time: Video & images

0
[ad_1]

The Google Pixel 8 and Pixel 8 Pro got unboxed ahead of time. This is not exactly surprising, as a ton of leaks have already surfaced, and it basically happens every year. That being said, we’re talking about two separate leaks here

The Google Pixel 8 gets unboxed ahead of time, in a video format

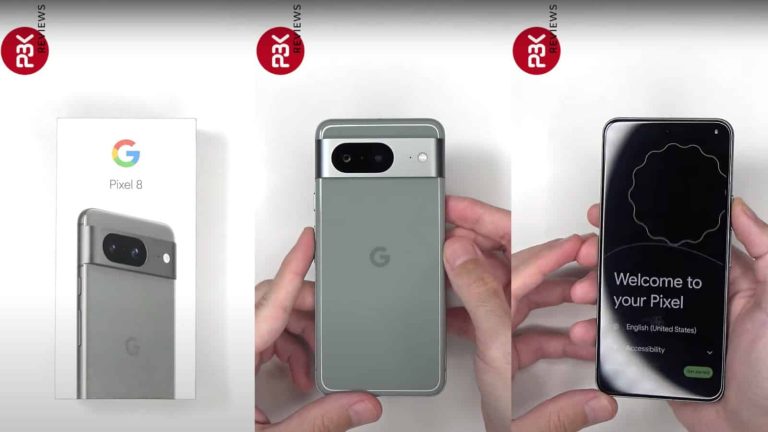
The first leak shows us the Pixel 8. The device got unboxed in a video format, and that was shared by PBKreviews. That YouTube channel is well-known for providing smartphone teardowns, first and foremost.

This is a 26-second video, and you can check it out below this paragraph. You can see the phone itself, and the contents of the box. The Quick Switch adapter is included in the box, and so is a USB-C to USB-C cable. A charger is not, of course.

The box also confirms that the phone will feature a 6.2-inch display, and this is a 128GB storage variant of it. Chances are we’ll get at least one more variant, a 256GB storage model. But we’ll have to wait and see.

Now, the design of the phone is exactly what we expected based on leaks. It’s similar to the Pixel 7, but the phone is smaller this time around. This seems to be the ‘Hazel’ color variant of the phone.

The Pixel 8 Pro also got the unboxing treatment, but that was shared via several images

The Pixel 8 Pro also got unboxed, but not in a video format. If you check out the gallery below this paragraph, you’ll see a bunch of images showing the Pixel 8 Pro unboxing. These images have been shared via Facebook, by Vật Vờ Studio.

These images show us the ‘Porcelain’ color variant of the phone, the one with a silver frame, and a white-ish backplate. The contents of the box are identical to what we’ve seen for the Pixel 8.

You can clearly see how much bigger the Pixel 8 Pro is here. It will ship with a 6.7-inch display, so the size difference between these two models will be bigger than between the Pixel 7 and Pixel 7 Pro.


[ad_2]
Source link

iPhone 15 & 15 Plus ace durability tests, unlike iPhone 15 Pro Max

0
[ad_1]

JerryRigEverything managed to get his hands on the iPhone 15 lineup, and we all know what that means. A couple of days ago, he tested the iPhone 15 Pro and Pro Max. Unfortunately, the iPhone 15 Pro Max back glass shattered during the bend test, which managed to surprise Zack. It never happens. Well… spoiler alert… the iPhone 15 & 15 Plus managed to ace the durability tests.

The iPhone 15 & iPhone 15 Plus did great in JerryRigEverything’s durability tests

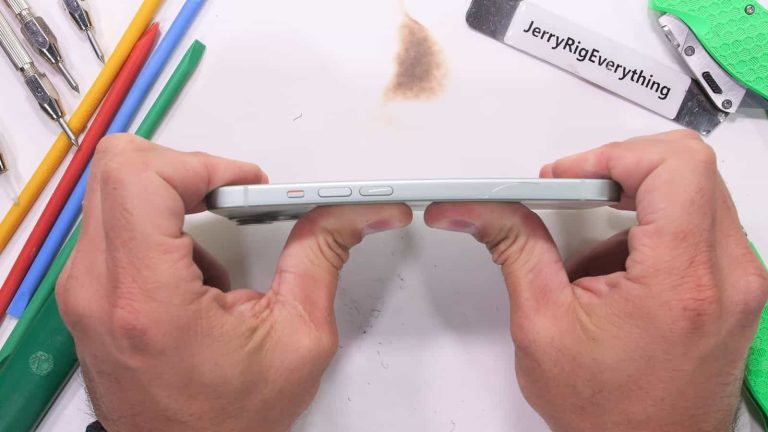
Neither of the two vanilla iPhone 15 models broke during the bend test, not at all. The glass remained intact, as did the phones themselves. Let’s take it one step at a time. Zack from JerryRigEverything released an 11-minute video to detail all this. That video is embedded below the article.

He essentially performed most of his tests on the iPhone 15, as the two phones are the same except for the size. The bend test, however, he conducted on both phones, just to check out whether the larger one would break, like the iPhone 15 Pro Max did.

The first test was done using picks to scratch the display, as per usual. The iPhone 15 series displays are protected by the Ceramic Shield glass, as were on the last generation models. Scratches were barely visible after using the level six pick, and not at all after wiping the glass. That seemingly makes this protection more scratch resistant than what Corning offers, at least based on this.

The vanilla iPhone 15 models have a frame made out of aluminum

The phone’s frame is made out of aluminum, as are the phone’s buttons. He also showed us that the glass sits on both the front and the back of the phone, and that the cameras are well protected. As per usual, Zack also took the lighter to heat up the display, just for fun, more than anything. This did show us that an OLED display is used, though, as we all know.

Now, for the fun part, the bend test. The iPhone 15 and iPhone 15 Plus barely flexed a bit when he applied pressure from the front and the back. They also reversed to their original position when he stopped. In other words, they did much better than the iPhone 15 Pro Max.

You can check out both videos Zack shared below. The first shows the vanilla iPhone 15 models, while the second tests the iPhone 15 Pro models.


[ad_2]
Source link

Progress S/W Warns of Critical Vulnerability in WS_FTP Server

0
[ad_1]

Multiple vulnerabilities have been discovered in Progress’s WS_FTP, which include .NET deserialization, directory traversal, reflected cross-site scripting (XSS), SQL injection, stored cross-site scripting, cross-site request forgery, and unauthenticated user enumeration vulnerability.

These vulnerabilities’ severities range from 5.3 (Medium) to 10.0 (Critical). However, Progress has released patches for fixing these vulnerabilities in the WS_FTP server. 

Moreover, the MOVEit file transfer application, which was one of the most exploited applications by threat actors, is also owned by Progress.

Document
FREE Demo

Implementing AI-Powered Email security solutions “Trustifi” can secure your business from today’s most dangerous email threats, such as Email Tracking, Blocking, Modifying, Phishing, Account Take Over, Business Email Compromise, Malware & Ransomware

Technical Analysis

The most critical vulnerabilities were CVE-2023-40044 and CVE-2023-42657. CVE-2023-40044 was a .NET deserialization vulnerability that an attacker could exploit to execute remote commands on the WS_FTP Server operating system. This vulnerability had a severity of 10.0 (Critical).

CVE-2023-42657 was associated with a directory traversal vulnerability which threat actors can use to perform file operations like delete, rename, rmdir, mkdir on files and folders outside of the WS_FTP folder path.

High Severity Vulnerabilities

In addition to this, three high-severity vulnerabilities were discovered on the WS_FTP server, which were CVE-2023-40045, CVE-2023-40046, and CVE-2023-40047. CVE-2023-40045 and CVE-2023-40047 had a severity score of 8.3 (High) and were related to reflected cross-site scripting and stored reflected cross-site scripting.

CVE-2023-40046 was linked with a SQL injection vulnerability that threat actors can use for gathering information about the structure and contents of the SQL database. This vulnerability can also be used to execute SQL for altering or deleting the database elements. 

Medium Severity Vulnerabilities

As for the Medium severity vulnerabilities, CVE-2023-40048 (CSRF – 6.8 (Medium)), CVE-2023-27665 (Reflected XSS – 6.1 (Medium)) and CVE-2023-40049 (Unauthenticated user enumeration) were discovered.

A security advisory has been published by Progress, which provides detailed information about these vulnerabilities. 

Fixed in Version

Users of the Progress WS_FTP server are recommended to upgrade to the latest version, 8.8.2 in order to fix these vulnerabilities from getting exploited by threat actors.

Protect yourself from vulnerabilities using Patch Manager Plus to quickly patch over 850 third-party applications. Take advantage of the free trial to ensure 100% security.


[ad_2]
Source link

Motorola blocks phones sold through unauthorized channels in one country

0
[ad_1]

Motorola is dealing with an unusual problem in Mexico. Unauthorized sales of its phones in the country have grown fivefold over the past three years. Despite repeated warnings, this practice hasn’t stopped. It has now decided to take strict action and disable those phones entirely, limiting their usage to making emergency calls only.

Motorola disables phones purchased through unauthorized channels in Mexico

The devices in question are illegally imported to Mexico from foreign territories. They don’t have regulatory approval for sale and use in the country. Motorola says this poses a security risk to the user of such phones as they don’t comply with all domestic standards and lack warranty policies. These phones may also fail to work properly on Mexican wireless networks due to the lack of official support.

As reported by Xataka, Motorola has been warning Mexicans against buying or using these “irregular” phones since at least May this year. It started sending a push notification saying “Your device is irregular because it does not comply with the regulations in Mexico.” However, unauthorized sales of Motorola phones continued in the country.  Consumers seemingly ignored the company’s warning.

The Lenovo-owned firm has now had enough. It is disabling the devices purchased through those channels. Unauthorized Motorola phones activated on or after July 27, 2023, in Mexico will stop working a few days later. The company will show two warnings to users during this period. “Your device will be disabled in 10 days for not complying with regulations in Mexico,” the first warning notification reads.

This warning message shows up immediately after the setup process and comes with a huge banner that will certainly draw your attention. Users can tap on it to learn more about the matter. Motorola will follow up with the same warning ten days later, with it noting that there’s only one more day left before the phone is disabled. The device will no longer be operable from the next day.

“The user will not be able to use the device, consequently, they will not have access to its files, functions or applications, since there will be a disabling screen and they will only be able to access Emergency Calls,” Motorola explains in a support page. The page also provides more information on the risks of using such phones and the benefits of buying approved devices from authorized channels.

Affected users will get a 30 percent discount on approved Motorola phones

It’s worth noting that Motorola won’t disable phones purchased through authorized channels on foreign land but used in Mexico. Irregular phones purchased within the country and activated before July 27, 2023, will also continue to work as before. This is despite those devices lacking regulatory approval. The company will show a usage warning but won’t block access to the device.

Unsurprisingly, Mexicans aren’t happy about Motorola disabling phones with similar limitations but purchased within the country. They don’t have any choice, though. If they want to buy an approved Motorola phone, the company is giving them a 30 percent discount. Users will need to validate the IMEI of the irregular device to receive the discount coupon that will be valid for 30 days. The company won’t take the disabled phone.

You can find more information about the process of obtaining the discount coupon on this support page. Devices approved for sale and use in Mexico will feature a “NOM” (Norma Oficial Mexicana) certification label on the retail box.


[ad_2]
Source link

Get ready to see Meta’s AI chatbot everywhere

0
[ad_1]

There’s this big AI rat race going on, and Meta is the next to skurry up to the starting line. It’s no surprise that the company eventually entered the fray, being a huge tech company. Well, Meta’s AI assistant is on its way, and you’re going to see it pretty much everywhere.

Right now, we don’t know too much about the assistant, as it’s still behind closed doors. Alex Heath from The Verge was given an early look at the bot. As for the capabilities, speed, and other information about this chatbot, we’re all still in the dark. More details about this AI assistant will come out as time goes on. One thing we do know is that it should be coming to the public pretty soon.

Meta’s AI assistant will be prevalent, to say the least

What does Google and Microsoft have in common? They both not only have powerful AI under their belts, but they also have massive ecosystems of products to implement said AI. Well, Meta is the same way. The company owns some of the biggest social media/messaging platforms on the earth. We’re talking about Facebook, Facebook Messenger, Instagram, Threads, and WhatsApp.

So, Meta definitely has a lot that it can squeeze its AI into, and it’s going above and beyond. For starters, we covered that it’s going to create AI personas based on different human beings. Some of them are going to be based on existing celebrities like Snoop Dogg, MrBeast, Dwyane Wade, Paris Hilton, Kendall Jenner, and more. There will also be generic personas like people with different occupations to help you with different tasks.

Meta’s AI assistant will be multi-modal. This means that it will be able to output different forms of media. As you can expect, it’s able to create written content just like other chatbots. It will also be able to produce AI-generated images. One image that it created looks like your typical AI-generated image.

When it came to safety, Heath tried to get the chatbot to say something bad, but the assistant was able to keep a clean tongue. Meta said that it put 6,000 hours into searching for problematic use cases. Basically, the assistant will be able to identify a ton of different problematic topics.

Meta’s AI assistant is coming to Instagram, WhatsApp, and Messenger, but we won’t be surprised if it comes to Facebook and Threads eventually. When it does, we’ll get a better idea of what this chatbot can do.


[ad_2]
Source link