Meta brings AI stickers to Instagram, Facebook Stories, Messenger, and WhatsApp

0
[ad_1]
At Connect earlier today, Meta revealed a bunch of AI editing tools and AI-powered features coming to many of its apps and services. Additionally, we’ve finally learned when the Meta Quest 3 will hit shelves after the company announced its price a while ago.

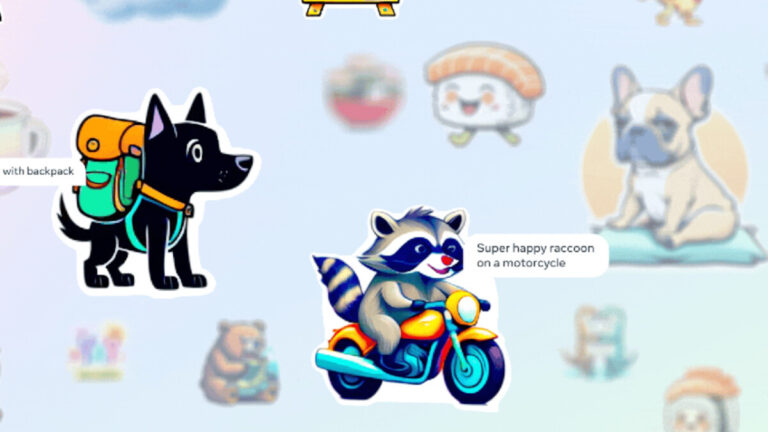
One of the most interesting AI experiences introduced by Meta is the ability to send AI stickers. These are customized stickers generated by AI based on the user’s searches.

Meta’s AI stickers use technology from Llama 2 and the company’s model for image generation called Emu. The AI tool will turn your text prompts into multiple unique stickers in seconds. Simply search for a specific sticker that you want to use like a hedgehog or blue heart, and the AI tool will generate a high-quality sticker for you to include in your conversations.

According to Meta, the new feature will be rolled out to select English-language users over the next month in WhatsApp, Messenger, Instagram, and Facebook Stories.

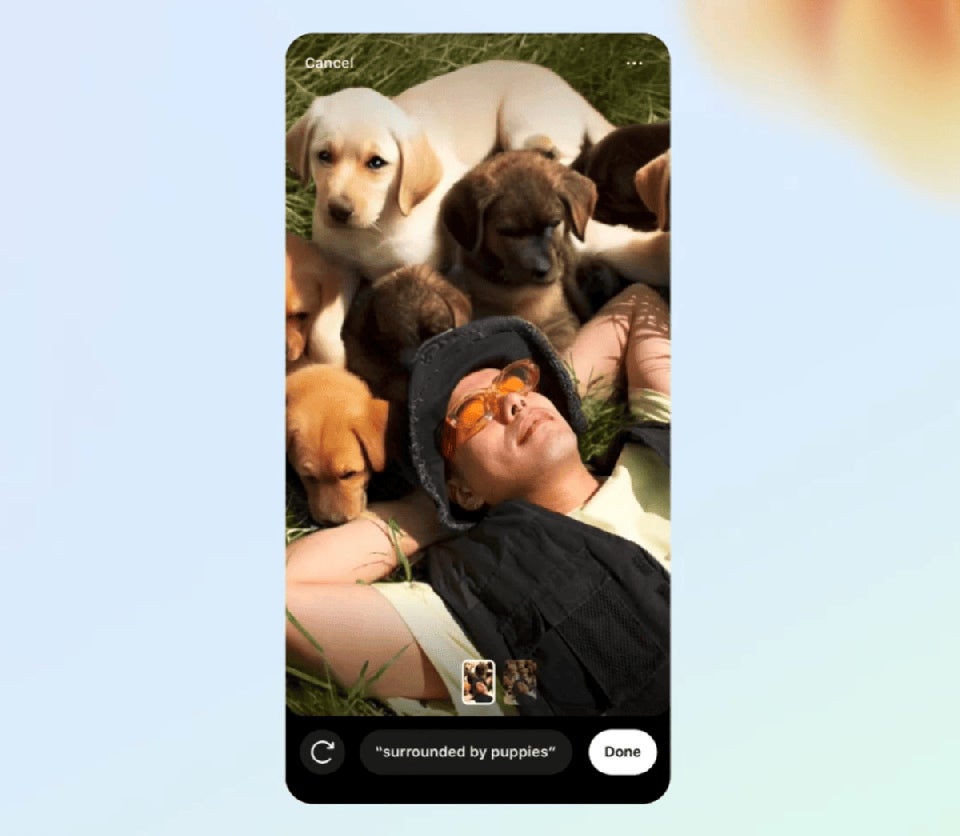
Along with AI stickers, Meta also announced some AI editing tools that also use the technology from Emu. Two new features are coming to Instagram, restyle and backdrop, which will allow users to transform their images or co-create AI-generated images with friends.

With restyle, users can reimagine their images by applying the visual styles they describe (i.e. watercooler, collage). On the other hand, backdrop changes the scene or background of an image.


You can use commands like “put me in front of an aurora borealis” or “surrounded by puppies” to cue the tool to create an image of the primary subject in the foreground with the background that you want.

It’s important to note that all images created with restyle and backdrop will indicated the use of AI to avoid being confused with human-generated content.


[ad_2]
Source link

Cisco WAN Manager Vulnerabilities Attacker Conduct DoS Attack

0
[ad_1]

Cisco, a prominent player in the world of networking and cybersecurity, has issued a critical security advisory concerning multiple vulnerabilities in their Catalyst SD-WAN Manager, formerly known as Cisco SD-WAN vManage. 

These vulnerabilities could potentially open doors for cyber attackers to access affected systems or cause a significant denial of service (DoS) situation.

First and foremost, it’s important to note that there are no workarounds available to mitigate these vulnerabilities. 

This means that immediate action is necessary to address these critical issues.

Document
FREE Demo

Implementing AI-Powered Email security solutions “Trustifi” can secure your business from today’s most dangerous email threats, such as Email Tracking, Blocking, Modifying, Phishing, Account Take Over, Business Email Compromise, Malware & Ransomware

Vulnerabilities Unveiled: CVEs and CVSS Scores

CVE-2023-20252: This vulnerability involves unauthorized access to Cisco Catalyst SD-WAN Manager via Security Assertion Markup Language (SAML) APIs. 

An attacker, even if unauthenticated, could potentially gain unauthorized access to the application as an arbitrary user. The severity of this vulnerability is rated as Critical with a CVSS Base Score of 9.8.

CVE-2023-20253: This vulnerability affects the CLI (Command-Line Interface) of Cisco Catalyst SD-WAN Manager. 

It could allow an authenticated, local attacker with read-only privileges to bypass authorization and roll back controller configurations, which could then be deployed to downstream routers. 

This vulnerability is rated as High with a CVSS Base Score of 8.4.

CVE-2023-20034: Here, an information disclosure vulnerability is revealed. It involves an unauthenticated, remote attacker accessing the Elasticsearch database of an affected system with the privileges of the Elasticsearch user. 

This vulnerability is rated as High with a CVSS Base Score of 7.5.

CVE-2023-20254: This vulnerability pertains to the session management system of Cisco Catalyst SD-WAN Manager’s multi-tenant feature. 

An authenticated, remote attacker could access another tenant managed by the same instance, potentially leading to unauthorized configuration changes or causing a denial of service (DoS) situation. It has a High severity rating with a CVSS Base Score of 7.2.

CVE-2023-20262: Lastly, there is a vulnerability in the SSH (Secure Shell) service of Cisco Catalyst SD-WAN Manager, which could lead to a process crash, resulting in a DoS condition for SSH access. 

This vulnerability is rated as Medium with a CVSS Base Score of 5.3.

Affected Products and Fixed Software

The vulnerabilities impact Cisco Catalyst SD-WAN Manager, and users must determine if their software releases are vulnerable. 

Cisco has released software updates to address these issues. Users with service contracts should obtain security fixes through their usual channels.

Protect yourself from vulnerabilities using Patch Manager Plus to quickly patch over 850 third-party applications. Take advantage of the free trial to ensure 100% security.


[ad_2]
Source link

Multiplayer shooter ‘Hyenas’ was shot down just before launch

0
[ad_1]

Last year, Sega introduced us to a new and exciting game. Called Hyenas, it was a multiplayer shooter that had a fun aesthetic and interesting characters. Well, according to Sega, Hyenas was shut down just before its launch.

The company unveiled the game last year, and it’s been beta testing the game ever since. There was a lot of hype for this game, as it seemed like a very fun time. The unfortunate thing is that it was meant to be coming out rather soon. Those waiting for the public release are going to be disappointed.

Hyenas was shut down in the wake of potential layoffs

Why did Sega shut down this interesting-looking shooter? It’s not because the company wants to punish its fans. The studio behind the game is Creative Assembly, and it’s also responsible for Alien: Isolation and Total War. Well, Creative Assembly could be facing some layoffs soon.

Currently, Sega is going through a structural reform at the moment, and one area that’s seeing the biggest impact is the European market. “…the business environment surrounding the Consumer area has been rapidly changing, including reactionary decline from the stay-at-home demand in COVID-19 and the economic downturn due to inflation in European region, and profitability has been lowered mainly in European bases.”

The company’s European business is facing some hurdles, unfortunately, and it needs to make some cutbacks. This includes canceling games in development. One of those games being shut down is Hyenas.

Not only that, but the company is getting ready to lay off employees. We’re not sure how many people will be let go, however. The studio stated that it’s going to focus on reducing redundant positions, and it’s going to try to find new positions for employees where possible. This isn’t great news for the employees at the company or for the people who were waiting to play Hyenas.

However, if the economic conditions are bad, they’re bad. Large companies are still struggling to maintain profitability, and that’s led to rolling layoffs across the industry. All we can do is hope that the company won’t need to make many more decisions like this one.


[ad_2]
Source link

The Meta Quest 3 is getting a nifty wireless charging dock

0
[ad_1]

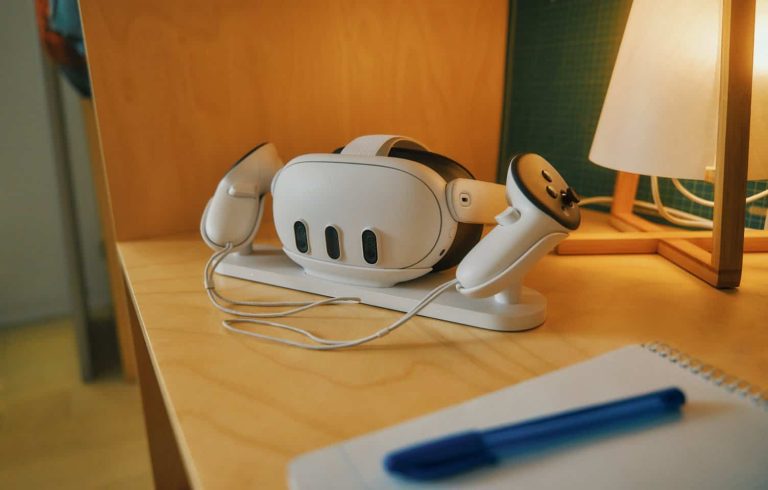
Meta officially announced the Quest 3 headset this week alongside a handful of companion accessories, including a wireless charging dock. As spotted by The Verge, the dock for the Quest 3 charges both your headset and your controllers wirelessly. Which provides two really useful benefits over the dock that was used for the Quest Pro.

The first and most obvious being that charging is now wireless. There’s one less cable for you to have to deal with. And any time that you get to use less cables is a good time. The other major benefit here is that the dock now supports the headset and the controllers in one single unit.

With the Quest Pro dock, the dock itself would charge the controllers. While a cable plugged into the dock would charge the headset. Now you can just place the headset and controllers down on the dock altogether. The controllers still take AA batteries but the dock comes with rechargeable lithium ion “Meta” batteries that the company says provides hundreds of charging cycles. And the headset of course has an internal battery that can charge via the contacts on the underside of the VR headset.

The Meta Quest 3 wireless charging dock retails for $129.99

If you want to charge your headset and controllers wirelessly be prepared to cough up a little extra cash. As the dock will set you back $129.99. Pair that up with the Quest 3’s starting $499 price tag and you’re in for a $630 investment. And that’s before you throw down any other money on games or additional accessories.

The overall cost is certainly not inexpensive. But the value is likely there for those that want the added convenience of just picking up the hardware and being ready to play. No having to mess about with unplugging everything. Or store an extra cable away somewhere when it’s not in-use. You can buy the dock directly from Meta but you can also get it from retailers like Best Buy. The dock is still in a pre-order status though and won’t officially be shipping until November 10.

Meta Quest 3 Wireless Charging Dock – Best Buy


[ad_2]
Source link

Say goodbye to password sharing on Disney+

0
[ad_1]

Disney+ has over 140 million subscribers worldwide. But in the past year, the streaming giant saw a drop in paying users, with almost 20 million people saying goodbye to their Disney+ memberships. At the same time, the company introduced new plans and hiked up the prices for some of them. Now, there are more changes on the way.Users in Canada won’t be able to share their Disney+ passwords and accounts with people outside their households anymore, as reported by Android Authority. Disney+ sent out emails to its users, letting them know that starting from November 1st, shared accounts will be restricted. Only people living under your roof will be allowed to watch on devices connected to your primary account.

This move to crack down on password sharing isn’t entirely new, as Netflix has already done it. Netflix lets users pay for extra subscribers who don’t live in the same house, but Disney+ hasn’t announced such a feature. So, if you’ve been sharing a Disney+ account in Canada, you might find yourself kicked out unceremoniously come November 1st.

Netflix also allows you to transfer your profile to keep your watchlist and recommendations intact. Whether Disney+ will offer similar options remains unclear.

Disney+ recently introduced an ad-supported option to soften the blow of an upcoming price increase for ad-free subscriptions. However, with this password-sharing crackdown, it might need to think of more ways to keep its current users and attract new ones. Content is essential, but don’t underestimate the impact of prices and the ability to use your profile from anywhere.

Some users on Reddit have reported difficulties logging into their Disney+ accounts when they’re away from home, which can be a hassle, especially when you’re paying for it every month.

This password-sharing restriction kicks off in Canada on November 1st. Whether it will affect the US and other countries remains uncertain for now.


[ad_2]
Source link

Dark Web Pedophiles Using Open-Source AI to Generate CSAM

0
[ad_1]

Pro tip: Do not upload images of your children on the internet, including your social media profile, even if your friends list consists of people you know or trust.

  • The availability and sophistication of generative AI platforms is a growing issue of concern. Cybercriminals can easily manipulate videos, images, and audio to create deep fake content.
  • A UK-based internet watchdog has shared startling details of how paedophiles have switched to generative AI to create child sexual abuse content.
  • Research revealed that paedophiles use freely available AI software to create illegal child pornographic material.
  • The Internet Watch Foundation observed that paedophiles are openly discussing how to modify the software to manipulate children’s photographs on the dark web.
  • This can make it challenging to help real-life victims.

We all know OpenAI’s ChatGPT chatbot. You may also be aware that cybercriminals have developed malicious alternatives of ChatGPT known in the cybersecurity community as FraudGPT and WormGPT. The bottom line is that cybercriminals will go to great lengths to turn the power of Artificial Intelligence (AI) to their advantage for malicious purposes.

Now, according to a report published by a UK-based internet watchdog, the Internet Watch Foundation (IWF), cybercriminals are turning to generative AI platforms to create child sexual abuse material (CSAM).

As per the research from IWF, cybercriminals’ increasing preference to create deep fake content fabricating people or events is a concerning issue because of the sheer scope of damage it can cause. The problem becomes more concerning when it involves minors, particularly children. The ease with which sex offenders can create this imagery can also encourage its widespread acceptability.

The IWF found that there’s been a sudden surge in AI-generated child sexual abuse content available online. The organization noticed discussions among paedophile rings on dark web forums frequently used by sex offenders regarding tips on creating fake images of children via open-source AI models.

Child safety experts and law enforcement agencies are afraid that the availability of realistic photos will make it challenging to help real-life victims of child sexual abuse. It must be noted that creating photorealistic content is illegal in the UK.

Open-source AI models differ from closed AI models like Google’s Imagen, as anyone can download them. It is easier to use these models because they can download and run them on PCs, and there’s no need to run them on the cloud. So, they can evade the controls and detection tools on the cloud and distribute the content online more regularly than they do now.

Offenders can use a basic source image-generating model containing billions of tagged images and fine-tune the images with child sexual abuse images to create a similar model with low-rank adaptation. Hence, with minimal computation, they can produce realistic images and mislead law enforcement by diverting their focus on child victims that don’t exist.

Earlier, the IWF’s chief executive, Susie Hargreaves OBE, had warned the government regarding the seriousness of this issue. 

In May 2023, the Internet Watch Foundation (IWF) initiated the recording of instances involving AI-generated child sexual abuse material, marking a significant development for its hotline. Over the span of May 24 to June 30, the IWF diligently investigated 29 reports encompassing URLs suspected of housing AI-generated child sexual abuse imagery. These reports came from concerned members of the public.

Among these cases, the IWF successfully verified that seven of the reported URLs indeed contained AI-generated child sexual abuse imagery. Notably, these URLs often hosted multiple images, which could be entirely AI-generated or a combination of AI-generated and authentic content.

Disturbingly, the addressed URLs covered a distressing range of material, spanning from Category A to Category B, and depicted children as young as 3 to 6 years old, comprising both female and male victims.

“We are not currently seeing these images in huge numbers, but it is clear to us the potential exists for criminals to produce unprecedented quantities of life-like child sexual abuse imagery. This would be potentially devastating for internet safety and for the safety of children online. We have a chance, now, to get ahead of this emerging technology, but legislation needs to be taking this into account and must be fit for purpose in the light of this new threat,” Hargreaves had said.

The head of the UK government’s AI task force, Ian Hogarth, had raised red flags about child sexual abuse material created using open-source AI models, claiming that it was amongst the “most heinous things out there.”

The IWF chief Dan Sexton regarded this as a “public health epidemic” that will get only worse as cybercriminals switch their focus on generative AI technology.

The IWF is a non-profit organization founded in 1996 to monitor the internet for sexual abuse content and receive tips about such content, especially involving children.

How to Protect your Child and their Photos from Malicious Elements on Dark Web?

Here are 10 ways parents can protect their children and their photos from exposure to the dark web and individuals with malicious intent:

  1. Educate Your Children: Teach your kids about online safety, including the importance of not sharing personal information, photos, or engaging with strangers online.
  2. Use Privacy Settings: Adjust the privacy settings on social media platforms to ensure that only trusted contacts can view your child’s content.
  3. Regularly Check Friend Lists: Encourage your child to regularly review their friend lists and followers on social media and remove anyone they don’t know in real life.
  4. Watermark Photos: If you choose to share photos of your children online, consider watermarking them to deter unauthorized use.
  5. Limit Location Sharing: Disable location sharing on your child’s devices and social media accounts to prevent tracking by malicious individuals.
  6. Use Secure Devices: Ensure your child’s devices have up-to-date security software and are protected with strong passwords or biometrics.
  7. Teach Responsible Posting: Encourage responsible posting by discussing the potential consequences of oversharing personal information or photos.
  8. Monitor Online Activity: Keep an eye on your child’s online activity without being overly invasive. Use parental control software if necessary. Use parental control apps!
  9. Promote Open Communication: Create an environment where your child feels comfortable discussing any online interactions or concerns they may have.
  10. Report Suspicious Activity: Teach your child how to recognize and report suspicious behavior or content to both you and the relevant authorities.
  1. Hackers Claiming to Jailbreak AI Chatbots to Write Phishing Emails
  2. Microsoft’s new tool detects & reports pedophiles from online chats
  3. Fake ChatGPT and AI pages on Facebook are spreading infostealers
  4. Operation Narsil – INTERPOL Busts Decade-Old Child Abuse Network
[ad_2]
Source link

ZYXEL Buffer Overflow vulnerability – Attacker Launch DoS Attack

0
[ad_1]

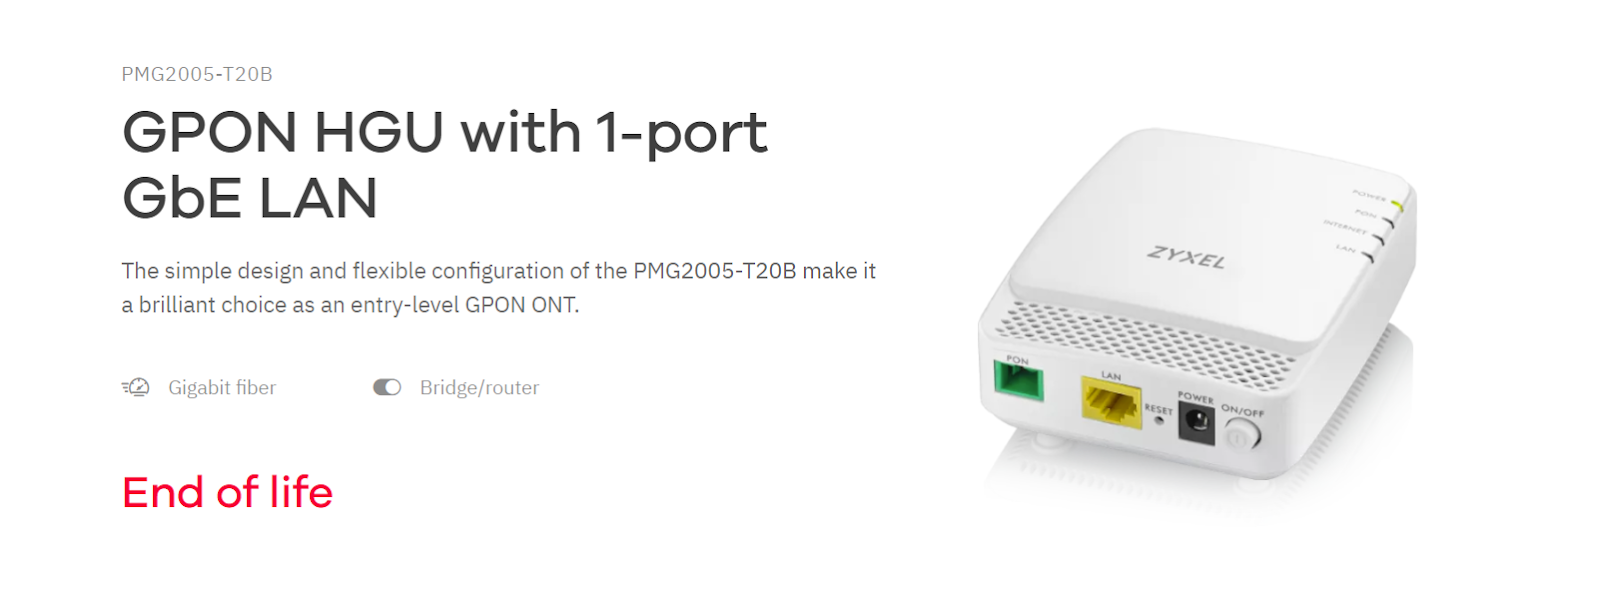
ZYXEL has been discovered with a Buffer Overflow vulnerability on their ZYXEL-PMG2005-T20B device, which can result in a denial-of-service condition. This condition exists due to improper sanitization of user-supplied input on their HTTP request.

Zyxel is a Taiwanese multinational company that manufactures several networking products like Routers, DSL CPE, WiFi Systems, 5G NR/4G LTE CPE, Carrier and Access Switches, Network Extenders, and Network Management devices.

Technical Analysis

A threat actor can exploit this vulnerability by providing a crafted script to the uid parameter in the cgi-bin/login.asp, leading to a Buffer Overflow, eventually causing the DoS condition. This vulnerability has been assigned with the CVE as CVE-2023-43314, and the severity is being analyzed.

Document
FREE Demo

Implementing AI-Powered Email security solutions “Trustifi” can secure your business from today’s most dangerous email threats, such as Email Tracking, Blocking, Modifying, Phishing, Account Take Over, Business Email Compromise, Malware & Ransomware

This vulnerability arises in the ZYXEL-PMG2005-T20B product when the number of admin in the uid exceeds the maximum threshold of 50, which crashes the application when parsed in the backend. Additionally, the COOKIE header in the HTTP request is supplied with a SESSIONID parameter for creating a valid session with the ZYXEL product.

However, further analysis revealed that the ZYXEL-PMG2005-T20B product has reached End-of-Life as per the ZyXEL website. 

End-of-Life
End-of-Life (Source: Cyber Security News)

The researcher created an HTTP request to replicate this vulnerability with the following parameters and values.

GET /cgi-bin/index.asp HTTP/1.1
Host: {HOST IP}
Upgrade-Insecure-Requests: 1
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/109.0.5414.120 Safari/537.36
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,/;q=0.8,application/signed-exchange;v=b3;q=0.9
Referer: http://{HOST IP}/cgi-bin/login.asp
Accept-Encoding: gzip, deflate
Accept-Language: zh-CN,zh;q=0.9
Cookie: SESSIONID=4450a48a; uid=adminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadminadmin; psw=1234
Connection: close

This request to the ZyXEL product causes the Buffer Overflow due to the number of admin thresholds resulting in the Denial of Service condition. In addition to this, more than 20 URLs were listed by the security researcher, which were affected by the same vulnerability.

A GitHub repository, along with the proof-of-concept was published, which provides detailed information about this vulnerability, its existence, and other information. 

Users of this ZyXEL product are recommended to upgrade to the latest version of the product in order to prevent this vulnerability from getting exploited.

Protect yourself from vulnerabilities using Patch Manager Plus to quickly patch over 850 third-party applications. Take advantage of the free trial to ensure 100% security.


[ad_2]
Source link

Galaxy Tab A9+ specs revealed by Google Play ahead of launch

0
[ad_1]

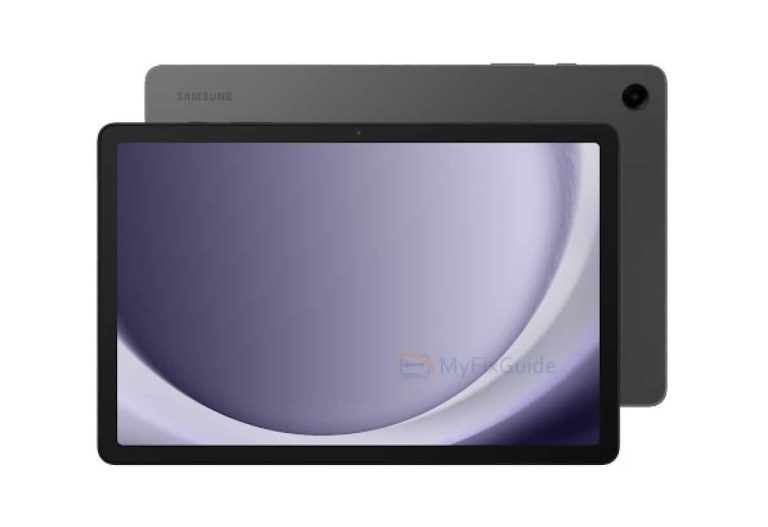
We recently got confirmation that Samsung will unveil the Galaxy Tab A9 series on October 5. The base model showed up on the Google Play Console last week to reveal some of its key specs. The Plus model has now surfaced on the same website, giving us an idea of what to expect from it.

Google Play Console reveals key specs of the Galaxy Tab A9+

Spotted by MyFixGuide, Google has listed the 5G version of the unannounced Samsung tablet. We can see that the device has a Qualcomm processor with the model number SM6375. It’s none other than the Snapdragon 695, a 6nm mid-range chipset featuring two ARM Cortex-A78 CPU cores clocked at 2.2GHz and four Cortex-A55 cores at 1.8GHz. Qualcomm has paired the CPU with the Adreno 619 GPU. The SoC supports both sub-6 and mmWave 5G networks.

Samsung will offer at least 4GB of RAM with the Galaxy Tab A9+. The tablet may also be available in a 6GB RAM variant. Storage configurations are not known but we should get 128GB of internal storage space if not more. The device will support microSD cards for expandable storage. The Korean firm may let you add up to 1TB of additional storage space externally.

This tablet features a Full HD+ (1200×1920 pixels resolution) display. It is presumably an LCD panel measuring between 11 and 12 inches diagonally. The Google Play Console listing also confirms that the Galaxy Tab A9+ will run Android 13 out of the box. Samsung will likely ship it with its One UI 5.1.1 custom software. The device has one camera each on the front and back. Earlier rumors have revealed a 7,040mAh battery with 15W fast charging.

The rest of the specs of this tablet are still under the wraps. However, as said earlier, Samsung plans to launch the Galaxy Tab A9 series next week, so it won’t be long before we get to know everything about the duo, including the pricing structure. We might even come across more detailed leaks ahead of the official unveiling. Stick around and we will keep you posted with all the latest information.

Samsung has more devices lined up for launch in early October

The two new A-series tablets could be accompanied by a bunch of other Galaxy devices out of Samsung’s doors next week. The Korean firm also has the Galaxy S23 FE, Galaxy Buds FE, Galaxy Tab S9 FE, Galaxy Tab S9 FE+, and Galaxy SmartTag 2 in the pipeline. All of these devices are scheduled for an early October release. It remains to be seen if they break cover on the same day.

Samsung Galaxy Tab A9 Plus Google Play Console 2


[ad_2]
Source link

Jony Ive & OpenAI’s Sam Altman reportedly have an AI gadget in works

0
[ad_1]

Apple’s veteran designer, Jony Ive, and OpenAI CEO Sam Altman will collaborate to build an AI gadget. As The Verge (via The Information) reported, the product would be an AI “hardware device,” but there are no more details about it yet.

Artificial intelligence is taking over our lives and becoming an integral part of all new devices. Most new startups that come to life claim to incorporate AI into their operations. Meanwhile, older AI companies are exploring the idea of building AI hardware, including ChatGPT’s parent company, OpenAI.

OpenAI’s Sam Altman and Apple’s former chief design officer, Jony Ive, reportedly met to discuss what “new hardware for the AI age could look like.” The outlet states that both have just talked about the possibility of building AI hardware, and there’s yet to be a firm decision to make one.

OpenAI’s Sam Altman and Jony Ive might be developing an AI hardware

Jony Ive is a legendary designer who is well-known for his memorable works at Apple, including iMac, iPod, iPhone, iPad, MacBook, and iOS interfaces. He parted ways with Apple in 2019 to work on independent projects.

Altman has already worked with former Apple designer Thomas Meyerhoffer on his Worldcoin crypto project. Meyerhoffer was Ive’s assistant in designing the iMac, and he also designed the spherical retina-scanning Orb for Altman’s startup.

Altman’s connection with former Apple employees doesn’t end here. He’s an investor in Humane, a startup founded by ex-Apple staff. Humane aims to make wearable AI devices to replace smartphones. The startup also works with OpenAI to incorporate AI technology into its devices. A smartwatch with advanced AI capabilities and ChatGPT could be the result of this project.

If Altman and Ive ever decide to build their AI hardware, SoftBank CEO Masayoshi Son is ready to step in and fund the project. Son is reportedly in talks with both about the project. With over $140 billion worth of investment in AI startups, SoftBank aims to become “the investment company for the AI revolution.”


[ad_2]
Source link

Vivaldi browser is now available on iPhones and iPads

0
[ad_1]
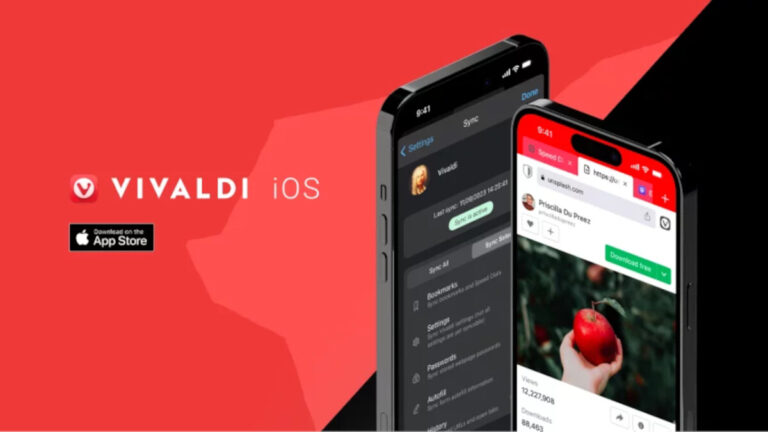
Four years after its release on Android, Vivaldi browser is finally making its debut on iOS. Featuring a distinctive look and providing different experience to casual and advanced users, Vivaldi prides itself for being flexible and versatile.

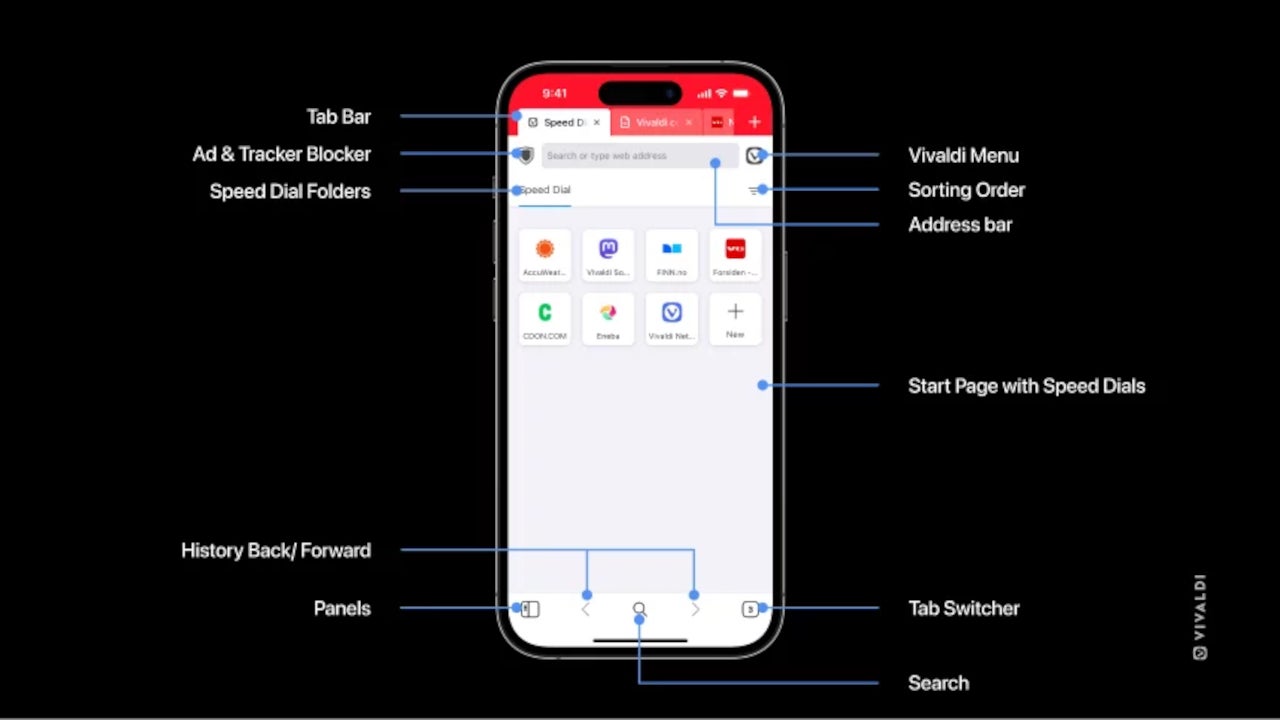
Just like the Android version, Vivaldi for iOS starts with Speed Dials when launched. You can put here all your favorite sites organized the way you want, so when you launch the browser, they’re just one tap away.

Panels is positioned at the bottom-left corner of the app and allow users to quickly access useful tools like Bookmarks, History, Notes, Reading List, and Downloads. The Tab Switcher from the bottom-right corner lets users access regular, private, and synced tabs, as well as the trash can to retrieve recently closed tabs.

The Search tab and buttons for moving back and forth in History, in the middle. You can search for information directly in the Address Bar too. The Tab Bar with desktop-style tabs helps users view and switch between tabs smoothly.

Vivaldi keeps track of the open tabs thanks to the elegant desktop-style Tab Bar in the UI. It reminds me of Opera, but on desktop. The bottom line is that while the way Vivaldi keeps track of open tabs improves usability significantly, it’s not really unique, even for a mobile browser.

What’s unique to Vivaldi is the built-in Notes feature, which allows users to write down ideas, to-dos, and anything else worth remembering while browsing. Additionally, it’s possible to highlight any text and copy it into the Notes section of the browser.

More importantly, Notes can be synced between phone, desktop, and car. In fact, you can sync all your browsing data, including Bookmarks, Speed Dials, saved passwords, autofill information, typed History, and Notes, between installations of Vivaldi and other devices.

Vivaldi browser is now available for free via the App Store and is fully compatible with devices running iOS/iPad OS 15 or above.


[ad_2]
Source link