TikTok flooded with fake celebrity nude photo Temu referrals

0
[ad_1]

A bogus celebrity leaked photos scam linked to Temu referrals is doing the rounds on TikTok.

Sites and apps frequently gamify their products and experiences to grow their user base. It’s a relatively easy way to have their customers become more involved thanks to whatever incentives may be on offer. A game here, a rewards program there, and everyone is happy.

Well, almost everyone. If scammers insert themselves into the process then it may not all be plain sailing. Unfortunately, Bleeping Computer is reporting a wave of dubious Temu referral scams pretending to offer up salacious leaks of private celebrity photos.

These scams are being posted to video platform TikTok, where high visibility and the desire for good deals runs the risk of making these fake ads go viral.

Temu, in operation since 2022, is known for offering a wide selection of goods at cheap prices. The site makes use of a rewards system, where users can generate referral numbers and send them to friends and family. The referral links are frequently shared in places like Facebook groups, which offer a combination of discounts. Mobile games tied to the referral process can often increase the discounts still further. This feedback loop of gaming and rewards is quite the successful combination in most instances.

So far, so good. Where this goes horribly wrong is a nasty wave of spam cluttering TikTok with the promise of fake celebrity nudes taking up space on the social network. Using the tagline “If you search it up, be prepared” along with common hashtags like “#anime, #manga, #art”, a variety of photos of celebrities are overlaid with text saying things like “I thought she was innocent”. It’s all very sleazy, tricking the viewer to install the Temu app and enter the referral number to see the supposedly leaked images.

But these images don’t exist, it’s just the main bait for the scam. As we’ve seen in the past, leaked photographs and celebrity deepfakes are a potent mix and guaranteed to drive clicks, traffic, or installations. Bleeping Computer cites Jenna Ortega, Brooke Monk, Hailie Deegan, and Olivia Rodrigo as just some of the celebrities used for this scam campaign.

The only good thing we can really say here is that the links don’t lead to phishing or malware. So far, it’s “just” scammers racking up store credit. However this is still a big problem for many reasons, not least of which for Temu which is faced with the possibility of people gaming its system.

Bogus celebrity nude promos posted to TikTok aren’t good for the platform or the users, and both services will have to try and take these fraudsters to task. Meanwhile, users can also do their bit and report any such videos they spot on their feeds. Nobody is posting genuinely leaked imagery to TikTok, and most definitely not for the purposes of store credit.

The promise of fake stolen imagery is one of the oldest tactics in the book, and yet remains a very effective resource in the scammer’s toolkit. Whether you hear about such a thing by email or social media, our advice is to steer clear. Apart from it being incredibly distasteful and quite possibly illegal depending on where you reside, you run a major risk of falling victim to a more serious form of scam.

Is a quick clickthrough for store credit or some other reward really worth putting your system at risk? We’d suggest that the answer is most definitely a resounding no.


We don’t just report on threats—we remove them

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.


[ad_2]
Source link
Google Pixel 8 series gets Super Bright “Actua Display” for Direct Sunlight

0
[ad_1]

An issue that many of us suffer from with our smartphones is, not being able to see it well in direct sunlight. Well, Google is looking to fix that with the Pixel 8 series this year.

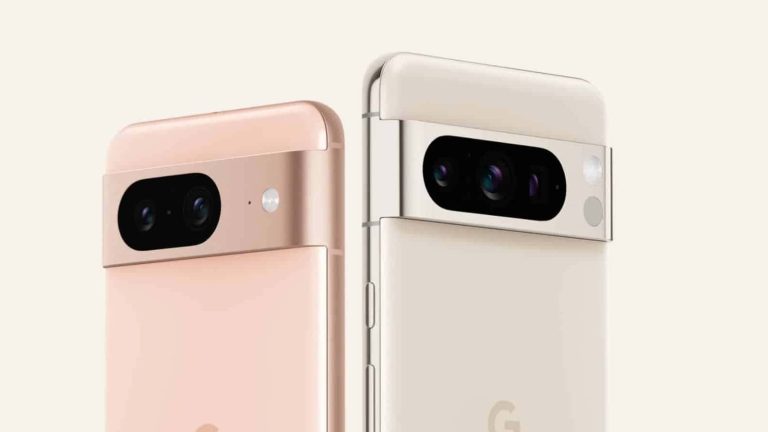
Among all of the other leaks of the Pixel 8 and Pixel 8 Pro from this morning, is a part about the display. Which Google is calling the “Actua Display”. I’m sure, Google will spend a good amount of time talking about this name, but the most important part is just how bright these displays will be.

The Pixel 8 will have a peak brightness of 2,000 nits, while the Pixel 8 Pro gets a peak brightness of 2,400 nits. Now, to put things in perspective, the latest Samsung smartphones (Galaxy S23 Ultra, Galaxy Z Fold 5, etc) have a peak brightness of 1,750 nits. And the latest iPhone 15 Pro has a peak brightness of 2,000 nits. So this is rather impressive, and that means that the Pixel 8 Pro will have the brightest display on the market.

Flat display all but confirmed on Pixel 8 Pro

Another little tid bit from these leaks this morning, is that the Pixel 8 Pro is basically confirmed to have a flat display. Now, we had already seen this in other leaks and rumors. But to see this straight from an image on the Google Play Store, that’s another thing. And basically makes it official.

It’s still a 6.7-inch QHD display, but now it is flat. That’s going to make a lot of people happy. While a curved display does look nice when watching video, it makes it much harder to have a screen protector on. It also gets scratched a lot easier than a flat display, and overall makes the phone less rugged.

Google will officially announce the Pixel 8 and Pixel 8 Pro at its annual fall event on October 4. We’ll be there to cover everything that Google has in store.

google pixel 8 actua display


[ad_2]
Source link

Flipper Zero can now be used to spam iPhone users with fake notifications

0
[ad_1]

Flipper Zero has quickly become one of the most popular hacking tools, thanks in part to its interface and the thriving community that surrounds it. However, security researcher Anthony has recently unveiled a new attack that leverages Flipper Zero to spam iPhone users with pop-up notifications.

How does the attack work?

To grasp how the attack works, it’s crucial to understand that Apple devices use Bluetooth advertising packets (ADV packets) to broadcast their presence to nearby devices, such as AirPods. Taking advantage of this, bad actors can craft and spread fake ADV packets while adhering to the Bluetooth Low Energy (BLE) protocol. As a result, any iPhone within range perceives these transmissions as real connection requests irrespective of whether a user has disabled Bluetooth through the Control Center or not.

While the attack looks more like a prank, it could have vast applications. These include confusing a victim by overwhelming them with fake requests or outright imitating trusted devices for potential phishing attacks.

“When a device like Flipper Zero mimics the advertising packets of real devices or services, it can create a lot of phantom devices in the vicinity of an iPhone user. Imagine searching for a device to connect to and being presented with a list of dozens, if not hundreds, of fake device names,” reads Anthony’s blog post.

Furthermore, Anthony has developed an “amplified board” capable of broadcasting Bluetooth packets over a significantly greater range than standard Bluetooth Low Energy devices. This technique could provide threat actors with an avenue to exploit this attack, although he has, fortunately, refrained from disclosing specific details about this method.

What can Apple do?

While Apple has yet to issue an update fixing this issue, the company could adopt measures to check the legitimacy of Bluetooth devices trying to connect with iPhones and restrict the distance at which Bluetooth devices can establish connections.

“For iOS users, this mimicry can be more than just an annoyance. It can lead to confusion, disrupt workflows, and, in rare cases, pose security concerns. It underscores the importance of being aware of the devices around us and the potential flaws inherent in wireless communications,” reads the blog post.


[ad_2]
Source link

Say goodbye to YouTube’s Premium Lite subscription plan

0
[ad_1]

While most streaming services increased prices this year, YouTube has decided to even more to adjust its offering. Starting next month, YouTube’s ad-free Premium Lite subscription plan will no longer be available, the company confirmed today in an email.

The fine folks at The Verge got their hands on the email that YouTube is now sending to those who pay for the Premium Lite subscription plan, so here is the relevant content:

For those who don’t know, the Premium Lite plan is still available for €6.99 and made its debut two years ago in select European countries, including Belgium, Denmark, Finland, Luxembourg, the Netherlands, Norway, and Sweden.

Despite its name, the plan doesn’t offer the usual Premium features that other plans have included such as offline downloads, background playback and YouTube Music. The only major benefit of paying for Premium Lite is that you can watch videos without being served any ads.

The email sent by YouTube to notify Premium Lite subscribers about the upcoming changes includes information about at least one benefit that they will get.

All Premium Lite subscribers will receive a one-month free trial of YouTube Premium even if they previously had a trial. After the free trial expires, Premium Lite subscribers will have to choose a more expensive Premium plan or continue to watch YouTube with ads.


[ad_2]
Source link

Ransomware group claims it’s “compromised all of Sony systems”

0
[ad_1]

The ransomware group RansomedVC says its selling Sony’s data.

Newcomer ransomware group RansomedVC claims to have successfully compromised the computer systems of entertainment giant Sony. As ransomware gangs do, it made the announcement on its dark web website, where it sells data that it’s stolen from victims’ computer networks.

RansomedVC announces it's compromised Sony

The announcement says Sony’s data is for sale:

Sony Group Corporation, formerly Tokyo Telecommunications Engineering Corporation, and Sony Corporation, is a Japanese multinational conglomerate corporation headquartered in Minato, Tokyo, Japan

We have successfully compromissed [sic] all of sony systems. We wont ransom them! we will sell the data. due to sony not wanting to pay. DATA IS FOR SALE

Sony has yet to comment on the matter, and it’s important to understand that we only have one side of the story—and the side we have comes from a group of criminals. The claims of Sony’s compromise may yet prove false or, perhaps more likely, exaggerated.

If RansomedVC is to be believed though, Sony has not caved into the group’s demands for a ransom, so good for Sony, bravo. Sometimes businesses feel they have to pay their extortionists, and we aren’t going to judge anyone for making that choice. However, we’re definitely happy to applaud loudly when they don’t pay.

If Sony has been breached then its customers will be understandably concerned to safeguard their data. With information so thin on the ground it’s too early to offer specific advice, but we suggest you read our guide to what you need to know if you’re involved in a data breach.

Should it confirm the breach, Sony will join a fairly lengthy list of games and entertainment companies that have had data stolen or ransomed. Games companies are prime targets for theft and extortion because of the high value and high profile of their intellectual property.

Notable victims have included Capcom and Ubisoft in 2020, and CD PROJEKT RED, makers of Cyberpunk 2077 and Witcher 3, in 2021, the same year that FIFA 21 source code stolen from Electronic Arts. In 2022 Bandai Namco was attacked by ransomware, and Rockstar Games suffered a serious breach at the hands of the short-lived Lapsus$ gang.

RansomedVC is a new ransomware group, first tracked by Malwarebytes in August 2023 after it published the details of nine victims on its dark web site. The only departure it makes from the usual cut ‘n’ paste criminality of ransomware groups is that it threatens to report victims for General Data Protection Regulation (GDPR) violations. It describes itself as a “digital tax for peace”, but of course it isn’t. We’ve heard this a million times before, and it’s always just a cash grab.

How to avoid ransomware

  • Block common forms of entry. Create a plan for patching vulnerabilities in internet-facing systems quickly; disable or harden remote access like RDP and VPNs; use endpoint security software that can detect exploits and malware used to deliver ransomware.
  • Detect intrusions. Make it harder for intruders to operate inside your organization by segmenting networks and assigning access rights prudently. Use EDR or MDR to detect unusual activity before an attack occurs.
  • Stop malicious encryption. Deploy Endpoint Detection and Response software like Malwarebytes EDR that uses multiple different detection techniques to identify ransomware, and ransomware rollback to restore damaged system files.
  • Create offsite, offline backups. Keep backups offsite and offline, beyond the reach of attackers. Test them regularly to make sure you can restore essential business functions swiftly.
  • Don’t get attacked twice. Once you’ve isolated the outbreak and stopped the first attack, you must remove every trace of the attackers, their malware, their tools, and their methods of entry, to avoid being attacked again.

Malwarebytes EDR and MDR removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

The Galaxy Tab S9 FE tablets just had their specs leaked

0
[ad_1]

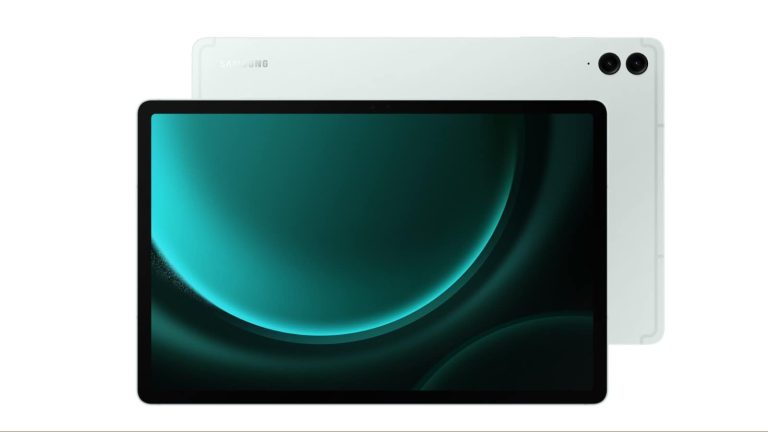
Along with the powerful and premium Samsung Galaxy Tab S9 tablets, the company is launching some more accessible tablets under its FE series. Over the past several months, we’ve been covering information about these tablets. Well, thanks to WinFuture, we have a new leak for the Galaxy Tab S9 FE and its Plus counterpart.

In case you don’t know about the FE series of devices, these are the more affordable versions of Samsung’s premium devices. We’re also covering information about the Galaxy S23 FE. This is set to be a pretty powerful device when it launches.

The Galaxy Tab S9 FE tablets just got a new leak

This is a tell-all leak about these tablets, leaving very little to the imagination. However, this is still a leak, so you’ll want to take it with a grain of salt.

Galaxy Tab S9 FE specs

Starting off with the base model this tablet is expected to have a high-quality design just like that of the S9 tablets proper. As for the display, this tablet could sport a 10.9-inch display with a resolution of 2304 x 1440. This gives it a 2K display that is just short of the QHD resolution. Regardless, you’ll have a great viewing experience. It’s also going to be an LCD panel.

Galaxy Tab S9 Plus Leaked image

Looking at the internals, this tablet is expected to use a Samsung-made Exynos SoC with a 2.4GHz clock speed. We’re not sure what chip it’s going to be, but we expect an upper-mid-range chip. This could be backed up by 6GB of RAM and 128GB of storage.

As for the rest of the camera specs, we could be looking at a 12MP camera on the front for video calls. On the back, there could be an 8MP camera. These cameras could be good to record 4K video at up to 30fps.

Other specs include an IP69 water and dust resistance rating and an 8000mAh battery.

 Galaxy Tab S9 FE+ Specs

Moving onto the Plus model, this tablet is expected to have a larger 12.4-inch display with a WQXGA resolution (2560 x 1600). This will also be an LCD display, and it could use the S Pen as well.

This tablet is expected to use the same chip as the base model but it could start with 8GB of RAM and 128GB of storage. It might be able to go up to 12GB of RAM and 256GB of storage.

Galaxy Tab S9 FE Plus Leaked image

The camera specs are expected to be the same as the base model, however, the Plus model could come with an additional 8MP camera on the back. This model could also have IP68 water and dust resistance and a 10,090mAh battery.

Both tablets are expected to be compatible with Bluetooth 5.3 and Wi-Fi 6.

The Galaxy Tab S9 FE is expected to start at €529 and the Plus model could start at €699. The 5G-enabled version could cost you €799.


[ad_2]
Source link

The Apple Watch Series 8 has a feature similar to Double Tap

0
[ad_1]

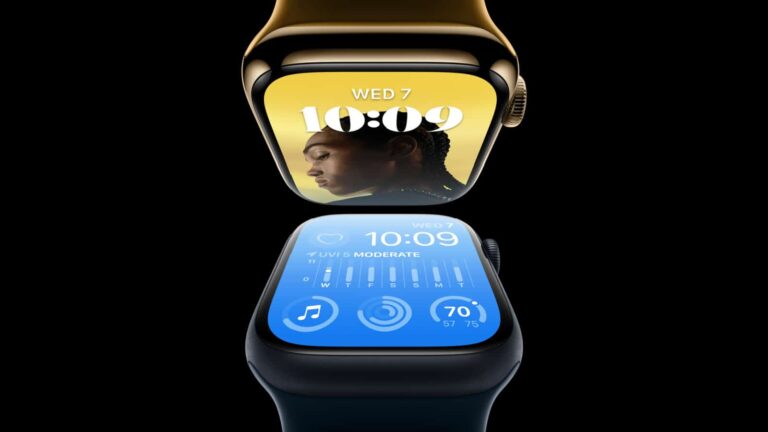
Earlier this month Apple unveiled the Watch Series 9 and the Watch Ultra 2, both of which come with a new feature Double Tap and surprisingly a similar feature already exists on the Watch Series 8.

As noted by TechRadar, gesture controls like the Double Tap aren’t a brand-new concept and the Watch Series 8 does offer a range of different gesture control features. These were designed as accessibility features and meant primarily for those who might have trouble interacting the watch using the touch display.

However, these gestures are not the same thing as Double Tap. They are however likely Apple’s jumping off point that led to it. The main thing to remember is that Double Tap is exclusive to the Watch Series 9 and Watch Ultra 2. And that’s because they use the S9 chip inside which is needed to power the feature.

To truly get what Double Tap offers, you’ll need to be on one of the new watches. But even if you are on the Watch Series 8, you can still access the other gesture controls.

Double Tap on the Apple Watch Series 8 is better known as Assistive Touch

As the name suggests, Assistive Touch is there to assist users who might have need of accessibility features. In this case, gesture controls to allow for a range of interactions. Users can enable all or some of these. Which augments their experience by lessening how much they have to touch the display.

In fact Apple’s own description of the feature states these allow for watch use without “ever” having to touch the display at all. Or the controls. So if it’s not a double tap then what is it? Well Apple specifically calls these gestures pinches and clenches. There’s also a double pinch and a double clench. You can set these up to do a number of things like launching the action menu or opening up the notification center.

It’s not quite as robust as the Double Tap feature. And based on TechRadar’s user experience, it may not work as well either. But it is there.


[ad_2]
Source link

SafeStop lets drivers video chat with police pulling them over

0
[ad_1]

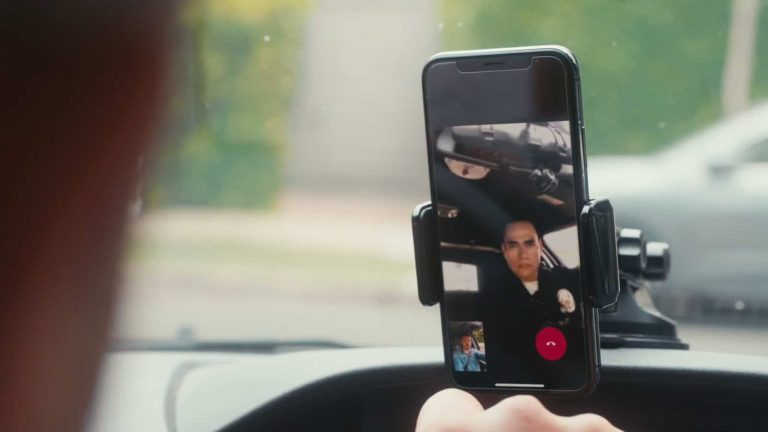
SafeStop is a new app that just started operating in West Hollywood. According to ABC, It allows drivers to video chat with the deputy pulling them over, aiming to enhance safety for both deputies and drivers.

Every year, dozens of police officers get injured while pulling over reckless drivers. A simple traffic stop might sometimes turn into violence, leaving a few dead. The police departments have taken measures to prevent these incidents. Now, technology is coming to help.

The SafeStop app claims nearly 1,500 deaths have been recorded since 2016 during traffic stops. Additionally, 70% of shots at police officers occur before or during a traffic stop, and over 15,000 stops escalated to firearm points in California. The app now wants to bring “policing into the 21st century” by allowing deputies and drivers to video chat before meeting face-to-face.

The SafeStop app aims to make traffic stops safer through video chat

The program is now being launched in West Hollywood. The Los Angeles County Sheriff’s Department has taken the initiative to use this technology to communicate with drivers while pulling them over. SafeStop might expand its operations to other states if the testing in West Hollywood is successful.

The way SafeStop works is pretty straightforward. Once a cop pulls you over, the app gives instructions on “how to facilitate dialogue” during the traffic stop. Then, you can video chat with the officer who pulled you over. The conversation will help the deputy officer to de-escalate the situation and prevent further conflicts.

“By introducing video contact at this crucial point, police officers have the option to add another layer of identification before arriving to the vehicle,” SafeStop added.

SafeStop promises to pay a percentage of its user’s ticket for a limited time. The app also needs to clarify whether there’s an opt-out option and if the calls are recorded for future reference.

Developers claim the app can create more transparency in traffic stops while alerting deputies of a person’s presence. The app is now available for Android and iOS.


[ad_2]
Source link

Small number of iPhone 15 models shipping with defects

0
[ad_1]

Normally, Apple’s QA is pretty good. But every year it seems that the very early units tend to have some defects that Apple needs to deal with. Usually, replacing them. Which is why Apple tends to keep a number of units in-store, unsold, for replacements.

It looks like there are some iPhone 15 Pro models shipping with some decent defects this time around. Majin Bu mentioned on X that some iPhone 15 Pro models are having display misalignment issues. And it seems to be happening to those units that are going to the US, China and some European markets.

Another major issue that’s being reported, is that there’s some dust in the lens and motherboard. That should definitely not be happening, and can cause the phone to produce worse images. These factories are supposed to be dust free, but it appears that this one is not.

Some are pointing to the fact that some of the iPhone 15 line is being in India this time around. Instead of 100% in China. The change in factory could be the cause for these issues. Hopefully they get them sorted out pretty quickly.

What to do if you have these issues

If you have any sort of issue with your new iPhone 15, make sure to take it back to Apple. Right now, everyone is within the return window, and definitely still has the manufacturers warranty. So Apple will need to fix these issues. What would likely happen is, Apple will just hand you a new phone to replace it.

Apple’s customer service is very good. And one of the advantages of Apple over its competitors like Google and Samsung, is that they have thousands of stores around the world. Which makes it easy to pop into the Genius Bar and get your phone taken care of.

Quality Assurance is pretty important for smartphones and really any tech product, but sometimes things can happen, and cause things to slip through the cracks. Hopefully Apple is looking into these issues and making changes to rectify the issues.


[ad_2]
Source link

The Android 14 QPR is no longer breaking Google Wallet

0
[ad_1]

Not too long ago, we covered the story surrounding an issue with the most recent Android beta version. It seemed that the update was breaking the Google Wallet app. However, according to 9To5Google, the Android 14 QPR is no longer messing up Google Wallet.

What was the issue?

For some reason, the latest beta version of Android 14 was raising a false alarm in Google Wallet. Before you can use Google Wallet, your phone’s software needs to meet the proper security standards. If you don’t have the proper security settings enabled or if you’re not using a legitimate version of Android, then you won’t be able to use Google Wallet. It doesn’t matter if you were able to use it on another phone with your account.

Well, after installing the update, people found that the app was telling them that their phones didn’t meet the proper security standards. This was happening even if their phones were previously cleared. That’s frustrating, especially for people who have gotten used to using contactless payments.

It seems that the Android 14 QPR isn’t messing up Google Wallet anymore

Google has caught wind of the issue, and it was quick to issue an update. The fix didn’t come via another Android update. Rather, this change came through a new Google System update, so it’s quick and painless. If you still can’t use your contactless payments, you may want to wait just a bit. The update might not have come to you just yet.

What is Google Wallet?

If you’re curious about what Google Wallet is, then here’s a quick rundown. It’s just as its name suggests, it’s a wallet that lives on your phone. You can store different types of cards on it that you can use in different real-world locations.

Google Wallet lets you store your credit/debit card on it to make payments. It also allows you to store reward cards and gift cards for different establishments. Google is also working on letting you store your passport, ID, and more on the app.

Download Google Wallet


[ad_2]
Source link