Active Exploitation Of Adobe ColdFusion Vulnerabilities Detected

0
[ad_1]

Months after patching the vulnerabilities, researchers still detected active exploitation of Adobe ColdFusion for malware attacks. Researchers warn users to patch their systems as soon as possible.

Adobe ColdFusion Vulnerabilities Under Attack

Researchers from Fortinet’s FortiGuard Labs have detected active exploitation of Adobe ColdFusion vulnerabilities that the tech giant has already patched.

As explained in their post, the researchers found multiple threat actors exploiting ColdFusion flaws to deploy malware. Briefly, they detected numerous probing activities using the tool “interacts, which otherwise facilitates the researchers in checking successful exploits. These activities linked back to various suspicious domains, hinting at malicious use of the tool, likely to identify vulnerable systems.

In the next step, the threat actors triggered shell sessions on vulnerable devices to access the computers. Once obtained, the attackers then deployed different malware on the target systems. These include

  • XMRig Miner – a cryptominer actively involved in various malicious campaigns where attackers try to exploit the victim machines’ resources for Monero mining.
  • Satan DDoS/Lucifer – a cryptojacking malware that can also trigger DDoS attacks. While it initially emerged as a Windows malware, Fortinet researchers noticed another malware variant involved in the attacks that targeted Linux too.
  • RudeMiner – another malware targeting cryptowallets that also conducts DDoS attacks.
  • BillGates/Setag backdoor – a potent backdoor allowing threat actors to hijack target devices.

The ColdFusion vulnerabilities exploited in these campaigns first made into the news in July this year as zero-day flaws when Adobe released urgent patches for the flaws following their active exploitation.

However, even after months since the patches were available, users seem ignorant about updating their systems with the latest versions.

Consequently, despite patching the vulnerabilities as actively exploited zero-days, the threat actors still appear successful in continuously exploiting the flaws for malware attacks. It now seems inevitable for all Adobe ColdFusion users to update their systems immediately to avoid falling prey to malware.

Let us know your thoughts in the comments.


[ad_2]
Source link
Chinese APT Slid Fake Signal and Telegram Apps onto Official App Stores

0
[ad_1]

Key Findings

  • Fake Signal and Telegram apps have been distributed through the Google Play Store and Samsung Galaxy Store.
  • The apps are designed to steal user data, including contact lists, call logs, and device information.
  • The apps were created by a Chinese APT known as GREF, while malicious code found in these apps is attributed to the BadBazaar malware.
  • The apps were initially targeted at users in China, but have since expanded to other countries.
  • If you have installed Signal Plus Messenger or FlyGram, you should remove them from your phone.
  • Before uninstalling the apps, make sure to unlink your Signal and Telegram accounts to prevent further data exposure.

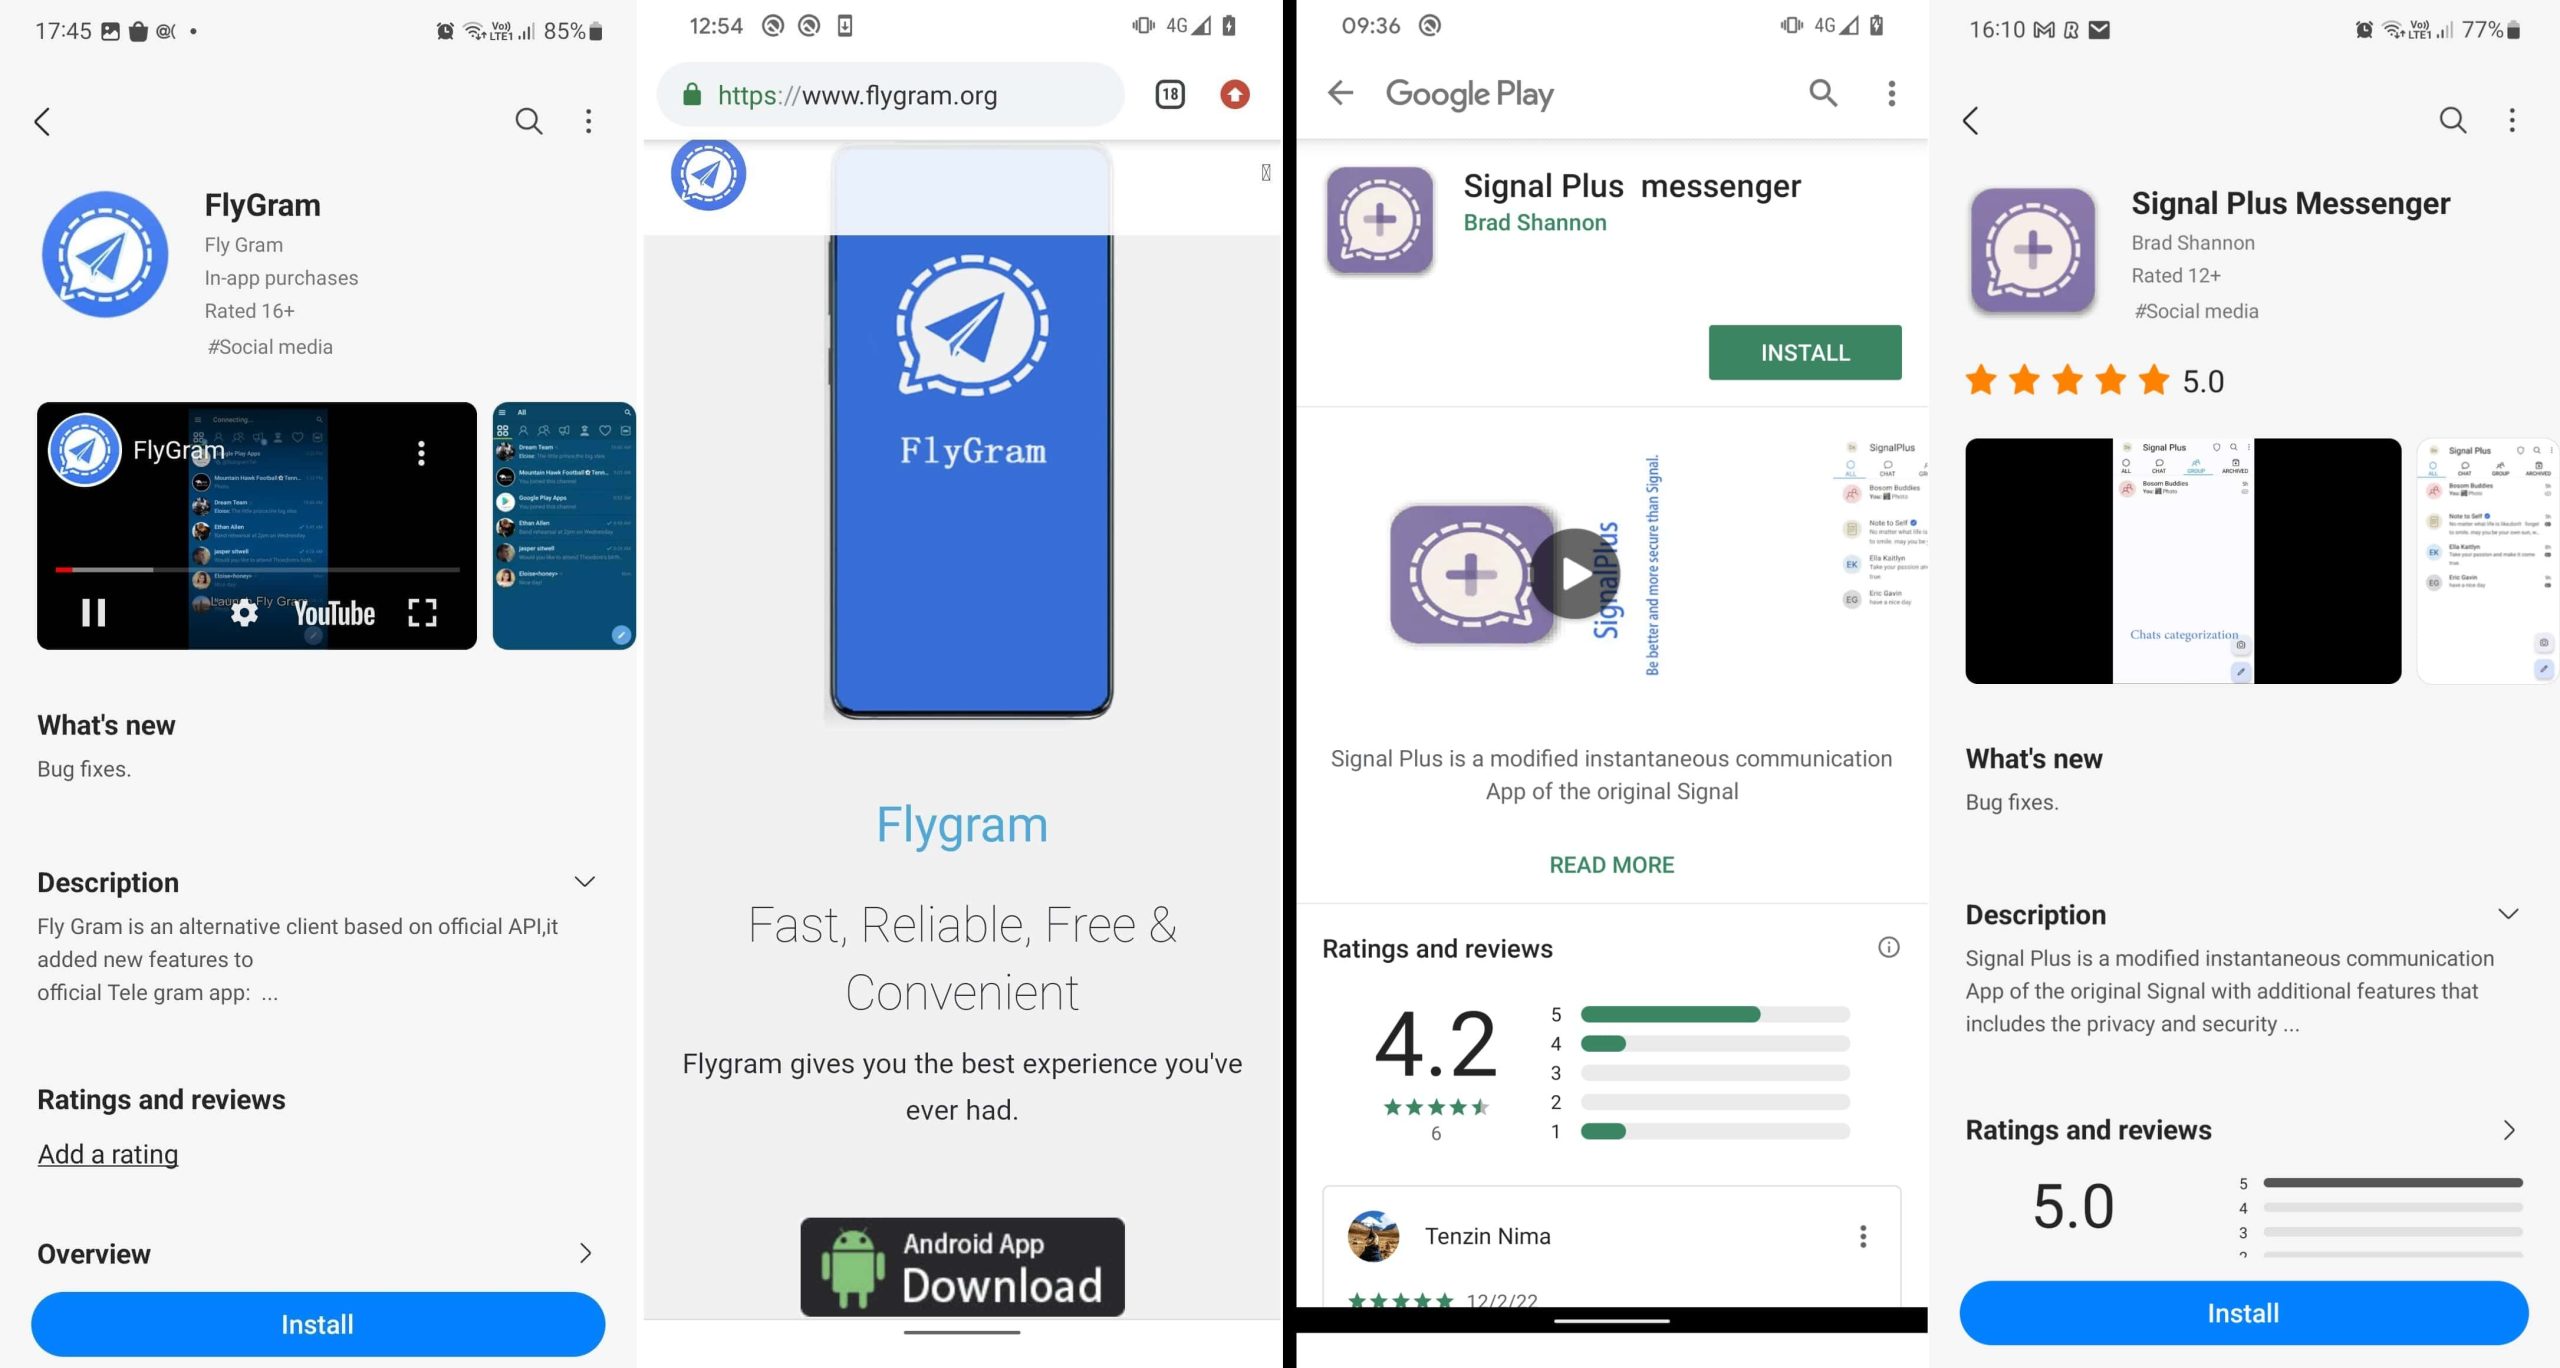
Cybersecurity researchers have warned of fake Signal and Telegram apps that have been distributed through the Google Play Store and Samsung Galaxy Store. The apps, which are called Signal Plus Messenger and FlyGram, are designed to steal user data, including contact lists, call logs, and device information.

Signal Plus Messenger, a bogus version of the popular Signal app, managed to slip under the radar for nine months in the Google Play Store. It garnered over 100 downloads before Google finally removed it from the app storefront.

FlyGram, developed by the same threat actor, followed a similar trajectory but was removed in 2021. The Slovak cybersecurity firm ESET has identified these apps as malicious versions of Signal and Telegram, designed to deliver malware to unsuspecting users.

Chinese APT Group Slid Signal and Telegram Apps onto Official App Stores
Fake Singnal and Telegram apps on Google Play Store and Samsung Galaxy Store (Image: ESET)

These fake apps were more than just imitations; they were sophisticated tools for cyber espionage. In a blog post, ESET researchers mentioned that the counterfeit Telegram app could harvest basic device information, sensitive data, Google accounts, and call logs. Additionally, it had a feature enabling it to back up data to a remote server controlled by the attacker.

The malicious Signal Plus app, on the other hand, could monitor both incoming and outgoing messages, transmitting them to a remote server for unauthorized access. To appear legitimate, dedicated websites were created for both apps, complete with links for direct installation from the Google Play Store.

The apps were created by a China-based hacking group known as GREF. GREF, also know as APT15, Ke3chang, Mirage, Vixen Panda and Playful Dragon, was also pointed out in July 2020 over the China’s insidious surveillance against Uyghurs with Android malware

Back in March 2018, these same threat actors were also found targeting a UK Government Contractor to steal military technology secrets. GREF is know the BadBazaar malware and in this campaign, the malicious code found in these apps is also attributed to the BadBazaar malware.

This should not be surprising, as another Chinese APT group, Smishing Triad, was recently reported to be carrying out a large-scale smishing campaign against users in the United States. This attack involved impersonating leading mail and delivery services.

Initially, users in China were the primary targets of these fake apps. However, the threat has since expanded to include users in Ukraine, Poland, the Netherlands, Spain, Portugal, Germany, Hong Kong, and the United States. 

If you’ve unwittingly installed Signal Plus Messenger or FlyGram, removing them from your phone is crucial. However, exercise caution when doing so. Before uninstalling these apps, make sure to unlink your Signal and Telegram accounts to prevent further data exposure. Google has labeled these apps as malicious and capable of stealing personal information.

Some quick tips for staying safe from fake apps

  • Only download apps from official app stores, such as the Google Play Store and the Apple App Store.
  • Be wary of apps that ask for more permissions than they need.
  • Read the reviews of an app before you download it.
  • Keep your apps updated.
  • Regularly scan your device for malware using a security app.
  1. Phishers Now Actively Automating Scams with Telegram
  2. Telegram and Discord Bots Delivering Infostealing Malware
  3. New MMRat Android Trojan Uses Fake App Stores for Bank Fraud
  4. Researcher Identifies Popular Swing VPN Android App as DDoS Botnet

[ad_2]
Source link

iPhone & Pixel enjoy a spa day in Google’s new ad

0
[ad_1]

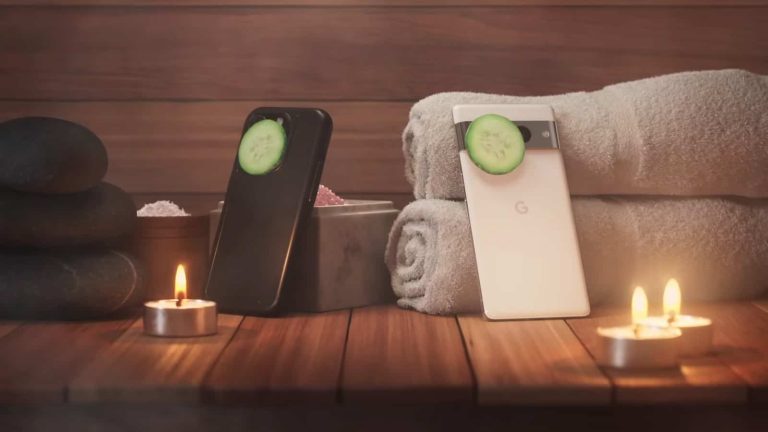
Google’s #BestFriendsForever ads have been very popular. Ads in which iPhone and Pixel are best friends have been keeping people entertained for a while now, and a new ad just dropped. In this ad, the iPhone and Pixel are enjoying a spa day together, actually.

iPhone & Pixel enjoy a spa day in Google latest #BestFriendsForever ad

First and foremost, the setting itself is quite funny. Both phones have a cucumber over their “eyes”, or should we say “cameras”. People usually do have them over their eyes, so… there you go.

During the video, an iPhone complains to a Pixel that “these launches just keep getting harder”. Then it goes down memory lane, to the very first event, which occurred 16 years ago. Then he admits that he’s a little sad.

That’s the point where an iPhone said: “Now it seems like every time I turn around, phones like you are doing stuff I can’t. Like unblurring old photos, answering unknown calls with AI, and live translating messages. It’s exhausting but I still have a few tricks up my sleeve”.

Following that, Pixel is curious, and he asks the iPhone what tricks? At that point, an iPhone indirectly says it’ll get Type-C charging, trying to keep it a mystery, but the Pixel managed to guess it, which shocks the iPhone.

Google took this opportunity to promote its Pixel 8 launch event

After all that, a tagline appears, and says: “Rest up for October 4”, which is the Pixel 8 launch event, of course. As a reminder, the iPhone 15 event takes place on September 12. Google is also expected to announce the Pixel Watch 2 and the new Pixel Buds Pro colors during that event, in addition to the Pixel 8 series.

This ad is yet another fun way to highlight some features of the Pixel phones, features that iPhones do not have. At the same time, Google kind of poked Apple for taking so long to introduce Type-C charging.

The ad has a duration of around a minute. In case you’re interested, it’s embedded below.


[ad_2]
Source link

Microsoft issues important Windows 11 update reminder

0
[ad_1]

Microsoft has issued a crucial reminder to all users currently running the original version of Windows 11, known as 21H2. The clock is ticking, and the original Windows 11 is about to lose its lifeline of support. In this comprehensive new update, there is a breakdown of the key details and why it’s essential to stay informed.

Neowin reported recently that Microsoft took action to ensure that users on Windows 11 21H2 including Home, Pro, and Pro variants, are well aware of the impending changes. The critical information revolves around the end of support, which Microsoft has set for October 10, 2023. After this date, Windows 11 21H2 will enter a phase where it will no longer receive updates, except for one final cumulative security update that Microsoft has scheduled for release on that exact day. This update will mark the end of an era for this particular Windows 11 version.

To provide further clarity, Microsoft explains, “The September 2023 non-security preview update will be the last optional release, and the October 2023 security update will be the last security release for Windows 11, version 21H2. Windows 11, version 22H2 will continue to receive security and optional releases.”

What this means is that Microsoft will soon prompt users currently on 21H2 to upgrade to version 22H2. Windows 11 itself will take the initiative to initiate this update either when the end date approaches or even a couple of months prior to it. So, if you are still using Windows 11 21H2, prepare for this forced upgrade in the near future.

Importance of this to Windows 11 Users

The importance of this transition cannot be overstated. Keeping your operating system up to date with the latest security fixes is paramount. Failing to do so could leave your PC vulnerable to cyberattacks, as hackers and opportunists actively target systems with known vulnerabilities.

As for the possibility of Windows 11 23H2 arriving soon and potentially diverting users from upgrading to 22H2, it seems rather unlikely. While the exact release date remains unconfirmed, most sources suggest a launch in the fourth quarter, possibly around October or later. The situation will become clearer as time progresses.


[ad_2]
Source link

WhatsApp is working on a new interface design with changed colors and chat filters

0
[ad_1]
WhatsApp often releases updates, and while some may be minor, like, for example, avatar reactions to status updates, the upcoming WhatsApp update seems to be quite big, as it involves interface redesign.

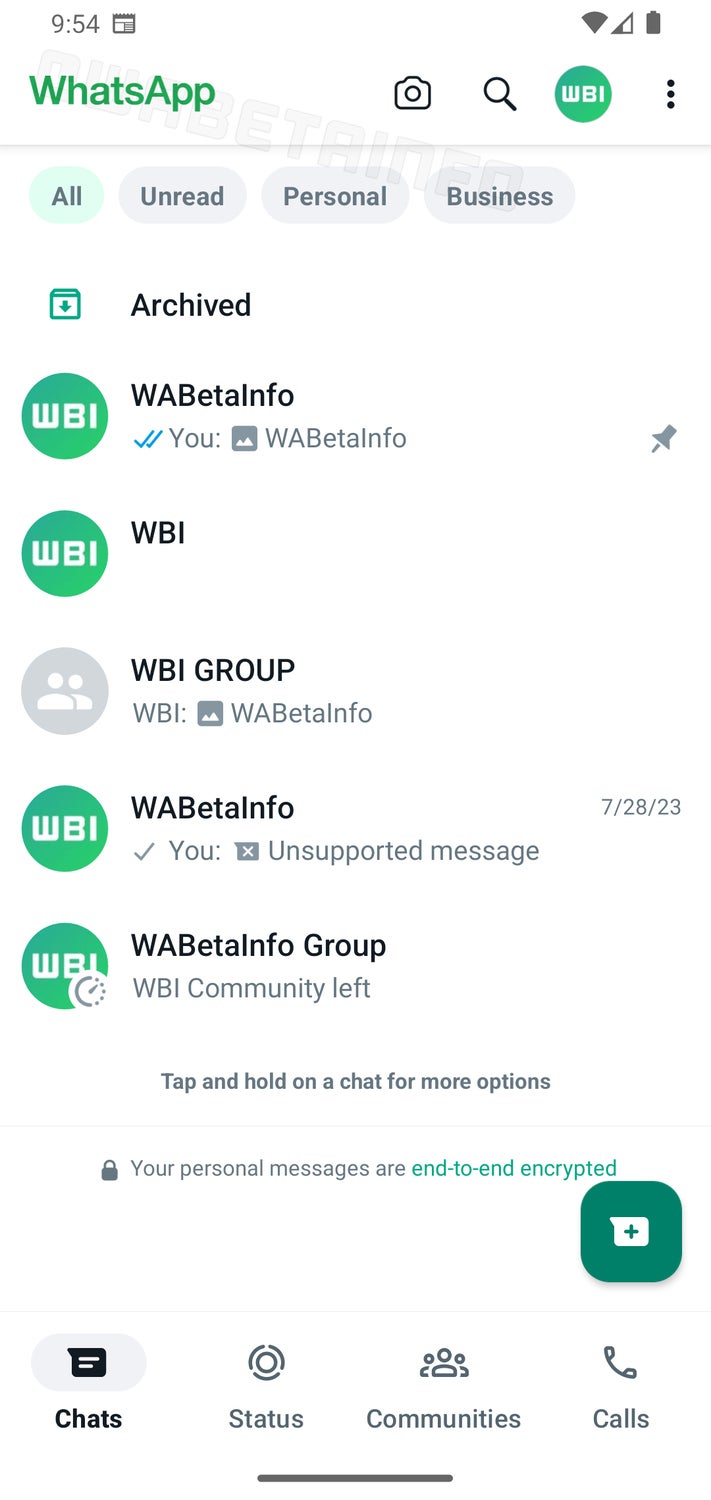
As reported by Wabetainfo, WhatsApp is in the process of redesigning its interface. The latest WhatsApp beta for Android, version 2.23.18.18, available on the Google Play Store, reveals several enhancements to the top app bar for a future app update. These enhancements include altering the background color, modifying the top bar navigation, and introducing chat filters.

Earlier in June, an alteration in the background color from green to white was observed, and it’s now evident that this change will be included in a future app update.
 

WhatsApp’s top bar is being redesigned to include an additional menu button to the right, next to your profile avatar. The background color of this area, as well as the top status bar, has transitioned from green to white. The WhatsApp logo on the app bar shifts its color from white to green.

Furthermore, WhatsApp is actively developing a new feature that will enable users to filter their conversations by sorting them into lists of unread messages, personal chats, or business discussions. This forthcoming feature aims to provide users with greater control when navigating their conversations.

It’s worth noting that similar changes are also in progress for WhatsApp on iOS. This indicates WhatsApp’s intent to align both apps with a similar interface and feature set, with both apps adhering to the Material Design 3 guidelines. Material Design 3 is the latest version of Google’s open-source design system that uses dynamic color, typography, motion, and components to create a more personalized and accessible user experience. Material 3 is designed to be used across a variety of platforms, including Android and iOS.

The new interface, featuring a white top app bar and a green app name, is currently in development and will be included in a future app update.


[ad_2]
Source link

Microsoft Says Goodbye to Wordpad, Snipping Tool, & Other Utilities

0
[ad_1]

Microsoft Windows announced deprecated features for Windows clients 11 and 10.

In this article, we’ll delve into the features and functionalities that are no longer actively developed for Windows clients. 

Please note that the information below is subject to change and might not encompass every affected feature or functionality.

WordPad (Deprecation Announced: September 1, 2023)

WordPad, the simple text editor, is no longer receiving updates and is slated for removal in a future Windows release. For rich text documents (.doc and .rtf), it’s recommended to use Microsoft Word, and for plain text documents (.txt), Windows Notepad is the way to go.

AllJoyn (Deprecation Announced: August 17, 2023)

Microsoft’s implementation of AllJoyn, a protocol for Internet of Things scenarios, has been deprecated. Customers seeking alternatives should refer to Iotivity.org for options like Iotivity Lite or Iotivity.

TLS 1.0 and 1.1 (Deprecation Announced: August 1, 2023)

In response to evolving security standards, TLS versions 1.0 and 1.1 will be disabled by default, starting with Windows 11 Insider Preview builds for September 2023. This shift encourages the adoption of modern protocols, enhancing Windows’ security posture.

Cortana in Windows (Deprecation Announced: June 2023)

Cortana, as a standalone app in Windows, is deprecated. However, Cortana remains available in various other forms, including Outlook mobile, Teams mobile, Microsoft Teams display, and Microsoft Teams rooms.

Update Compliance (Deprecation Announced: November 2022)

The cloud-based service Update Compliance for Windows clients is no longer under development. It’s been replaced by Windows Update for Business reports, accessible from the Azure portal.

BitLocker To Go Reader (Deprecation Announced: 21H1)

Reading BitLocker-protected removable drives from Windows XP or Windows Vista in later operating systems is deprecated. Associated items like ADMX policies and the BitLocker 2 Go Reader app may also no longer be available in future Windows releases.

The WMIC tool is deprecated in Windows 10, version 21H1, and the 21H1 General Availability Channel release of Windows Server. Windows PowerShell for WMI supersedes this command-line management tool.

Microsoft Edge (Deprecation Announced: 2004)

The legacy version of Microsoft Edge is no longer being developed.

OneSync Service Deprecation

The OneSync service, previously responsible for synchronizing data across the Mail, Calendar, and People apps, has changed. Microsoft integrated a sync engine directly into the Outlook app to enhance synchronization capabilities. This new engine offers the same robust data synchronization experience.

The Snipping Tool, a utility in Windows 10 for capturing screen content, has evolved with the introduction of Windows 10, version 1809. Microsoft introduced Snip & Sketch, a universal app that retains the screen-snipping functionality and brings additional features to the table.

This comprehensive list of deprecated features provides insights into Windows’ evolution and encourages users to adapt to newer alternatives. Keep an eye out for further updates and announcements as Windows evolves.

For more details on these deprecated features and additional information, visit Microsoft’s official documentation.

Keep informed about the latest Cyber Security News by following us on Google News, Linkedin, Twitter, and Facebook.


[ad_2]
Source link

HONOR Magic V2 global price hinted at by the CEO

0
[ad_1]

The HONOR Magic V2 was originally launched back in July, in China. The phone made its first global appearance at IFA 2023 in Berlin. It managed to attract a lot of attention, for a good reason, more on that soon. The phone did get shown off on a global scene, but the company did not share its price tag. Well, the company’s CEO did give out a hint as to what HONOR Magic V2 price we can expect, though.

The HONOR Magic V2 global printed hinted at by the company’s CEO

This did not happen during the event, though. We were there, and the pricing was not mentioned. GSM Arena notes that it happened “at the sidelines of the event”. George Zhao allegedly said that the Magic Vs’ price tag is a good reference for the Magic V2’s price.

So, the HONOR Magic Vs did launch globally back in February, with a price tag of €1,599 for the 12GB RAM + 512GB storage model. That is the only model that was announced, actually. So, the Magic V2 may carry the same price tag, or something similar to it.

We still do not know when it’s going to arrive, though. We’d like to believe it’ll happen at some point this year, but Q1 2024 is also a possibility considering the Magic Vs launch timeframe. On the other hand, the Magic Vs launched in China in November, and to global markets in February, so… based on that difference, the Magic V2 should arrive by the end of this year to global markets. We’ll see.

The phone’s design is in focus here, as it’s unbelievably thin & light

In any case, the Magic V2 is a true powerhouse, but the main attraction of this phone are not the specs. The main attraction is its design. The device feels like a regular phone when it’s folded, and you hold it. Not only because it’s 9.9mm thick when folded, but because it weighs 231 grams, which is the weight of some regular, non-folding flagships these days.

The device is fueled by the Snapdragon 8 Gen 2 SOC, while it also includes 16GB of LPDDR5X RAM and up to 1TB of UFS 4.0 flash storage. A 5,000mAh battery is also included, and the phone supports 66W wired charging.

A 50-megapixel main camera (OIS, Laser AF) is backed by a 50-megapixel ultrawide camera. A 20-megapixel telephoto camera (2.5x optical zoom, OIS) is also here. A side-facing fingerprint scanner is also a part of the package, and there are also two 120Hz displays on offer here. If you’d like to know more about the phone, click here.


[ad_2]
Source link

FBI Disrupts Qakbot (QBot) Malware Network – Frees Victim PCs

0
[ad_1]

After years of malicious activities, the notorious QakBot (or QBot) malware finally meets its fate as the FBI disrupts the botnet network. Besides taking down the botnet, FBI also cleaned infected systems from the malware.

FBI Disrupts Qakbot Network

Reportedly, the FBI has dismantled the notorious Qakbot malware network in a recent operation.

Qakbot, also known as QuakBot and QBot, is a known malware that has executed numerous malicious campaigns alongside facilitating other threat actors for various activities, especially ransomware attacks.

Announcing the achievement, FBI officials explained how they conducted a large-scale operation across six countries to take down the botnet. These countries include the United States, Germany, France, the Netherlands, Latvia, Romania, and the United Kingdom.

According to the details shared by the US Attorney’s Office, the FBI and the Dutch National Police officials discovered multiple compromised account credentials, which they shared with the HIBP website for public accessibility.

The Bureau, after obtaining the due permissions following their application, traced down the threat actors’ physical location, alongside mapping out the botnet’s infrastructure. Moreover, they also identified 20 cryptocurrency wallets associated with the botnet.

More details are available in the following announcement video.

FBI Removes The Malware From Infected Systems

Alongside disrupting the botnet activity, the FBI also confirmed freeing up the victim machines from the malware infection.

The FBI Director, Christopher Wray, stated that QBot’s victim list includes various firms across different regions. FBI could identify over 700,000 victim machines, over 200,000 of which existed within the US.

The victims ranged from financial institutions on the East Coast to a critical infrastructure government contractor in the Midwest to a medical device manufacturer on the West Coast.

Hence, to relieve all the infected systems that inadvertently constituted the botnet, the FBI redirected its traffic to its servers. It then released an uninstaller file to the QBot victim machines to uninstall the malware and prevent further infection.

While the threat from QBot is seemingly over, the risk never fades as more and more malware families keep emerging online to target victims. Therefore, all users, especially organizations, must remain vigilant to prevent similar threats.

Let us know your thoughts in the comments.


[ad_2]
Source link
Google Photos about to get huge update in photo quality

0
[ad_1]
Back in May, we told you that Google had announced Ultra HDR which would allow compatible apps on devices running Android 14 could show photos with a wider range of colors and tones. According to Forbes, based on hidden code strings found in the Google Photos app (version 51.0.561138754), it seems that Ultra HDR compatibility is about to come to the Google Photos app.
The new code strings found in Google Photos include phrases such as:
  • Ultra HDR disabled
  • UltraHdrPreviewFragment
  • EDITOR_ULTRA_HDR_PREVIEW
  • photos_mediadetails_details_ultra_hdr
Now it goes without saying (although we will anyway) that if Google Photos is adding support for Ultra HDR, a future update to Google’s camera app will have to give Android phones the capability to shoot in Ultra HDR. Perhaps the Pixel 8 series will have the first cameras able to shoot in Ultra-High Dynamic Range.
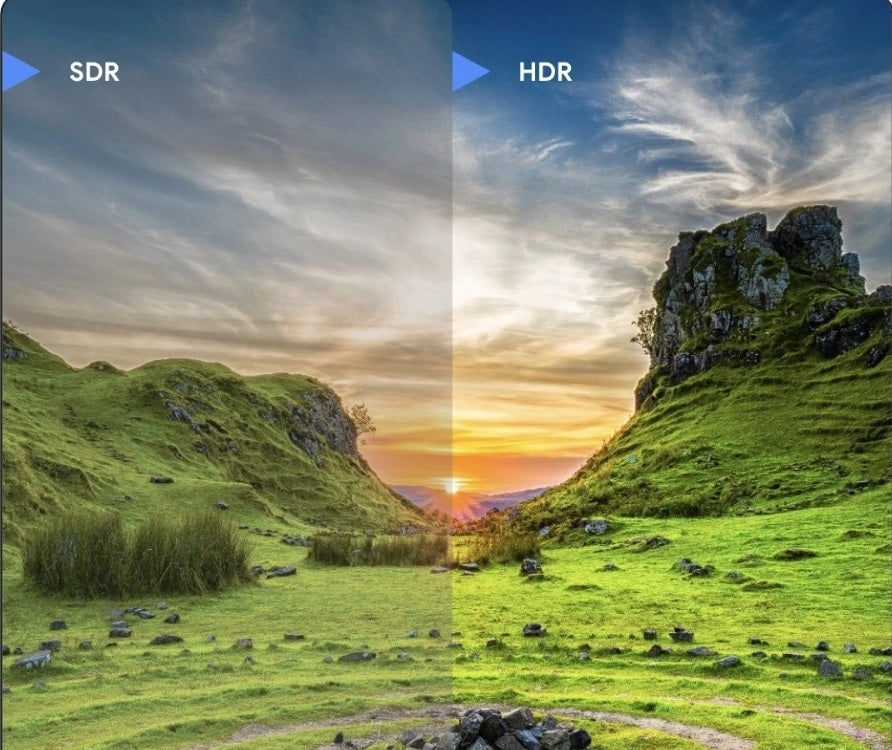
As we explained back in May, Ultra HDR adds an extra layer of information called a “gain map” to a standard JPEG image. The improvement in the quality of a photo in Ultra HD is said to be the same as watching television in standard SDR and improving it to Ultra HD. Since existing apps will be able to process and display Ultra HD pictures as though they were normal JPEGs, users can take photos using Ultra HD and share them without having to worry about whether other people could show them. 
Ultra HDR is backward compatible which means photos shot using this feature will still be able to appear on apps that don’t support the latest standard. However, on such apps the images will show up in SDR only. And you can look at the embedded image above to see the difference in photo quality.
While the code strings appear in the aforementioned version of the Google Photos app, Google will still have to activate the update to make the Google Photos app support Ultra HDR. We’d expect that update to quietly take place just a little before Google is expected to release the Pixel 8 and Pixel 8 Pro which is reportedly going to take place on October 11th.

[ad_2]
Source link