The Ultra HDR feature was discovered in Google Photos

0
[ad_1]

Android 14 will soon launch, and with it, we’re going to see some new and exciting features. If you use Google Photos, then you might like this news. According to Android Police, Google Photos is preparing to support Android 14’s Ultra HDR format.

Back in May, Google announced the Ultra HDR format slated to come with Android 14. This is a backward-compatible HDR format that will actually downgrade to SDR (standard dynamic range) when needed. Say, you take an HDR image, but you’re trying to view it on a non-HDR display. Well, the system will actually drop that down to SDR.

However, if you then view that same photo on an HDR screen, it will then snap to HDR. This is a way of letting apps knock images down to SDR without compressing them.

The Ultra HDR format was discovered in Google Photos

This is a standard that Google is planning on distributing to many apps, but it was first discovered in its first-party photo app. AssembleDebug discovered some code in Google Photos version 6.51.0.561138754. These notes read”

Ultra HDR disabled

UltraHdrPreviewFragment

EDITOR_ULTRA_HDR_PREVIEW

photos_mediadetails_details_ultra_hdr

These notes point to the Ultra HDR feature in the app. These are just a few lines for right now, so we’ll see more code for this feature come up as time goes on. As stated before, this is going to come out with Android 14, so there’s still some time to wait. Also, we don’t know if this feature will come out when Android 14 hits or if it will launch in a QPR. Only time will tell.

In other Google news

Google Chat, the company’s WhatsApp competitor, now has a new AI feature called Duet AI. This is a generative AI assistant that users can use to speed up their tasks. Since it uses generative AI, it’s able to create content, summarize documents, answer questions about Drive files, and more.

If you have a Workspace account, and you want to try it out, you can do so today.


[ad_2]
Source link

BadBazaar Malware Attacking Users Via Weaponized Apps

0
[ad_1]

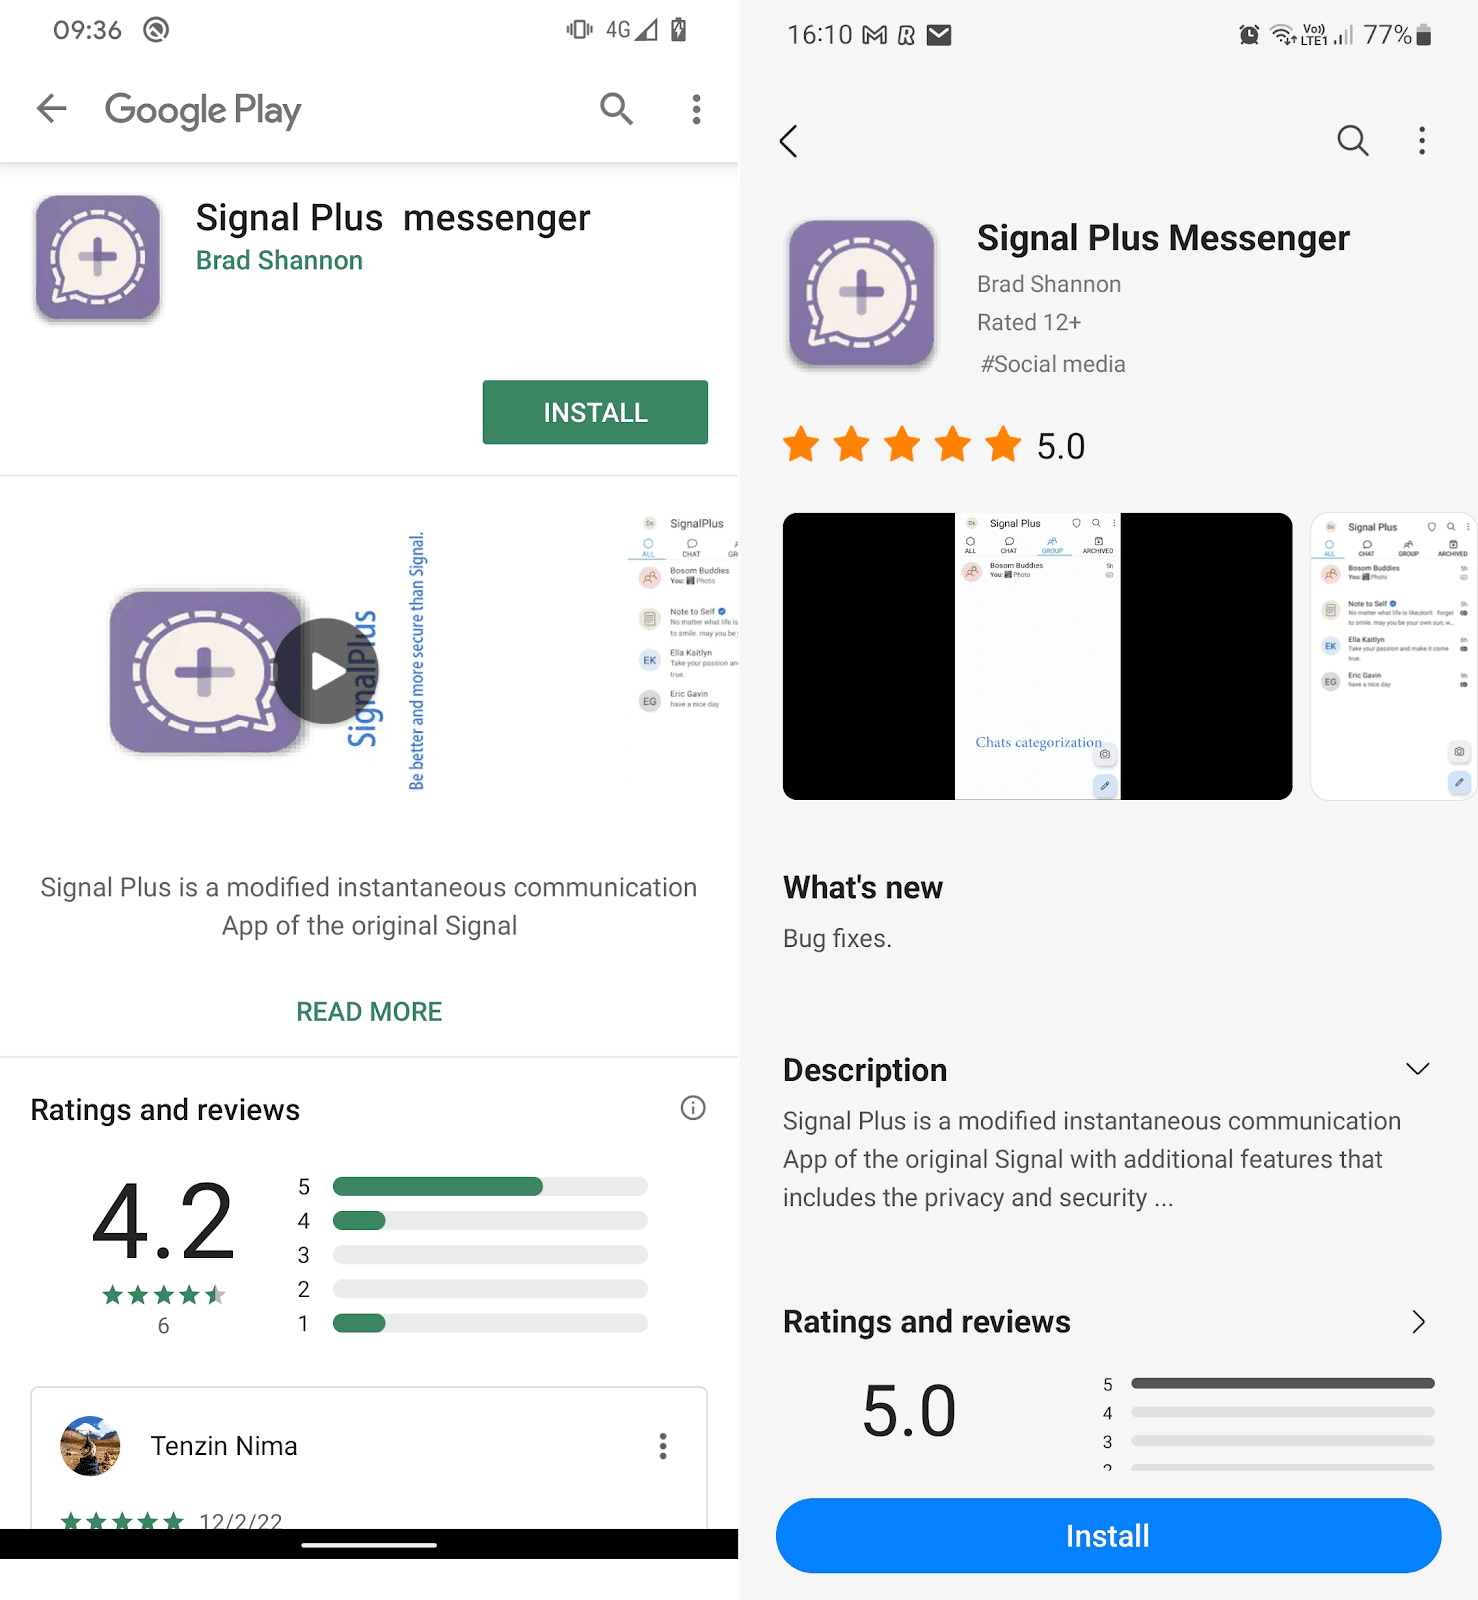
The Android BadBazaar malware is being distributed through the Google Play store, Samsung Galaxy Store, and dedicated websites mimicimg Signal Plus Messenger and FlyGram malicious applications.

These active campaigns are connected to the China-aligned APT organization known as GREF. Uyghurs and other Turkic ethnic minorities have historically been the target of the spyware known as BadBazaar.

The BadBazaar malware family has already been targeted, and the FlyGram malware was also observed being spread in a Uyghur Telegram channel.

According to ESET researchers, Germany, Poland, the U.S., Ukraine, Australia, Brazil, Denmark, Congo-Kinshasa, Hong Kong, Hungary, Lithuania, the Netherlands, Portugal, Singapore, Spain, and Yemen are the countries where victims have been found most often.

Specifics of the Attack

Researchers found active Android campaigns where malicious apps with the names Signal Plus Messenger and FlyGram were uploaded and disseminated through the Google Play store, Samsung Galaxy Store, and specific websites, imitating the Signal app (signalplus[.]org) and a Telegram alternative app (flygram[.]org).

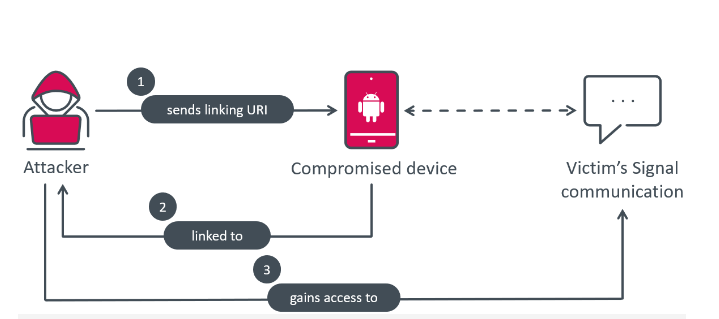
The primary objective of BadBazaar is to steal device information such as the contact list, call logs, and the list of installed applications, as well as to spy on Signal conversations by secretly attaching the victim’s Signal Plus Messenger app to the attacker’s mobile device.

BadBazaar Figure_01
Signal Plus Messenger is available on Google Play (left) and Samsung Galaxy Store (right)

FlyGram can specifically extract not just sensitive data like contact lists, phone logs, and a list of Google Accounts but also basic device information. 

Additionally, the malware can exfiltrate some Telegram-related data and settings; researchers say this data excludes the Telegram contact list, messages, and any other sensitive data.

“If users enable a specific FlyGram feature that allows them to back up and restore Telegram data to a remote server controlled by the attackers, the threat actor will have full access to these Telegram backups, not only the collected metadata,” according to report shared with Cyber Security News.

Linking the victim’s Signal communications to the attacker

Every newly created user account receives a special ID from the server. This ID has a sequential pattern, which shows that at least 13,953 FlyGram accounts have this feature turned on.

Similar device data and private information are gathered by Signal Plus Messenger, but its primary objective is to track the victim’s Signal communications.

It may obtain the Signal PIN that secures the Signal account and abuses the link device feature, which enables users to link Signal Desktop and Signal iPad to their phones.

“Malicious code from the BadBazaar family was hidden in trojanized Signal and Telegram apps, which should provide victims a working app experience (without reason to remove it) but with espionage happening in the background”, researchers said.

Keep informed about the latest Cyber Security News by following us on Google News, Linkedin, Twitter, and Facebook.


[ad_2]
Source link

A foldable that doesn’t feel foldable

0
[ad_1]

HONOR showed off its latest smartphones at IFA 2023 in Berlin. It brought over the HONOR Magic V2, which is its latest foldable flagship. That device launched in China in July, and this was its global debut of sorts. In addition to that, the HONOR V Purse concept was shown off, but that’s a story for another article, We’re here to focus on the HONOR Magic V2, as that’s the only phone I managed to get some hands-on time thus far. It’s probably more appealing to many of you, as it’s an actual product on the market at the moment.

It feels like a regular smartphone when folded

Having said that, I had high hopes for the design of this phone, and I wasn’t disappointed. The Magic V2 really does feel like a regular smartphone when you hold it. This thing is only 9.9mm thick (eco-leather model). The glass variant is 0.2mm thicker at 10.1mm. Either way, this is the thinnest book-style foldable on the market. It’s a lot thinner than the Galaxy Z Fold 5 (13.4mm), when folded, just to give you one example. It also trumps the Google Pixel Fold, the Huawei Mate X3, and even the Xiaomi MIX Fold 3.

When it’s folded, you can normally use its 6.43-inch display, and you won’t feel the extra thickness of a foldable. When unfolded, you get access to a large 7.92-inch panel. HONOR also fixed one of my display-related gripes with the HONOR Magic Vs, this phone’s successor. Both displays offer a 120Hz refresh rate now. On the Magic Vs, one of them stood at 90Hz. That is something you do notice when you jump between panels often.

Unfolding the phone is much easier now

The company even improved the unfolding experience of the device this time around. How? Well, the Magic Vs was not the easiest phone to unfold, as its two halves were too close together, and you had no proper point of pulling the phone apart. It wasn’t a bit issue, as you do get used to it, but that’s handled a lot better on the Magic V2. The hinge also feels better this time around, as HONOR rebuilt it entirely. The company used titanium in order to improve the hinge, and you can definitely feel that.

What about the crease? Well, it’s barely noticeable, especially in comparison to the Galaxy Z Fold 5. You can see it, but you won’t feel it under your finger nearly as much. That’s in line with some other Chinese smartphone OEMs. Needless to say, that’s great to see, as it does make a difference when using the device, it’s not only for aesthetics.

It’s also quite light for a book-style foldable

Many of you are probably wondering about its weight. Well, despite the fact it has a 5,000mAh battery, the Magic V2 weighs only 231 grams. That’s actually quite light compared to most other foldables in the same category. The Galaxy Z Fold 5 weighs 253 grams, while the Pixel Fold weighs 283 grams. You will feel that difference. As I said, this phone feels like a regular smartphone when it’s folded, and that goes for its weight too.

HONOR didn’t say anything about this phone’s global availability, but considering the attention it got here at IFA, and the fact that HONOR used the word ‘global’ a lot, it’s probably coming later this year.


[ad_2]
Source link

When is the best time of day to play mobile casino games?

0
[ad_1]

Casino gamers are always looking for a strategy to win despite them being games of chance. Does the time that you play mobile casino games influence increased chances of winning one of them?

There is no exact best time of day to play mobile casino games. It’s up to your preference and personal schedule as to when is the best time to play online casino games.

Log on to an online casino to take your chances when betting on your favorite games. Since casino games are won by chance, it does not matter what time of day you log on to a mobile casino game to play for real money.

To get a better night’s rest, maybe limit your casino gaming at night to end an hour or so before bedtime so you have time to wind down. Casino gaming in the morning or during your lunch break at work may be better options, so you have the best focus during your most productive hours.

For Progressive Jackpots, Play On Holidays or During the Summer

Even though there is no specific time formula to guarantee a win on casino games, there are special exceptions. For example, there may be a higher chance of hitting a progressive jackpot when more people are available to play at once.

Engage in progressive jackpot slots when it’s around popular commercial holidays. Think Easter, Thanksgiving, and Christmas as these are holidays when most people are not at work and more at home doing things they want to do such as playing mobile casino games.

Try your hand at playing progressive jackpot slot games during the summertime as well. Most people take a week’s or more vacation in the summer to enjoy the weather and time with their children as they are off of school. Plus, they’ll be casino gaming during their downtime.

Since progressive jackpots increase as more people bet on them over time, there is a larger chance of someone within the betting pool hitting the jackpot as everyone keeps playing. Holidays are when most people have free time to do what they like to do while hanging out with family and friends.

Even if you do not hit the jackpot yourself, you are entitled to a part of the winnings as long as you have placed any bet during the duration of the promised reward payout. However, betting what you can in a progressive jackpot can help it to gradually increase for your benefit if someone does hit it.

More People Play Casino Games At Night Time

Let’s face it. Mornings are hectic for casino gamers as they get ready for work. Afternoons are just as busy with finalizing the day’s responsibilities and errands after a work shift. Hence, most gamers prefer logging on to their mobile casino games during the evening hours when they’ve finished dinner and all their daytime tasks.

The highest traffic times for nighttime gaming on mobile casino games are 8 p.m. to 2 a.m. On weekdays, the start of this popular play time is around when families have finished cleaning up from dinner, their children have gone to bed, and adults start to have their time before they lay down for the night.

Plus, if you like playing craps online, doing so in the late weekday evening hours around midnight means it’ll be a bit easier to make your bets to be competitive with the high rollers. Be mindful that live dealer mobile casino games will be more crowded with bettors in the late-night weekend hours as more people are off work and don’t have to be up early the next morning.

Pros of Mobile Casino Games

Playing mobile casino games is a remote experience that can be enjoyed from anywhere you are. Whether commuting to work, lounging in your room, or visiting family and friends out of state, your favorite mobile casino games are accessible from the palm of your hand using a smartphone or tablet.

As long as you have a mobile connection or access to Wi-Fi, you can play mobile casino games on your device’s web browser or use the casino’s app on your device. Especially if you have an Android device with fast processing speeds and lots of data storage, you can access as many casino apps as you want for an optimal mobile casino gaming experience.

Mobile gaming is much more comfortable than playing casino games from your PC. Whereas you’d have to stay seated in front of your PC if playing on the desktop platform, you can choose to sit or lounge anywhere you want when doing mobile casino gaming because you only have to hold a smartphone or tablet in your two hands.

Cons of Mobile Casino Gaming

If you do not have a high-speed mobile connection or Wi-Fi access, you may have a subpar casino gaming experience. Be sure your connection is strong enough to prevent game lagging and to instantly see if you get a payout from a win or not.

You are limited to mobile casino gameplay for as long as you have a battery charge on your device. You’ll have to stop the fun if you do not have your device’s charger with you while on the go.

Because mobile casino gaming enhances its availability to players, it increases the chances of gambling addiction. Reassure this does not happen by budgeting your bankroll for the week and stop betting when you have run out of discretionary funds rather than depositing more from your needed funds.

Conclusion

Whatever time you want to play mobile casino games is up to you. There is no specific formula on what time of day to play casino games to increase your chances of winning. However, in some cases, playing at specific times of the year can enhance winning chances, but they do not guarantee them.

Was there a time that you hit a big win in a casino game? If so, what time of day did it happen? Share your experiences below!

[ad_2]
Source link

Hackers Exploit Openfire Vulnerability To Deploy Kinsing Malware

0
[ad_1]

The Kinsing malware has resurfaced with a new attack method that exploits the Openfire vulnerability tracked as CVE-2023-32315. A path traversal attack caused by this vulnerability allows an unauthorized user access to the Openfire setup environment.

Researchers from Aqua Nautilus report that the threat actor may upload malicious plugins and create a new admin user as a result of this. The attacker eventually has complete control of the server.

Openfire is a real-time collaboration (RTC) server that serves as a chat platform for transmitting instant messages over the XMPP (Extensible Messaging and Presence Protocol).

It was discovered in May of this year, intended to act as an internal IM server for businesses, supporting more than 50,000 concurrent users and giving them access to a secure channel for departmental interaction.

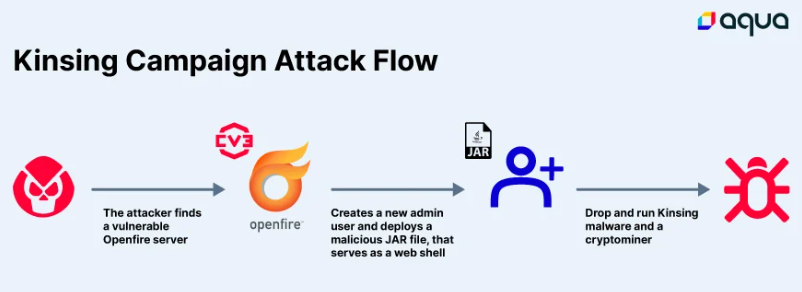
Kinsing Campaign Attack Flow

This Kinsing campaign makes use of the flaw, injects runtime Kinsing malware and a crypto miner, works to avoid detection, and seeks to establish persistence.

The threat actor checks the internet for Openfire servers, and once a server is identified, it is immediately checked to see if it is CVE-2023-32315 susceptible.

“In this campaign, the threat actor uses the vulnerability to create a new admin user and upload a plugin (cmd.jsp), which was designed to deploy the main payload – Kinsing malware”, researchers said.

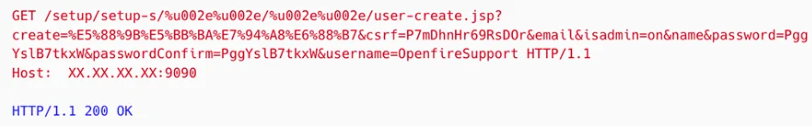
Request made by the attacker to create a new user on our Openfire server

The threat actor can then successfully finish the authentication procedure for the Openfire Administration Panel and acquire full access as an authenticated user once the new user has been successfully formed. 

Furthermore, the threat actor is given increased access within the system because the person has been added as an admin.

The threat actor then uploads a malicious plugin, enabling web shell commands on the server.

“The threat actor uploads a zip file which is a Metasploit exploit aimed to extend the cmd.jsp to enable HTTP requests at the threat actor’s disposal. This allows downloading the Kinsing malware which is hard coded in the plugin”, researchers explain.

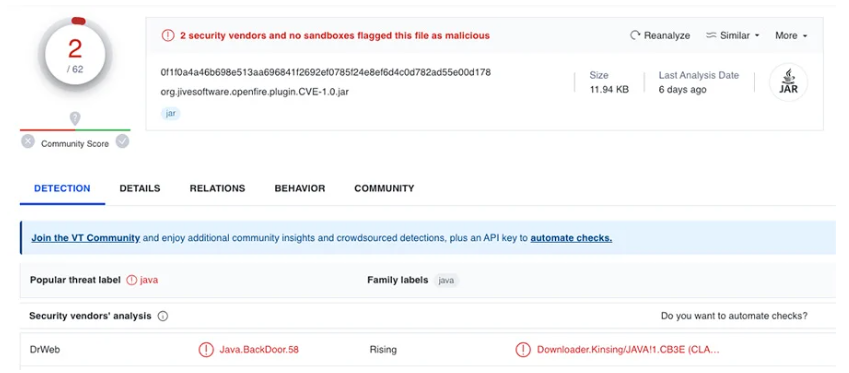
File flagged in VirusTotal (VT) as malicious (backdoor/Kinsing)

In less than two months, researchers have seen over a thousand attacks that take advantage of the Openfire vulnerability.

Recommendation

It is advisable to increase your understanding and give the protection of resources a higher priority.

  • Keep your environment up-to-date
  • Configure environments diligently
  • Perform extensive environmental scans for unknown threats.

Keep informed about the latest Cyber Security News by following us on Google News, Linkedin, Twitter, and Facebook.


[ad_2]
Source link

HONOR Magic V2 showcased on a global stage for the first time

0
[ad_1]

The HONOR Magic V2 was announced in China back in July. At that time, we had no idea whether the phone would become available in more markets, even though we expected it to happen. Well, today, HONOR showcased the Magic V2 on a global stage for the first time ever, hinting at what’s to come.

The HONOR Magic V2 gets showcased on the global stage

The phone got presented at IFA 2023 in Berlin. The company did not say anything about its availability outside of China, though, not yet. It seems like it is coming to more markets, though, we just don’t know when… yet.

HONOR’s latest foldable is the thinnest book-style foldable smartphone on the market, at least as far as inwards-folding foldables are concerned. It is only 9.9mm thick when folded, which makes it almost as thin as some regular smartphones. The Xiaomi MIX Fold 3 and Mate X3 come close to this, but not quite. The Magic V2 holds the crown at the moment.

It’s extremely thin, and actually not that heavy for what it is

On top of that, the phone is quite light for its size. It weighs 231 grams, which is not light per se, but considering the fact it’s a rather large foldables… it’s light. It’s all in the perspective of things. The Pixel Fold, for example, weighs over 280 grams.

How did HONOR manage to do this? Well, it had to rebuild its hinge from the ground up (it’s made out of titanium), and in addition to that, the company used a Silicon-Carbon-Dual-Battery setup here. They have an average thickness of 2.72mm, which is crazy thin in terms of such high battery capacities. Those two batteries form a combined battery capacity of 5,000mAh.

It has been tested to withstand more than 400,000 folds

HONOR also wanted to emphasize that the phone has been tested to withstand more than 400,000 folds, which means you can fold it 100 times a day for 10 years. That’s plenty, needless to say.

The device looks quite sleek, and it comes in vegan leather (9.9mm when folded) and glass (10.1mm when folded) variants. When unfolded, the phone is 4.8mm thick, which is also unbelievably thin.

The Snapdragon 8 Gen 2 is here to fuel the phone, while 16GB of LPDDR5X RAM is included, and up to 1TB of UFS 4.0 flash storage. A 50-megapixel main camera is backed by a 50-megapixel ultrawide camera, and 20-megapixel telephoto cameras. For the two front-facing cameras (one on each display), HONOR used 16-megapixel cameras.

The HONOR Magic V2 has two 120Hz displays

Two 120Hz OLED displays are included here too, and both support a 120Hz refresh rate. The main, foldable one measures 7.92 inches, while the cover panel measures 6.43 inches.

We’ll let you know as soon as we get more information regarding the device’s availability outside of China.


[ad_2]
Source link

New MMRAT Android Malware Runs Sneaky Campaigns

0
[ad_1]

Another threat for Android users has emerged online, emphasizing the need to use apps from legit sources only. Researchers have spotted a new Android malware, “MMRAT,” that targets devices via fake app stores.

MMRAT Android Malware Spreads Via Fake App Stores

Elaborating on the matter in a detailed post, researchers from Trend Micro urged Android users to remain vigilant.

As explained, Trend Micro researchers discovered a new Android malware, “MMRAT,” actively running malicious campaigns this year.

In brief, the threat actors target Android users via phishing websites impersonating fake app stores that deliver the malware “AndroidOS_MMRat.HRX” to the target devices.

Upon reaching the device, the malware requests necessary permissions from the victim to access various device components. Besides, it connects with its C&C server to transmit the data collected from the device.

MMRAT serves as a potent remote access trojan, giving the attackers unrestricted access to the victim’s devices. The malware can then perform various spying activities, including keylogging, screen recording, gathering data such as contacts, installed apps, network details, and even performing bank fraud. It exploits the device’s Android Accessibility service and MediaProjection API to execute these tasks.

Once the intended actions are completed, the malware sneakily uninstalls itself, leaving behind no traces. That’s how the malware has managed to stay under the radar despite running active campaigns.

The malware has been active since June 2023 and mainly targets Android users from Southeast Asia. Analyzing the campaign patterns also indicates that the threat actors behind this campaign specifically aim at a particular user group.

Given the stealthy execution of this malware, the researchers advise all Android users to remain careful for their devices’ security. At first, users must avoid downloading apps or interacting with app stores other than the official sources. Then, users must remain cautious when granting permissions to an app, especially if the app asks for seemingly unnecessary access. In addition, users must equip their devices with robust antimalware programs to repel known malware attacks.

Let us know your thoughts in the comments.


[ad_2]
Source link

HONOR turned a phone into a purse, meet the HONOR V Purse

0
[ad_1]

In addition to showcasing the HONOR Magic V2 globally for the first time, HONOR also showed off its new concept smartphone at IFA. The device in question is called the HONOR V Purse, and… well, it’s interesting, that’s for sure.

The HONOR V Purse is a fashion-forward concept device

HONOR says that this phone “reimagines a foldable smartphone as a wearable, fashion-forward purse, offering endless possibilities for style and self-expression”.

Are you confused? Well, that’s understandable, so let me explain. The HONOR V Purse is essentially an outwards-folding smartphone, to which you can attach a strap, basically. That way, you can turn it into a purse. That strap attaches to the phone’s hinge.

HONOR V Purse lifestyle image 2

HONOR also showed off various different straps for the device, including chains, features, and tassels, so that you can adapt the phone to any occasion. That’s not all, though. Its display also plays a part in the whole thing.

Its display also plays here, from the fashion standpoint

Several well-known designers partnered up to bring a series of designs for this phone’s AOD feature. In other words, HONOR utilizes the Always-On Display feature to change the style of the HONOR V Purse when you wear it.

HONOR will soon start inviting talent from all over the world to offer their designs. To utilize sensors like gyroscope and ambient light sensor to create something unique.

HONOR does plan to invite designers to pitch in with AOD designs

HONOR did not share any spec info when it comes to this device. That’s not surprising, as this is just a concept phone at this point. Based on the fact HONOR plans to invite designers to pitch in, however, it seems like it plans to shape this into an actual product.

When folded, on one side, there’s only a display, while most of the other side is also covered by the display. Aside from the display, you’ll also see the phone’s cameras, and a place to grab the phone.

The HONOR V Purse is definitely not aimed at just about anyone, though it’s an interesting concept. The fashion-centric announcement also fits well here.


[ad_2]
Source link

Kiss the iTunes Movie Trailers app goodbye… and say hello to the Apple TV app

0
[ad_1]

Win some, lose some. Today, one iOS application goes down for good – the iTunes Movie Trailers app. It has just received a terminal update and now instead of showing movie trailers (like it used to do since its inception in 2011), it prints a message that reads “Apple TV app is the new home of iTunes Movies Trailers” (via 9to5Mac).The relevant iTunes Movie Trailers (trailers.apple.com) website is gone, too – it is now redirecting users to the URL of the Apple TV website, landing at the trailers section.

That change is not unexpected. At the beginning of August, Apple introduced this same message (“Apple TV app is the new home of iTunes Movie Trailers”) on both the mobile application and on the website, preparing users for this present situation.

Upon opening the now-non-functional iTunes Movie Trailers app, users are not only informed where to go for their favorite flick teasers and trailers but there’s also a blue button at the bottom that says “Open” and serves as a getaway to the Apple TV app.

Tapping on it takes you directly to the “Movie and TV Trailers” section of the Apple TV app. But if you’re opening the same app from ground zero and wish to get to the trailers module, you can do that by going to the “Store” tab of the app, and then scrolling down to the “Watch the Latest Trailers” header.

Some users are not amused by the change: “I’m gonna miss it. I actually used it to add showtimes to my calendar since it would account for the exact time of the movie”, while some are nostalgic: “I remember going to the Apple movie trailer website to kill some time while my iPhone 3G was syncing with iTunes for the first time on launch day. Memories.” Others are completely on board with Apple’s decision and cheer the update, stating that the standalone app was archaic.


[ad_2]
Source link

Smishing Campaign Attack the US Citizens to Steal Payment Data

0
[ad_1]

Smishing is a type of cyberattack in which attackers use SMS (text messages) to trick individuals into revealing the following type of Personal and financial data or information:-

  • Passwords
  • Credit card numbers
  • Debit card numbers
  • Banking Credentials
  • Make download malicious software

In attacks like this, threat actors mimic government, bank, or postal agencies like USPS to seem legitimate, tricking victims into sharing payment info for fake fees.

Recently, cybersecurity researchers at RSecurity uncovered a new extensive smishing campaign dubbed “Smishing Triad,” in which threat actors are actively targeting the citizens of the United States.

Besides the US, researchers also unveiled that in earlier incidents, threat actors targeted victims from several other countries:-

  • The U.K.
  • Poland
  • Sweden
  • Italy
  • Indonesia
  • Japan

Entities Mimicked

Here below, we have mentioned all the entities that the operators of this campaign mimicked:-

  • The Royal Mail (UK)
  • New Zealand Postal Service (NZPOST)
  • Correos (Spain)
  • Postnord (Sweden)
  • Poste Italiane and the Italian Revenue Service (Agenzia delle Entrate)
  • J&T Express (Indonesia)
  • Poczta Polska (Poland)

USPS warns of summer package tracking text scams via SMS/iMessage, noting a surge in August with many attacker-registered a huge number of domains.

In this latest campaign, ‘Smishing Triad’  threat actors employed compromised Apple iCloud accounts to send malicious messages solely through iMessage.

This shift set it apart from the following previous scams, which relied on traditional SMS or calls:-

Furthermore, these perpetrators are supplying other cybercriminals with tailor-made ‘smishing kits,’ available for purchase through a group in Telegram.

On August 27, through iMessage, a victim received a fraudulent message from a compromised and threat actor-controlled Apple iCloud account (mjlozak@icloud[.]com).

Fraudulent message (Source – Resecurity)

Domains Identified

Resecurity found “Smishing Triad” using “.top” domains via NameSilo, which Cloudflare protects, and analyzing texts and DNS history the earlier domains were found to be registered in the following zones:-

Here below we have mentioned all the domains that were identified by the security experts:-

  • ususmx[.]top
  • ususnb[.]top
  • ususgs[.]top
  • ususcgh[.]top
  • uspoddp[.]top
  • uspsjh[.]top
  • ususnu[.]top
  • usushk[.]top
  • ususcsa[.]top
  • uspoky[.]top
  • usplve[.]top
  • ususcac[.]top
  • uspshhg[.]top
  • uspodad[.]top
  • uspogumb[.]top
  • uspsuiu[.]top
  • uspshhg[.]top
  • uspsuiu[.]top
  • uspskkq[.]top
  • ususuua[.]top
  • uspodaa[.]top
  • uspoadc[.]top
  • uspshhg[.]top
  • usplve[.]top
  • usushk[.]top
  • uspshhg[.]top
  • ususcgh[.]top
  • ususnu[.]top
  • ususnb[.]top
  • uspoddp[.]top
  • ususuua[.]top

Threat actors mimic the delivery failures with familiar routes that are sourced from hacked online shops. 

They often pinpoint the billing and location details of the victims, and besides this, some craftily accurate routes distract the victims from verifying the source.

Fake delivery failure (Source – Resecurity)

Smishing Triad targets ID theft and financial fraud, supplying custom kits to cybercriminals for $200/month. After crypto payment, they give activation codes and scripts for the following frameworks:-

  • ThinkPHP
  • Laravel
  • VueJS
  • React
  • Uniapp

Online shopping sites were also attacked by the operators of the ‘Smishing Triad,’ from which they steal customer data by injecting malicious code.

Indicators Of Compromise (IOCs)

  • wangduoyu[.]me
  • wangduoyu[.]shop
  • wangduoyu[.]site
  • poczta-polska[.]cc
  • ususmx[.]top
  • ususmx[.]top
  • ususnb[.]top
  • ususgs[.]top
  • ususcgh[.]top
  • uspoddp[.]top
  • uspsjh[.]top
  • ususnu[.]top
  • usushk[.]top
  • ususcsa[.]top
  • uspoky[.]top
  • usplve[.]top
  • ususcac[.]top
  • uspshhg[.]top
  • uspodad[.]top
  • uspogumb[.]top
  • uspsuiu[.]top
  • uspshhg[.]top
  • uspsuiu[.]top
  • uspskkq[.]top
  • ususuua[.]top
  • uspodaa[.]top
  • uspoadc[.]top
  • uspshhg[.]top
  • usplve[.]top
  • usushk[.]top
  • uspshhg[.]top
  • ususcgh[.]top
  • ususnu[.]top
  • ususnb[.]top
  • uspoddp[.]top
  • ususuua[.]top

Keep informed about the latest Cyber Security News by following us on Google News, Linkedin, Twitter, and Facebook.


[ad_2]
Source link