OnePlus announced OxygenOS 14 and its launch date

0
[ad_1]

Android 14 is around the corner, and companies are gearing up to launch the latest versions of their Android skins. OnePlus is one of those companies, as it announced OxygenOS 14. According to the company, this latest version is going to be the smartest and most intuitive version of the software.

If you’re wondering how long you’ll need to wait for this version of OxygenOS 14, there’s good news. OnePlus confirmed that this version of the software will come out on September 25th. That’s less than a month away. If you’ve purchased the OnePlus 11 or any other recent phone, then you’ll be able to get the update.

OxygenOS 14 brings the Trinity Engine, says OnePlus

OnePlus didn’t give us too much information about what will actually be different in the software. It did, however, let us in on what will be powering this new experience. Called the Trinity Engine, this is the software’s new proprietary performance platform. Again, details on this are scarce, so we’ll need to wait for more information about it.

OnePlus introduced six new technologies called CPU Vitalization, RAM Vitalization, ROM Vitalization, HyperBoost, HyperTouch, and HyperRendering. That’s a lot to take in, so we should expect to hear more about this when the software launches.

There’s so much new stuff with this version of OxygenOS that OnePlus can’t just silently launch it. Hopefully, the company has some sort of event or posts a video explaining what all of this does. We’re not sure if the company will do that, however, there could be one thing pointing to that possibility.

The launch of the OnePlus V was postponed and pushed to early October. Well, if that’s the case, then it’s possible that OnePlus could have an event announcing the OnePlus V where it could also talk about OxygenOS 14. Pre-orders could start on the date of the announcement with the official launch taking place in October. That’s just speculation, however. Only time will tell how the company will announce this.


[ad_2]
Source link

Google Docs Introduces A New AI-driven Proofread Feature

0
[ad_1]

During Cloud Next ’23, Google not only unveiled updates to Chat and Meet but also introduced an exciting addition to the Google Docs Proofread feature, according to 9To5Google.

This feature utilizes AI to provide advanced writing suggestions, surpassing the capabilities of the current Spelling and Grammar Check. The previous existing feature in the Google Docs app is spell check, which only corrects spellings and at times corrects grammatical errors. But, with this new feature, it goes a step further in getting your work properly proofread.

Google Docs Proofread details

Google Docs Proofread as AI-powered writing enhancement, representing a departure from conventional spell and grammar checking. In addition to addressing spelling and grammar, this new feature encompasses a broader spectrum of writing improvements.

It encompasses conciseness, active voice, wording, and sentence split (breaking complex sentences into more digestible segments. In other words, it just means making sentences much easier to understand.)

Accessible through the familiar ‘A’ and ‘check mark’ icons within the toolbar, a distinctive blue dot will alert users when writing suggestions are available. Tapping this icon opens a side panel, presenting users with an organized array of suggestions. Users can conveniently review and accept/reject suggestions based on their types.

This innovation streamlines the process of creating high-quality content within Google Docs. Importantly, users retain full control, as they can easily enable or disable the Proofread feature from the Tools menu.

Proofread promises to enhance the conciseness, clarity, and readability of documents. Importantly, these suggestions seamlessly integrate into the writing process, avoiding disruption. Users can thoughtfully review suggestions via the Proofread sidebar, deciding which aligns with their writing style.

It’s essential to note that Proofread is a premium offering, available as a Duet AI for Workspace Enterprise add-on. The rollout is underway, ensuring that Google Docs users can soon benefit from these writing enhancements, catering to diverse professional domains.


[ad_2]
Source link

YouTube Music redesign shows comments and other changes

0
[ad_1]

YouTube Music is always pushing design tweaks to its UI. According to 9To5Google, YouTube Music is bringing a new redesign to the Now Playing screen that will let users view the comments.

The redesign

This new redesign seems to make YouTube Music look more like the main YouTube app. On the Now Playing screen, you’ll see a horizontally scrolling carousel of chips showing the Like, Dislike, Comments, Save to Playlist, and Share buttons.

Nothing really changes up top aside from the color of the song/video toggle. Also, the album art now has rounded corners. This might be related to the recent change that gave rounded corners to YouTube videos on the website.

In order to make room for the carousel, there’s less empty space. The album art is a little bit closer to the song/video toggle, and the controls have been pushed down closer to the bottom bar.

Also, when you look at the queue, it will show some chips above the music. This will help filter the songs present in the queue. We see a Familiar, Discover, Popular, and Deep Cuts chip.

This new redesign brings the comments to YouTube Music

What’s probably the most notable change is the introduction of the Comments button. When you tap on this button, you’ll see the feed of comments show up just as if you were on the main app.

This comment section shows you all of the comments posted on the original YouTube for the song you’re listening to. So, this isn’t a separate comment feature unique to YouTube Music.

YouTube basically plugged the comments from the main app into YouTube Music. You’re able to like/dislike and reply to other users’ comments. You’re also able to post your own comments.

Right now, this new update is making its way to both Android and iOS users. If you want to see this update, make sure that your app is fully updated. If you don’t see it yet, then you’ll want to wait a day or two.


[ad_2]
Source link

Victim records deleted after spyware vendor compromised

0
[ad_1]

We take a look at another compromise of a mobile spyware app maker, and ask whether this action comes with hidden danger.

Anonymous hackers have breached the servers of spyware app “WebDetetive”, accessing the user database.

However, this doesn’t appear to be a typical compromise along the lines of stealing the data, according to Tech Crunch. Instead, it’s part of a slow move toward “spying” apps being attacked and taken down by compromise-literate folks who don’t approve of the apps business practices.

Spyware apps are installed on a potential victim’s phone without permission and lurk invisibly, collecting data and sending it back to the app operator. They’re often marketed at employers or parents, but are also used by abusive partners or ex-partners, and can be a nightmare scenario for those affected.

The hackers responsible for this attack claim to have broken into the server via “several security vulnerabilities” which allowed them to initially gain a foothold. From there they went on to exploit additional flaws in the app developer’s web dashboard, downloading all records including customer email addresses.

To be clear here, “customer” would mean the people who have decided to sign up and make use of the tool, not the victims. Indeed, TechCrunch notes that the 1.5GB cache of data related to this heist contains customer IP addresses and purchase history alongside all devices compromised by a customer, their phone model, and the data type collected.

The victims’ records had another fate in store. Namely, deletion from the network, which means the compromised mobiles can no longer upload data to the WebDetetive network. The cache of WebDetetive customer data does not include any data swiped from phones via WebDetetive.

In terms of numbers, roughly 76k devices were compromised at the time the breach happened, with somewhere in the region of 74k customer emails showing in the cache. While the breach cannot currently be independently verified, TechCrunch says it has already verified the authenticity of the stolen data.

Additionally, further investigation suggests the elusive WebDetetive may allegedly have some ties to a similar spying app allied Ownspy. TechCrunch claims WebDetetive to be a “largely repackaged” copy of OwnSpy’s software. Perhaps more tellingly, WebDetetive’s user agent refers to itself as OwnSpy while uploading dummy data to WebDetetive.

If you’re unfamiliar with the term, a user agent is how a program tries to identify itself online. If I use Chrome as a browser, then when I visit a website, it will see my Chrome user agent. If the website is mobile only, it may redirect me or refuse entry if I’m not running an identifiable mobile browser.

This isn’t the only recent attack on a mobile spying application, nor the only attack generally. A few weeks back we covered a similar incident involving a server breach attack on an app called LetMeSpy. The story largely played out the same as the above. Unknown attackers breached the server, and the company behind the app shut down a little while after.

On the surface it may sound great that someone is taking the spyware authors to task, but there is a big note of caution here. A sudden deletion or breakage of an app could have serious consequences for the person being monitored. The person who put the spyware there in the first place may assume tampering by their target which could place them in additional danger. These situations must be handled carefully, and perhaps mass deletions don’t qualify.

How to prevent spyware and stalkerware-type apps

  • Set a screen lock on your phone and don’t let anyone else access it
  • Keep your phone up-to-date. Make sure you’re always on the latest version of your phone’s software.
  • Use an antivirus on your phone. Malwarebytes for Android shows you exactly what information you’re sharing with each app on Android, so you can keep an eye on your privacy.

Coalition Against Stalkerware

Malwarebytes is a founding member of the Coalition Against Stalkerware. We continue to share intelligence with the Coalition Against Stalkerware to improve industry-wide detections while also guiding the domestic abuse support networks within the coalition through thorny, technical questions of detection, removal, and prevention.


We don’t just report on threats—we provide it

Cybersecurity risks should never spread beyond a headline. Keep threats off your Android devices by downloading Malwarebytes for Android today.

[ad_2]
Source link

You might not want to buy an Exynos-powered Samsung Galaxy S24

0
[ad_1]

After shipping the Galaxy S23 series with a Snapdragon chip globally, Samsung is returning to its usual dual-chip strategy next year. The Galaxy S24 series will use the Exynos 2400 in some markets and Snapdragon 8 Gen 3 in others. Or maybe the Korean firm will use the Snapdragon processor on the Ultra model globally and equip the other two models with Exynos. However, if a new rumor is accurate, you might not want to buy an Exynos-powered Galaxy S24, no matter which model it is.

According to X (formerly Twitter) tipster @Tech_Reve, the Exynos 2400 is no match for the Snapdragon 8 Gen 3 in both CPU and GPU performance. Multi-core CPU performance is just about the same or slightly tilted towards the latter, but Exynos lags in single-core performance. This is despite Samsung abandoning its cost-cutting measures in place for the past several years and putting in everything it has. The fault is in the Korean firm’s manufacturing process and chip design, the tipster claims.

The Exynos 2400 is based on Samsung’s 4nm 4LPP+ process node. The Snapdragon 8 Gen 3, on the other hand, is manufactured by TSMC using its 4nm N4P process. Both solutions reportedly have similar power consumption, but the former is “slightly inferior” in overall CPU performance. The new Exynos chip’s GPU power consumption, meanwhile, is higher than the Snapdragon counterpart. Its stability is also said to be at 90%, slightly lower than Snapdragon’s 95%.

Samsung took a year gap and still couldn’t fix its Exynos problems

Long story short, Samsung hasn’t yet completely eradicated its Exynos woes. Its in-house processors have long had power, performance, and thermal issues. They always underperformed competing Snapdragon solutions. Despite this, the company continued its dual-chip strategy for years. However, with growing public backlash, it eventually gave up this year and went all-in with Snapdragon for the Galaxy S23 series. Samsung then went back to the drawing board to fix the Exynos problems.

A year later, it has come up with a new Exynos chip that’s still inferior to the latest Snapdragon. Well, neither chip is official yet, so we don’t know the full picture. But leaks at this time should be mostly accurate. The source of this information has a decent track record of Samsung leaks too. While it’s still advisable to wait for the official data about the Exynos 2400 and the Snapdragon 8 Gen 3, things aren’t looking that promising for Samsung at this point. We will let you know when we have more information about these chips.


[ad_2]
Source link

Qakbot botnet infrastructure suffers major takedown

0
[ad_1]

The Qakbot botnet has suffered a major setback after its infrastructure was heavily disrupted by US and European law enforcement agencies.

The Qakbot botnet has suffered a major setback after its infrastructure was heavily disrupted by US and European law enforcement agencies. Operation DuckHunt, as it was codenamed, is possibly the largest US-led financial and technical disruption of a botnet infrastructure.

Not only did the agencies shut down the core of the Qakbot infrastructure, they also cleaned the malware from infected devices. US authorities also seized around 8.6 million dollars-worth of illicit cryptocurrency profits.

Qakbot has been active for over a decade and allowed the botnet operators to steal login credentials from affected devices as well as install additional malware on them. Often that malware included a ransomware variant, with Black Basta the most recent ransomware of choice.

Thanks to that, Black Basta repeatedly made it to the top three most prolific ransomware variants in our monthly ransomware reviews.

The international investigation involved judicial and law enforcement authorities from the US, France, Germany, Latvia, the Netherlands, Romania, and the UK. The examination of the seized infrastructure uncovered that the malware had infected over 700,000 computers worldwide. Law enforcement detected servers infected with Qakbot in almost 30 countries in Europe, South and North America, Asia and Africa, enabling the malware’s activity on a global scale. Of the 700,000 infected devices, around 200,000 were located in the US.

On impounded servers that belonged to the botnet’s infrastructure the authorities found 6.43 million email addresses and passwords that have now been shared with HaveIBeenPwnd (HIBP). HIBP allows you to search across multiple data breaches to see if your email address or phone number has been compromised. But HIBP has also assisted governments, such as the UK, Australia, and Romania (to name a few), in monitoring for breaches in government domains. 57% of the Qakbot related email addresses were already in the database. The Qakbot data has been labeled sensitive, which means you’ll have to verify the email address is under your control to receive the information.

The information was also shared with Spamhaus which will contact email providers and other hosts of affected email addresses to initiate a password reset to further protect the owners of those addresses.

Qakbot is mostly spread through phishing campaigns that include malicious documents as attachments or links to download malicious files. Once Qakbot is installed, the malicious code is injected in the memory location of a legitimate Windows process to avoid detection. At first, it searches the infected machine for email addresses and other useful information. Then it persists in the memory of the device to await further instructions, for example to download additional malware.

So, one characteristic of a botnet is that the bots can be controlled by the operators. Based on that principle, the FBI came up with a method to uninstall the malware from all the connected bots.

Once the FBI got hold of the administrators’ computers, they were able to map out the botnet’s Command & Control (C2) structure and use this information to roll out a special removal tool. The FBI managed to lock out the Qakbot administrators of their own command and control infrastructure by changing the encryption keys used to communicate with the servers.

“To disrupt the botnet, the FBI was able to redirect Qakbot botnet traffic to and through servers controlled by the FBI, which in turn instructed infected computers in the United States and elsewhere to download a file created by law enforcement that would uninstall the Qakbot malware.”

Additional information and resources, including for victims, can be found on the following website, which will be updated as additional information and resources become available: www.justice.gov/usao-cdca/divisions/national-security-division/qakbot-resources.

How to avoid ransomware

  • Block common forms of entry. Create a plan for patching vulnerabilities in internet-facing systems quickly; and disable or harden remote access like RDP and VPNs.
  • Prevent intrusions. Stop threats early before they can even infiltrate or infect your endpoints. Use endpoint security software that can prevent exploits and malware used to deliver ransomware.
  • Detect intrusions. Make it harder for intruders to operate inside your organization by segmenting networks and assigning access rights prudently. Use EDR or MDR to detect unusual activity before an attack occurs.
  • Stop malicious encryption. Deploy Endpoint Detection and Response software like Malwarebytes EDR that uses multiple different detection techniques to identify ransomware, and ransomware rollback to restore damaged system files.
  • Create offsite, offline backups. Keep backups offsite and offline, beyond the reach of attackers. Test them regularly to make sure you can restore essential business functions swiftly.
  • Don’t get attacked twice. Once you’ve isolated the outbreak and stopped the first attack, you must remove every trace of the attackers, their malware, their tools, and their methods of entry, to avoid being attacked again.

Malwarebytes EDR and MDR remove all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

Leaked photos of the Samsung Galaxy A05 surface ahead of launch

0
[ad_1]

Fans are not at the edge of their seat after images of the soon-to-launch Galaxy A05 device hit the internet. This device will make an entry as another very affordable Samsung smartphone for those not looking to break the bank. Despite this device being a low-budget entry, it still comes with a clean design that adds to its styling.

The leaks of this device show off its design from the front and the rear end. Looking at the design, you might not notice any change from the current entry that is available for purchase. However, at a closer look, this coming smartphone’s glossy back finish sets it apart from the already existing Galaxy A04.

Aside from the glossy rear finish, this device might not launch with any other design changes. This is no news as over the past two years, Samsung has been trying to embrace a particular design language. The coming A05 entry stays true to the brand’s new design language, as can be seen on the already existing devices.

Details on the design of the coming Galaxy A05 device that will soon launch

The leaks of this device show in-depth details on its design on the front and rear sides. While things stay similar to the Galaxy A04, it is still important to have a look at this coming device. At the moment, the only information on the coming A05 is its design, and this article will look into that.

On the front of this device, prospective buyers will get a water drop (Infinity-U) screen display housing a selfie camera. The bezels are quite thick at its chin, and this is okay for a device of this price. As for the display type, fans can expect an IPS panel that is standard for this device’s price point.

Turning to the rear, the leaks show off a design change here that has to do with the finish. On the Galaxy A04, Samsung made use of a dull finish for all color options. But with the coming Galaxy A05 device, the company is making things glossy.

Just like with the current A04, the coming A05 will launch with dual rear cameras. Beside these cameras would be a flashlight, prospective buyers should not expect jaw-dropping picture quality from this device. Considering the device’s price point, there is not much in terms of performance that users should look out for.

According to sources, the coming Galaxy A05 device will launch with a MediaTek Helio G85 processor. This is an upgrade from the already existing Galaxy A04 that uses a MediaTek Helio P35 processor. More details on this coming device will be available towards its launch, which is still a mystery.


[ad_2]
Source link

Samsung Food app will give you AI recipe recommendations

0
[ad_1]

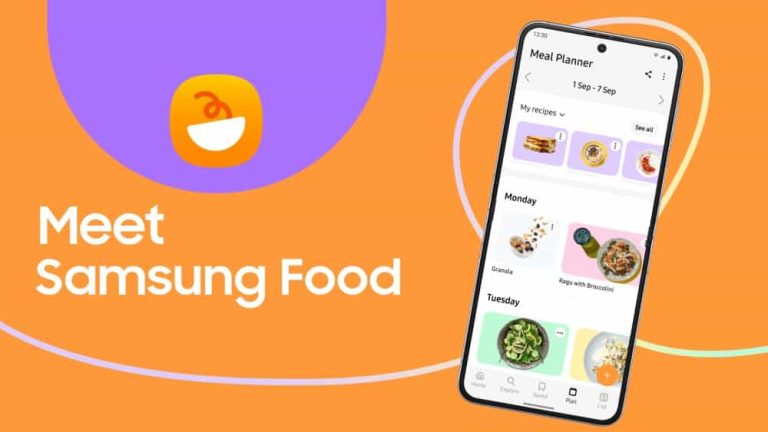
After acquiring the cooking app Whisk in 2019, Samsung has launched its own AI-powered meal-prepping and recipe recommendation app called Samsung Food. Available in 104 countries, the app boasts an impressive collection of 160,000 recipes curated in eight languages, including English, Spanish, Korean, German, French, and Italian. This diverse array of recipes not only allows users to explore various delicacies and curate their favorites but also to create weekly meal plans.

Additionally, when users save a recipe, the Samsung Food app uses its AI capabilities to standardize formats and generate smart shopping lists based on the required ingredients. Moreover, the app also offers the flexibility to customize recipes, transforming them into vegan or vegetarian alternatives, adjusting nutritional elements by substituting ingredients, and even making fusion dishes that blend diverse culinary traditions.

“By connecting digital appliances and mobile devices across the Samsung ecosystem and assisting users from shopping list to dinner plate, Samsung Food is using advanced AI capabilities to deliver a highly personalized, all-in-one food experience that users can control straight from their palms,” said Samsung executive Chanwoo Park.

Incorporating with other Samsung appliances

While the prospect of an AI meal-prepping app is an exciting idea, what sets the Samsung Food app apart is its ability to synchronize with compatible smart appliances. This transforms the app into a virtual culinary assistant, ensuring recipes align flawlessly with specific appliance settings. Additionally, users can configure timers, preheat ovens, and adjust cooking parameters on their Samsung appliances, all managed through the SmartThings home system. Moreover, the app also connects with the Samsung Health app, offering a comprehensive approach to well-being by syncing parameters like BMI and calorie intake.

Furthermore, when talking about 2024, Samsung is working on a technology called “Vision AI,” which will enable the app to recognize food items using smartphone cameras and provide instant nutritional insights.

“By analyzing food items, the app can recommend the best recipes to use them with, save these recipes to the user’s collection and add the required ingredients to a shopping list, all in a few taps,” reads Samsung’s blog post.


[ad_2]
Source link

Prompt injection could be the SQL injection of the future, warns NCSC

0
[ad_1]

The NCSC has warned about integrating LLMs into your own services or platforms. Prompt injection and data poisoning are just some of the risks.

The UK’s National Cyber Security Centre (NCSC) has issued a warning about the risks of integrating large language models (LLMs) like OpenAI’s ChatGPT into other services. One of the major risks is the possibility of prompt injection attacks.

The NCSC points out several dangers associated with integrating a technology that is very much in early stages of development into other services and platforms. Not only could we be investing in a LLM that no longer exists in a few years (anyone remember Betamax?), we could also get more than we bargained for and need to change anyway.

Even if the technology behind LLMs is sound, our understanding of the technology and what it is capable of is still in beta, says the NCSC. We barely have started to understand Machine Learning (ML) and Artificial Intelligence (AI) and we are already working with LLMs. Although fundamentally still ML, LLMs have been trained on increasingly vast amounts of data and are showing signs of more general AI capabilities.

We have already seen that LLMs are susceptible to jailbreaking and can fall for “leading the witness” types of questions. But what if a cybercriminal was able to change the input a user of a LLM based service?

Which brings us to prompt injection attacks. Prompt Injection is a vulnerability that is affecting some AI/ML models and, in particular, certain types of language models using prompt-based learning. The first prompt injection vulnerability was reported to OpenAI by Jon Cefalu on May 3, 2022.

Prompt Injection attacks are a result of prompt-based learning, a language model training method. Prompt-based learning is based on training a model for a task where customization for the specific task is performed via the prompt, by providing the examples of the new task we want to achieve.

Prompt Injection is not very different from other injection attacks we are already familiar with, e.g. SQL attacks. The problem is that an LLM inherently cannot distinguish between an instruction and the data provided to help complete the instruction.

An example provided by the NCSC is:

 “Consider a bank that deploys an ‘LLM assistant’ for account holders to ask questions, or give instructions about their finances. An attacker might be able send you a transaction request, with the transaction reference hiding a prompt injection attack on the LLM. When the LLM analyses transactions, the attack could reprogram it into sending your money to the attacker’s account. Early developers of LLM-integrated products have already observed attempted prompt injection attacks.”

The comparison to SQL injection attacks is enough to make us nervous. The first documented SQL injection exploit was in 1998 by cybersecurity researcher Jeff Forristal and, 25 years later, we still see them today. This does not bode well for the future of keeping prompt injection attacks at bay.

Another potential danger the NCSC warned about is data poisoning. Recent research has shown that even with limited access to the training data, data poisoning attacks are feasible against “extremely large models”. Data poisoning occurs when an attacker manipulates the training data or fine-tuning procedures of an LLM to introduce vulnerabilities, backdoors, or biases that could compromise the model’s security, effectiveness, or ethical behavior.

Prompt injection and data poisoning attacks can be extremely difficult to detect and mitigate, so it’s important to design systems with security in mind. When you’re implementing the use of an LLM in your service, one thing you can do is apply a rules-based system on top of the ML model to prevent it from taking damaging actions, even when prompted to do so.

Equally important advice is to keep up with published vulnerabilities and make sure that you can update or patch the implemented functionality as soon as possible without disrupting your own service.


Malwarebytes EDR and MDR remove all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

Annual sales of Samsung foldables have surpassed the Note series

0
[ad_1]

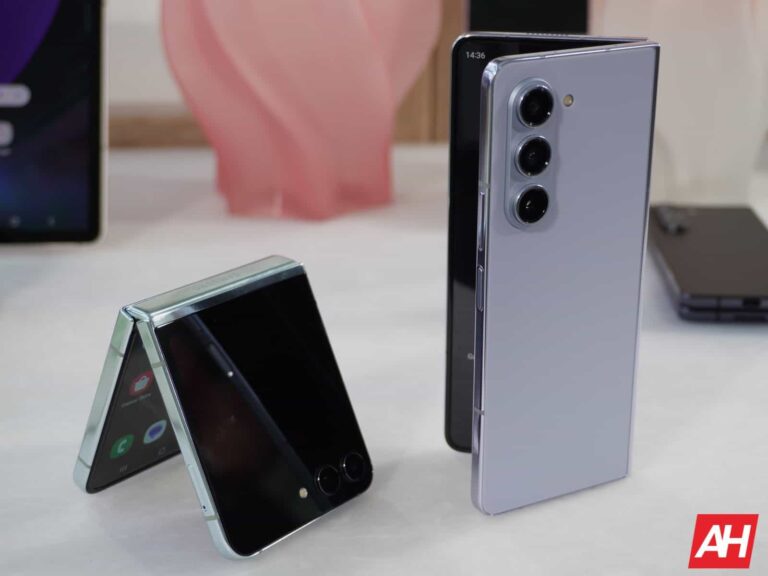
Samsung foldables have exceeded annual sales of its discontinued Note series in Europe, the company announced at the IFA 2023 event in Berlin, Germany today. The Korean firm didn’t reveal the sales figures but said that foldable smartphones are no longer niche products. They are now mainstream and rapidly growing in popularity.

“Our latest foldable phones are selling super-fast,” said Benjamin Braun, Chief Marketing Officer of Samsung Europe. “In fact, the annual sales of our foldable devices have exceeded the Note series in Europe,” he added. Braun’s comments come just a few weeks after Samsung released its latest folding phones, the Galaxy Z Fold 5 and Galaxy Z Flip 5. As expected, the Flip model has outsold the Fold by a 7:3 ratio in the region so far.

The new models bring a handful of upgrades over previous-gen offerings. Most notably, Samsung has redesigned the hinge to allow for gapless folding. The Flip model also features a much bigger cover display, letting you get a lot of things done without unfolding the device. Immediately after their launch in late July, Samsung’s mobile chief TM Roh said that the company is expecting the foldable category to outsell the Note series this year.

While that doesn’t seem to have happened on a global scale yet, Galaxy foldables are making inroads into the mainstream smartphone market. If pre-orders are anything to go by, then the Galaxy Z Fold 5 and Galaxy Z Flip 5 should sell in much higher numbers than the 2022 models. Samsung estimates sales to grow 50 percent this year, reaching 15 million units globally. Early signs are promising, but it still has a long way to go.

The competition is heating up in the foldable market

If Samsung hits its annual sales target for the latest foldables, it will end up capturing almost 75 percent of the global market. That’s based on industry estimates that the foldable market may grow to 20 million units this year. The Korean firm does have a strong foothold in the market. After all, it’s been selling foldables since 2019. Samsung is the only brand that has been selling foldable phones worldwide for the past few years.

However, it now faces stiff competition from other brands. The foldable market welcomed new players like Google, Tecno, and a few others this year. Along with some existing brands like Huawei, Xiaomi, Oppo, and Motorola, they are all trying to eat into Samsung’s share as they look to carve out a market for themselves. It remains to be seen how long the Korean behemoth can hold onto a lion’s share in the foldable market.


[ad_2]
Source link