The new X job search feature might threaten LinkedIn’s business

0
[ad_1]

In a bid to build the “everything platform,” the coming X job search feature aims to get a good chunk of LinkedIn’s business. The coming of this feature to the platform is becoming ever clearer, as a new post from Elon Musk points out. From the post, it is not only clear that he is planning to bring a job listing feature to the social media platform, but he also wants a bite of LinkedIn’s cake.

In the post, Elon points out how cringe he feels making use of job applicants’ LinkedIn links. Instead of making use of these links sent to him by others, he says that he prefers them to share their resume or bio via email. The billionaire now has his attention on bringing job applicants over to X instead, hence standing as a competition to LinkedIn.

However, the plan of Elon Musk to bring a new X job feature is not a new one, as the platform has already been working on it. A few months ago, news about this coming feature hit the Internet, proving that X is evolving into an everything platform. Here are the details on this future feature that will be making its way to Elon Musk’s social media platform.

Laski will help bring the X job search feature to users of the platform in the coming months

A few months ago, X purchased a firm known as Laskie to help them build job features into their platform. Laskie on its own ran a job listing firm before X purchased them, and this gave them the idea to work on this feature. Already, this feature has been tested by a few organizations using the social media app, but it is not yet available for public usage.

According to an organization that had access to this feature, it is part of the $1,000 monthly verification X premium package. In the coming weeks, this feature might resurface, allowing X users to access it via their accounts. With this, they would be able to list their personal work information and history for prospective employers to see once they apply for a job via the X platform.

In an official statement, X confirms that they might need the personal information of those who intend to use this feature. With this information, the platform would be able to recommend jobs to users once available. These jobs would be tailored to the qualifications of the users, as seen in the personal information that X might require.

Now, this might sound a lot like LinkedIn to you, and that’s what it aims to sound like. With this feature, some Twitter users might drop using LinkedIn entirely while searching for jobs and employment opportunities. Another vital point to note is that this coming X job search feature will also need user biometric data.

Once available, this feature sits behind the Blue subscription plan, hence not being accessible to all. More details on this job search feature will become available in the coming weeks. Would you make use of this feature while searching for jobs online?


[ad_2]
Source link
Cigna Health Data Leak: 17 Billion Records Exposed

0
[ad_1]

Key Findings

  • A non-password-protected database containing over 17 billion records was exposed.
  • The leaked records included healthcare provider information, such as names, addresses, and contact numbers.
  • The leaked records also included negotiated rates for medical procedures.
  • The data leak was caused by a security lapse at Cigna Health.
  • Cigna Health has taken steps to secure the database and is investigating the incident.

Cybersecurity researcher Jeremiah Fowler has unearthed a concerning incident involving a non-password-protected database containing over a staggering 17 billion records. The extensive records were traced back to Cigna Health, a major player in the health insurance industry. The company’s effort to bolster transparency inadvertently led to this massive data leak, as disclosed by Fowler.

The leaked records, amounting to a colossal 6.35 terabytes, primarily consisted of healthcare provider information. Details included the names of hospitals and doctors, location addresses, contact numbers, and various identification numbers such as the National Provider Identifier (NPI). Importantly, these records also disclosed negotiated rates for medical procedures. However, it is essential to clarify that the exposed data did not encompass customer or patient information.

Cigna Health Data Leak: 17 Billion Records Exposed
Screenshot from the leaked records (Jeremiah Fowler)

Fowler’s discovery prompted a swift response from Cigna, acknowledging the security lapse and taking immediate measures to secure the vulnerable database from public access. Cigna defended its stance by citing its Transparency in Coverage program, which adheres to federal regulations in place since 2022.

Notably, the information contained within the database was intended for public access due to regulatory requirements. However, the lack of proper security measures posed potential risks to Cigna’s broader internal storage network.

The exposed database, which offered an unprecedented behind-the-scenes look into Cigna Health, detailed the company’s operations spanning all 50 states in the United States. Cigna Health offers an array of health insurance plans, catering to individuals, families, employers, and various government programs. 

The database’s structure was logically organized and easily searchable, revealing provider records alongside Current Procedural Terminology (CPT) codes. Under the Affordable Care Act, health insurers are mandated to disclose negotiated rates publicly, emphasizing transparency. Despite the potential benefits of this disclosure, the size and complexity of these data files could prove challenging for non-technical individuals to navigate effectively.

Security concerns regarding the leaked data revolve around the potential misuse of National Provider Identifier (NPI) numbers, which serve as unique identifications for healthcare providers. While the leaked data did not indicate any misconduct by Cigna, NPIs have been exploited in the past for fraudulent activities such as Medicare and Medicaid scams and non-password-protected databases could expose companies to ransomware attacks.

  1. Cybersecurity firm exposes 5 billion data breach records
  2. DreamHost hosting firm exposed almost a billion sensitive records
  3. 9,517 unsecured databases identified with 10 billion records globally
  4. Online trading broker FBS exposes 20TB of data with 16 billion records
  5. Brazilian marketplace integrator Hariexpress exposed 1.75 billion records

[ad_2]
Source link

Verizon makes it easier to block spam email texts

0
[ad_1]

Verizon is making it easier to block email-to-text messages. You can now get rid of those pesky texts coming from unknown or spammy email addresses by simply sending a message. You have to send the text “Off” to 4040 and you will no longer receive text messages from emails.

According to Verizon, more than 80 percent of email-to-text messages received by its customers are spam. This is worrying data, and the carrier wants to safeguard consumers from potential harm. It already allows users to turn email-to-text off by logging into their My Verizon account.

However, not everyone seems to be using this feature. Verizon is now giving them an alternate and easier way to block email-to-text messages directly from their phone. If you are receiving those annoying texts, you might want to send a message to 4040 and block all such spammy texts.

It’s worth noting that turning email-to-text off will block all text messages coming from email addresses. This means you won’t receive legitimate messages from emails either. If you frequently receive such messages, you might be better off keeping email-to-text enabled for your Verizon number.

Thankfully, it’s equally easier to enable it. Simply send the text “On” to 4040 and you will once again start receiving email-to-text messages. If you’re not sure whether you have the feature enabled or disabled, you can check the status by sending the text “Status” to 4040.

Depending on your status, you will receive one of the following messages: “Email-to-Text is blocked for your phone number. Text “on”  to 4040 to allow.” or “Email-to-Text has been allowed for your phone number. Text “off” to 4040 to block.” You can act accordingly. You can also send “Help” to 4040 to receive instructions on how to enable/disable email-to-text.

Verizon gives users more weapons to fight spam email texts

US wireless carriers including Verizon offer various tools to help their customers fight spammers. This is on top of the protective measures implemented by carriers themselves. Verizon’s call filter feature already alerts you about potential spam calls so you can avoid picking them up. It has now made blocking email-to-text messages easier

“Our pursuit to eliminate the annoyance of unwanted calls and texts improves customer experiences and satisfaction. Our efforts have empowered customers with the knowledge and the tools that have boosted their confidence in knowing which calls and texts are worth their time,” Verizon said in a press release. You can always report spam texts by forwarding them to 7726.


[ad_2]
Source link

Google Chat gets new redesign and Duet AI assistant

0
[ad_1]

Google’s messaging platform has undergone numerous changes and iterations over time. Now, in a recent development, the company has announced a slew of new features for Google Chat that draw parallels with Slack and Microsoft Teams, along with a new Duet AI collaboration tool.

Announced through the company’s Workspace blog, Google Chat will now feature a new Duet AI, which allows users to search for information, ask questions related to their Drive files and emails, and even receive concise summaries of documents and conversations. Additionally, Duet AI can also generate responses for conversations, reducing the need for manual interactions with colleagues.

Moreover, the app is receiving a substantial redesign that incorporates a new home view, offering quick access to recent conversations, along with a dedicated section for starred conversations and mentions. While the initial layout follows a reverse chronological organization, Google intends to implement context-aware ordering mechanisms. Furthermore, the company is also raising the member limit of Spaces to 500,000, a significant increase from the previous cap of 50,000 and introducing a “huddles” feature that simplifies the process of initiating video or audio chats.

“You essentially have a co-worker who has infinite memory and amazing recall at your fingertips,” said Vamsee Jasti, Google’s product lead for Chat.

Messages from all places on Google Chat

google chat redesign

In an effort to cater to enterprise users, Google is partnering with Mio to establish messaging interoperability not only within Google Chat but also across major platforms like Slack and Microsoft Teams. The aim is to streamline communication and prevent message loss when switching between multiple messaging tools. However, it is important to note this feature is currently in the beta phase, and the company plans to release it publicly in 2024.

“We know that communication and collaboration happens over multiple channels and tools. That’s why we’re partnering with Mio, a leading provider of collaborative interoperability solutions helping customers enhance their productivity by streamlining communication across multiple channels,” reads Google’s blog post.


[ad_2]
Source link

Google Maps tests the use of some colors that copy Apple Maps

0
[ad_1]
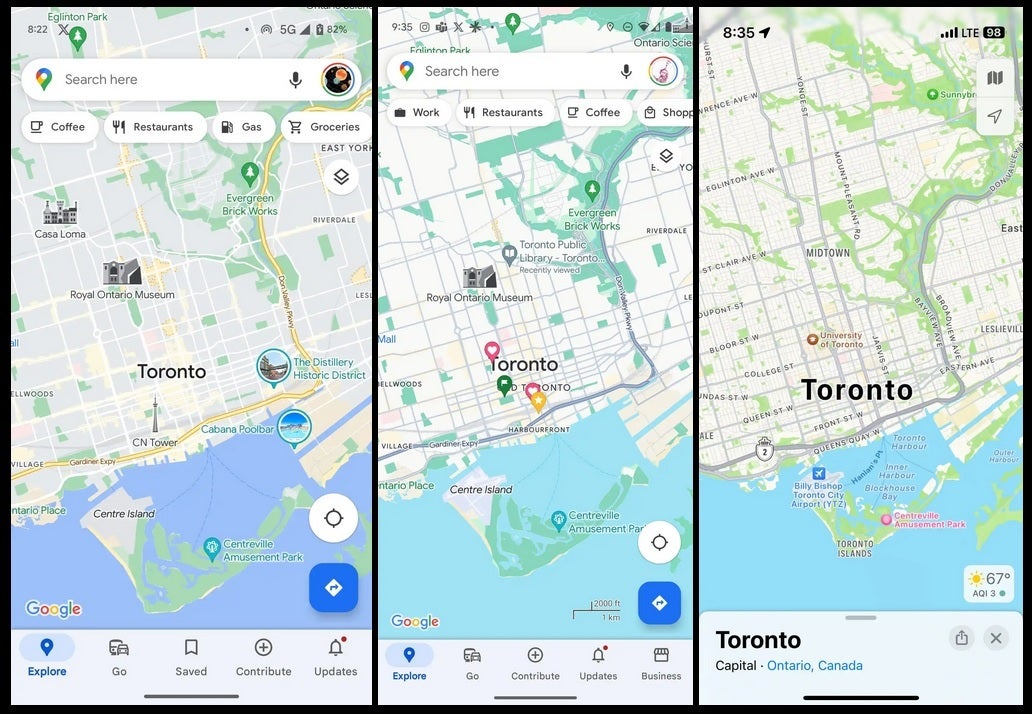
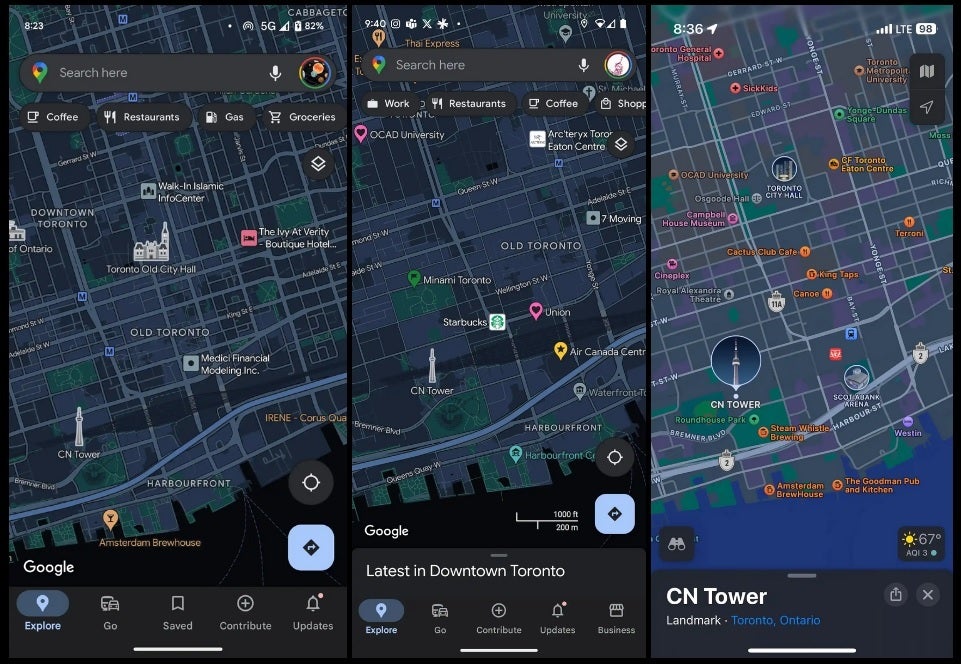
While Google Maps is still considered the top mapping and navigation app for mobile devices, Apple Maps has made an incredible turnaround after the fiasco that was the original launch of the service back in 2012 with the release of iOS 6. Apple was forced to start from scratch to revise the app and has done a pretty decent job of doing so, And now Google appears to be testing some new color options for Google Maps that match some of the shades used by Apple Maps.
Spotted by 9to5Google, Google Maps is testing a lighter blue color to represent water and any difference to the hue used by Apple is very minor. On the other hand, Google appears to be moving away from Apple by using a darker green color to indicate areas like parks and forests. Previously, Google and Apple both used a lighter shade of green to represent such areas.

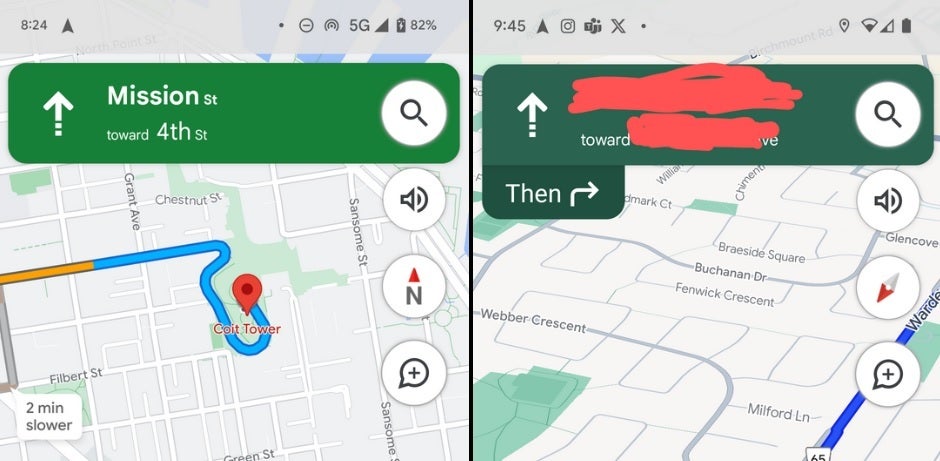
But Google Maps is also testing the use of gray, instead of white, to signify a road, and dark gray to represent a highway. All of these color changes being tested bring Google Maps in line with Apple Maps’ color scheme. And if you use Dark theme on both apps, Google Maps’ implementation of it remains darker than Apple Maps. Dark theme on the mapping apps is an acquired taste with some drivers complaining that it is harder to view the maps on the apps using a darker background.

You can go into the settings for both apps and keep them in Light mode if that is what you prefer. Additionally, Google Maps is also giving the driving directions at the top of the screen a darker green background color although you will have to use it under real-world conditions to see what impact the darker color has on you.

The updated version of Google Maps is reportedly rolling out today to Android users although it has yet to hit my Pixel 6 Pro running Android 14 beta 5.2.

[ad_2]
Source link

Garmin’s Venu 3 lets you manually track your sleep

0
[ad_1]

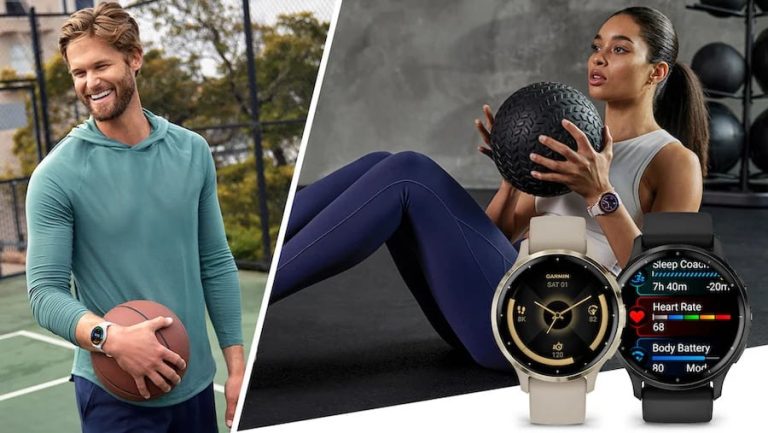
The Garmin Venu 3 is out and it appears to have a big focus on sleep features. Sleep tracking has become a very popular feature set for smartwatches and sport watches in recent years. And Garmin seems to be following this trend with its latest watch. A big feature with this device is sleep coaching. The new Sleep Coach feature will allow users to work towards a better night’s rest.

The feature will analyze HRV data along with your recorded sleep stages and use that to begin coaching you on how to sleep better. It can then add that information into your Morning Report. The Sleep coach isn’t the only new sleep feature though.

You can manually track your sleep with the Garmin Venu 3

The Sleep Coach is just the beginning. With the Garmin Venu 3 you can also now manually track your sleep. Just like you can do with other activities such as running, walking, cycling and more. With manual sleep tracking, you can start the process whenever you decide it’s time to get a little rest. Making this a really useful tool for those that take scheduled naps and want that data recorded. But you can also setup auto nap detection to automatically track long naps if you don’t want to deal with setting up the tracking manually. Garmin says the auto detection can also suggest how long naps should be. So you know how long to doze off the next time.

In addition to manual sleep tracking the smartwatch also has a new Wheelchair Mode. With this enabled, users can track how many times a day their push the chair around. This mode can also tell users when they shift their weight in the chair and it offers workout and sport tracking specific to wheelchairs.

The new Venu 3 and Venu 3S version both feature an AMOLED touchscreen and boast a battery life of up to 14 days in smartwatch mode. The Venu 3 and Venu 3S are available from August 30 and retail for $449.99. If you’re interested in picking up the watch you can find it at the link below.

Garmin Venu 3 – Best Buy


[ad_2]
Source link

Hackers Launch MiTM Attack to Bypass VMware Tools SAML

0
[ad_1]
VMware Tools SAML

VMware has been reported with a SAML token signature bypass vulnerability, which a threat actor can exploit to perform VMware Guest operations. CVE ID has been assigned for this vulnerability, and the severity was mentioned as 7.5 (High).

VMware tools are a set of modules and services for enabling several services in VMware products, which help better manage guest operating systems and flawless user interactions between the host and the guest operating system. VMware tools also can pass messages from the Host to the Guest operating system.

However, VMware has released a security advisory for addressing this vulnerability.

An attacker with a man-in-the-middle (MITM) network positioning between the vCenter server and the virtual machine can bypass the SAML token signature verification and exploit this vulnerability to perform VMware guest operations. The CVSS score for this vulnerability has been given as 7.5 (High).

There has not been a publicly available exploit released for this vulnerability yet.

Affected Products

ProductVersionRunning OnCVE IdentifierCVSSv3SeverityFixed VersionWorkaroundsAdditional Documentation
VMware Tools12. x.x, 11.x.x, 10.3.xWindowsCVE-2023-209007.5Important12.3.0NoneNone
VMware Tools10.3.xLinuxCVE-2023-209007.5Important[1] 10.3.26NoneNone
[2] VMware Tools (open-vm-tools)12. x.x, 11. x.x, 10.3.xLinuxCVE-2023-209007.5Important[3] 12.3.0NoneNone

VMware has been previously found to have a critical vulnerability in the Aria Operations for Networks, which lets threat actors perform authentication bypass and arbitrary file write operations. 

To remediate the vulnerability, VMware released a security advisory and Knowledge Base for VMware Aria Operations for Networks. Similarly, a security advisory has been released to fix this VMware tool vulnerability.

Users of VMware tools are recommended to upgrade to the latest version in order to prevent this vulnerability from getting exploited by threat actors.

Keep informed about the latest Cyber Security News by following us on Google News, Linkedin, Twitter, and Facebook.


[ad_2]
Source link

Aqara debuts new Matter-compatible Smart Home Products at IFA 2023

0
[ad_1]

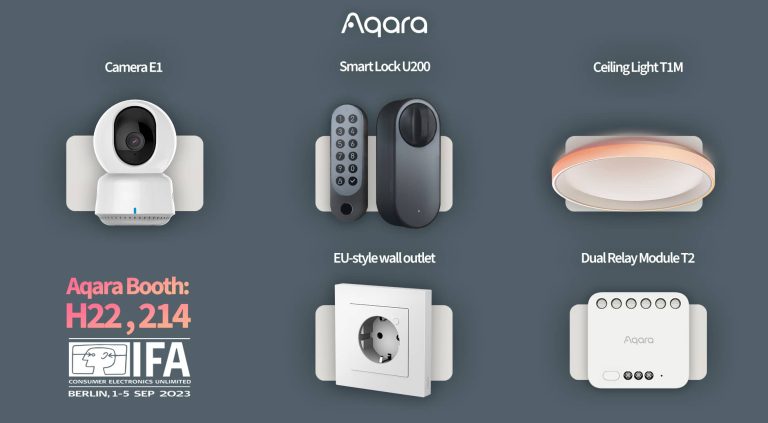
Aqara showed up in Berlin for IFA with a couple of new smart home products, and they are all Matter-compatible. Which is a huge deal, as we start to move towards the Matter protocol taking over the smart home.

First up is the Smart Lock U200. This is a new smart lock that actually doesn’t require you to change your actual lock. This is a retrofit solution, giving users a keyless home access option. As this does work with a NFC card, or specific NFC-enabled mobile devices. You can also use a PIN, fingerprint or a mobile app to get into your home.

Aqara has also announced its Camera E1. This is a smart camera for your home. It’s a Pan/Tilt Camera with 2K resolution. It does support Apple HomeKit Secure Video, as well as Amazon Alexa and Google Assistant. So you can use your voice to control it. Aqara is using WiFi 6 and Bluetooth 5.2 here for connecting to your home and smart devices.

Next up is the Dual Relay Module T2. This is is a versatile home automation solution, and gives you control over various devices, including lights, motorized window coverings, garage doors, boilers, electric heaters and even underfloor heating. It was built on Zigbee 3.0, and supports Matter-over-Bridge, and other major third-party platforms.

Aqara’s Ceiling Light has a LED status light

Many have been wanting smartphones to bring back a LED status light, but Aqara did it with their ceiling light. It’s a multi-color light, and has about 16 million vibrant colors, which enables users to set ideal lighting for different moods and occasions. It does have Matter-over-bridge support, and works with other major platforms.

The ring around the light can serve as a status indicator when linked to other smart home products. This would allow you to program the outer link to show a specific color when one of your other smart devices detects an issue, such as a leak or an open door.

These are all set to be available in the coming months, but Aqara did not mention specific availability dates, nor pricing.


[ad_2]
Source link

HP launched the Pavilion Plus 16 laptop with NVIDIA RTX graphics

0
[ad_1]

HP has a ton of high-quality computers on the market, and the company also has some more affordable offerings. While the Pavilion Plus series of computers do get up there in price, they don’t shoot too far above the $1,000 mark. The company just introduced the new HP Pavilion Plus 16. This is the first 16-inch computer in the series, according to Engadget.

This series of computers could be thought of as the premium mid-rangers of HP’s computers. There’s a 14-inch variant that starts at $849.99. It comes with Windows 11 Home, a 13th-gen Intel Core i5 processor, 256GB of onboard storage, 16GB of RAM, and a 2.2K IPS LCD display.

The HP Pavilion Plus 16 comes with NVIDIA RTX graphics

As stated, this computer is the first in the series with a 16-inch display. Actually, the screen is 16.5 inches diagonal, and it’s an impressive panel. It’s a 2.2K OLED display with a 120Hz refresh rate. So, you can expect whatever you’re looking at to pop.

Moving onto the internals, this computer will have a selection of processors, but it will max out with the 13th-gen Intel Core -7 processor. Also, if you’re looking to do some gaming on this computer, the top model of the computer will use the NVIDIA GeForce RTX 3050 GPU. This is a pretty high-end GPU, and it will be able to run a ton of the games that are on the market.

Aside from those internals, the HP Pavilion 16 Plus has up to 16GB of LPDDR5x RAM and 1TB of SSD storage. Just know that these will be present in the top model of the computer. As for battery capacity, we’re looking at a large 68Wh battery, and the company states that it can last up to 11:45 hours on a single charge for typical usage. If you’re only video-watching, then it should last you to around 15:45 hours.

Moving onto the ports, this computer gives you a nice array. It has two USB-A ports, a USB 3.2 Type-C port, and a Thunderbolt 4 port with USB power delivery. Other specs include B&O audio and Wi-Fi 6E.

This computer starts at $1,000 for the base model. It will arrive sometime in October in Natural Silver and Warm Gold. You’ll be able to pick one up from HP.com, Costco, and Amazon.


[ad_2]
Source link

Cisco Patched Multiple NX-OS And FXOS Vulnerabilities

0
[ad_1]

Multiple vulnerabilities riddled Cisco’s NX-OS and FXOS software, putting the networking devices at risk. Cisco patched the vulnerabilities with updated NX-OS and FXOS versions, urging Nexus and Firepower users to upgrade their systems as soon as possible.

Cisco NX-OS And FXOS DoS Vulnerabilities

Specifically, FXOS and NX-OS software power the networking giant’s Nexus (Ethernet switches for data centers) and Firepower (Next-Generation Firewall (NGFW)) devices.

The service confirmed patching five different vulnerabilities affecting its FXOS and NX-OS software. Exploiting three of these vulnerabilities could allow an adversary to trigger denial of service on the target devices. These include,

  • CVE-2023-20200 (CVSS 7.7) – This vulnerability affected the Simple Network Management Protocol (SNMP) service of FXOS software. An authenticated remote attacker could exploit the inherent improper handling of specific SNMP requests by sending maliciously crafted requests to the device to trigger system crashes. This flaw affected Firepower 4100 Series, Firepower 9300 Security Appliances, and UCS 6300 Series Fabric Interconnects when running Cisco FXOS Software or Cisco UCS Software with SNMP service enabled (which is disabled by default).
  • CVE-2023-20169 (CVSS 7.4) – This vulnerability affected the Intermediate System-to-Intermediate System (IS-IS) protocol of Cisco NX-OS Software. Due to insufficient input validation when parsing an ingress IS-IS packet, the flaw allowed an unauthenticated, remote adversary to trigger denial of service on the target device by sending maliciously crafted IS-IS packets. It affected Nexus 3000 Series Switches and Nexus 9000 Series Switches in standalone NX-OS mode when running Cisco NX-OS Software Release 10.3(2) with IS-IS protocol enabled.
  • CVE-2023-20168 (CVSS 7.1) – This security flaw impacted the TACACS+ and RADIUS remote authentication for Cisco NX-OS Software. With the directed request option enabled for TACACS+ or RADIUS, the software developed incorrect input validation when processing authentication attempts. Hence, an authenticated remote adversary could trigger the DoS on the target device by entering a maliciously crafted string at the login prompt. This vulnerability affected multiple Nexus devices running Cisco NX-OS Software with the directed request option enabled for TACACS+ and RADIUS.

Other Important Bug Fixes

Alongside the three high-severity vulnerability fixes, Cisco has also addressed two medium-severity flaws affecting its devices. These include,

  • CVE-2023-20115 (CVSS 5.4) – This vulnerability affected the SFTP server implementation for Cisco Nexus 3000 Series Switches and 9000 Series Switches in standalone NX-OS mode. An authenticated remote attacker could trigger the flaw and download or overwrite arbitrary files from the OS on the target devices.
  • CVE-2023-20234 (CVSS 4.4) – An arbitrary file write vulnerability affecting the CLI of Cisco FXOS Software. Exploiting this flaw could allow an adversary to overwrite system files, provided the attacker possesses admin credentials.

Cisco patched all five vulnerabilities with subsequent NX-OS and FXOS software releases. The tech giant has also listed all the vulnerable devices in its advisories, which users can refer to upgrade their systems accordingly.

Let us know your thoughts in the comments.


[ad_2]
Source link