Google Messages is preparing to support satellite connectivity

0
[ad_1]

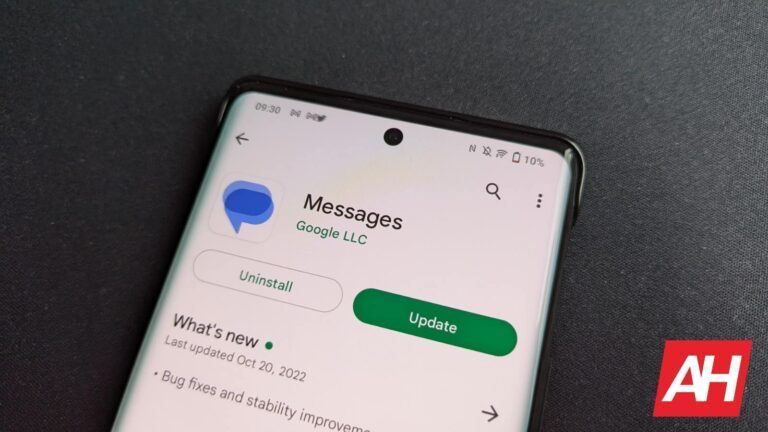
Satellite connectivity has quickly become one of the more necessary features on modern smartphones, thanks in part due to its ability to save crucial lives in dangerous times. Now, in line with its efforts to make the feature available to all users with Android 14, Google has started implementing a new interface within Google’s Messages app, specifically designed to facilitate emergency SOS conversations via satellite.

As first spotted by the tipster @neil_rahmouni, who also shared some photos, Google’s fresh new interface for emergency connectivity interface mirrors the familiar layout of a standard text message thread, complete with a text entry field labelled “Satellite messages.” This implies that users will have the ability to craft personalized messages when communicating with emergency services, thus giving Google a massive advantage over Apple’s implementation, which only allows for certain predefined messages.

Additionally, the text entry box will also feature a character counter, which suggests that satellite messages could potentially be subject to distinct character limitations, differing from the conventional SMS format. Furthermore, in instances where the signal strength isn’t sufficient for a satellite call, the Google dialer will proactively guide users to switch to satellite messages.

New hardware required

While the prospect of using satellite connectivity in emergency situations could help save a lot of precious lives, most of the existing phones do not have the required hardware in place to use satellite connectivity. However, it is important to note that Google’s Pixel 7 series already incorporates the required hardware, albeit necessitating substantial software updates.

Moreover, the geographical context also plays a pivotal role. In some countries, the use of satellite phones is strictly banned or heavily restricted, casting doubts on the universal applicability of this technology. As a result, users who require satellite connectivity in their daily lives can explore interim solutions like Motorola’s Defy satellite Bluetooth dongle.


[ad_2]
Source link

WhatsApp may soon get new text formatting tools

0
[ad_1]

WhatsApp is already one of the best messaging apps, but there’s always room for improvement. That’s why we’re getting new updates that bring important new features almost every month. Recently, the app added support for high-resolution photos and promised to bring support for HD videos very soon too.On top of that, we’ve just learned that WhatsApp is working on additional text formatting tools that will make communications easier and even more fun. The fine folks over at WabetaInfo spotted a brand-new feature in the latest beta version of WhatsApp, which indicated that Meta’s developers have started to implement new text formatting tools.

Currently, there’s proof about three new text formatting options, which will be added on top of the already available italics, bold, strikethrough, and monospace options.

The first one is called “Code Block” and is aimed at software developers and programmers who might want to send code snippets to their friends or colleagues. This particular text formatting tool will prevent the confusion created when code snippets were not being displayed accurately in the chat window.

Another interesting text formatting tool, Quote, will receive a small yet important improvement. WhatsApp plans to introduce a new option that will allow users to highlight portions of a text that they want to quote. Currently, you can only quote entire messages, not parts of them.

Last but not least, one of the latest beta versions of WhatsApp had a new formatting tool that allowed users to create lists of items. That will basically eliminate the need to manually add bullet points to every item that you want to be included in your list.

The report mentions that these features are now in development, so it may take some time until WhatsApp actually releases them for everyone to use. Still, it’s nice to know what we’ll be getting in future updates, even if these new features won’t be available for a long time.


[ad_2]
Source link

WinRAR Security Flaw Could Allow Command Execution

0
[ad_1]

Heads up, WinRAR users! It’s time to update your systems with the latest WinRAR version to avoid security risks. The developers have patched a severe security flaw in WinRAR that could allow remote code execution attacks.

Remote Code Execution Flaw Discovered In WinRAR

Researchers from Trend Micro Zero Day Initiative (ZDI) discovered a serious vulnerability affecting RARLAB’s WinRAR archiving tool.

WinRAR is a popular file archiving tool available as trialware, allowing enterprise or personal users to create .rar archives. The software’s support for various archive formats has won it a vast customer base, suggesting the massive impact of the tool’s malicious exploitation.

According to ZDI’s latest advisory, a high-severity security flaw existed in WinRAR that could allow remote code execution attacks.

The vulnerability CVE-2023-40477 (CVSS score 7.8) existed in the recovery volumes processing due to “lack of proper validation proper validation of user-supplied data, which can result in a memory access past the end of an allocated buffer.” An adversary could easily exploit this flaw by tricking the target user into opening a maliciously crafted archive file or visiting a malicious URL. Once done, the attacker could execute arbitrary codes in the current process’s context.

Following this discovery, the developers patched the flaw with WinRAR version 6.23, sharing all the changes via an advisory. Besides the out-of-bounds write vulnerability that ZDI researchers highlighted, the advisory also mentioned fixing other bugs, including opening the wrong file after double-clicking an item in a specially crafted archive, and others.

Since the patch has been released, users must download the latest WinRAR versions from the official website to avoid potential threats. Besides, users must always remain careful when interacting with attachments or URLs from unsolicited sources. In addition, users should ensure to equip their systems with robust anti-malware programs to prevent such threats.

Let us know your thoughts in the comments.


[ad_2]
Source link

Chrome Password Manager gets a new shortcut for easier access

0
[ad_1]

The Chrome Password Manager on both Windows and macOS is now getting a new shortcut. This is a long-awaited feature that will help improve the accessibility of user passwords. Some users are already getting acquainted with this new feature on their Chrome browser.

With this new feature, Chrome users can better find their passwords whenever they need to with ease. Asides from the autofill password benefit of having your password saved, there might be times you’d need to access it. For this reason, there is a need for a shortcut to the Google Password Manager page.

This shortcut is an extension Google provides for users to install on their Chrome browser. The extension is only available on Windows and macOS devices at the moment. Here is how you can access this new shortcut button or extension app on your browser.

How to access the new Google Chrome Password Manager shortcut extension

Accessing this new shortcut to the password manager is quite straightforward. Google did a great job by making this entire process simple for all to understand. So if you use Google Chrome on your Windows or macOS device, and you are finding a hard time accessing your saved passwords, this one’s for you.

To access this shortcut extension on the Chrome browser, users need to first tap on the three-dot menu button. This button sits on the top right-hand side of the screen, just under the close button. Tapping on this will pull up a drop-down menu from where users will be able to access this new feature.

On the drop-down menu, users are to find and select the Google Password Manager option. This will pull up the password manager interface, where you can find all your saved passwords. But to access this new shortcut, tap on the hamburger icon at the top left-hand corner of the screen.

From the list provided by the menu, find and select the settings option. Within the settings page is the “Add shortcut” option, tap on this as well. You’d get a prompt to install the Google Password Manager extension, which is a shortcut to accessing your saved passwords.

Installing this extension will make it a lot easier to access all your saved passwords for usage. If you don’t already have this feature, you can head over to your Chrome browser and install the extension now. It is now available on Windows, macOS, and lastly ChromeOS devices.


[ad_2]
Source link

Threat actors have started using QR codes in phishing attacks

0
[ad_1]

In this day and age, QR codes have become a popular way for users to access quick information about a product or service, eliminating the need for manual searches. However, taking advantage of this convenience and the relaxed security policies in email clients, threat actors have reportedly started using QR codes in widespread phishing campaigns and targeting major US institutions.

According to Cofense, among the 1,000 emails associated with the phishing campaign, a staggering 29% were directed to a single major US energy company, while the others targeted a diverse array of sectors, including manufacturing (15%), insurance (9%), technology (7%), and financial services (6%).

Why use QR codes?

While email platforms like Gmail and Outlook have implemented robust security protocols to shield users from common phishing attacks, QR codes, often presented as image files like .PNG or .JPG, provide threat actors with a means to bypass conventional security measures. Additionally, to further elude detection, these emails employ base64 encoding for phishing links, with QR codes utilizing redirects through platforms like Bing, Salesforce, and Cloudflare’s Web3 services.

“What is important to note is that aside from hiding in QR codes, threats are abusing a trusted domain to carry out attacks. Abusing trusted domains, using obfuscation tactics, coupled with hiding the URLs inside QR codes embedded into a PNG or PDF attachment, helps ensure that emails bypass security and make it into inboxes,” reads the report.

The campaign’s modus operandi involves sending a phishing email that urges recipients to swiftly update their Microsoft 365 account settings by scanning a QR code, purportedly for account verification. Furthermore, threat actors manipulate recipients by imposing a three-day deadline to update their account settings, capitalizing on a common psychological trigger.

What is the solution?

Given the efficacy of QR codes in evading security detection, companies like Google and Microsoft will need to develop new ways of scanning QR codes for phishing links. Additionally, Cofense recommends comprehensive employee training to recognize signs of phishing attempts, including emails that pressure immediate action and landing pages that diverge from official designs.


[ad_2]
Source link

Thanks to this YouTube Music update for Wear OS you get to browse albums

0
[ad_1]

New functionalities regarding browsing tracks in the latest YouTube Music for Wear OS update. Finally, there’s the option to dive in an album playlist through your smartwatch and cherry-pick that one track that gives you the goose pimples!

The update was spotted by 9to5Google. The new functionalities are being rolled out with YTM (YouTube Music) version 6.15 for Wear OS, so make sure to check your watch’s app version and promptly update, if you’re not happy with the current functionalities.

Before the v. 6.15 update, smartwatch users had to put up with the following UI – when selecting an album (or playlist) in YouTube Music on Wear OS, the app would take them to a stripped-down page with two options – buttons for “Download” or “Play”. So, for example, if you wanted to listen to the last song from a given album – like Bob Dylan’s 2017 Triplicate which consists of 30 tracks – you’d be hitting that “Next” button… a lot.Now, instead of mad skipping, the v. 6.15 update allows users to see the playlist as listed songs with the option to navigate, select and play whatever you choose to. There’s also a design tweak – when you enter an album/playlist, the tracklist will appear over a blurred artwork background.

When selecting a song from a playlist, your queue becomes that playlist, similar to YouTube Music on a smartphone.

Things are slightly different when it comes to selecting a track from an album – it basically starts a “radio” mode, so the next song will not be from the album that you were just browsing, but a random one. If you want to play an entire album, you should hit the new shuffle button, which replaced “Play” as part of this update.

Google announced YouTube Music for Wear OS well over two years ago and last year, the app got a pack of new features and functionalities, like streaming music over LTE or Wi-Fi.


[ad_2]
Source link

Pixel 8 & Pixel 8 Pro could be eSIM only, just like iPhones

0
[ad_1]

The Pixel 8 and Pixel 8 Pro are coming in a couple of months, and some interesting info just surfaced. According to Mishaal Rahman, the Pixel 8 and Pixel 8 Pro could be eSIM-only devices… at least in some markets.

At least some Pixel 8 & Pixel 8 Pro units could actually be eSIM only

He noticed something very interesting in the CAD-based renders @OnLeaks shared. Those renders surfaced a while back, but this detail managed to escape pretty much everyone.

Mishaal Rahman noticed that SIM card slot trays are missing on the left side of the devices. The Pixel 6 and 7 series featured those lots in CAD-based renders, but that’s not the case for the Pixel 8 and Pixel 8 Pro.

Do note this info with a grain of salt, though. Why? Well, Mishaal talked to Steve (the person behind the @OnLeaks account). He said that “sometimes his CADs don’t include every detail, so instead of taking a guess and being wrong, he’ll ignore those missing details”.

The Pixel 8 Pro that surfaced had a SIM card tray

On top of that, in a video that @Za_Raczke leaked, of the Pixel 8 Pro, there seems to be a SIM card tray on the left side. That doesn’t confirm that one will be available in all markets, though, so we’ll have to wait and see.

As you all know by now, the iPhone 14 units, all of them, are eSIM only in the US. That’s not the case in almost every other market, though, as eSIM is still not as popular. In Europe, for example, models with SIM card slots are being sold.

Misaal says that it would make sense for Google to ditch SIM card slots in the US, though. Not only did Apple already do it, but Google has been working on making it possible to transfer eSIMs between devices, and on top of that, convert a pSIM to an eSIM.

If these new features get announced by the company with the Pixel 8 series, it would make sense for the devices to be eSIM only, at least in the US.


[ad_2]
Source link

Hackers are using new compression technique to hide malware in APK files

0
[ad_1]

Threat actors are always on the lookout for new ways to infiltrate your devices and gain unauthorized access. Now, according to a report from security firm Zimperium, a prominent participant in the ‘App Defense Alliance,’ hackers have found a new way to discretely spread malware on devices by using a novel compression technique on APK files, which effectively makes the malware invisible to conventional security measures.

The new technique was first reported by Joe Security, who discovered that an APK managed to remain inscrutable to analysis, all while seamlessly executing on Android devices. This is because, unlike traditional malware that triggers recognizable alarm bells, the new tactics allow hackers to remain in uncharted territory for both antivirus programs and cybersecurity experts. One such tactic involves using filenames that exceed the 256-character limit, deliberately causing crashes in various analysis tools. Additionally, hackers also manipulate the AndroidManifest.xml files and employ malformed String Pools to disrupt tools that handle Android XML files.

Moreover, to make matters worse, the report also discovered a staggering 3,300 APKs, which are presently employing these novel anti-analysis techniques. And although most of these APKs are corrupted beyond a point where Android can load them, a subset of 71 malicious APKs has been proven to operate seamlessly on Android OS versions 9 (API 28) and later.

Not on the Play Store

Although the new type of malware could wreak havoc for Android users, the report highlights that none of the applications exploiting this new APK compression technique has breached Google’s Play Store. As a result, users who refrain from sideloading apps – that is, installing applications from sources outside the official Play Store – are presently safe.

Nonetheless, this report once again highlights the importance of maintaining caution while downloading things directly from the internet. However, in situations where external app sources are unavoidable, users should perform antivirus scans on their devices and refrain from granting unnecessary permissions to apps.


[ad_2]
Source link

Meta might launch a web version of Threads early this week

0
[ad_1]

Meta is trying hard to bring as many users as possible back to Threads, and the best thing to do that is to add all the features they requested. Having the app available on all major platforms is another way to regain many of the users that stopped using Threads after a few weeks.

Currently, Threads is available on Android and iOS, but Meta is still missing a web version. Although Adam Mosseri, head of Instagram, said one week ago that the company is already working on a web version of Threads, he didn’t say when we can expect it.

Over the weekend, he reiterated the fact that Meta is testing a web version of Threads internally, which should be launched early this week. According to Mosseri, the app is “a little bit buggy right now, you don’t want it just yet.” He went on to say that “as soon as it is ready, we will share it with everybody else.”

However, people familiar with Meta’s plans told Wall Street Journal that the company plans to launch the web version of Threads early this week. But there’s a catch though, as the source added that the launch plans aren’t final and could change.

After rushing the mobile version of Threads, which led to over half of the initial users dropping the app due to important features missing, including a web version of the app, it looks like Meta wants to avoid releasing yet another unfinished product.

Despite rolling out dozens of new features for Threads on Android and iOS, Meta’s app still has a lot of things to improve before the app can actually compete with Twitter.

Launching the web version of Threads will be just another step toward closing the gap between Meta’s micro-blogging app and the competition, which includes multiple apps at the moment, not just Twitter (i.e. Mastodon, Bluesky).


[ad_2]
Source link

Pixel 8 will bring a Google Camera UI revamp: Gallery

0
[ad_1]

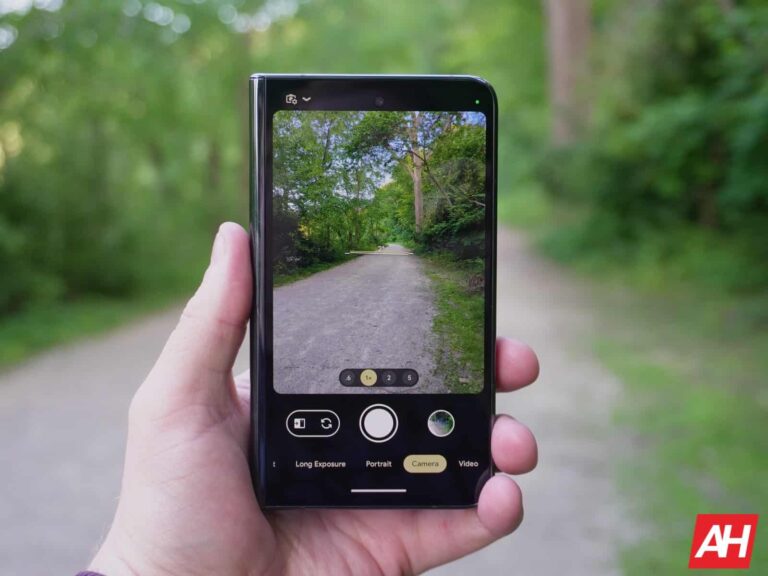
The Google Pixel 8 series is coming in October, most likely, and along with the devices we’ll get a Google Camera UI revamp, it seems. This information has been revealed by Android Authority, and a bunch of screenshots also got shared. So, we can take a closer look at the new UI.

This information has been shared by an “anonymous source inside Google”, says Android Authority. Regarding the change itself, it’s not all that surprising, as the Google Camera UI has been mostly unchanged since the Pixel 4 launched back in 2019.

The Pixel 8 series will bring a Google Camera UI revamp

In the new UI, photo and video modes will be more clearly separated. They were both a part of a carousel of modes you could switch between, but that will change. There will be a separate switch between photo and video modes below the carousel itself. Then, based on your choice, the carousel will change too. You can see all that in the two images below.

Google will also swap the location of the camera switch button with the gallery preview button. Also, the settings pop-up will now appear if you swipe from the bottom up, not the other way around, as was the case before. You can, alternatively, of course, tap the settings icon too.

The company will also rearrange some camera modes too. The ‘Motion’ tab will be separated into ‘Long Exposure’ and ‘Action Pan’. Google wants to make them easier to spot.

Pixel 8 Google Camera 9 revamp leak image 5

The ‘Cinematic Pan’, on the other hand, will become simply ‘Pan’.

Another thing you’ll notice is the fact the old stabilization modes are gone. Those options will be placed in the pop-up menu. You’ll be able to choose between standard, active, and locked.

The Pixel 8 & Pixel 8 Pro camera specs also surfaced a while back

That is basically it as far as the camera UI is concerned. The Pixel 8 and Pixel 8 Pro camera specs have also been revealed by Android Authority in the past, in case you’re interested in checking those out. Both the Pixel 8 and Pixel 8 Pro are expected to arrive in October, but Google did not reveal the launch date yet.


[ad_2]
Source link