Have you considered the need for a darker dark mode on Google Play?

0
[ad_1]
Do you remember back in the day when most of the best phones on the market didn’t have dark modes? The mode, which aims to preserve your eyesight while improving your device’s power consumption (and thus, battery) was so wildly successful that it eventually made its way to basically everything we own.(Please, shout out below if you have a fridge or washing machine with a dark mode. I’m betting that one exists!)

But there is still an ongoing debate regarding the dark factor of the mode: how dark exactly should it be? Well, I see the sides as follows:

  • Aesthetics dictates a lighter tone, around charcoal and gravel-gray, as to reduce eye-strain and improve readability through reducing maximum contrast
  • Optimization requires absolute black, the kind that AMOLED displays love, which would improve your device’s battery

Well, Google says: why not both? Or at least, this is how I view the news that Google Play’s dark theme got just a bit darker. It’s not lite-black. It’s not pitch-black. It’s in between. But it’s also just a test for now.

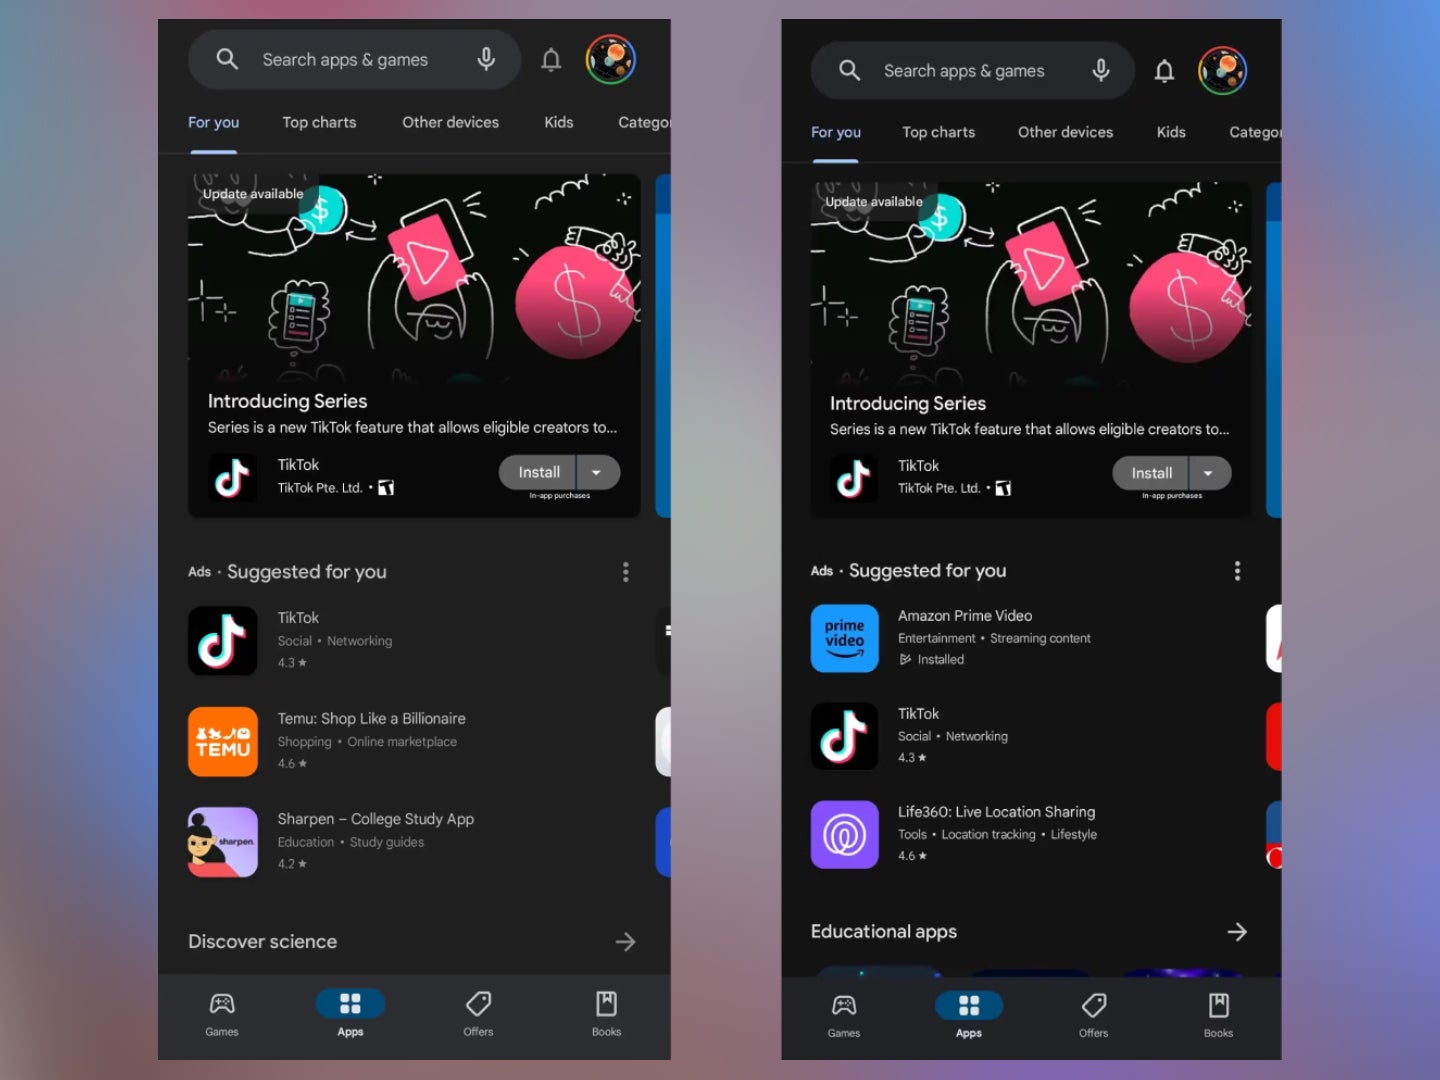
So, after checking the comparison above, you can certainly notice how the image on the right is just a splash darker than the one on the left. Would this change effectively help to cater to both camps?

Technically, yes. Version 37.0.22-29 brings a darker tint, so in theory that should mean a very slight and most likely hardly noticeable improvement in the battery department. That being said, the move to not overexpose things through plastering the background in jet black will certainly please that part of the crowd, which finds high-contrasted areas difficult to view.

So, win-win? Maybe. This change may be just a test or an implementation, which is part of the Big G’s updated design guidance. Something similar did happen to Chrome and YouTube recently, so the latter may very well be the case. 


Could the Big G be doing this in preparation for the upcoming Pixel 8 series of flagships? Probably not, but it’s always worth it to remember to be hyped about something cool in the smartphone world! 


Personally, I’m a big fan of buttons and letting people choose their colors, but hey — what do I know? I’m just a dark mode fan, who wants to see a consumer appliance with a screen that also has the option.


[ad_2]
Source link

Multiple Vulnerabilities Found In Ivanti Avalanche EMM

0
[ad_1]

Researchers detected numerous security vulnerabilities in Ivanti Avalanche EMM, allowing remote code execution attacks from unauthenticated adversaries. Ivanti patched the flaws following the bug report; hence, users must update their systems with the latest releases to receive the patches.

Ivanti Avalanche EMM Vulnerabilities

According to a recent report from Tenable, their researchers found two different vulnerabilities affecting Ivanti Avalanche.

Ivanti Avalanche is a dedicated Enterprise Mobile Device Management (EMM) solution, offering its customers to manage wireless settings across the network.

Specifically, the researchers observed two critical-severity buffer overflow vulnerabilities affecting the WLAvalancheService.exe (version 6.4.0.0 and older). The service used a “fixed-size stack-based buffer to store converted binary data from a hex string.” Hence, the first vulnerability would allow an unauthenticated, remote adversary to specify a long hex string that could trigger a buffer overflow.

Then, the next vulnerability appeared during data type 9 item processing, when the service used a fixed-size stack-based buffer to store and convert user-supplied data to an integer using atoll(). A remote adversary could trigger buffer overflow via a long type 9 item, without authentication.

Both issues received a CVE ID CVE-2023-32560 and a CVSS score of 9.8. In their post, the researchers shared the vulnerable scripts, demonstrating the exploits.

Ivanti Patched The Flaws

Tenable researchers discovered and reported the vulnerabilities in early April 2023. Almost after a week, Ivanti confirmed receiving the report and started working on a fix upon receiving the PoC script.

While Tenable set the initial disclosure period as the standard 90 days, Ivanti explained that it would take longer to deploy a patch. Consequently, both parties agreed upon extending the disclosure window, and Ivanti confirmed August 2023 as the patch release month.

Finally, the vendors released the fix with Avalanche 6.4.1, following which, Tenable disclosed the initial advisory.

Recently, Ivanti made it to the news following back-to-back zero-day fiascos in its EPMM that went under attack.

Let us know your thoughts in the comments.


[ad_2]
Source link

Everything you need to know

0
[ad_1]

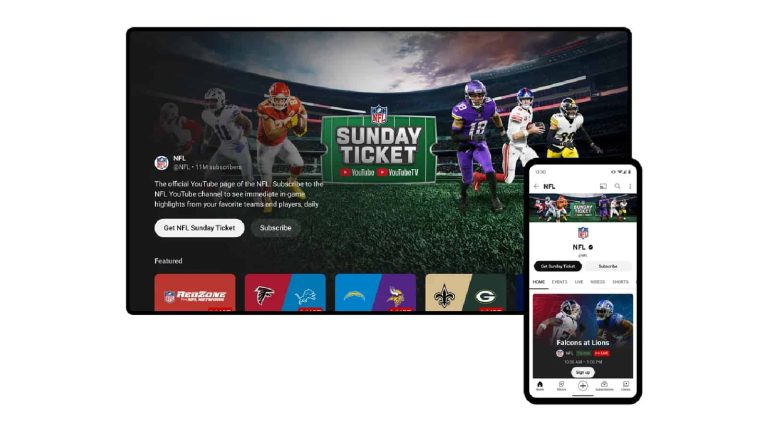
Google, or more specifically, YouTube won the rights to host NFL Sunday Ticket for the next seven years. YouTube is paying the NFL about $2 billion per year for these rights, and YouTube is going all out with promoting it, providing discounts and different plans that you can subscribe to. Now in this article, we’re going to tell you everything you need to know about NFL Sunday Ticket on YouTube, and help you decide if you should subscribe or not.

What is NFL Sunday Ticket?

First off, let’s talk about what NFL Sunday Ticket actually is. It first debuted in 1994, and DIRECTV had the rights to it the entire time until the 2023 season. It’s a premium sports package that broadcasts NFL games in every market. But it does not include local or nationally broadcast NFL games.

Screenshot 2023 08 17 at 9 12 18 AM

Because the NFL has deals with NBC, FOX and CBS across the country for games, NFL Sunday Ticket has to be more expensive, so that they don’t cut out their partners. Which will explain why NFL Sunday Ticket is so expensive.

In addition to getting every single NFL game this season, you will also get unlimited simultaneous streams at home for NFL Sunday Ticket.

How much is NFL Sunday Ticket?

Google is actually doing something really smart here. They are offering NFL Sunday Ticket with YouTube TV and without YouTube TV. You can also subscribe to it directly through YouTube Primetime channels. Of course, the cost for NFL Sunday Ticket is lower with YouTube TV – but then you also need to factor in the $72.99/month for YouTube TV which does include over 100 channels.

Screenshot 2023 08 17 at 9 11 48 AM

The pricing for NFL Sunday Ticket with YouTube TV is as follows. For NFL Sunday Ticket and YouTube TV, it’s $349. For NFL Sunday Ticket with NFL RedZone and YouTube TV, it’s $389.

Without YouTube TV, NFL Sunday Ticket is going to cost you $449 for the season. Or NFL Sunday Ticket and NFL RedZone will cost you $489 for the season.

YouTube has also announced monthly pricing for NFL Sunday Ticket, but it seems to only be for YouTube TV. It’ll cost you $99.75/month for four months. Which makes it more expensive than just paying for it all at once.

Why is it so much more expensive than when DIRECTV had NFL Sunday Ticket?

When DIRECTV had NFL Sunday Ticket, it cost $294 for the season. Now we’re seeing it cost $349 for the season with YouTube TV, or $449 without. Which sounds like it’s more expensive, but with DIRECTV you had to have satellite, which was definitely way more than $72.99. So all things considered, it’s really not that much more expensive.

But part of the reason for this is, YouTube is paying the NFL $2 billion per year for the rights to NFL Sunday Ticket. And obviously, Google needs to recoup that cost somehow. DIRECTV was paying $1.5 billion pear year and losing $800 million per year for NFL Sunday Ticket.

YouTube has said that they will be experimenting with different pricing plans and options in the future. In fact, they just announced a new student plan (pricing has not yet been announced), which is just the start of that.

Does NFL Sunday Ticket include local games?

NFL Sunday Ticket does not include local games, nor nationally broadcast games. Which is why the bundle with YouTube TV is a pretty good option. That is because you will get local and nationally broadcast games with YouTube TV. And you can also record them to watch later with unlimited cloud DVR included.

YouTube TV does have ESPN, NBC, FOX and CBS which covers all of the channels that local and national games are part of. It also has the NFL Network, which has the occasional NFL game – typically around Christmas and New Years. Some Thursday night games are on Prime Video, which is not part of YouTube TV.

So the bottom line here is, if you want local games too, then you’re going to want to get YouTube TV plus NFL Sunday Ticket.

Does YouTube TV offer multiview for NFL Sunday Ticket?

YouTube TV actually announced Multiview earlier this year and began testing it during the NCAA March Madness. This was in preparation for NFL Sunday Ticket.

With Multiview, you’ll be able to watch, two, three or four games at the same time. Subscribers will be able to choose from a bunch of options for multiview, and you’ll also be able to add games to multiview on your own. So if there’s a couple of games you want to watch at the same time, you can do just that.

NFL Sunday Ticket on YouTube will include live chat

Much like a live stream on YouTube, NFL Sunday Ticket is also including live chat – which can be toggled on and off. Since this will only be for those that subscribe to NFL Sunday Ticket, the chat should hopefully not be full of spam, and not move as fast as with some YouTube live streams.

YouTube is also going to utilize Shorts for NFL Sunday Ticket. By adding real-time NFL highlights to YouTube Shorts, which likely won’t be limited to just NFL Sunday Ticket subscribers.

YouTube’s popular “catch up with key plays” feature will be available too

YouTube TV has a pretty popular feature that allows you to catch up with key plays for different games in different sports. And that feature will be available on NFL Sunday Ticket on both YouTube and YouTube TV.

This will kind of speed up the game to the part that you started watching. So you can ensure that you do not miss any big plays, or anything else important that happened in the game.

C4k1myQwYi2JQZTJCReNgdvst9gLdgdas49Q

Are pre-season and post-season games included?

Yes, both pre-season and post-season games are included in NFL Sunday Ticket on YouTube TV – but not on YouTube. Technically, they are only included in YouTube TV because they are on the channels included in YouTube TV. But nonethless, you an see them while subscribed to NFL Sunday Ticket.


[ad_2]
Source link

Android flubot malware installs itself by faking security update

0
[ad_1]

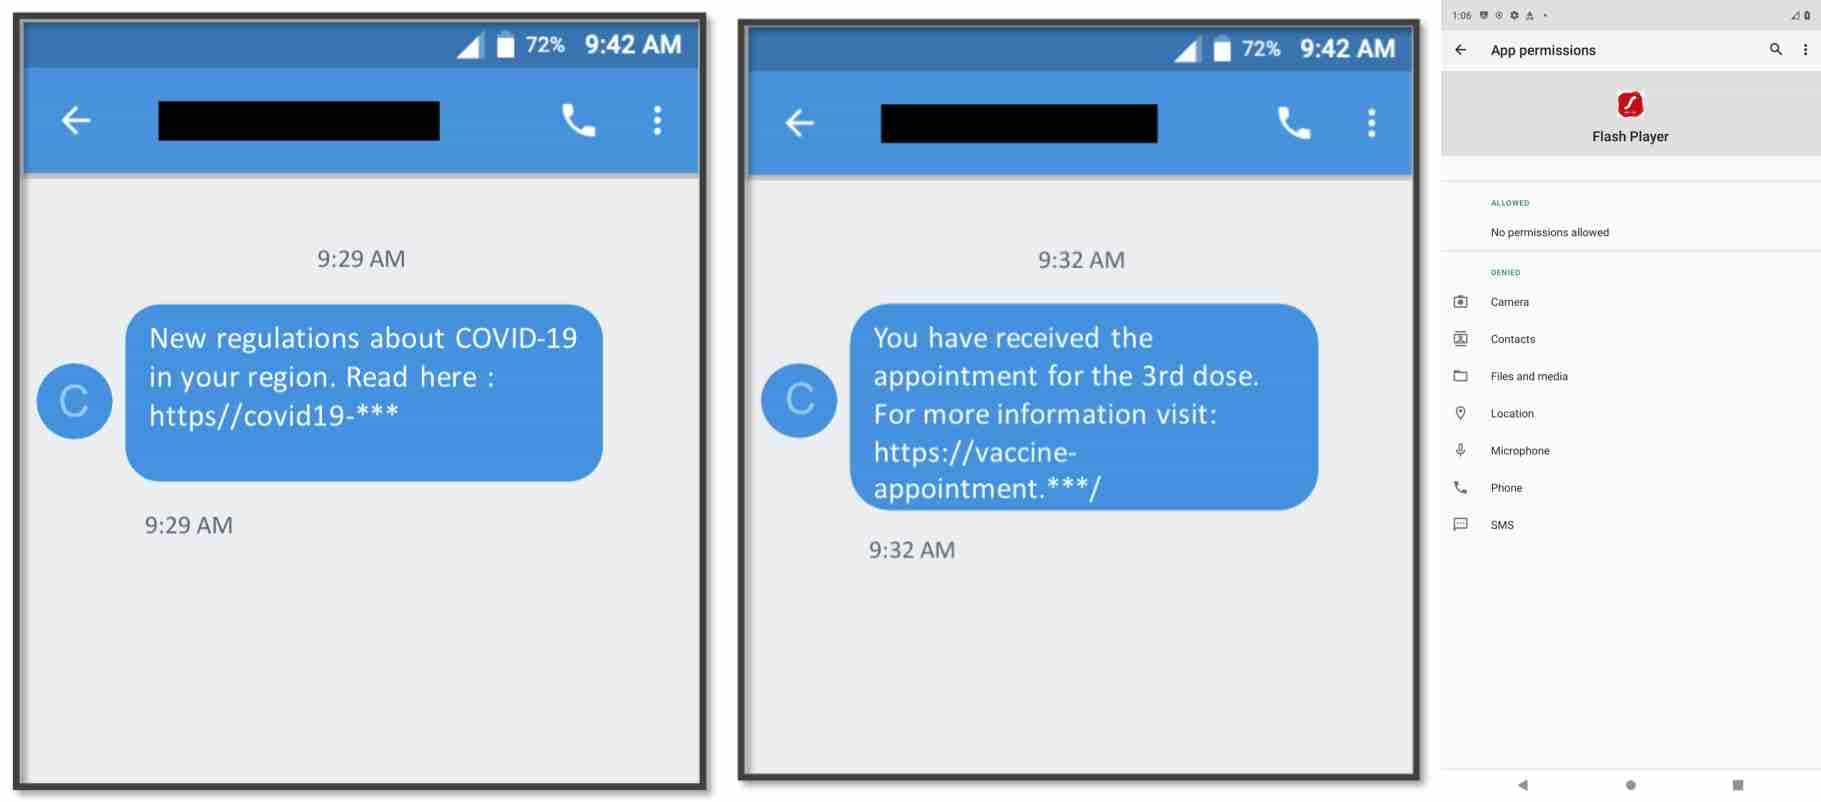
The security update is obviously phony but looks authentic that can deceive users into installing Flubot malware on their devices.

New Zealand’s Computer Emergency Response Team (Cert NZ) has issued a new warning involving the spread and infection of the infamous Flubot malware known for its password stealing capabilities.

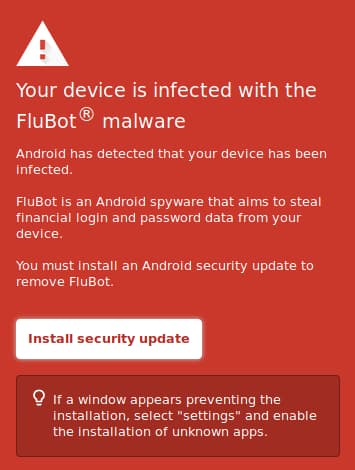
According to authorities, the threat actors are now trying to trick users into believing that their devices are infected with Flubot malware by displaying a fake security warning message.

SEE: GriftHorse Android malware hit 10 million devices in 70 countries

The warning is obviously phony that may become a reality if the recipient of this message clicks on the Install Security Update button that’s part of the message.

Flubot Strikes Again

CERT NZ released an advisory to warn users about a deceptive text message that reads: “Android has detected that your device has been infected.” The message contains further instructions on how to install a security update to remove the malware.

Flubot Password Stealer Trapping Android Users With Fake Security Updates

However, when the recipient clicks on the install security update button, this action triggers the Flubot infection. CERT NZ also mentioned that Flubot malware message is targeting Android phones, and the content of these messages is constantly changing.

For instance, previously, the message was supposedly sent by a courier company, alerting users to click on an enclosed URL or download an app to know parcel delivery details.

Flubot Looking to Steal Banking Information

According to New Zealand’s Telecommunications Forum’s chief executive, Paul Brislen, the payload resends the text through the users’ address book. Additionally, it asks for banking information.

“Needless to say at a time when everyone is using courier delivery services, this has the potential to cause a lot of damage,” Brislen said.

Threat Actors Also Using Your Photos to Install Flubot

In addition to fake text messages from the courier service, the Flubot banking trojan is tricking Android users into downloading malicious software in the disguise of fake Flubot deleting the app or upload photos of the victims as well. A fake text is sent to random Android users stating that the recipient’s photos have been uploaded.

Flubot against Android smartphones

Flubot malware was initially observed in Spain in late 2020 and within months its infection was found spreading Android devices globally including Australian banks.

However, in March 2021, the malware was caught with additional capabilities including mimicking popular apps like FedEx, DHL, Correos, and Chrome to steal user data.

How to Stay Protected?

Since threat actors continually update their attack tactics, CERT NZ urges users not to fall prey to this scam and forward the texts to 7727 before deleting the message.

“Given that the wording of these texts has changed within a short timeframe, it is likely the wording will change again. Be wary of any suspicious text messages you receive, asking you to click on a link, and forward any new suspicious texts to 7726.” advisory from CERT NZ read.

Forwarding them to 7726 helps CERT NZ and the Department of Internal Affairs to permanently shut down the links provided in the message and contact users who have been infected by the app.

It is important to note that only Android users can be targeted with these fake texts, while iOS devices may receive the message but won’t get infected with Flubot.

Did you enjoy reading this article? Like our page on Facebook and follow us on Twitter.


[ad_2]
Source link

The Xbox 360 store will go away next year

0
[ad_1]

Back in November 2005, Microsoft launched the Xbox 360, and this system was a fan favorite among users. If you had an online connection, then you were most likely downloading games right to your system. You’re still able to do that today, but all good things must come to an end. Microsoft announced that the Xbox 360 store will close next year.

That’s hard to hear, but you have to admit that was a heck of a run. That becomes even clearer when you consider that Nintendo shut down the Wii U e-shop, and that console came out in 2012. If you still have your Xbox 360, and you want to swoop up some more games, you can still do it.

The Xbox 360 store will close next year

It’s hard seeing the doors close on a nearly 20-year-old legacy. However, seeing as there have been two more Xboxes since the 360, it’s no surprise that the company is soon to pull the plug. You will no longer be able to buy games from the storefront. Not only will you lose the ability to buy new games, but you also won’t be able to download DLC for them.

In the announcement, Microsoft stated that on July 29th, 2023, the company will close the Xbox 360’s storefront. So, the clock is ticking, but you’re not running out of time just yet. That’s still 11 months away from now, so you have plenty of time to scoop up more games.

This change doesn’t only affect games. If you enjoy streaming movies and TV shows on your Xbox 360, there’s bad news. When the date comes, the app will no longer function on your console. So, even if you have the app on your system, you won’t be able to stream your content.

After the date

After the date passes, you won’t be cut off from the system altogether. Of course, you’ll still be able to play the games that you’ve purchased. If you downloaded a game, but you deleted it, you’ll still be able to redownload it after the death date. That’s a neat addition.

Now, what about multiplayer games? Well, even when the storefront is gone, you’ll still be able to play online multiplayer games. You’ll be able to play them for as long as the individual developers keep the servers up.

This will mark the end of a nearly 20-year-old legacy, but it was bound to happen. If you’re looking to collect as many games as you can, you have 11 months to do so.


[ad_2]
Source link

Samsung’s The Freestyle 2 might be the best portable projector for Gamers

0
[ad_1]

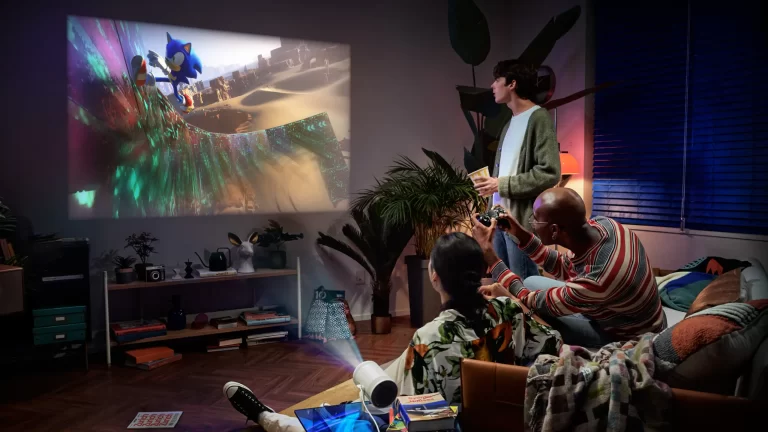
On Thursday, Samsung announced The Freestyle 2 portable projector is now up for pre-orders. The Freestyle 2 takes what made The Freestyle so great, and improves on it. Including built-in cloud gaming with support for Xbox, NVIDIA GeForce Now, Amazon Luna, Utomik, Antstream Arcade and Blacknut.

Of course, it’s still running Samsung’s TV software (which runs on Tizen), so all of your favorite TV apps are here still. That includes YouTube, Netflix, Hulu and much more. There’s also loads of ad-supported free TV available through Samsung TV Plus. There’s over 250 live TV channels in Samsung TV Plus, and it’s completely free.

The Freestyle will project an image up to 100-inches diagonal, at 1080p resolution. And it’s still pretty portable, with a weight of less than two pounds. It can also provide 360-degree sound for a pretty immersive experience.

Samsung has increased memory in The Freestyle 2, making the UX a bit snappier. But other than adding support for cloud gaming, it’s mostly the same as the original The Freestyle.

The Freestyle 2 is going to be really great for small spaces. Like a dorm room, or maybe a studio apartment. Where you really can’t afford to lose a ton of space to a TV and console table. And instead, you can place The Freestyle 2 anywhere and start playing some games or catching up on your favorite shows. So really great for taking back to school this fall.

How much is The Freestyle 2?

With adding support for cloud gaming, you might expect The Freestyle 2 to cost a bit more than the original right? Well, it’s actually $100 less.

Samsung has opened pre-orders for The Freestyle 2 today on their website for $799. And if you pre-order now through August 30, you can get a free, IP55-rated water and dust resistant case. This is a $59.99 value, so a pretty good gift for your pre-order.

Pre-order the freestyle 2 – Samsung


[ad_2]
Source link

Staggering growth of cybercrime and how data science helps improve online security

0
[ad_1]

Did you know if you were to compare the money generated by cybercrime with the GDP of world nations, it would come third behind the economic powerhouses of America and China?

Cybercrime is one of the greatest dangers facing both individuals and companies today. By the end of 2021, the total cost [PDF] of online criminality is expected to reach $6 trillion globally – with that figure increasing to an incredible $10.5 trillion by 2025.

If you were to compare the money generated by cybercrime with the GDP of world nations, it would come third behind the economic powerhouses of America and China. Somewhat unbelievably, the revenue tallied through online crime makes it larger than the entire global drugs trade and bigger than the damage caused by natural disasters annually. 

Why cybercrime has become such an issue

Ninety percent of the total data created in history has been made in the last two years and the latest figures suggest the world is now outputting an incredible 2.5 quintillion bytes of data per day (for reference, there are 18 zeros in a quintillion). Experts claim that data is now the world’s most valuable commodity – ahead of even traditional heavyweights like oil and gold.

As is always the way, where there’s money to be made, the criminals soon follow and data is no exception. From hacking private Facebook accounts to phishing attacks, malware, and MitM attacks, no business or individual is above the sights of the modern cybercriminal.

Worse yet, hackers are becoming increasingly sophisticated and devious in their tactics and are now even employing Artificial Intelligence (AI) and machine learning to automate intelligent attacks against users and companies.

The problems with complacency – particularly among business owners

Unfortunately, many company owners believe their firm to be too small or their income too low to be the target of hackers – however, the truth is quite the opposite. With many Small to Medium-sized Enterprises (SMEs) often taking a laxer approach to their online security compared to larger firms, they are becoming an increasingly tempting prospect for cybercriminals. 

SEE: Best Data Science Tools in 2020

Sometimes, this reduced data protection is down to the perceived high costs of security but, more often, it’s simply down to complacency, leading to a huge surge in attacks against SMEs. Indeed, recent research found that one in five SMEs has fallen victim to a cyberattack – and, of them, 60% fail to survive as a result and end up going out of business. 

Hackers don’t just attack businesses – individual users are a target, too

While it might be tempting to think hackers are only interested in big-time corporate attacks, their reach extends to personal users, too. Cybercrime is now a massive problem for individual users with the criminals using a vast range of tactics used to infiltrate private data – everything from credit card and financial fraud to ransomware attacks and identity theft.

Hackers are also employing different types of so-called social engineering attacks to trick users into revealing sensitive data. In 2020, phishing became the most common type of cybercrime as it is particularly effective against individual users.

Phishing sees the hacker take on the guise of a trusted and respected individual or business to gain the confidence of the user. In a typical phishing attack, the cybercriminal will contact the user through a branded email, designed to look like it came from a trusted source.

Often, they will directly ask for users to divulge private account details but, more commonly, they will redirect the individual to a similarly branded, mock website requiring them to input their account credentials.

The problems with existing rigid cybersecurity techniques

In the past, cybersecurity took a largely reactive approach to protection – more often than not by studying previous attacks then building rules and employing security measures to ensure the same attack couldn’t happen again. One example of this approach can be seen in Web Application Firewalls (WAFs), which are still widely in use today.

WAFs offer protection by identifying potentially malicious code then determining the best course of action to secure a system. However, the major issue with WAFs is that they need to be hard-coded and the rules are rigid, built on evidence from previous attacks that are then extended to isolate the signs of a future attack. 

This reactive approach to online security meant that, in real terms, the hackers were always one step ahead and had the upper hand. It also led to frequent false positives and slowing down network operability.

How data science is helping in the fight against cybercriminals

With so much data already in existence, it might seem slightly unlikely that data science principles could be used to protect the data itself. However, by studying data and, in particular, the tools and tactics used by hackers, it’s possible to build a better picture of how cybercriminals have been able to infiltrate networks and gain access to sensitive data.

By then applying machine learning processes, it’s now possible to build protection mechanisms that are proactive rather than reactive, increasing the protection of networks and digital infrastructures.

Cybersecurity Data Science (CSDS) is a growing field within the overall online security sector and represents the merging of the two disciplines. CSDS brings a more scientific approach to the protection of data. 

Experts with an online master of computer science in data science can first study previous attacks then build machine learning applications that can proactively identify threats. For example, these intelligent apps can use anomalous code detection to prevent a previously unknown type of attack from gaining access to a network.

Turning the protection idea on its head, these same machine learning apps can also be used to launch autonomous attacks against firewalls and other similar security mechanisms to identify potential backdoors or potential points of penetration. 

The takeout

There’s little doubting the dangers of cybercrime will continue to increase in coming years with hackers employing an even wider range of techniques to gain access to our private data with malicious intent. As online criminals increase their use of AI to launch these attacks, it seems only logical that cybersecurity firms will fight like with like and use data science and machine learning to stay one step ahead. 

If you thought data science was just about crunching numbers and making forecasts, think again. In the future, it’s highly likely data science will be powering your firewall and antivirus protection – from both a business and personal perspective.

Did you enjoy reading this article? Like our page on Facebook and follow us on Twitter.

[ad_2]
Source link

iPhone 13 Pro, Windows, Chrome, Linux and others pwned at Tianfu Cup

0
[ad_1]

Tianfu Cup is the Chinese version of the Pwn2own in which hackers from Kunlun Lab managed to secure first place by hacking iPhone 13 through a vulnerability in the Safari mobile browser.

The Chinese version of the Pwn2own hacking competition called Tianfu Cup took place from Oct. 16 to Oct. 17 in Chengdu, China.

The competition allowed teams of ethical hackers and security researchers to demonstrate their skills by exploiting zero-day vulnerabilities in popular software products and operating systems.

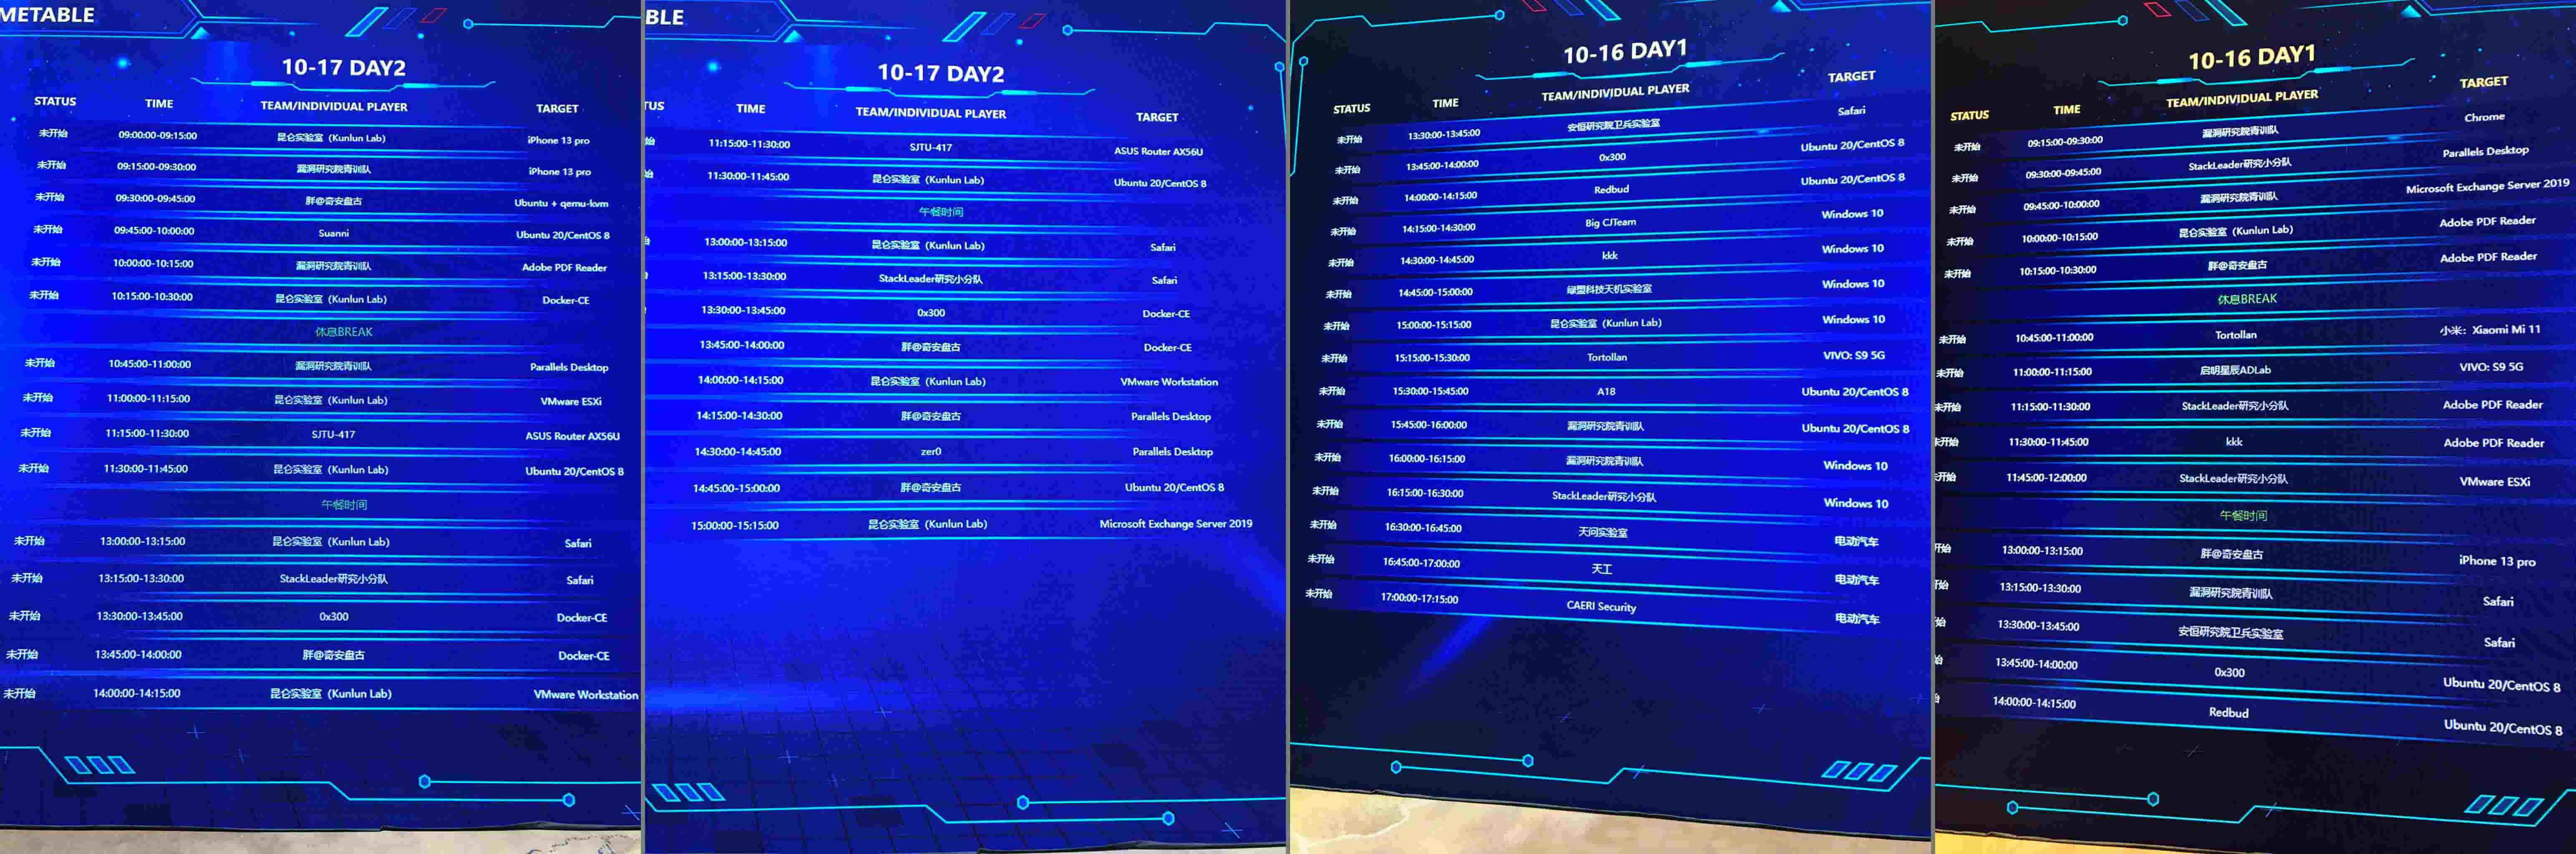
Some of the known targets in the competition included the following:

  • Linux
  • Vmware
  • Windows 10
  • VIVO: S9 5G
  • Chrome browser
  • Safari browser
  • Exchange Server
  • Vmware ESXi
  • Vmware Workstation
  • Ubuntu 20
  • Adobe PDF reader
  • Docker-CE
  • Parallels Desktop
  • ASUS Router AX56U
  • Xiaomi Mi 11.

Full list of targets exploited at Tianfu Cup

iPhone 13 Pro, Windows, Chrome, Linux and others pwned at Tianfu Cup
Full list of targets exploited at Tianfu Cup.

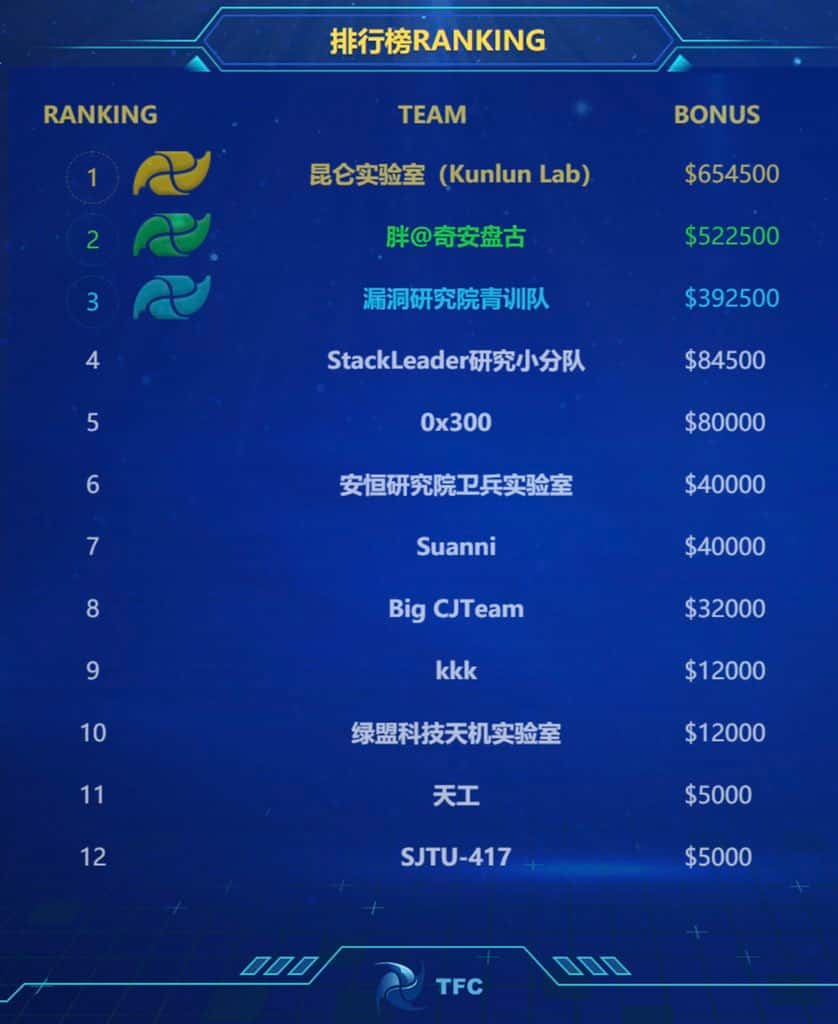
The winner of the Tianfu Cup was Kunlun Lab who made the biggest dent in the pot. The team managed to secure $ 654,500 in total for several feats, including hacking iOS 15 through a vulnerability in the Safari mobile browser.

On the other hand, Pangu Team won 300,000 US dollars after breaking into an iPhone 13 Pro during this weekend’s Tianfu Cup.

The team has been known for jailbreaking mobile phones since 2014. This time they managed to crack the security of a brand new top model with iOS 15.

Although technical details are limited at the moment, it will be the first time that someone has publicly demonstrated a successful remote attack on the iPhone 13 since its release on Friday, September 24.

iPhone 13 Pro, Windows, Chrome, Linux and others pwned at Tianfu Cup
Teams and prize money they won at Tianfu Cup.

As part of the challenge, participants had to circumvent the Pointer Authentication Code (PAC), a security mechanism (in practice a cryptographic signature of pointer values) that Apple has introduced at the chip level.

In total, prizes were awarded for 1.88 million dollars, which is equivalent to just over £1.37 million. Since iPhone 13 is one of the most expensive smartphones in the market at the moment, it is expected that Apple will be contacted by security researchers about the vulnerabilities identified during Tianfu Cup.

Therefore, expect more iOS 15 security updates in the coming weeks.  

Did you enjoy reading this article? Like our page on Facebook and follow us on Twitter.

[ad_2]
Source link

Beware- FontOnLake Rootkit Malware Attacking Linux Systems

0
[ad_1]

According to ESET’s researchers, components of FontOnLake malware are divided into three groups: Trojamized app, Rootkit, and Backdoor. 

Researchers at Slovak cybersecurity company ESET have identified a new malware family utilizing custom and well-designed modules. In ESET’s white paper [PDF], researchers revealed that the malware dubbed FontOnLake Rootkit malware targets Linux systems and its modules are under active development.

The malware samples uploaded to VirusTotal indicate that the first intrusion through this previously unidentified threat happened in May 2020. Tencent, Lacework Labs, and Avast are also tracking this malware using the moniker HCRootkit. 

About FontOnLake

Researchers noted in their report that FontOnLake has a “sneaky nature,” “advanced design,” and “low prevalence.” Therefore, it is easier to use this malware in targeted attacks.

According to ESET researcher Vladislav Hrčka, it allows remote access to the attackers, can serve as a proxy server, and steal credentials. This malware family uses “modified legitimate binaries” to collect data, and these binaries have been adjusted to load more components.

Moreover, to stay undetected, the malware uses a rootkit. These binaries are used on Linux systems but “can additionally serve as a persistence mechanism,” Hrčka wrote in a blog post.

Likely Targets

The information about its C&C server’s location and the countries where the samples were uploaded indicates that the campaign targets users in Southeast Asia.

ESET researchers further stated that they have discovered two versions of the Linux rootkit based on the Suterusu open source project and perform similar functions such as:

  • File hiding
  • Hiding itself
  • Process hiding
  • Performing port forwarding
  • Hiding network connections
  • Exposing the collected credentials to its backdoor
  • Magic packets reception (These packets instruct the rootkit to download and execute another backdoor)

“We believe that FontOnLake’s operators are particularly cautious since almost all samples seen use unique C&C servers with varying non-standard ports. The authors use mostly C/C++ and various third-party libraries such as Boost, Poco, or Protobuf. None of the C&C servers used in samples uploaded to VirusTotal were active at the time of writing – which indicates that they could have been disabled due to the upload,” researchers explained.

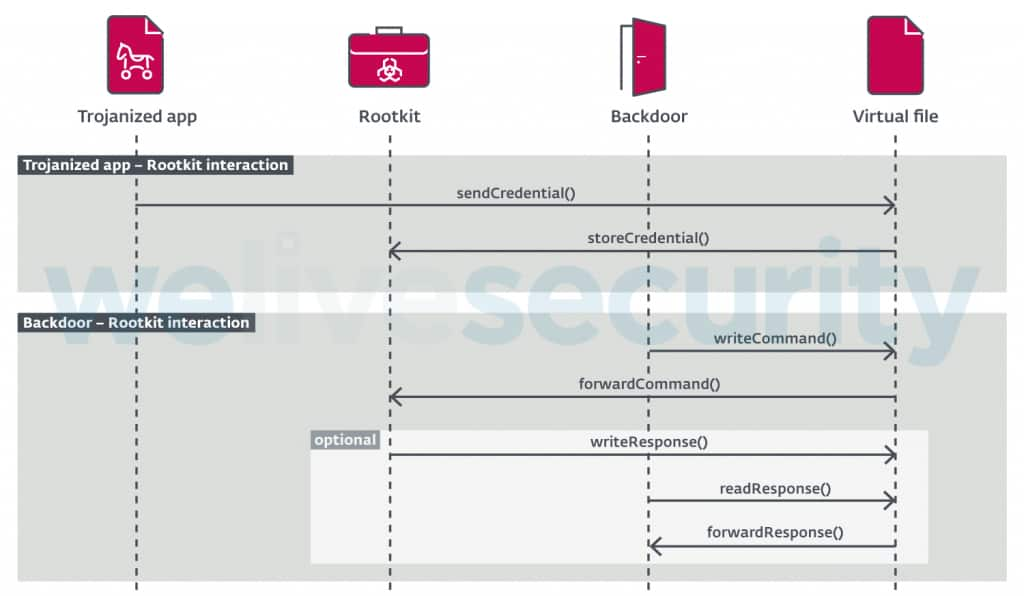
Beware- FontOnLake Rootkit Malware Attacking Linux Systems
Interaction of FontOnLake’s components

Known Components

As shown in the screenshot above; FontOnLake malware’s known components are divided into three groups: Trojanized applications are the modified legitimate binaries adjusted to conduct a range of malicious activities.

The second component is user-mode backdoors that serve as the main communication point for the malware operators. Thirdly, it has Rootkits, which are kernel-mode components used to provide fallback backdoors and assist with updates.

“Their scale and advanced design suggest that the authors are well versed in cybersecurity and that these tools might be reused in future campaigns,” Hrčka wrote, adding that most of the features are designed to hide FontOnLake’s presence, offer backdoor access, and relay communication, researchers concluded.

Did you enjoy reading this article? Like our page on Facebook and follow us on Twitter.

[ad_2]
Source link