Analyst believes Apple is cutting iPhone 15 production, before official launch

0
[ad_1]

Typically, we hear from analysts around a big launch like the iPhone 15 launch. However, this one is a bit surprising. According to analyst Jeff Pu, Apple is apparently already cutting production of the new iPhone 15 models.

Pu mentions that Apple is expected to build approximately 77 million iPhone 15 units by the end of the year. Apple was originally estimated to build around 83 million units by the end of the year. So it’s a reduction, but not a huge one – about 7%.

So why could Apple be cutting production already? Well, according to Pu, there are two main reasons for this. First, the more obvious one is, supply issues. Yes, three years after the pandemic started, we’re still talking about supply chain issues. And it is likely to affect the mass production of iPhone 15. Specifically, Pu is mentioning the Sony camera sensors as well as the new titanium frame for the pro models. Another issue that Apple might be having is with the new thinner bezels on the Pro displays here.

Apple may have adjusted production based on projected demand

Companies like Apple are usually really in tune with the demand for an upcoming product. While something like the iPhone will be starting mass production months ahead of the launch, Apple still needs to have a rough idea of how many units they are going to sell. And it could be that the cut in production is due to the demand concerns.

While some are thinking that the iPhone 15 is going to be a super-cycle for Apple, others don’t agree. On top of that, the iPhone 15 Pro and Pro Max are set to be more expensive than their predecessors. Seeing the first real price increase in the US since the iPhone X back in 2017. Which could result in lower demand too. Of course, we cannot forget about the fact that iPhone sales revenue dropped in the third fiscal quarter of 2023. From $40.67 billion to $39.67 billion. Not a huge drop at all, but a drop nonetheless.

Then there’s the iPhone 16. There’s rumors that this could be a huge upgrade for the iPhone. With WiFi 7 and a new 48-megapixel ultrawide sensor being included. Of course, there’s a long way to go for the iPhone 16, and likely plenty more upgrades coming to that model too.


[ad_2]
Source link

New Garmin heart rate monitor device is coming soon

0
[ad_1]

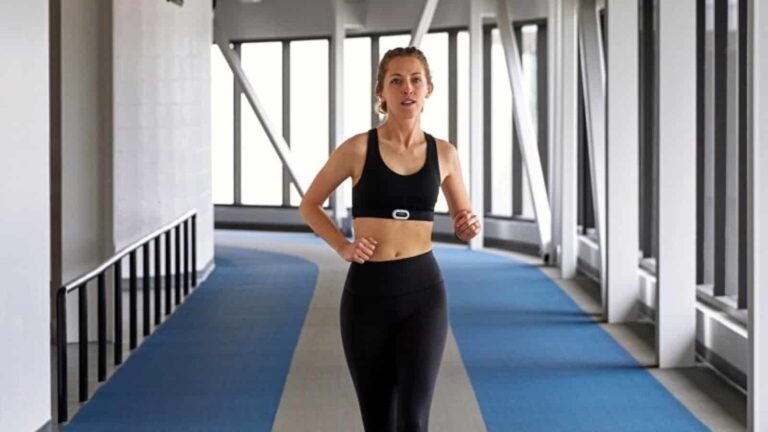
Garmin makes great smartwatches, and now they are turning attention to a new heart rate monitor device. Of course, most Garmin smartwatches come with heart rate monitoring, but this new device is different. According to the reports, this is more of a smart band than it is a smartwatch, and it doesn’t fit on the user’s wrist.

This coming device is not the first of its kind, but it’d stand out in the crowd of health-tracking devices. Some sources have already spotted this device on the Malaysian SIRIM database. From the naming of the device on this database, it’s clear that this coming device will join another Garmin product line-up.

The name of this coming Garmin heart rate monitor device is the HRM-FIT, and this name isn’t new. Already the fitness brand, Garmin, has an existing HRM line-up that consists of Pro, Dual, and Pro Plus entries. Just like these current devices, this coming might follow their styling and functions.

You’d soon be able to track your health on the go with the coming Garmin heart rate monitor

The coming Garmin heart rate monitor device will join the HRM line-up and offer some vital stats. This device will be a fitness tracker, but it’ll offer a few benefits against purchasing a smartwatch. Also, this coming entry will improve on certain features and heart rate monitoring technology present in its predecessors.

Considering that this coming device isn’t a smartwatch, it might not come with a screen. For this reason, users will access their health details via their smartphone, as both devices will sync together. Not having a screen might be beneficial to some users since this device will eradicate any screen distraction.

Of main concern to most potential buyers of this device would be its health features and technology. This device will come with a heart rate monitoring feature, excellent battery life, smartphone connectivity, walking/running tracking features, and so much more. These are just some features that you can find on the HRM-Pro and the HRM-Pro Plus.

It’s safe to say that this coming heart rate monitoring device would be purely sporting-oriented. This device’s design might be similar to the already existing HRM devices that are available for purchase on the Garmin official website. If it follows the same design language, then users will strap it around their chest while in use.

This might be an awkward position for a fitness tracker, but it can erase the need for a smartwatch. Additionally, this coming Garmin HRM-Fit would be much more affordable than most of the brand’s smartwatches. For this reason, some people looking out for a workout partner would quickly opt for the HMR-Fit instead of a more expensive smartwatch. More details on the launch of this device and its specifications will soon be made available.


[ad_2]
Source link

Another price hike for Amazon Music Unlimited, this time Prime members will pay more

0
[ad_1]

“I want to pay more for the same service!” said no one ever, yet here we are: Amazon Music Unlimited is raising prices for certain subscription plans, including Amazon Prime members.

Following Spotify’s recent price hike and YouTube Premium’s monthly subscription increase, now it’s time for Amazon Music Unlimited to announce the news (via 9to5Mac). It’s like they’re taking turns at this point. Apple Music raised its plans almost a year ago, so maybe this coming fall it will be their turn again… (we really hope this joke does not materialize).

This is not even the first time Amazon Music Unlimited has raised its prices this year alone. At the beginning of 2023, they upped individual and student subscription plans from $9.99 to $10.99 and from $4.99 to $5.99, respectively. In 2022, the Music Unlimited for Prime subscription went from $8 to $9 per month ($79 to $89 annually).

The price increases are to go into effect immediately for new customers. Current Amazon Music Unlimited users are given a little more than a month – they will be charged more come September 19. For the record, Amazon claims that price increases will “bring you even more content and features” in the future.

Who’ll pay more?


So, the individual plan for Prime members for Amazon Music Unlimited is changing from $8.99 to $9.99 per month. If you’re the type of person who’s into single yearly payments, you can kiss the current $89 goodbye and say hello to the new 12-month tariff: $99.Those on the family plan will too face a $1 increase for the monthly subscription rate, and $10 for the year-round plan: from $15.99 to $16.99, and, respectively, from $159 to $169.

For those that are wondering what type of Amazon Music type of subscription would suit them best, here’s a nice comparison chart between Free, Prime and Unlimited.


[ad_2]
Source link

Cisco Communications Manager Flaw – SQL injection Attacks

0
[ad_1]
Cisco Communications Manager Flaw

An SQL injection vulnerability was discovered in the web-based management interface of Cisco Unified Communications Manager (Unified CM) and Cisco Unified Communications Manager Session Management Edition (Unified CM SME). 

Cisco Unified CM is used for handling voice and video calls, whereas Cisco Unified CM SME is used for session routing intelligence.

This SQL injection vulnerability allows an authenticated remote attacker to conduct SQL injection attacks on any affected system. However, Cisco has released software updates to fix this vulnerability.

CVE-2023-20211: SQL Injection Vulnerability

This vulnerability exists due to improper validation of user-supplied input. An attacker can authenticate as a read-only user into the application and exploit this vulnerability by sending crafted HTTP requests to an affected system.

The result of a successful exploitation results in reading or modifying the data in the system or performing privilege escalation. The CVSS score for this vulnerability is given as 8.1 (High).

Affected Products

Products that are affected due to this vulnerability include Cisco Unified CM and Cisco Unified CM SME. In addition, Cisco has also mentioned that the below products are not affected by this vulnerability.

  • Emergency Responder
  • Finesse
  • Hosted Collaboration Mediation Fulfillment (HCM-F)
  • Packaged Contact Center Enterprise (Packaged CCE)
  • Prime Collaboration Deployment
  • Prime License Manager (PLM)
  • SocialMiner
  • Unified Communications Manager IM & Presence Service (Unified CM IM&P)
  • Unified Contact Center Domain Manager (Unified CCDM)
  • Unified Contact Center Express (Unified CCX)
  • Unified Contact Center Management Portal (Unified CCMP)
  • Unified Intelligence Center
  • Unity Connection
  • Virtualized Voice Browser

Fixed in Version

Cisco Unified CM and Unified CM SME ReleaseFirst Fixed Release
11.5(1)Migrate to a fixed release.
12.5(1)12.5(1)SU8
14Apply patch file
ciscocm.V14SU3_CSCwe89928_sql-injection_C0194-1.cop.sha512.

Users of these products are recommended to upgrade to the latest version to prevent threat actors from exploiting this vulnerability.

Keep informed about the latest Cyber Security News by following us on GoogleNews, Linkedin, Twitter, and Facebook.


[ad_2]
Source link

New York City bans TikTok from all government devices

0
[ad_1]

New York City has banned TikTok from all government devices. The directive issued on Wednesday requires city agencies to remove the ByteDance-owned social media app from their official devices within 30 days, while new downloads of the app are banned immediately. City employees are also barred from accessing the video-sharing platform through its website on city-owned mobile phones, tablets, computers, and other gadgets.

The decision came after NYC Cyber Command, which is a subset of the city’s Office of Technology and Innovation and leads its cyber defense efforts, stated that TikTok “posed a security threat to the city’s technical networks.” In its directive, New York City cited US Office of Management and Budget guidelines encouraging government authorities to ban TikTok’s use on official devices. The city also mentioned a similar federal legislation passed earlier this year.

“While social media is great at connecting New Yorkers with one another and the city, we have to ensure we are always using these platforms in a secure manner,” a New York City Hall spokesperson said in a statement to The Verge following the announcement of the TikTok ban. “NYC Cyber Command regularly explores and advances proactive measures to keep New Yorkers’ data safe.”

Several other US states have banned TikTok on government devices

New York City joins several other US states and localities in banning TikTok from official devices. New York State banned the app on state-owned devices way back in 2020. But things went particularly downhill for the social media platform late last year after FBI Director Christopher Wray labeled it as a national security threat. The US lawmakers believed TikTok’s Chinese owner ByteDance has backdoors for the country’s ruling party.

More than 30 US states and the federal government have since banned the app on government devices. In May, Montana went a step ahead of others and announced a statewide ban on TikTok, blocking citizens from using the app within its territorial jurisdiction. The ban is to take effect on January 1, 2024. However, TikTok users and the company itself have sued the state over the decision. The legal hurdles may delay the ban or even revoke it.

Meanwhile, Congress is pushing for a nationwide ban on TikTok. In March, the US House Foreign Affairs Committee passed the bill, known as the Deterring America’s Technological Adversaries (DATA) Act, to ban the popular Chinese social media platform across the country. This is despite ByteDance repeatedly denying the reports that Beijing has access to its user data. Time will tell whether TikTok manages to avert a nationwide ban in the US.


[ad_2]
Source link

Major iPhone 16 Pro improvements may convince you to skip the iPhone 15 Pro

0
[ad_1]

The iPhone 15 series is right around the corner, and the iPhone 15 Pro series is set to deliver some notable improvements. Still, based on a new report, the iPhone 16 Pro will be a true jump forward, so you may want to skip the iPhone 15 Pro, and wait for next year’s model.

The iPhone 16 Pro may bring notable improvements, which may push you to skip the iPhone 15 Pro

Well, according to Jeff Pu (via MacRumors), a tech analyst, we’re looking at some notable improvements with the iPhone 16 Pro series. The phones will allegedly come with a new 48-megapixel ultrawide camera. On top of that, Wi-Fi 7 is said to be supported by both.

That’s basically all the info he shared. Is that enough for you to wait? Well, that’s a question only you can answer. It’s also worth noting that other improvements will be included, but we still don’t know the details.

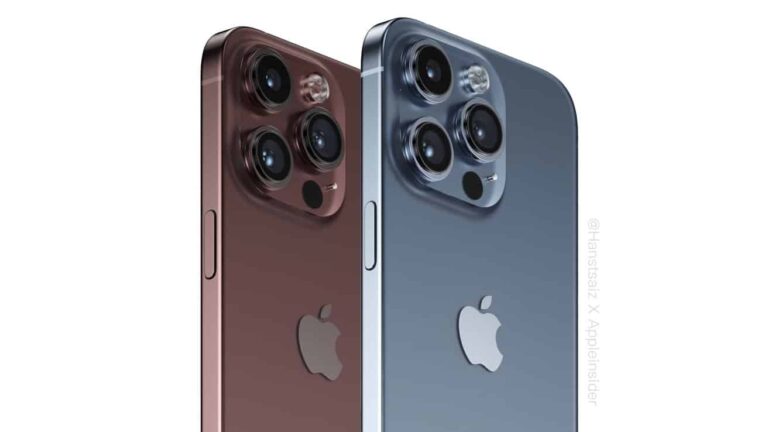
What we do know, however, is what the iPhone 15 Pro series is bringing. It will have noticeably thinner bezels than the iPhone 14 Pro models, and also a frame made out of titanium. On top of that, a Type-C USB port will be included, as will an Action Button. The iPhone 15 Pro Max model will also offer a periscope telephoto camera.

The regular iPhone 15 Pro won’t offer a periscope telephoto camera

So, one might argue that the iPhone 15 Pro series is bringing more than enough improvements. Well, once again, that’s something only you can answer. Another thing to note is that the iPhone 16 Pro (smaller model) will feature a periscope telephoto camera too, allegedly, but the iPhone 15 Pro won’t, unlike the Pro Max model.

The entire iPhone 15 series is expected to arrive next month. Apple will allegedly announce the phones on September 12 or 13, while they’re expected to go on pre-order on September 15. You’ll be able to buy them in stores on September 22. Those are just rumored dates, for now, so keep that in mind.


[ad_2]
Source link

HPE Aruba Networking Product Vulnerabilities Allow File Overwrite

0
[ad_1]

The vulnerabilities, CVE-2023-38401 and CVE-2023-38402, affect the HPE Aruba Networking Virtual Intranet Access (VIA) client for the Microsoft Windows operating system. If the exploit is successful, the attacker can overwrite arbitrary files.

HPE Aruba Networking has issued an upgrade to address these multiple high-severity vulnerabilities. There is no workaround for these vulnerabilities. 

The company said that versions of the Networking Virtual Intranet Access (VIA) that have reached the End of Maintenance (EoM) milestone are not patched.

Details of the Vulnerabilities

  • CVE-2023-38401 – Local Privilege Escalation

The flaw tracked as CVE-2023-38401 with a CVSS score of  7.8 with high severity range found in the HPE Aruba Networking Virtual Intranet Access (VIA) client might allow local users to elevate privileges.

Will Dormann (@wdormann) found and reported this vulnerability through Networking’s Bug Bounty Program.

“The Successful exploitation could allow execution of arbitrary code with NT AUTHORITY\SYSTEM privileges on the operating system”, Aruba Networks said in its advisory.

  • CVE-2023-38402 – Arbitrary File Overwrite

The Arbitrary File Overwrite flaw is tracked as CVE-2023-38402 with a CVSS score of  7.1 with high severity range. 

The Networking Virtual Intranet Access (VIA) client has a flaw that might let malicious users overwrite arbitrary files as the NT AUTHORITY SYSTEM.

Through the HPE Aruba Networking Bug Bounty Program, Gee-netics found and reported this vulnerability.

“A successful exploit could allow these malicious users to create a Denial-of-Service (DoS) condition affecting the Microsoft Windows Operating System boot process,” reads the advisory.

Affected Products

These flaws impact Networking Virtual Intranet Access (VIA) customers running the following versions:

– HPE Aruba Networking Virtual Intranet Access (VIA) client for Microsoft Windows:

    – 4.5.0 and below.

These flaws do not impact HPE Aruba Networking Virtual Intranet Access (VIA) customers running other operating systems.

Fix Available

The HPE Aruba Networking Virtual Intranet Access (VIA) for Microsoft Windows should be updated to version 4.6.0 or higher to fix the vulnerabilities present.

Keep informed about the latest Cyber Security News by following us on GoogleNews, Linkedin, Twitter, and Facebook.


[ad_2]
Source link

London police says every six minutes a smartphone is stolen in this city

0
[ad_1]

The London mayor and Met Police say in the course of every six minutes, a smartphone is stolen in this city. So If you are traveling to London, it’s better to look after your smartphone.

According to the BBC, nearly 250 smartphones a day, or 90,864 phones a year, are stolen in London. City officials are now asking the manufacturers to make their devices less appealing to thieves. London Mayor Sadiq Khan and Met Chief Sir Mark Rowley urged smartphone manufacturers to “design out” incentives in their products. Additionally, software designers are required to “develop solutions to make this crime less rewarding.”

London is becoming the capital of smartphone theft in the world

The officials asked manufacturers to collaborate with the City Hall and police department to reduce crimes. The high crime rate in London has become a problem for the city authorities. Statistics show that 38% of all personal robberies in London last year involved a smartphone being stolen. Likewise, mobile phones accounted for nearly 70% of all thefts in London last year.

“The current practice of allowing stolen mobiles to be re-registered by new users within the phone industry inadvertently enables a criminal market which drives robbery, thefts, and violent offending in London.” The Met Police chief said. As per police data, young smartphone owners between the age of 14-20 are more likely to be targeted by thieves. On the other hand, most criminals involved in smartphone robberies also belong to a younger demographic.

Asking smartphone makers to “design out” their devices to prevent robberies might seem odd. Every company wants to sell more smartphones in a year. And no company would ever sacrifice its device’s features and beauty to stop criminals from stealing it. Tech expert Jake Moore also believes what the London mayor and Met Police chief proposed won’t work because companies are reluctant to enforce these policies. “It would cause a potential nightmare, and you could find people accused of owning a stolen phone when it’s actually theirs,” he added.

In previous years, car manufacturers could reduce the theft of car radios and satellite navigation gear by integrating them into vehicle dashboards. It remains to be seen if a similar plan works for the stolen smartphones in London.


[ad_2]
Source link

Enhancing e-commerce security with web application firewalls

0
[ad_1]

Web Application Firewalls (WAFs) defend applications against cyber threats that aim to exploit vulnerabilities in web applications. These attacks mainly aim to steal sensitive data or bring down the website. According to statistical data, by 2027, WAFs size is expected to reach USD 13.8 Billion.

Many e-commerce companies are implementing WAF (Web Application Firewall) into their IT infrastructure since it is a barrier between website and internet traffic, which monitors and filters HTTP requests.

Understanding the Basics: What is a Web Application Firewall (WAF)

WAF or web application firewall safeguards web applications by monitoring and filtering HTTP traffic that flows between the application and the internet. WAFs block all malicious requests, present a challenge to suspicious requests, and allow visitors to access your website securely.

One of the most common attacks that WAF protects against is DDoS (denial of service) attack. These attacks are performed by sending excessive traffic to the web application, which causes the server to become overloaded and unable to process legitimate requests.

The Increasing Importance of Security in E-Commerce

The increasing significance of security in e-commerce is driven by the growing incidence of regulatory requirements, data security concerns, expanding reach of e-commerce, and cyber security issues. To protect customers’ data, e-commerce should implement robust cyber security protocols.

Specific Security Threats Faced by E-Commerce Websites

E-commerce websites have to face several security threats because of the valuable data they handle. Below are the key security threats faced by e-commerce websites.

Payment-Card theft

Cybercriminals target e-commerce websites to steal payment card data, including expiration dates and credit card numbers, through several methods like web skimming.

SQL Injection (SQLi) and Cross-Site Scripting (XSS)

These web application vulnerabilities allow hackers to implement malicious codes, steal sensitive information, and manipulate data from the user’s web browsers or website’s database.

Distributed Denial of Service (DDoS)

E-commerce websites are vulnerable to DDoS attacks that overpower their server with huge amounts of traffic, causing prolonged or temporary downtime.

How WAFs Enhance E-Commerce Security: The Technical Perspective

Let’s look at how WAFs enhance e-commerce security from a technical perspective.

Web traffic filtering

The WAF is configured to intercept incoming and outgoing traffic between the client and the web application server. In incoming traffic, the WAF checks suspicious activity and identifies malicious traffic patterns that specify intrusion attempts, e.g. SQL injection and cross-site scripting (XSS), etc.

Geo-location filtering

WAF can be configured to block traffic from specific countries or regions, helping to reduce the number of attacks reaching applications.

Application Programming Interface (API) security

For e-commerce businesses that use APIs for several integrations, WAF can protect API endpoints from cyber attacks and enforce API-specific privacy policies.

SSL/TLS termination

Some advanced WAFs offer SSL/TLS termination capabilities. They help in decrypting incoming encrypted traffic, re-encrypt traffic, and inspect for threats before sending it to the application server. These allow the WAF to examine the traffic in clear text, enhancing its capability to block and detect attacks hidden in encrypted data.

Real-World Examples: E-Commerce Businesses Benefiting from WAFs

Let’s look at some of the real-world examples where e-commerce businesses benefit from WAFs.

SHOPPY

SHOPPY, an e-commerce business based in Xiamen, China uses CloudFlare WAF for its websites. It is now more protected from application vulnerabilities, brute-force login attempts, and malicious attacks. WAF has created a dedicated security defense system for them, making SHOPPY more secure for its online customers.

Alibaba

Alibaba Group is a Chinese Multinational e-commerce conglomerate operating multiple online services and marketplaces. It deploys WAFs across its several platforms to secure customer data, protect against web-based threats and prevent unauthorized access.

Choosing the Right WAF for Your E-Commerce Business: Key Factors to Consider

Choosing the right WAF is a challenging task, but there are several criteria that can help you in your analysis:

Functionalities

Assess the functionalities offered by the WAF, e.g. prevention of SQL injection attacks, defense against DDoS attacks, alleviation of malicious bots, and other features that meet the needs of the organization.

Scalability

Ensure the WAF is scalable and capable of meeting your organization’s growing needs and requirements.

Usability

Evaluate the ease of use of the WAF, verifying that the management interface is intuitive and that the automation features help simplify security management.

Technical Support

Ensure the WAF vendor offers good technical support, including business hours or 24/7 support, complete documentation, and training resources.

Implementing a WAF in an E-Commerce Environment: Step-by-Step Guide

Implementing a WAF in an e-commerce environment is a vital step to improve privacy and protect against diverse online threats. Below are step-by-step guides to help you implement a WAF efficiently:

Step 1: Assessment and Planning

Identify the e-commerce application’s architecture, including the application server, database server, and web server. Also, verify the types of safety threats the WAF should protect against based on the e-commerce platform’s possible risks and vulnerabilities.

Step 2: Preparation

Inform your operation and development team about the upcoming WAF execution to guarantee the least disruption and coordination. Also, back up your e-commerce databases and websites to guarantee you can restore the environment in case of any problem during the implementation process.

Step 3: Configuration

Configure SSL/TLS termination settings; configure the WAF settings based on your privacy requirements. This will contain specifying rules for common threats like XXS or SQL injections. Enable geo-location filtering to block traffic from malicious websites or high-risk regions.

Step 4: Testing

You should perform systematic testing of WAF before putting it into production. Test dissimilar scenarios, including virtual attacks and valid traffic. Perform vulnerability scanning to guarantee WAF efficiently blocks common web application vulnerabilities.

Step 5: Monitoring

Do continuous monitoring to capture possible threats. Regularly review WAF performance metrics to guarantee its efficiency and recognize any anomalies. Also, keep WAF rules and software updated to defend against new threats.

Step 6: Incident Response

Implement an incident response plan, particularly for WAF-related privacy incidents, to handle detected attacks and threats efficiently.

Step 7: Educate Employees and Users

It is important to train employees about the significance of WAF and how to respond to possible security incidents. Also, inform your users about best practices for online security, including how to avoid phishing attacks.

Maintaining and Updating Your WAF: Best Practices for Continued Security

Maintaining and updating WAF is important to guarantee privacy in e-commerce. Implement these best practices to keep WAF updated and effective:

Threat intelligence integration

It is important to integrate threat intelligence feeds in WAF to guarantee its ability to block and detect possible threats.

Logging and monitoring

Maintain a check on detailed logs of WAF activity, monitor them regularly, and respond quickly to any suspicious activity.

Incident response planning

Develop an incident response plan, particularly for WAF-related privacy incidents, to handle possible threats effectively.

Final Words

A WAF protects your website against known cyber attacks such as cross-site scripting (XSS), SQL injection, and malicious activities. Usually, these threats use an authorized protocol, such as HTTP, and attack applications and systems via that protocol.
[ad_2]
Source link

Banned: NY city employees have 30 days to delete (and not download again) TikTok

0
[ad_1]

The state of Montana should be really proud of New York City: it has banned TikTok on city-owned devices. City employees and agencies have 30 days to remove the app and not use it again. All of that is over security concerns.

A nationwide TikTok ban is something you’ve been hearing for years now. While it’s not clear when (or if) such a harsh measure could be imposed on private citizens, it’s definitely being implemented wider and wider on the government front by the day.

The Verge has the story about the Wednesday-issued directive, that’s starting immediately and is banning TikTok for city employees not only on mobile devices but also forbidding them to access the short video-sharing app’s website from any city-owned devices. That’s because TikTok “posed a security threat to the city’s technical networks”, a city official said and added:Members of the New York City agencies have 30 days to remove the application from Chinese tech giant ByteDance, which was repeatedly painted by both FBI Director Christopher Wray and CIA Director William Burns as a threat and as a negative influence by China’s government to US citizens.

Even before those comments by high-level security officials, many US states had already banned TikTok on government-owned devices. Montana went a tad further and in May, Governor Greg Gianforte signed a bill banning the app within the entire state – the first state to do so.

TikTok is used by more than 150 million Americans (close to half of the population). Controversy over security concerns and a Chinese government influence arose more than three years ago. Even people who dislike TikTok’s lifestyle influence on the younger generation and – to put it mildly – are not fans of the app, are in a dilemma, when matters come to a nationwide ban, citing First Amendment infringes.


[ad_2]
Source link