Google Pixel has the third-largest Android brand in North America

0
[ad_1]

According to recent statistics, Google Pixel is now the third-largest Android brand in North America. At the moment, in this region, Google Pixel accounts for 2.46% of Android smartphones out in the wild. This means that more and more people are gaining interest in the brand and purchasing some of its products.

Fans in this region are proud of this growth, and so is Google, the owner and manufacturer of the Pixel brand. The brand has gained these numbers from Android users that were previously into Samsung or Motorola devices. Additionally, part of this number is Apple users that have switched over to the Android side in the North American region.

While 2.46% of all devices in North America sounds small, it is a great growth for Google Pixel. Over the past years, the brand has appealed to netizens as a phone for core Android fans and enthusiasts looking out for the best software experience. But all of that is changing and people are now benefiting from the ton of features that Google has been packing in their Pixel devices over the past few years.

Google Pixel is crushing its game in North America as it gains more users

Over the years, the Google Pixel brand has rolled out a good number of smartphones. Some of these entries only appealed to enthusiasts that wanted that pure stock Android software feel. This is because Google is the company that owns Android, therefore it’s only right that they offer the best software experience on their devices.

One device release after another, Google proved to the crowd that they offer the purest Android feel on a device. But users didn’t just want the purest Android feel, they wanted more than that. They wanted performance, great camera technology, sleek design, a better ecosystem of devices, and so much more.

Google knew that they were up to the task and got all hands-on deck to give users what they wanted. The Pixel 4 series marked a revolution for the Pixel smartphone line-up. Moving on from the Pixel 4 series, Google kept nailing it, one device launch after another, from the 5 series to the 7 series.

With the 6 series, Google brought its own processor (Tensor) to the smartphone market. This gave the Pixel 6 series better camera technology and also helped refine the performance as well as the software experience. The Pixel 7 series hit the launch stage with a new and refreshed Tensor processor, improving upon the previous processor on the 6 series.

Google’s improvements over the years have earned it a place as the fourth-largest smartphone brand in North America. Additionally, the brand is also the second-largest in Japan and the fourth-largest in Australia. With the launch of the coming Pine 8 series, Google will continue growing the Pixel brand one step at a time.


[ad_2]
Source link
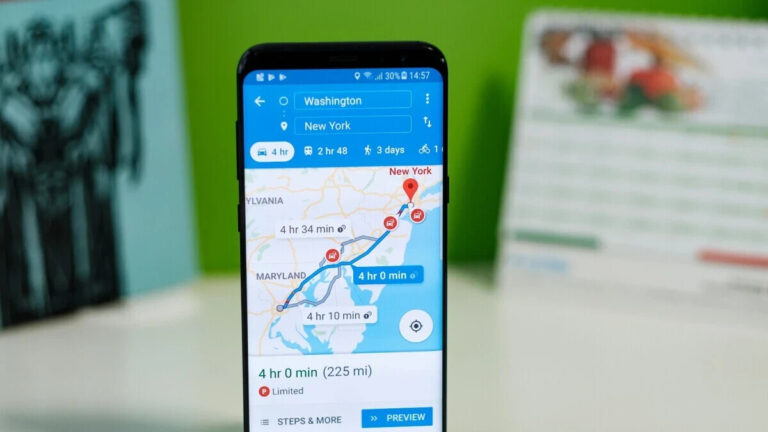
It now takes a swipe instead of a tap to see a full-screen map in Google Maps

0
[ad_1]
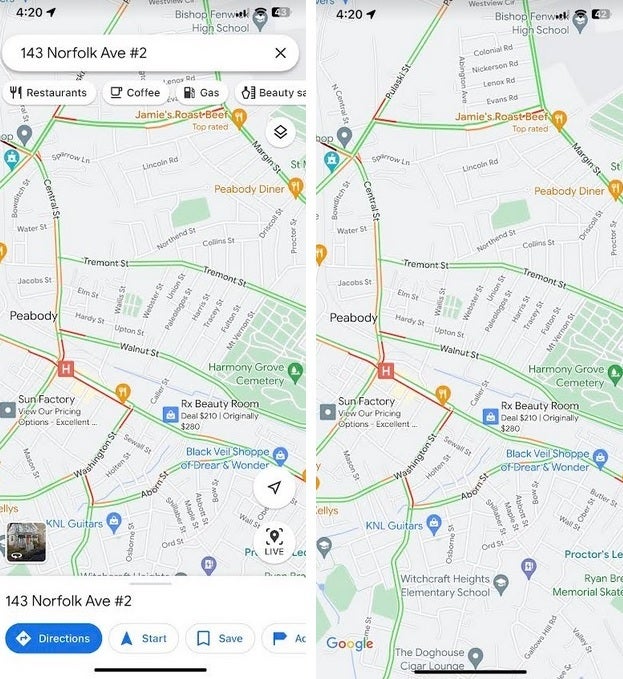
Spotted first by 9to5Google, it used to be that when you wanted to remove the top search bar and the bottom bar from Google Maps, you would tap on the screen and end up with a full-screen map. But Google has made a change. Now, if you want to see just a map and nothing more than a map on your display, you simply swipe up on the search bar and both top and bottom bars go away.
It is interesting how the rationale changed. At first, Google had you tap the map anywhere on the screen to remove the bars because a full-screen map is what you wanted to see. But with the change, Google has you sliding up on the search bar as if you could slide it off of the display to leave the full-screen map to view. And now, after you remove the top and bottom bars by swiping up on the search bar, you can return them to the screen by tapping on the display.
Keep in mind that if you tap on the screen with both bars showing, instead of making them disappear like they used to, it will drop a pin on the location you tapped.

So let’s recap. If you want to remove the top and bottom bars on Google Maps to leave a full-screen map, swipe up on the search bar at the top of the display. If you want to bring back the top and bottom bars, just tap on the screen. Yes, this is different than the method you might have used at an earlier time to leave yourself with a full-screen map, but this is what happens when you’re dealing with “progress.” Google started testing this earlier this year and it seems to have been rolled out to the iOS and Android versions of the app.

There is the possibility that you might have to swipe on the search bar twice to get to the full-screen map. That would be only when the Explore tab’s “Latest in [the Area]” bar is showing at the bottom of the screen. In that case, you’ll swipe the top search bar once to remove the bottom bar and swipe again to remove the search bar.


[ad_2]
Source link

New SectopRAT Steals Browser Passwords, 2FA Codes

0
[ad_1]

LummaC, an information stealer, is being disseminated on Russian-speaking forums through a Malware-as-a-Service (MaaS) approach. Sensitive data from affected devices is intended to be stolen by this malware. 

Cryptocurrency wallets, browser add-ons, two-factor authentication credentials, and numerous files are some of the data that are targeted.

Recently, Cyble Research & Intelligence Labs (CRIL) discovered a cutting-edge strategy for disseminating SectopRAT. 

SectopRAT is a . NET-based remote access malware.  It has a wide range of capabilities, including stealing browser data and cryptocurrency wallet details.

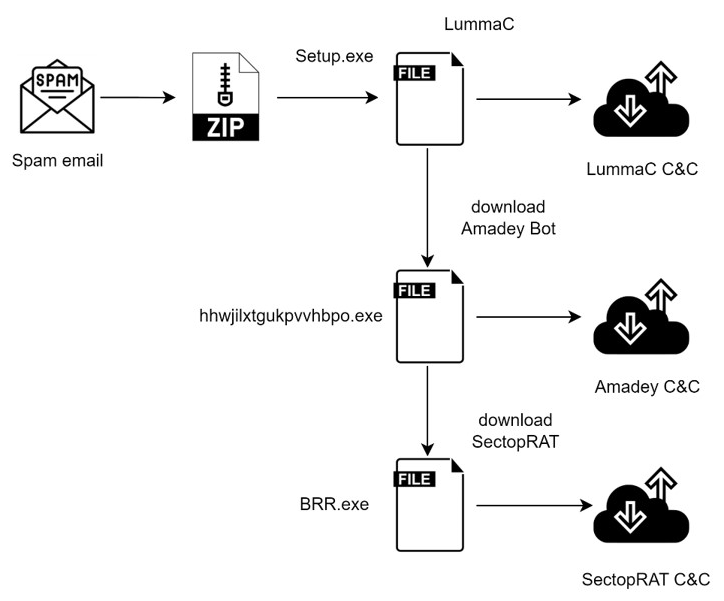
This method involves retrieving the Amadey bot malware from the LummaC stealer and using it to deliver the SectopRAT payload.

The Attack Chain

The LummaC Stealer has mostly been spread using spear-phishing emails and phishing websites that seem to be legitimate software providers.

Infection chain

In the past, the LummaC stealer was spread via fraudulent websites like those selling fake Microsoft Sysinternals Suite. Spear-phishing emails were used to target YouTubers as well. It spread further by pretending to be illegal software cracks.

Researchers come across ZIP files that appear to contain the LummaC stealer malware in the wild. Through a YouTube campaign disguising them as software setup files, these files are being circulated. 

These files appear to have been labeled to lure users in and mislead them into running the malware they carry.

The TAs’ information indicates that LummaC2 is a next-generation stealer with a high success rate. Notably, it runs efficiently without any dependencies whatsoever on clean systems. 

One of its essential components is server-based log decryption. About 70 browser-based cryptocurrencies and 2FA addons are included in LummaC2’s expertise in data theft from Chromium and Mozilla-derived browsers. 

In 2018, the malware family known as “Amadey Bot” was discovered. It can do actions including investigating infected systems, acquiring information, and loading more malicious payloads. 

It was used by TAs to introduce several malware strains, such as the Flawed Ammyy Remote Access Trojan (RAT) and the GrandCrab ransomware.

SectopRAT Stealing Browser Passwords, 2FA Codes

The Remote Access Trojan (RAT) SectopRAT, also known as Arechclient, was created using the .NET compiler. It offers a broad range of functionalities, such as stealing browser information and Bitcoin wallet information. 

It may create a concealed secondary desktop that it utilizes to manage and keep an eye on browser sessions. 

Notably, SectopRAT has Anti-VM and Anti-Emulator techniques that are designed to make malware analysis more difficult.

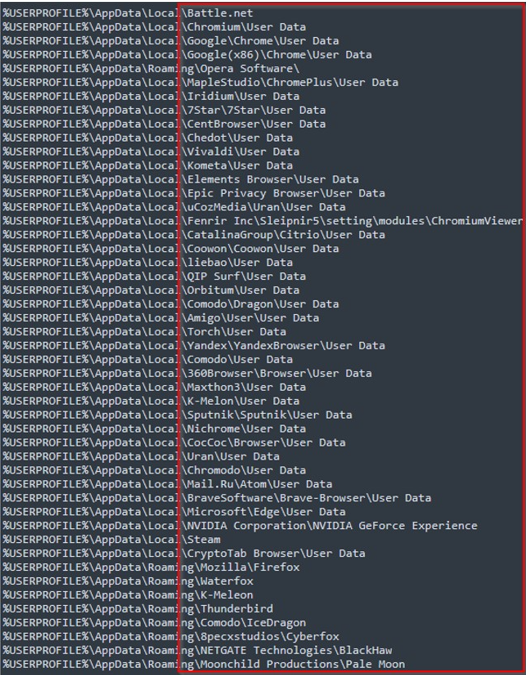
“The malware begins scanning through the target system’s directories. It aims to retrieve sensitive data from files such as “Cookies,” “Local State,” “Login Data,” and “Web Data”, researchers explain.

“These files are sourced from a diverse array of over 35 web browsers, gaming platforms, and other software applications that have been installed on the compromised system”.

SectopRAT target application list to steal sensitive information

The malware can extract information from cryptocurrency wallet browser extensions in addition to particular folders through which it may access cryptocurrency wallets.

Hence, a new level of cyber threat complexity has been revealed by the identification of the LummaC-Amadey-SectopRAT alliance. This planned attack chain demonstrates how hackers have evolved their strategies, from data collection to payload dissemination.

Keep informed about the latest Cyber Security News by following us on GoogleNews, Linkedin, Twitter, and Facebook.


[ad_2]
Source link

Setapp is ready for Alternative App Stores on iPhone

0
[ad_1]

The EU is forcing Apple to allow alternative App Stores on the iPhone in the next couple of years, thanks to the Digital Markets Act or DMA, legislation. And popular app store, Setapp is ready to compete.

You might know Setapp for it’s popular bundle of paid apps that are included for a low monthly subscription. It includes apps for iOS and Mac, for as low as $9.99 per month, and includes plenty of paid apps for that price. Making it a lot more affordable to get an email app like Newton.

Setapp is already claiming that they have over 30 developers ready to offer their apps on its own app store. This would include popular tools like Ulysses, Taskheat, NotePlan, PDFSearch and Soulver.

Setapp is promoting a 90/10 split for this app store

One big way that Setapp could lure developers away from Apple’s App Store is with a more generous revenue split. Which is what they have already announced. Setapp is currently planning a 70/30 split currently on its app store, but developers can earn as much as 90%. This is because it will share 20% of its fees with whoever brings in new customers. That’s going to be a big way to get developers on-board, for Setapp. Many have already voiced complaints with Apple’s “greedy” 70/30 split for literally everything you buy on your iPhone.

The DMA has set a deadline of March 2024 for Apple and other companies to comply. But you can expect that Apple will further contest this law around the app stores. So it will likely take a bit longer. Of course, Apple hasn’t been as quick to adopt this as they were to adopt USB-C, when the EU forced them to do so. However, every other product in their lineup does have USB-C except for the iPhone. Whereas, allowing other app stores on its platform would greatly eat into their revenues.


[ad_2]
Source link

Samsung sold ASML shares worth over $2.2 billion

0
[ad_1]

Samsung has reportedly sold more than half of its stake in Dutch chip equipment supplier ASML. The Korean firm sold over 3.5 million shares of the Dutch company for roughly KRW 3 trillion (approx. $2.24 billion). The transaction happened in the second quarter of the year.

Samsung sold ASML shares to secure funds for semiconductor investment

Samsung acquired a three% stake in ASML in September 2012. It sold almost half of its stake (1.4%) in the company in September 2016, keeping the remaining 1.6% stake. The Korean media is now reporting that the firm has further sold a 0.9% stake sometime between April and June this year, bringing its stake in ASML down to just 0.7%.

According to a hankyung.com report, Samsung disclosed this transaction in a half-year report earlier today. The company held 6,297,787 shares of ASML at the end of March, but that dropped to 2,750,072 shares at the end of the second quarter. So it sold 3,547,715 shares or 0.9% stake in ASML. Considering ASML’s stock price trend during this period, Samsung may have made about $2.24 billion from this sale.

“We sold some of our ASML shares in the second quarter of this year,” a Samsung official confirmed to the publication. While they didn’t share further details, industry experts believe the company is security funds for semiconductor investment. Despite an economic slowdown and declining profits, the Korean firm has no intention to scale back investments in the semiconductor business. It sees sustained investment as the right way to avoid similar downturns in the future.

ASML returned a handsome profit to its investors

Samsung wasn’t the only company to buy a stake in ASML (originally standing for Advanced Semiconductor Materials Lithography) in 2012. The Dutch firm, which is the world’s only supplier of extreme ultraviolet lithography (EUV) machines used to manufacture advanced semiconductor chips, also invited investments from Intel (15% stake) and TSMC (five% stake) to secure funds to keep its operations running back then.

TSMC sold all of its ASML shares in January 2015, while Intel cut its stake to 4.9% in late 2017. Intel further reduced its stake in ASML to under three% in 2018. The investment eventually paid off big time. Both Samsung and Intel reportedly earned a 17X return on their investments in ASML in recent years. It has helped Samsung secure funds during a challenging economic environment. The Korean firm’s operating profit dropped a staggering 95% in Q2 2023, hitting a 14-year low.


[ad_2]
Source link

Netflix starts testing games on TV following its new game controller mobile app

0
[ad_1]
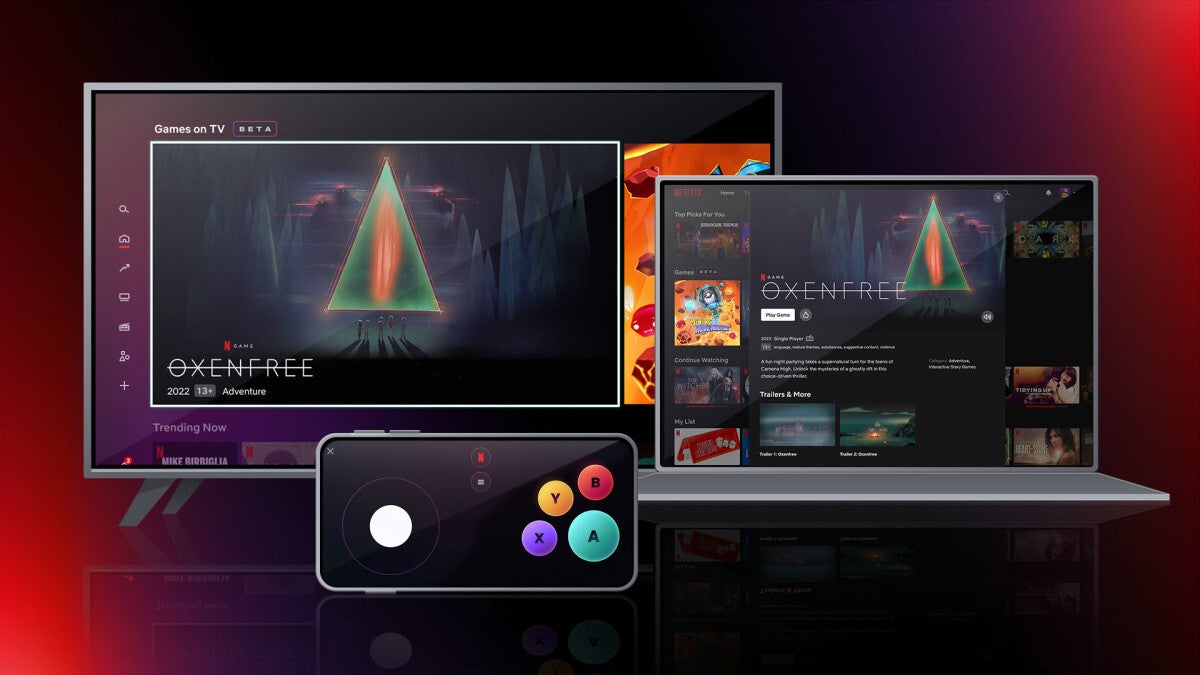
Back in 2021, Netflix jumped into the gaming scene for mobile devices. Just recently, it sprang a surprise with a new app that transforms your iPhone into a game controller. The problem with using your smartphone as a controller was that the company’s games library was only available on IOS and Android, but this will change soon.Netflix is rolling out a limited beta test to a small number of users in Canada and the UK. The company’s goal is to make games playable on every device where users can use Netflix, including TVs, computers, and mobile. In the following few weeks, games on Netflix will also be available for beta test on supported browsers on PCs and Macs through netflix.com.

So, what’s on the testing menu? Right now, a pair of games: Oxenfree from Night School Studio and Molehew’s Mining Adventure, a game that’s all about snagging gems in an arcade setting. If you’re one of the lucky ones with beta access, you can grab the Netflix game controller app from the App Store and use your iPhone as the controller. The app isn’t out for Android users yet, but there’s a chance it could be coming soon.

According to Netflix, this trial run is all about putting its game streaming technology and controller to the test, so the company can fine-tune the user experience as time goes on. When it comes to gaming on your TV, Netflix is gearing up. Games will be available on various devices from Netflix’s partners like Amazon Fire TV Streaming Media Players, Chromecast with Google TV, LG TVs, Nvidia Shield TV, Roku devices and TVs, Samsung Smart TVs, and Walmart ONN.

More devices will be added gradually, and Netflix is determined to bring gaming on its platform to users all around the world. Right now, you can already dive into a bunch of games on the Netflix mobile app. This year, the streaming platform is adding 40 new mobile games to the mix. And that’s not all – it also says that it is cooking up 70 more titles in collaboration with its partners.


[ad_2]
Source link

Intel Patched Newly Reported Downfall Attack Affecting Its CPUs

0
[ad_1]

Google researchers recently reported a vulnerability in Intel CPUs leading to a new “Downfall” side-channel attack. The attack seems a predecessor for the previously discovered Meltdown and Fallout flaws, leaking data. Following the report, Intel released a microcode firmware update to fix the vulnerability.

Downfall Attack Threatens Intel CPUs

Security researcher Daniel Moghimi shared insights about a severe vulnerability affecting Intel CPUs. Exploiting this vulnerability enabled Moghimi to devise a new side-channel attack “Downfall” that triggers data leak.

The vulnerability, CVE-2022-40982, affects the Intel CPUs’ microarchitecture, causing information disclosure to an authenticated adversary. The flaw exists in the memory optimization features exposing internal vector register files during speculative execution.

Executing this attack requires using the Gather instruction; hence the researcher devised two techniques, Gather Data Sampling (GDS) and Gather Value Injection (GVI), to demonstrate the exploit.

Although, detecting the Downfall attack is theoretically possible if a detection system scans hardware performance counters for anomalies like cache misses. However, most existing antivirus software cannot detect Downfall attacks.

On the other hand, executing this attack is “highly practical” for an adversary with a shared physical processor core can execute the attack. The attacker may deploy malware to execute this attack and steal sensitive data, such as passwords and encryption keys.

The researcher has shared a detailed technical analysis of the vulnerability and the Downfall attack in a separate research paper. Whereas users may also visit the specific web page created for this attack to learn more about Downfall, and find the PoC on GitHub.

Intel Released A Fix

The Downfall attack affects a large number of Intel processors, making various computers and laptops vulnerable globally. Moghimi explained that the vulnerability existed since 2014, but remained under the radar. Specifically, the vulnerability impacts Intel Core processors from the 6th Skylake through the 11th Tiger Lake generation.

Following the researcher’s report in August 2022, Intel worked on developing a fix for the flaw. Consequently, a year after the initial disclosure, the tech giant released a patch with the latest firmware updates for all devices, alongside sharing a detailed list of vulnerable CPUs, urging users to update their systems. Besides, Intel has also published a detailed security guide in this regard.

Let us know your thoughts in the comments.


[ad_2]
Source link

New Gigabud Android RAT Bypasses 2FA, Targets Financial Orgs

0
[ad_1]
  • New Malware Variant: Gigabud introduces a fresh wave of sophisticated cyber danger.
  • Global Operation: Gigabud has targeted at least 25 companies, financial institutions, and government departments across several countries.
  • Bypasses 2FA: Gigabud malware can adeptly circumvent two-factor authentication (2FA).
  • Targets Financial Giants: Financial institutions face a growing threat from Gigabud’s focused attacks.
  • Gigabud family: Gigabud.Loan variant presents itself as a fake loan application, luring victims with promises of low-interest loans.
  • Emerging Cyber Risk: The rise of Gigabud underscores the evolving landscape of financial cyber threats.

A new banking trojan named Gigabud has emerged as a formidable adversary, posing a persistent danger to financial institutions worldwide. Originating as an Android Remote Access Trojan (RAT), Gigabud first came to the attention of security experts in September 2022 when it targeted a Thailand-based financial organization and its customers across the Asia-Pacific region.

Group-IB’s experts, in response to a customer’s request, undertook a comprehensive analysis of the malware to decode its intricate tactics. The defining feature of Gigabud is its cautious approach to executing malicious actions.

Unlike conventional malware that acts immediately upon infiltration, Gigabud waits for user authorization within the malicious application, a strategy that makes it notably elusive. Instead of relying on HTML overlay attacks, Gigabud employs screen recording to gather sensitive information, further complicating its detection.

One standout feature of Gigabud is its use of accessibility services, which allows it to perform actions on the victim’s device remotely. This capability, known as “TouchAction,” enables the attacker to perform gestures on the user’s device, giving them the power to evade defence mechanisms, including two-factor authentication (2FA).

Gigabud RAT has targeted at least 25 companies, financial institutions, and government departments across several countries, aiming to mimic their identities and deceive users.

Researchers also uncovered a parallel threat within the Gigabud family: Gigabud.Loan. This variant presents itself as a fake loan application, luring victims with promises of low-interest loans. Once users engage with the app, they are coerced into providing sensitive personal information, which can later be exploited by the threat actors.

Gigabud.Loan’s modus operandi involves impersonating fictional financial institutions from various countries, such as Thailand, Indonesia, and Peru.

The distribution strategy for both Gigabud.RAT and Gigabud.Loan centers around phishing websites. These websites are disseminated through tactics like “smishing,” where victims are sent misleading messages via instant messengers, SMS, or social networks, leading them to malicious links. In certain cases, the malware is even delivered directly through messages on platforms like WhatsApp.

Watch as Group-IB’s researchers looks into Gigabud RAT

Over the course of 2022 to 2023, Group-IB’s researchers detected over 400 Gigabud RAT samples and more than 20 Gigabud.Loan samples using advanced hunting techniques. 

To counteract the threat posed by Gigabud, Group-IB suggests a multi-pronged defence strategy. Organizations should prioritize proactive monitoring of user sessions, prioritize client education on safe online practices, and employ digital protection tools.

Users, in turn, are advised to exercise caution when clicking on links, refrain from downloading risky apps, and utilize reliable VPNs on public Wi-Fi networks.

  1. FakeTrade Android Malware Attack Steals Crypto Wallet Data
  2. Android banking malware distributed with fake Google reCAPTCHA
  3. New Android banking malware Xenomorph found in Play Store apps
  4. Experts concerned over emergence of Android banking trojan S.O.V.A.
  5. Iranian Stalkerware ‘Spyhide’ Steals Data from 60,000 Android Devices

[ad_2]
Source link

FBI warns against threat actors using beta apps to steal money

0
[ad_1]

Beta programs are an excellent way for developers to test their applications in real-world scenarios as it helps them identify and resolve bugs before a public release. However, according to a new report from the FBI, threat actors have started taking advantage of the relaxed security policies for beta apps to steal personal information and gain unauthorized access.

Taking advantage of Google’s relaxed security testing, threat actors design counterfeit beta apps that, at first glance, seem authentic. Once the app is up and running, the threat actors then send out phishing emails, luring unsuspecting victims to download the app embedded with malicious software. In some instances, cybercriminals even succeeded in persuading users to jailbreak their devices and permit installations from unofficial sources.

According to the report, the scam primarily focuses on cryptocurrency enthusiasts, luring them with promises of substantial investment returns via counterfeit trading apps. Upon downloading the app, the unsuspecting users are manipulated into sharing their online financial account credentials, under the impression that this information will be employed to oversee their investments. Unfortunately, the threat actors exploit this data to execute fund transfers.

How to spot such malicious apps?

To help people identify such beta apps, the FBI, in its report, has also highlighted the telltale signs of such malware on your device. These include rapid battery depletion, sluggish processing performance, and the abrupt appearance of unauthorized applications. Additionally, users should also be wary of installing apps from unfamiliar developers and always check user reviews, particularly those detailing excessive battery drainage or overheating concerns.

Moreover, in order to protect against cyberattacks, the FBI advocates refraining from clicking on suspicious links within emails, meticulously checking emails that prompt immediate action, and activating two-factor authentication (2FA).

However, should one, unfortunately, fall victim to such a scam, the FBI has established a system where victims can fill out a form, contributing to the broader endeavor of countering these cyber threats.


[ad_2]
Source link

The Zuckerberg and Elon fight experiences delay thanks to X’s CEO

0
[ad_1]

Ever since the news made its way to the internet, the Zuckerberg and Elon fight has gotten tons of attention. However, one party involved in this fight accuses the other party of delaying the showdown. Mark Zuckerberg, founder and CEO of Meta, has taken to his Threads page to point out Elon’s delay.

According to Zuckerberg, his opponent Elon Musk is yet to agree “on an actual date.” The CEO of Meta also says that he is and has always been ready for the fight. Regardless of how ready Meta’s CEO is, he needs to agree with his opponent on a date.

Because this fight is one that the tech world looks forward to, it’s not going to be a small brawl between friends. There are plans that the fight will stream live, although it’d still be friendly. For these reasons, there is a need for both parties to agree on a date when they’d meet in a cage and settle the months-long question of which of them is stronger.

Details on the supposed cage fight between Zuckerberg and Musk

Back in June, Elon Musk, CEO of X had a brilliant idea to challenge Zuckerberg to a fight. Both men have a major of training and experience in various forms of martial art. Elon had the idea that they both bring their various skills into a cage to determine who’s better fit in combat.

Lots of tech enthusiasts labeled this fight X versus Threads as the two platforms competing with one another. For a fight to hold, there must be a set date when contestants will tackle each other in the ring. This area is becoming a problem for the Zuckerberg and Musk fight, as both parties are yet to agree on a date.

Zuckerberg’s initial suggestion was that the fight takes place on August 26th, which is a few days away. This suggestion became public at the beginning of the month, with Musk kicking against it considering his recent minor surgery. According to X’s CEO, he needs to heal first before getting into the cage with Zuckerberg and showing off his strength.

Elon Musk also took to his Twitter account to share details on the fight. These details include how it’d be live-streamed, its overall style, and much more. According to him, the fight will be Roman-styled, which might sound like some gladiator event in a coliseum.

He goes on to tell the public that he has spoken with the PM of Italy and an epic location is ready. But the Cultural Minister of Italy says that the fight won’t take place in Rome, this points out some lack of planning. Regardless of all this, Musk takes to Twitter again to call out Zuckerberg, hence accepting his challenge.

Meta’s CEO, on his part, says he’s ready, as long as Elon is ready. Does Elon’s recent tweet mean that he’s no longer stalling the fight? Will the Zuckerberg and Elon fight take place on August 26th or at a later date? The answers to these questions will be available in the coming days.


[ad_2]
Source link