UK Electoral Commission Admits Major Data Breach Spanning Over a Year

0
[ad_1]
  • UK’s Electoral Commission discloses major cyber attack exposing millions of voters’ data.
  • The data Breach occurred in August 2021, detected in October 2022, compromising internal systems.
  • Hostile actors accessed servers, compromising emails, control systems, and electoral registers.
  • Commission expresses regret and collaborates with cybersecurity experts to investigate.
  • Incident raises global concerns about democratic process security and election interference.

Britain’s Electoral Commission, responsible for overseeing elections and regulating political finance, has revealed details of a major cyber attack that left millions of UK voters exposed to hostile actors for over a year. 

The data breach, characterized as a “complex cyber incident,” first occurred in August 2021 but was only detected in October 2022. Hostile actors gained access to the Commission’s servers, compromising internal emails, control systems, and copies of electoral registers, potentially putting personal data at risk.

The Commission, acknowledging the data breach and its implications, expressed regret over the security lapse. Shaun McNally, the Chief Executive of the Electoral Commission, admitted that while they know which systems were accessed, it’s impossible to definitively determine what files were accessed or manipulated. He reassured, however, that due to the largely paper-based nature of the UK’s elections, it would be challenging for hackers to influence the outcome of a vote directly.

The compromised electoral registers contained information from 2014 to 2022, including the names and addresses of voters, both domestic and overseas. While the Commission acknowledged that much of this data was already publicly available, it emphasized that the potential exposure was a cause for concern and apologized to the affected individuals.

“The registers did not include the details of those registered anonymously. The Commission’s email system was also accessible during the attack,” McNally said in a statement.

Commenting on the issue, Mr. Tom Hamersley, Senior Solutions Architect at HackerOne, told Hackread.com, “A breach on the Electoral Commission sounds critical and important, and the news is getting a lot of attention. However, looking at the incident more closely, the fact it was identified in October 2022 and is only being reported now, suggests the impact wasn’t critical.”

“This is also illustrated by the fact the PII breach was limited, with most of the information already being in the public domain, and the breach has not affected the rights or access to the democratic process or affected electoral registration status.”

Mr. Hamersley showed his concern for future cyber attacks aimed at the UK Electoral Commission and other critical infrastructure in the country. “I’m more concerned that the measures they’ve stated as having taken to prevent future attacks look reactive and basic,” he added.

“While they are increasing their overall alerting to suspicious login activity, it doesn’t suggest an improvement in the overall security maturity of their electoral assets and whether or not they will undergo sufficient automated and human testing.”

“Many other government agencies, including the NCSC, already take an advanced approach to security testing and engage with the ethical hacking community to report any potential vulnerabilities,” Mr. Hamersley said.

The incident has raised broader concerns about the security of democratic processes globally. Electoral security has become a key issue following instances of interference in elections, such as Russia’s alleged involvement in the 2016 U.S. presidential election.

In response to the attack, the Electoral Commission has collaborated with the UK’s National Cyber Security Centre (NCSC) and external experts to investigate the data breach. The Commission has also taken steps to improve the security, resilience, and reliability of its IT systems, aiming to prevent future cyber incidents that could potentially compromise the democratic process.

  1. The 10 Best Cybersecurity Companies in the UK
  2. UK Police mistakenly deleted 150,000 arrest records in software glitch
  3. British Airways, BBC and Boots Hit by Suspected Russian Cyber Attack
  4. Mastermind Behind iSpoof Fraud Website Sentenced to 13 Years in the UK

[ad_2]
Source link

Galaxy Note 20 grabs Samsung’s August 2023 update

0
[ad_1]

Samsung has released the August 2023 security update for a couple more Galaxy devices. The Galaxy S20 FE 5G and Galaxy Note 20 series are the latest to get the new security patch. The company has already pushed the update to the Galaxy S23 series, Galaxy Z Fold 4, Galaxy Z Flip 4, and a few other models in some regions. The August SMR (Security Maintenance Release) contains fixes for more than 80 vulnerabilities.

The Galaxy S20 FE was the first Samsung device to pick up this month’s security update. The company began the rollout last week but only covered the 4G/LTE model initially. But now, it has expanded the rollout to the 5G model as well. As of this writing, the Galaxy S20 FE 5G is receiving the August SMR in Latin America, the same market where its 4G sibling got the update. A global release should follow in the coming days.

The updated firmware build number for the 5G version of this Fan Edition (FE) phone is G781BXXS7HWG9. First reported by SamMobile, the update is already live in Brazil, Colombia, Ecuador, Guatemala, Mexico, Panama, Paraguay, Trinidad and Tobago, and Uruguay. Samsung’s official changelog confirms that the device isn’t receiving anything more than the latest security fixes, which we will discuss in more detail shortly.

Meanwhile, Samsung is pushing those fixes to the Galaxy Note 20 and Galaxy Note 20 Ultra as well. The same publication reports that the update is available in Southeast European countries with the build number N98*FXXS8HWH3 and in China with N98*0ZSS6HWG8. It seems we are talking about 4G models in the former region and 5G models in the latter. A wider rollout should be just around the corner.

Samsung’s August 2023 update patches over 80 security issues in Galaxy devices

Samsung began rolling out the August SMR to Galaxy devices last week, but it hadn’t published the content of the patch back then. We now have the details, and it’s a pretty big one. The latest security release fixes more than 80 vulnerabilities in Galaxy devices. 86, to be precise. 51 of those are Android flaws coming from Google and partners (including two critical issues), while the remaining 35 are Galaxy-specific patches coming directly from Samsung.

As usual, Samsung has fixed issues across various system apps, services, and components in Galaxy devices with the August SMR. These include at least one critical flaw that allowed remote code execution on affected units. If you’re using a Galaxy smartphone, watch out for the latest security update in the coming days. You can manually check for new updates from the Settings app on your phone.


[ad_2]
Source link

TikTok Gimme The Mic competition brings the platform to show off your voice

0
[ad_1]

If you want to show off your vocal talent on a global platform, the TikTok Gimme The Mic competition is perfect for you. TikTok took to its official blog to announce the arrival of this competition to its global audience. The video-sharing platform is inviting users to audition for this competition and stand a chance to win big.

This will sound exciting for a lot of emerging talents in the music industry just waiting to emerge from their shells. Considering that TikTok has a large user base worldwide, this competition will give these talents a chance to go global. Daily, musicians around the world turn to TikTok as a platform to promote their new songs to a wide audience of users.

These promotions give birth to various music trends that are quite popular on the platform. Now, TikTok is turning its attention to upcoming talents, giving them the platform to show off their vocal talent to the world. If you have interest in joining this music competition, there are a few things you need to take in mind.

An opportunity to get your vocal talent out there with the TikTok Gimme The Mic competition

Just like every other music singing competition, there are a few steps to take to join the TikTok Gimme The Mic competition. A very basic requirement to meet before applying for this competition is to have a TikTok account. Additionally, all applicants must be 18 years or older before they can audition for this competition.

Having met the requirements above, you can now move on to audition to join and show off your vocal talent. The audition process is already open for applicants and will close on August 16. To audition, TikTokers need to register on the dedicated app page for this competition.

After the registration is complete, applicants will need to upload a 30-sec video showing off their vocal talent. This video should use the hashtag #GIMMETHEMIC applicants have until August 16 to upload this video. TikTok will then move to select 30 applicants that have the most liked videos from the audition.

These 30 applicants will move on to compete among themselves for a place in the semi-finals. This competition will be live-streamed on TikTok for the world to view and engage with their favorite contestants. Those contestants will compete from September 1 to September 3 for a place in the grand finale.

A total of 10 contestants will make it to the grand finale, which will take place on September 10. The winner of the TikTok Gimme The Mic competition will go home with 50,000 diamond rewards. This 50,000 diamond reward can only be used on TikTok to purchase virtual gifts and not exchanged for cash.

The winner of this competition will also progress to the global finale, where they stand a chance to win 500,000 diamond rewards. So, therefore, it’s clear that this competition will take place globally in various regions. Winners from all regions will compete among themselves for the global crown on September 22. This competition proves that TikTok is ready to give you the mic or the platform to let the world hear your voice, but the question is if you are willing to take it.


[ad_2]
Source link

Apple Music’s New Feature Helps You Discover New Songs Based on Your Music Taste

0
[ad_1]

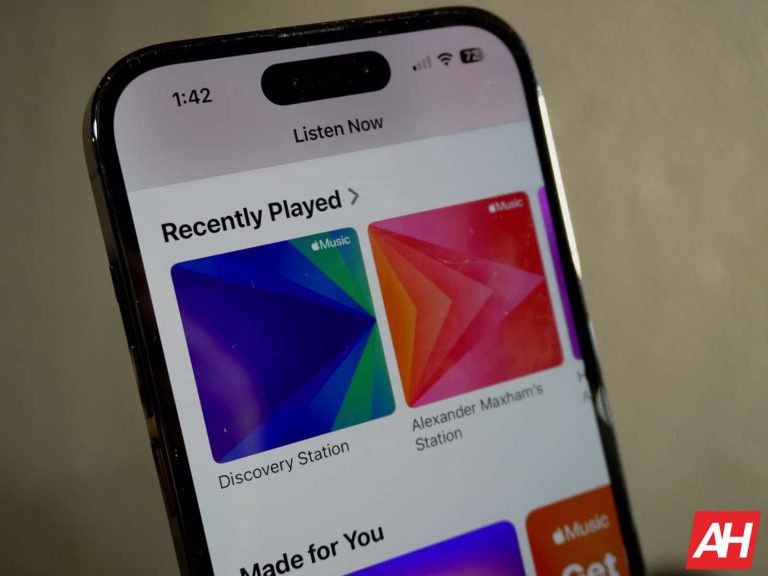
Apple Music has rolled out a couple of new stations to help you discover new songs to add to your playlists. It’s aptly named “Discovery Station” and will play a curated list of music based on what you’ve been listening to lately. These will mostly be songs that you have not added to your library yet. So it’ll be helpful to find new music.

Apple Music has also changed the album art for your own station. It’s now in red, pink and orange, and has a similar look to the album art on the Discovery Station which is in green, blue and a sort of purple color.

The Discovery Station has rolled out, and it appears to be a server-side change, as there has not been an update to iOS to bring this feature, nor an update in the Play Store for the Android version. So everyone should have it on Apple Music now.

It does a decent job with Discovery

For a long time now, a big issue with Apple Music had been that it pretty much sucked with discovery. It would surface different radio stations and playlists. But trying to discover individual songs based on what you are already listening to, it didn’t do that well at all. However, this new Discovery Station does a pretty decent job, so far.

Will this help Apple Music catch up to Spotify? Probably not. But it is a step in the right direction. Spotify has two main features that makes it better than Apple Music – that’s Discovery and Spotify Connect. Discovery is something Apple can work on, and is working on. Though Spotify Connect, that might take longer to do. Spotify Connect basically allows you to play music on literally anything, from any other platform. And control it all from the Spotify app. Including Sonos and PlayStation 5.

The new Discovery Station should be available in your Apple Music app now.


[ad_2]
Source link

Meta is ignoring reports from its Trusted Partner program

0
[ad_1]

Meta, formerly known as Facebook, has always had a troubled history of regulating harmful content on its platforms. However, a new report from Internews has highlighted the company’s operational failures within its Trusted Partner program, which is responsible for helping organisations report dangerous and harmful content on Meta.

As per the report, the Trusted Partner program, which includes over 456 global civil society and human rights groups, has been facing significant obstacles, including prolonged delays of several months in receiving responses from Meta. Additionally, to make matters worse, this sluggishness also extends to severe cases of harmful content, such as death threats, incitements to violence, and other time-critical matters.

“Two months plus. And in our emails, we tell them that the situation is urgent and people are dying. The political situation is very sensitive, and it needs to be dealt with very urgently. And then it is months without an answer,” reads the report.

Disparities between responses based on the region

In addition to the widespread delay in responses, the report also highlights the regional discrepancies in Meta’s efforts to combat harmful content. For example, when compared to the Ukrainian partners who reported receiving responses within 72 hours, the Ethiopian partners, on the other hand, had to wait for several months just to hear the response related to the Tigray War. This delay also sadly contributed to the tragic passing of Tigrayan professor Meareg Amare, who suffered a racist assault on Facebook, where the platform allegedly failed to act promptly.

Moreover, this report echoes the disclosures from former Facebook employee Frances Haugen, whose internal documents uncovered a marked disregard for countries in South Asia and Africa, including Ethiopia.

“Trusted flagger programs are vital to user safety, but Meta’s partners are deeply frustrated with how the program has been run,” reads the report.


[ad_2]
Source link

Snapchat facing a possible $184 million fine, if found guilty over underage users

0
[ad_1]

Social media platforms don’t have it too easy these days, and Snapchat is no exception to that. Snapchat owner Snap Inc could face a formal investigation and, if found guilty, be fined some $184 million. All of this – over mismanaging and not enforcing strict enough policies to remove underage users from its platform (via Reuters).Ofcom is the UK’s communications regulator – last year it found out that in the UK, the most popular app for underage social media users was none other than Snapchat. According to their data, more than half (approximately 60%) of kids that are aged between 8 and 11 had “at least one social media account, often created by supplying a false date of birth”. UK’s data protection law states that social media companies need consent from the parents, if in need to process data of kids under 13.So far Snapchat has not issued an official statement on the matter of reducing the number of underage users. A Snap person says the company does strive towards ensuring that “digital platforms are age appropriate and support the duties set out in the Children’s Code”. Before starting an official investigation, ICO (Information Commissioner’s Office) has to gather information and may ask the company to aid the investigation.

A report from Reuters in March claimed that Snapchat had only removed “a few dozen” under-13 accounts from its platform in Britain last year. Ofcom estimates Snapchat has “thousands of underage users”. If an investigation launches and if found guilty, Snap Inc could be fined an equivalent to up to 4% of its annual global turnover, which Reuters estimates at $184 million (based on recent Snap Inc financial results).

On a side note, the NSPCC (National Society for the Prevention of Cruelty to Young Children), said that figures it had obtained showed that Snapchat accounted for 43% of cases in which social media was used to distribute indecent images of children.


[ad_2]
Source link

Bug Bounty Program: Microsoft Rewarded $13.8M

0
[ad_1]

Microsoft Bug Bounty Program awarded $13.8M for their collaboration with over 345 security researchers from +45 countries around the world between July 01, 2023, to June 30, 2023.

Bug Bounty Programs authorize independent security experts to report bugs to a company in exchange for rewards or compensation. 

These bugs can include security exploits, vulnerabilities, process issues, hardware flaws, etc. It is also known as a vulnerability rewards program (VRP).

Bug bounty programs allow companies to leverage the hacker community to improve their systems’ security posture over time.

Larger companies, including Apple, use bug bounty programs as a part of their security program.

These programs have access to a larger number of hackers or testers, thereby increasing the chances of finding bugs before malicious hackers attempt to exploit them.

The bounty programs are spread across cloud, platform, and Defense & Grant programs such as Microsoft Azure, Xbox, Microsoft Dynamics 365 and Power Platform, M65, and more.

Each program has its own scope, eligibility criteria, award range, and submission guidelines.

Bug Bounty Program in the Past 12 Months

  • Intune Bug Bounty research invitation challenge July 2022
  • New high-impact research scenarios added to the Microsoft 365 Insider Builds on Windows Bounty Program January 2023
  • Microsoft Teams Preview Bug Bounty research invitation challenge January 2023
  • New Bing Bug Bounty research invitation challenge March 2023
  • New severity classification for Online Services added to the Microsoft 365 Bounty Program April 2023
  • New scope added to the Identity Bounty Program June 2023
  • Secure boot research scenarios added to Windows Insider Preview Bounty Program July 2023

“In the coming year, we will continue to improve our programs based on your feedback. We appreciate our global security research community for their ongoing partnership and for sharing their expertise to help secure millions of Microsoft customers.

We look forward to strengthening our existing relationships and building new ones”, said the Microsoft Bug Bounty Team.

Keep informed about the latest Cyber Security News by following us on GoogleNews, Linkedin, Twitter, and Facebook.


[ad_2]
Source link

Galaxy Tab S9 FE & S9 FE+ seen in live photos ahead of launch

0
[ad_1]

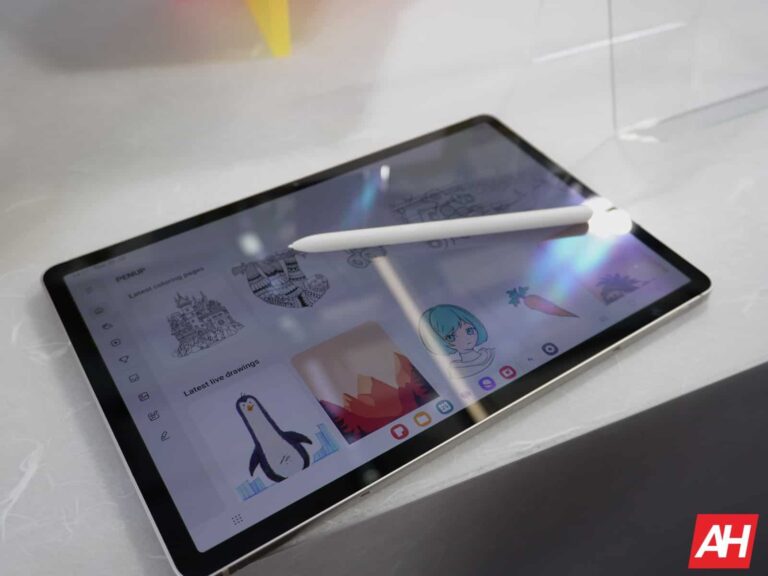
Samsung‘s Galaxy Tab S9 FE and Galaxy Tab S9 FE+ mid-range tablets might go official soon. The new Fan Edition (FE) tablets have already picked up several regulatory approvals, while leaks have revealed their key specs. We now also have our first live look at the duo thanks to photos shared by the South Korean certification agency Safety Korea.

The agency recently certified the Galaxy Tab S9 FE and Galaxy Tab S9 FE+ for launch in Samsung’s homeland. As part of the process, it published live photos of both devices on its official website. First spotted by TabletMonkeys, the photos show us the front of the duo, both of which are locked. We can still see relatively big bezels and one front-facing camera each, though.

The Safety Korea listings for the Galaxy Tab S9 FE and Galaxy Tab S9 FE+ don’t reveal anything else that we don’t already know. As expected, both devices will be available in Wi-Fi and cellular (5G) versions. The vanilla model has the model numbers SM-X510 (Wi-Fi) and SM-X516N (5G), while the Plus model has model numbers SM-X610 (Wi-Fi) and SM-X616N (5G).

Note that these are the 5G versions of the two tablets have different model numbers in other markets. The US models are identified as SM-X516U and SM-X616U, while the international models have the model numbers SM-X516B and SM-X616B. Regardless of these identifiers, the specs of the Galaxy Tab S9 FE and Galaxy Tab S9 FE+ will remain the same globally.

The Galaxy Tab S9 FE and Galaxy Tab S9 FE+ will pack modest specs

As you might expect, the vanilla Galaxy Tab S9 FE will be smaller, featuring a 10.9-inch display. The Plus model, on the other hand, sports a 12.4-inch display. Both tablets are rumored to be powered by Samsung’s in-house Exynos 1380 processor. Additionally, we are expecting a single rear-facing camera, S Pen support, a side-mounted fingerprint scanner, a smart connector, and a dual stereo speaker setup.

Rumors are that the Galaxy Tab S9 FE series tablets will run Android 13 out of the box. That suggests the duo could debut within the next couple of months or so, as Samsung’s Android 14/One UI 6.0 update will arrive in October. Unfortunately, we don’t yet have an official word on their launch. The company did name the devices on its website recently, but the launch date is still missing. The wait may not be much longer now, so stay tuned.


[ad_2]
Source link

Apple’s upcoming M3 Max chip is set to be a monster

0
[ad_1]

Apple is apparently testing its new M3 Max chipset that we expect to see in some new Macs next year. And according to Bloomberg, it’s a pretty monster chip from Apple. It’s set to offer a 16-core CPU and a 40-core GPU. The M3 Max will likely be available in the MacBook Pro, Mac Studio and possibly the Mac Pro next year.

However, the first M3 Macs are set to come out as early as this October. Which we would expect to see the M3 coming in the MacBook Air, iMac and Mac Mini.

The M3 Max is looking to be a slight upgrade over the M2 Max, at least in terms of the cores. The M3 Max is going to have 12 high performance cores and four efficiency cores. And with a 16-core CPU and 40-core GPU, that’s two more GPU cores than the M2 Max currently has. But don’t forget, the M3 series is set to be a 3nm chipset, which is going to provide more performance, while also being more efficient. So we could see some pretty big changes to battery life here.

M3 could be the next big leap for Apple, in terms of performance and efficiency

M1 was a big leap for Apple. Jumping from Intel over to it’s own silicon, which brought about some incredible performance, and efficiency. Giving us laptops that offer up to 18 hours of battery life. Which did seem pretty incredible back in 2020. Now it’s expected from Apple.

Now the next step is going to be M3, since it’ll be a 3nm process. At least that is what the rumors are pointing towards. The M1 and M2 were both 5nm, though M2 used a slightly improved 5nm process, which made it a small step, but still bigger than first expected. At 3nm, we should see some pretty big gains in both performance and efficiency. After M3, it’s unclear when we might see the next big leap. But M3 could bring 24 hour battery life to MacBooks. We’ll have to wait until October to see.


[ad_2]
Source link

Netflix is making rating shows and movies on mobile much easier

0
[ad_1]

Many of us, including myself, often forget to rate a show or movie after watching it. While not necessary, it can help improve your suggestion list. Now, Netflix is simplifying the process for users to rate movies and shows on mobile devices.

According to TechCrunch, Netflix has updated the rating feature on its mobile app, enabling you to rate a show while still watching it. Instead of returning to a show or movie page to give a thumbs-up or thumbs-down, you can now simply tap the screen while watching, whether it’s in the middle or at the end. You can just click the thumbs buttons at the top and keep watching.

The new update will probably encourage more users to use the feature, which will help Netflix suggest more personalized recommendations based on users’ watch history and what they have liked or disliked. Or, to put it in a few words, by rating what you are watching, you are helping Netflix’s algorithm understand you better.

The system that suggests new movies and shows on Netflix uses two different data sets to make personalized recommendations for what you might want to watch. The first data comes from what you’ve watched before and the kinds of genres you prefer, while the second is based on your ratings.

On the mobile app, you can rate using three reaction buttons: a thumbs up, a thumbs down, and a double thumbs up button. The latter was introduced last year in an attempt to teach Netflix’s algorithm not only which movies or shows you like or don’t like but also which you love.

Based on which movies and shows received your double thumbs-up reaction, Netflix’s algorithms will better recommend similar ones. With the improved rating feature, now more user-friendly on mobile devices, starting to use it could lead to receiving more accurate and tailored suggestions.


[ad_2]
Source link