Russian Hackers were behind the Microsoft teams phishing attacks

0
[ad_1]

It’s no secret over the past few months, Microsoft has had a tough time with security breaches. Now, in another concerning development, the company has recently discovered a series of highly sophisticated phishing attacks orchestrated by a Russian government-linked hacking group named Midnight Blizzard, which targeted organizations and governments by posing as technical support staff on Microsoft Teams.

How did the hack work?

Instead of using regular hacking attempts, the hackers utilized clever social engineering techniques and leveraged already-compromised Microsoft 365 accounts owned by small businesses to create deceptive domains that appeared to be legitimate technical support entities. Once these fake accounts were up and running, the hackers then sent Teams messages containing phishing lures, aiming to steal credentials from targeted organizations and ultimately trick them into approving multifactor authentication (MFA) prompts. The MFA authentication allowed the hackers to perform an account takeover.

Additionally, in an effort to bypass conditional access policies, the hackers occasionally tried to add a device to the organization as a managed device through Microsoft Entra ID (formerly known as Azure Active Directory).

Furthermore, Microsoft says that they have been monitoring these attacks since late May 2023, and they have affected around 40 organizations globally, spanning various sectors, including government, non-government organizations (NGOs), IT services, technology, discrete manufacturing, and media.

Microsoft’s response

In response to the phishing attacks, Microsoft has taken immediate steps and blocked the use of malicious domains in Teams. Additionally, the company is also actively investigating the matter and working towards securing affected organizations. However, until then the investigation is complete, the company has advised users and organizations to exercise caution when engaging with unfamiliar support accounts.

“As with any social engineering lures, we encourage organizations to reinforce security best practices to all users and reinforce that any authentication requests not initiated by the user should be treated as malicious,” reads Microsoft’s blog post.


[ad_2]
Source link

Global ransomware attacks at an all-time high, shows latest 2023 State of Ransomware report

0
[ad_1]

Ransomware gangs are also starting to focus on exploiting zero-days for initial access.

Ransomware attacks have shown no signs of slowing down in 2023.

A new report from the Malwarebytes Threat Intelligence team shows 1,900 total ransomware attacks within just four countries—the US, Germany, France, and the UK—in one year.

The findings, compiled together in the 2023 State of Ransomware Report, show alarming trends in the global ransomware surge from July 2022 to June 2023. For example, the report shows that the US shouldered a hefty 43 percent of all global attacks and that ransomware attacks in France nearly doubled in the last five months.

To say ransomware gangs have been unkind to the US in the past year is an understatement.

Malwarebytes found that a total of 48 separate ransomware groups attacked the US in the observed period. To boot, there was a 75 percent increase in the average number of monthly attacks in the US between the first and second half of the last 12 months.

The UK, on the other hand, emerged as the second-largest ransomware target, enduring close to 200 ransomware attacks.

Malwarebytes tracked 32 separate ransomware groups attacking the UK, seven of which recorded more than ten known attacks. In addition, more ransomware gangs are attacking targets multiple times a month: the number of groups carrying out more than one known attack per month in the UK has climbed steadily for a year, from just one in July 2022 to eight in June 2023.

Neither France or Germany have been spared by the growing menace of ransomware, either.

Germany retained its place as the fourth most attacked country in the world, and the most attacked country outside of the anglosphere. France meanwhile experienced a disproportionately high rate of attacks on its government sector (9 percent of attacks).

Perhaps the biggest takeaway from the report, however, is that the ascension of the CL0P group—which has effectively harnessed zero-day vulnerabilities to amplify its attacks—could signal a change in the game.

A New Threat on the Horizon: CL0P

For a year and a half, LockBit, which claims to have 100 affiliates, has been the most dominant form of “Ransomware-as-a-Service” (RaaS) in the US, averaging about 24 attacks per month.

However, twice this year, in March and June, LockBit’s considerable rate of attacks was vastly exceeded by CL0P, which was otherwise dormant.

The drive behind the sudden change? CL0P used separate zero-days in GoAnywhere MFT and MOVEit Transfer to gain an edge. This gave them the ability to launch an unprecedented number of attacks within a short time frame and across a massive scale.

The use of zero-day vulnerabilities by ransomware groups like CL0P may trigger a significant shift in ransomware strategies, mirroring the adoption of the “double extortion” tactic in 2019.

If more groups start adopting CL0P’s zero-day exploitation techniques, the ransomware landscape could tilt from service-oriented attacks to a more aggressive, vulnerability-focused model—a move that could skyrocket the number of victims.

Want to learn more?

Read our 2023 State of Ransomware Report


[ad_2]
Source link

Smartphone shipments decline, as Omdia reveals top 10 smartphone OEMs

0
[ad_1]

A new report from Omdia, a research group, has surfaced. The report says that smartphone shipments have declined again, year-on-year, and they’ve been declining for eight consecutive quarters. This report has also revealed a list of the top 10 smartphone OEMs.

Previous reports that we’ve seen have focused on the top 5 smartphone OEMs, so this will be interesting to check out. Before we get to it, however, do note that this report is for Q2 2023, of course.

Omdia has revealed top 10 smartphone OEMs, as shipments declined yet again

Omdia reports that smartphone shipments totaled 265.9 million units in Q2 this year. That’s a 9.5% decrease compared to the same period last year, and a 1.2% decline compared to Q1 this year.

Samsung is first-placed, as expected. The company managed to ship 53.3 million smartphones, and faced a 14.3% decline YoY. Apple is second with 43.2 million units shipped, and is facing a decline of 11.7%.

Xiaomi managed to claim third place with 33.2 million shipped units, as the company’s sales declined 15.7% YoY: OPPO Group (includes OnePlus too) managed to squeeze itself to fourth place with 25 million sold smartphones, which is 10.5% less than a year before.

Transsion managed to claim fifth place

The fifth place is reserved for… Transsion. We’ve talked about that company recently, when Canalys’ report surfaced. That Chinese OEM includes Tecno, Infinix, and iTel brands. Transsion shipped out 24.5 million smartphones, and is actually one of two smartphone manufacturers who has seen YoY growth. It grew by 38.4%.

Vivo claimed sixth place with 22.3 million sold units, and has declined 10.1% YoY. HONOR is seventh with 14.1 million sold smartphones, and has seen a decline of 6.6%. Motorola is eighth with 10.4 million sold smartphones, and has declined 18.2%.

Realme has seen quite a considerable decline in shipments, as it sold 24.6% fewer smartphones than a year ago. Huawei closes out the top 10 list with 7.4 million smartphone shipments, which is actually 15.6% more than in Q2 2022.

You can check out the entire list in the image below, and that table considers more information, including a comparison with Q1 2023 for every brand.

Omdia top 10 smartphone manufacturers Q2 2023


[ad_2]
Source link

Possible iPhone 15 series launch date has been tipped

0
[ad_1]

Apple is expected to announce its iPhone 15 series in the near future, and a possible launch date has just been tipped. This report comes from 9to5Mac, as multiple sources shared the same info.

The iPhone 15 series launch date tipped for September 13

It seems like carriers have asked their employees not to take days off on September 13 due to a major smartphone announcement. Now, this is not necessarily Apple that we’re talking about, but it almost certainly is.

Apple usually announces its iPhones in September, and despite the fact a recent rumor said it may happen in October this year, this could be it. Also, September 13 is Wednesday, as was last year’s event (September 7). Apple usually does it on Tuesdays, but it chose to do things differently last year.

Now, if the phones do get announced on September 13, pre-orders will kick off on September 15, on a Friday. The phones will then become available on September 22, quite probably.

Having said that, last year, the iPhone 14 Plus sales were late due to supply issues. The same could happen with at least one of the iPhone 15 Pro models this year. Apple is allegedly having problems with displays for Pro models (at least one of them), so… we’ll see.

All models will feature Type-C ports, first iPhones ever to include them

The entire iPhone 15 series will feature Type-C ports this year. These four phones will actually debut Type-C for iPhones, as the EU basically forced Apple’s hand this time around. All devices will also feature a Dynamic Island cutout.

The iPhone 15 Pro models will come with a better camera setup, thinner bezels, and a titanium frame, based on rumors. The iPhone 15 Pro Max model will set itself apart by also having a periscope telephoto camera, unlike the iPhone 15 Pro.

Despite these changes, the demand for the iPhone 15 series is tipped to be lower than for the iPhone 14 series. We’ll see if that’ll pan out.


[ad_2]
Source link

What is BEC Attacks (Business Email Compromise)?

0
[ad_1]
BEC Attacks

BEC, an acronym for Business Email Compromise, is a sophisticated form of cybercrime. Cyber threats have become a pressing concern in a world where almost every aspect of our lives is digitized. One of these threats that have been growing exponentially in recent years is the BEC attacks.

What Are BEC Attacks? 

These attacks are carefully orchestrated scams perpetrated by cybercriminals to trick businesses into transferring money or sensitive information. The attackers usually impersonate a high-ranking official in the company, such as the CEO or CFO, and send an email request for a wire transfer or confidential data to another employee.

They’re not just any random email scams; BEC attacks are highly targeted and involve a great deal of planning and research. The cybercriminals behind them often know a lot about their targets and use this information to make their fraudulent requests seem legitimate. So, it’s no surprise that these attacks pose a significant threat to businesses of all sizes and industries worldwide.

Understanding BEC Attacks 

Process and Mechanics of a BEC Attack

Understanding how BEC attacks work is the first step in preventing them. The process often starts with extensive research. The attackers gather information about the target company and its employees. They look for information such as who is in charge of finances, who they report to, and when these officials will likely be out of the office.

Once they’ve gathered enough information, they craft a convincing email. This email is usually disguised as originating from a high-ranking official and sent to an employee with the authority to transfer funds or access sensitive information. The email will request a wire transfer, often with a sense of urgency to pressure the employee into acting quickly without questioning the request’s legitimacy.

The mechanics of these attacks are what makes them so effective. The attackers exploit the trust and authority of high-ranking officials to bypass traditional security measures. And because the emails are so well-crafted, they can be tough to detect.

Common Forms of BEC Attacks

There are several common forms of BEC attacks. The most common is ‘CEO Fraud,’ where the attacker impersonates the CEO or another top executive. They send an email to an employee in finance, requesting an urgent wire transfer.

Another form is ‘Invoice Scams.’ In these cases, attackers impersonate a vendor or supplier and send a fake invoice to the company. The invoice will typically request payment to a new account controlled by the attacker.

There’s also ‘Account Compromise.’ Here, an attacker hacks into an employee’s email account and sends fraudulent emails to vendors listed in their email contacts. The email will request that future payments are sent to a new account.

The Targets and Motives Behind BEC Attacks

The targets of BEC attacks are typically businesses that work with foreign suppliers or regularly perform wire transfer payments. However, any business can be a target. The motive behind these attacks is simple: money. Cybercriminals are looking for the easiest way to get their hands on your cash.

Prevention of BEC Attacks 

The best way to deal with BEC attacks is to prevent them from happening in the first place. Prevention requires a multi-faceted approach that includes technical, administrative, and human elements.

Email Security Measures

The first line of defense against BEC attacks is implementing robust email security measures. It is essential to use email filtering solutions that can detect and block phishing emails. These solutions can flag emails from outside your organization that are crafted to look like they’re from within.

Furthermore, you should also implement Domain-based Message Authentication, Reporting & Conformance (DMARC), an email authentication protocol. DMARC can prevent attackers from spoofing your organization’s domain in their phishing attempts, significantly reducing the chances of a successful BEC attack.

Multi-Factor Authentication (MFA)

Multi-factor authentication is another crucial element in preventing BEC attacks. MFA requires users to provide two or more forms of identification before they can access their email accounts or other sensitive systems. This could be something they know (like a password), something they have (like a physical token or a smartphone), or something they are (like a fingerprint or other biometric data).

By implementing MFA, even if a criminal manages to steal an employee’s login credentials through a phishing attack, they would still need the additional factor(s) to access the account. This significantly increases the difficulty for attackers, often deterring them from attempting to compromise your business.

Employee Training

The human element is often the weakest link in cybersecurity. Therefore, regular employee training is essential in preventing BEC attacks. Employees should be taught to identify phishing emails and be aware of the tactics used by cybercriminals in these attacks.

Moreover, it should be emphasized that everyone, regardless of their position in the company, could be a target. Regularly updated training programs can help employees stay abreast of the latest threats and the best practices to mitigate them.

Verify Requests

Given the nature of BEC attacks, it is crucial to establish a process to verify requests for funds or sensitive information, especially if they are unexpected or come from high-ranking individuals. This could be as simple as making a phone call to the person making the request.

The more significant the request, the more critical it is to verify it through multiple channels. This practice can significantly reduce the chances of an employee inadvertently complying with a fraudulent request.

Incident Response Plan

Even with the best preventative measures in place, it’s essential to be prepared for the worst-case scenario—a successful BEC attack. This is where an incident response plan comes into play.

An effective incident response plan should outline the steps immediately after detecting a BEC attack. This includes identifying and isolating affected systems, investigating the breach, notifying affected parties, and reporting the incident to the relevant authorities.

Use of Secure Email Gateways

Secure email gateways can be a valuable tool in the fight against BEC attacks. These solutions provide an additional layer of security, filtering incoming and outgoing emails to identify potential threats.

They use techniques such as link protection and attachment sandboxing to protect against malicious content. Moreover, they can also detect and block emails that attempt to spoof your organization’s domain, reducing the risk of BEC attacks.

Regular Monitoring

Last, regular monitoring of your email systems and network activity can help detect unusual behavior that may indicate a BEC attack. This could include abnormal login patterns, unexpected email forwarding rules, or sudden changes in email volume.

Monitoring tools can automate this process, alerting your IT team to potential threats so they can take swift action. Regular auditing of your systems can also help identify any security gaps that must be addressed.

Conclusion

To summarize, understanding and preventing BEC attacks is critical in today’s digital world. It requires a combination of robust technical measures, comprehensive employee training, and vigilant monitoring. Remember, the cost of preventing these attacks is far less than the potential financial and reputational damage they can cause. So, stay informed, stay prepared, and stay safe.
[ad_2]
Source link

Hey, are you REALLY ready to go on vacation? (No, you aren’t)

0
[ad_1]

We’ve made a handy flow chart to help IT and security folk decide if they’re ready to go on vacation.

Are you ready for a challenge? A real challenge? Do you laugh in the face of shark cages, scoff at the Marathon des Sables, and waft a dismissive finger in the direction of the Everest ascent? Are you ready to conquer the impossible?

If so, then you might be ready for the ultimate challenge—taking a vacation while working in IT or computer security. Our handy flow chart will help you decide if you’re ready (TL;DR, you aren’t, but you already knew that).

Click on the image to view it full size.


Malwarebytes EDR and MDR removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

You can play these mini-games on Galaxy Z Flip 5 cover screen

0
[ad_1]

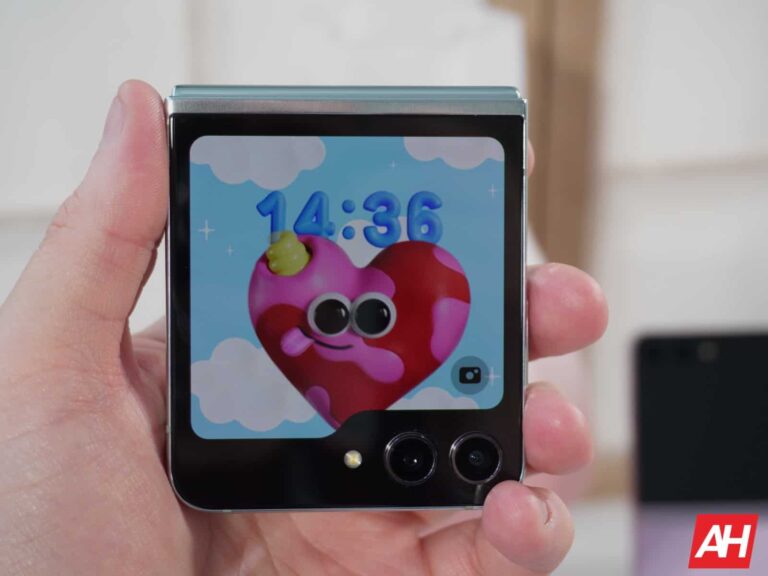
You can play some fun games on the Galaxy Z Flip 5‘s cover screen. The 3.4-inch squarish display supports a bunch of mini-games that can quickly freshen up your mood. The only catch is that you need Good Lock. If you have access to this customization suite from Samsung, here’s how to activate mini-games on the cover screen of your Galaxy Z Flip 5.

To get started, you must download Good Lock on your foldable. If you live in a supported region, you can find the app on the Galaxy Store. You can click here or manually search for the app on the store if the link doesn’t work. Once Google Lock is installed, download and install the MultiStar module on your Galaxy Z Flip 5. It’s available on the Galaxy Store too (click here).

Now, open the MultiStar app and tap on the I ♡ Galaxy Foldable menu at the top. Go to the Game Widget section and activate the widget. When done, go back to the homescreen, fold your Galaxy Z FLip 5, and turn on the cover screen. Finally, swipe to the left side of the screen until you find the Games Widget. Tap on it and voila! You have a dozen mini-games to play on the cover screen.

A list provided by SamMobile has the following titles: Back Bounce, Cake Slice Ninja, Carrom Clash, Color Burst, CubeTower, Daily Solitaire, Gold Adventures, Moving, Northern Heights, Pin The Ufo, Retro Drift, and Tiger Run. All of these games are optimized for the Galaxy Z Flip 5’s cover screen, so you should get smooth gameplay. It’s unclear if Samsung plans to add more games in the future.

The Galaxy Z Flip 5 can run any app on the cover screen

The Galaxy Z Flip 5’s larger cover screen isn’t just about playing mini-games, though. The screen is big enough to run any app, and it does. Unfortunately, Samsung doesn’t offer this capability by default and instead, it wants you to manually enable the feature using Good Lock.

The problem is that Good Lock isn’t available globally, blocking some Galaxy Z Flip 5 users from getting the best out of their new foldable. Thankfully, there’s a third-party alternative that offers the same function. The CoverScreen OS app allows you to run any app on the new Samsung foldable’s external display. Hopefully, the Korean firm will roll out Good Lock globally to ensure that users don’t have to rely on third-party software.


[ad_2]
Source link

Dell enters generative AI fray with hardware and software solutions

0
[ad_1]

PC maker Dell is entering the generative AI fray with new hardware and software infrastructure to help companies get started with their AI projects. The Texas-based firm has released what it calls Dell Generative AI Solutions to facilitate the efforts. According to the company, it delivers everything you need to set up large language models (LLM) for creating AI tools.

Dell‘s Generative AI Solutions include an end-to-end enterprise framework that can be used to build, customize, and deploy AI tools with “billions of parameters.” AI Ops and ML Ops platforms developed in partnership with Nvidia will help developers deliver a smooth end-user experience. Its software infrastructure lets them train the tool to quickly scale inferencing, which is the process of deducing input data to provide accurate output.

The PC giant also offers hardware infrastructure comprising servers, storage solutions, networking solutions, and Nvidia GPUs. The company touts the setup to be robust enough to run powerful LLMs efficiently. Developers can leverage Dell’s management tools to proactively monitor operations and get predictive analytics for simplified infrastructure operations.

“Generate higher quality, faster time-to-value predictions and outputs, while accelerating decision-making with a powerful full-stack GenAI solution from Dell Technologies and NVIDIA,” Dell said in an official product brief. “This joint architecture delivers a modular, secure, and scalable design supporting a multitude of inferencing use cases and computational requirements.”

The generative AI craze is getting a new push from hardware companies

Microsoft-backed OpenAI opened up a new world of generative AI tools with the launch of ChatGPT last year. Google followed up with Bard earlier this year. Many other smaller software companies have also come up with similar tools to help their customers with everyday tasks. Meta, Samsung, and more are working on their respective solutions too.

While the public mostly sees the software front of this AI race, hardware companies have been silently giving the generative AI craze a push with infrastructure setups for those looking to experiment with AI. Dell is joining the fun too. It is targeting enterprises that are still exploring how generative AI can help their businesses and clients. The PC maker will make it easy for them to get started and scale over time.

“Generative AI represents an inflection point that is driving fundamental change in the pace of innovation while improving the customer experience and enabling new ways to work,” Dell co-COO Jeff Clarke said in a statement to The Verge.


[ad_2]
Source link

Hacker Group of 1980s Returns With Secure Coding Framework

0
[ad_1]
Hacker group creating Framework

Cult of the Dead Cow (cDc) is one of the oldest and most highly influential hacking groups that was formed at the end of the 1980s.

This group was once responsible for distributing hacking tools and pointing out flaws in software companies, shaming them to improve their security posture.

However, Cult of the Dead Cow is now back with a coding framework that can be used by developers who are willing to use strong encryption and renounce revenue from targeted ads based on the users’ detailed information gathered, as most social media apps do now.

Government Eroding Privacy

There have been several cases where the government is asking application owners to sell the encryption details to the government so as to disclose the content and user identities to the government on demand. 

Many tech giants like Apple, Meta, and Signal are struggling to fight the Online Safety Bill passed by the Britain Government.

As part of this, the CDC has released a framework known as “Veilid,” which can develop applications that work similarly to peer-to-peer network sharing like BitTorrent.

Cindy Cohn, the executive director of the nonprofit Electronic Frontier Foundation, said, “It’s great that people are developing an end-to-end encryption framework for everything. We can move past the surveillance business model.”

Biggest minds of Cybersecurity in cDc

The hacking group had numerous members who were highly skillful in the field of cybersecurity and have helped a lot towards securing the application and security posture for top tech firms.

Two of the cDc persons were responsible for disclosing a critical flaw in one of the most widely used software and coordinated with the vendors for patching them.

One of them was Peiter “Mudge” Zatko, a former head of security at Twitter and Stripe, and the other was Christien Rioux, the founder of Veracode.

“Veilid” is one of the biggest releases in over a decade, coding for more than three years, as per reports from Washinton Post.

However, no documentation was released regarding the design choices and collaborative work on the initial messaging app which does not require mobile numbers.

Keep yourself informed about the latest Cyber Security News by following us on GoogleNews, Linkedin, Twitter, and Facebook.


[ad_2]
Source link

How to protect your child’s identity

0
[ad_1]

Identity theft is a serious problem, especially when it affects children.

As we have mentioned before, identity theft is a serious problem, especially when it affects children. Identity thieves love preying on minors, simply because it usually takes longer before the theft is noticed.

A person’s identity represents a certain value. If it is stolen and abused, it can cause a lot of harm.

Stolen identities (even childrens’) can be abused to:

  • Apply for credit cards
  • Obtain loans
  • Seek benefits
  • Open bank accounts

In many cases, the consequences are only financial and there is a good chance you will be compensated if you can show the theft was not a consequence of negligence on your part. If your identity is used for criminal activities, it could be a lot worse. Suppose a criminal uses the bank account opened in your name as a money mule. A money mule is someone who is used to accepting money from scammers, keeping it in their account for a period of time, and then forwarding it on to a second account. Intentional money muling is a form of money laundering. Those found guilty can face imprisonment of up to 14 years.

The additional problem for children is that they typically don’t receive the bank statements, credit card bills, and other communications that would alert adults about suspicious financial activity. This is why child identity theft can go on for years before it is discovered.

And when it is discovered it’s often in a very annoying way. For example when the child’s first student loan application is denied.

You should never share a child’s Social Security Number (SSN) with anyone who doesn’t have a very good reason for having it. Even those that mean well can have their data stolen at some point. Sometimes we read advice stating that you can limit the consequences by only providing the last four digits of the SSN, but you should be aware that even the “last four” can be useful to identity thieves.

When your child gets their first phone, explain to them that caller-IDs can be spoofed. And if they receive a call from someone claiming to be from banks or other trusted institutions, have them answer that this person needs to call one of the parents and hang up.

Also tell your children not to give their email address to just anyone when they get their own, and have them ask permission before registering for an online contest or a service. Many spammers and phishers watch these groups or emailing lists to get new email addresses.

If a site or service is covered by the Children’s Online Privacy Protection Act (COPPA), it has to get your consent before collecting personal information from your child if they are under the age of 13, and it has to honor your choices about how that information is used. This is a reason why you should tell your kids never to lie about their ages when they’re signing up for new accounts. The age requirements are there to protect them from online harm.

Be aware that you are a role model. Don’t spy on your children, but openly follow their social media accounts. It’s a win-win that keeps you in the loop and it makes them a bit more conscious of what they post.

Still, even if you have been careful, an identity can be stolen. More often than not identities get stolen in data breaches. With most data breaches, cybercriminals want to steal names, email addresses, usernames, passwords, and credit card numbers. But most cybercriminals will steal any data that can be sold, used to breach other accounts, steal your identity, or make fraudulent purchases with.

Countermeasures

You have every right to become anxious when your child starts receiving credit offers in the mail, or if you see unexpected activity on their email, phone or bank accounts. It may mean that their personal information has been compromised.

If you become aware of anything suspicious you can request a security freeze for your child at each of the three national credit bureaus (Experian, TransUnion and Equifax). When you request a security freeze, the bureau creates a credit report for your child and then locks it down, so that any lender who attempts to process an application that uses your child’s credentials will be denied access to their credit history. This prevents any loans or credit cards from being issued in the child’s name. When the child becomes an adult you’ll have to lift the freeze by contacting each credit bureau individually.

For more tips on how to protect your identity, or if you believe you are the victim of on identity crime, contact the Identity Theft Resource Center. You can speak to an advisor toll-free by phone (888.400.5530) or live-chat on the company website idtheftcentidtheftcenter.orger.org.


Malwarebytes EDR and MDR removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link