The Collide+Power security flaw could affect almost every CPU

0
[ad_1]

Researchers from the Graz University of Technology in Austria and CISPA Helmholtz Center for Information Security in Germany have recently discovered a new security flaw named “Collide+Power,” which can not only affect almost every CPU but also allow threat actors to monitor CPU power consumption, potentially leading to the unauthorized leakage of sensitive information.

Dubbed CVE-2023-20583, the vulnerability involves studying power consumption patterns during the processing of both known data from the attacker and unknown data from the victim. Therefore, by examining the power usage, a threat actor can deduce the contents of the victim’s CPU cache memory, thus revealing encryption keys and short identifiers.

Additionally, the Collide+Power security flaw comes in two variants: MDS-Power and Meltdown-Power. When it comes to MDS-Power, it can steal data from another security domain co-located on a sibling hardware thread at a rate of 4.82 bits per hour, provided hyperthreading is active. However, at this pace, extracting a 4,096-bit RSA key from a cloud vendor would take a full month.

On the other hand, Meltdown-Power is even slower, leaking data at a rate of 0.136 bits per hour. And in real-world scenarios, the attack becomes even more sluggish due to memory prefetching, requiring an estimated 2.86 years to obtain a single bit from the kernel if fully deployed.

“However, this low-security risk might drastically change if new architectural or microarchitectural ways of prefetching victim data in co-location with attacker-controlled data are discovered,” said the researchers.

Patching the vulnerability

Although the security vulnerability might not seem viable for regular hackers, it has garnered widespread interest from companies like AMD, which has already confirmed that their EPYC server processors include a performance determinism mode that can mitigate the risk of data leakage. Similarly, Intel also cited the effectiveness of existing features and guidance for mitigating power side-channel attacks demonstrated in response to previous threats like PLATYPUS and Hertzbleed.


[ad_2]
Source link
The number of daily Threads users is in free-fall; those who visit the platform close the app quickly

0
[ad_1]
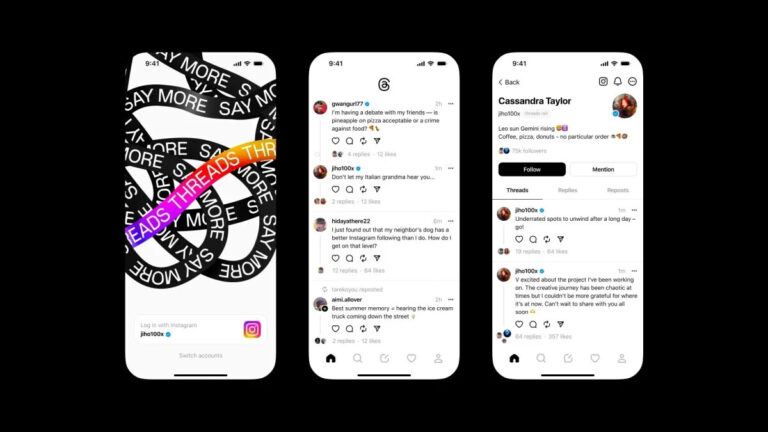
The early strength of X competitor Threads has disappeared. If you were the kind of person to throw out puns, you might say that the Instagram-based social media platform was (ahem) getting to be threadbare. Luckily, this writer would never subject you to this kind of corny writing style (ahem, again). Let’s get to some actual data thanks to CNN. The latter cites information from app research firm Sensor Tower which shows that Threads’ daily active users count has plummeted 82% from its launch day through the end of July. Ouch.
That figure indicates that just 8 million users are visiting Threads every day. You might recall that Threads burst onto the scene by notching 100 million accounts during its first five days in business. The platform, linked to Instagram and owned by Meta, was created to give people an alternative to what was then called Twitter after many Twitter users were unhappy with changes that owner Elon Musk was bringing to the site.
The day after the release of the Threads app, the latter had a peak number of 44 million active users visiting the social media platform and it has been downhill since. Sensor Tower also pointed out that people are opening the app less and when they do open the app, subscribers are spending less time using it. 

On the day Threads went live, users opened the app 14 times on average and spent 19 minutes during each session rummaging through the site’s content. By August 1st, the average user opened the app only 2.6 times (again, on average) and each time these subscribers spent only 2.9 minutes browsing through Threads. Those figures come from Sensor Tower but another market research firm, Similarweb, reported similar findings.

Similarweb’s data reveals that a peak 49 million users visited Threads on July 7th, the day following the platform’s launch. David Carr, a senior insights manager at Similarweb, said that by July 29th that figure had dropped to 11 million which was a 78% decline from the peak number. Sensor Tower says that the average user count for Threads continues to decline at the rate of 1% daily. Despite the falloff, Meta CEO Mark Zuckerberg said last month that he was “quite optimistic” about Threads.

Zuckerberg, who co-founded Facebook which changed its corporate name to Meta back in 2021, also stated that “We saw unprecedented growth out of the gate and more importantly we’re seeing more people coming back daily than I’d expected. And now, we’re focused on retention and improving the basics. And then after that, we’ll focus on growing the community to the scale we think is possible.”

When Threads launched early last month, it did so without many of the features that you find on X. But late last month the platform did disseminate an update and while it still doesn’t offer several key Twitter features, Threads hopes to narrow the gap soon including the launch of a Threads website.

[ad_2]
Source link

Tired of Gmail? Well, Shortwave is now on Android

0
[ad_1]

Back in 2014, Google brought forth an amazing email application that was well-loved… then the company got rid of it. It was called Inbox, and it offered a unique email experience. Well, if you miss it, you’ll be glad to know that Shortwave, its spiritual successor, is now available as an Android app, according to Android Police.

Google Inbox had a completely different approach to the email experience. Rather than presenting your emails in a chronological feed, the platform would actually bundle your emails into different folders. This lets you organize your emails however you wanted and avoid clutter. But, it was a Google product, so it, naturally, came with an expiration date. It was discontinued about five years later.

The Shortwave Android app is now available

With Shortwave, it’s the classic story of “Company employee leaves company and makes a product that the company used to make.” Shortwave is an email client that offers close to the same functionality as Inbox, and it was created by an ex-Google employee. It was in beta testing for quite some time before finally getting a stable release. As with most apps, it was available on iOS before hitting Android, but you can now get it on the Play Store.

Shortwave takes the same approach as Inbox did. It takes emails from the same source and automatically bundles them into groups. For example, if you’re an avid Redditor, and you like to receive emails from the platform, well you’ll be able to view all of the emails from Reddit all in one place rather than seeing them pepper your inbox. They’ll all be kept in one clean-looking bundle.

If there are email conversations or bundles that are important, then you’ll want to see them the moment you open the app. Shortwave lets you pin conversations and bundles to the top of the UI. So, you’ll be able to easily access them at a glance. Also, you can name the bundles.

Shortwave is free to use, but if you want to access emails in your conversations that are more than 90 days old, then you’ll need to pay the $9/month subscription. Also, with the subscription, you’ll have faster customer support with responses within one business day.


[ad_2]
Source link

Major ChatGPT update brings suggested replies, keyboard shortcuts

0
[ad_1]

OpenAI has announced a major update for ChatGPT. Or as the company puts it, “a bunch of small updates” that will improve your user experience with the generative AI tool. It’s pushing prompt examples, suggested replies, keyboard shortcuts, and more. All of the new features and improvements will roll out to users over the next week.

For starters, ChatGPT will now show prompt examples on the home page to help you get started. If you can’t frame a powerful prompt quickly, you can use the examples to boost your creativity. You can also simply click on an example to start a conversation and get along with the generative AI tool before following up with your prompts.

To ensure continued conversations, ChatGPT will suggest relevant follow-up prompts or replies after generating a response. Clicking on those suggestions will give you more relevant information on what you are looking for. Additionally, all ChatGPT Plus users will now have access to GPT-4 by default.

GPT-4 is the latest and most advanced version of the large language model powering the tool. Released in March, it has been available to Plus users for a while now. However, all this while, ChatGPT didn’t remember the last model used and defaulted Plus users back to GPT-3.5 when starting a new chat, forcing them to manually switch to GPT-4. OpenAI has finally fixed this annoying behavior. Free users remain on GPT-3.5, though.

The latest round of updates for ChatGPT also brings support for multiple files. Part of the Code Interpreter beta for Plus users, this feature allows you to upload several files and have the tool analyze data across them all to generate insights and meaningful observations. OpenAI doesn’t let free users upload files to ChatGPT for analysis.

ChatGPT is also adding keyboard shortcuts

OpenAI is further improving the ChatGPT experience with keyboard shortcuts. The AI tool currently supports seven keyboard shortcuts on Windows PCs: Ctrl+Shift+O (open new chat), Shift+Esc (focus chat input), Ctrl+Shift+; (copy last code block), Ctrl+Shift+C (copy last response), Ctrl+Shift+S (toggle sidebar), Ctrl+Shift+Backspace (delete chat), and Ctrl+/ (show all keyboard shortcuts).

You can also see these shortcuts from the “question mark” button on the bottom right corner of the chat screen. Last but not least, ChatGPT will no longer log you out of your account every two weeks. It will keep you logged in. And when you manually log out and log back in, the AI tool will greet you with a “much more welcoming page.” As said earlier, these changes will reach all ChatGPT users globally over the next week.


[ad_2]
Source link

TikTok adapts to EU digital rules: non-personalized For You feed coming soon

0
[ad_1]

In 2022, the European Union created clear rules for online platforms’ regulations with the Digital Services Act (DSA). The DSA oversees platforms like social media, online marketplaces, and search engines, introducing measures to curb discriminatory targeted ads, reduce illegal and hateful online content, and enhance safeguards for minors against harmful material.Soon after, the EU urged TikTok to comply with the new law or face a ban, which seems to have worked, as TikTok has been updating its policies ever since. According to a blog post from the social media platform, in the coming weeks, TikTok is introducing an option for its users in the EU to turn off personalization in the For You feed. Additionally, EU users aged 13-17 will no longer see personalized advertising based on their activities on or off TikTok.When personalization is turned off, the For You and LIVE feeds will display popular videos from users’ local areas and around the world, moving away from personalized content recommendations. Non-personalized search will offer results with popular regional content and preferred language. The Following and Friends feeds will maintain a chronological display of followed creators rather than based on the viewer’s profile.

Throughout the past year, TikTok introduced several updates focused on user control over recommendations. This includes the option to filter specific hashtags in the For You feed and the introduction of Refresh, allowing users to experience their For You feed content as if they were newcomers to TikTok.

In addition to these updates, TikTok also mentions an additional reporting option for its EU users. This option will allow users to report content they believe is illegal, including advertising. Users will be able to select from a predefined list of categories like hate speech, harassment, and financial crimes for reporting content.

Content reported as illegal will go through a two-step review on TikTok. First, if it violates TikTok’s policies, it will be removed globally. If not, a specialized team will assess its legality under the specific country’s laws. If found unlawful, access will be restricted. Both the creator and reporter will be informed of the decision and reasons, with a chance to appeal if they disagree.

[ad_2]
Source link

Google Results about you dashboard gets an impressive upgrade

0
[ad_1]

In a recent blog post, Google announces its upgrade to the Results About You dashboard. This upgrade brings a ton of improvements to the privacy-focused features, and users might get to use the new features more often. With this tool, users can keep a tab on their personal information that is lurking somewhere on the internet.

Not only can they find such information, but they also can request the removal of this information. Netizens around the world will appreciate this tool, as well as its recent improvements. Now, users can get notifications informing them when anyone searches the internet for their personal information.

The tech company had plans to roll out this notification feature last year, but the plan didn’t see the sun. However, it’s good to know that the notification feature is finally here, along with other necessary improvements. Let’s now have a look at the improvement to Google’s Results About You dashboard.

All improvements coming to the Google Results About You dashboard

When this feature became available last year, netizens that had access to it were joyful. This joy came as a result of knowing that they could find their personal information online and request its deletion. However, there were some flaws regarding this feature and how users can benefit from it.

The major flaw with this feature was that for users to find their personal information, they will need to search for themselves. With this new update, users can find their details without searching for themselves on the internet. This is a very important update as it goes further to protect users’ privacy.

Now all users need to do is input their personal information into the dashboard. Once this is done, the dashboard will in turn pull up all websites that have the user’s personal information in them. From here, the users can then request that this information be taken off the internet.

Also, the improvement to the Results About You dashboard brings notifications to users’ devices. These notifications will tell how many search results on the internet show the users’ personal information. Users can then act on this information and request that the details be taken off the internet. Other updates bring more controls for the family and updated policies on personal explicit images.

However, requesting that personal information be taken down from search will not erase your details from the internet. It’d only help to limit how people get access to these details, hence protecting user privacy. Currently, this feature is only available for usage in the US via the Google App.


[ad_2]
Source link

Warner Bros. Discovery lost subscribers following Max rebranding

0
[ad_1]

Warner Bros. Discovery lost nearly two million subscribers across its streaming apps in the second quarter of 2023. The drop came amid a massive rebranding and restructuring of its products that saw HBO Max turn to Max in May, encompassing Discovery Plus within it. The latter service is also available standalone, though.

In its Q3 2023 earnings report on Thursday, Warner Bros. Discovery stated that it had 95.8 million subscribers across all of its streaming services globally. The figure is down by 1.8 million from the 97.6 million subscribers it had at the end of Q1. However, the company doesn’t seem to be worried. Its chief financial officer, Gunnar Wiedenfels, attributed the drop to “overlapping subscriber bases between Max and Discovery Plus.”

The Warner Bros. Discovery executive further added that it was an “expected churn” following the end of The Last of Us season 1 and the series finale of Succession. CEO David Zaslav echoed his comments, saying that the subscriber disruption was expected after the Max rebranding. The process involved asking existing HBO Max subscribers to download a new Max app to their devices, which many likely decided not to do.

Zaslav hinted that the company was expecting an even bigger churn, so a loss of 1.8 million subscribers isn’t too bad news. More importantly, the drop didn’t hurt streaming revenue. Warner Bros. Discovery generated a revenue of $2.73 billion from the streaming business between April and June of 2023. That’s notably more than the $2.5 billion it generated in the first three months of the year.

The Max rebranding hasn’t helped the company become profitable yet

The company’s streaming business still isn’t profitable, though. It reported a three million operating loss this past quarter. But on the bright side, Zaslav said that the firm is expecting to become profitable at least in the US this year. Warner Bros. Discovery is also looking to launch Max internationally over the next year and beyond. The platform is touted to boast “full capability to deliver live programming,” with the company planning to share more soon.

“We’re early on, but news and sports are important differentiators – they’re compelling, and they make these platforms come alive,” Zaslav said during an earnings call (via The Verge). He has talked about the importance of incorporating news and sports into Max in the past as well. Rumors have it that the platform could add live CNN broadcasts and more live programming down the line.

This is part of a broad strategy that involves exiting the regional sports network business. Warner Bros. Discovery is looking to “sell or cease operations of the company’s networks by the end of this year.” Its AT&T SportsNet channels currently air local baseball, basketball, and hockey games in the US.


[ad_2]
Source link

CISA Advisory of Top 42 Vulnerabilities Frequently Exploited

0
[ad_1]
Exploitation of Vulnerabilities 2022

The Cybersecurity and Infrastructure Security Agency (CISA) has published a report which was co-authored by the NSA, FBI, and the FYEY (Five Eyes) from different countries.

The report provides a complete insight into the Common Vulnerabilities and Exposures (CVEs) that were frequently exploited by threat actors.

As per the report, threat actors have been relying on outdated software vulnerabilities for exploitation instead of those disclosed recently. Systems that were exposed to the internet and left unpatched were mostly targeted.

The Exploitation of Vulnerabilities in 2022

In 2022, threat actors were found to be exploiting known vulnerabilities within two years of their public exposure. Most of the exploited vulnerabilities had Proof-of-concept (PoC) available publicly.

However, timely patching of these vulnerabilities will reduce threat actor operations resulting in the malicious actors switching to a more time-consuming process like a Zero-Day exploit or conducting software supply chain operations).

Top Exploited Vulnerabilities

The most exploited vulnerability of 2022 was CVE-2018-13379 which affected Fortinet SSL VPNs. Moreover, this vulnerability was one of the most exploited in 2020 as well as in 2021.

Many organizations still haven’t patched this vulnerability which gives more space for malicious actors.

Atlassian had two vulnerabilities CVE-2021-26084 (arbitrary code execution) and CVE-2022-26134 (Remote code execution), which were exploited mostly in 2022. Both of these belong to Confluence Server and Data Center.

Microsoft Exchange email servers had three CVEs CVE-2021-34473, CVE-2021-31207, and CVE-2021-34523 which were frequently exploited in 2022. All of these vulnerabilities are known as ProxyShell which can allow a threat actor to execute arbitrary code.

VMware Workspace ONE Access, Identity Manager, and other VMware products had two vulnerabilities CVE-2022-22954 and CVE-2022-22960 which were mostly targeted by threat actors.

These vulnerabilities were RCE, Privilege Escalation, and Authentication.

Furthermore, the CISA has released a list of 42 vulnerabilities that were exploited by threat actors very often and they are yet to be patched by many organisations.

Users of the specified products are recommended to upgrade their products to the latest patched version to avoid exploitation by threat actors.

It is a best practice to keep track of the recent patches and the versions of software that are under use in an organization.

Keep yourself informed about the latest Cyber Security News by following us on GoogleNews, Linkedin, Twitter, and Facebook.


[ad_2]
Source link

Phishing campaigns are using AMP URLs to avoid detection

0
[ad_1]

Researchers have found a new phishing tactic that uses Google Accelerated Mobile Pages (AMP) URLs to look trustworthy

Researchers have found a new phishing tactic which uses Google Accelerated Mobile Pages (AMP) to make URLs look trustworthy. The tactic is designed to slip past both software and users on the lookout for strange and untrustworthy domain names.

AMP is an open-source HTML framework designed to make web content load faster on mobile devices. The framework was originally created by Google, but over 30 news publishers and several technology companies have collaborated on the project.

AMP works by stripping bloat from web pages by forcing heavy restrictions on the kind of code that can be included. If it’s slow, you can’t have it. The stripped down pages are served from caches so they load faster, and the most popular cache by far is Google’s.

The phishing technique uses the URL of a web page cached by the Google AMP Viewer. For example, the home page of the website example.com would appear in the Google AMP Viewer as https://www.google.com/amp/s/example.com.

Although they look similar, and both contain ‘example.com’, the crucial difference is the first is served from the example.com domain and the second is served from the google.com domain.

Because of that, it’s just another web page on the google.com website and therefore inherits alll the trust that very well known domain name carries with both individuals and software, like email filters. And while it’s possible to block everything under https://google.com/amp/s/, that would inevitably block huge numbers of legitimate websites as well.

Threat actors can use this technique to cloak malicious websites in the legitimacy of the google.com domain, or they can use it to trigger redirects from the AMP URL to a malicious site.

The researchers found that the Google AMP URLs have proven to be very successful at reaching users, even in environments protected by secure email gateways.

Alongside the use of AMP URLs, the researchers also saw:

  • Open redirects on trusted domains like microsoft.com being used.
  • Chains of redirects linking the AMP URL to the malicious site, not just a single redirect.
  • Image-based phishing emails that bypass filters looking for common phrases in text.
  • CAPTCHA services used to disrupt automated analysis.

Using CAPTCHAs, the attackers try to keep automated crawlers belonging to security vendors and researchers out, and only let humans through that are rife to be phished. I used the word “try” in that last sentence on purpose because there are several crawlers out there that are equipped with CAPTCHA solving abilities that outperform mine.

How to avoid phishing attacks

  • Don’t take things at face value. Phishing attacks often seem to come from people or brands you know, and use themes that require urgent attention, such as missed deliveries, account suspensions, and security alerts.
  • Take action. If you receive a phishing attempt at work, report it to your IT or security team. If you fall for a phish, make your data useless: If you entered a password, change it, if you entered credit card details, cancel the card.
  • Use a password manager. Password managers can create, remember, and fill in passwords for you. They protect you against phishing because they won’t enter your credentials into a fake site.
  • Use a FIDO2 2FA device. Some forms of two-factor authentication (2FA) can be phished just as easily as a password. 2FA that relies on a FIDO2 device can’t be phished.

Malwarebytes removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

Samsung website confirms Galaxy Tab S9 FE, S9 FE+ names

0
[ad_1]

Samsung has confirmed the existence of the Galaxy Tab S9 FE and Galaxy Tab S9 FE+. An official Samsung website in France has named the two unannounced tablets, hinting at an imminent launch. The tablets feature in a list of Galaxy devices compatible with the company’s digital assistant, Bixby. The website (via) itself is a Bixby guide.

Rumors about Samsung working on new Fan Edition (FE) tablets have been doing rounds on the internet for some time now. We have already seen the devices in various certification and benchmark listings, while leaked renders have revealed their design too. However, the Galaxy Tab S9 FE and Galaxy Tab S9 FE+ continue to evade the market.

There were speculations that Samsung might unveil the new affordable tablets during the Galaxy Unpacked event last week, but it didn’t. The Korean firm only launched the Galaxy Tab S9, Galaxy Tab S9+, and Galaxy Tab S9 Ultra, all of which are true-blue flagships. The FE models got no mention anywhere, with the event also bringing the Galaxy Z Fold 5, Galaxy Z Flip 5, and Galaxy Watch 6 series.

While we still await the launch of the Galaxy Tab S9 FE and Galaxy Tab S9 FE+ or even a tentative launch date, Samsung mentioning them on its website suggests the wait won’t be much longer. The company also has the Galaxy S23 FE in the works, with rumors pointing at a September launch for it. Maybe all three FE devices will debut on the same day next month, we will have to wait and watch.

The Galaxy Tab S9 FE and S9 FE+ will be affordable flagship tablets

Samsung’s FE lineup of Galaxy devices is known for offering flagship-grade specs at a lower price point. The company makes that possible by removing some premium features from existing flagship products while keeping the basics. It should be no different with the Galaxy Tab S9 FE and Galaxy Tab S9 FE+.

Based on leaks and certification listings, the two will be stripped-down versions of the Galaxy Tab S9 and Galaxy Tab S9+, respectively. The FE models share the screen size, S Pen, battery capacity, charging speed, and more specs and features with the flagships. At the same time, they might miss out on a Dynamic AMOLED 2X display, an under-display fingerprint scanner, and the latest flagship processor. Stay tuned for more information about the upcoming FE-series Samsung tablets.

Samsung website Galaxy Tab S9 FE names confirmed


[ad_2]
Source link