Wii U players can now play Mario Kart 8 and Splatoon online again

0
[ad_1]

If you’re a Wii U player, it’s natural to feel like your days are numbered. The Wii U shop went down not too long ago. Also, the Wii U version of Mario Kart 8 and Splatoon lost their online access, but that problem seems to have been solved. You can play these two titles online again.

Back in March, these two games lost their access to the online servers, and that upset a lot of players. While it might feel like Nintendo did this to push them to buy a Switch (which has Mario Kart 8 and Splatoon 2), that’s not the case. The company announced that there was a security flaw affecting these two titles. So, it had to take them down.

The Wii U version of Mario Kart 8 and Splatoon are back online

If you own these games, and you play them online often, then it might have been a pretty grueling wait. These games went down about four months ago, and that could be frustrating.

Nintendo didn’t give too many details on what the issue with these two games was. Be that as it may, OatmealDome (via Engadget) stated on Twitter that the Wii U is vulnerable to an attack called “ENLBufferPwn”. This issue also affected other games like the Switch version of Mario Kart 7.

As you can imagine, Nintendo dragged its heels on fixing the Wii U versions of its games. The Switch is the more modern console, and it’s still raking in money for the company. The Wii U was swiftly dropped when Nintendo Switched over to its new console. Now, six years later, we’re all talking about the next generation of the Switch.

Dubbed the Switch 2, this console could be one of the few actual Nintendo console sequels. The SNES was the sequel to the NES and the Wii U directly succeeded the Wii. There’s no consistent line of consoles as we see with the PlayStation and Xbox consoles.

The Switch 2 is believed to come out next year. When that happens… well, the Wii U has been on death’s door for a while; it might finally cross the threshold.


[ad_2]
Source link

Nothing has a more affordable sub-brand named CMF by Nothing

0
[ad_1]

Compared to other companies like Samsung, Apple, Motorola, Nokia, and so on, Carl Pei’s Nothing still is a baby. It’s only a few years old, yet the company already has a sub-brand. It’s called CMF by Nothing, and it’s going to center around selling more affordable products.

What is CMF by Nothing all about?

This is a pretty surprising move by Nothing. The company is only three years and two smartphones in. While we’re all familiar with the overall Nothing aesthetic, the company is still forming its own identity. However, in a new Nothing Community update, Carl Pei announced the new sub-brand.

This brand will launch cheaper devices under Nothing’s name. So, it will be similar to Redmi (owned by Xiaomi) or Honor (previously owned by Huawei). It will sell these cheaper devices using resources from Nothing. So, while they’ll be under its own name, we’ll still associate them with the Nothing brand.

These two brands will share different end goals, as you can imagine. Nothing will focus on pushing boundaries, innovative designs, and employing the latest technology in its products. This will maintain the vision set forth by Nothing since day one.

CMF by Nothing, on the other hand, will mainly focus on being more accessible to users- meaning they’ll be cheaper. They won’t have the more interesting designs we see, and will continue to see, in the Nothing devices. So, if the brand eventually develops a phone, we shouldn’t expect a Glyph interface. That’s to be expected, however.

What to expect from this brand

It’s a little odd that Carl Pei is talking about a sub-brand offering more affordable devices when all of their devices have already been pretty affordable. Even the Nothing Phone (2), which got a notable boost in price over its predecessor, undercuts most of the competition.

However, the company is going forward with this new brand, and we know about two of the products coming from it. Carl Pei said in the video that it’s working on bringing a smartwatch and a pair of earbuds. One thing to note about this is that he said that it will launch them later this year. Considering that the year is already halfway finished, there’s not much time to wait.

The fact that they’re going to launch later this year means that they’ve already been in production for a while. We’re just hearing about this brand today, but CMF by Nothing could have been in the cards for quite some time. Who knows if Carl Pei was thinking of launching a sub-brand from day one? Only time will tell how these devices will fare and if starting a sub-brand will help the company.


[ad_2]
Source link

Mysterious Team Bangladesh Hackers Launched 750 DDoS Attacks

0
[ad_1]

The notorious Hacktivists group, Known as Mysterious Team Bangladesh, exploits vulnerable versions of PHPMyAdmin and WordPress.

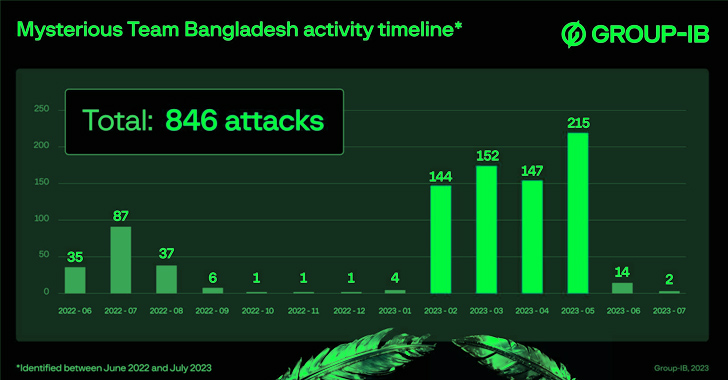
It conducts DDoS and defacement attacks through open-source utilities and is believed to have carried out over 750 DDoS and 70+ website defacements within a year.

The group has been active since 2020 and targets logistics, government, and financial sector organizations in India and Israel.

The Group-IB Threat Intelligence shared the latest report on Mysterious Team Bangladesh activities.

Detailed analysis:

According to the report, India was the most targeted nation, and the group launched a large-scale campaign against India in May 2023.

It is suspected that the group will expand its operation across Europe and Asia Pacific and the middle east at the end of 2023.

The most common technique utilized by the group to target the victim is DDOS and defacement attacks.

In addition to that, it exploits widely deployed and outdated services, such as PHPMyAdmin and WordPress.

A D4RK TSN threat actor is believed to be behind this group, and multiple active social media pages such as Facebook, Twitter, and Telegram were identified.

The group posted its past and upcoming attacks on their telegram channel which has been active since 2022.

A prime example of a group driven by religious motives is a recent campaign targeting multiple organizations in Sweden, triggered by the incident involving the burning of the Quran.

The percentage of attacks launched by the group is as follows: 88% were DDos,9% were defacement and 2.9% attacks were launched against databases.

In some cases, the group exfiltrated data from the organization and posted it on their Telegram channel.

They have the capability to launch attacks against a large number of targets quickly and assume that it has scripts for the mass exploitation of websites using the same frameworks or server software versions.

Keep yourself informed about the latest Cyber Security News by following us on GoogleNews, Linkedin, Twitter, and Facebook.


[ad_2]
Source link

How does Malwarebytes ransomware rollback work?

0
[ad_1]

Malwarebytes Ransomware Rollback rescues your data from encryption by effectively “turning back the clock” of a ransomware attack. But how does it work, exactly?

As the old cybersecurity saying goes: “It’s not if, but when.”

Everyone and their grandma have repeated this foreboding maxim about the nature of ransomware attacks, but sadly, that doesn’t make it any less true. Time and again we’re reminded that ransomware can slip past even the best defenses.

Prevention alone, it seems, can only take us so far—so when ransomware hits, organizations need a way to emerge safely from the fallout, data intact.

Enter Malwarebytes Ransomware Rollback, which rescues your data from encryption by effectively “turning back the clock” of a ransomware attack. Dr. Strange style.

But how does it work, exactly? And what are some of the advanced settings that are available?

Let’s dive into the finer details in this post.

How It Works

The bedrock of Ransomware Rollback is a kernel mode driver to monitor file system changes and make a copy of files before modification. This includes self-protection against attack to the backups.

Malwarebytes Endpoint Detection and Response (EDR) first spends a 14-day period learning what applications on the system can be trusted. During this time, it logs the various applications that typically interact with files. After this period, the EDR establishes a list of trusted, or “whitelisted,” applications.

Advanced settings includes additional features for Ransomware Rollback. Learn more here.

For performance optimization, an application that is on the whitelist is ignored.

Before any application can make any changes, apart from ignored applications, Malwarebytes EDR saves a backup copy of the file it’s trying to modify. It is unknown at the time of modification whether a process is malicious, so every file is backed up.

If the application is later found to be ransomware that encrypts the file, making it unreadable and demanding a ransom for its decryption, the EDR system can use the backup copy it saved to restore the file to its previous state. This is what is meant by “rollback.”

When all’s said and done, the system effectively nullifies the ransomware attack by ensuring a recent clean, unencrypted copy of the file is always available.

FAQ

Does ransomware rollback use Volume Shadow Copy Service?

No, ransomware rollback does not use Volume Shadow Copy Service. Instead, it uses proprietary and patent-pending technology, with protected folders as malware often targets the Volume Shadow Copy Service.

How does the service know which files to restore, is it a snapshot?

Backups are continuous, for any files modified, and are not a snapshot

The process making the change is recorded for each file. Subsequently when a rollback is performed, it is precise because only files modified by the specific process are restored.

Where is the rollback cache stored in the system?

The rollback cache is stored in a hidden Windows system folder. Typically, you can find it under: C:\ProgramData\Malwarebytes Endpoint Agent\Plugins\EDRPlugin\Backup.

Does ransomware rollback always use some amount of disk space? Why is that?

Yes, ransomware rollback always uses some disk space due to its buffer and cleanup operations. This means there will always be some small disk space used by the feature.

For every file modified, e.g., documents, pictures, etc., space for a copy is required. If there is no activity, then after a few days there would be zero used. However, if ransomware encrypted 10 Gb of files, then there would be 10 Gb of backup/before copies.

How much space does the rollback cache take up on a typical laptop or desktop?

On a typical laptop using common applications like Microsoft Office, the endpoint usually uses less than 200MB of space for a 72-hour rollback window and a maximum individual file size of 20MB – 100 Mgb.

If a computer is under attack and 10 Gb of files were encrypted, how much space would we use for the ‘before’ encryption file backup?

If a computer is under attack and 10 GB of files were encrypted, we would use approximately 10 GB of space for each ‘before’ encryption file. The system will back up the files in their original state before encryption, so the space used is equal to the size of the original files.

How far back can I rollback if my files are encrypted by ransomware?

By default, ransomware rollback stores the last 48 hours and is configurable up to 72 hours of file changes for files. You can alter these parameters in the Endpoint Protection Advanced policy.

What types of files does ransomware rollback back up? Are there any limitations or exclusions?

Ransomware rollback preemptively backs up all file types including pictures, documents, JSON/XML configurations, EXEs, unless they are explicitly excluded, globally excluded, or exceed the maximum file size.

What happens to my files in case of a ransomware attack if my disk is full?

If the hard drive is full and file encryption starts without enough disk space for a backup copy of the files, the data will be lost. Therefore, it’s crucial for users to monitor for low disk space.

Does Malwarebytes clean up files that have been backed up by Endpoint Detection and Response (EDR) after 72 hours?

Yes, our system is designed to be self-cleaning. Files that are backed up by EDR are frequently cleaned, if they are older than the configured period.

Try Ransomware Rollback Today

To recap, Malwarebytes Ransomware Rollback is a last-resort recovery tool within Malwarebytes EDR, designed for swift recovery after other defense layers have been compromised.

While useful, Ransomware Rollback doesn’t replace classic backups or EDR’s other proactive measures like Suspicious Activity Monitoring. It’s a rarely needed, but vital last-resort option. 

Read our Ransomware protection with Malwarebytes EDR: Your FAQs, answered! article for more on how Malwarebytes EDR stops ransomware attacks.

For a more technical deep-dive into Ransomware Rollback, check out https://service.malwarebytes.com/hc/en-us/articles/4413802760851-Configure-Ransomware-Rollback-in-Nebula 

Get a free EDR demo today


[ad_2]
Source link

This feature will be a nightmare for Instagram spammers

0
[ad_1]

Online communication is a great thing, but spammers can make it a nightmare. They run rampant on all major platforms, and this includes Instagram. Well, a new feature will make spamming other users a nightmare. Instagram will have people send you a message invite before they can message you, according to The Verge.

There are tools on Instagram that help to fend off spammers, but there is still room for them to leak through. It’s not as big of an issue for smaller accounts, but it can be trouble for larger accounts. These messages try to push scams, services, and even malicious links onto people, and it’s become a major problem.

Instagram is bringing message invites to help cut down on spamming

This might sound like a pretty basic feature, and Instagram does have people send message invites, but this new feature is a bit different. Normally, messages sent to you will be sent to your message requests if the account isn’t really associated with yours. However, messages from many other accounts can still fill up your inbox.

This new feature takes a more extreme approach. If an account that you don’t follow tries to message you, it will only be able to send you a single-message invite. If that account wants to message you again, you’ll need to accept that invite. Otherwise, they’re out of luck.

Also, and this will be majorly appreciated, the messages can only contain text. So many people have to deal with strangers sending them unwanted pictures and videos. They’re usually lewd in nature, and that’s not something everyone wants to open their messages to.

Instagram is rolling out this feature at the moment, so there’s a chance that you won’t see it just yet. Make sure that your app is updated just in case. One thing to note is that, in order to take advantage of this feature, you’ll need to enable it in your privacy settings.


[ad_2]
Source link

LG’s 97-inch wireless OLED TV will be available globally

0
[ad_1]

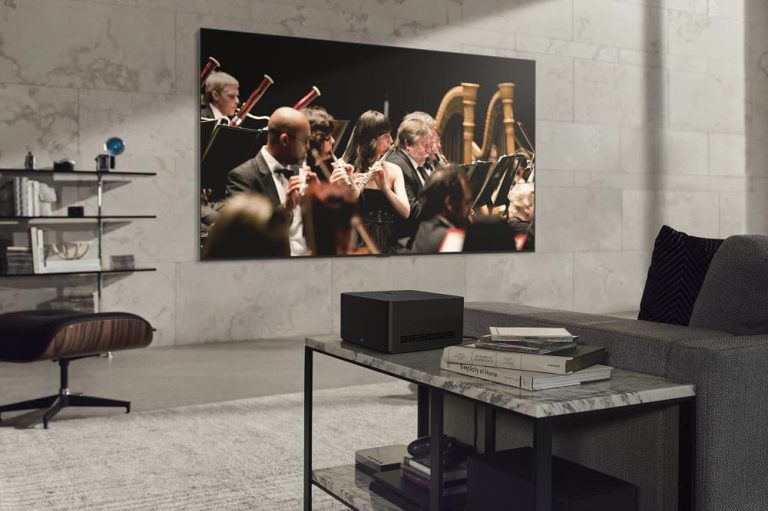
LG has just announced the global launch of its insanely expensive 97-inch wireless OLED TV. The LG Signature OLED M (97M3) is the result of LG’s mission to curb issues with cable management for a cleaner look with your TV setup. Intended to provide a simpler way to keep multiple devices connected without having to worry about an excess of wires.

The TV itself is connected to a single cable – the power cord. Everything else you want to plug into it is all connected to the TV wirelessly. How you ask? Using LG’s Zero Connect box. You connect things like your game consoles and set top boxes into the Zero Connect box and it transmits all the audio and video to the TV. It’s a super neat trick but not one that comes without a cost. The large 97-inch TV retails for 45,800,000 won in South Korea where it’s already available. Which means it won’t be cheap elsewhere.

LG plans to launch the Signature OLED M wireless TV in the US later this year

There’s no exact pricing or availability details for the US yet. But LG does confirm that “key markets” in North America and Europe will be getting the TV later in 2023. It’s also planning to launch two smaller sizes of the TV alongside the 97-inch model. This includes the 83-inch and 77-inch evo M models. Both of which come with the same Zero Connect technology but should cost a lot less than the 97-inch version. Although, consumers should still expect them to be set at pretty high prices.

The TV can support up to a 120Hz refresh rate and the Zero Connect box can be positioned up to 10 meters away from it. But LG says the box has to be facing in the direction of the screen. So you will still probably be limited in where you can place it. For connectivity the box has support for HDMI 2.1, Bluetooth, USB, LAN, and RF, and it’s compatible with Dolby Vision and Dolby Atmos. Which is perfect for connecting the PS5 now since it just got support for Dolby Atmos as well.


[ad_2]
Source link

Beta Gboard update shows a drag mode for simpler keyboard resizing

0
[ad_1]
By now, you may already be sort of fused to your phone’s keyboard, having mastered it in a spectacular way. Maybe so, but that’s not a valid reason for Google to stop updating its Gboard, bringing new tools and changes in the UX (via 9to5Google).

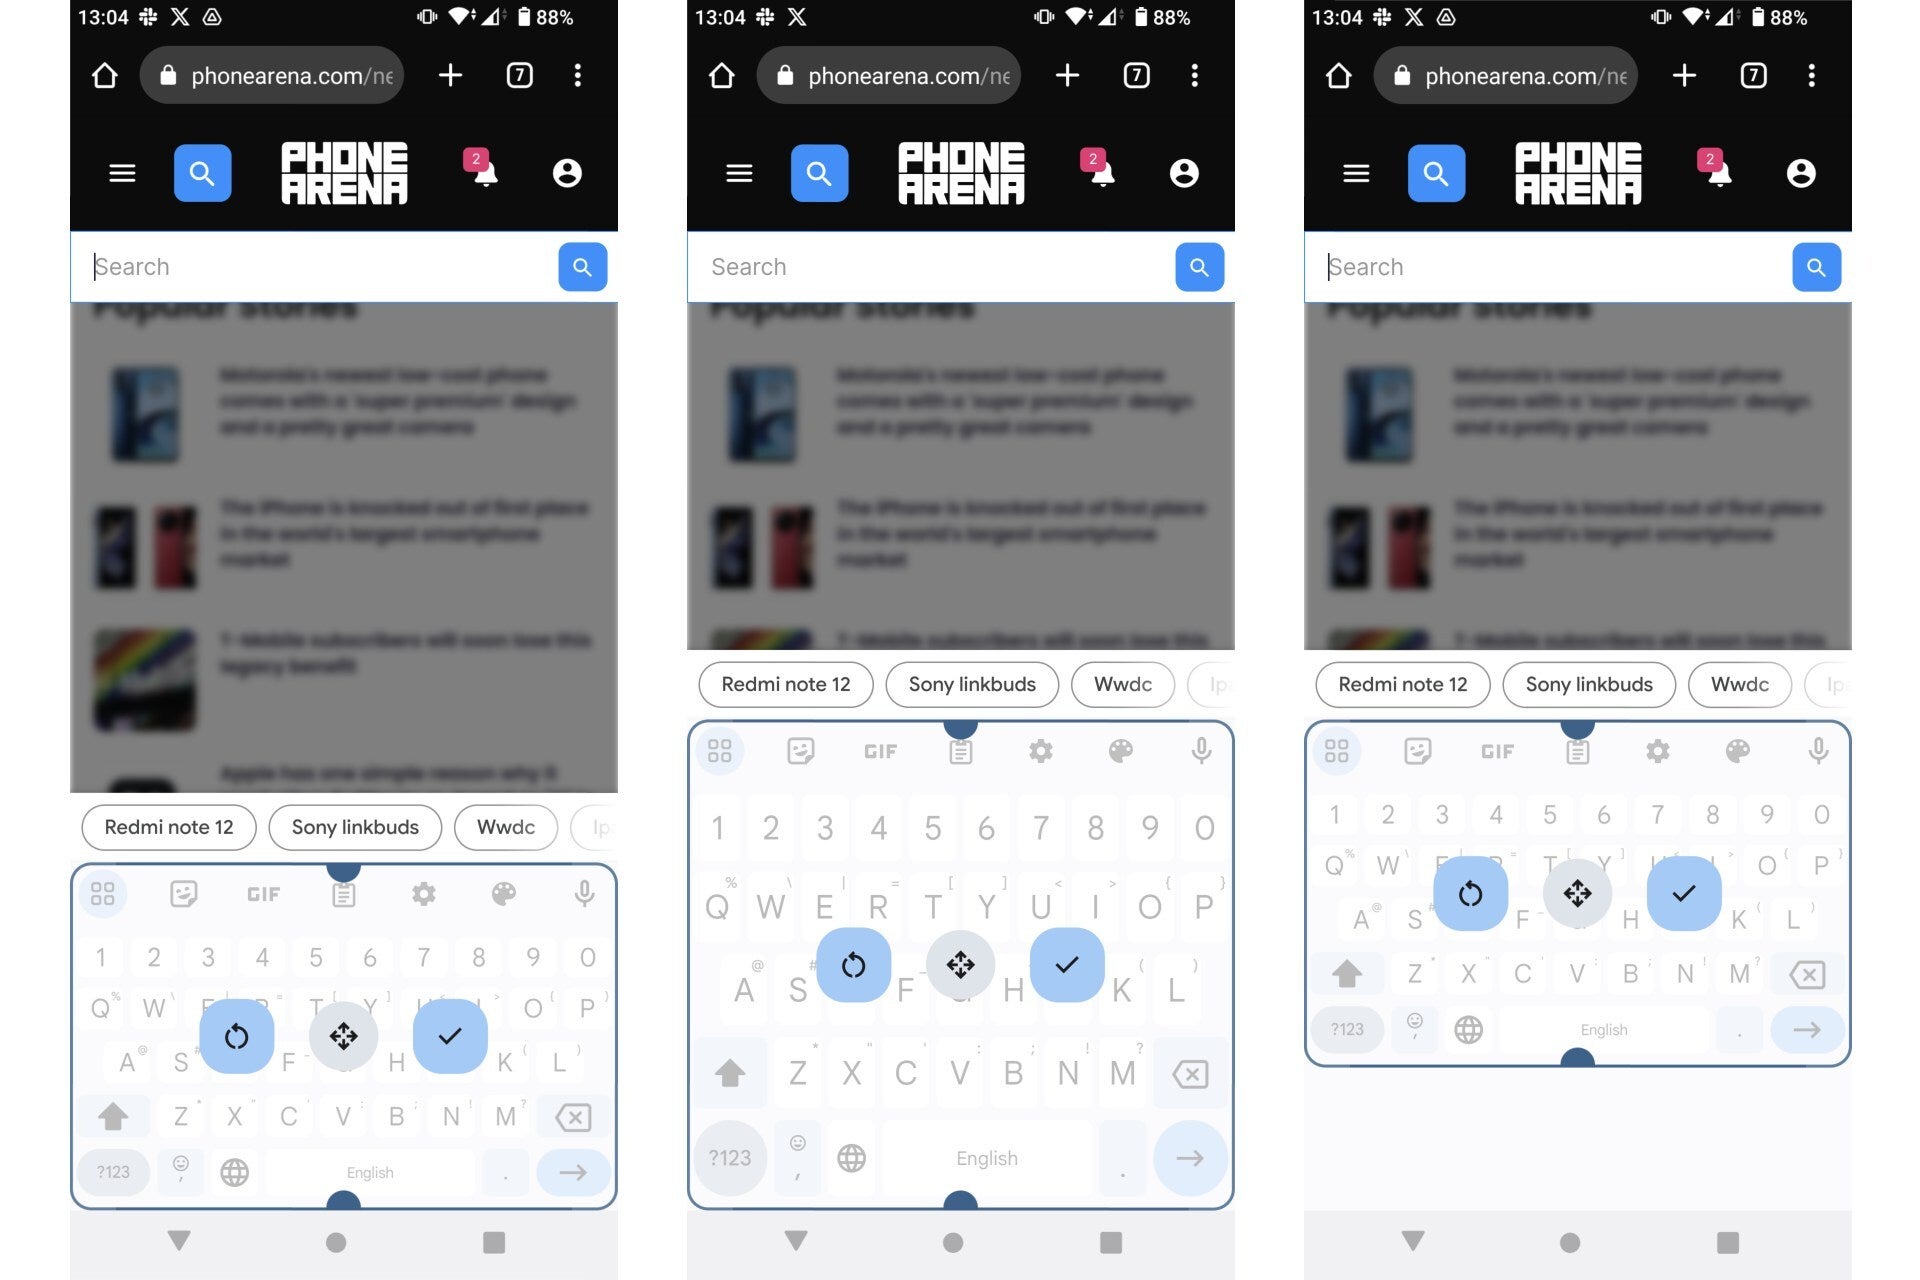
A beta update for Gboard introduces a feature to resize and customize the keyboard in a more intuitive way. The new option is accessed by tapping “Resize” in the toolbar, which takes you to an interface where the magic happens. Here is the option to drag to adjust your keyboard – release your inner control freak!

Different layouts of the new Gboard beta version


Until now, the option for Gboard resizing was buried in the Settings menu, then Preferences, then Keyboard height menu, where seven variants were presented to choose from:
  • Extra-short
  • Short
  • Mid-short
  • Normal
  • Mid-tall
  • Tall
  • Extra-tall

These seven options are not too few to choose from, but having the ability to drag the corners around is an even greater deal for everyone who values ultra customization above all. This beta “Resize” option allows users’ keyboards to take up as little as a third of the screen, or a half, or three-quarters.

What shall we do with the empty spaces?


When you resize your Gboard to a smaller form factor, you’ll see that free space opens up around/under. That’s the moment you realize you can actually move around the keyboard layout. There’s an option to “lock” it via a checkmark to hit or to reset it.

This mode is different from the Floating keyboard, which too allows users to move around and resize the keyboard, but Resize offers more customization. Though sharing some resemblance with One-handed mode, it’s not the same, either.

Resize comes with Gboard version 13.2.05.x (for both phones and tablets), which is currently in beta. Please, take note that this version it’s not available on all Android devices right now.

[ad_2]
Source link

Film companies lose battle to unmask Reddit users

0
[ad_1]

A Judge has thrown out a case where multiple movie producers sought to deanonymise Reddit users for posts they made in 2011.

An interesting case marking the limits of what data big business can expect to dig up has concluded its day (or to be more accurate, many days) in court. Ars Technica reports that film companies have lost their battle to make social site Reddit identify anonymous users discussing piracy. No fewer than 20 popular movie producers felt they needed this information in order to show that ISP Grande is liable for their subscriber’s copyright infringement.

Reddit was urging a US court to maintain the anonymity of six Reddit users who’d mentioned piracy all the way back in 2011 and 2018. Reddit argued that the First Amendment “protected their right to anonymous speech” in one of several similar cases which the movie industry had previously lost. From the relevant court filing:

Plaintiffs’ Motion seeks to unmask six anonymous Reddit users that Plaintiffs assume to have committed copyright infringement using Grande, an Internet service provider (ISP). If these Reddit users did engage in copyright infringement on Grande’s networks, then Plaintiffs hope to learn whether the users were drawn to Grande for the ease of infringement. Weeks ago, this Court denied a nearly identical motion by these same Plaintiffs… But rather than returning with better facts capable of meeting the applicable First Amendment standard, Plaintiffs here offer worse facts–expressly acknowledging that they have no need to identify these Reddit users at all.

As it happens, we’re now right back in our own movie industry Groundhog Day: Another case, another loss. The Reddit users here are stepping stones in a battle against an ISP called Grande. The movie producers are trying to prove liability for user piracy because the ISP “allegedly ignores piracy on its network”.

The justification for needing to know the identities of said reddit users comes from comments like the below:

In a 2018 Reddit thread titled “Texas ISP [Grande] slams music biz for trying to turn it into a ‘copyright cop,'” one user says, “I have Grande and torrent a lot. Always thought it was pretty cool of them to not snitch.” a user said, “[l]ike everyone else I miss Grande and I’m stuck with Spectrum or AT&T in my area. I use Spectrum. Those [expletive deleted] have turned my connection off completely on one occasion and would not turn it back on until I agreed to stop pirating media.”

According to Ars Technica, the most recent Reddit users were in the firing line for having their identities revealed for similar posts made in 2011. One individual posted that “I have Grande. No issues with torrent or bandwidth caps”. This was seemingly enough to gain the attention of the movie producers.

You’ll note that the post does not mention piracy, nor do they specify what they were doing. There are plenty of instances where Torrenting something (download files using the BitTorrent peer-to-peer protocol) is absolutely legal and above board. You may be downloading a large piece of software or a game broken up into chunks, for example.

Despite this, the film industry had another go anyway.

US Magistrate Judge Laurel Beeler observed that although users of Reddit and other sites do have their details turned over when appropriate, it would not be in this particular situation. 

The film companies claimed that user comments demonstrated Grande’s lack of policy implementation with regard to terminating the account(s) of offenders. They also went on to claim that they’d obtained 118 of Grande’s “top pirating IP addresses” in May but had little success communicating with said alleged pirates.

The Judge had this to say:

As with the last subpoena, the plaintiffs have not shown that the identifying information is directly or materially relevant or unavailable from another source. This is a high standard. The plaintiffs already have 118 subscribers’ identifying information: they primarily resist serving those subscribers with subpoenas as burdensome and inconsistent with their August expert-disclosure deadline. They are the top pirating IP addresses, and they are from a more recent time period: it is not obvious why subpoenaing even a subset of those addresses would not yield information at least equivalent to, if not better than, information from the six Reddit subscribers. The information may be relevant, but it also is attenuated: it is at best weak evidence about Grande’s insufficient policy regarding repeat infringers or its appeal to pirating subscribers.

Essentially: Dredging around the internet for the slightest available slice of data from a decade or more ago, in relation to specific data you have now which still isn’t really helping, is likely not going to help you very much either.

There’s no real way to know the specifics of what people in 2011 were talking about, or what they downloaded. The ISP may not even carry records for that far back. Maybe the Reddit accounts are abandoned, or perhaps some of the users have died. All in all, it seems like an incredible amount of work to put in for what would almost certainly be zero useful result.

This case is a valuable reminder that every single thing you post online, no matter how innocent (or otherwise) could end up rattling around a court of law many years down the line.


We don’t just report on threats—we remove them

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.


[ad_2]
Source link

Samsung extends partnership with uBreakiFix for device repair

0
[ad_1]

Samsung and uBreakiFix are extending their years-long partnership to create a more wide-reaching and accessible Galaxy device repair system. Since 2018 both companies have worked together to ensure customers have had the ability to get their phones fixed. Now that partnership is going further by making repairs more accessible than ever before.

Samsung announced the news today, laying out its goals for providing same-day repairs for broken phones. “When your device isn’t working, you want it fixed right and fixed fast. Partnering with uBreakiFix by Asurion to open these flagship locations means we can provide enhanced care for more Galaxy customers at an in-store level. Coupled with We Come to You service, we’re able to better serve our customers’ needs in even more communities where they live and work,” said Samsung Electronics America VP of Customer Care Mark Williams.

The expansion plan includes taking 50 uBreakiFix stores from around the country and turning them into flagship Samsung repair locations. The company says it aims to have this completed by the end of 2023. Five of these stores are already up and running and can be found in Dallas, Houston, San Antonio, Orlando, and Los Angeles.

uBreakiFix employees will receive Samsung training

(Image credit: Samsung)

The expanded partnership isn’t just about making existing stores flagship locations. There’s actually a lot more that goes into it. Repair technicians at uBreakiFix will receive training from Samsung on how to properly repair devices. They’ll also have access to specialized equipment and official parts and inventory.

This will “often” lead to devices being repaired within the same day they were brought in. But won’t necessarily happen every time. As things will be on a case-by-case basis. And will likely depend on the severity of the damage to a phone and the complexity of the repair. Other factors could come into play too. Such as how busy a store might be and how many other repairs are already on schedule.

Still, Samsung says this partnership will lead to more same-day repairs. Pre-partnership, 94% of walk-in repairs had a same-day completion. The partnership will only push that number higher. Leaving less customers waiting for a fixed device.


[ad_2]
Source link

The new Rokid Station is an Android TV for only your eyes

0
[ad_1]

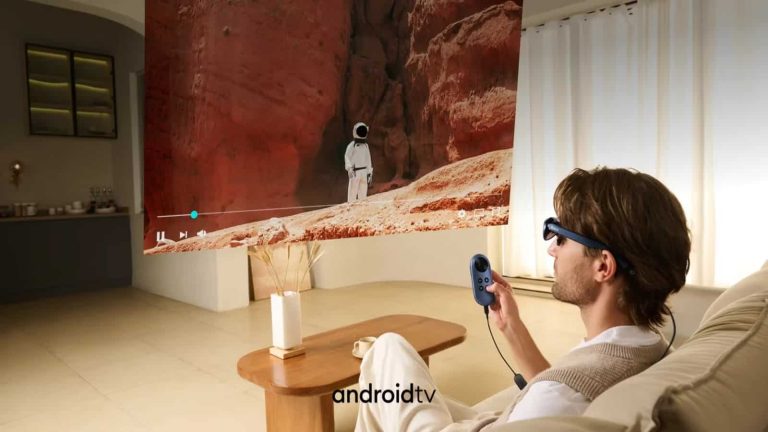
The new Rokid Station is here to personalize your Android TV viewing experience. This new product is a fine combination of an Android TV box and a pair of AR glasses. With these paired up, you’d no longer worry about watching content with others.

This device from Rokid just launched, and it has captured the attention of netizens around the world. From its design to its specifications and even its price, this device has got some to reconsider their stand regarding AR products. Rokid is making the AR industry a bit more practical for potential users with these new products.

Asides from being an Android TV, when used together, the Rokid Max can connect to other devices. This makes it possible for users to also experience AR apps and services in real-time. In this article, you’d find the full details on this new AR product.

The features and price of the new Rokid Station might just blow you away

This new product from Chinese startup Rokid comes in two parts, one being an Android TV and the other being a glass. The Rokid Station is an Android TV box and the Rokid Max is a pair of AR Glass. These two products connect to give users a personalized viewing experience.

Part of the Max’s specifications include a micro OLED screen that will project a 215-inch screen. This virtual screen will sit 10 feet away from the user’s eyes, and this brings an immersive experience. The AR glass also features a comfortable design that sits well on the user’s face.

As for the Rokid Station, this is an Android TV box that connects with the Rokid Max glasses. This Android TV box also doubles as a remote that users can control the interface. Rokid did a great job with the design of the Station device, making it easy to use.

These Rokid devices come with a 5000mAh battery that is said to last for five hours. The Rokid Max also comes with a 32GB storage capacity as well as an HDMI port. With this HDMI port, users can connect the Rokid Max with other AR Glasses.

For compatibility, the Rokid Max can be connected to other devices like gaming consoles for an AR experience. This new AR product, Rokid can as well connect to the internet for streaming. For its pricing, the Rokid Station and Max start at $529 on the brand’s official website.


[ad_2]
Source link