Supply chain attacks disrupt emergency services communications

0
[ad_1]

We take a look at a supply chain attack which disrupted two UK-based ambulance service’s ability to access customer records.

A supply chain attack rendered two ambulance trusts incapable of accessing electronic patient records in the UK. The two services, which operate in a region of 12 million people, were not targeted directly. Instead, the attack was aimed at a third-party technology provider used by both the South Central Ambulance Service (SCAS) and the South Western Ambulance Service (SWASFT).

According to reports, the systems were attacked sometime on the evening of July 18, impacting “customer systems within its hosted datacentre environment”.

The targeted organisation, Ortivus, has the following to say in a statement regarding the attack:

The electronic patient records are currently unavailable and are until further notice handled using manual systems. No patients have been directly affected. No other systems have been attacked and no customers outside of those in the hosted datacenter have been affected. 

Ortivus are currently working in close collaboration with the affected customers to restore the systems and recover data. The affected customers are the ones using MobiMed ePR, electronic patient record systems in a hosted environment. 

The organization behind the cyber-attack is not known at this stage and the incident has been reported to the authorities as a crime. 

The targeted platform is called MobiMed. This is a “modular platform that connects and enable(s) real-time information sharing throughout the prehospital care chain”. It is claimed to be used by “over 12,000 paramedics in over 2,700 emergency vehicles”.

To lose access to patient record data under these conditions is clearly far from ideal. The Register reports that healthcare workers are having to resort to pen and paper, alongside staff being warned of the potential for phishing attacks.

While there is a backup system able to take MobiMed’s place “within 24 hours” of an attack, integration with other systems is not 100%. Until a full analysis of the attack has taken place, the backup system will remain in place.

Regular readers of the blog will know of the chaos that accompanies attacks on healthcare providers. If crucial systems are compromised, people’s lives are put at risk. It’s something of a hot-button issue for ransomware authors, to the extent that some of them will apologise and offer up free decryption tools. They have calculated that it is simply not worth the press heat and possibility of angering law enforcement. Much better to blame an affiliate (whether an affiliate is responsible or not) and try to salvage some good PR from the situation.

Supply chain attacks are another large wrinkle on top of the original problem. Whether the attacker knows their target is used for medical work or something else altogether, it impacts organisations along the supply chain either way. Everything from healthcare to fuel suppliers are at risk when the supply chain attacks come to town.

Securing your supply chain

Here’s how you can protect your organization from risks your suppliers might pose:

  1. Know who your vendors are. Knowing this allows you to look for risks and vulnerabilities in the chain that threat actors might exploit.
  2. Use EDR or MDR. Invest in an effective endpoint detection and response (EDR) system, or managed detection response (MDR) if you don’t have the expert staff to monitor EDR 24/7.
  3. Segment your network. This limits attackers ability to move laterally, either stopping them or forcing them into actions your monitoring is more likely to pick up.
  4. Develop an incident response (IR) plan. If you don’t know what framework to build on, check out this incident handling guide from the National Institute of Standards and Technology. Include transparent and timely communication between your stakeholders and customers when something happens, so your business can provide steps to mitigate the problem if needed.
  5. Have a plan for patching. Patching in an organisation of any size is difficult: You need a systematic way to understand what hardware you have, what software it’s running, what patches that software needs, how important they are, and what the risks of deploying them are.
  6. Create and test offline backups. Speaking of backups, never assume they work, test them.
  7. Apply the principle of least privilege. Give suppliers the access they actually need and nothing more.
  8. Make multi-factor authentication (MFA) a norm. Supply chain attackers have been known to use stolen credentials to compromise systems. They know business systems trust credentials, regardless of who uses them.
  9. Train your employees. Gaps in security hygiene practices can open up opportunities for attackers. It’s important to keep employees and partners aware of the possible risks and red flags associated with supply chain attacks.

Malwarebytes EDR and MDR removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

Samsung Galaxy Z Flip 5 vs Motorola Razr+

0
[ad_1]

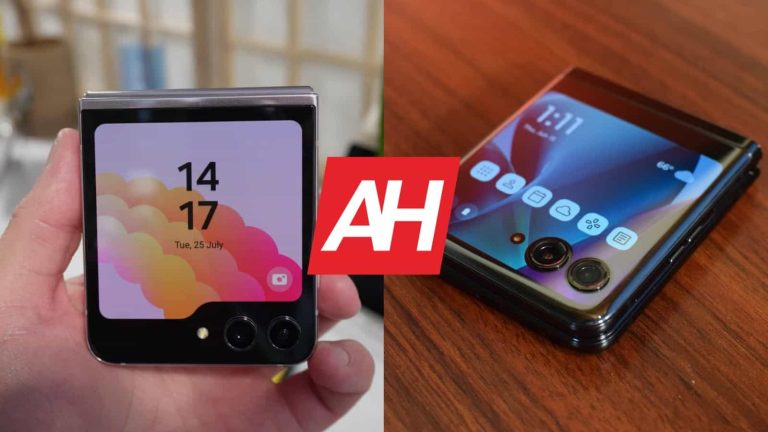
The Samsung Galaxy Z Flip 5 is the latest clamshell foldable smartphone on the market, at least at the time of writing this article. The phone got announced during Samsung’s second Unpacked event of 2023. Having said that, in this article, we’ll compare the Samsung Galaxy Z Flip 5 vs Motorola Razr+. These two smartphones are direct rivals in the market, as direct as it gets, actually. That goes for the US market too.

One thing to note is that the Motorola Razr+ name is used in the US, while in most other regions the phone is known as the Motorola Razr 40 Ultra. These two smartphones both have a large outer display, and have plenty to offer in general. We’ll first list out their specifications, and will then compare them across a number of different categories.

Specs

– Main display: 6.7-inch fullHD+ foldable Dynamic AMOLED (120Hz) / 6.9-inch fullHD+ LTPO AMOLED (165Hz)
– Cover display: 3.4-inch 720 x 748 Super AMOLED (60Hz) / 3.6-inch 1056 x 1066 AMOLED (144Hz)
– SoC: Snapdragon 8 Gen 2 for Galaxy / Snapdragon 8+ Gen 1
– RAM: 8GB (LPDDR5X) / 8GB/12GB (LPDDR5)
– Storage: 256GB/512GB (UFS 4.0) / 256GB/512GB (UFS 3.1)
– Rear cameras: 12MP (wide, OIS, PDAF, f/1.8 aperture, 1.8um pixel size), 12MP (ultrawide, 123-degree FoV) / 12MP (wide, f/1.5 aperture, 1.4um pixel size, OIS, PDAF), 13MP ultrawide (f/2.2 aperture, 108-degree FoV)
– Front cameras: 10MP (f/2.2 aperture, 1.22um pixel size) / 32MP (f/2.4 aperture, 0.7um pixel size)
– Battery: 3,700mAh (25W wired, 15W wireless, 4.5W reverse wireless), no charger / 3,800mAh (30W wired, 5W wireless), no in some markets
– Dimensions (unfolded): 165.1 x 71.9 x 6.9mm / 170.8 x 74 x 7mm
– Dimensions (folded): 85.1 x 71.9 x 15.1mm / 88.4 x 74 x 15.1mm
– Weight: 187 grams / 184.5/188.5 grams
– Connectivity: 5G, LTE, NFC, Wi-Fi, USB Type-C, Bluetooth 5.3
– Security: Side-facing fingerprint scanner
– OS: Android 13 with One UI / Android 13
– Price: $999 / $999
– Buy: Amazon / Amazon

Samsung Galaxy Z Flip 5 vs Motorola Razr+: Design

Both of these smartphones are made out of metal and glass, but they do feel different in the hand. The Motorola Razr+ has fewer flat sides, which is the main reason for a different in-hand feel. Both phones have a centered display camera hole on the inside, and they fold right down the middle. They also both have very thin bezels on the main display. When they’re open, and you look at them from the front, they’re extremely similar.

Now, the differences can be seen on the back, easily. They both do have two cameras on the back, which are horizontally aligned in the top-left corner. What’s different is their cover displays. They’re both quite large, but the Galaxy Z Flip 5’s has a folder-like shape, while the Motorola Razr+’s goes around the cameras, and has a rather normal shape for a display. It takes more room than the Galaxy Z Flip 5’s panel.

The Motorola Razr+ is a bit taller and wider than the Galaxy Z Flip 5, while they’re about the same in terms of thickness. That goes for both the folded and unfolded states. It is worth noting that the Motorola Razr+ has a larger main display too, which is the main reason for the size difference between them. The Galaxy Z Flip 5 is IPX8 rated for water resistance, while the Motorola Razr+ has water-repellent coating.

Samsung Galaxy Z Flip 5 vs Motorola Razr+: Display

The Galaxy Z Flip 5 features a 6.7-inch fullHD+ (2640 x 1080) Foldable Dynamic AMOLED 2X display. That panel has a 120Hz refresh rate, and HDR10+ support too. It goes up to 1,200 nits of brightness at its peak. A 3.4-inch cover display is also included. It’s a Super AMOLED panel with a 720 x 748 resolution, and that panel is protected by the Gorilla Glass Victus 2.

Samsung Galaxy Z Flip 5 AH 9
Galaxy Z Flip 5

The Motorola Razr+, on the other hand, includes a 6.9-inch fullHD+ 2640 x 1080 Foldable LTPO AMOLED display. That panel can project up to 1 billion colors, and it’s a 165Hz unit. HDR10+ content is supported on this panel, and the display goes up to 1,400 nits of peak brightness. The cover display on Motorola’s device measures 3.6 inches, and it offers a 1056 x 1066 resolution. Gorilla Glass Victus protects this display.

Both smartphones are well-equipped in the display category. Truth be said, they both do the job phenomenally. Neither display feels too plasticky or anything (in terms of foldable panels), and they’re all bright enough. Of course, don’t expect the same brightness as the most powerful (regular) smartphones out there offer, but it’ll be enough for most people. Touch response is also good, as are the viewing angles. The Motorola Razr+ allows you to run any app on the cover display, while the Galaxy Z Flip 5 will do the same soon, as soon as the Good Lock update arrives. You’ll need to enable that manually, though. The Motorola Razr+’s cover display does offer a considerably higher resolution, and refresh rate, though.

Samsung Galaxy Z Flip 5 vs Motorola Razr+: Performance

The Snapdragon 8 Gen 2 for Galaxy fuels the Galaxy Z Flip 5. In addition to that, Samsung included 8GB of LPDDR5X RAM and UFS 4.0 flash storage too. The Motorola Razr+, on the flip side, has a Snapdragon 8+ Gen 1 SoC on the inside. That chip is inferior to the Snapdragon 8 Gen 2, but it’s extremely powerful nonetheless. Motorola offers 8GB or 12GB of LPDDR5 RAM here, along with UFS 3.1 flash storage.

So, as you can see, the Galaxy Z Flip 5 does have more powerful internals. Does that mean it has a huge advantage in the performance department? Well, no, not really. Both phones perform admirably. They’re very smooth in day-to-day performance, and can even handle the most demanding games out there The Galaxy Z Flip 5 does usually open apps slightly faster, but that’s not something you’ll notice unless you run them side by side. The Galaxy Z Flip 5 is more future-proof, in a way, thanks to the specs, but they both run beautifully at the moment.

Samsung Galaxy Z Flip 5 vs Motorola Razr+: Battery

Samsung’s latest clamshell foldable includes a 3,700mAh battery. The Motorola Razr+, on the other hand, has a 3,800mAh battery on the inside. The Motorola Razr+ actually offers really good battery life, at least it did during our testing. We were able to pull out 7.5-8 hours of screen-on-time from the device. Based on the specs alone, the Galaxy Z Flip 5 should be able to offer something similar.

We’re still testing the device, though, our verdict is not ready yet. From what we’re seeing, however, it still flies a bit under the levels of the Motorola Razr+. The battery life the phone provides is better than what the Galaxy Z Flip 4 had to offer. That may change, however, as we’re still in the early days of Galaxy Z Flip 5 usage. Our full review will reveal far more information, stay tuned for that.

When it comes to charging, the Galaxy Z Flip 5 offers 25W wired, 15W wireless, and 4.5W reverse wireless charging. The Motorola Razr+ supports 30W wired, and 5W wireless charging, no reverse (wireless) charging. Do note that the Galaxy Z Flip 5 does not include a charger in the box, while the Motorola Razr+ does, but only in some markets. That’s not the case in the US, however.

Samsung Galaxy Z Flip 5 vs Motorola Razr+: Cameras

Both smartphones include two cameras on the back, and one on the main display. You can, of course, use their rear-facing cameras as the only cameras, as you can use them in collaboration with cover displays on both phones. The Galaxy Z Flip 5 includes a 12-megapixel main camera, and a 12-megapixel ultrawide unit (123-degree FoV). The Motorola Razr+ features a 12-megapixel main camera, and a 13-megapixel ultrawide unit (108-degree FoV).

Motorola Razr plus 2023 review AM AH10

When it comes to image quality, both smartphones are quite good. The Galaxy Z Flip does have a tendency to crank up the saturation, while the Motorola Razr+ images can look a bit muted sometimes. Neither phone is aiming for true-to-life portrayal, but both do a good job. In most situations, we end up preferring the Galaxy Z Flip 5 shots in daylight, and Motorola Razr+ shots in low light. Do note that we’ve recently started using the Galaxy Z Flip 5, though, so we’re not making our final impressions yet.

When it comes to ultrawide cameras, they do their best to follow the main shooters, but are a level below them. The Galaxy Z Flip 5 does offer a noticeably wider FoV, and we didn’t really use the Motorola Razr+’s ultrawide camera due to its (108-degree) field-of-view.

Audio

What about audio? Well, first and foremost, do note that there is no audio jack on either of these two phones. They do offer a set of stereo speakers, however. The Motorola Razr+ speakers do seem to be a bit louder, but both sets are very good in terms of quality.

If you’d like to hook up your wired headphones to either phone, you’ll have to use their Type-C ports. Wireless connections are an option too, of course. Both of these smartphones offer Bluetooth 5.3 for such purposes.


[ad_2]
Source link

AI made it easier for hackers to write malware, FBI says

0
[ad_1]

The Federal Bureau of Investigation (FBI) says hackers use AI to write malware. The agency declared AI tools have made it much easier for bad actors to write and spread malicious programs or phishing emails.

Every useful tool can become a dangerous weapon if it falls into the hands of the wrong people, including AI. Artificial intelligence can be used in various fields and for different purposes like healthcare or enhancing productivity. However, the FBI is now complaining about free, customizable open-source AI models that are writing malicious codes for hackers.

Hackers usually need a high level of programming knowledge to write strong, hard-to-detect malware. On the other hand, the currently available AI tools allow almost everyone to build a program (or malware) without having any programming knowledge. The generative AI placed at the heart of these tools can write or debug the codes like an experienced programmer.

FBI says AI is writing malware for hackers

The agency’s warning comes as cybercrime continues to rise and hackers become increasingly sophisticated in their methods. The malware created by AI is usually hard to detect and more difficult to delete once it has infected a system. AI also makes it easier for hackers to launch attacks on a larger scale, targeting multiple systems simultaneously.

Deepfakes are another tool that fraudsters use to their advantage. Deepfakes are movies or photos that have been artificially enhanced to make them look realistic. They can be used to mimic other people online or spread misleading information like propaganda or fake news. This way, a victim might be persuaded into performing specific actions, like making a payment or sending private information.

As AI is rapidly growing, many governments are still struggling with designing and implementing protective measures against potential harm. The White House has recently called for a “voluntary commitment” program to mitigate AI risks with the help of major tech companies like Google, Amazon, Meta, etc.


[ad_2]
Source link

Meta subsidiaries must pay $14m over misleading data collection disclosure

0
[ad_1]

We take a look at reports that Meta subsidiaries have been ordered to pay a sizeable fine relating to disclosure issues for a now discontinued VPN.

Meta has run into yet another bout of court related issues—two subsidiaries have been ordered to pay $14 million regarding undisclosed data collection. The Australian case, which has rumbled on for the best part of two and a half years, has focused on claims related to a now discontinued Virtual Private Network (VPN).

The subsidiary Onavo, acquired in 2013 by Facebook, was supposed to be keeping the VPN a separate brand from the main flagship company. Among various privacy based claims were “peace of mind when you browse” and “keep you and your data safe online”. It was certainly popular, with more than 270,000 downloads in Australia.

One of the app’s major selling points was that users were told their data would not be used for any purposes other than “the provision of Onavo Protect’s products”.

However the app, functional from 2016 to 2017, was found to be sending data to Facebook. This included user location, frequency using other apps, time, and also unrelated websites visited for the purposes of advertising. Here’s a rundown of some of the things the app was tracking, from the original research in 2018:

  • When a mobile is turned on and off
  • Daily Wi-Fi data usage (even when the app is off)
  • Daily cellular data usage (even when the app is off)
  • Amount of time the VPN connection is used

This was not what app users had signed up for, and so things quickly turned legal as a result. From the judgement:

Facebook Israel and Onavo admit that they offered, advertised and promoted Onavo Protect and made the app available to download by users in Australia via the App Store (for iOS users) and the Play Store (for Android users) during the Available Period.

Meta and Facebook Israel’s internal documents state that Onavo Protect was “a business intelligence tool” for Meta, which provided Meta with “a sample of users who we are able to know nearly everything they are doing on their mobile device” (which was in the form of anonymised, aggregated data). Meta then used anonymised and aggregated data derived from sets of the Onavo Protect Data (in the form of statistical information) for a range of purposes, including in relation to its advertising and marketing activities, improving its products and services and developing commercial strategies.

Disclosures related to how consumer data would be used for purposes other than providing Onavo Protect were listed in the Terms of Service and Privacy Policy, in the form of website links promoting the product. Additionally, users were taken to a page containing said documents when using Onavo Protect for the first time after installation. However, the disclosures in question were not “sufficiently prominent or proximate to the listings”.

Back to the judgement, where there is every sense that those responsible have dodged a potentially much larger fine:

Facebook Israel and Onavo admit that, given the above facts, the Listings that contained the Statements were likely to mislead or deceive (within the meaning of s 18 of the ACL), and liable to mislead the public (within the meaning of s 33 of the ACL), in the absence of sufficient disclosures to Australian consumers (which they admit were not made in those Listings) of the fact that Australian users’ data would be used for purposes other than providing Onavo Protect.

Where the theoretical maximum penalty is in the billions or trillions of dollars, the overall maximum penalty will not be a meaningful factor in the court’s assessment. In these circumstances, the appropriate range is best assessed by reference to factors other than where the conduct falls in the range of seriousness of offending in relation to the maximum penalty.

Last year, Instagram received a record fine of $400m for the abuse of children’s data. Elsewhere, Meta was fined $277m for a data breach which impacted around 500 million users. Some believe that social networks simply consider fines like these to be the cost of doing business. A few million dollars here or there doesn’t necessarily convince those responsible to do anything about it.

Even so, the fines keep coming. It remains to be seen if the long-term impact will eventually amount to anything meaningful.


Malwarebytes EDR and MDR removes all remnants of ransomware and prevents you from getting reinfected. Want to learn more about how we can help protect your business? Get a free trial below.

TRY NOW


[ad_2]
Source link

The PS5 now supports Dolby Atmos thanks to the latest beta

0
[ad_1]

The PS5 is getting the latest beta software update today and it’s introducing quite a few new features, including Dolby Atmos support. This is one of the core new features, but it’s hardly the only noteworthy addition.

Sony is loading up a raft of new accessibility and UI features too. And for those with some money to spare, support for an 8TB M.2 NVMe SSD should they want to upgrade. This update won’t be available for most users for a while longer but if you’re enrolled in the beta, you might see these new features after installing the software.

Provided Sony has selected you to participate. The beta is also only available in a few different regions. This includes the US, Canada, Japan, Germany, UK, and France. All of which were available to participate in the last beta, Sony says. All of these new features definitely make the PS5 more capable than ever and enhance the overall experience. The upgraded storage capacity support in particular will be great for people who never want to worry about having enough space for games again.

An 8TB M.2 NVMe SSD will have to meet the console’s requirements though. And there aren’t many out there. Not to mention an 8TB NVMe SSD won’t be cheap. One of the SSDs we’ve recommended for example is the Sabrent Rocket 4 Plus. It’s available in an 8TB model and it does meet the PS5 requirements. But it’s also $999.99. And that’s without the $17 heatsink.

PS5 beta participants can use Dolby Atmos audio gear

PS5 Beta Dolby Atmos (1)

The biggest feature addition is without a doubt the Dolby Atmos support. And with it, the PS5’s Tempest 3D Audio Tech will be compatible with Dolby Atmos devices. Such as sound bars, headphones, home theater systems, and TVs.

Sony says this will allow for even greater levels of immersion within games.

Search for games in your library and more

PS5 Beta Dolby Atmos (2)

One of the many new features is the ability to search for games within your library. This is a simple change but a very useful one if you have a lot of games. There’s also a few new social features like the ability to add people to a closed party without adding them to the group.

Additionally, it’ll be much easier to join friends who are playing a game where you’re able to join. You can do this from the friends tab, and friends whose activities can be joined will be listed. You can view all the details of the beta update in the official blog post.


[ad_2]
Source link

Dish bring its unlimited postpaid plan to Amazon

0
[ad_1]

If you use the Dish Boost Infinite unlimited wireless service, you will be able to purchase plans from Amazon. Dish officially announced this improvement a few days ago, giving users a new way to purchase this exclusive deal. Over the past few months, experts have made speculations about the availability of this plan on Amazon for purchase.

Finally, these speculations have become reality and users will soon start running to Amazon to purchase this wireless service offer. Well, the fact that the Infinite wireless service offer is available on Amazon is not the only thing that’ll attract buyers. The luring part of this offer is the discount that some shoppers will get when they make their purchases on Amazon.

Also, this method of purchase is very easy for buyers as they won’t need to step foot into any physical store. Certainly, this offer will attract a ton of shoppers on Amazon to try out Dish’s wireless service. In this article, you’d find all the details you need regarding the arrival of the Infinite wireless service on Amazon.

Prime members to benefit from the Boost Infinite unlimited wireless service arrival on the online shopping platform

Dish, the owners of Boost, have a new offering for their customers in the US. Amazon Prime subscribers will benefit more from this new arrangement. These individuals will be able to purchase the wireless service plan at a discounted rate.

The telecom company will offer its new unlimited plan for purchase via the online retail company. Boost will retail the plan at $25, which is just one of the data plans that the company offers. This plan gives users 35GB worth of data for a 5G or LTE connection for an entire month.

It also brings unlimited text and talk time to the user for the month the subscription lasts. Finally, those hoping to switch to the Dish Boost network will be able to purchase the unlimited plan from Amazon at the regular price of $25 per month. However, those who have a Prime subscription will get the Dish Boost Infinite unlimited wireless service at a 20% discount.

Now, customers can purchase a new Boost Infinite SIM and activate the unlimited plan directly from their homes. Jeremy McCarty, the head of Boost Infinite, says that Amazon is the best place to offer this deal. Partnering with Amazon will give the company access to more customers that actively shop on the platform.

The SIM card is already available for purchase on Amazon, and anyone can grab one for themselves today. Boost claims that their monthly price for the Infinite wireless service will stay the same for life. Would you consider purchasing this SIM and wireless coverage plan from Amazon?


[ad_2]
Source link

Don’t sleep on these Galaxy Z Flip 5 upgrades

0
[ad_1]

A bigger cover display and redesigned hinge may be the highlights of the Galaxy Z Flip 5, but the new Samsung clamshell foldable also brings plenty of other minor upgrades. It features the brightest cover screen on any Galaxy foldable yet. The device also supports video output via USB and boasts Wi-Fi 6E. It misses out on Samsung DeX support, though.

The Galaxy Z Flip 5 features a folder-shaped 3.4-inch Super AMOLED panel on the outside. The 720 x 748 pixels screen has a 60Hz refresh rate and a 306 PPI pixel density, with Gorilla Glass Victus 2 protection on top. Called Flex Window by Samsung, the cover display lets you use various apps through widgets and can also be your viewfinder for taking selfies with the rear cameras. And you can do all of this in bright outdoor environments with ease.

This is thanks to the peak brightness of 1,600 nits (via SamMobile). At this brightness level, the Galaxy Z Flip 5’s cover display is brighter than its main foldable display (1,200 nits) and almost as bright as the Galaxy Z Fold 5 and Galaxy S23 Ultra’s main displays (1,750 nits). It’s the brightest cover display Samsung has used on any of its foldable phones yet, across both Fold and Flip lineups.

Note that the Galaxy Z Flip 5 uses an under-display photo resistor sensor to control the adaptive brightness of the cover display. It’s located near the hinge, perpendicular to the two rear cameras. If you accidentally cover this sensor with your fingers or something else, the sensor may detect a pitch-black external environment and lower the brightness level. Just reposition your fingers and the brightness level should go up again.

Galaxy Z Flip 5 supports video output via USB but no Samsung DeX

Samsung has upgraded the Galaxy Z Flip 5 to Wi-Fi 6e, making it the first model to support the faster and more reliable Wi-Fi standard. The new Flip also boasts a USB-C 3.2 port, another upgrade from a USB-C 2.0 port on the Flip 4. This brings video output support, allowing you to mirror the content of its screen to an external monitor via a USB cable.

However, despite this improvement, the Galaxy Z Flip 5 misses out on Samsung DeX support. The Korean firm told SamMobile that it tried adding the feature, which lets you use the phone in a PC setup, but canceled the plans due to heating issues. The foldable doesn’t have a sufficient “heatproof performance in the structure,” to efficiently run Samsung DeX. This is a shame but it is what it is. If the lack of Samsung DeX isn’t a dealbreaker for you, the Galaxy Z Flip 5 is currently available for pre-order. Samsung will open general sales on August 11.


[ad_2]
Source link

Recent iOS 17 update unintentionally reveals Apple’s Action Button

0
[ad_1]

According to some reports, the Apple Action Button will launch with future iPhones Pro models. These reports claim that the iPhone 15 Pro series will replace the mute slider with a button. However, some experts and insiders say that Apple will not make this switch with the coming iPhone 15 Pro series.

While the brand may or may not be bringing this change to their coming smartphone, they are nurturing the plan. So on future iPhones, fans might get to see the exit of the mute slider, which will be a remarkable change. This slider will get replaced by what Apple calls an Action Button, which will be touch-sensitive and will be more functional than the mute slider.

Apple fans around the world should get themselves ready for this remarkable change. Reliable sources have found lines of code in the iOS 17 beta update that gives away the function of this mute slider replacement. The use of this coming button will certainly change the way iPhone fans interact with their device.

Possible uses of the Apple Action Button as shown off by the iOS 17 update

While iOS 17 is still in the beta testing phase, it is already showing some features that are yet to launch. Sources claim that the update has shown off the possible uses of the Apple Action Button, which isn’t yet a real thing. This update proves that Apple is preparing to launch a device that will help phase out the mute slider and usher in a new era.

From the update, experts were able to dig up some functions of this new button, and it promises to be very functional. A total of nine abilities have been linked to this button and, yes, it will still perform the function of the mute slider. Aside from muting the device, this Action Button will perform eight other impressive actions.

These include accessibility, shortcuts, camera, flashlight, focus, magnifier, translation, and voice memo. All of these are impressive quick-access features that Apple will be giving users at the press of a button. Of course, users will also get to pick which control they want the Action Button to activate, depending on their needs and preferences.

While some sources claim that the Action Button will not launch with the iPhone 15 Pro series, it’s pretty confusing why its controls are available on the iOS 17 beta upgrade. In the recent Power On newsletter, Mark Gurman also makes mention of the possible presence of the Action Button. At this point, fans and netizens around the world can keep their fingers crossed while in expectation of the launch of this feature.


[ad_2]
Source link

Apple bends its rule to allow Musk’s rebranded Twitter app “X” to be listed in the App Store

0
[ad_1]
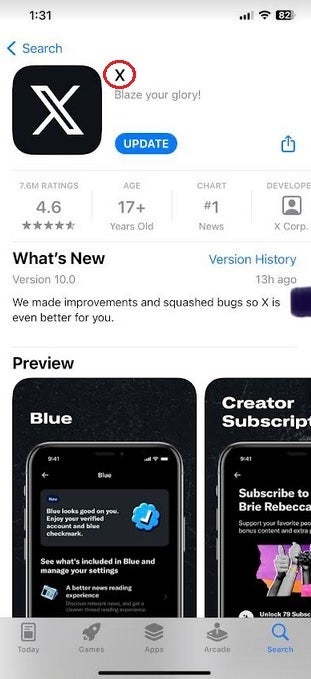
The other day we told you that Apple had not allowed Twitter to rebrand as “X” in the App Store since it had a rule preventing app developers from naming their apps as a single character. We also pointed out that Google didn’t have such a rule and did allow “X” to mark the spot of the social media platform’s Android app. But if you look at your iPhone’s home screen this morning, you’re likely to note that the “X” app icon doesn’t say Twitter underneath it anymore and says “X” which means Apple has officially approved the new name.
Likewise, if you go to the App Store and search for “X,” you’ll see no mention at all of the Twitter name as all reference to the old moniker has been replaced by the 24th letter of the alphabet. Just the other day, the listing in the App Store showed the new “X” icon but called the app “Twitter.” We wonder whether Musk will end up selling the Twitter name since there still might be some value to it, and it might bring in some much-needed cash to the company.

As we’ve noted before, Elon wants to make “X” a super-app like China’s WeChat which is used for instant messaging, mobile payments, and for social media posts. Also, Elon has had an obsession with the letter “X.” He named his first company X.com and it was later sold to PayPal. Walter Isaacson, who wrote the biography “Jobs” and is writing one about Musk, made a comment that helps us understand why Elon is naming his WeChat competitor “X.”

The author said, “His concept for X.com was grand. It would be a one-stop everything-store for all financial needs: banking, digital purchases, checking, credit cards, investments, and loans. Transactions would be handled instantly, with no waiting for payments to clear. His insight was that money is simply an entry into a database, and he wanted to devise a way that all transactions were securely recorded in real-time.”

Eventually, Musk bought the name back from PayPal and we should see a huge transformation in the platform formerly known as Twitter. It would be funny, if after all of the complaints and insults launched at Musk over his running of Twitter, he had the last laugh after all. Getting Apple to greenlight the “X” name in the App Store is just the first step.


[ad_2]
Source link

New Android Malware Uses Optical Character Recognition

0
[ad_1]

A new Android malware strain uses OCR (Optical Character Recognition) techniques to extract sensitive data from pictures.

This new Android malware strain is dubbed “CherryBlos,” and along with this malware strain, another malware was also discovered that is dubbed “FakeTrade.”

Cybersecurity researchers at Trend Micro discovered the new malware strains with shared network infrastructure and certificates, hinting at the involvement of identical threat actors.

Apart from this, these malicious apps employ multiple channels for distribution, and here below we have mentioned them:-

Android Malware Use OCR

In April 2023, CherryBlos malware emerged as an APK file that was found to be promoted on Telegram, Twitter, and YouTube as:-

All the malicious APK files were downloaded from domain-matching websites. Here below, we have mentioned the malicious APK file names and matching domains:-

APK files:

  • GPTalk
  • Happy Miner
  • Robot999
  • SynthNet

Matching domain names:

  • chatgptc[.]io
  • happyminer[.]com
  • robot999[.]net
  • synthnet[.]ai

Moreover, the SynthNet app, a malicious version, was downloaded around 1,000 times on Google Play before being reported and removed.

Synthnet App (Source – Trend Micro)

CherryBlos malware targets crypto wallet credentials and alters withdrawal addresses since it’s mainly designed to steal cryptocurrency wallet-related information.

The CherryBlos exploits accessibility service permissions to:-

  • Fetch config files
  • Auto-approve permissions
  • Block app termination

Besides stealing cryptocurrency-related data, CherryBlos also has an extraordinary feature that enables OCR for text extraction from images on the device.

Code to perform OCR on images (Source – Trend Micro)

When EnableImage is true in the config, CherryBlos reads media files, applying OCR for potential mnemonic recognition.

Despite the risk, people save recovery phrase photos on devices, enable malware extracts, and send data to threat actors.

Moreover, the malware also hijacks the Binance app clipboard, then alters the recipient address with the attacker’s, as this enables attackers to initiate illicit fund transfers stealthily.

Recommendations

Here below, we have mentioned all the recommendations offered by the security researchers at Trend Micro:-

  • Always download apps from the Google Play store and official app stores that are trusted. 
  • Make sure to keep your system, software, and AV tools updated with the available security patches and updates.
  • To block threats like these and other malware strains, make sure to install a robust and renowned AV solution.
  • Before allowing any permissions to apps, make sure to cross-check each permissions carefully.
  • Do not download any unknown attachments received via email.
  • Suspicious links could be dangerous, so, do not click on any suspicious links.

Keep yourself informed about the latest Cyber Security News by following us on GoogleNews, Linkedin, Twitter, and Facebook.


[ad_2]
Source link