Twitter has problems that X can’t solve

0
[ad_1]

Well, he did it. While, deep down, we knew he was crazy enough to do it, we didn’t think he’d actually do it. Elon changed Twitter to X, and we’re all suffering a bit of whiplash. But, for as bold and meme-worthy as this change is, changing Twitter to X won’t fix the platform’s problems.

Right now, Twitter seems to be imploding. Sure, the platform had its critics before Elon took over; all social media sites do. But, when Elon took the helm, our favorite blue bird started taking a nosedive. A slew, rather, a torrent, of questionable changes brought by the billionaire gradually made Twitter a worse place to be.

At this point, we don’t know how long Twitter can limp along like this. While the company’s been gutted to force profitability, it’s undoubtedly lost a ton of money. In fact, it’s valued at about a third of the $44 billion that Elon bought it for (about $15 billion). That number is only going to get lower as more people flock from Twitter to its alternatives.

With all this happening, what is an eccentric CEO to do? Change the name…

Twitter has problems that X can’t solve

When we got the news that Twitter was being named to X, there was a bit of information that we didn’t get. We got no word on what Elon and Twitter are planning on doing to make the platform better. There were no tweets or announcements about how X will be different from Twitter. Something like that would be much better than just switching over.

cuva
_cuva

What we’re getting, instead, is Elon reacting to everyone’s growing contempt for the platform. We get heated tweets about Elon challenging Mark Zuckerberg to cage matches and calling him a cuck rather than actual information.

But there are problems going on with Twitter, and changing the name to X won’t fix them.

Let’s start with the selfish and narrow-sighted changes

Before Elon Musk, changes that Twitter brought, for better or worse, reflected what a group of people thought was good for users. They weren’t all universally loved; you can’t please everyone. But, that’s how most companies are. Changes are distributed after going through multiple brains, and they reflect the company’s views.

However, that’s not what we’re seeing with Elon Musk. The changes that he’s making don’t reflect the company, they don’t reflect what is best for the user; they reflect what’s best for Elon.

He bought Twitter on the platform of free speech, and that’s in his best interest. Links from other platforms like Mastodon and Threads were either blocked or deprioritized on Twitter. He’s battling data scraping, and that led to the rate limit. He thought about getting rid of light mode because dark mode is better in his opinion. The list goes on.

We’re constantly seeing half-baked changes being sent out into the company that only reflect what he feels should be done. It’s like he’s sitting at a computer, coding these changes, and pushing them out himself. They’re half-baked, and they don’t take into account how they affect the average user.

Twitter logo red overlay image 101

Sure, data scraping is a thing, but limiting the number of tweets that people can view has a more negative user-facing effect than the supposed slowdown. Many people view tweets while not logged in. Requiring people to be logged in inconvenienced people more than it helped them. These changes have larger negative user-facing effects than positive.

The overly aggressive push for Twitter Blue

We get it, Elon is trying to make Twitter profitable. Twitter Blue is a direct source of revenue for the company along with advertisements. However, one thing that’s killing Twitter is his overly aggressive focus on Blue. Immediately after he took over, the price jumped to $8/month ($11/month if you sign up through the app).

Since then, it seems that all new and useful features have been reserved for Blue users. Boost in the algorithm, fewer ads, longer tweets, undoing and editing tweets, text formatting, etc. Free users are sitting by and watching all of these features fly over their heads.

Yes, it’s an exclusive service, and all exclusive services need to have, well, exclusive features. Snapchat+ has some of them as well as Meta verified. However, unlike Twitter, those other services still distribute features to their free users. Free users still feel like they’re using a full social media platform, not the Lite version.

It wasn’t supposed to be like this…

Twitter Blue was originally a service where you’d pay a bit a month and get to test out new features early. They’d make their way to the public after a bit. Well, it looks like Elon just threw that out of the window. Free users are still not able to edit their tweets even when he said that it would trickle down over a year ago. Blue users can type tweets up to 20,000 characters long while free users are still stuck on 280 characters.

cuva
_cuva

Elon is putting so much effort to get the Blue revenue that it doesn’t feel like he’s trying to appeal to Twitter users in general. He’s just trying to make Twitter Blue more appealing so that people will pay.

The diminished staff

Twitter is operating with a skeleton crew now. When Elon took over the company, he wiped out half of its staff in one fell swoop. Entire teams were killed off. Obviously, with such a reduced staff, it’s a lot harder for the company to operate.

Also, Elon fired top executives when he took control. This means that there aren’t any checks or balances to steer him from making awful decisions with the company.

Elon’s playful attitude toward the situation

Elon is piloting a plane in a wild tailspin, and he knows it. Yet, he’s treating it like a joke. It’s okay to make jokes every now and then, and it’s okay to take criticism in stride. But, Elon is striving to be a living breathing meme at this point.

It feels like he’s not taking the situation seriously. Remember, this is the man who walked into the Twitter HQ holding a kitchen sink. This is the man who tweeted “Zuck is a cuck” when Threads launched. Just recently, he posted an AI-generated video of him singing Rick Astley’s “Never Gonna Give You Up”. This attitude leads the internet to treat Elon and Twitter itself as a joke.

There’s still a chance for a turnaround

So, it’s obvious that Elon is not the man to push Twitter to new heights, but he won’t be responsible for the company going forward. He appointed Linda Yaccarino, the former head of advertising at NBCUniversal as the new CEO of the company.

Elon and Linda
Image from The Guardian

Linda is a fresh face and, hopefully, has some fresh ideas to turn Twitter around. Could she be the one to turn the company in the right direction? Right now, there’s a lot in the air, and we don’t know if Elon will have some sort of influence in her decision-making. Yaccarino might be the CEO, but Elon is still the owner. We’ll have to wait and see if they can fix the problems affecting Twitter or X.


[ad_2]
Source link
Major iPhone 15 Pro design improvements detailed

0
[ad_1]

We’ve seen a ton of rumors regarding the iPhone 15 Pro thus far. Well, the latest one comes from one of the best-known Apple analysts, Mark Gurman. He basically detailed major iPhone 15 Pro design improvements for Bloomberg.

Major iPhone 15 Pro design improvements get detailed by Mark Gurman

First and foremost, the iPhone 15 Pro and Pro Max will both see the changes mentioned here. Both phones will include a titanium frame, which is a first for Apple. On top of that, thinner bezels will be a part of the offering too.

We’ve heard both of those rumors before, several times, but Mark Gurman gives them even more credibility… and info too. He did mention some of these changes in the past, though, as a side note. Apple will use a new production tech called ‘low-injection pressure over-molding’, or in short, LIPO.

The bezels will be trimmed down considerably

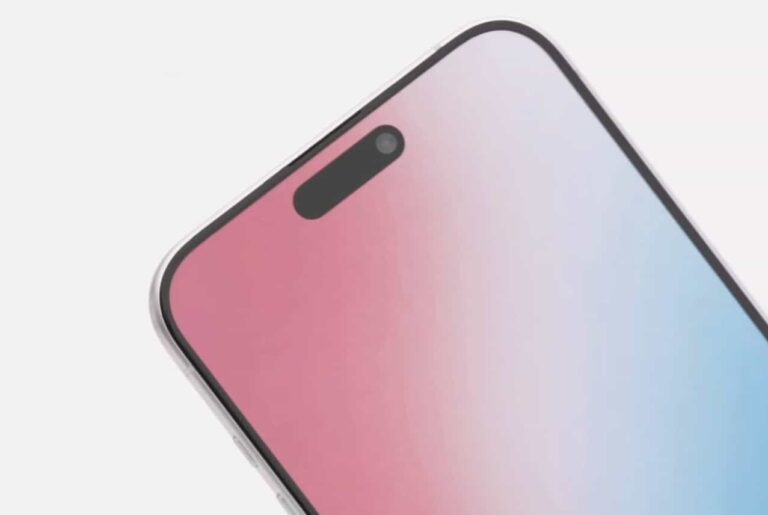
That tech will make it possible for Apple to trim down the bezels, it seems. The bezels on both phones are expected to be trimmed down to 1.5mm. They’re currently sitting at 2.2mm, and they’re quite thin. So, you can only imagine the change.

iPhone 15 Pro mockup Ice Universe
Third-party mockup (Ice Universe)

Apple also used LIPO on the Apple Watch Series 7, in case you’re wondering. It’s also worth noting that all the bezels on the iPhone 15 Pro and Pro Max will be uniform, as expected. They will also be uniform on the iPhone 15 and 15 Plus, but not as thin.

The switch to a titanium frame was also expected. That should make both phones a bit lighter, actually, if Apple doesn’t counterbalance the change with battery capacity or something of the sort. Titanium is both stronger and lighter than stainless steel, which Apple used in the iPhone 14 Pro and Pro Max.

The edges of the iPhone 15 Pro series will be less sharp than before

Now, Gurman also mentioned that the edges of the iPhone 15 Pro and 15 Pro will be less sharp than the edges on their predecessors. We’re talking about the edges connecting the side and the front of the devices. That means that the iPhone 15 Pro and Pro Max won’t dig into your palm as much.

On top of all that, all iPhones will include a Type-C port, which is something Gurman felt the need to reiterate. The new iPhones are expected to land in September, though the launch could be delayed to October.


[ad_2]
Source link

U.S. Senator Blasts Microsoft for Chinese Hack

0
[ad_1]

A joint alert from the FBI and CISA concerning a hacking campaign that targeted Microsoft customers, including government entities, was released on July 12.

In a letter to the directors of the Department of Justice, Federal Trade Commission (FTC), and Cybersecurity and Infrastructure Security Agency (CISA), U.S. Senator Ron Wyden stated that Microsoft “bears significant responsibility for this new incident.”

Microsoft is held accountable for its poor cybersecurity procedures, which let China carry out a successful espionage campaign against the US government, reads the letter sent by Senator.

An Overview of the Chinese Hack

Press sources claim that “at least hundreds of thousands of individual U.S. government emails” were taken, and that the email accounts of the secretary of commerce, the ambassador of the United States to China, and the assistant secretary of state for East Asia were among those that were affected.

According to Microsoft, the breach happened as a result of hackers obtaining an encryption key that the company had created for its identification service, Microsoft Account (MSA).

Microsoft made another mistake, which led to the theft of government emails. Although the encryption key was for consumer accounts, “a validation error in Microsoft code” allowed the hackers to access accounts for government agencies and other organizations that were hosted by Microsoft by making fake tokens for such accounts.

Wyden’s List OfMicrosoft’sCybersecurity Flaws

First, according to Wyden’s letter, Microsoft shouldn’t have had a single skeleton key that, in the event of theft, might be used to get access to various customers’ private conversations.

Secondly, he said, high-value encryption keys should be kept in an HSM, whose main purpose is to prevent encryption key theft, as Microsoft noted in a recent SolarWinds incident.

Third, the encryption key that was utilized in this most recent attack was made by Microsoft in 2016 and it expired in 2021.

As a final point, although Microsoft’s engineers shouldn’t have released systems that broke such fundamental cybersecurity rules, Microsoft’s internal and external security audits ought to have discovered these issues, he said.

“These flaws were not detected raises questions about what other serious cybersecurity defects these auditors also missed”, he said.

“While Microsoft certainly deserves most of the blame, the executive branch also bears responsibility”.

Wyden asked for many investigations to look into why Microsoft neglected its security recommendations.

Additionally, he urges directors to take all necessary actions to hold the business accountable for any violations of that orders.

Keep yourself informed about the latest Cyber Security News by following us on GoogleNews, Linkedin, Twitter, and Facebook.


[ad_2]
Source link

Galaxy Z Fold 5 finally fixes Samsung’s annoying camera lag issue

0
[ad_1]

The Galaxy Z Fold 5 seems to have fixed an annoying camera issue that exists on pretty much every Samsung smartphone. We are talking about the camera lag problem that the company has kept unfixed for years. Galaxy phones take a while to update the viewfinder after you press the shutter button. There’s no such delay on the new foldable.

It’s been just a few days since Samsung launched the Galaxy Z Fold 5 and Galaxy Z Flip 5 foldables. The devices bring a handful of upgrades over their respective predecessors. Most notably, they get a redesigned hinge that makes them thinner and lighter, while the Flip model also gains a bigger cover display. Apart from that, many other minor improvements enhance the user experience.

Among them is improved camera performance, at least on the Fold model. The folks at Android Central spotted that the Galaxy Z Fold 5 doesn’t exhibit any “perceivable shutter lag.” The publication tested the foldable’s shutter speed in various lighting conditions and found it to be “a lot faster” than the Fold 4’s. The camera viewfinder is updated instantly after pressing the shutter button to capture a shot.

Samsung needs to fix this camera lag issue on other Galaxy devices

On the Galaxy Z Fold 4 and other older Samsung phones, the viewfinder freezes for a fraction of a second once you press the shutter button. This prevents you from capturing multiple shots in quick succession, which is critical when taking pictures of a moving object. The problem also occasionally leads to blurry photos because the device can’t focus on the subject quickly enough.

The Korean firm improved this behavior a little on the Galaxy S23 series earlier this year, particularly on the Ultra model. However, the problem wasn’t completely gone. It seems to have finally fixed it once and for all. A video shared by Android Central (embedded at the end of this article) suggests the Galaxy Z Fold 5 has zero camera lag. Notably better than the Galaxy S23 Ultra even though the two phones use the same chipset.

Hopefully, this camera lag issue won’t resurface on the new foldable later. We also expect Samsung to push this shutter speed improvement to other Galaxy devices. The company is already preparing to bring a host of new camera features introduced with the Galaxy Z Fold 5 and Galaxy Z Flip 5 to older models, including all foldables launched in 2020 and beyond and Galaxy S21, Galaxy S22, and Galaxy S23.


[ad_2]
Source link

CherryBlos malware uses OCR to scan victims photos for passwords

0
[ad_1]

Over the past few years, it’s no secret that threat actors have ramped up their efforts to gain unauthorized access and steal your hard-earned money. As part of these efforts, hackers have developed two new cryptocurrency stealer malware named ‘CherryBlos’ and ‘FakeTrade,’ which use optical character recognition (OCR) to scan victims’ photos for sensitive information, such as passwords.

First discovered by Trend Micro and in distribution since April 2023, the CherryBlos malware spreads through various social media networks, deceiving unsuspecting users by disguising itself as innocent AI tools or coin miners. Once installed, the malware requests permission to access crucial functionalities and then grants itself additional privileges, making it difficult for a user to stop its harmful activities.

While the malware primarily uses common tactics like loading fake user interfaces that closely mimic official apps to phish for login credentials, it also utilizes OCR to extract valuable data from images and photos stored on the infected device. This is because many cryptocurrency wallets have a recovery password in case a user forgets their main one. However, users often take screenshots of the recovery password, and OCR allows the malware to search for such screenshots and upload them to a remote server, putting the victim’s sensitive data at significant risk.

In addition to the CherryBlos malware, the same threat actors were also behind the broad FakeTrade campaign, which involved a staggering 31 scam money-earning apps on the Play Store, targeting users in Malaysia, Vietnam, Indonesia, Philippines, Uganda, and Mexico.

Evading Play Store guidelines

While threat actors spreading malware through various channels isn’t new, the fact that one of these malicious APKs, namely Synthnet, made its way onto Google Play, masquerading as a legitimate application, raises serious concerns. Fortunately, Google swiftly intervened and removed the app before it could cause any significant harm, but the app did accumulate over a thousand downloads.

In response to threats like these, Google will require all new developer accounts registering as organizations, starting from August 31, 2023, to provide a valid D-U-N-S number assigned by Dun & Bradstreet before submitting apps. This move will not only prevent the misuse of the platform for distributing malware but also improve overall security.


[ad_2]
Source link

Pentagon Looks Into ‘Critical Compromise’ of Air Force and FBI Contacts

0
[ad_1]

The communications systems of 17 Air Force stations were concerned about “critical compromise” after $90,000 in federal radio technology had been stolen by a Tennessee-based engineer.

According to the warrant that Forbes was able to obtain, the breach could potentially have affected FBI communications.

As law enforcement searched the engineer’s house, they discovered that he had “unauthorized administrator access” to radio communications equipment used by the Air Education and Training Command (AETC), which was “affecting 17 DoD installations”.

The Pentagon defines the possible compromise of technology employed by the AETC, one of the nine “major commands,” as “interrelated and complementary” to Air Force headquarters. This occurred only three months after another breach of security at the Pentagon was exposed.

Air Force Engineer’s Home Raided 

During the raid, authorities also found an open computer screen that showed the suspect was using Motorola radio programming software, which included the “entire Arnold Air Force Base (AAFB) communications system.”

The suspect was running a Motorola radio programming software, “which contained the entire Arnold Air Force Base (AAFB) communications system,” according to a Department of Justice search warrant.

Authorities claimed to have discovered evidence the suspect may have had access to communications of the FBI and several Tennessee state agencies.

He was found to have a USB that included “administrative passwords and electronic system keys” for the AETC radio network, according to a paper outlining the forensics on the technologies that were confiscated from his residence.

He was found to have a USB that included “administrative passwords and electronic system keys” for the AETC radio network, according to a paper outlining the forensics on the technologies that were confiscated from his residence.

Additionally taken from the flash drives were “local law enforcement radio programming files,” Another USB device included “Motorola radio programming files,” which, when accessed, displayed a banner informing the user that they were U.S. government property.

When accessed, installation files found during the search displayed a “CONFIDENTIAL RESTRICTED” pop-up.

The warrant states that “witnesses and co-workers” informed investigators that the suspect sold radios and radio equipment, worked irregular hours, was arrogant, frequently lied, engaged in inappropriate workplace behavior and sexual harassment, had money issues, and owned (Arnold Air Force Base land mobile radio) equipment.

According to investigators, a colleague had twice reported him because of “insider threat indicators” and unauthorized possession of Air Force equipment, reads Forbes report.

According to his LinkedIn profile, the 48-year-old engineer at the Arnold air force base has extensive experience in both radio communications and cybersecurity.

He claimed to have conducted multiple tests of the security at Arnold Air Force Base, enhanced radio communication protection on the site, and knew the encryption used for government data.

As of right moment, the police have not charged the suspect with any crimes.

Keep yourself informed about the latest Cyber Security News by following us on GoogleNews, Linkedin, Twitter, and Facebook.


[ad_2]
Source link

FakeTrade Android Malware Attack Steals Crypto Wallet Data

0
[ad_1]

IN SUMMARY

  • The malware campaigns have been dubbed CherryBlos and FakeTrade.
  • The prime target of this attack is crypto wallet data on Android devices.
  • TikTok, Twitter and Telegram are being used to promote malicious apps.

A new malware campaign is currently focusing its sights on Android devices, aiming to surreptitiously steal personal information and cryptocurrency wallet credentials from unsuspecting users.

According to the latest report by Trend Micro, cybersecurity researchers have detected two financially motivated malware campaigns. These malicious operations exploit applications within the official Google Play Store, making the platform an attractive target for such cybercriminal campaigns.

Dubbed CherryBlos and FakeTrade by researchers, these two malware campaigns have been identified as potentially related by Trend Micro. The link between them lies in the fact that both types of malware utilize identical application certificates and network infrastructure.

Researchers have identified that campaign operators are increasingly targeting Android users with banking trojans to steal cryptocurrency. To achieve their malicious objectives, they distribute fake Android applications loaded with malware. These apps are advertised on the Google Play Store, phishing websites, and social media platforms. The same pattern is identified in the latest campaigns.

It is worth noting that the malware operators are exploiting various social networking platforms, including X (formerly Twitter), TikTok, and Telegram, to promote fraudulent Android apps. All of the offensive apps have been removed from Google Play.

FakeTrade Malware Attack Steals Crypto Wallet Data on Android Phones
Fake TikTok and (X) Twitter account dropping malicious apps (Screenshots credit: Trend Micro)

CherryBlos Campaign

The CherryBIos campaign exploits social network sites to promote fake services and ads, leading users to phishing websites. Unsuspecting individuals are deceived into downloading and installing Android apps infected with malware from these sites.

The malware, known as CherryBIos, first appeared online in April 2023. It earned its name from the unique string found in its hijacking framework. Once installed, CherryBIos can pilfer cryptocurrency wallet credentials and alter a user’s address, diverting funds to the attackers’ address during withdrawals.

“Upon further investigation, we were able to trace its source to a telegram group called Ukraine ROBOT that had been posting messages related to cryptocurrency mining since early 2023. This group’s profile directly points to the phishing website where the malware was downloaded,” Trend Micro’s report read.

(Screenshots credit: Trend Micro)

Later, the malware was found in Happy Miner, GPTalk, and SynthNet apps. An interesting feature of CherryBIos malware is that it exploits OCR (optical character recognition) to read mnemonic phrases found in images on a compromised device and send the data to a C2 server.

These phrases are specifically helpful when users want to restore a crypto wallet. It is a notorious Android banking trojan that first requests Android accessibility permissions to perform malicious activities. These permissions are designed for people with disabilities and help them interact with the device via gestures and perform tasks like reading screen content aloud or automating repetitive tasks.

FakeTrade Campaign

In the FakeTrade campaign, malware operators use numerous fake money-earning apps that appear to be e-commerce platforms, promising increased income through referrals and top-ups. The malware (AndroidOS FakeTrade.HRXB), hidden inside the apps, prevents users from withdrawing funds.

Researchers found approximately 31 fake Android apps distributing the FakeTrade malware, most of which were designed for shopping or persuading users to complete various tasks in order to earn money or purchase app credits to top up their accounts. However, those who fell for this trap were unable to withdraw funds when they attempted to do so. Most of the apps were uploaded to Google Play in 2021, with some appearing in 2022.

Researchers suspect that the threat actors behind these campaigns aren’t targeting any specific region, considering the languages used in their analyzed samples. This means their victims could be dispersed worldwide, as attackers can conveniently replace resource strings and upload these fake apps to different Google Play regions such as Vietnam, Mexico, Indonesia, the Philippines, and Uganda.

  1. Triada Malware Infects Android Devices via Fake Telegram App
  2. Google Removes Swing VPN Android App Exposed as DDoS Botnet
  3. Iranian Stalkerware ‘Spyhide’ Steals Data from 60K Android Devices
  4. Popular Android Screen Recorder iRecorder App Revealed as Trojan
  5. Global Malware Attack Imitates VPN, Security Apps on Android Phones

[ad_2]
Source link

Certification reveals the battery capacity of Galaxy S24+, S24 Ultra

0
[ad_1]

With the new foldables out of the way, more information about Samsung‘s 2024 flagships has started to hit the internet. We recently learned that the Galaxy S24 series would feature a titanium body and come in two processor variants. A certification listing has now revealed the battery capacities of the Galaxy S24+ and Galaxy S24 Ultra. The Plus model will seemingly get a bigger battery than its predecessor.

Certification agency Dekra recently listed battery modules for the Galaxy S24+ and Galaxy S24 Ultra. The former unit has the model number EB-BS926ABY, while the latter has the mode number EB-BS928ABY (S926 and S928 are the model identifiers of the two phones, respectively). These listings reveal that the Plus model has a rated battery capacity of 4,755mAh. The Ultra model’s battery has a 4,855mAh rated capacity.

A quick look at the rated battery capacities of the Galaxy S23 series reveals that Samsung is adding more power to the Plus model. This year’s Galaxy S23+ has a rated capacity of 4,565mAh. Comparing this value with the one seen in the new certification listing, the battery capacity of the Galaxy S24+ is 190mAh more than its predecessor. This should mean a typical capacity of 4,900mAh (vs. 4,700mAh of the Galaxy S23+).

Samsung is increasing the battery capacity of its Plus flagship, again

This is incredible work on Samsung’s part, considering that it increased the battery capacity of the Plus model by 200mAh this year as well (from 4,500mAh on the Galaxy S22+). Unfortunately, the Ultra model hasn’t gotten a battery boost ever since Samsung started making Ultra-branded Galaxy S flagships (since the Galaxy S20 Ultra in 2020). It has remained at a rated capacity of 4,855mAh and a typical capacity of 5,000mAh.

The base model, on the other hand, got a 4,000mAh battery (typical capacity) in 2020 and 2021. Samsung lowered it to 3,700mAh with the Galaxy S22 last year, before increasing to 3,900mAh this year. It remains to be seen if the base Galaxy S24 will get a bigger battery or if the Korean firm will keep things unchanged. The base Galaxy S23’s rated battery capacity is 3,785mAh.

The Dekra certifications don’t reveal anything else about the Galaxy S24 duo. It’s unclear if Samsung will increase the charging speed a little next year. The base Galaxy S23 charges at a maximum speed of 25W, while the Plus and Ultra go up to 45W. You can expect to get more information about the next-gen Samsung flagships in the coming months. The devices should debut in early 2024.


[ad_2]
Source link

Twitter phishing campaign is targeting Blue subscribers amidst X rebranding

0
[ad_1]

Twitter’s erratic changes since Musk’s acquisition, including the recent rebranding to X, have caused widespread confusion among users. Taking advantage of this havoc, threat actors have launched a new phishing campaign, targeting unsuspecting Twitter Blue subscribers in an attempt to gain unauthorized access.

First discovered by the Twitter Blue user @fluffypony, the phishing emails appear deceptively authentic, seemingly originating from a reputable source labelled ‘[email protected].’ And although the emails do appear legitimate, threat actors are sending them through the mailing list platform, Sendinblue, now known as Brevo. Additionally, to make matters worse, the emails successfully pass SPF authentication checks, further enhancing their perceived trustworthiness.

What do the emails contain?

Taking advantage of the rebranding, the emails claim that the recipient’s existing Twitter Blue subscription is about to expire, urging them to migrate to the new platform, X. To achieve this migration, users are prompted to click on a link that directs them to what appears to be a legitimate API authorization page. Unfortunately, unsuspecting users who authorize this new X app unknowingly grant access to their entire Twitter accounts, including the ability to view, update, and delete followers, manipulate profile and account settings, post and delete Tweets, and engage with other Tweets.

How to regain access?

If you have unknowingly fallen victim to this phishing scam or a similar one, you can get your account back by revoking access to Twitter’s API. To do this, head over to Settings > Security and Account access > Apps and Sessions > Connected Apps, and revoke permissions for any suspicious or unrecognized apps. Afterwards, change your Twitter password immediately and enable 2-step authentication, preferably using non-SMS methods like One-Time Passwords (OTP).

However, this incident once again raises concerns about Twitter’s practices, which have repeatedly caused widespread confusion among users. Additionally, users should remain vigilant and exercise caution when dealing with any emails advising them to take immediate action.


[ad_2]
Source link

Peloton Treadmill Vulnerabilities Risk Users Data

0
[ad_1]

Researchers found numerous vulnerabilities affecting Peloton Treadmill systems that allow malware attacks. An adversary may exploit the flaws to access sensitive device data, including users’ information.

Multiple Vulnerabilities Affected Peloton Treadmill Firmware

According to a recent blog post from Check Point Research, their researchers found numerous security issues with Peloton Treadmills.

Peloton is a popular brand producing a wide range of fitness and workout equipment, particularly boasting internet-connected features. The smart technology empowers the users to demonstrate effective workout sessions with live training videos.

Explaining the issues, the researchers specified that they found multiple security vulnerabilities in the Peloton Treadmill firmware.

Precisely, they first noticed that the treadmills run on Android 10 – a much older version with numerous potential vulnerabilities. Next, the equipment allows an adversary to enable USB debugging and access the shell.

Accessing the shell empowers an attacker to scan installed apps for vulnerabilities, exploiting which could help steal data. Hence, the researchers do not recommend enabling USB debugging.

Moreover, the researchers also found hardcoded sensitive data on the device firmware, including the license key. Accessing these details lets an attacker perform DoS attacks on the target equipment.

Another severe issue CPR highlighted is the existence of unprotected services that allow third-party apps to gain elevated privileges. Again, an attacker may exploit the apps’ tokens to access personal data.

Similarly, attackers may exploit broadcast receivers, preventing device system updates and gaining infinite control over the treadmills.

Above all, an attacker may exploit the flaws in the standard APIs running on the treadmill systems to install malware. In turn, the attacker may perform various malicious activities on the equipment, including exploiting the integrated webcam and microphone to spy on the user.

Peloton To Patch the Flaws Soon

After discovering the vulnerabilities, Check Point Research responsibly disclosed the flaws to Peloton. In response, Peloton explained that exploiting the flaws require an attacker to have physical access to the treadmills. Nonetheless, they appreciated the researchers for highlighting the bugs. It remains unclear if the vendors plan to address these issues anytime soon.

On a side note, McAfee researchers also highlighted numerous security issues with Peloton Bike+ and Tread+ in 2021. At that time, Peloton deployed the patches with subsequent firmware release.

Let us know your thoughts in the comments.


[ad_2]
Source link