Microsoft Expands Security Logging and Offers 365 Clients Free Access

0
[ad_1]

Microsoft expanded cloud logging accessibility and flexibility for customers’ deeper security visibility.

This expansion coordinates results with commercial and government customers and the Cybersecurity and Infrastructure Security Agency (CISA) about security to provide cloud customers with insight and analysis.

The wider availability of a Microsoft signing key has emerged following a notorious incident involving Chinese hackers.

These hackers managed to exploit the key, gaining unauthorized access to numerous corporate and government Microsoft Exchange and Microsoft 365 accounts, ultimately resulting in the theft of sensitive email data.

With the cloud, software updates happen automatically and security monitoring is centralized.

Log data provides detailed and auditable information on application and device access for customers using the cloud.

Digital forensics and incident response teams rely on log data to identify instances where an attacker is posing as an authorized user.

Microsoft provides cloud security to worldwide customers at no additional ended the coming months.

Microsoft Purview Audit

Customers can utilize Microsoft Purview Audit to visualize various types of log data, enabling them to respond more effectively to security events, investigations, and compliance obligations.

In Audit (standard), after expanding, the customer has a detailed log of email access and more than 30 other types of log data previously available only at the premium level also it increases the retention period from 90 days to 180 days.

In Audit (Premium) already, customers will receive access to all available audit logging events, including insights it helps in the Microsoft purview compliance portal and Office 365 Management Activity API.  An additional feature of expanding Premium includes longer retention periods and automation support for importing log data. 

“After working collaboratively for over a year, I am extremely pleased with Microsoft’s decision to make necessary log types available to the broader cybersecurity community at no additional cost,” said CISA Director Jen Easterly.

The update will be rolled out over September 2023 to all government and commercial customers.

All the existing and new logs can be accessible; visit the Microsoft Purview compliance portal and select Audit from the Solutions panel.

“We believe that every organization deserves to have products that are secure by design and come with necessary security data “out of the box,” reads the CISA report.


[ad_2]
Source link
WhatsApp will let you initiate 2x larger group calls

0
[ad_1]

WhatsApp is making it easier to initiate larger group voice and video calls. The latest beta version of the Meta-owned messaging app (v2.23.15.14 for Android) lets users begin a group call with up to 15 people. That’s more than double the previous limit of seven participants at the beginning.

WhatsApp has allowed group voice and video calls in groups with up to 32 participants since April last year. However, it has put in place a weird limit on the number of people that can join a group call from the beginning. You can only initiate a call with a maximum of seven group members. You have to select those seven participants beforehand (you can proceed with fewer participants as well).

If you want to add other group members to the call, you have to manually do that later. This is a bit of a hassle for calls in larger groups. WhatsApp is fixing it by raising the limit to 15 people (via WABetaInfo). You can now select up to 15 group members before initiating a voice or video call. Like before, you can add more later. The overall participant limit for group calls on WhatsApp is still 32, though.

As said earlier, WhatsApp is currently testing this change among beta users on Android. If everything goes according to the plan, the update should reach the stable version of the app soon. But if you can’t wait for it, you can try your luck by signing up for the beta program here. If you’re lucky enough, you may get early access to the new group call limit on the Meta-owned messaging platform.

WhatsApp is working on more new features

Over the past couple of years or so, Meta has shaped WhatsApp into a more comprehensive communication and collaboration tool. While it’s still not as feature-rich as the likes of Google Meet and Zoom, WhatsApp can do a lot that the latter two can also do. Moreover, Meta is frequently pushing new features to it. Features like screen sharing and group video calls are among those.

Going forward, WhatsApp will gain more power. The company is testing the ability to send messages to new phone numbers without saving them first. WhatsApp also recently launched an app for Wear OS smartwatches. Stay tuned to find out what Meta has in the pipeline for its messaging app in the coming months. You can click the button below to download the latest version of the app for your Android smartphone.

DOWNLOAD WHATSAPP


[ad_2]
Source link

Amazon is expanding its palm-based payments to more stores

0
[ad_1]

Forget tapping your phone or your card, Amazon lets you pay with your palm. This feature is called Amazon One, and it’s available in more than 200 Amazon stores in the US. That’s a lot, but Amazon is planning on bringing palm-based payments to more stores by the end of the year.

The e-commerce super giant brought this technology to several of its Whole Foods stores in states like Texas, California, and New York. Instead of pulling out your card or phone, you just need to hover your palm over the reader. The machine will use your unique palm signature as a form of identification.

Supposedly, your palm signature should be unique to you just like your fingerprint. With that, you should be able to make secure payments and redeem your Amazon perks.

Amazon is bringing palm-based payments to more stores

As stated, Amazon One is available in more than 200 stores. However, the company plans on more than doubling this number by the end of the year, according to Engadget. It plans on the functionality making it to more than 500 stores.

While the technology is available for Amazon-owned stores, it won’t only be limited to those stores. The technology is available in some third-party venues at the moment. This includes the Colorado Rockie’s Stadium and Panera. We can guess that this expansion will include more third-party stores.

We’re not sure what stores will gain this functionality. However, if you live close to an Amazon-owned store, then you should be on the lookout for it to come later this year.

This isn’t without its controversy

As you can imagine, a feature such as this has landed Amazon in some legal trouble. This feature uses biometric data… let’s rephrase that, Amazon collects your biometric data in order for this feature to work. While this might not be an issue for most people, there are plenty of folks who don’t like this.

In fact, the company could be looking at a class-action lawsuit over this in New York. The suit says that Amazon didn’t inform its users that it collects this data. Thus, many people are giving away their biometric data without the proper heads-up. Regardless, Amazon is still going ahead with this expansion.


[ad_2]
Source link

Samsung brings WhatsApp, Wallet and Thermo Check apps to the Galaxy Watch series

0
[ad_1]

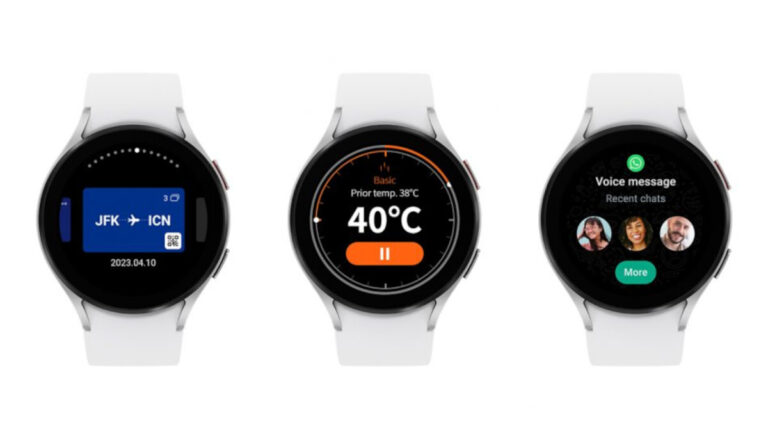
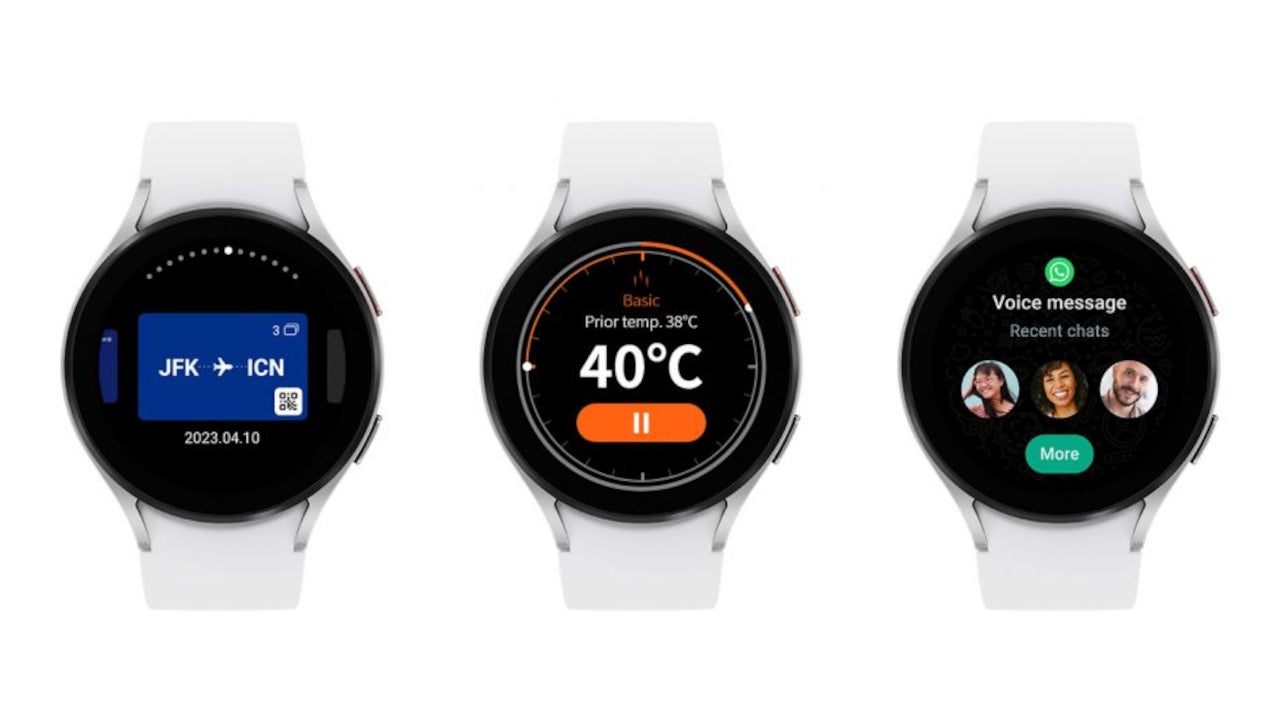
One day after Meta announced the rollout of the standalone WhatsApp for Wear OS app, Samsung replied with an announcement of its own. The South Korean giant has just revealed that three apps are coming to its Galaxy Watch series: WhatsApp, Wallet, and Thermo Check.

Samsung Wallet made its debut last year when it bundled together Samsung Pay and Samsung Pass to make it easier for users to manage their wallets on their smartphones. Starting today, Samsung Wallet is making its way to Galaxy Watch wearable devices, allowing users to make payments, provide IDs, and pull up show tickets right on their wrists.

It’s worth noting that the Wallet app is not yet available in all countries, although Samsung is trying hard to expand its availability to additional markets. Early this year, Samsung Wallet was launched in 8 new markets, after the app was originally debuted in 21 countries in 2022.

The new Thermo Check app takes advantage of the Galaxy Watch’s advanced infrared technology to make accurate temperature measurements. The app allows users to measure the temperature of their surroundings, from meals to water, all without any physical contact required. According to Samsung, the Thermo Check app will first be available on the upcoming Galaxy Watch 6 devices and later expanded to Galaxy Watch 5 series.

Last but not least, WhatsApp is now available for Galaxy Watch 5 and Galaxy Watch 4 users. The app is simple to use and offers some basic messaging features, including the option to continue conversations, reply to messages by voice, as well as answer calls. All these features are available to Galaxy Watch 5 and 4 users without having to pair their smartwatches with a phone.

But that’s not all! Samsung hinted at even more “versatile functions” to be unveiled at Galaxy Unpacked on July 26, so expect even more improvements to Galaxy Watch users to be announced next week.


[ad_2]
Source link

Poisoned Facebook Ads Deliver Malware Using Fake ChatGPT

0
[ad_1]

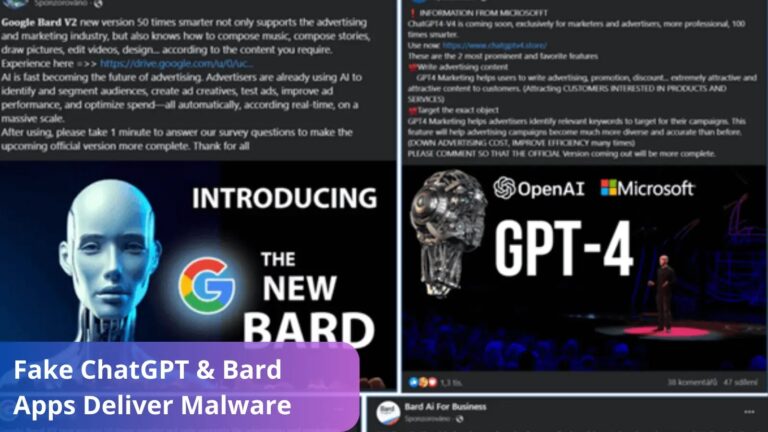
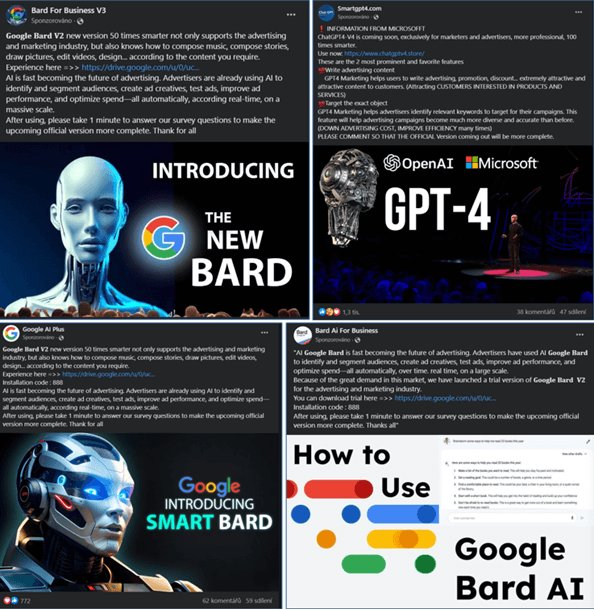
Cyber criminals have recently started using Facebook to pretend to be well-known generative AI brands like ChatGPT, Google Bard, Midjourney, and Jasper to steal users’ personal information.

Users on Facebook are deceived into downloading content from fake brand sites and advertisements.

These downloads contain harmful malware that steals users’ internet credentials for banking, social networking, gaming, and other services, their cryptocurrency wallets, and any data saved in their browsers.

According to the Check Point Research Team (CPR), the majority of Facebook campaigns that use fake sites and dangerous advertisements eventually spread malware that steals information.

Users who are not aware of the situation are liking and commenting on fake posts, spreading them to their social networks.

How Criminals Use Facebook Ads to Steal Private Information?

This new scam makes use of people’s curiosity about popular generative AI apps to trick them out of their passwords and sensitive data.

The intruders begin by making fake Facebook pages or groups for well-known brands and adding interesting content to them. The unaware individual comments on or likes the content, guaranteeing that it appears on their friends’ news feeds. 

Through a link, the false page advertises a new service. When the user clicks on the link, malicious malware that is intended to steal their internet passwords, cryptocurrency wallets, and other information saved in their browser is unknowingly downloaded.

“Many of the fake pages offer tips, news, and enhanced versions of AI services Google Bard or ChatGPT”, researchers said.

Fake posts displayed to the users

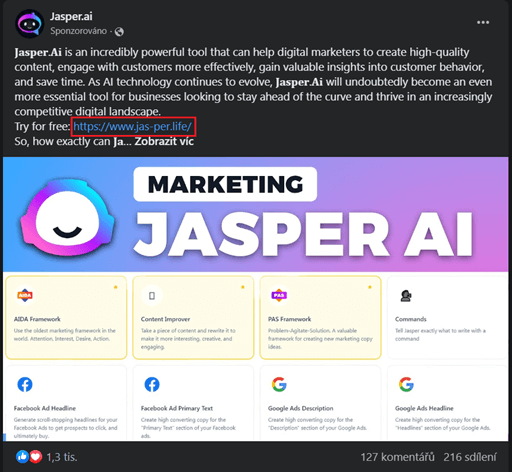
Additionally, cyber criminals frequently persuade users to utilize other AI services and tools. Jasper AI is another well-known AI brand that has amassed over 2 million followers and is being impersonated by online crooks.

Jasper AI impersonated by cyber criminals

In reality, people are furiously debating the role of AI in the comments and liking/sharing the posts, which increases their reach.

“Most of those Facebook pages lead to similar type landing pages which encourage users to download password-protected archive files that are allegedly related to generative AI engines”, say the researchers.

Notably say, when an ignorant user looks for ‘Midjourney AI’ on Facebook and comes across a page with 1.2 million followers, they are likely to assume it is genuine.

Researchers mention that the main goal of this fake Mid-Journey AI Facebook page is to mislead visitors into downloading malware. Links to malicious websites are combined with links to authentic Midjourney reviews or social networks to offer credibility.

“The malware makes efforts to gather various types of information from all the major browsers, including cookies, bookmarks, browsing history, and passwords,” researchers.

“It targets cryptocurrency wallets including Zcash, Bitcoin, Ethereum, and others.”

Final Thoughts

The primary objective of cybercriminals seems to be information related to Facebook accounts and the theft of Facebook pages. Even many pages with a wide audience might be used in this way to propagate fraud since cybercriminals are seeking to take advantage of pages with significant audiences and advertising budgets already in place.

Individuals and organizations must thus educate themselves, be aware of the hazards, and maintain vigilance against the strategies used by cybercriminals. To defend against these changing dangers, advanced security solutions are still crucial.

Stay up-to-date with the latest Cyber Security News; follow us on GoogleNews, Linkedin, Twitter, and Facebook.


[ad_2]
Source link

Self-Replicating P2PInfect Worm Hits Redis Instances

0
[ad_1]

The worm exploits a sandbox escape vulnerability in the Lua Library, which has received a maximum severity score of 10.0 on the CVSSv3 severity scale.

Security experts have issued a warning about a highly sophisticated peer-to-peer (P2P) worm, written in Rust, that is specifically targeting instances of the popular open-source database software Redis.

Known as ‘P2PInfect,’ the worm exploits a critical vulnerability to infiltrate Redis instances and assimilates them into a larger P2P network, enabling it to spread rapidly.

Researchers from Unit 42, Palo Alto Networks’ cloud research team, identified the worm and named it after a term found in leaked symbols within its code. The worm exploits CVE-2022-0543, a sandbox escape vulnerability in the Lua Library, which has received a maximum severity score of 10.0 on the CVSSv3 severity scale, indicating its significant threat potential.

P2PInfect: Self-Replicating Worm Hits Redis Instances
Screenshot shared by researchers shows P2PInfect appears in the leaked symbols

P2PInfect establishes its foothold in cloud container environments, making it stand out from other worms targeting Redis, such as the cryptojacking malware operated by Adept Libra (aka TeamTnT), Thief Libra (aka WatchDog).

Once inside a Redis instance, the worm executes a Powershell script that alters local firewall settings, preventing the infected Redis instance from being accessed by legitimate owners while granting the worm operators unrestricted access.

One of the worm’s sophisticated techniques for persistence involves a process named ‘Monitor,’ stored in the Temp folder within a user’s AppData directory. This process downloads multiple randomly named P2PInfect executables alongside an encrypted configuration file, ensuring its long-term presence on infected systems.

Researchers have observed that the worm establishes a P2P connection via port 60100 to a large command and control (C2) botnet. While samples downloaded from the C2 include files labelled ‘miner’ and ‘winminer,’ there is no evidence yet of P2PInfect engaging in cryptomining using infected instances.

Experts speculate that the worm might be laying the groundwork for future campaigns, potentially involving mining activities using the botnet.

According to Unit 42’s blog post, the company discovered P2PInfect on July 11th using its HoneyCloud platform, a diverse array of honeypots designed to attract and analyze public cloud threats. The worm’s rapid spread has been noted, with 934 out of 307,000 publicly-communicating Redis instances identified as vulnerable.

The unique use of Rust programming language by P2PInfect raises concerns among cybersecurity experts, as many ransomware groups have also shifted to Rust due to benefits such as faster encryption and evading common detection methods.

As the threat landscape continues to evolve, researchers are closely monitoring the worm’s behaviour, including the possibility of new behaviours and features being added to P2PInfect in the future.

While Rust offers numerous advantages beyond its use in malware, its adoption in sophisticated worms like P2PInfect highlights the importance of constant vigilance and proactive security measures in the face of ever-evolving cyber threats. Organizations and individuals are urged to update their Redis instances and implement robust cybersecurity practices to safeguard against potential attacks.

In the wake of this discovery, the cybersecurity community must remain vigilant and proactive in safeguarding critical systems and data against emerging threats like P2PInfect and other advanced malware strains.

  1. 10 Application Security Best Practices To Follow
  2. Thousands of GitHub Repositories Cloned in Supply Chain Attack
  3. VirusTotal Data Leak Exposes User Info, Including Intel Agencies’ Data
  4. Threat actors hijacking Bitbucket and Docker Hub for Monero mining
  5. LemonDuck Cryptomining Botnet Hunting for Misconfigured Docker APIs

[ad_2]
Source link

We have a leak of the OnePlus 12R long before it launches

0
[ad_1]

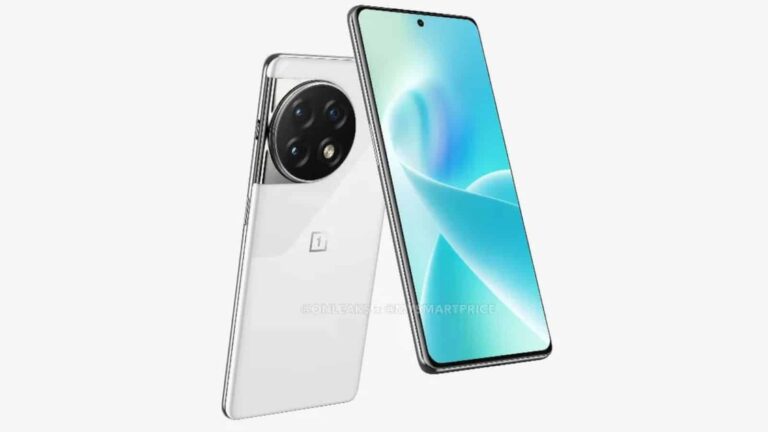
We just had a significant leak of the OnePlus 12 half a year before it’s slated to launch. Now, we’re looking at a leak of the more affordable version of that phone. Thanks to OnLeaks (via Phone Arena), we have a leak of the OnePlus 12R.

If you want to know more about the OnePlus 12 leak, you can click here. We see that this phone is going to look similar to the OnePlus 11 with its circular camera package. We see that it’s going for a center-mounted punch-hole rather than one on the left of the screen.

The leaked specs point to it using the most powerful Snapdragon SoC that will be available at that time and come with up to 16GB of RAM. There’s a lot more to this leak, so be sure to check out the article.

The OnePlus 12R got an early leak

Just like the OnePlus 12, the OnePlus 12R looks like it’s going to retain the same design as the OnePlus 11. It could look 1:1 with the OnePlus 11  with no noticeable change.

As for the display, this phone could sport a large 6.7-inch AMOLED display with a smooth 120Hz refresh rate. We don’t know the resolution, but the leak points to it being 1.5K. That’s somewhere between 1080p and 1440p.

As for the internals, the leak points to this phone using the Snapdragon 8 Gen 2 SoC, which is the same chip powering the OnePlus 11. We’re looking at up to 16GB of RAM and up to 256GB of storage. We’re sure that the base model will come with 8GB of RAM and 128GB of storage.

Moving onto the camera, the OnePlus 12R could come with a 50MP main camera, 8MP ultrawide camera, and a 32MP 2x zoom camera. Up front, we could be looking at a 16MP selfie camera.

The battery in this phone looks like it will also get a boost. The OnePlus 12R could have a 5,000mAh battery. That’s 10% larger than the standard flagship capacity of 5,000mAh.

So far, it looks like this phone is going to be a powerful alternative to the latest Galaxy S phones, iPhones, and Pixel phones that will be out next year. We’re not sure how much this phone will cost when it launches. However, we expect it to be more affordable than the OnePlus 12.


[ad_2]
Source link

Apple is internally testing its own AI chatbot codenamed Apple GPT

0
[ad_1]

Ever since ChatGPT kicked off the AI revolution, major tech companies have been on their toes to develop the next big thing in generative AI. Now, in line with these efforts, Apple is reportedly testing its own AI chatbot, which some engineers are unofficially referring to as “Apple GPT.”

While the specific details about the Apple GPT chatbot remain unclear, it will run on the company’s newly developed “Ajax” framework, a collaboration between Apple and Google’s JAX machine learning framework and Google Cloud. Additionally, the chatbot will primarily focus on addressing privacy and security concerns associated with other chatbots like OpenAI’s ChatGPT and Google’s Bard.

Moreover, Bloomberg’s Mark Gurman reported that the internal tests for the chatbot show promising results, as employees are leveraging its text summarization and question-answering capabilities to streamline and optimize the product development process.

Apple’s stance on generative AI

This report comes after CEO Tim Cook expressed the company’s keen interest in AI technology and emphasized the need to carefully monitor the field’s advancements. However, it is important to note that Cook also highlighted the importance of addressing various issues before the widespread adoption of AI products during an earnings call.

“I do think it’s very important to be deliberate and thoughtful on how you approach these things. There’s a number of issues that need to be sorted…in a number of different places, but the potential is certainly very interesting,” said Tim Cook.

Breathing a new life in Siri

While it’s too early to say Apple’s intention behind developing a generative AI chatbot, one possible reason could be to revamp Siri, which has fallen behind competitors like Google Assistant. This is because integrating the Apple GPT chatbot into Siri could potentially be a game-changer, enabling users to interact more naturally with the voice assistant without relying on specific phrases. Moreover, the company is also actively hiring new engineers, especially those with a deep understanding of large language models and generative AI.


[ad_2]
Source link

Pokémon Sleep tracker / game is now available for iOS and Android devices

0
[ad_1]

Less than a month after opening pre-registrations for its Pokemon game / sleep tracker hybrid, The Pokemon Company announced it’s now available on the App Store and Google Play. The new sleep tracking app has a gaming aspect to it to cater to Pokemon fans.

In order for the app to be able to track your sleep, you must put your phone by your pillow. Alternatively, you can purchase Pokemon GO Plus+ device, which does the same thing. This particular device will then sync the collected sleep data with your phone via Bluetooth. You’ll also be able to unlock some exclusive characters in Pokemon Sleep if you buy the Pokemon GO Plus+ device.

Pokemon Sleep offers four main features: sleep score / sleep type, sleep trends, Pokemon-inspired music, and audio recordings. Various noises detected during sleep tracking will be automatically recorded and you’ll be able to play the recordings back and hear your snores and sleep talk or environmental noises.

As far as the sleep type goes, you can be tagged to be “dozing,” “snoozing,” or “slumbering” for the night, based on how much you moved in your sleep. The sleep score you receive is usually based on how long you slept.

The sleep trends feature does exactly what you think it does: it allows users to look back in detail on how regular their sleep has been on a week-by-week basis.

If you’re more interested in the gaming aspect, in Pokemon Sleep you’ll team up with Professor Neroli and Snorlax to study the sleeping habits of Pokemon as you try to complete your Sleep Style Dex. Pokemon with sleep patterns similar to yours will be gathering around your Snorlax companion, which you will discover once you wake up.

Your goal is to befriend as many Pokemon as possible to discover more. This will offer you various rewards, just like meeting sleep habits goals. If you’re interested in checking out this free app, you can download it now via the App Store and Google Play.


[ad_2]
Source link

Kevin Mitnick Dies: The Legendary Hacker’s Journey

0
[ad_1]

Kevin Mitnick dies at the age of 59 after a battle with pancreatic cancer. His life journey from a notorious hacker to a respected cybersecurity consultant is a tale of transformation and redemption.

The Early Days of Hacking

Mitnick began his hacking career at the tender age of 16, targeting a computer system that Digital Equipment Corporation was using in the 1980s. His exploits soon caught the attention of the authorities, leading to his conviction in 1988. He was sentenced to 12 months in prison and another three years of supervised release. However, this did not deter him from his hacking pursuits. At the end of his release, he was caught again for hacking Pacific Bell voicemail computers, leading to a warrant for his arrest.

The FBI’s Most Wanted

Mitnick’s hacking exploits escalated to the point where he landed on the FBI’s most wanted list. He lived as a fugitive for two-and-a-half years, eluding the authorities while continuing his hacking activities. His exploits were so infamous that they inspired the 2000 film “Takedown” and led to a highly publicized FBI manhunt. Mitnick was eventually arrested and served several stints in prison, including eight months in solitary confinement.

From Black Hat to White Hat

After his release from prison, Mitnick underwent a significant transformation. He changed his hacker status from black hat to white hat, using his social engineering services for good through security consulting. He also wrote several books on computer security, including the New York Times bestseller “The Ghost in the Wires: My Adventures as the World’s Most Wanted Hacker.” His other notable works include “The Art of Deception,” “The Art of Intrusion,” and “The Art of Invisibility.”

A Respected Cybersecurity Consultant

Mitnick later pivoted to a lucrative career as a cybersecurity consultant. He worked as a security evangelist and ‘Chief Hacking Officer’ at KnowBe4, a security awareness training company based in Florida. His unique insights and experiences made him a sought-after security consultant, winning over people who worked in tech, government, and finance.

The Legacy of Kevin Mitnick

Mitnick’s death has left a significant void in the cybersecurity world. He is survived by his wife Kimberley, who is pregnant with their first child. His life, filled with controversy and transformation, has been described by his family as being like a fiction story. His journey from infamy to redemption serves as a powerful reminder of the potential for change and the importance of ethical conduct in the digital world.

For more information about Kevin Mitnick’s life and career, visit his Wikipedia page. For more articles related to cybersecurity, check out our previous blog post.


[ad_2]
Source link