Malware Campaign Targets F5 BIG-IP Appliances To Steal Data

0
[ad_1]

Researchers discovered a malware campaign targeting F5 BIG-IP appliances that could remain hidden for years. The threat actors behind the malware aim to steal data while evading detection, which can severely impact victim organizations.

Outdated F5 BIG-IP Appliances Could Remain Under Malware Attack Undetected For Years

According to a recent post from Sygnia, their researchers detected malware intrusion on an organization following a cyber attack. Investigating the matter made them unveil a sneaky malware campaign that remained undetected for a couple of years.

Specifically, the malware campaign linked back to a China-nexus threat actor “Velvet Ant” that managed to infiltrate the target network by compromising F5 BIG-IP appliances. Using this custom malware allowed the attackers to evade detection for at least two years before catching Sygnia’s attention.

As observed, the victim organization had two vulnerable F5 BIG-IP appliances on its network for firewall, WAF, load balancing, and local traffic management services. Moreover, both devices remained exposed to the internet instead of being protected via the company firewall. Consequently, the threat actors possibly exploited known vulnerabilities in those devices, gaining remote access to the network.

After establishing persistence, the threat actors deployed various binaries on the network to execute malicious activities and steal data.

The researchers have shared a detailed technical analysis of the entire malware attack in their post. However, how exactly the threat actors compromised the vulnerable devices remains unclear.

While the researchers have described the single event in detail, they suspect this might be a part of a widespread cyberespionage campaign from the threat actors. Therefore, they advise organizations to implement robust security measures to prevent threats.

Some key steps that firms should deploy on their networks include limiting outbound internet traffic and deploying firewalls to protect internet-facing devices, limiting traffic over management ports to prevent lateral movement, replacing legacy systems, and deploying Endpoint Detection and Response (EDR) systems for adequate monitoring.

Let us know your thoughts in the comments.


[ad_2]
Source link
How Android’s security features safeguard your mobile app experience

0
[ad_1]

Android remains at the forefront of cybersecurity, deploying a suite of security features tailored to protect its users. Emphasizing user control and data integrity, Android’s security architecture is built on a foundation of app permissions, biometric technologies, and continuous updates. These layers of protection ensure that personal information remains secure and that the functionality of devices is not compromised, even as potential security threats grow in complexity and number.

App Permissions

Android’s approach to app permissions is designed to give you complete control over what personal information and device functions each app can access. This system ensures that no app can access your camera, contacts, GPS location, or storage without asking you first.

For example, if you download a mobile casino app, it might ask for permission to use your device’s GPS to provide location-based services or to access your device’s storage to save game data. Android makes sure that you see a prompt asking if you agree to these requests, and the app can make no changes or access any data unless the user allows this.

Android has also introduced new features that give you even more control, like one-time permissions and auto-reset. One-time permissions mean an app can only access certain data like your location while it’s being used. If an app hasn’t been used for a while, auto-reset will turn off permissions automatically.

Google Play Protect

This integral feature operates by continuously scanning all apps on the Google Play Store prior to their download, certifying that they are devoid of any malicious software or vulnerabilities.

Beyond just initial app reviews, Google Play Protect remains active in the background of your device, persistently monitoring for any unusual behaviors or updates from installed apps that could indicate a security risk. Its real-time protection capabilities are designed to quickly identify and neutralize threats without waiting for user intervention.

Biometric Security Features

Today, Android devices are equipped with sophisticated biometric systems that include fingerprint scanning, facial recognition, and iris scanning, each providing a secure method to verify a user’s identity.

Fingerprint scanning on Android devices captures the unique patterns of ridges and valleys on a user’s fingertip. When access is attempted, the device compares the presented fingerprint with the stored data.

Facial recognition technology in Android uses complex algorithms to map the user’s facial features. This system analyzes numerous points on the face, such as the eyes, nose, and mouth, to create a detailed biometric profile.

Iris scanning, another advanced feature available on some Android devices, utilizes an infrared camera to capture the intricate patterns of the user’s iris. Like other biometric data, this information is encrypted and stored on the device. During authentication, the device scans the iris and compares it to the stored pattern to verify the user’s identity.

Sandboxing

This security mechanism works by creating an isolated environment, a sandbox, for each application on the device. Within this sandbox, the app’s processes are executed separately from the system’s core processes and other applications.

The main benefit of sandboxing is its ability to contain any potential damage caused by malicious software. For instance, if an app is downloaded and later found to be infected with malware, the effects of this malicious app are confined to its own sandbox. This containment prevents the malware from spreading to other parts of the system or accessing sensitive information from other apps.


[ad_2]
Source link

Beats has some new headphones, and they’re pretty awesome

0
[ad_1]

We should all be familiar with the Beats line of premium audio gear. It made a name for itself back in 2011, and it’s looking to do it all over again in 2024. The company just launched the new Beats Solo 4 series of headphones and Solo Buds.

It’s Beats season, as the Apple-owned brand is launching its latest and greatest devices. Not too long ago, we got word about the company preparing to launch a new Beats Pill. This one will share some design attributes with previous iterations, but it’ll still come with some defining features. Right now, we’re still waiting for information about this new speaker. What we know is that it’s going to be a powerful device that you can take pretty much anywhere.

Beats unveil the new Beats Solo 4 and Solo Buds

Starting off with the buds, this isn’t Beats’ first round of TWS earbuds, but they do stand out. The company has a line of earbuds called the Studio Buds. Those are designed to be premium, and they have a price to show.

The Solo Buds, on the other hand, bring power down to a more affordable price point. Coming in at only $79.99, these are targeted to the mid-range audio market. Also, this makes them the cheapest Beats on the market. While they’re affordable, they still offer a great audio experience.

Each earbud has a dual-layer driver which the company says minimizes the micro-distortions in the audio. The result is an overall more accurate sound. Those drivers are axel-aligned to be parallel to the nozzle. This delivers the audio directly to your ears.

The Solo Buds support both Android and iOS, and they’re also compatible with both the Find My Device network and Apple’s Find My network. They can last up to 18 hours on a single charge but your mileage will vary. To get that 18-hour figure, the Solo Buds were tested at 50% volume and streamed audio at 256-Kbps with AAC encoding.

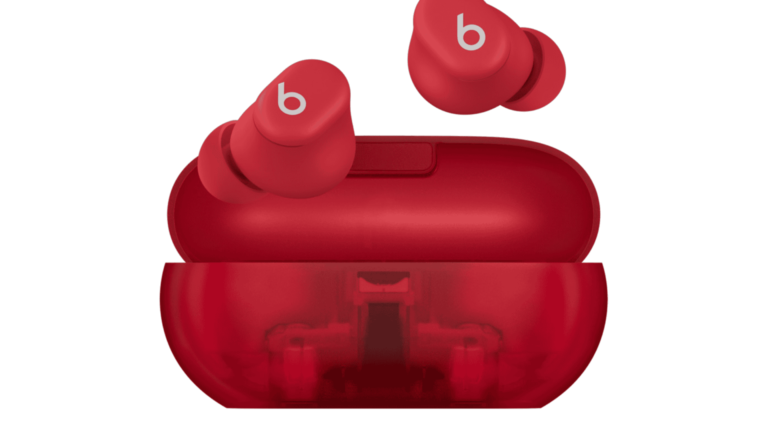
The Solo Buds come in Matte Black, Arctic Purple, Transparent Red, and Storm Gray. You can order them from the official Beats website today.

Beats Solo 4

Moving on to bigger fish, the Beats Solo 4 are the company’s newest flagship headphones. They come in at $199.99, and they’re worth every dime. Since these are the latest headphones from the company, they’re better in just about every way.

The Solo 4 come with updated 40mm drivers. They’re designed to minimize electronic artifacts, distortion, and latency. You’re getting the best and highest-detailed sound from any Beats product.

Adding to this experience is the spatial audio. These headphones have dynamic head tracking that makes you feel like you’re in the middle of the action.

These are Bluetooth headphones, but what if you’re an audiophile? You’re covered too. Bluetooth audio is compressed, but if you want to listen to uncompressed (lossless) audio, you can use them in wired mode with a USB-C cord. Listening to services like Apple Music or Tidal will be a treat.

If you’re using them in Bluetooth mode, you can expect up to 50 hours of listening time on a single charge. Just like with the Solo Buds, the Solo 4 were tested at 50% volume listening to music at 256-Kbps with AAC encoding.

The Solo 4 are available to buy, so you can pick up a pair today.


[ad_2]
Source link

Google brings brings Gemini AI to teen students in over 100 countries

0
[ad_1]

Image credit — Google

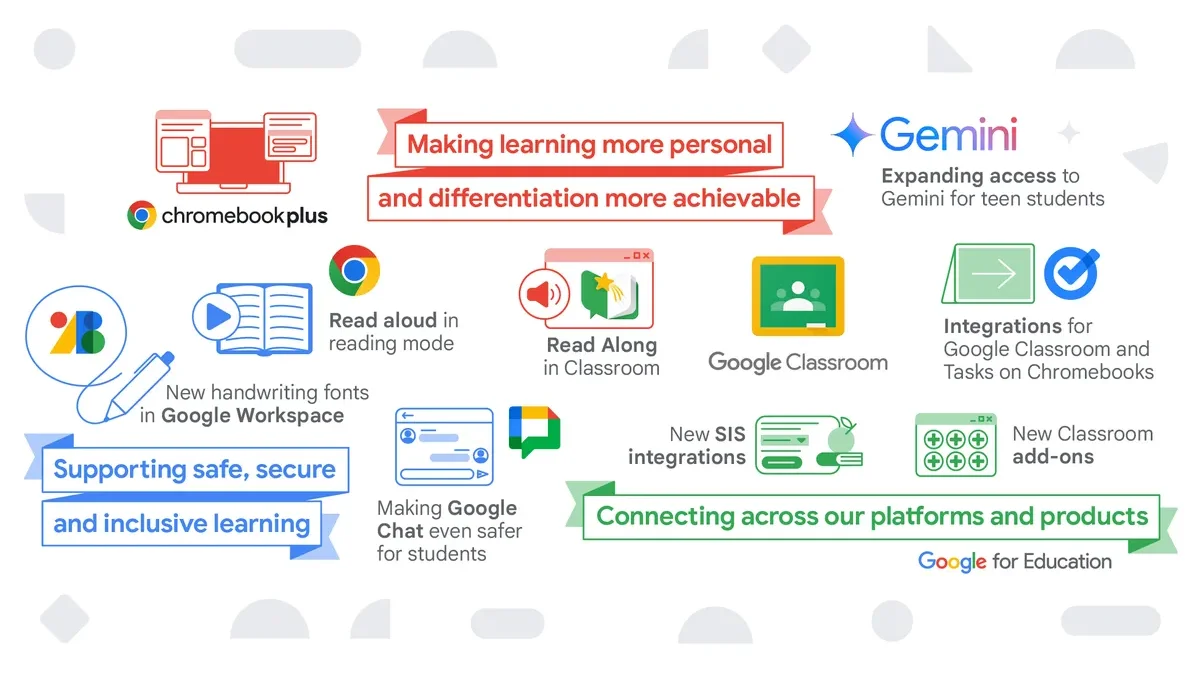
Google is bringing its AI chatbot, Gemini, to teen students in over 100 countries. This was announced today by the company in a blog post where it outlined how Gemini will make learning more personal and engaging for students and how it will be available for free to schools.

The company stated in its announcement that it has partnered with experts in child safety and development to ensure that Gemini is used responsibly in schools. As far as how it will help students learn, an example given is how students can chat with Gemini to get help with their homework or to learn more about a topic they’re interested in. Gemini can also provide personalized feedback on students’ work and help them identify areas where they need to improve. For instance, if a student is writing a paper, Gemini can help them to improve their grammar, spelling, and clarity of writing. Overall, Gemini can be a valuable tool for students who want to learn more and improve their academic performance.

Video Thumbnail

The above video is what will be shown to students when they’re first given access to Gemini, teaching them how to use it responsibly

In addition to Gemini, Google is also adding a number of other AI-powered tools to Chromebooks and Google Workspace for Education. These tools include Read Along in Classroom, which helps students improve their reading skills; Google Classroom, which makes it easier for teachers to create and deliver lessons; and Google Vids, which helps students create engaging videos. Here are some of the key features of Google’s new AI-powered tools for education:

  • Gemini: Chatbot that can help students learn in a variety of ways.
  • Read Along in Classroom: Helps students improve their reading skills.
  • Google Classroom: Makes it easier for teachers to create and deliver lessons.
  • Google Vids: Helps students create engaging videos.
  • Media literacy curriculum: Helps students learn how to navigate the internet safely and responsibly.

An example of how Gemini will help users in the classroom

Google says it is also committed to helping students stay safe online. As a result, the company has developed a new media literacy curriculum, in partnership with leading experts like the National Association of Media Literacy Education (NAMLE), that helps students learn how to navigate the internet safely and responsibly. This curriculum covers a wide range of topics, including how to identify credible sources of information, how to avoid online scams, and how to be respectful of others online.

Google’s new AI-powered tools for education are a promising step forward in the use of technology to improve learning, and have the potential to make a real difference in the lives of students around the world. It is kind of amazing how much information is available to students now right at their fingerprints. The only challenge now is to ensure that these tools are used properly and fairly.


[ad_2]
Source link

Threat Actor Claiming a 0-day in Linux LPE Via GRUB bootloader

0
[ad_1]

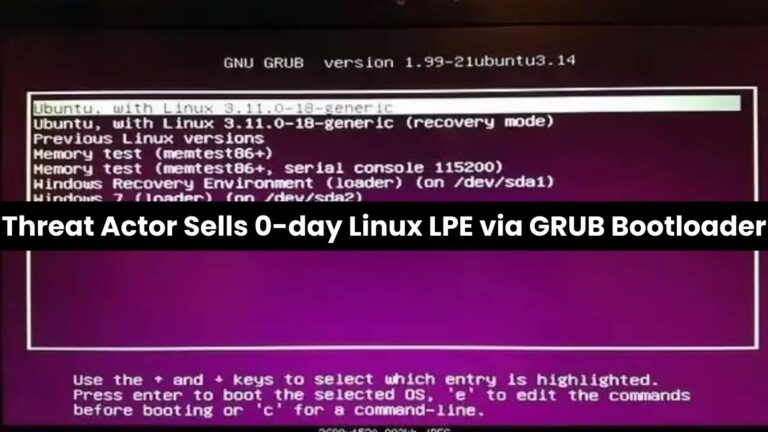
A new threat actor has emerged, claiming a zero-day vulnerability in the Linux GRUB bootloader that allows for local privilege escalation (LPE).

This alarming development has raised significant concerns within the cybersecurity community.

A recent tweet from Dark Web Intelligence shared that the Threat Actor Claimed a 0-day in Linux LPE Via GRUB bootloader.

Scan Your Business Email Inbox to Find Advanced Email Threats - Try AI-Powered Free Threat Scan

The Vulnerability

The zero-day vulnerability reportedly affects the GRUB bootloader, a critical component most Linux systems use to manage the boot process.

The exploit allows attackers to bypass authentication mechanisms, potentially gaining root access to the system.

This type of vulnerability is hazardous as it can be used to install persistent and stealthy malware, making detection and mitigation challenging.

This is not the first time GRUB has been targeted.

In 2015, a similar vulnerability (CVE-2015-8370) was discovered. It allowed attackers to bypass authentication by pressing the backspace key 28 times at the GRUB username prompt.

This flaw affected GRUB versions from 1.98 to 2.02 and was widely exploited before being patched. 

More recently, in 2020, the BootHole vulnerability (CVE-2020-10713) was identified, which could be exploited to install malware during the boot process.

Implications and Response

The implications of this new zero-day are severe.

If exploited, attackers could gain complete control over affected systems, leading to data breaches, system disruptions, and potential espionage.

Major Linux distributions, including Debian, RedHat, and Ubuntu, have quickly released advisories and patches for previous GRUB vulnerabilities, and they are expected to respond similarly to this new threat.

Cybersecurity experts urge users to stay vigilant and apply security updates as soon as they become available.

Additionally, system administrators are advised to implement security hardening measures to mitigate the risk of exploitation during the window of vulnerability.

This new zero-day vulnerability in the Linux GRUB bootloader underscores the ongoing challenges in securing critical system components.

As the cybersecurity community works to address this threat, users must remain proactive in maintaining their systems’ security.

Free Webinar! 3 Security Trends to Maximize MSP Growth -> Register For Free


[ad_2]
Source link

Google Pixel vulnerability is worrying even the US government

0
[ad_1]

The latest monthly Pixel security update revealed a vulnerability that could be exploited, and that has even worried the US government. Officials were urged to update their phones within a maximum of 10 days or stop using them.

The US government warns federal employees to update their Pixel devices or stop using them

The vulnerability in question is listed as CVE-2024-32896. It could go unnoticed in normal situations, but Google added a note giving it special importance. The note says: “There are indications that CVE-2024-32896 may be under limited, targeted exploitation.” The entry is listed as “High Severity.”

Google has not revealed more specific details about the vulnerability. However, the US government warned all federal employees that “Android Pixel contains an unspecified vulnerability in the firmware that allows for privilege escalation.” The term “privilege escalation” refers to the fact that exploiting the vulnerability potentially allows the capture or access of the data of the attacked person.

It’s noteworthy that the vulnerability that is worrying the U.S. government is a “zero-day exploit.” This means that it was already present for a while but had not been detected by the OS developer or phone manufacturer. Therefore, there was no patch available yet to fix it.

Fix available with the QPR3 update

It’s noteworthy that, for Google Pixel devices, the fix is available with the latest Android 14 QPR3 (June) update. So, it is recommended that all Pixel device users update their devices if they have not already done so. That said, the GrapheneOS team says that the vulnerability could also be present in Android devices from other brands. However, the fix for them will be available with Android 15.

It is very unlikely that your device will be the target of an attack using the CVE-2024-32896 vulnerability. After all, Google is using the term “limited, targeted exploitation,” in the listing. However, it never hurts to keep your mobile device up-to-date in terms of security. You can update your Pixel device by going to Settings > System > Software Updates.


[ad_2]
Source link

Apple charged under EU’s DMA rules for App Store violations

0
[ad_1]

Apple has become the first company to be charged under the European Union’s Digital Markets Act (DMA). The European lawmakers found the iPhone maker non-compliant with their app store rules. It allegedly doesn’t allow app developers to freely steer users to offers outside its App Store. The European Commission has sent a formal warning to the company over the matter. The EU also launched a fresh investigation into Apple’s support for third-party iOS app marketplaces.

The EU charged Apple with violating DMA rules for app stores

The DMA is the EU’s new law aimed at identifying and regulating digital gatekeepers so the market is fairer and more contestable for all players, big and small. The so-called six gatekeepers—Apple, Amazon, Microsoft, Alphabet (Google), Meta, and ByteDance (TikTok)—were given until March 2024 to comply with the new rules. Among those is a rule that makes third-party developers more independent in choosing payment avenues and installation sources for their apps.

Developers can steer users to other platforms with better offers, and the gatekeepers can’t stop them. They also can’t levy any fee on developers for doing so. However, Apple didn’t fully comply with this rule. While it did open up the App Store to outside stores and payment avenues, the company tried to play smart. First, it froze Fortnite and Epic’s developer accounts for steering users away. And when it lifted the ban, the iPhone maker charged a 27% commission on transactions.

Of course, European lawmakers were watching this and promptly charged Apple under the DMA. “Our preliminary position is that Apple does not fully allow steering,” said Margrethe Vestager, the head of competition policy in Europe. “Steering is key to ensure that app developers are less dependent on gatekeepers’ app stores and for consumers to be aware of better offers.” Apple has until March 2025 to respond to the EU’s allegations, which is a long time to make amendments.

If Apple still doesn’t comply with the EU’s DMA rules, it faces a fine of up to 10% of its annual worldwide revenue. Based on last year’s earnings, the fine would amount to $38 billion. The fine amount increases to 20% of the annual revenue if a company is charged with repeat infringements. Time will tell how Apple will respond. The EU previously fined the company €1.84 billion (approx. $2 billion) for similar anti-steering practices in an antitrust case pre-dating the DMA.

Apple is also facing a fresh investigation from the European watchdog

Apple has another case looming over its head in Europe. The EU is investigating its policies for third-party iOS app stores. The primary focus is on the company’s Core Technology Fee, which requires outside app stores and apps to pay a €0.50 fee per installation. Apple also makes users pass through a laborious multi-step process to install third-party marketplaces and apps from those marketplaces. All the while, it shows various warnings to try and restrict users to its App Store.

Additionally, the EU is looking into Apple’s various eligibility requirements for developers to be able to offer third-party app stores. “The developers’ community and consumers are eager to offer alternatives to the App Store. We will investigate to ensure Apple does not undermine these efforts,” said Vestager. Apple, meanwhile, recently blamed the DMA’s “regulatory uncertainties” for delaying the launch of its AI features in Europe. The firm says the EU’s interoperability requirements are a threat to privacy and security.


[ad_2]
Source link

Blackmagic releases its excellent camera app for Android, but only if you have certain devices

0
[ad_1]

Image credit — Blackmagic

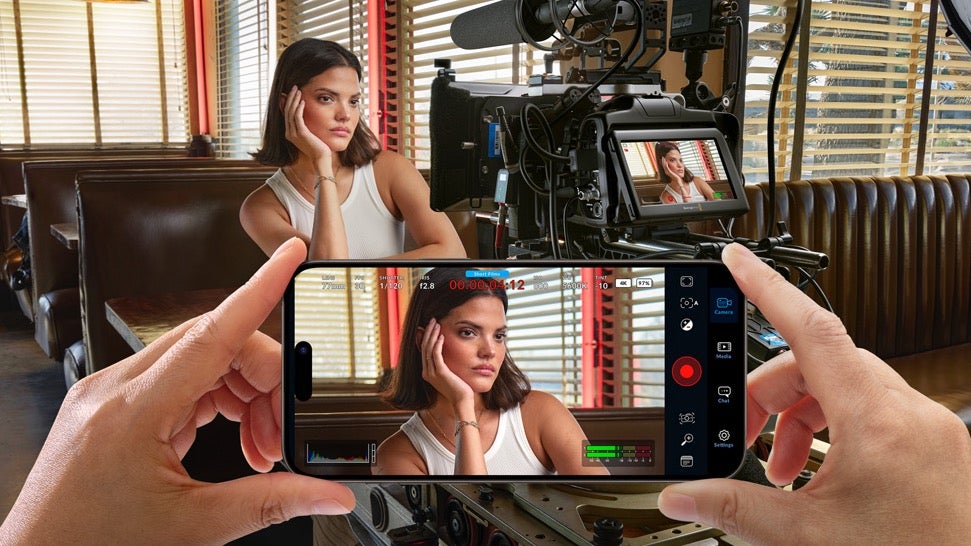
Blackmagic, a name known for high-quality digital film cameras and DaVinci Resolve video editing software, has released a free camera app for Android devices that promises to deliver professional-level video controls to smartphones.

The Blackmagic Camera app, now available on the Google Play Store, is packed with features that will appeal to experienced videographers, including histograms, audio meters, focus assist, frame guides, and a customizable viewfinder. Users can record videos in up to 8K resolution on compatible devices and have full control over shutter speed, ISO, white balance, tint, and 3D LUTs.

The app works with all camera sensors on a phone and supports recording in the H.265 codec with Rec.709 or HLG10 color space. It also integrates with DaVinci Resolve, allowing users to upload footage directly to a specific project.

Blackmagic Camera for Android supports many of the features of its iOS counterpart | Images credit — Blackmagic

While the Blackmagic Camera app unlocks a wide range of professional shooting options, it’s important to remember that the app itself can’t magically enhance the physical camera hardware on your phone. This means that the maximum recording resolution you’ll be able to achieve will ultimately be determined by the capabilities of your phone’s camera sensors. For instance, while the app can take advantage of the high-end hardware in the Samsung Galaxy S23 Ultra to capture stunning 8K footage, it will be limited to 4K resolution on the Google Pixel 8 Pro, which has a less powerful camera system.

It’s true that some advanced controls might already be available in the Pro mode of certain Android phones, particularly those from Samsung and Xiaomi. However, for Pixel users this will be a game-changer, as they will find that the Blackmagic Camera app offers significantly more powerful options than the standard Pixel Camera app. Grant Petty, Blackmagic Design CEO, said of this launch:
The Blackmagic Camera app is currently in its early stages, and Blackmagic Design has only confirmed compatibility with a limited selection of recent flagship smartphones. However, the app is expected to receive updates in the future that may broaden its compatibility with additional devices. So far, the app has been successfully installed and confirmed to work on the below devices:

I was disappointed to see that the Google Pixel Fold, Samsung Galaxy Z Fold 5, OnePlus Open, and OnePlus 12 were left out of the list of supported devices. I was very excited to try this out on my Pixel Fold, only to be met with a sad no. Hopefully support for these devices will be added soon as their specs can certainly handle the requirements for this app. 

[ad_2]
Source link

Google Addressed Numerous Security Flaws With Chrome 126

0
[ad_1]

With the latest Chrome 126 release, Google patched multiple security flaws affecting the browser, including a high-severity vulnerability exploited at a hacking event.

Google Chrome 126 Fix Multiple Security Flaws

This week, Google rolled out the Chrome browser version 126 (stable release) for the users. Like most security updates, this stable release also addressed numerous security flaws in the browser that could have severely impacted users when exploited.

One of these vulnerabilities includes a type confusion vulnerability in Chrome’s V8 component. The vulnerability first caught the attention of security researcher Seunghyun Lee, who demonstrated the flaw at the recent SSD Secure Disclosure’s TyphoonPWN 2024 hacking event. Identified as CVE-2024-6100, this vulnerability received a high severity rating and earned the researchers a $20,000 bounty for the discovery.

Another major security fix addressed CVE-2024-6101, a high-severity vulnerability due to inappropriate implementation in WebAssembly. Google credited the researcher with the alias “ginggilBesel” for reporting the flaw, who also won a $7000 bounty.

Besides, this Chrome release also includes two other security fixes for high-severity vulnerabilities in Dawn. These are CVE-2024-6102, an out-of-bounds memory access, and CVE-2024-6103, a use-after-free flaw. Google acknowledged the researcher with the alias “wgslfuzz” for reporting both vulnerabilities.

As mentioned in Google’s release update, these security fixes have been released with Chrome 126.0.6478.114/115 for Windows and Mac devices and 126.0.6478.114 for Linux systems. Moreover, the tech giant released the same security patches with Chrome for Android version 126.0.6478.110, which users may download from the Google Play Store.

Since Google released these patches with the respective Chrome browsers for different systems, users must keep their devices updated with the latest browser releases to remain safe. Thankfully, none of these vulnerabilities is zero-day, saving users from the worries of active attacks. Still, keeping all devices up-to-date with the latest releases is important for better security.

Let us know your thoughts in the comments.


[ad_2]
Source link
OnePlus Pad Pro live images surface ahead of launch

0
[ad_1]

The OnePlus Pad Pro live images have just appeared, ahead of launch, following official renders. As a reminder, this tablet is expected to arrive in a couple of days, on June 27. It will be accompanied by a number of other devices, more on that later on.

The OnePlus Pad Pro live images have just surfaced

Nine OnePlus Pad Pro live images have surfaced, courtesy of Digital Chat Station. This is one of the most prolific tipsters in the industry, so chances are that these images are spot on.

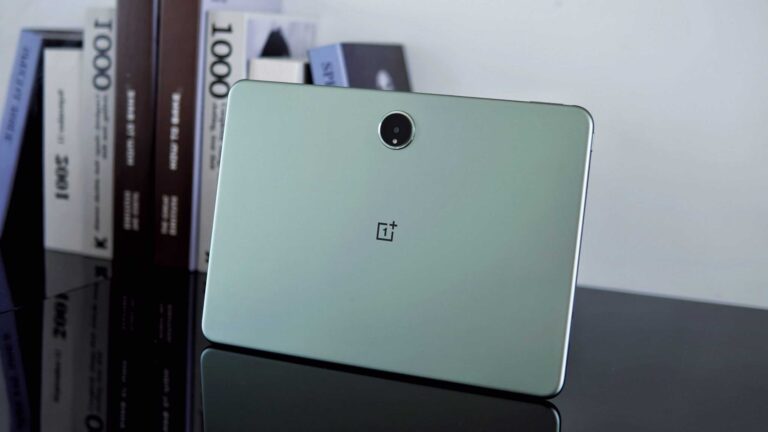
We get to see the tablet from both front and back here. It will have rather thin bezels (for a tablet), but not too thin, so you’ll be able to grip it… easily. Glass will be included on the back, with a centered OnePlus logo.

A single camera will be included inside a circular camera island, while an LED flash will also sit in there. That camera island will be centered up top, looking from a horizontal position, of course. The frame on the sides will be rounded, and both the front and the back side will curve into it.

This tablet will look a lot like the company’s current-gen model

Design-wise, this thing looks very similar to the OnePlus Pad 2. The bezels on it do seem to be a bit thicker, though, but not by much. This tablet is expected to include the Snapdragon 8 Gen 3 SoC, Qualcomm’s most powerful chip.

Now, you’ll also notice that a keyboard accessory is pictured in the provided images. The same goes for a stylus. Well, both of those accessories will likely be announced on June 27 too.

In addition to the OnePlus Pad Pro, OnePlus is aiming to launch the OnePlus Watch 3 on June 27. The OnePlus Ace 3 Pro will also be announced, and the same goes for the OnePlus Buds Pro 3.

OnePlus will have a lot on its plate on June 27. All of these devices are expected to launch globally too, though the OnePlus Ace 3 Pro will likely be called the OnePlus 12T.


[ad_2]
Source link